Secure on paper.
And when it counts?
Raise your security level, strengthen cyber resilience.
Assets, controls, risks and evidence connected, for ISO 27001, NIS2 and DORA.
Trusted by leading organizations
From a documented ISMS
to an effective ISMS
Policies, asset lists and control catalogues exist in most organizations. What sets them apart is whether they are connected.
An ISMS that lives for the auditor
Assets in Excel, controls in a Word catalogue, risks on a separate list. The connection is only made during the audit, by hand.
- Assets, controls and risks on separate lists
- Evidence is collected shortly before the audit
- Every standard is mapped and maintained on its own
- Exceptions expire without anyone noticing
An ISMS that works day to day
Protection requirements, controls, risks, incidents and actions stay linked to the asset. Evidence builds up continuously in the process, not in a final sprint.
- Protection requirements and controls linked to the asset
- Evidence builds up continuously, the ISMS stays audit ready
- One control set for ISO 27001, NIS2, DORA and more
- Exceptions, deadlines and actions monitored automatically
Your entire ISMS,
in one place
Capture, assess, treat, monitor and report. Click through the six views.
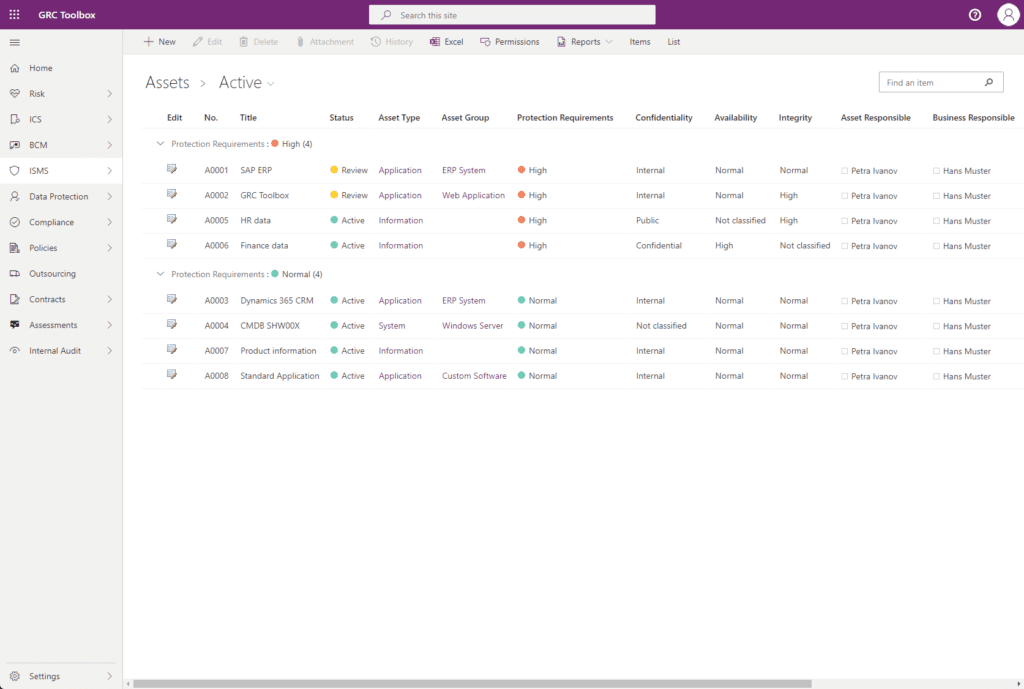
Every asset with its protection requirement
Processes, information, systems and applications in one inventory. Confidentiality, integrity and availability are rated, and the protection requirement follows from them.
- Complete asset inventory with clear ownership
- Protection requirement derived from confidentiality, integrity and availability
- Integration with SNOW, LeanIX and other sources
See what depends on which asset
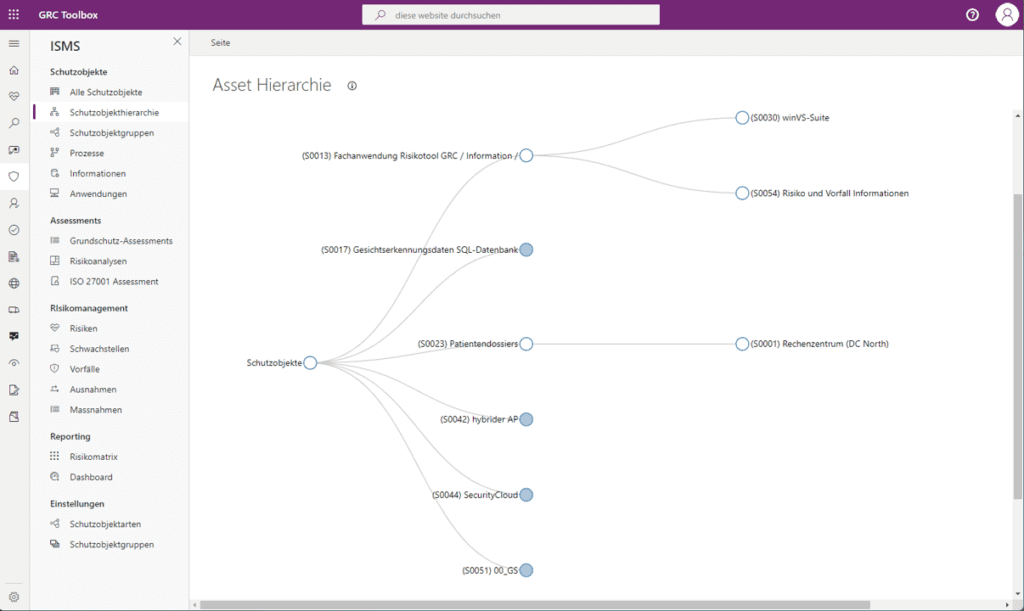
Trace the connections between processes, information, systems and applications and recognize how a single change ripples through.
- Dependencies as a graph instead of a table
- Protection requirements traceable along the chain
- Single points of failure and bottlenecks spotted early
Implementation status per control, evidenced
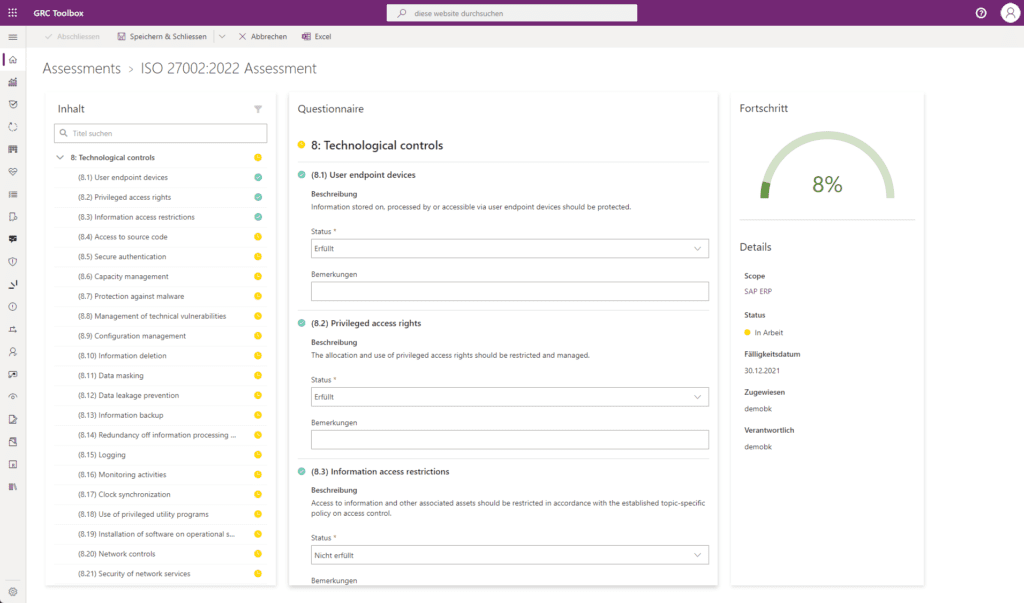
Questionnaires and workflows determine the implementation status of every control, with evidence file, owner and due date. Coverage becomes visible.
- Assessments for ISO 27001, IT-Grundschutz and more
- Evidence attached directly to the control
- Gaps lead to actions or documented exceptions
Risks assessed, actions tracked
Capture, analyse, assess and prioritize information security risks. Treatment runs through workflows with clear ownership and deadlines.
- Risk matrix and dashboards per organizational unit
- Actions with owner, due date and progress
- Linked to assets, controls and incidents

From the event to the cause and back
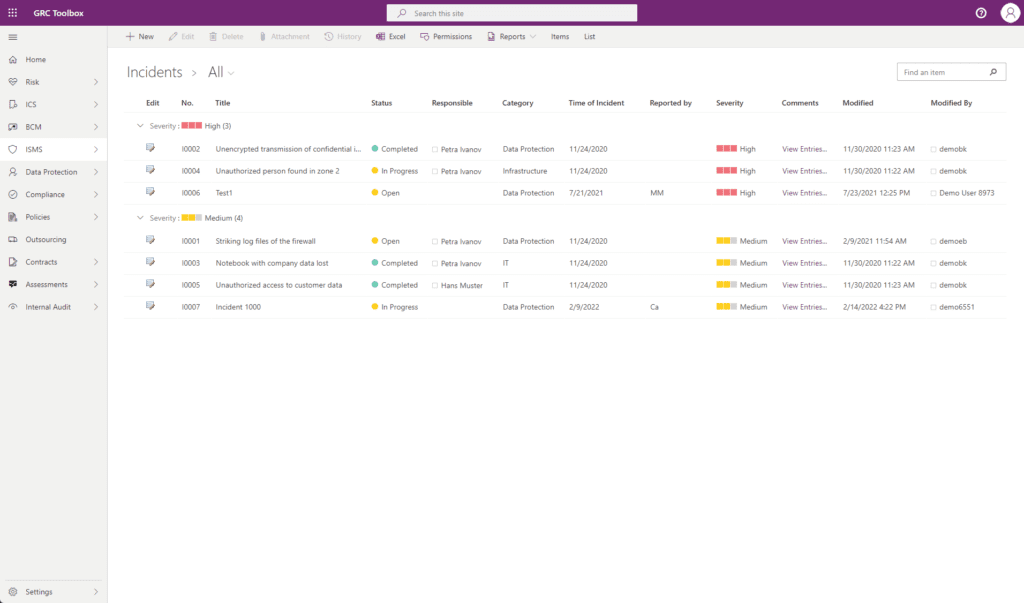
Security events, incidents and vulnerabilities captured and assessed centrally, with the full cause and effect chain down to the affected asset.
- Incident dashboard by severity and over time
- Vulnerabilities linked to source, asset and risk
- Treatment tracked through workflows
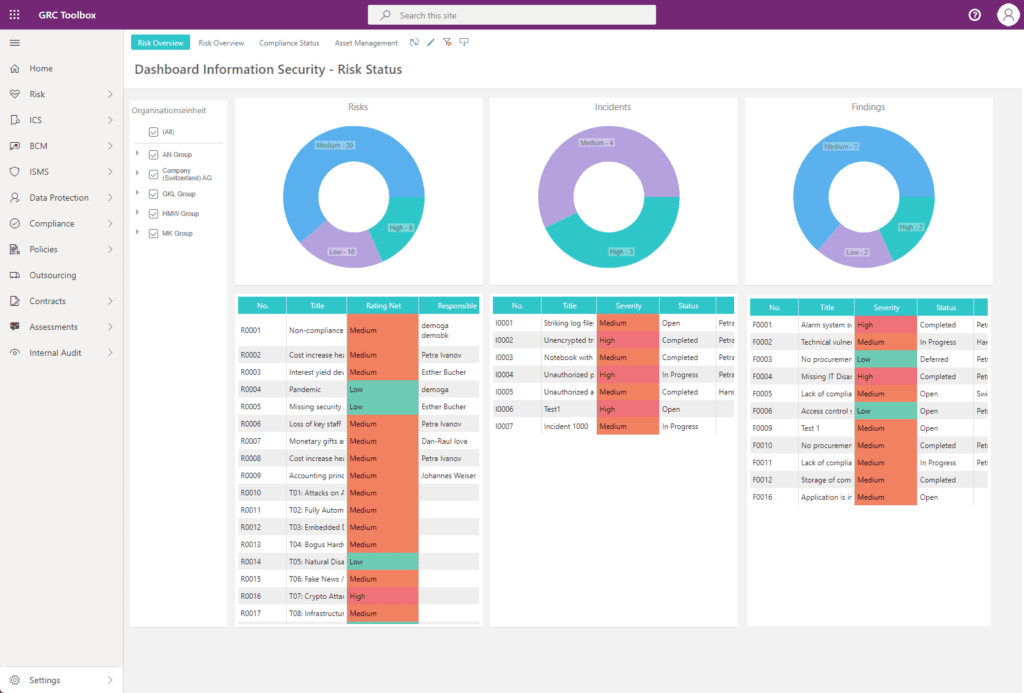
Security posture reported to the right audience
Assets, control status, audit results and risks in one dashboard. One picture that both management and the auditor can rely on.
- Control status and coverage per standard
- Risks, incidents and findings side by side
- Custom reports for every committee
From the Statement of Applicability
to defensible evidence
Certification is not a project, it is a cycle. The platform carries it, from the policy through to the management review.
Greater effectiveness,
less effort
Comprehensive and simple at the same time. That is what drives adoption and lifts maturity.
Everything connected to the asset
Protection requirements, controls, risks, incidents and actions all hang on the asset. The connection can be queried, not reconstructed.
One control set, many standards
Assess once, evidence many times: ISO 27001, NIS2, DORA, NIST CSF, IT-Grundschutz and CIS on the same foundation.
Audit ready at any time
Evidence builds up continuously in the process. Internal and external audits stop being exceptional events.
Part of a connected GRC system
Information security shares one foundation with ICS, risk management, BCM, data protection and TPRM.
Stronger security culture
Workflows involve asset and process owners in their day to day work, not just once a year.
Higher maturity through standards
Standardized along ISO/IEC 27001 and 27005: one consistent, automated approach across the entire organization.
See our ISMS solution
in action
In a personal demo we walk you through the SwissGRC® Platform and show how assets, controls, risks and evidence work together.
DE
FR