Generated by All in One SEO Pro v5.0.1.1, this is an llms-full.txt file, used by LLMs to index the site.
# Swiss GRC (FR)
Governance, Risk & Compliance (GRC)
## Articles
### [Three Lines, One Picture: What the New Three Lines Model Changes](https://swissgrc.com/fr/three-lines-one-picture-three-lines-model-iia-guidance/)
**Published:** septembre 3, 2026
**Author:** superadmin
**Excerpt:** The revised IIA statements of 2026 do not shift responsibility away from the first line, which continues to own and manage risk. They do, however, require closer coordination and documented safeguards wherever internal audit takes on second line tasks or contributes to the five ERM activities of identifying, assessing, managing, monitoring and reporting, without making risk decisions itself.
**Content:**
On 8 July 2026, the IIA published two revised statements of position: one on the Three Lines Model, one on the role of internal audit in enterprise risk management. Both replace the previous position papers and shift the emphasis from rigid separation to coordination between the lines. For governance, risk and compliance leaders, the question is where the day to day boundary between management, the second line and internal audit actually changes.
In short
The revised IIA statements of 2026 do not shift responsibility away from the first line, which continues to own and manage risk. They do, however, require closer coordination and documented safeguards wherever internal audit takes on second line tasks or contributes to the five ERM activities of identifying, assessing, managing, monitoring and reporting, without making risk decisions itself.
Contents
1. [What exactly changes on 8 July 2026?](#a1-what-exactly-changes-on-8-july-2026)
2. [Where does the new boundary between management and the second line run?](#a2-where-does-the-new-boundary-between-mana)
3. [What can internal audit do, and not do, within the ERM cycle?](#a3-what-can-internal-audit-do-and-not-do-wi)
4. [Why does internal audit remain the integrator rather than one line among many?](#a4-why-does-internal-audit-remain-the-integ)
5. [Is the new ERM statement binding?](#a5-is-the-new-erm-statement-binding)
6. [How should GRC leaders proceed now?](#a6-how-should-grc-leaders-proceed-now)
## What exactly changes on 8 July 2026?
On that date, the IIA published two new statements of position that replace the previous position papers on the Three Lines Model and on the role of internal audit in enterprise risk management.
The revised Three Lines Model is addressed primarily to the board and emphasises the accountability of every organisational role for its own distinct contribution to governance and risk management. As a modernised framework, it is meant to remain flexible enough to apply to organisations with different structures, risk environments and levels of maturity, as the IIA sets out in its statements of position.
At the same time, the statement reaffirms that appropriate safeguards must be in place for the Chief Audit Executive whenever that role takes on second line tasks. These safeguards are meant to protect the independence of internal audit and the objectivity of auditors.
## Where does the new boundary between management and the second line run?
The first line remains the owner of risk: management owns and manages risk and is accountable for it, as stated in the official PDF of the statement.
The body text itself does not give a final definition of the second line, but the published section headings on implementation scenarios point to more flexibility than earlier versions allowed. The statement acknowledges that roles across the three lines can overlap in practice, and it offers guidance on managing such arrangements rather than ruling them out on principle.
Organisations that allow such overlaps should document the allocation of responsibilities in a way that makes gaps between assigned and actually exercised responsibility visible, an idea that aligns with using governance lag as a metric for the risk register.
- Transparent and documented allocation of responsibilities
- Independent review of activities that carry self-review or oversight risk
- Explicit board approval of expanded mandates
- Timely communication of actual or perceived threats to objectivity
Dashboard for Assessing the Adequacy and Effectiveness of Controls## What can internal audit do, and not do, within the ERM cycle?
The ERM statement describes enterprise risk management as a coordinated set of five activities, identifying, assessing, managing, monitoring and reporting, to which internal audit contributes through assurance and advice without taking on responsibility itself.
A technical analysis by Symbiant notes that internal audit can provide advice or assurance on each of the five activities, but must not determine management’s approach, prioritise responses, implement controls, or take ownership of risk reporting. In practice, this dividing line decides whether an audit activity still counts as assurance or has effectively become management.
According to the statement, other functions and roles also support the organisation’s assurance and advisory efforts. This is consistent with the principle that risk management serves the achievement of objectives rather than existing for its own sake, which is why responsibility for risk decisions must stay with those accountable for the objective.
## Why does internal audit remain the integrator rather than one line among many?
The model reaffirms internal audit’s role as the integrator of assurance, providing the board with a comprehensive, organisation-wide view, regardless of how many functions contribute to assurance.
A technical article on Tandfonline notes that the core accountabilities are preserved in the 2026 statements, but coordination, reliance and integrated assurance receive markedly more weight than in the 2020 version. The renaming from Three Lines of Defense to Three Lines Model back in 2020 had already, according to Accounting Today, softened the purely defensive orientation and given more emphasis to seizing opportunity as part of risk-based decision making.
## Is the new ERM statement binding?
No: one commentator, writing on 16 July 2026, classifies the document as a position paper that reflects the IIA’s view but does not constitute a binding requirement.
For governance, risk and compliance functions, this means the statements offer orientation for clarifying their own roles but do not trigger any certification obligation. Organisations revising the boundaries between the three lines should nonetheless measure their own governance model against the safeguards described, because doing so makes independence easier to verify.
## How should GRC leaders proceed now?
The first step is to take stock of which second line tasks internal audit already performs in practice today, and whether the safeguards named in the statement are documented for them.
This stocktaking should be carried out by the head of internal audit together with the Chief Risk Officer or the compliance officer, and reported to the board before any new mandates are assigned. Where roles already overlap, it is worth examining new interfaces, for instance where additional audit and advisory tasks arise, a question that also comes up when considering whether AI governance is merging with GRC or remaining a separate silo.
Related
### Document role clarification in a traceable way
The Internal Audit solution maps the audit plan and findings. It records responsibilities and safeguards between the lines in a way that stays traceable.
[Internal Audit ](https://swissgrc.com/fr/internal-audit-software/)
For practice
## Key points
- Check which second line tasks internal audit currently performs, and document the safeguards required for them.
- Keep internal audit’s contributions to the five ERM activities clearly separated from management responsibility.
- Obtain explicit board approval for any expanded mandate of the Chief Audit Executive.
- Use the new statements as orientation, not as a binding requirement, when clarifying your own roles.
FAQ
## Frequently asked questions
Who remains responsible for risk under the revised Three Lines Model?The first line, meaning management, remains the owner of risk and stays accountable for it. The revised Three Lines Model does not change this, but it does require closer coordination and documented safeguards whenever internal audit takes on second line tasks.
What safeguards does the IIA require when internal audit takes on second line tasks?The statement names four safeguards: transparent and documented allocation of responsibilities, independent review of activities that carry self-review or oversight risk, explicit board approval of expanded mandates, and timely communication of actual or perceived threats to objectivity, so that independence and auditor objectivity are preserved.
Can internal audit make risk decisions within the ERM cycle?No. Internal audit can contribute assurance and advice to all five ERM activities, identifying, assessing, managing, monitoring and reporting. It must not determine management's approach, prioritise responses, implement controls, or take ownership of risk reporting.
What role does internal audit keep relative to other assurance functions?Internal audit remains the integrator of assurance and provides the board with a comprehensive, organisation-wide view, regardless of how many other functions contribute to assurance. This role sets it apart from the other lines, even though coordination and reliance carry markedly more weight in the revised model than before.
Are organisations required to implement the revised IIA statements?No, the statements are position papers that reflect the IIA's view but are not binding and do not trigger any certification obligation. GRC leaders can use them as orientation for clarifying their own roles and measure their governance model against the safeguards described, without this creating any compliance obligation.
Sources
1. [Statements of Position for Internal Auditing](https://www.theiia.org/en/resources/statements-of-position/)IIA
2. [Internal audit and risk management](https://normanmarks.wordpress.com/2026/07/16/internal-audit-and-risk-management-3/)Norman Marks on Governance, Risk Management, and Internal Audit
**Catégories:** Regulation & Supervision
**Étiquettes:** IIA Statements of Position, Enterprise Risk Management, Chief Audit Executive, second line internal audit, Governance Risk Compliance
---
### [Where the Business Continuity Plan Hands Off to the Crisis](https://swissgrc.com/fr/business-continuity-plan-crisis-handover/)
**Published:** septembre 2, 2026
**Author:** superadmin
**Excerpt:** The handover between a documented business continuity plan and operational crisis management usually does not fail because a plan is missing, but because of shift changes and role handovers in the crisis team that classic tests rarely simulate. Regulatory requirements such as FINMA Circular 2023/1 do require tests based on severe but plausible scenarios, but these primarily verify that a plan exists, not whether the organisation can actually act under time pressure.
**Content:**
The business continuity plan is in place, approved by executive management and formally covers the regulatory requirements. Yet in many organisations operational crisis management does not fail because a plan is missing, but at the point where documented measures must turn into actual action. This handover between paper and practice is rarely tested explicitly and is often left out of classic tests. Exactly where this interface breaks usually only becomes apparent in a real crisis.
In short
The handover between a documented business continuity plan and operational crisis management usually does not fail because a plan is missing, but because of shift changes and role handovers in the crisis team that classic tests rarely simulate. Regulatory requirements such as FINMA Circular 2023/1 do require tests based on severe but plausible scenarios, but these primarily verify that a plan exists, not whether the organisation can actually act under time pressure.
Contents
1. [What does regulation require of the business continuity plan?](#a1-what-does-regulation-require-of-the-busi)
2. [Why is a plan on file not enough on its own?](#a2-why-is-a-plan-on-file-not-enough-on-its-)
3. [Where exactly does the handover break down in a real crisis?](#a3-where-exactly-does-the-handover-break-do)
4. [Who is responsible for these handover points?](#a4-who-is-responsible-for-these-handover-po)
5. [How can the handover be tested and closed in concrete terms?](#a5-how-can-the-handover-be-tested-and-close)
## What does regulation require of the business continuity plan?
FINMA Circular 2023/1 on operational risks requires banks to maintain a documented business continuity plan including a disaster recovery component, which is reviewed at least once a year.
The circular replaces the previous ‘Recommendations for Business Continuity Management’ issued by the Swiss Bankers Association as the minimum standard and entered into force on 1 January 2024, with staggered transition periods of up to two years to ensure operational resilience.
As part of the business impact analysis, each institution identifies its critical processes together with recovery time, data loss tolerance and the resources required for them. Implementation must be assessed regularly through tests such as table-top exercises, with the test scope covering severe but plausible scenarios.
## Why is a plan on file not enough on its own?
Because in practice tests often confirm only that the plan exists and is up to date, not that the organisation is actually able to execute it under pressure.
A specialist analysis of the practical implementation of business continuity plans finds that many companies have already identified their risks but struggle to implement the strategy derived from them. The focus is usually on drafting the plan rather than on realising it, because translating theory into practice requires coordination, precision and continuous adjustment.
ISO 22301 addresses this pattern with the PDCA cycle: in the ‘check’ phase, business continuity plans must be tested and the results monitored, not documented just once. The plan thus remains a means to an end, not an end in itself.
Exercises and Tests on the SwissGRC Platform## Where exactly does the handover break down in a real crisis?
At the shift changes and role handovers within the crisis team, which become unavoidable in situations that last longer.
A specialist article on exercises in business continuity management notes that longer exercises spanning two or more days reflect the realistic challenges of an emergency particularly well, because they require shift changes in crisis management and handovers within processes. It is precisely at these handovers that it becomes clear whether responsibilities, awareness of the situation and decision-making authority are actually passed on, or whether knowledge is lost with every change.
ISO/IEC 27031 therefore requires that tests and exercises not be limited to restoring ICT services, but also cover protecting assets from disruption and minimising the impact of damage. A test that only measures the technical recovery time does not examine the point where the handover actually fails in practice.
## Who is responsible for these handover points?
Executive management is responsible for implementing and documenting the management of operational risks, while the board of directors regularly approves and oversees this management.
This allocation formally clarifies who is responsible for the plan as a document. It does not, however, answer who is responsible for the handover between shifts in the crisis team in a real event, or who decides when an escalation to the next level takes place.
Even for third parties whose resources feed into the business impact analysis, a designated party is needed to coordinate the handover in a real event. Without this allocation, responsibility remains where it is written in the document, not where it is needed in the event itself.
## How can the handover be tested and closed in concrete terms?
By having the next test exercise specifically simulate a shift change or role handover and document who takes over responsibility and at what point.
A first step: during the next annual review of the business continuity plan, the responsible party defines which handover points exist within the crisis team and assigns a name and a trigger to each point. This assignment is documented as an explicit part of the plan, not merely noted as an observation from the last test exercise. A similar gap between what a document prescribes and what must already be operationally in place also appears in other regulatory deadlines, such as the ISMS obligation under Switzerland’s Information Security Act (ISG).
Related
### From plan to rehearsed handover
Business Continuity documents critical processes, resources and exercise results in one place, and records who is responsible for each handover point in the crisis team.
[Business Continuity ](https://swissgrc.com/fr/bcm-software/)
For practice
## Key points
- Institutions check whether their business continuity plan explicitly names handover points in the crisis team, not just critical processes and resources.
- Test exercises specifically simulate shift changes over several days, because that is exactly where knowledge and decision-making authority can be lost.
- Under ISO/IEC 27031, tests cover more than ICT recovery and include the protection of assets and the minimisation of damage.
- For each handover point, a named responsible person with a clear trigger is documented, not just executive management as the overall responsible party.
- The annual review of the plan under FINMA Circular 2023/1 is used to add handover points, not only to update RTO and RPO.
FAQ
## Frequently asked questions
What deadline applies to implementing FINMA Circular 2023/1?FINMA Circular 2023/1 entered into force on 1 January 2024 and replaces the previous BCM recommendations of the Swiss Bankers Association as the minimum standard. Staggered transition periods of up to two years apply to implementation, within which institutions must align their business impact analysis, business continuity plan and associated tests with the new requirements.
Why does a tested business continuity plan not automatically suffice?In practice, tests often confirm only that a business continuity plan exists and is up to date, not that the organisation can actually execute it under time pressure. The focus is frequently on drafting the plan rather than on realising it, because translating it into practice requires coordination and continuous adjustment.
What role do shift changes in the crisis team play in crisis management?In exercises lasting two or more days, shift changes in the crisis team become unavoidable. It is precisely at these handovers that it becomes clear whether responsibilities, awareness of the situation and decision-making authority are actually passed on, or whether knowledge is lost with every change, which reveals the actual resilience of crisis management.
Who is responsible for managing operational risks according to FINMA?Executive management is responsible for implementing and documenting the management of operational risks, including the business continuity plan. The board of directors regularly approves and oversees this management. Who specifically coordinates the handover between shifts in the crisis team in a real event is, however, not yet formally clarified by this.
What does ISO/IEC 27031 require in addition to recovery tests?ISO/IEC 27031 requires that tests and exercises not be limited to restoring ICT services. They should also cover protecting assets from disruption and minimising the impact of damage, so that not only the technical recovery time is tested but also the organisation's actual ability to act.
Sources
1. [FINMA Circular 2023/1 on operational risks and resilience](https://www.finma.ch/en/news/2022/12/20221213-mm-anh-rs-op-risks/)FINMA
2. [Principles for Operational Resilience](https://www.bis.org/press/p210331a.htm)Bank for International Settlements (BIS)
**Catégories:** Regulation & Supervision
**Étiquettes:** FINMA Circular 2023/1, crisis team handover, business impact analysis, ISO 22301
---
### [24 Hours to Report: Who Needs to Be Part of the Internal Decision](https://swissgrc.com/fr/24-hours-to-report-internal-decision-makers/)
**Published:** septembre 1, 2026
**Author:** superadmin
**Excerpt:** From 11 September 2026, Article 14 of the Cyber Resilience Act requires an early warning within 24 hours of becoming aware of an actively exploited vulnerability, submitted simultaneously to the competent CSIRT and to ENISA. To meet this deadline, CSIRT assignment, named primary and secondary contacts with a backup rule, and internal triage must already be established before an incident occurs.
**Content:**
From 11 September 2026, manufacturers must report actively exploited vulnerabilities to a competent CSIRT and simultaneously to ENISA within 24 hours of becoming aware of them. This deadline starts when awareness is gained, not when an internal decision is made about whether to report. Organisations that only clarify responsibility, contacts and triage criteria once an incident occurs lose valuable hours. The reporting obligation under Article 14 of the Cyber Resilience Act only works if the decision chain is already in place beforehand.
In short
From 11 September 2026, Article 14 of the Cyber Resilience Act requires an early warning within 24 hours of becoming aware of an actively exploited vulnerability, submitted simultaneously to the competent CSIRT and to ENISA. To meet this deadline, CSIRT assignment, named primary and secondary contacts with a backup rule, and internal triage must already be established before an incident occurs.
Contents
1. [What exactly must be reported within 24 hours?](#a1-what-exactly-must-be-reported-within-24-)
2. [Which CSIRT is responsible, and how does ENISA come into play?](#a2-which-csirt-is-responsible-and-how-does-)
3. [Why must the decision chain be established before an incident occurs?](#a3-why-must-the-decision-chain-be-establish)
4. [What follows the early warning?](#a4-what-follows-the-early-warning)
5. [Who is exempt from the reporting obligation?](#a5-who-is-exempt-from-the-reporting-obligat)
6. [What specifically needs to be clarified by 11 September 2026?](#a6-what-specifically-needs-to-be-clarified-)
24hrs
Deadline for the early warning after becoming aware
cyber-resilience-act.de, Article 14 Reporting Obligations of Manufacturers
72hrs
Deadline for the follow-up report with detailed information
mogwailabs, Reporting and Disclosure Obligations under the Cyber Resilience Act
14days
Deadline for the final report after a corrective measure becomes available
itmr-legal, Cyber Resilience Act: Reporting Obligations under the CRA from 11 September 2026
## What exactly must be reported within 24 hours?
The manufacturer submits an early warning about the actively exploited vulnerability, naming at least the affected member states, simultaneously to the competent CSIRT and to ENISA.
The deadline starts when awareness is gained and requires action without undue delay, but in any case within 24 hours at the latest. The relevant provision is [Article 14 of the Cyber Resilience Act](https://cyber-resilience-act.de/cra/kapitel-2/artikel-14/), which provides for reporting via the single reporting platform, so that the CSIRT and ENISA receive access at the same time.
This first report deliberately stays brief: it identifies the vulnerability and the affected states, nothing more. Organisations that only clarify who is authorised to report and what information is permissible at this stage have already missed the deadline.
## Which CSIRT is responsible, and how does ENISA come into play?
The competent CSIRT is the one in the member state of the manufacturer’s main establishment, in Germany for example the BSI; ENISA receives the same report in parallel via the shared platform.
If a manufacturer has no main establishment in the EU, a statutory order of precedence applies: first the member state of the authorised representative, then of the importer, then of the distributor, and finally the state with the most users. This cascade from Article 14(7) cannot be improvised once an incident occurs; it must be worked through and documented in advance.
Similar uncertainty about one’s own classification is already visible in the NIS2 registration gap, where companies only clarify their own scope of application at a late stage. Under the Cyber Resilience Act, the short deadline makes this problem even more pressing.
## Why must the decision chain be established before an incident occurs?
Because the 24-hour deadline runs from the moment awareness is gained and leaves no time for subsequent organisational clarification, CSIRT assignment, contacts and the approval process must be established in advance.
Before 11 September 2026, a competent CSIRT must be determined based on the location of the main establishment, and a [primary and secondary contact](https://www.advisori.de/blog/cra-meldeplattform-enisa-srp-registrierung) must be named, including a backup rule for holidays and weekends. This preparatory work concerns not only the legal department but also the unit that first detects an actively exploited vulnerability, such as a security operations center.
The backlog visible in other CRA obligations, for instance around the software bill of materials, shows that this kind of preparatory work often only begins late across the industry. Organisations that only clarify approval for a report once an incident occurs lose time that the deadline does not allow for.
CSIRT assignment and named contacts should not be tested for the first time when an incident occurs.
## What follows the early warning?
Within 72 hours, the manufacturer provides a follow-up report with affected product versions, the type of vulnerability and available measures; a final report follows later.
The final report is due within 14 days of a corrective measure becoming available for an actively exploited vulnerability, or within one month for a severe security incident. The coordinating CSIRT only requests an intermediate report on demand; it is not a standard obligation.
Article 14(8) additionally obliges the manufacturer to inform affected users about the vulnerability; if the manufacturer fails to do so, the CSIRTs may carry out this notification themselves instead. This user notification also requires its own approval, which must be planned into the decision chain.
## Who is exempt from the reporting obligation?
Micro and small enterprises remain subject to the reporting obligation but face no fine if they miss the 24-hour deadline; good-faith security research without malicious intent does not fall under the reporting obligation at all.
These exemptions do not change the organisational task: even a small enterprise must know which CSIRT to contact and who approves the report internally. The fine is waived, the deadline is not.
An academic paper describes vulnerability governance as the central lever of this hybrid regulation, in which legally binding requirements are implemented through co-regulation and internal corporate self-regulation, coordinated at EU level by ENISA and the CSIRTs.
## What specifically needs to be clarified by 11 September 2026?
Companies falling under the Cyber Resilience Act should establish the CSIRT assignment, the contacts and the internal approval for the 24-hour report in writing before this date.
A first verifiable step: the unit responsible for product security determines the competent CSIRT by 11 September 2026, based on the main establishment or, in the absence of an EU establishment, on the cascade of authorised representative, importer, distributor and user numbers, and records this in writing. In parallel, primary and secondary contacts with a backup rule are named and integrated into the existing reporting organisation for security incidents.
That short reporting deadlines are not an isolated case is also shown by the BACS reporting deadlines in Switzerland. Organisations that document their own decision chain cleanly once are prepared for both regimes.
Related
### Mapping vulnerability reporting workflows
Information Security maps reporting channels and deadlines for vulnerabilities and documents responsibilities and approvals in a traceable way.
[Information Security ](https://swissgrc.com/fr/information-security-management-isms-software/)
For practice
## Key points
- Determine the competent CSIRT based on the main establishment or the statutory cascade before an incident occurs.
- Name primary and secondary contacts with a backup rule for holidays and weekends.
- Establish in writing who may approve an early warning without a prior case-by-case legal review.
- Plan the follow-up report, the final report and the user notification under Article 14(8) into the same process.
- Micro enterprises remain subject to the reporting obligation; the same preparation pays off even without the risk of a fine.
FAQ
## Frequently asked questions
From when does the 24-hour reporting obligation of the Cyber Resilience Act apply?From 11 September 2026, Article 14 of the Cyber Resilience Act requires an early warning within 24 hours of becoming aware of an actively exploited vulnerability. The report goes simultaneously to the competent CSIRT and to ENISA via the single reporting platform.
Which CSIRT is responsible if a manufacturer has no establishment in the EU?Without an EU main establishment, a statutory cascade applies: first the member state of the authorised representative, then of the importer, then of the distributor, and finally the state with the most users. This order under Article 14(7) must be clarified and documented in advance.
What happens if a micro enterprise misses the reporting deadline?Micro and small enterprises remain subject to the reporting obligation, but face no fine if they miss the 24-hour deadline. This does not remove the organisational task: they too must know which CSIRT to contact and who approves the report internally.
What information must the first report under Article 14 contain?The early warning deliberately stays brief and names the actively exploited vulnerability along with at least the affected member states. Further details, such as affected product versions, only follow in the follow-up report within 72 hours.
What follows the early warning under the Cyber Resilience Act?Within 72 hours, the manufacturer provides a follow-up report with product versions, the type of vulnerability and measures taken. The final report follows within 14 days or one month depending on the case, and Article 14(8) additionally requires informing affected users.
Sources
1. [Article 14 Reporting Obligations of Manufacturers](https://cyber-resilience-act.de/cra/kapitel-2/artikel-14/)cyber-resilience-act.de
2. [CRA Reporting Platform: What Must Be in Place by 11 September 2026](https://www.advisori.de/blog/cra-meldeplattform-enisa-srp-registrierung)advisori
**Catégories:** Regulation & Supervision
**Étiquettes:** CSIRT responsibility, 24-hour deadline vulnerability, ENISA reporting platform, early warning actively exploited vulnerability, Article 14 Cyber Resilience Act
---
### [Does AI Governance Merge with GRC or Create a New Silo](https://swissgrc.com/fr/ai-governance-grc-convergence-or-silo/)
**Published:** août 30, 2026
**Author:** superadmin
**Excerpt:** The AI Act, ISO/IEC 42001 and FINMA Supervisory Notice 08/2024 all point in the same direction: AI governance should be integrated into existing governance, risk management and control structures rather than built as a separate silo. AI-specific requirements around data quality, explainability and model risk call for additional expertise within the existing GRC function, not necessarily a new organisational unit.
**Content:**
In June 2026, Gartner published its first Magic Quadrant for AI Governance Platforms, assessing 13 vendors. An independent analysis of that publication finds that artificial intelligence is dissolving the boundaries that previously separated AI governance, data and analytics governance, business process governance, IT governance and classic GRC. For those responsible for governance, risk and compliance, this raises a structural question: should AI governance be integrated into the existing GRC function, or built up as a separate discipline alongside it. Regulation and standards already offer some initial guidance.
In short
The AI Act, ISO/IEC 42001 and FINMA Supervisory Notice 08/2024 all point in the same direction: AI governance should be integrated into existing governance, risk management and control structures rather than built as a separate silo. AI-specific requirements around data quality, explainability and model risk call for additional expertise within the existing GRC function, not necessarily a new organisational unit.
Contents
1. [What Does the First Magic Quadrant for AI Governance Platforms Show?](#a1-what-does-the-first-magic-quadrant-for-a)
2. [How Does the AI Act Regulate the Relationship Between AI Risk Management and Existing Processes?](#a2-how-does-the-ai-act-regulate-the-relatio)
3. [What Does ISO/IEC 42001 Offer as a Standalone Standard for AI Management Systems?](#a3-what-does-iso-iec-42001-offer-as-a-stand)
4. [Where Do Swiss Supervisors and Legislators Stand on AI Governance?](#a4-where-do-swiss-supervisors-and-legislato)
5. [How Can This Integration Be Implemented in Practice?](#a5-how-can-this-integration-be-implemented-)
## What Does the First Magic Quadrant for AI Governance Platforms Show?
In June 2026, Gartner assessed 13 vendors of AI governance platforms for the first time, confirming a distinct market for software that manages AI risk.
An independent analysis of the publication places the finding in a broader context: artificial intelligence is dissolving the boundaries that previously separated AI governance, data and analytics governance, business process governance, IT governance and GRC. This points less to a new, isolated discipline than to an extension of existing governance tasks to cover AI-specific questions. For organisations with an established GRC system, the relevant question is therefore less about adding another platform and more about which existing processes should absorb AI risk.
## How Does the AI Act Regulate the Relationship Between AI Risk Management and Existing Processes?
Article 9 of the AI Act requires a continuous risk management system throughout the lifecycle of high-risk AI systems, but explicitly allows this system to be integrated into processes that already exist.
Under [Article 9(10)](https://ai-act-service-desk.ec.europa.eu/en/ai-act/article-9), providers already subject to risk management obligations under other Union law may integrate the relevant aspects into their existing processes rather than building a parallel system. Article 17 additionally obliges providers of high-risk AI systems to maintain a quality management system, and Article 10 sets out specific requirements for data governance and data quality: datasets must be relevant, representative, free of errors and complete, as far as this is possible. The legislator itself therefore applies an integration logic, even though the substantive requirements are new for many GRC functions. This stance contrasts with the public debate about the AI Act stifling innovation or imposing overregulation.
## What Does ISO/IEC 42001 Offer as a Standalone Standard for AI Management Systems?
ISO/IEC 42001:2023 is the first international standard to set requirements for establishing, implementing, maintaining and continually improving an AI management system.
Like other management system standards, ISO/IEC 42001 is designed as a system that can be certified on its own, but it can equally be docked onto existing GRC structures, for example an existing information security or quality management system. This dual compatibility mirrors the logic of the AI Act: AI governance requires its own specialist building blocks, but does not need to be anchored organisationally apart from the rest of risk management. For those responsible for GRC, the decision therefore shifts from structure to resources: who contributes the expertise needed to handle intelligent risks, and which existing process carries the evidence.
## Where Do Swiss Supervisors and Legislators Stand on AI Governance?
In Supervisory Notice 08/2024, FINMA does not call for a standalone AI governance structure but for the extension of existing governance, risk management and control systems, while the Federal Council is moving towards sector-specific AI regulation.
FINMA bases its [Supervisory Notice 08/2024](https://www.finma.ch/en/news/2024/12/20241218-mm-finma-am-08-24/) on findings from ongoing supervisory activity and states that most financial institutions are still at an early stage of development. Every supervised institution must reconsider the effect of AI use on its risk profile and adapt its governance, risk management and control system to the applicable regulatory framework. As Switzerland has no AI-specific legislation, FINMA follows a risk-based approach that covers operational, data, IT and cyber risk as well as legal and reputational aspects.
The Federal Council has decided to ratify the Council of Europe’s AI Convention and to adapt Swiss law accordingly; Federal Councillor Albert Rösti signed the Convention on behalf of Switzerland. The Federal Department of Justice and Police, together with the Federal Department of the Environment, Transport, Energy and Communications and the Federal Department of Foreign Affairs, is to prepare a consultation draft by the end of 2026 setting out measures on transparency, data protection, non-discrimination and oversight. Legislative amendments are intended to be as sector-specific as possible, while any cross-sector rules should be limited to core areas touching on fundamental rights. The current maturity level of institutions is described in detail in FINMA’s survey on the use of artificial intelligence.
## How Can This Integration Be Implemented in Practice?
The first step is to take stock of the AI applications already in use and map them to existing risk registers, controls and data protection processes.
The function responsible for GRC should complete this mapping within the current planning cycle before deciding on a separate AI governance function. Only after that can it be assessed which AI-specific gaps require additional expertise, for example around data quality under Article 10 of the AI Act or the explainability of model decisions. In most cases, these gaps can be closed through new roles and review steps within the existing structure, rather than through an additional silo.
A separate AI governance function is worthwhile only once the existing GRC structure demonstrably cannot cover the AI-specific requirements.
Related
### A shared data foundation for AI risk
AI GRC maps AI risk into the same risk register already used for other risk types. It links requirements from the AI Act to existing controls and evidence.
[AI GRC ](https://swissgrc.com/fr/ai-grc/)
For practice
## Key points
- Article 9(10) of the AI Act explicitly permits integrating AI risk management into existing processes.
- ISO/IEC 42001 can be certified as a standalone system or docked onto existing management systems.
- FINMA requires supervised institutions to extend existing governance, risk management and control systems rather than build a new structure.
- The Federal Council is moving towards sector-specific AI regulation, with a consultation draft from the Federal Department of Justice and Police due by the end of 2026.
- Taking stock of the AI applications already in use is the practical first step before any structural decision.
FAQ
## Frequently asked questions
Does a company need to set up a new department for AI governance?No. The AI Act, ISO/IEC 42001 and FINMA Supervisory Notice 08/2024 all point towards integrating AI governance into existing governance, risk management and control structures. A standalone AI governance function is worthwhile only once the existing GRC structure demonstrably cannot cover the AI-specific requirements.
What does Article 9 of the AI Act require regarding risk management for high-risk AI systems?Article 9 of the AI Act requires a continuous risk management system throughout the lifecycle of high-risk AI systems. Under Article 9(10), providers already subject to risk management obligations under other Union law may integrate these aspects into existing processes rather than building a parallel system.
Can ISO/IEC 42001 be certified on its own, or only as an addition to existing systems?Like other management system standards, ISO/IEC 42001:2023 is designed as a system that can be certified on its own, but it can equally be docked onto existing GRC structures, for example an existing information security or quality management system. This dual compatibility mirrors the integration logic of the AI Act.
What role does FINMA Supervisory Notice 08/2024 play for Swiss financial institutions?FINMA does not require a standalone AI governance structure but the extension of existing governance, risk management and control systems. Every supervised institution must reconsider the effect of AI use on its risk profile and follow a risk-based approach, since Switzerland has no AI-specific legislation.
What is the first practical step in embedding AI governance into GRC?The first step is to take stock of the AI applications already in use and map them to existing risk registers, controls and data protection processes. Only after that can it be assessed which AI-specific gaps require additional expertise, before deciding on a separate AI governance function.
Sources
1. [Article 9, risk management system for high-risk AI systems](https://ai-act-service-desk.ec.europa.eu/en/ai-act/article-9)AI Act Service Desk, European Commission
2. [Supervisory Notice 08/2024 on governance and risk management in AI](https://www.finma.ch/en/news/2024/12/20241218-mm-finma-am-08-24/)FINMA
**Catégories:** Regulation & Supervision
**Étiquettes:** AI Act risk management, ISO/IEC 42001, FINMA Supervisory Notice 08/2024, AI governance structure, GRC integration
---
### [The Governance Lag: A New Metric for the Risk Register](https://swissgrc.com/fr/governance-lag-metric-risk-register/)
**Published:** août 31, 2026
**Author:** superadmin
**Excerpt:** The governance lag measures, in days, how long an AI application operates without oversight between its initial deployment and its full onboarding into the governance structure. As an additional field in the risk register, it can be combined with likelihood and impact: the longer the gap, the higher the priority. The criticality of the data involved determines thresholds and escalation levels.
**Content:**
Discussions of shadow AI often go no further than describing a gap between AI deployment and AI governance. For a risk register, a description is not enough. The gap only becomes relevant once it can be measured, compared and prioritised as a period of time. The governance lag does exactly that: it records how many days pass between the first use of an AI application and its full onboarding into the governance structure.
In short
The governance lag measures, in days, how long an AI application operates without oversight between its initial deployment and its full onboarding into the governance structure. As an additional field in the risk register, it can be combined with likelihood and impact: the longer the gap, the higher the priority. The criticality of the data involved determines thresholds and escalation levels.
Contents
1. [What exactly does the governance lag measure?](#a1-what-exactly-does-the-governance-lag-mea)
2. [How is the governance lag calculated?](#a2-how-is-the-governance-lag-calculated)
3. [How does the governance lag help prioritise risks?](#a3-how-does-the-governance-lag-help-priorit)
4. [What thresholds and escalation levels make sense?](#a4-what-thresholds-and-escalation-levels-ma)
5. [How does the governance lag become part of existing GRC processes?](#a5-how-does-the-governance-lag-become-part-)
4.99USD million
average global cost of a data breach
IBM Cost of a Data Breach Report 2026
25%
share of malicious attacks that were already AI-powered
IBM Cost of a Data Breach Report 2026
63%
organisations without adequate AI governance policies
IBM Cost of a Data Breach Report, previous year edition
## What exactly does the governance lag measure?
The governance lag measures the time span between the first productive use of an AI application and the point at which it is fully captured in the governance structure: inventoried, risk-assessed, assigned an owner and covered by controls.
This definition turns a soft description into a hard figure. Instead of stating that an AI application is not yet fully governed, it becomes possible to state for how many days it has already been in use without oversight. This precision matters because risk can materialise precisely during that time span.
The IBM Cost of a Data Breach Report 2026 shows that the average global cost of a data breach has risen to USD 4.99 million, 12 percent higher than the previous year. A quarter of malicious attacks were already AI-powered, with an average cost of around USD 6 million per incident. These figures show that the duration of the governance gap is directly linked to the potential damage.
## How is the governance lag calculated?
The governance lag is the difference between the date an AI application was first deployed and the date it was fully onboarded into governance, measured in days per application.
The start date can be derived from procurement records, activation logs for SaaS features, API access logs or reports from business units. The end date is reached once four conditions are met: an entry in the AI inventory, a completed risk assessment, a named owner and implemented controls.
Much like building a supplier register, governing AI risk begins with a complete inventory, not with assessing individual cases one by one. Without this inventory, the governance lag remains invisible, even though it exists in practice.
- Start date: first demonstrable use of the AI application
- End date: completed governance onboarding with owner and controls
- Metric: difference in days, calculated per AI application
- Aggregation: median and outliers across the entire AI inventory
Oversight und Monitoring mit fälligen Assessments, Audits, Modellvalidierungen und vollständiger Historie in der SwissGRC Plattform## How does the governance lag help prioritise risks?
The governance lag acts as an additional dimension alongside likelihood and impact: the longer the gap, the higher the priority, regardless of the originally estimated likelihood.
In a classic risk matrix, priority is derived from likelihood and impact. The governance lag adds the duration of the control gap to that matrix. An AI application with medium impact potential that has been running outside governance for an extended period can therefore be prioritised above a newly introduced application with a similar risk profile.
A tiered approach based on the criticality of the data and systems involved is advisable. AI applications with access to particularly sensitive data should be given a shorter permissible lag before an escalation is triggered than applications with a low risk profile.
The governance lag does not prioritise based on the intent behind an AI application, but on the actual duration of its exposure without oversight.
## What thresholds and escalation levels make sense?
Organisations set their own thresholds based on the criticality of the respective AI application, with clearly defined escalation levels once the governance lag exceeds that threshold.
A workable structure distinguishes three levels. Applications within the permissible period are considered in progress. Exceeding it triggers escalation to the responsible risk owner; a significant overrun triggers escalation to executive management, along with a decision on whether to restrict the application until it is fully onboarded into governance.
FINMA’s assessment of artificial intelligence describes AI applications as widespread, while the associated governance is, in many places, still described as having room for improvement.
## How does the governance lag become part of existing GRC processes?
The governance lag can be maintained as an additional field in the risk register and integrated into the regular reporting cycles of risk management, rather than remaining an isolated, separate AI metric.
An additional data field per AI application is sufficient for this: the date of first deployment, the date of governance onboarding, the resulting lag in days, and the associated escalation status. These fields fit into a logic where risk management serves the achievement of objectives, not the maintenance of a register as an end in itself.
Third-party risk management, information security and compliance draw on the same field whenever an AI application was introduced through a supplier or an existing application. As a first step, risk owners should backfill the date of first deployment for every application recorded in the AI inventory and compare it with the date of governance onboarding. This difference can be introduced as a new metric at the next regular risk meeting, before further AI applications are added unnoticed.
Related
### Making the governance lag visible and closing it
The AI GRC solution records first deployment, risk assessment and governance onboarding for each AI application. It makes the governance lag visible and traceable in the risk register.
[AI GRC ](https://swissgrc.com/fr/ai-grc/)
For practice
## Key points
- The governance lag measures the difference, in days, between an AI application’s first deployment and its full governance onboarding.
- The longer the lag, the higher the priority in the risk register, regardless of the original risk estimate.
- Thresholds and escalation levels depend on the criticality of the data and systems processed.
- The governance lag can be integrated into existing risk register processes as an additional field, without building separate AI structures.
- A complete AI inventory is a precondition for calculating the governance lag at all.
FAQ
## Frequently asked questions
What is the governance lag in AI applications?The governance lag measures, in days, the time span between the first productive use of an AI application and its full onboarding into the governance structure, that is, inventorying, risk assessment, owner assignment and controls. It turns the often only vaguely described gap between AI deployment and AI governance into a concrete, comparable metric that can be used in the risk register.
Where does the data for the governance lag's start date come from?The start date can be derived from procurement records, activation logs for SaaS features, API access logs or reports from business units. Only with a complete AI inventory are these data sources captured systematically, so that the governance lag can be reliably calculated for each application.
Why can an AI application with a long governance lag be prioritised above a new one with a similar risk profile?A long governance lag means that an AI application has been running for an extended period without an owner, risk assessment or controls. This time span increases its priority in the risk register regardless of the originally estimated likelihood, since risks can materialise precisely during periods without oversight.
What do the thresholds for the governance lag depend on?Organisations set their own thresholds based on the criticality of the data and systems processed. AI applications with access to particularly sensitive data are given a shorter permissible lag before an escalation to the risk owner or executive management is triggered.
What precondition is needed to calculate the governance lag at all?A complete AI inventory is a precondition, since without this register the governance lag remains invisible, even though it exists in practice. Only once the first deployment and governance onboarding of every AI application are documented can the difference in days be reliably calculated and aggregated.
**Catégories:** Regulation & Supervision
**Étiquettes:** Escalation Levels, Shadow AI, AI Inventory, AI Governance, Risk Register Metric
---
### [Third-Party Risk Governance: From Vendor Register to Steering](https://swissgrc.com/fr/third-party-risk-governance-from-vendor-register-to-steering/)
**Published:** août 29, 2026
**Author:** superadmin
**Excerpt:** Effective governance of third-party risk needs more than a vendor register: it combines structured register data on criticality and substitutability with a continuously updated risk assessment and regular reporting to the governing body. DORA, the EBA guidelines on outsourcing and FINMA supervision require this structure, because a register alone does not remedy the deficiencies in service provider management that supervisory authorities have identified.
**Content:**
Third-party risk management today requires more than a well-maintained vendor list. Supervisory authorities in the EU and Switzerland demand structured registers, a continuously updated risk assessment and regular reporting to the governing body. The first-ever designation of critical ICT third-party providers in November 2025 shows that systemic risks are now being derived from this register data. For GRC functions, this marks the shift from recording to steering, supported by metrics, defined responsibilities and escalation paths.
In short
Effective governance of third-party risk needs more than a vendor register: it combines structured register data on criticality and substitutability with a continuously updated risk assessment and regular reporting to the governing body. DORA, the EBA guidelines on outsourcing and FINMA supervision require this structure, because a register alone does not remedy the deficiencies in service provider management that supervisory authorities have identified.
Contents
1. [What do supervisory authorities require beyond register maintenance?](#a1-what-do-supervisory-authorities-require-)
2. [What does the designation of critical ICT third-party providers in November 2025 show?](#a2-what-does-the-designation-of-critical-ic)
3. [What deficiencies does FINMA identify in service provider management?](#a3-what-deficiencies-does-finma-identify-in)
4. [What structure does effective governance of third-party risk require?](#a4-what-structure-does-effective-governance)
5. [What first step leads from list to steering?](#a5-what-first-step-leads-from-list-to-steer)
19providers
Critical ICT third-party providers designated for the first time by EBA, EIOPA and ESMA under DORA
European Banking Authority, press release, 18 November 2025
50%
Share of successful cyberattacks on service providers of financial institutions, up from around 25 percent
FINMA, Supervisory Communication 03/2024, 7 June 2024
1/3
Share of cyberattacks reported to FINMA that occur indirectly via third parties
FINMA Risk Monitor 2024, cited in Handelszeitung Insurance, 19 February 2025
## What do supervisory authorities require beyond register maintenance?
Under Article 28(3) of the [DORA Regulation](https://www.fma.gv.at/en/cross-sectoral-topics/dora/dora-managing-of-ict-third-party-risk/), financial entities must maintain a register of all contractual arrangements with ICT third-party providers and report it to the competent authority.
Beyond the register, DORA requires a strategy for ICT third-party risk, due diligence assessments before the use of ICT services, and clear requirements on contract content and exit strategies. The European Banking Authority (EBA) additionally obliges institutions, in its guidelines on outsourcing published in 2019, to inform the governing body regularly about identified risks and to keep the risk assessment continuously updated. These requirements presuppose a structure that goes beyond a plain list of names: data fields on criticality, contract duration, substitutability and concentration must be maintained and evaluated.
## What does the designation of critical ICT third-party providers in November 2025 show?
On 18 November 2025, the European Supervisory Authorities EBA, EIOPA and ESMA designated 19 [critical ICT third-party providers](https://www.eba.europa.eu/publications-and-media/press-releases/european-supervisory-authorities-designate-critical-ict-third-party-providers-under-digital) under DORA for the first time, deriving systemic concentration risks from reported register data.
According to the European Insurance and Occupational Pensions Authority (EIOPA), the designation followed a multi-stage process: collection of data from the registers of financial entities, a criticality assessment based on systemic importance, the role played in critical functions and substitutability, and a right of the affected providers to be heard. For financial entities, this means that their own register data no longer serves internal oversight alone, but feeds directly into a supervisory risk analysis. The regulatory overlaps between EBA guidelines, DORA and MaRisk sharpen this requirement further.
## What deficiencies does FINMA identify in service provider management?
In Supervisory Communication 03/2024, FINMA identified significant deficiencies in service provider management, including missing inventories, incomplete controls and insufficient integration into the internal control system.
The communication is based on Article 29 paragraph 2 of the Financial Market Supervision Act, which governs the reporting obligation for cyberattacks and is in principle also relevant for small and medium-sized asset managers. FINMA also found that cyberattacks on service providers of supervised institutions were successful more often than average; the share of such successful attacks rose in subsequent years from around 25 to over 50 percent. Circular 2018/3 on outsourcing at banks and insurers had already aligned supervisory practice with a principles-based approach and left the materiality assessment of outsourcing arrangements more to the institutions’ own responsibility.
A loss of EUR 89 million at an ICT service provider illustrates how quickly gaps in controls can become financially material.
## What structure does effective governance of third-party risk require?
Effective governance combines a structured register with a continuously updated risk assessment and regular reporting to the governing body.
According to the FINMA Risk Monitor 2024, one third of the cyberattacks on financial institutions reported to FINMA occur indirectly via third parties, which underlines the importance of continuous rather than point-in-time observation.
A governance structure must define who assesses criticality, concentration and contractual risk, at what interval this assessment is updated, and which thresholds trigger escalation to executive management. The principle that risk management serves the achievement of objectives, not itself, applies directly to the governance of third-party risk.
## What first step leads from list to steering?
The first step is to extend the existing vendor register with fields on criticality and concentration, enabling a recurring assessment rather than a one-off recording exercise.
Those responsible for third-party risk management should determine, before the next review of the register, which metrics are reported regularly to executive management, for example the share of critical providers, open audit findings, or contracts without a documented exit strategy. Equally important is clarifying who within the organization is responsible for updating the risk assessment and at what interval this happens. Governance that answers these questions does not automatically satisfy every supervisory requirement, but it creates the basis on which such compliance becomes possible in the first place.
Related
### From list to resilient steering
The Third-Party Risk Management solution maps register, risk assessment and escalation paths within a single structure, and supports reporting to executive management with traceable data.
[Third-Party Risk Management ](https://swissgrc.com/fr/tprm-software/)
For practice
## Key points
- Extend the ICT third-party provider register with fields on criticality, substitutability and contract duration, as required by Art. 28(3) DORA.
- Establish a recurring risk assessment that is reported regularly to the governing body, as required by the EBA guidelines on outsourcing.
- Review internal service provider management against the gaps identified by FINMA: missing inventories, incomplete controls, insufficient integration into the internal control system.
- Define thresholds above which a third-party provider triggers escalation to executive management.
- Document exit strategies for critical contracts before a supervisory authority asks for them.
FAQ
## Frequently asked questions
What distinguishes a vendor register from effective third-party risk governance?A vendor register only records names and contracts. Effective governance extends this register with data fields on criticality, substitutability and concentration, links these to a continuously updated risk assessment, and ensures regular reporting to the governing body, as required by DORA and the EBA guidelines.
What does Article 28(3) DORA require for the ICT third-party provider register?Article 28(3) DORA obliges financial entities to maintain a register of all contractual arrangements with ICT third-party providers and to report it to the competent supervisory authority. Beyond this, DORA requires a strategy for ICT third-party risk, due diligence assessments before contract conclusion, and clear requirements on contract content and exit strategies.
How many critical ICT third-party providers were designated under DORA in November 2025?On 18 November 2025, the European Supervisory Authorities EBA, EIOPA and ESMA designated 19 critical ICT third-party providers under DORA for the first time. The designation was based on register data from financial entities, from which a criticality assessment was derived using systemic importance, role in critical functions, and substitutability.
What deficiencies did FINMA identify in service provider management?In Supervisory Communication 03/2024, FINMA identified missing inventories, incomplete controls and insufficient integration of service provider management into the internal control system. It also found that the share of successful cyberattacks on service providers of supervised institutions rose from around 25 to over 50 percent.
What share of reported cyberattacks on financial institutions occurs via third parties?According to the FINMA Risk Monitor 2024, one third of the cyberattacks on financial institutions reported to FINMA occur indirectly via third parties. This figure underlines why continuous rather than point-in-time monitoring of third-party risk is necessary.
Sources
1. [DORA – Managing of ICT third-party risk](https://www.fma.gv.at/en/cross-sectoral-topics/dora/dora-managing-of-ict-third-party-risk/)Austrian Financial Market Authority (FMA)
2. [Designation of critical ICT third-party providers](https://www.eba.europa.eu/publications-and-media/press-releases/european-supervisory-authorities-designate-critical-ict-third-party-providers-under-digital)European Banking Authority
3. [Designation of critical ICT third-party providers](https://www.eiopa.europa.eu/european-supervisory-authorities-designate-critical-ict-third-party-providers-under-digital-2025-11-18_en)European Insurance and Occupational Pensions Authority (EIOPA)
4. [FINMA publishes outsourcing circular](https://www.finma.ch/de/news/2017/12/20171205-mm-rs-outsourcing/)FINMA
5. [Guidelines on outsourcing arrangements EBA/GL/2019/02](https://www.eba.europa.eu/documents/10180/2761380/EBA+revised+Guidelines+on+outsourcing_DE.pdf/5546a705-bff2-43eb-b382-e5c7bed3a2bc)European Banking Authority
6. [Article on the FINMA Risk Monitor 2024](https://www.handelszeitung.ch/insurance/it-auslagerungen-erhohen-cyberrisiken-drastisch-792082)Handelszeitung Insurance
**Catégories:** Regulation & Supervision
**Étiquettes:** Third-Party Risk Management, DORA third-party risk, ICT third-party provider register, EBA guidelines on outsourcing, FINMA service provider management
---
### [Basel III: Three International Deadlines by 2027 at a Glance](https://swissgrc.com/fr/basel-iii-deadlines-2026-2027-international/)
**Published:** août 29, 2026
**Author:** superadmin
**Excerpt:** Switzerland completed its Basel III implementation on 1 January 2025, but institutions with international business face diverging deadlines abroad: the United States is consulting on a new Basel III proposal until 18 June 2026, the United Kingdom launches Basel 3.1 on 1 January 2027, and the EU adjusts its market risk framework from the same date for three years.
**Content:**
The Federal Council decided on the final implementation of Basel III in Switzerland as of 1 January 2025, together with the FINMA implementing provisions. For institutions with purely domestic business, their own implementation is therefore complete. Institutions active in the United States, the United Kingdom or the EU, however, must track three different deadline calendars from 2026 onward, and these calendars diverge considerably. What matters here is not an institution’s own capital ratio, but its ability to remain compatible with business partners and supervisory authorities abroad.
In short
Switzerland completed its Basel III implementation on 1 January 2025, but institutions with international business face diverging deadlines abroad: the United States is consulting on a new Basel III proposal until 18 June 2026, the United Kingdom launches Basel 3.1 on 1 January 2027, and the EU adjusts its market risk framework from the same date for three years.
Contents
1. [Why is the Swiss Basel III implementation already considered complete?](#a1-why-is-the-swiss-basel-iii-implementatio)
2. [What changes with the new US Basel III proposal?](#a2-what-changes-with-the-new-us-basel-iii-p)
3. [When does Basel 3.1 take effect in the United Kingdom?](#a3-when-does-basel-3-1-take-effect-in-the-u)
4. [How is the EU handling the Fundamental Review of the Trading Book?](#a4-how-is-the-eu-handling-the-fundamental-r)
5. [What does this mean for Swiss institutions with international business?](#a5-what-does-this-mean-for-swiss-institutio)
## Why is the Swiss Basel III implementation already considered complete?
The Federal Council brought the revised Capital Adequacy Ordinance and the FINMA implementing provisions on the final Basel III standards into force on 1 January 2025. For Swiss institutions, the substantive implementation is therefore complete.
The Basel III finalisation in Switzerland covered, among other things, the revised standardised approach to credit risk and the output floor. The Basel Committee on Banking Supervision reviews, through its Regulatory Consistency Assessment Programme, how individual jurisdictions adopt and apply the final standards. Such a consistency framework, however, does nothing to change the fact that actual implementation dates are set differently from country to country. For an institution with business in the United States, the United Kingdom or the EU, monitoring these dates therefore remains necessary even after its own implementation has been completed.
## What changes with the new US Basel III proposal?
The US supervisory authorities, the Federal Reserve, the OCC and the FDIC, withdrew the original 2023 Basel III endgame proposal on 19 March 2026 and replaced it with a new, more capital-neutral Basel III proposal.
A key element of the revised proposal is the removal of the so-called dual-stack framework, under which banks previously had to calculate their capital ratios using both the standardised approach and internal models. The comment period on the three new proposals runs until 18 June 2026. The Federal Reserve Board approved the proposals by a vote of 6 to 1, with Governor Michael Barr as the sole dissenting member. A date for the final US rule to take effect has not yet been set following the conclusion of the consultation.
## When does Basel 3.1 take effect in the United Kingdom?
The UK Prudential Regulation Authority confirmed on 20 January 2026, with the final [Policy Statement PS1/26](https://www.bankofengland.co.uk/prudential-regulation/publication/2026/january/implementation-of-the-basel-3-1-final-rules-policy-statement), that Basel 3.1 will take effect on 1 January 2027, one year later than originally planned.
The internal models approach for market risk under the Fundamental Review of the Trading Book is being delayed further, to 1 January 2028. The PRA had already announced the one-year delay in consultation with HM Treasury, in order to allow more clarity on implementation plans in the United States. During the transition phase from 2027, UK banks may continue to use existing IMA model approvals for trading book positions until FRTB-IMA is fully implemented in 2028.
## How is the EU handling the Fundamental Review of the Trading Book?
After two postponements, the EU has not deferred the application of the Fundamental Review of the Trading Book a third time, but has instead adopted targeted adjustments that will apply for three years from 1 January 2027.
The EU banking package CRR3/CRD6 already entered into force on 1 January 2025, and most Basel III requirements were implemented on schedule. Only the market risk framework was first postponed by the Commission to 2026 and then, through a further delegated act of 12 June 2025, to 2027, exhausting the two-year postponement permitted under the CRR3 mandate. The [new delegated act of 4 June 2026](https://finance.ec.europa.eu/news/eu-temporarily-amends-prudential-rules-banks-market-risk-2026-06-08_en) is subject to a three-month scrutiny period by the European Parliament and the Council, which can be extended by a further three months. The European Banking Authority has confirmed that its no-action letter on the boundary between the trading book and the banking book remains valid during this period as well.
## What does this mean for Swiss institutions with international business?
Institutions with US, UK or EU business must track three separate deadline calendars from 2026 onward, even though their own implementation in Switzerland has already been completed.
Institutions active in the United Kingdom should build 1 January 2027 for Basel 3.1 and 1 January 2028 for FRTB-IMA into their own planning. Institutions subject to reporting obligations in the EU should track the effect of the delegated act from 1 January 2027 as well as its scrutiny by Parliament and Council. For US business, it remains open until the end of the comment period on 18 June 2026 in what form the new Basel III proposal will be finalised.
A suitable first step is a monitoring plan per jurisdiction that names the responsible supervisory authority, the next deadline and the group entities affected. Such a plan fits into targeted risk management and makes capital planning traceable across jurisdictional boundaries.
For practice
## Key points
- The Swiss Basel III implementation has been complete since 1 January 2025, but this does not extend to foreign business units.
- Institutions with US business should track the comment period on the new Basel III proposal, running until 18 June 2026, and the subsequent finalisation.
- For UK business, 1 January 2027 for Basel 3.1 and 1 January 2028 for FRTB-IMA are the relevant dates.
- In the EU, an adjusted FRTB framework applies for three years from 1 January 2027, subject to scrutiny by Parliament and Council.
- A jurisdiction-specific monitoring plan helps track the three deadline calendars separately and transparently.
Sources
1. [Policy Statement PS1/26 on the implementation of Basel 3.1](https://www.bankofengland.co.uk/prudential-regulation/publication/2026/january/implementation-of-the-basel-3-1-final-rules-policy-statement)Bank of England
2. [Delegated act on targeted FRTB adjustments](https://finance.ec.europa.eu/news/eu-temporarily-amends-prudential-rules-banks-market-risk-2026-06-08_en)European Commission
**Catégories:** Regulation & Supervision
**Étiquettes:** Fundamental Review of the Trading Book, US Basel III proposal, CRR3 CRD6, Capital Adequacy Ordinance, Basel 3.1
---
### [Risk management serves objectives, not itself](https://swissgrc.com/fr/risk-management-serves-objectives-not-itself/)
**Published:** août 20, 2026
**Author:** superadmin
**Excerpt:** Risk management is not justified by the completeness of a register, but by whether it helps the board of directors make better decisions under uncertainty. Anyone who wants to demonstrate this value to the board must link risk information to concrete decisions and objectives rather than to reporting duties. Recent examples, such as the warning issued by the European financial supervisory authorities on AI-related ICT risks, illustrate how governance is meant to create decision-making capability rather than documentation.
**Content:**
In the boardroom, risk management is easily misunderstood as a compliance exercise that fills registers and produces reports. GRC analyst Michael Rasmussen of GRC 20/20 Research reminds us that risk management only fulfils its purpose when it improves decisions and makes objectives achievable under uncertainty. For the board, a different yardstick than completeness is therefore worthwhile: how often a piece of risk information has actually led to a decision.
In short
Risk management is not justified by the completeness of a register, but by whether it helps the board of directors make better decisions under uncertainty. Anyone who wants to demonstrate this value to the board must link risk information to concrete decisions and objectives rather than to reporting duties. Recent examples, such as the warning issued by the European financial supervisory authorities on AI-related ICT risks, illustrate how governance is meant to create decision-making capability rather than documentation.
Contents
1. [What is the purpose of risk management in an organisation?](#a1-what-is-the-purpose-of-risk-management-i)
2. [How does the board recognise whether risk management is a means or an end in itself?](#a2-how-does-the-board-recognise-whether-ris)
3. [What does the example of AI risks in the European financial sector show?](#a3-what-does-the-example-of-ai-risks-in-the)
4. [How can this logic be conveyed to the board in practice?](#a4-how-can-this-logic-be-conveyed-to-the-bo)
5. [What is the first step for the next board meeting?](#a5-what-is-the-first-step-for-the-next-boar)
## What is the purpose of risk management in an organisation?
Risk management serves to improve decisions under uncertainty and make the achievement of corporate objectives more reliable, not to maintain a register.
Michael Rasmussen proposes a simple test for risk owners and boards of directors. What matters is whether registers, controls, assessments, analytics, models, reporting and technology actually help make better decisions and reliably achieve objectives under uncertainty. If the answer is negative, Rasmussen argues, the question arises why the effort is being made at all.
Administrative duties around risk management do not disappear as a result. Supervisory authorities expect reports, boards need information, policies must be maintained, and controls and assessments must be documented. The problem arises when this administration replaces actual steering rather than supporting it.
## How does the board recognise whether risk management is a means or an end in itself?
The board recognises the difference by whether a risk report leads to a traceable decision or merely documents what is already known.
Rasmussen describes a common pattern: organisations can become extremely efficient at producing risk information that nobody uses for decisions. For the board, this translates into a concrete test question for every risk agenda item.
A concise set of criteria that the board can apply to every risk submission is helpful. The Chief Risk Officers Outlook 2024 shows that many risk functions are working on exactly this link between reporting and decision-making.
- Is the submission linked to an upcoming decision for which it is actually used?
- Would a missing metric actually prevent a concrete action, or would it only leave a report incomplete?
- Does the discussion in the board lead to an adjustment of strategy, limits or resources?
## What does the example of AI risks in the European financial sector show?
The European financial supervisory authorities are not demanding additional documentation for its own sake, but governance structures that enable institutions to actually respond to new risks.
The European supervisory authorities EBA, EIOPA and ESMA call, in a joint statement, for a cross-sectoral, risk-based and consistent supervisory approach to mitigating the ICT risks posed by frontier AI models. The focus is not the reporting itself, but the ability of institutions to act.
The statement emphasises that financial institutions should have robust governance and risk management structures in place to effectively support the management and mitigation of these risks. This is the same logic that should apply at board level: structures exist so that decisions can be made in an actual event, not so that a file is complete.
## How can this logic be conveyed to the board in practice?
It is most effective to present risk information in the language of objectives, limits and courses of action rather than in the language of controls and percentages.
Instead of presenting a heatmap with many cells, it is worth asking which three risks could actually endanger the current strategy and what course of action the board has in response. This shortens the agenda item but sharpens its decision relevance.
The Global Risks Report 2026 analysis shows, by way of example, how global risk trends can be broken down into a few questions relevant to an individual company. The board should demand this kind of distillation from the risk function, rather than mistaking it for completeness.
A risk report that does not lead to any decision has failed its purpose, even if it was delivered complete and on time.
## What is the first step for the next board meeting?
The first step is a one-off review of the last risk agenda items for their decision impact, carried out by the risk function and signed off by the chair of the board.
The risk owner checks, ahead of the next ordinary meeting, which of the last five risk agenda items led to a documented decision and which were merely noted. The result is presented to the chair of the board as a brief overview.
On this basis, the format of the next risk reporting can be adjusted in a targeted way: less completeness, more decision relevance. An overview of current regulatory developments supports this prioritisation, for instance through the Swiss GRC news overview.
For practice
## Key points
- Check every risk agenda item for whether it is linked to a specific, upcoming decision.
- Reduce board reports to the risks that actually endanger the current strategy.
- Treat administrative duties such as notifications and documentation as support for steering, not as its replacement.
- Use regulatory examples such as the statement by EBA, EIOPA and ESMA to explain governance as decision-making capability rather than formality.
- Have the risk function document, ahead of the next meeting, which previous submissions led to a decision.
FAQ
## Frequently asked questions
How can you tell that a risk register serves documentation only?A risk register primarily serves documentation when reports are delivered complete and on time without leading to a traceable decision in the board. Rasmussen points out that organisations can efficiently produce risk information that nobody actually uses for decisions. That is the real warning sign.
Which criteria should the board apply to risk submissions?The board should check whether a submission is linked to an upcoming decision, whether a missing metric would actually prevent an action, and whether the discussion leads to an adjustment of strategy, limits or resources. These three questions replace completeness as the yardstick for the quality of a risk submission.
What do EBA, EIOPA and ESMA demand from financial institutions regarding AI risks?The three European supervisory authorities call for a cross-sectoral, risk-based and consistent supervisory approach to mitigating ICT risks posed by frontier AI models. Financial institutions should have robust governance and risk management structures in place that effectively support the management and mitigation of these risks, rather than merely generating additional documentation.
How does a decision-relevant risk report differ from a plain status update?A decision-relevant risk report names a small number of risks that actually endanger the current strategy and shows concrete courses of action for the board. A plain status update, by contrast, lists many metrics or a complete heatmap without any resulting adjustment to strategy, limits or resources.
What first step can the risk function take before the next meeting?The risk function can check, ahead of the next ordinary meeting, which of the last five risk agenda items led to a documented decision and which were merely noted. The result is presented to the chair of the board as a brief overview and serves as the basis for a decision-oriented reporting format.
Sources
1. [The Prime Directive of Risk Management](https://grc2020.com/2026/08/19/the-prime-directive-of-risk-management-risk-is-our-business-but-decisions-and-objectives-are-the-mission/)GRC 20/20 Research
2. [Joint statement on ICT risks from frontier AI models](https://www.eba.europa.eu/publications-and-media/press-releases/eba-eiopa-and-esma-call-enhanced-governance-and-consistent-supervision-mitigate-ict-risks-frontier)European Banking Authority
**Catégories:** Risk & Decision Making
**Étiquettes:** ICT risks, risk report, board of directors, risk information, governance
---
### [NIS2 Registration Gap: What It Reveals About Scope Uncertainty](https://swissgrc.com/fr/nis2-registration-gap-scope-uncertainty/)
**Published:** août 21, 2026
**Author:** superadmin
**Excerpt:** The gap of roughly 10,000 companies between the number of NIS2-affected entities expected by the German government and the number actually registered with the BSI shows that determining one's own applicability is a demanding process requiring documentation. Companies should make their sector and threshold assessment traceable in writing, rather than relying on a gut-feeling judgement.
**Content:**
The German government originally assumed that almost 30,000 companies would have to register as critical infrastructure under NIS2. In fact, around 10,000 notifications are still missing relative to that expectation, as Golem reports. The government itself does not describe this as a gap in the strict sense. This assessment deserves a closer look, because it says something about the nature of scope determination itself.
In short
The gap of roughly 10,000 companies between the number of NIS2-affected entities expected by the German government and the number actually registered with the BSI shows that determining one's own applicability is a demanding process requiring documentation. Companies should make their sector and threshold assessment traceable in writing, rather than relying on a gut-feeling judgement.
Contents
1. [How large is the gap between expected and registered NIS2-affected entities?](#a1-how-large-is-the-gap-between-expected-an)
2. [Why can companies not simply read off whether they are affected?](#a2-why-can-companies-not-simply-read-off-wh)
3. [What does this mean for the quality of a company's own scope assessment?](#a3-what-does-this-mean-for-the-quality-of-a)
4. [What does this mean for companies outside Germany?](#a4-what-does-this-mean-for-companies-outsid)
5. [How can companies concretely improve their own scope assessment?](#a5-how-can-companies-concretely-improve-the)
29'500entities
NIS2-affected entities expected by the German government, based on a calculation by the Federal Statistical Office
it-daily.net, NIS2: Nach Nachfrist weiter zu wenig Registrierungen
10'000companies
gap between expected and actually registered entities
it-daily.net, NIS2: Nach Nachfrist weiter zu wenig Registrierungen
18sectors
sectors relevant to NIS2 classification under the annexes of the BSIG
mars-solutions.de, NIS-2-Registrierung: Frist abgelaufen, Lücke bleibt
## How large is the gap between expected and registered NIS2-affected entities?
The expectation of around 29,500 entities subject to registration was based on a calculation by the Federal Statistical Office. The actual number of notifications remained well below that figure.
The expectation of 29,500 affected entities was based on a calculation by the Federal Statistical Office (Statistisches Bundesamt), which the German government relied on when passing the NIS2 Implementation Act. Even after a granted grace period, the gap persisted. Around 10,000 registrations are currently missing relative to the forecast, after only about 11,500 operators had registered properly by the originally set deadline.
It is remarkable how the government frames this gap: not as evidence of systematic non-registration, but as an open question of whether the original estimate itself was set too high. This uncertainty on the statistical side mirrors an uncertainty that also exists on the corporate side.
## Why can companies not simply read off whether they are affected?
NIS2 applicability results from a combination of sector affiliation and size threshold, which each company must assess and document itself, without any prior notification from the authorities.
Applicability results from two criteria that must both be met: sector affiliation and company size, whereby the relevant annexes list 18 sectors, including energy, transport, health, water, digital infrastructure, IT services, chemicals, food and manufacturing. There is no external assignment by an authority. Affected entities must identify themselves; there are no official notices and no request from an authority.
The association of municipal utilities states the cause clearly: the main reason for the existing registration gap lies in the complexity of the applicability assessment. Where self-assessment without a feedback loop forms the basis, the quality of the internal assessment methodology becomes the decisive factor.
## What does this mean for the quality of a company's own scope assessment?
A one-off, informal assessment is not sufficient, because sector classification, group structures and thresholds can change over time and must be documented in a traceable way.
Experience from Germany shows that even companies with compliance resources can misjudge the classification, or simply overlook that part of their own activity falls into a regulated sector. This affects not only companies with an obvious link to critical infrastructure, but also suppliers and service providers whose classification only arises through chain relationships. A company that carries out its applicability assessment only once, without renewing it at every relevant change, risks quietly growing out of scope or quietly growing into it.
For the GRC function, this means that scope determination itself should be treated as a control object, with clear responsibilities and recurring review. The article « Rethinking cyber resilience in the context of NIS2 » describes how this requirement can be embedded into an existing resilience concept.
## What does this mean for companies outside Germany?
Swiss companies with subsidiaries, branches or significant customer relationships in the EU should also check whether NIS2 applicability arises through this connection.
The registration gap is a German phenomenon, but the underlying problem of scope determination is not. Each EU member state implements NIS2 with its own deadlines and procedures, which means additional assessment steps for companies operating across borders. The review « NIS2 resolution in the Bundestag: pressure to act for companies » outlines the consequences arising from the German implementation for cross-border business relationships.
For Switzerland itself, the discussion around a separate cyber resilience law is running in parallel, with its own systematics. The article « Federal Council announces new cyber resilience law » describes the current status of this initiative.
## How can companies concretely improve their own scope assessment?
The first step is a written, documented sector and threshold analysis, approved by executive management and updated at every relevant structural change.
The analysis should record which activity is assigned to which sector, which size indicators were used, and who is responsible for the assessment. This documentation serves not only internal clarity but also as evidence towards supervisory authorities and business partners, who increasingly demand proof themselves. The article « ISMS: people, processes and technology are decisive » shows how such an assessment can be integrated into an existing management system.
The compliance or risk officer should complete the scope analysis before the next management review of the information security management system and submit it to the person responsible for governance for approval. This is a manageable, verifiable first step that can be implemented regardless of company size.
For practice
## Key points
- The gap between expected and registered NIS2-affected entities points mainly to methodological uncertainty in scope determination, not necessarily to widespread refusal.
- Sector affiliation and size threshold must be assessed together, without any authority notifying the classification in advance.
- A one-off assessment is not enough, because group structures, fields of activity and key figures change over time.
- Swiss companies with EU exposure should assess their own applicability independently of the German discussion.
- A written, documented scope analysis approved by executive management is the verifiable first step.
FAQ
## Frequently asked questions
What is the NIS2 registration gap?The German government expected around 29,500 companies to be subject to NIS2 registration, based on a calculation by the Federal Statistical Office. By the original deadline, however, only around 11,500 operators had registered, and around 10,000 notifications are still missing relative to the forecast today. The government does not treat this as proof of non-registration, but also as a possible overestimation of the original figure.
Which criteria determine whether a company is affected by NIS2?Applicability results from two criteria that must both be met: affiliation with one of the 18 listed sectors, such as energy, transport, health or IT services, and reaching certain company size thresholds. There is no external classification by an authority; companies must identify themselves.
Do Swiss companies need to concern themselves with NIS2?NIS2 is EU law that directly applies only to companies within member states. Swiss companies with subsidiaries, branches or significant customer relationships in the EU should nonetheless check whether applicability arises through this connection. For Switzerland itself, a separate cyber resilience law is being discussed in parallel.
Why is a one-off assessment of NIS2 applicability not sufficient?Sector classification, group structures and thresholds can change over time, for example through growth, restructuring or new business lines. A company that carries out the applicability assessment only once risks unnoticed growing out of or into scope. The assessment should therefore be renewed and documented at every relevant change.
How should an NIS2 scope analysis be documented?The documentation should record which activity is assigned to which sector, which size indicators were used, and who is responsible for the assessment. It should be approved by executive management and updated at relevant structural changes. This documentation also serves as evidence towards authorities and business partners.
Sources
1. [NIS-2-regulierte Unternehmen](https://www.bsi.bund.de/DE/Themen/Regulierte-Wirtschaft/NIS-2-regulierte-Unternehmen/nis-2-regulierte-unternehmen_node.html)Bundesamt für Sicherheit in der Informationstechnik (BSI)
**Catégories:** Regulation & Supervision
**Étiquettes:** GRC scope analysis, NIS2 scope determination, sector and threshold assessment, NIS2 registration requirement, critical infrastructure NIS2
---
### [EUR 89 Million in Losses: What ICT Risk Controls Miss](https://swissgrc.com/fr/89-million-euro-loss-ict-risk-controls-dora/)
**Published:** août 21, 2026
**Author:** superadmin
**Excerpt:** A recent fraud report shows that social engineering attacks on wire transfers are rare but especially costly. The lesson for the control landscape: documented controls such as the four-eyes principle say nothing about whether they actually hold up under time pressure. Effectiveness can only be verified through realistic testing, not through process descriptions alone.
**Content:**
The Oesterreichische Nationalbank recorded total payment fraud of EUR 115.4 million for 2025, an increase of 17.6 percent over the previous year. Wire transfers accounted for only nine percent of fraud cases, yet caused around EUR 89 million, or 78 percent of total losses. Social engineering attacks, in which victims authorise the payment themselves, were responsible for 83 percent of these cases. For ICT risk controls under DORA, this holds a lesson that control documentation alone does not reveal.
In short
A recent fraud report shows that social engineering attacks on wire transfers are rare but especially costly. The lesson for the control landscape: documented controls such as the four-eyes principle say nothing about whether they actually hold up under time pressure. Effectiveness can only be verified through realistic testing, not through process descriptions alone.
Contents
1. [Why do so few wire transfer cases cause the largest share of losses?](#a1-why-do-so-few-wire-transfer-cases-cause-)
2. [What does social engineering have to do with DORA's ICT risk framework?](#a2-what-does-social-engineering-have-to-do-)
3. [Why does documentation fail to reveal a control gap?](#a3-why-does-documentation-fail-to-reveal-a-)
4. [Which specific control elements should be reviewed now?](#a4-which-specific-control-elements-should-b)
5. [What is the next step for one's own control landscape?](#a5-what-is-the-next-step-for-ones-own-contr)
89EUR million
Losses from fraudulent wire transfers in Austria in 2025
Oesterreichische Nationalbank, cited by Meinbezirk.at
83%
Share of wire transfer losses attributable to social engineering
Oesterreichische Nationalbank, cited by Meinbezirk.at
3,000EUR
Average loss per fraudulent wire transfer in 2025
Oesterreichische Nationalbank, cited by Leadersnet.at
## Why do so few wire transfer cases cause the largest share of losses?
Because the average loss per fraudulent wire transfer, at around EUR 3,000, far exceeds that of a card payment, and in individual cases exceeds one million euros.
According to the Oesterreichische Nationalbank, nine out of ten fraud cases involved card payments, with an average loss of around EUR 75 per case. For wire transfers, the average was around EUR 3,000, and in individual cases exceeded one million euros. Measured by transaction volume, Austria’s fraud rate for wire transfers, at 0.004 percent, is twice the EU average.
This distribution follows a pattern that is underrepresented in many risk registers: high frequency with low individual loss versus low frequency with high individual loss. Control catalogues calibrated primarily on case numbers tend to underestimate the second pattern, even though it accounts for the larger share of total losses.
## What does social engineering have to do with DORA's ICT risk framework?
DORA requires an independent ICT risk control function, but this function primarily oversees technical and procedural controls, not the moment at which an authorised person releases a payment themselves.
Under Article 6(4) of the DORA regulation, financial entities must ensure an appropriate level of independence for their ICT risk control function, implemented through a separation of risk management, control and audit functions following the three-lines-of-defence model, as explained by the Austrian Financial Market Authority (FMA).
Social engineering undermines this structure without formally breaching it: the person who releases the payment acts within their authority, deceived by a fabricated sense of urgency. As described in ‘ISMS: People, Processes and Technology are Decisive’, a technical control is only as effective as the behaviour of the person operating it in a real incident.
## Why does documentation fail to reveal a control gap?
Because a documented four-eyes principle looks complete in every audit file, but says nothing about whether it is actually observed under time pressure and a perceived sense of urgency.
A control register confirms the existence of a process step, not its effect in a concrete attack scenario. As the article ‘Risk Management Serves the Achievement of Objectives, Not Itself’ points out, a system fails its purpose when it looks complete on paper but has never been tested operationally under real conditions.
Only a targeted review shows whether a callback requirement for changed account details is actually observed, or whether exception approvals under time pressure quietly become the rule. This exact difference between documented and lived control often goes undetected in a standard audit.
## Which specific control elements should be reviewed now?
Three elements are most likely to show, in a real incident, whether the release chain holds: the callback channel, the threshold logic and the escalation path.
These three elements can be reviewed individually and therefore provide more reliable statements than a pure process description.
- Callback requirement: Is there an obligation to verify changed payment details through a second, independent channel, and is this obligation checked on a sample basis?
- Thresholds: Are wire transfers above a defined amount manually cross-checked, regardless of time of day or a fabricated sense of urgency?
- Escalation: Can employees stop a payment without this being treated as a breach of trust towards an apparent superior?
## What is the next step for one's own control landscape?
Internal audit should carry out a simulated social engineering test case for payment release in the next audit cycle, rather than limiting itself to confirming process documentation.
The idea behind ‘FINMA Supervisory Communication 05/2025 as a Wake-up Call for Resilience by Design’, building resilience into processes from the outset rather than reviewing it afterwards, applies directly to payment releases.
A concrete first step is a simulated CEO fraud test case in the next ICS review round, jointly owned by internal audit and the payments team, evaluating actual response times and escalation paths rather than just the process documentation.
For practice
## Key points
- A few cases with high individual losses cause the largest share of total wire transfer fraud losses, not the mass of small fraud cases.
- A documented ICT risk control function under DORA only covers social engineering if processes such as callbacks and escalation are regularly tested under realistic conditions.
- Internal audit should include effectiveness tests for payment releases, rather than pure documentation reviews, in the next audit cycle.
- Thresholds and callback requirements are only as robust as their actual enforcement under time pressure.
FAQ
## Frequently asked questions
How high was total payment fraud in Austria in 2025?The Oesterreichische Nationalbank recorded total losses of EUR 115.4 million for 2025, an increase of 17.6 percent over the previous year. Wire transfers accounted for only nine percent of cases, yet caused around EUR 89 million, or 78 percent of total losses.
What is the difference between the average loss in card fraud and wire transfer fraud?Card payments accounted for nine out of ten fraud cases, with an average loss of around EUR 75 per case. For wire transfers, the average was around EUR 3,000, and in individual cases exceeded one million euros, which is why a small number of cases cause the largest share of total losses.
Why does a documented four-eyes principle not reliably prevent social engineering?The person releasing the payment formally acts within their authority but is deceived by a fabricated sense of urgency. A control register only confirms the existence of the process step, not whether it is actually observed under time pressure in a concrete attack scenario.
What role should internal audit play in reviewing payment releases?Internal audit should carry out a simulated social engineering test case for payment release in the next audit cycle, together with the payments team, evaluating actual response times and escalation paths rather than merely confirming the process documentation.
Which three control elements show, in a real incident, whether a release chain holds?The decisive elements are the callback requirement for changed payment details via a second channel, the threshold logic for manual cross-checking above a defined amount, and an escalation path that allows employees to stop a payment without a breach of trust.
Sources
1. [DORA – ICT Risk Management](https://www.fma.gv.at/querschnittsthemen/dora/dora-ikt-risiko-management/)Austrian Financial Market Authority (FMA)
2. [OeNB Report: Payment Fraud Caused EUR 115 Million in Losses Last Year](https://www.meinbezirk.at/c-wirtschaft/zahlungsbetrug-verursachte-im-vorjahr-115-millionen-euro-schaden_a8857823)MeinBezirk.at
**Catégories:** Industry News
**Étiquettes:** social engineering wire transfer fraud, DORA ICT risk control function, four-eyes principle effectiveness, CEO fraud test case, payment fraud 2025
---
### [What the UBS fine shows about long-term supervisory review](https://swissgrc.com/fr/ubs-fine-long-term-supervisory-review-evidence-tracking/)
**Published:** août 24, 2026
**Author:** superadmin
**Excerpt:** The record fine of USD 125 million against UBS Financial Services shows that supervisory authorities do not require the promise of a measure, but its demonstrable implementation over years. Continuous, documented tracking of remediation measures with evidence of effectiveness, rather than a one-off promise, would have changed the path from the first fine in 2018 to the current sanction.
**Content:**
FinCEN imposed a fine of USD 125 million on UBS Financial Services Inc., the highest ever issued against a broker-dealer for violations of the Bank Secrecy Act. This followed a fine of USD 14.5 million in 2018 for the same weakness: the monitoring of foreign currency transactions. At the time, UBS Financial Services had committed to fixing the monitoring system by mid-2019, but only delivered the automated solution in 2021. In the meantime, more than 61,500 foreign currency transfers with a volume of USD 10.5 billion remained unmonitored.
In short
The record fine of USD 125 million against UBS Financial Services shows that supervisory authorities do not require the promise of a measure, but its demonstrable implementation over years. Continuous, documented tracking of remediation measures with evidence of effectiveness, rather than a one-off promise, would have changed the path from the first fine in 2018 to the current sanction.
Contents
1. [How did the record fine against UBS come about?](#a1-how-did-the-record-fine-against-ubs-come)
2. [Which commitment was not enough for the supervisory authority?](#a2-which-commitment-was-not-enough-for-the-)
3. [What evidence tracking would have made the difference?](#a3-what-evidence-tracking-would-have-made-t)
4. [Why does recidivism weigh so heavily with the supervisory authority?](#a4-why-does-recidivism-weigh-so-heavily-wit)
5. [What does this mean for your own GRC function?](#a5-what-does-this-mean-for-your-own-grc-fun)
125USD million
Fine imposed by FinCEN on UBS Financial Services
FinCEN, press release
61,500transfers
unmonitored foreign currency transactions 2019 to 2023
Wealth Management, cited in FinCEN consent order
14.5USD million
Fine from the 2018 consent order
Compliance Week
## How did the record fine against UBS come about?
The fine is the result of a relapse: UBS Financial Services had already paid for the same shortcomings in 2018 and failed to implement the promised correction on time.
In 2018, a consent order was reached with FinCEN, under which UBS Financial Services paid a fine of USD 14.5 million for various AML deficiencies. At the time, the company assured the US financial supervisory authority that it would remedy the weaknesses in the monitoring system for foreign currency transfers by mid-2019. The existing system was inadequate: transactions were reviewed at most quarterly, based on an error-prone, improvised Excel process.
Despite these known weaknesses, implementation was delayed, and a modern automated monitoring system did not go live until 2021. In the meantime, between January 2019 and June 2023, more than 61,500 foreign currency transfers with a total volume of USD 10.5 billion remained unmonitored. This is the second enforcement action taken by FinCEN against the same company.
## Which commitment was not enough for the supervisory authority?
A one-off commitment to remedy deficiencies was not enough for FinCEN, which required ongoing proof of actual implementation.
FinCEN expects financial institutions to remedy identified AML compliance deficiencies promptly, and found that UBS Financial Services continued to fail at monitoring foreign currency transactions even after settling with FinCEN, the SEC and FINRA for the same shortcomings. Significant parts of the remediation were only addressed once FinCEN’s investigation was already underway.
The current consent order therefore demands more than a renewed commitment. UBS Financial Services must engage an independent third party to conduct a retrospective review of undetected suspicious transactions as well as a comprehensive review of the AML programme. Only if this review is completed satisfactorily and the recommendations are implemented will FinCEN credit up to USD 15 million of the costs.
## What evidence tracking would have made the difference?
A continuous, verified record of the implementation status of every single remediation measure would have changed the path to the record fine, not another action plan.
Between the commitment made in 2018 and the actual go-live in 2021 lay the gap that FinCEN ultimately priced expensively. What would have been effective was a chain of evidence linking every committed measure to a verified implementation status: test results for the new system, documented sampling, and tracking of open findings through to demonstrable closure.
This idea aligns with the insight discussed in « Risk management serves the achievement of objectives, not itself »: a control promise without ongoing evidence of effectiveness remains paper. A comparable pattern, in which a one-off commitment concealed a persistent control gap, is also shown in « EUR 89 million in losses from overlooked ICT risk controls under DORA ».
## Why does recidivism weigh so heavily with the supervisory authority?
A second violation of the same obligation signals to the supervisory authority that internal controls no longer provide reliable self-correction, and increases the risk of external tips.
The UBS Financial Services case is seen as a warning to anyone who underestimates recidivism and hesitant action in combating money laundering. This focus carries additional weight now that a new whistleblower programme is intended to strengthen AML enforcement, since an earlier fine makes a tip from within the company more likely.
Where a first fine failed to bring about real change, employees lose confidence in an internal solution, and expect the authority to act more forcefully the second time. For the GRC function, this means that documented tracking demonstrates to the supervisory authority, and to the workforce itself, that findings are taken seriously.
## What does this mean for your own GRC function?
Those responsible should link every open finding to a verified, dated evidence of effectiveness, rather than relying on status reports.
The first verifiable step: internal audit or the compliance function determines, for every finding arising from a supervisory review, which evidence would justify its closure, and documents this evidence before the next internal audit cycle. A comparable principle of ongoing rather than one-off evidence tracking is discussed in « TPRM in transition: EBA guideline, DORA and MaRisk at a glance » for the management of third parties.
Anyone who today merely marks findings from reviews as closed, without systematically archiving the evidence of effectiveness, is structurally repeating the pattern that led to escalation over years in the UBS Financial Services case.
For practice
## Key points
- Supervisory authorities do not assess the promise of a measure, but its verified implementation status over years.
- A gap between promised and actual implementation weighs significantly more heavily on a second violation than on the first.
- Every open finding should be tied to a specific, dated piece of evidence of effectiveness, not a status report.
- Recidivism measurably increases the risk of internal tip-offs, because employees lose confidence in an internal solution.
FAQ
## Frequently asked questions
How high is the FinCEN fine against UBS Financial Services?FinCEN imposed a fine of USD 125 million on UBS Financial Services. It is the highest sanction ever issued against a broker-dealer for violations of the Bank Secrecy Act, and the second enforcement action taken by FinCEN against the same company.
Why was UBS Financial Services already fined in 2018?In 2018, UBS Financial Services paid a fine of USD 14.5 million for various AML deficiencies in the monitoring of foreign currency transactions. The company committed to replacing the existing, error-prone monitoring system with an automated solution by mid-2019.
What must UBS Financial Services now do in addition to paying the fine?The current consent order requires UBS Financial Services to engage an independent third party to carry out a retrospective review of undetected suspicious transactions as well as a comprehensive review of the AML programme. If this review is completed satisfactorily and the recommendations are implemented, FinCEN will credit up to USD 15 million of the costs.
How many transactions remained unmonitored at UBS?Between January 2019 and June 2023, more than 61,500 foreign currency transfers with a total volume of USD 10.5 billion remained unmonitored, because the promised automated monitoring solution did not go live until 2021, instead of by mid-2019 as promised.
What role does a whistleblower programme play in AML violations?FinCEN has introduced a whistleblower programme intended to strengthen AML enforcement. An earlier fine makes a tip-off from within the company more likely, because employees lose confidence in an internal solution when findings are repeatedly not remedied effectively.
Sources
1. [Historic $125 Million Penalty Against UBS Financial Services Inc.](https://www.fincen.gov/news/news-releases/fincen-assesses-historic-125-million-penalty-against-ubs-financial-services-inc)FinCEN
2. [Record-setting AML penalty against UBS was years in the making](https://www.complianceweek.com/best-practices/fincen-record-setting-aml-penalty-against-ubs-was-years-in-the-making/)Compliance Week
**Catégories:** Regulation & Supervision
**Étiquettes:** AML compliance, supervisory review, Bank Secrecy Act, supervisory recidivism, GRC tracking
---
### [Solvency as Evidence: What FINMA Measures in the Insurance Market Report](https://swissgrc.com/fr/solvency-as-evidence-finma-insurance-market-report/)
**Published:** août 25, 2026
**Author:** superadmin
**Excerpt:** FINMA bases its assessment of the resilience of the Swiss insurance industry on an aggregated annual result of CHF 24.4 billion, 136 percent above the previous year, as well as on a significantly increased capital and solvency ratio. The main driver was investment income, not premium business. For internal documentation, this means that key figures require a calculation basis, a data source and a time series, not just a final number.
**Content:**
The latest insurance market report from FINMA shows, in exemplary fashion, how a supervisory authority underpins a resilience statement with concrete key figures. FINMA attests that the Swiss insurance industry is in a strong financial position and supports this with an aggregated annual result, an increased solvency ratio and a higher capital ratio. For governance, risk and compliance officers, it is worth examining the underlying logic of these key figures. It shows what level of documentation a robust resilience statement requires within their own organisation.
In short
FINMA bases its assessment of the resilience of the Swiss insurance industry on an aggregated annual result of CHF 24.4 billion, 136 percent above the previous year, as well as on a significantly increased capital and solvency ratio. The main driver was investment income, not premium business. For internal documentation, this means that key figures require a calculation basis, a data source and a time series, not just a final number.
Contents
1. [Which figures support FINMA's statement on industry resilience?](#a1-which-figures-support-finmas-statement-o)
2. [Why does premium volume remain almost unchanged despite record profit?](#a2-why-does-premium-volume-remain-almost-un)
3. [What does this key-figure logic mean for documentation within an organisation?](#a3-what-does-this-key-figure-logic-mean-for)
4. [What first step makes an organisation's own resilience documentation verifiable?](#a4-what-first-step-makes-an-organisations-o)
24.4CHF bn
Aggregated annual result of the Swiss insurance industry 2025
FINMA insurance market report, cited by cash
136%
Increase in annual result compared to the previous year
FINMA insurance market report, cited by cash
149CHF bn
Gross premium volume of the industry 2025
FINMA insurance market report, cited by thebrokernews.ch
## Which figures support FINMA's statement on industry resilience?
FINMA attests that the Swiss insurance industry is overall in a strong financial position and supports this with an aggregated annual result of CHF 24.4 billion, which is 136 percent above the previous year’s figure.
In addition, the supervisory authority notes that the industry significantly increased its capital and solvency ratio during the reporting year. For FINMA, this combination of result, solvency and capital development forms the evidence base on which the assessment of industry resilience rests.
The result was driven primarily by investment income: investment profit rose by 47.6 percent to CHF 24.8 billion, and the return on capital investments climbed from 3.37 to 5.00 percent.
Within the segments, the increase in profit was strongest among non-life insurers, at CHF 12.9 billion, and among reinsurers, at CHF 9.8 billion.
## Why does premium volume remain almost unchanged despite record profit?
The industry’s total gross premium volume fell only slightly in 2025, by 0.6 percent, to CHF 149 billion, while profit figures improved significantly over the same period.
A look at the individual segments reveals a mixed picture: life insurers grew by 3.7 percent and non-life insurers by 2.8 percent, while reinsurers had to accept a decline of 6.1 percent. FINMA attributes this primarily to the strength of the Swiss franc against the dollar, the euro and the pound.
For the interpretation of the resilience statement, this means that a single figure such as the aggregated annual result explains little unless it is linked to premium development, segment logic and exchange rate effects. How granular a review of key figures should be within internal risk management is described in the article Risk management serves goal achievement, not itself.
RiskQuant Solvency and Capacity, Risiko gegen Tragfähigkeit über die Zeit## What does this key-figure logic mean for documentation within an organisation?
Anyone who wants to justify a resilience statement internally with the same rigor as FINMA does in its report must document not only the figure itself, but also the calculation basis, data source and time series.
The article ERM Report 2023: Financial Resilience in Focus shows that financial resilience in risk management is increasingly treated as a distinct category of key figures, rather than merely as a by-product of the annual financial statements. For governance officers, this means concretely: key figures on financial resilience should be documented in the risk register just as traceably as their calculation logic.
How important seamless evidence over several years is when dealing with supervisory authorities is shown by the article What the UBS fine reveals about long-term supervisory review, using the example of a financial institution.
## What first step makes an organisation's own resilience documentation verifiable?
The first step is to bring together the solvency and capital ratios used within the organisation, along with their calculation basis and data source, in a traceable overview.
The risk manager presents this overview at the next meeting of the board of directors or the audit committee, explicitly indicating for which figures a seamless time series exists and where evidence is missing. Such an overview creates the basis for justifying resilience statements within the organisation with a rigor similar to that of FINMA’s insurance market report.
- Record the figure and its calculation basis in the same document
- Clearly assign data source and responsibility for each figure
- Demonstrate a seamless time series across multiple reporting periods
For practice
## Key points
- FINMA does not support its resilience statement with a single figure, but with result, solvency ratio and capital ratio taken together.
- A large part of the increase in result stems from investment income, not from premium business, which must be taken into account when interpreting the figures.
- Internal resilience figures should be documented with calculation basis, data source and time series, not just as a final number.
- The first verifiable step is a summary of key figures presented to the board of directors or the audit committee at the next meeting.
FAQ
## Frequently asked questions
How high was the aggregated annual result of the Swiss insurance industry according to FINMA?The aggregated annual result stood at CHF 24.4 billion, corresponding to an increase of 136 percent compared to the previous year. The main driver was investment income: investment profit rose by 47.6 percent to CHF 24.8 billion, and the return on capital investments climbed from 3.37 to 5.00 percent.
How did the gross premium volume of Swiss insurers develop?The industry's total gross premium volume fell slightly in 2025, by 0.6 percent, to CHF 149 billion. Life insurers grew by 3.7 percent and non-life insurers by 2.8 percent, while reinsurers recorded a decline of 6.1 percent, partly due to the strength of the Swiss franc against the dollar, the euro and the pound.
Which segments contributed most to the increase in profit?The increase in profit was strongest among non-life insurers, at CHF 12.9 billion, and among reinsurers, at CHF 9.8 billion. This increase was driven primarily by the industry's investment income and to a lesser extent by developments in the actual premium business of the individual insurance segments.
What information should internal resilience figures include to be robust?Internal resilience figures should document not only the final number, but also the calculation basis, the data source used and a seamless time series across multiple reporting periods. Only in this way can a resilience statement within an organisation be justified with a rigor similar to that of FINMA's insurance market report towards the public.
What is the first step in reviewing an organisation's own resilience documentation?The first step is to bring together all solvency and capital ratios used within the organisation, along with their calculation basis and data source, in a traceable overview. This is then presented to the board of directors or the audit committee, with a clear indication of where seamless time series exist and where the corresponding evidence is still missing.
Sources
1. [FINMA attestiert Schweizer Versicherungsbranche höhere Resilienz](https://www.cash.ch/news/top-news/finma-attestiert-schweizer-versicherungsbranche-hohere-resilienz-962288)cash
2. [FINMA-Bericht: Schweizer Versicherer trotzen der Zinswende mit Rekordgewinn](https://www.thebrokernews.ch/finma-bericht-schweizer-versicherer-trotzen-der-zinswende-mit-rekordgewinn/)thebrokernews.ch
**Catégories:** Risk & Decision Making
**Étiquettes:** solvency ratio, capital ratio, resilience statement, risk management documentation, GRC evidence
---
### [Cyber Resilience Act: Where the Gaps Actually Are](https://swissgrc.com/fr/cyber-resilience-act-gaps-reporting-obligations-sbom/)
**Published:** août 26, 2026
**Author:** superadmin
**Excerpt:** Until the Cyber Resilience Act applies in full on 11 December 2027, companies need to prepare two things above all: a working 24-hour reporting chain for actively exploited vulnerabilities from 11 September 2026, and a current, machine-readable software bill of materials that includes information from suppliers. Both require documented processes, not preparation shortly before the deadline.
**Content:**
The Cyber Resilience Act enters into full application on 11 December 2027, but the decisive groundwork is being laid well before that date. A recent survey reported by heise online shows that many companies are still not sufficiently familiar with the requirements on reporting obligations and software bills of materials. For governance, risk and compliance functions, the question is no longer whether the CRA is relevant, but which evidence must actually be in place by the next deadlines, and who is responsible for providing it.
In short
Until the Cyber Resilience Act applies in full on 11 December 2027, companies need to prepare two things above all: a working 24-hour reporting chain for actively exploited vulnerabilities from 11 September 2026, and a current, machine-readable software bill of materials that includes information from suppliers. Both require documented processes, not preparation shortly before the deadline.
Contents
1. [How far has industry actually progressed with CRA implementation?](#a1-how-far-has-industry-actually-progressed)
2. [Which deadlines lie between now and full application?](#a2-which-deadlines-lie-between-now-and-full)
3. [What does the reporting obligation under Article 14 CRA actually require?](#a3-what-does-the-reporting-obligation-under)
4. [Which evidence for the software bill of materials is most often still missing?](#a4-which-evidence-for-the-software-bill-of-)
5. [Which first step can be scheduled concretely right now?](#a5-which-first-step-can-be-scheduled-concre)
45%
of the companies surveyed are barely or not at all familiar with the CRA requirements
ONEKEY survey, cited by heise online, 25 August 2026
18%
of suppliers provide the necessary CRA information to manufacturers
ONEKEY survey, cited by heise online, 25 August 2026
24hrs.
deadline for the early warning of an actively exploited vulnerability
Regulation (EU) 2024/2847, Art. 14
## How far has industry actually progressed with CRA implementation?
According to a survey by cybersecurity provider ONEKEY cited by heise online, 45 percent of the companies surveyed are barely or not at all familiar with the CRA requirements.
A second finding carries more weight further down the supply chain: according to the same survey, only 18 percent of suppliers provide the necessary CRA information, even though manufacturers remain liable for supplied components as well. The real risk therefore lies less in a company’s own development department than in the chain of upstream suppliers.
Nevertheless, a third of companies state that they intend to meet all requirements by the December 2027 deadline, according to heise online. In many cases, a gap remains between this ambition and documented preparation. Similar uncertainty about the actual scope of application also shows up under other EU legislation, as the article « NIS2-Registrierungslücke: Was sie über Scope-Unsicherheit zeigt » illustrates.
## Which deadlines lie between now and full application?
The Cyber Resilience Act entered into force on 10 December 2024, the reporting obligation for vulnerabilities and incidents applies from 11 September 2026, and the regulation applies in full from 11 December 2027.
The real preparation time falls between these dates. Companies that want to meet the reporting obligation from September 2026 need a working detection and escalation chain in place by that date, not a draft of one. Full compliance, including the SBOM obligation, follows just over a year later, but the processes required for it cannot be built in the final weeks before the deadline.
The German Federal Office for Information Security (BSI) accompanies this transition period with a technical guideline that specifies requirements for SBOM and reporting, but this guideline does not replace a company’s own risk assessment.
Control Assessment in der SwissGRC Plattform## What does the reporting obligation under Article 14 CRA actually require?
Manufacturers must report actively exploited vulnerabilities and severe security incidents to the competent coordinating authority and to ENISA, with an early warning within 24 hours and a follow-up notification within 72 hours.
Both notifications go through the single reporting platform provided for under the CRA, which forwards them simultaneously to the coordinating CSIRT and to ENISA. The clock starts when the manufacturer becomes aware of the issue, not when a specialist department or an external reporter confirms it.
For a GRC function, this means the escalation paths within the 24-hour deadline must be documented in writing and rehearsed before the September 2026 deadline is reached. How strongly such a reporting chain depends on rehearsed processes rather than on technology alone is described in the article « ISMS: Menschen, Prozesse und Technologie sind entscheidend ».
## Which evidence for the software bill of materials is most often still missing?
The SBOM is part of the technical documentation and must cover at least the direct software dependencies, yet many companies are missing precisely this information for supplied components.
The CRA does not mandate a single technical format; in practice, CycloneDX and SPDX have become established. What matters is less the format than currency: an SBOM created once loses relevance with every software update and should be tightly coupled to build and release processes.
The finding on suppliers applies directly here: without reliable information from the supply chain, a company’s own SBOM remains incomplete, regardless of how well internal documentation is organised. How such dependencies on third parties can be captured systematically is described in the article « Was das Third-Party Cyber Risk Management von etablierten Sicherheitsfunktionen lernen kann ».
## Which first step can be scheduled concretely right now?
The next verifiable step is a complete product inventory that records, for each product, whether a machine-readable SBOM exists and which suppliers still need to provide missing information.
Security or compliance officers should have a documented escalation process for actively exploited vulnerabilities in place by the 11 September 2026 deadline, including access to the reporting platform and a named owner for the 24-hour deadline. In parallel, it is worth taking stock of which products and suppliers currently have machine-readable SBOM data at all.
Because CRA notifications are product-related while other regimes such as NIS2 report at the organisational level, it is also worth looking at the interfaces between the two obligations, as the article « Cyber Resilienz neu denken im Kontext von NIS2 » sets out. Companies that begin this stock-take now still have time before the September 2026 deadline for a test run of the reporting chain.
For practice
## Key points
- The reporting obligation under Article 14 CRA already applies from 11 September 2026 and requires an early warning within 24 hours.
- A working escalation chain with access to the reporting platform must be in place before this deadline, not built afterwards.
- Suppliers currently often fail to provide the necessary CRA information, even though manufacturers are liable for supplied components.
- An SBOM quickly loses relevance without being coupled to build and release processes and must be updated continuously.
- A complete product inventory with SBOM status per product is the next verifiable step before the December 2027 deadline.
FAQ
## Frequently asked questions
From when does the Cyber Resilience Act's reporting obligation apply?The reporting obligation under Article 14 CRA applies from 11 September 2026. Manufacturers must report actively exploited vulnerabilities and severe security incidents as an early warning within 24 hours and as a follow-up notification within 72 hours, via the single reporting platform, to the coordinating authority and to ENISA. The clock starts when the manufacturer becomes aware of the issue.
Which formats are used for the SBOM under the CRA?The Cyber Resilience Act does not mandate a specific technical format for the software bill of materials. In practice, CycloneDX and SPDX have become established. What matters is less the chosen format than the currency of the SBOM, which should be tightly coupled to build and release processes so it remains meaningful after updates.
When does the Cyber Resilience Act apply in full?The Cyber Resilience Act entered into force on 10 December 2024 and applies in full from 11 December 2027. In between lies the reporting obligation for vulnerabilities and incidents, which already applies from 11 September 2026 and requires corresponding processes to be in place early.
Who is liable for vulnerabilities in supplied components under the CRA?Under the Cyber Resilience Act, manufacturers are also liable for vulnerabilities in supplied components. According to a survey cited by heise online, however, only 18 percent of suppliers provide the necessary CRA information, so companies need to actively request the missing information from their supply chain.
What role does the BSI play in implementing the Cyber Resilience Act?The German Federal Office for Information Security (BSI) accompanies the transition period of the Cyber Resilience Act with a technical guideline that specifies requirements for SBOM and reporting. This guideline does not, however, replace the risk assessment that companies must carry out themselves for their products and supply chains.
Sources
1. [Umsetzung des Cyber Resilience Act: Deutsche Industrie hat noch Nachholbedarf](https://www.heise.de/news/Umsetzung-des-Cyber-Resilience-Act-Deutsche-Industrie-hat-noch-Nachholbedarf-11425603.html)heise online
2. [Cyber Resilience Act: Zeitplan und Anforderungen](https://www.bsi.bund.de/DE/Themen/Unternehmen-und-Organisationen/Informationen-und-Empfehlungen/Cyber_Resilience_Act/cyber_resilience_act_node.html)BSI
3. [Verordnung (EU) 2024/2847 (Cyber Resilience Act)](https://eur-lex.europa.eu/legal-content/DE/ALL/?uri=CELEX:32024R2847)EUR-Lex
**Catégories:** Regulation & Supervision
**Étiquettes:** SBOM software bill of materials, CRA deadlines 2027, 24-hour vulnerability reporting, CRA supply chain, CRA reporting obligation
---
### [ISG ISMS Obligation by End of 2026: What Had to Be Settled Before](https://swissgrc.com/fr/isg-isms-obligation-2026-milestones/)
**Published:** août 28, 2026
**Author:** superadmin
**Excerpt:** The ISMS obligation under the Information Security Act ends at the end of 2026, but it does not start there. As early as the end of 2024, affected organisations had to submit a classification catalogue, and by the end of 2025, a protection needs analysis and classification of their IT. Both milestones provide the basis on which risk assessment and security measures within the ISMS can only then be built. Organisations that have not completed these steps lose time that will be missing before the end of 2026.
**Content:**
At the end of 2026, a deadline under the Information Security Act expires whose actual starting point already lies two years in the past. The statutory timetable provides for its own intermediate steps in the years before, which precede the build-up of an information security management system (ISMS) and are the substantive precondition for it. Organisations that have skipped these milestones or only partially completed them face considerable time pressure as the final deadline approaches. This article sets out the sequence of steps and shows what those responsible should still check now.
In short
The ISMS obligation under the Information Security Act ends at the end of 2026, but it does not start there. As early as the end of 2024, affected organisations had to submit a classification catalogue, and by the end of 2025, a protection needs analysis and classification of their IT. Both milestones provide the basis on which risk assessment and security measures within the ISMS can only then be built. Organisations that have not completed these steps lose time that will be missing before the end of 2026.
Contents
1. [What does the Information Security Act specifically require by the end of 2026?](#a1-what-does-the-information-security-act-s)
2. [Which milestone already had to be in place by the end of 2024?](#a2-which-milestone-already-had-to-be-in-pla)
3. [Which milestone had to be completed by the end of 2025?](#a3-which-milestone-had-to-be-completed-by-t)
4. [Why is the reporting duty for cyberattacks interlinked with ISMS build-up?](#a4-why-is-the-reporting-duty-for-cyberattac)
5. [What should those responsible still check before the deadline expires?](#a5-what-should-those-responsible-still-chec)
## What does the Information Security Act specifically require by the end of 2026?
By the end of 2026, the authorities and organisations subject to the Act must operate a functioning ISMS that identifies and assesses risks and continuously reviews the effectiveness of measures.
The Information Security Act (ISG) governs the obligations of federal bodies, the cantons cooperating with the Confederation, and operators of critical infrastructure in Articles 6 to 23 ISG. At its core is the build-up of an information security management system that brings together protection needs analysis, risk assessment and security measures.
What matters is not a single certificate but demonstrability: organisations that know their risks, define responsibilities and document measures fulfil the statutory management logic regardless of the framework chosen. In practice, most affected organisations orient themselves on ISO 27001, because the standard maps precisely this logic into processes that auditors and supervisory bodies recognise.
The ISG does not require certification, but demonstrability of the management logic.
## Which milestone already had to be in place by the end of 2024?
By the end of 2024, affected organisations had to draw up a classification catalogue that forms the basis for all subsequent steps.
Without a categorisation of an organisation’s own information, neither protection needs nor risk can be assessed meaningfully. The classification catalogue determines how sensitive a given piece of information is and what level of protection it therefore requires.
According to the overview of the [staggered ISG timetable](https://www.infosec.ch/beratung/informationssicherheit/das-informationssicherheitsgesetz-des-bundes-isg/) published by Swiss Infosec AG, drawing up this catalogue was the first of three milestones preceding the actual ISMS build-up. Organisations that have not created the catalogue, or have only done so superficially, must now complete it retroactively before the following steps can become reliable.
Dashboard für Sicherheitsvorfälle und Ereignisse in der SwissGRC® Plattform## Which milestone had to be completed by the end of 2025?
By the end of 2025, affected bodies had to carry out a protection needs analysis and classify their IT in accordance with the new law.
The protection needs analysis builds directly on the classification catalogue: only once it is established how sensitive a piece of information is can the level of protection required for the associated IT resources be assessed. This classification determines which security measures will later need to apply within the ISMS.
If this classification is missing, the risk catalogue within the ISMS remains incomplete, because risks cannot be prioritised appropriately without a known level of protection need. Only with a complete classification can the build-up of an ISMS be planned so that the remaining time is actually sufficient.
## Why is the reporting duty for cyberattacks interlinked with ISMS build-up?
Because the reporting duty presupposes incident management that must be anchored in the ISMS anyway: detection, assessment and reporting of an event within the statutory deadline.
Operators of critical infrastructure must report a cyberattack to the Federal Office for Cybersecurity within the statutory [24-hour reporting deadline](https://www.ncsc.admin.ch/ncsc/de/home/meldepflicht/meldepflicht-info.html) after its discovery. This deadline can only be met if detection, escalation and reporting are already defined as a process within the ISMS, rather than improvised only once an incident occurs.
Supervisory practice regarding reporting deadlines has since become stricter, for instance with the reporting duty for cyberattacks. Organisations that only build up their ISMS after the 2024 and 2025 milestones have lapsed risk that their reporting processes, too, will be in place too late.
## What should those responsible still check before the deadline expires?
They should honestly compare their own status of classification catalogue, protection needs analysis and ISMS build-up before the remaining time for rework becomes too short.
Where the classification catalogue or the protection needs analysis is missing or outdated, this can no longer simply be made up within the ISMS build-up, but only worked through in parallel with it. This further shortens the already tight remaining period.
Security officers should therefore take stock of the milestones completed so far before the end of the year, and record open points in central documentation for the ISMS build-up rather than spreading them across various spreadsheets. This first step shows how much time actually remains for the ISMS build-up itself.
Related
### Bundle evidence for ISMS milestones centrally
The Information Security solution maps classification, protection needs and risk assessment within a shared structure. It supports the documentation of the individual ISG milestones through to ISMS evidence.
[Information Security ](https://swissgrc.com/fr/information-security-management-isms-software/)
For practice
## Key points
- Check whether the classification catalogue from the first milestone is complete before continuing with the protection needs analysis.
- Complete the protection needs analysis and the classification of your IT, as they form the basis for risk assessment within the ISMS.
- Anchor the reporting duty for cyberattacks as a fixed process within the ISMS, rather than improvising it when an incident occurs.
- Carry out an honest stocktake of all three milestones before the end of the year to realistically assess the time remaining.
FAQ
## Frequently asked questions
From when does the ISMS obligation under the Information Security Act apply?The Information Security Act requires a functioning ISMS by the end of 2026 that identifies and assesses risks and continuously reviews the effectiveness of measures. This deadline applies to federal bodies, cantons cooperating with the Confederation and operators of critical infrastructure, which previously already had to draw up a classification catalogue and a protection needs analysis.
Who is affected by the Information Security Act?The Information Security Act governs the obligations of federal bodies, the cantons cooperating with the Confederation and operators of critical infrastructure in Articles 6 to 23 ISG. These organisations must build up an information security management system that brings together protection needs analysis, risk assessment and security measures.
Does the ISG require certification to ISO 27001?No, the Information Security Act does not require certification, but demonstrability of the statutory management logic: knowing risks, defining responsibilities and documenting measures. Many organisations orient themselves on ISO 27001, because the standard maps this logic into processes that auditors and supervisory bodies recognise.
What happens if the classification catalogue was not drawn up by the end of 2024?Organisations that have not created the classification catalogue, or have only done so superficially, must now complete it retroactively before the following milestones, such as the protection needs analysis and ISMS build-up, can become reliable. This further shortens the time remaining before the end of 2026, since later steps cannot be built appropriately without this foundation.
Why must the reporting duty for cyberattacks be anchored in the ISMS?The statutory reporting duty requires a cyberattack to be reported to the Federal Office for Cybersecurity within 24 hours of its discovery. This deadline can only be met if detection, escalation and reporting are already defined as a fixed process within the ISMS, rather than being improvised when an incident occurs.
Sources
1. [Staggered timetable for the ISG](https://www.infosec.ch/beratung/informationssicherheit/das-informationssicherheitsgesetz-des-bundes-isg/)Swiss Infosec AG
2. [Information on the reporting duty](https://www.ncsc.admin.ch/ncsc/de/home/meldepflicht/meldepflicht-info.html)Federal Office for Cybersecurity (BACS)
**Catégories:** Regulation & Supervision
**Étiquettes:** Information Security Act, classification catalogue, protection needs analysis, ISMS build-up, reporting duty cyberattacks
---
### [BACS Tightens Tone on Reporting Deadlines](https://swissgrc.com/fr/bacs-tightens-tone-on-reporting-deadlines/)
**Published:** août 27, 2026
**Author:** superadmin
**Excerpt:** To prove that a cyber incident was reported to the Federal Office for Cyber Security on time, a company must document without gaps the moment of discovery, the course of internal escalation, the time of the initial report within 24 hours and the time of the follow-up report. What counts is the moment the attack became known, not the completion of the forensic analysis.
**Content:**
The Federal Office for Cyber Security (BACS) initially introduced the reporting obligation for cyberattacks on critical infrastructure in a cooperative manner and tolerated early teething problems. With the end of this transition phase in mid-2026, the trade publication sidd.swiss announces in its analysis of the NCSC/BACS reporting obligation a more consistent enforcement, particularly for repeated violations and reports that only became known late. For companies, one question moves to the foreground: which timeline they must document without gaps in an emergency.
In short
To prove that a cyber incident was reported to the Federal Office for Cyber Security on time, a company must document without gaps the moment of discovery, the course of internal escalation, the time of the initial report within 24 hours and the time of the follow-up report. What counts is the moment the attack became known, not the completion of the forensic analysis.
Contents
1. [What changes at BACS from mid-2026?](#a1-what-changes-at-bacs-from-mid-2026)
2. [When does the reporting deadline start running?](#a2-when-does-the-reporting-deadline-start-r)
3. [Which timestamps must a company document?](#a3-which-timestamps-must-a-company-document)
4. [How does the BACS deadline differ from other reporting obligations?](#a4-how-does-the-bacs-deadline-differ-from-o)
5. [What is the first concrete step towards demonstrable compliance?](#a5-what-is-the-first-concrete-step-towards-)
24hrs
Deadline for the initial report of a cyberattack to BACS
BACS, Information on the reporting obligation
14days
Deadline to complete the report with a follow-up report
BACS, Information on the reporting obligation
100000CHF
Maximum fine for failure to report
BACS, Six months of the reporting obligation for cyberattacks on critical infrastructure
## What changes at BACS from mid-2026?
After the end of the authority’s transition phase, BACS moves from awareness-raising to consistent enforcement, with particular attention to repeated violations and late reports.
The legal basis is the federal Information Security Act, whose contribution to strengthening the digital resilience of the federal government anchors the reporting obligation for operators of critical infrastructure. In the months following its introduction, BACS drew a positive balance: operators reported cyberattacks on time, within 24 hours, as the authority noted in its statement on six months of the reporting obligation. In total, 164 reports were received during this period, as BACS stated in the same communication.
Anyone who violates the reporting obligation must, according to BACS, expect a fine of up to CHF 100,000, whereby the authority first contacts the organisation concerned before imposing a sanction. With the end of the transition phase, sidd.swiss expects a tougher line in its analysis, above all for repeated violations and for reports that only became known through media coverage.
## When does the reporting deadline start running?
What counts is the moment the attack became known, not the completion of the forensic investigation.
sidd.swiss states in its practical analysis of the 24-hour reporting obligation that the deadline begins upon discovery, not at the original time of the attack. For companies, the decisive question thus shifts from technology to organisation: from what point is an incident considered sufficiently identified. Once this threshold is reached, the 24-hour deadline for the initial report to BACS starts running, as the authority sets out in its information on the reporting obligation.
Anyone who waits for a complete forensic investigation will, as a rule, already have missed the deadline. BACS explicitly expects a structured initial assessment, not finished forensics. Missing details can be added within 14 days in a follow-up report, as BACS states in its fact sheet on the reporting obligation.
## Which timestamps must a company document?
At least four points in time must be verifiable: detection, internal escalation, initial report and follow-up report.
Without documented timestamps, it is difficult to prove after the fact that a report was made on time. BACS requires details of the date and time of detection as well as of the attack in the report itself. These details only make sense if they come from unbroken internal logging rather than being reconstructed afterwards.
How demanding a complete evidence trail can become over several years is shown by the review of a long-running supervisory investigation in the UBS fine case.
- Time of the first indication of an incident
- Time of discovery by the responsible unit
- Time of internal escalation to management and the persons authorised to report
- Time of the initial report to BACS, at the latest 24 hours after discovery
- Time of the follow-up report with complete details, at the latest 14 days later
## How does the BACS deadline differ from other reporting obligations?
Companies subject to several regulations must keep several clocks in view at once; the BACS 24-hour deadline is only one of them.
Regulated financial institutions already know a similar logic from FINMA supervisory practice: for serious incidents, the supervisory authority expects an initial report within 24 hours and a follow-up report within 72 hours. The BACS reporting obligation applies alongside this supervisory duty, but does not replace it.
For manufacturers of products with digital elements, a further reporting obligation is added on 11 September 2026: from this date, the EU Cyber Resilience Act requires the reporting of actively exploited vulnerabilities and serious security incidents. A separate article examines where concrete gaps still remain in these CRA reporting obligations.
Any company that has not clearly determined whether it qualifies as an operator of critical infrastructure or as an entity subject to NIS2 falls behind on every one of these deadlines. How significant this uncertainty is in practice is shown by the registration gap that many companies only close after a subsequent self-assessment.
## What is the first concrete step towards demonstrable compliance?
The first verifiable step is a documented test report that runs through the complete timeline from detection to follow-up report.
Companies should run through a test report in their internal playbook within the current quarter and log all four timestamps: detection, escalation, initial report and follow-up report. The person responsible for reporting, whether CISO or information security officer, should be named in writing and given the necessary authority. This exercise provides the basis for presenting a complete and verifiable timeline to BACS in an emergency.
For practice
## Key points
- Document the moment of discovery as the starting point of the 24-hour deadline, not the completion of the forensic analysis.
- Name in writing who triggers the initial report to BACS in an emergency.
- Prepare templates for the initial and follow-up report so the 14-day deadline does not pass under time pressure.
- Check deadlines running in parallel under FINMA supervision, NIS2 and the Cyber Resilience Act, so that no reporting obligation is overlooked.
- Test the reporting chain annually with an exercise to credibly demonstrate the timeline in an emergency.
FAQ
## Frequently asked questions
### How high is the fine for a late BACS report?
Anyone who violates the reporting obligation must, according to BACS, expect a fine of up to CHF 100,000. Before imposing a sanction, the authority first contacts the organisation concerned. With the end of the transition phase in mid-2026, the trade publication sidd.swiss expects more consistent enforcement, particularly for repeated violations and reports that only became known late.
### How many hours does a company have for the initial report to BACS?
The initial report to BACS must be made within 24 hours of discovering the attack. What counts is not the time of the attack itself or the completion of the forensic analysis, but the moment at which the responsible unit within the company classifies the incident as sufficiently identified.
### How long is the deadline for the follow-up report to BACS?
BACS allows a deadline of 14 days after the initial report for the follow-up report. In this follow-up report, companies can add details that were not yet fully available in the first, structured initial assessment, such as findings from the forensic analysis.
### Does the BACS reporting obligation apply in addition to the FINMA reporting obligation?
Yes. Regulated financial institutions already know from FINMA supervision an initial report within 24 hours and a follow-up report within 72 hours. The BACS reporting obligation for operators of critical infrastructure applies alongside this supervisory duty and does not replace it; both deadlines must be observed in parallel.
### From when does the Cyber Resilience Act reporting obligation apply?
From 11 September 2026, the EU Cyber Resilience Act requires manufacturers of products with digital elements to report actively exploited vulnerabilities and serious security incidents. This deadline runs in parallel with the BACS reporting obligation and with further reporting obligations such as NIS2.
Sources
1. [Informationen zur Meldepflicht](https://www.ncsc.admin.ch/ncsc/de/home/meldepflicht/meldepflicht-info.html)Bundesamt für Cybersicherheit (BACS)
2. [Sechs Monate Meldepflicht für Cyberangriffe auf kritische Infrastrukturen](https://www.bacs.admin.ch/de/newnsb/gezctyF6KYR7UkCjXBC5s)Bundesamt für Cybersicherheit (BACS)
3. [NCSC / BACS: When Swiss Companies Must Report Cyber Incidents](https://www.sidd.swiss/en/insights/ncsc-bacs-reporting-obligation/)sidd.swiss
4. [24-Stunden-Meldepflicht für Spitäler – ISG/BACS in der Praxis](https://www.sidd.swiss/einblicke/kritis-24h-meldepflicht-spital/)sidd.swiss
**Catégories:** Regulation & Supervision
**Étiquettes:** 24-hour reporting obligation cyber incident, BACS fine reporting obligation, critical infrastructure reporting obligation, Information Security Act federal government, NCSC reporting obligation deadline
---
### [How do you report risks to your board?](https://swissgrc.com/fr/risk-quantification-how-do-you-report-risks-to-your-board/)
**Published:** juin 11, 2026
**Author:** Besfort Kuqi
**Excerpt:** Risk is usually reported in the language of risk professionals. Sometimes as a heat map that is hard to draw a firm conclusion from. Sometimes as a quantitative analysis, full of distributions and metrics that almost no one in the room truly reads. Neither is wrong. It simply is not the language a board decides in. More often than not, it is not the quality of the numbers. The report answered a question the board never actually asked.
**Content:**
**Every risk officer knows the moment. The report is ready: clean, complete, thorough. The board nods, perhaps asks a single question, then moves to the next item on the agenda. And nothing happens. Not because the board does not care, but because the report answered a question the board never actually asked.**
Risk is usually reported in the language of risk professionals. Sometimes as a heat map that is hard to draw a firm conclusion from. Sometimes as a quantitative analysis, full of distributions and metrics that almost no one in the room truly reads. Neither is wrong. It simply is not the language a board decides in.
More often than not, it is not the quality of the numbers. The report answered a question the board never actually asked.
## A board does not think in risks, it thinks in consequences
The questions actually raised around the table are remarkably simple, and always the same. What could this cost us? How bad does a bad year get? Can we absorb it? How much should we set aside, and how much of that should we insure? And what do we decide today? Good risk reporting is, at heart, nothing more than the discipline of answering that chain, and leaving out everything that does not help. That chain is exactly what we built Board Risk Reporting in GRC Toolbox around.
## From the risk register to a number in francs
The starting point is the data already sitting in your risk register. From the frequency and severity of each risk, GRC Toolbox runs thousands of scenarios and aggregates them into a single picture. "Risk XY is high" becomes an amount in francs. That is the depth a simulation gives you. But the depth is not the story, it is only the raw material. It is much like a weather forecast: no one wants to see the raw readings from the measuring stations. They want to know whether to take an umbrella tomorrow.
## From a number to a statement that matters
The real work begins after that: drawing from the distribution the few statements that move the board forward. What to expect in a typical year. How far it can climb in a rare but realistic one. And then the step that makes all the difference: holding that risk against the company's capacity to bear it, which for many of our clients is available liquidity. Only there does an interesting number become a relevant statement. Not "the loss could be high", but a concrete amount in francs, measured against the company's buffer.
GRC Toolbox . Solvency & Capacity

This is what that translation step looks like: aggregated risk set against the liquidity buffer, expressed as a concrete franc amount rather than a traffic light.
## The language boards understand
A board rarely decides on risk in the abstract. It decides on budget, on reserves, on insurance, and on which residual risk it is willing to carry. That is precisely the language the report translates the numbers into. The expected annual loss becomes the basis for the reserve to plan for. The gap between the expected loss and a rare, severe year reveals the layer worth insuring or otherwise transferring. And the range beyond that exposes the extreme residual risk that no insurance fully covers. A loss distribution becomes three concrete levers: how much to set aside, what to transfer, and what to knowingly accept.
GRC Toolbox . Insights for the Board

The same numbers, translated into the board's levers: reserve, risk transfer, and the consciously carried residual risk, checked against risk appetite.
---
## The value lies in what you leave out
The value comes not from what you show, but from what you deliberately leave out.
It is tempting to put all that computing power on display: every histogram, every percentile. But each additional metric the board does not understand costs the very attention the decision needs. So we did not remove the depth, we moved it one level down. Anyone who wants it finds the full methodology, the glossary and the assumptions a single click away. The board page itself stays calm.
GRC Toolbox . Overview

The board page opens with a two-sentence statement, not a chart. The statistics are there, but they do not force themselves on you.
## The decision belongs in the report
Then there is the part most reporting tools leave out altogether: the decision itself. A report that records no decision is merely a snapshot. So the board's decision, the rationale and the resulting actions are captured directly on the same run. Next time, you not only see the new numbers, you also see what was decided last time and whether it worked. That is how reporting becomes a traceable governance trail.
GRC Toolbox . Decision Log

The decision belongs in the report, not in a separate set of minutes. Documented and auditable.
---
## What actually changes
In the end, the change is both smaller and larger than it sounds. Smaller, because the building blocks, simulation, metrics, risk-bearing capacity, are nothing new. Larger, because the perspective turns: no longer "how do we show everything we calculated", but "what does the board need in order to decide".
Risk quantification delivers the numbers. Board Risk Reporting turns them into a decision.
See it in action
Most convincing on real numbers
Two ways to explore the approach, from simulation to decision.
Webinar on 7 July 2026
We walk you through the entire path live, from simulation to decision, with time for your questions.
[Join the webinar](https://events.teams.microsoft.com/event/a18cb3ff-5047-4ffb-aeb5-9bfe9d879c3e@e19b35f4-f7ad-4fe9-a202-26aeb3f7adb1)
Discovery session
We show you risk quantification and Board Risk Reporting on realistic data, and discuss how it fits your own risk register.
[Book a session](https://swissgrc.com/en/risk-quantification)
**Catégories:** Industry News
**Étiquettes:** First
---
### [World Day for Safety and Health at Work](https://swissgrc.com/fr/welttag-fur-sicherheit-und-gesundheit-am-arbeitsplatz/)
**Published:** avril 28, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** Was ist der Welttag für Sicherheit und Health care am Arbeitsplatz?
Der Welttag für Sicherheit und Health care am Arbeitsplatz wird...
**Content:**
### WHAT IS WORLD DAY FOR SAFETY AND HEALTH AT WORK?
The World Day for Safety and Health at Work is celebrated annually on April 28 to promote the prevention of occupational accidents and injuries worldwide. It is an awareness campaign designed to draw international attention to the scale of the challenge and how promoting and creating a culture of safety and health can help ensure the well-being of employees.
- Technologies such as digitization, robotics and nanotechnology have psychosocial impacts.
- – Industrialization and climate change are increasing the risks of air pollution, heat stress or emerging diseases
- – Nearly 36 percent of the global workforce already works excessive overtime (more than 48 hours per week).
However, workplace safety is no longer limited to preventing physical injury or illness, but also encompasses mental health and well-being. Traditional prevention and control tools may still be effective, but increasing dynamics in markets and complexity within organizations make an integrated and holistic, approach to optimally aligning strategies, processes, people and technology essential. One of the components of a modern and sustainable enterprise can be summed up in three terms, Governance, Risk & Compliance (GRC). But why is the GRC topic also of great importance on World Day for Safety and Health at Work?
Governance, risk and compliance (GRC) are three key aspects of corporate governance that define the strategies, processes, processes, policies and controls that help companies mitigate operational risk and be both commercially successful and comply with all laws and regulations.
The « G » in GRC, or governance, gets a little obscured in most definitions, possibly because risk management and compliance seem self-explanatory. On World Day for Safety and Health at Work, we want to focus on precisely this important « G » and show how crucial it is to the well-being of a company’s employees. In fact, governance is the ethical management of an organization in line with its strategy and goals. Culture, ethics, values and philosophies are thus the cornerstones of what is known as corporate governance. From a management perspective, the requirements cover many aspects such as quality management, environmental issues, business continuity, human resources management and nevertheless occupational health and safety.
The pandemic has put the health of employees in the spotlight. Many « nice-to-have » job benefits that served to establish the company as an attractive employer have now become a central element of the value proposition for employees. Companies actively take their social responsibilities seriously and see it as their duty to create a safe and conducive work environment with a company-wide risk management strategy, which is ultimately critical to competitiveness, sales, reputation and talent acquisition. The pandemic has also increased the affinity for sustainability, climate change and environmental protection. Health and environmental protection are closely linked, making the transition to a sustainable society and economy increasingly understood as necessary. The pandemic has also shown that our societies have immense potential for collective action and change. This year’s theme for World Day for Safety and Health at Work is fitting, namely « Act together to build a positive safety and health culture. » These plug-in principles are an important and effective ingredient for the functioning and interaction of corporate governance. At Swiss GRC, our understanding is that we, individual employees, are of immense value to the existence of the entire entity. It only works as a team. That’s why we promote an open work culture, with flat hierarchies, give our employees a flexible design freedom, work with a 40 hour week and balance between home office and office days, which we have coordinated. Work-life balance is one of the key factors for health and well-being. Less stress leads to fewer mistakes and thus ensures the quality of our work.
### OUR TIPS FOR THE WORLD DAY FOR SAFETY AND HEALTH AT WORK
It is important to be balanced and healthy at work and to remain that way. It is necessary to leave the desk from time to time, to take breaks, to move – ideally in the fresh air, this has a positive effect on our creativity and performance. Furthermore, drinking enough water, eating healthy food and getting enough sleep are other essential components.
The comfort zone with bundled security gives most people a good feeling; leave this from time to time and try something new. Many people live every day in their past – security and the known familiar. Your mind plays an essential role in this. Observe consciously your thoughts; if our thoughts are more conscious, then we can direct them also better.
Our brain reacts to new things. The more repetition and the more often you perform or implement something (also applies to thoughts), it systematically installs new circuits in the brain. Thoughts are the language of the brain – emotions, the language of the body!
Thinking and feeling creates your state of being, or condition, thus your feelings and emotions are usually the end points of experiences. Use this extremely important world day for more awareness in the company, for employees and for you as an individual and put it into practice every day.
**Catégories:** Digital, Software
---
### [ISMS: People, processes and technology are crucial](https://swissgrc.com/fr/isms-people-processes-and-technology-are-crucial/)
**Published:** septembre 14, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** The implementation of processes and policies within an organization to permanently define, manage, control, maintain and continuously improve information security is known as an information security management system (ISMS)...
**Content:**
The implementation of processes and policies within an organization to permanently define, manage, control, maintain and continuously improve information security is known as an information security management system (ISMS). In today’s world, the interaction of individuals, processes and technology is essential to the implementation of risk management in any company. Risk management is an continuous process of identifying information security risks and creating plans to mitigate those risks. While the ISMS aims to build a comprehensive information security management capability, the digital transformation of organizations requires constant improvement and evolution of security policies and controls. The ISMS aims to minimize risk and ensure business continuity while proactively limiting the impact of security breaches. The purpose of the ISMS is also to integrate IT with enterprise security and enable effective information security management for various business activities. However, best practices are not always the easiest and organizations often face significant hurdles in implementing an ISMS, such as implementing security controls for outdated systems and unsupported platforms. Organizations in highly regulated Industries such as healthcare or finance may require a broader range of security measures and risk mitigation techniques.
### KEY BENEFITS OF IMPLEMENTING AN ISMS
- Due to an ISMS's risk assessment and analysis approach, organizations can save on costs spent on indiscriminately adding layers of defensive technologies that may not work.
- An ISMS helps protect all types of information, including digital and paper-based data, intellectual property, trade secrets, data on devices and in the cloud, hard copies and all personal information.
- By constantly adapting to changes both in the environment and within the organization, an ISMS reduces the threat of ever-evolving risks.
- An ISMS protects your entire organization from technology-related risks and other, more general threats, such as poorly informed employees or ineffective processes.

### EMERGING TECHNOLOGIES AND ISMS: INFORMATION SECURITY VULNERABILITIES ARISE FROM INCREASINGLY COMPLEX INTERRELATIONSHIPS
The recently released RIMS (Risk and Insurance Management Society, Inc.) Executive Report provides insight and guidance on integrating emerging risks into the risk management program. Incorporating so-called « emerging risks » is necessary to avoid future threats. Strikingly, only 27% of companies surveyed in the report consider the impact of emerging risks in their risk assessments. Only 34% consider emerging risks when determining their business strategy. Cloud computing, the Internet of Things (IoT), blockchain, Robotic Process Automation (RPA), Machine Learning (ML) and Artificial Intelligence (AI) are just a few of the emerging technologies that are changing the way people live and work today. New forms of attack, such as Ransomware-as-a-Service (RaaS), are also evolving in response to technological advances. Enterprises are moving away from on-premise IT infrastructures and toward cloud-based technologies and shared service providers, automating and networking manufacturing lines via the Industrial Internet of Things (IIoT) and adopting next-generation digital identification systems. Security professionals and business leaders face numerous opportunities and difficulties arising from today’s digital technologies and systems.
Information security vulnerabilities are becoming more complex as the world becomes increasingly technologically interconnected. With the expected widespread adoption of the Internet of Things (IoT) and increasing reliance on operational technologies, security approaches must be developed. Adoption of new technologies is a way forward and emerging technologies must be leveraged to benefit enterprises. Organizations must not remain static in order to stay secure, but it is critical for anyone handling sensitive data to verify that existing security mechanisms are adequate for the risks posed by evolving technologies. Anyone working with sensitive data or evolving technologies, not just IT professionals, needs to be aware of the risks and how to manage them. In today’s increasingly complex technological ecosystem, security professionals need to increase their situational and technology awareness and work closely with business leaders to actively consider how to minimize these evolving threats.
**Catégories:** Digital, Software
---
### [SWISS GRC DAY 2023: Review of this year's topics](https://swissgrc.com/blog/2023/05/08/swiss-grc-day-2023-ruckblick-auf-die-diesjahrigen-themen/#new_tab)
**Published:** mai 9, 2023
**Author:** Yahya Mohamed Mao
**Excerpt:** The Swiss GRC Day 2023 impressively underlined the importance of interdisciplinary collaboration and adaptability to successfully manage growing risks and opportunities in today's world.
**Content:**
The Swiss GRC Day 2023 was a highlight for all those interested in governance, risk and compliance and provided an outstanding opportunity for participants to expand their expertise, share best practices and network with industry experts and peers. The event impressively underlined the importance of interdisciplinary collaboration and adaptability to successfully manage growing risks and opportunities in today’s world. It also emphasised the relevance of resilience, innovation and collaboration for businesses and the GRC community alike.
**Catégories:** Events
---
### [Federal Act on Information Security (ISG)](https://swissgrc.com/blog/2023/05/24/staerkung-der-digitalen-resilienz-das-informationssicherheitsgesetz-des-bundes-isg/)
**Published:** mai 24, 2023
**Author:** Besfort Kuqi
**Excerpt:** Switzerland plans uniform regulations and reporting requirements with ISG to strengthen information and cyber security, especially for critical areas. Entry into force still unclear.
**Content:**
The ISG or Federal Information Security Act aims to strengthen information and cyber security in Switzerland. It uniformly regulates the security of information and IT resources for all federal authorities and organizations and places a special focus on critical information and systems as well as on the standardization of measures. As part of the revision of the ISG, a reporting obligation for cyber attacks will be introduced, especially for operators of critical infrastructures. This is intended to improve the cybersecurity of the federal government as a whole and increase protection against cyber threats.
**Catégories:** Digital
**Étiquettes:** First
---
### [Federal Council brings ISG and ordinance law into force on January 1, 2024](https://swissgrc.com/fr/federal-council-brings-isg-and-ordinance-law-into-force-on-january-1-2024/)
**Published:** novembre 15, 2023
**Author:** Yahya Mohamed Mao
**Excerpt:** The Federal Council has set the date for the new Information Security Act (ISG) to enter into force on January 1, 2024. This decision marks an important milestone in protecting information and strengthening cyber security in Switzerland.
**Content:**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
**The Federal Council has set the date for the Information Security Act (ISG) to enter into force as January 1, 2024 ([press release](https://www.admin.ch/gov/de/start/dokumentation/medienmitteilungen/bundesrat.msg-id-98497.html)). This decision marks an important milestone in protecting information and strengthening cyber security in Switzerland. Find out more about the ISG in our [specialist article ](https://swissgrc.com/blog/staerkung-der-digitalen-resilienz-das-informationssicherheitsgesetz-des-bundes-isg/)(in German).**
The ISG, which combines the central legal bases for the security of federal information, prescribes uniform minimum requirements for federal authorities and organizations based on international standards. It also extends the scope of protection to third parties, cantons and international partners entrusted with the processing of sensitive federal data.
The introduction of three new ordinances – the Information Security Ordinance (ISV), the Ordinance on Personal Security Checks (VPSP) and the Ordinance on the Operational Security Procedure (VBSV) – as well as a partial revision of another ordinance, will further specify the measures for ensuring information security. As part of the implementation of the ISG, federal offices are now obliged to establish an information security management system (ISMS) – a standard that stands for the systematic management and continuous improvement of information security.
As a solution provider in the area of Governance, Risk & Compliance (GRC), Swiss GRC contributes with its GRC platform to making it easier for authorities and organizations to set up and operate an ISMS and thus ensure ISG/ISV compliance.
Webinar: ISG: Practical implementation of an ISMS with the GRC Toolbox \[Product demo\]
Take part in our webinar « ISG: Practical implementation with the GRC Toolbox » on 5.12.2023 from 10:00 to 10:45 am. Learn from our expert and CEO, Besfort Kuqi, how you can set up an ISMS in accordance with the requirements of the new Swiss Information Security Act (ISG).
Watch the webinar recording now (in German)
**Catégories:** Industry News
---
### [Review: Webinar on the new Information Security Act](https://swissgrc.com/fr/review-webinar-on-the-new-information-security-act/)
**Published:** décembre 7, 2023
**Author:** Yahya Mohamed Mao
**Excerpt:** With the Swiss Federal Council's decision to bring the Information Security Act (ISG) and the corresponding ordinance into force on January 1, 2024, Switzerland is sending a clear signal for increased information security and cyber security. In this context, Swiss GRC organized a webinar.
**Content:**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
With the Swiss Federal Council’s decision to bring the Information Security Act (ISG) and the corresponding ordinance into force on January 1, 2024, Switzerland is sending a clear signal for increased information security and cyber security. In this context, Swiss GRC organized a webinar that gave participants an insight into the upcoming legal changes as well as practical implementation options through a live demonstration of the GRC Toolbox.
The [imminent entry into force](https://swissgrc.com/bundesrat-setzt-isg-und-verordnungsrecht-per-1-januar-2024-in-kraft/) at the beginning of the new year of the Information Security Act (ISG) and the Information Security Ordinance (ISV) marks a turning point in information security that will occupy numerous organizations intensively in the coming months and years. With this in mind, the webinar launched by Swiss GRC aimed to provide crucial information and insights on how to effectively meet the key requirements of the ISG and ISV. Besfort Kuqi, CEO and co-founder of Swiss GRC, opened the webinar and got the participants in the mood for the program.
Insight into the significance and scope of the Information Security Act (ISG)
Reto Zbinden, Lawyer and CEO of [Swiss Infosec AG](https://www.infosec.ch/), gave an introduction to the Information Security Act (ISG). He discussed the key aspects of the law, explained what it means to be ISG-compliant and summarized the objectives of the ISG. In doing so, he addressed the key requirements, processes and evidence needed for effective implementation. Finally, he made it clear that the increasing pressure to implement security measures is driving organizations to move away from traditional methods such as Excel or Word and instead use specialized tools to meet the complex requirements.
> [Link to the presentation of Reto Zbinden](https://swissgrc.com/wp-content/uploads/2023/12/Webinar_Informationssicherheitsgesetz_RetoZbinden.pdf)
A GRC(O) framework for successful ISG/ISV implementation
In the second part of the webinar, Besfort Kuqi used a product demo to show how the Information Security Act (ISG) and the Information Security Regulation (ISV) can be implemented with the help of software such as the GRC Toolbox. As a proven ISMS industry solution, it supports organizations in implementing the ISG/ISV requirements. Besfort Kuqi not only spoke about the classic GRC approach, but went one step further and presented a GRC(O) framework to highlight the support of the GRC Toolbox for information security operations in accordance with Art. 25 (review of protection requirements and circle of authorized persons), Art. 27 (security procedures), Art. 28 (assignment to the security levels « high protection » and « very high protection ») and Art. 29 (security measures) of the ISG.

GRC(O) Framework © Swiss GRC AG 2023
As the graphic above makes clear, the software offers comprehensive support in the area of governance, in particular in setting up an information security management system (ISMS) in accordance with Art. 5 of the ISG. In the area of risk management, the functionality of the software includes important aspects such as the inventory of protected objects (Art. 7), coordination with third parties (Art. 10) and incident management (Art. 12). In the area of compliance, the software provides valuable support in the maintenance of legal bases and contractual obligations (Art. 6), in training and awareness-raising measures (Art. 11) and in the planning and implementation of controls and audits (Art. 13).
> [Link to the presentation of Besfort Kuqi](https://swissgrc.com/wp-content/uploads/2023/12/ISG-Webinar_BesfortKuqi.pdf)
Watch the webinar recording now (in German)
**Catégories:** Events
---
### [The EU's AI Dilemma: Innovation or Over-Regulation?](https://swissgrc.com/fr/the-eus-ai-dilemma-innovation-or-over-regulation/)
**Published:** janvier 25, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The tension between innovation and regulation presents the EU with a difficult task. It must find a way that both exploits the enormous potential of AI and protects the safety and rights of its citizens. The future of AI in Europe depends on how well this balance is achieved.
**Content:**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://swissgrc.com/en/discoverycall/)
**In November 2023, Germany, France and Italy, three major players in the European Union, reached a groundbreaking agreement on the regulation of artificial intelligence (AI). As reported by [Euronews](https://www.euronews.com/next/2023/11/19/eu-ai-act-germany-france-and-italy-reach-agreement-on-the-future-of-ai-regulation-in-europ), this agreement represents an important step in shaping the future of AI in the EU. Not only does it represent a joint effort by the major EU economies, but it is also a strategic step towards reconciling the rapid development of AI technologies with the necessary regulatory framework.**
This consensus is particularly remarkable in the context of the EU’s general efforts to create a unified and effective approach to AI governance, highlighting the Union’s commitment to leading the global discussion in this critical and constantly evolving area. On December 9, 2023, representatives of the European Parliament and the Council reached an agreement on the AI Act after several days of debate. However, it still needs to be formally adopted by both the Parliament and the Council before it can come into force, expectedly in early 2024. France, Germany, and Italy were among the larger member states initially opposing the regulation, potentially threatening the efforts to pass the bill in the European Parliament.
##### The EU’s reputation as a regulatory powerhouse
In the broader context of AI regulation, the European Union has taken a leading role by navigating the complex interplay between promoting technological innovation and ensuring ethical governance. The EU’s proactive stance on AI regulation reflects its commitment to balancing technological progress with the protection of societal values. This approach has given the EU a leading role in regulation, though not without criticism regarding its effectiveness and inclusivity.
Germany, France, and Italy, as key players in the EU, have significantly shaped AI policy. Their [agreement on AI regulation](https://politicstoday.org/europe-germany-france-italy-ai-regulation/), which mandates self-regulation for Foundation Models, was a pivotal moment in EU AI governance and significantly influenced the shaping of the AI Act. The trinational agreement reflects a unified approach to regulating AI applications, not the technology itself, emphasizing the importance of model cards for transparency and accountability. Their cooperative stance also indicates a broader EU trend to integrate various national perspectives into a coherent regulatory framework. However, this influence of major economies on EU policy-making has sparked [debates](https://www.theverge.com/2023/6/30/23779611/eu-ai-act-open-letter-artificial-intelligence-regulation-renault-siemens). Critics argue that these countries may prioritize their own interests or those of large tech firms, potentially overshadowing the collective needs of the EU. This situation highlights the challenge for the EU to maintain a unified approach to AI governance while considering the diverse interests of its member states.
##### The concept of mandatory self-regulation
The AI Act on AI regulation in the EU represents a significant shift in AI governance, particularly regarding the mandatory self-regulation of Foundation Models. These models, central to generating various AI outcomes, are now subject to regulation focusing more on their application than the technology itself. This is a crucial step towards greater transparency and accountability in AI development.
The [concept of mandatory self-regulation](https://www.bakermckenzie.com/en/insight/publications/2023/11/ai-regulation-agreement-germany-france-italy#:~:text=They%20propose%20mandatory%20self%2Dregulation,security%20of%20smaller%20EU%20companies.) introduces a nuanced approach to governance. By requiring Foundation Model developers to define « model cards, » the AI Act prescribes a level of self-assessment and disclosure previously absent. These model cards should provide comprehensive information about the functioning, capabilities, and limitations of AI models. This measure aims to demystify AI technologies for regulators and the public, leading to more informed decisions about their deployment and use.
However, this regulatory approach also raises concerns about its effectiveness and the potential burden on AI developers. The demand for detailed disclosure could be seen as an additional bureaucratic hurdle, particularly inhibiting innovation for smaller companies with limited resources. While the regulation aims to address this by extending mandatory self-regulation to all AI providers regardless of size, its practical impact remains to be seen.
Moreover, the balance between regulation and innovation is a delicate issue. The EU is traditionally seen as a regulatory leader, but there’s a risk that stringent regulations could stifle [innovation in the fast-paced AI industry](https://www.computerworld.com/article/3701510/businesses-and-tech-firms-criticize-proposed-eu-ai-act.html).
##### AI and society: understanding the EU’s ethical dilemma
Amnesty International has repeatedly highlighted risks to fundamental rights posed by AI technologies in the EU’s AI regulation process. Agnes Callamard, the Secretary-General of Amnesty International, emphasized that the [dichotomy between innovation and regulation is misleading](https://www.amnesty.org/en/latest/news/2023/11/eu-france-germany-and-italy-risk-unravelling-landmark-ai-act-negotiations/) and often used by tech companies to avoid strict accountability. The organization points out the risks of AI in mass surveillance, policing, distribution of social benefits, and at borders, where AI technologies can amplify discrimination and human rights violations. Marginalized groups, such as migrants, refugees, and asylum seekers, are most at risk.
Thus, the EU’s regulatory approach faces a dilemma: it aims to promote innovation while ensuring that AI systems, especially those used in critical areas like public safety and welfare, adhere to strict transparency and accountability measures. The challenge is to create a robust legal framework that considers both ethical considerations and the dynamic nature of AI advancements.
##### AI and data protection
The EU’s AI Act, with its risk-based approach, follows a path known from data protection and the General Data Protection Regulation (GDPR): AI applications are classified into different risk categories with varying levels of risk. The higher the risk, the higher the regulatory requirements. Thus, the AI Act is seen as a complement to the GDPR in specific AI issues. However, consider this: more than half of the companies have seen new, innovative projects fail due to the GDPR, either because of direct requirements or due to uncertainties in interpreting the GDPR. [In three out of ten companies](https://www.bitkom.org/Presse/Presseinformation/Jedes-2-Unternehmen-verzichtet-aus-Datenschutzgruenden-auf-Innovationen), the deployment of new technologies like AI failed due to GDPR consequences.
Although the use of AI does not raise entirely new issues for data protection, the effort for companies remains high or will increase. This is due to extensive information and transparency obligations, ensuring the rights of affected individuals, and ensuring necessary technical and organizational measures.
In this evolving scenario, the importance of [Governance, Risk, and Compliance (GRC)](https://swissgrc.com/en) becomes increasingly significant. Effective GRC strategies are not only essential to master these complex regulations but are also key to enabling companies to use AI opportunities responsibly and ethically. While the AI Act aims to mitigate risks associated with AI, it also underscores the need for robust and adaptable GRC frameworks. These frameworks are crucial to creating a harmonious balance between promoting innovation, complying with legal regulations, and ensuring ethical corporate governance in the rapidly developing field of AI technologies.
##### The EU approach in a global context
The AI Act will have significant global implications and could set a precedent for AI governance worldwide. It aims to establish a comprehensive AI regulation that can influence global standards and use the significant consumer market of the EU to trigger the so-called Brussels Effect. The AI Act covers AI systems used in sectors like aviation, automotive, and medical technology. Companies exporting to Europe must comply with these norms, leading to a broader adoption of EU regulations – the Brussels Effect. However, this influence could be mitigated by international companies and standard-setting bodies that set corresponding norms to the specific requirements of the AI Act. More likely, the regulation could inspire similar frameworks worldwide. As AI continues to evolve, the EU model, with its focus on a balanced relationship between innovation and regulation, could serve as a template for other countries grappling with the complexity of AI regulation. Consequently, the extent of the Brussels Effect and the role of the EU as a global regulatory leader in AI will evolve as other countries and international bodies engage with and respond to these regulations.
##### What to expect?
AI regulation is a crucial moment for the European Union, setting a new direction in AI governance. Its focus on mandatory self-regulation and application-based regulation could influence global AI policy, albeit with nuanced impacts on various sectors and AI systems. This agreement underscores the need for ongoing discussions and adjustments in AI regulation, especially given the rapid development of AI technologies and their societal impacts. However, concerns remain about finding a balance between innovation and ethical stewardship and ensuring that regulations are inclusive and effective, not hindering technological progress. The success of this regulatory approach will depend on its implementation and its ability to harmonize different interests within the EU and beyond. In the worst case, Europe could become a region where over-regulation hampers innovation in AI, creating a landscape where technological progress lags behind other global powers. This possibility underscores the urgent need for the EU to continuously refine its legal framework, ensuring it fosters innovation while protecting ethical standards and societal values.
Authors: Yahya Mohamed Mao (Swiss GRC AG), Michael Widmer (Swiss Infosec AG), January 2024
**Catégories:** Industry News
---
### [GCC GRC Day 2024: Navigating the Complexities of GRC in the Middle East](https://swissgrc.com/fr/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/)
**Published:** mai 27, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The GCC GRC DAY 2024 brought together leading industry experts who engaged in rich discussions about the most pressing GRC challenges, sharing insights and strategies to effectively navigate the complex landscape of governance, risk and compliance (GRC).
**Content:**
**The successful launch of GCC GRC DAY at Conrad Dubai has set a new standard in the field of governance, risk, and compliance within the Middle East, continuing the legacy of the SWISS GRC DAY by adapting it to the regional nuances of the GCC. The insights and strategies shared during the conference are invaluable for anyone involved in the complex world of GRC, ensuring preparedness and proactive management in the face of evolving challenges.**
The inaugural [GCC GRC Day](https://swissgrc.com/en/gccgrcday/) held on May 22, 2024, at Conrad Dubai, marked a pivotal moment for Swiss GRC. This expansion is highlighted by the establishment of a new branch and operational office in Dubai Internet City, UAE, designed to cater specifically to the unique demands of these markets. Swiss GRC has committed significant resources to the region, including investing in a local entity and data center to ensure compliance with operational and regulatory requirements.
The event itself extended the Swiss organization’s renowned conference series, [SWISS GRC DAY](https://swissgrc.com/swissgrcday), previously celebrated in Europe, to a dynamic new audience. This carefully curated conference brought together top-tier professionals from across the Gulf Cooperation Council (GCC) to engage deeply with the core themes of governance, risk, and compliance (GRC).
##### Strategic Initiative and Expert Collaboration
Swiss GRC’s introduction of GCC GRC Day in Dubai underscores its commitment to the unique GRC challenges in the Middle East. In partnership with [GEC Media Group](https://gecmediagroup.com/), the event was designed to facilitate a sophisticated environment for dialogue and knowledge exchange, tailored specifically to the nuanced needs of regional professionals. This collaboration enabled the conference to offer region-specific insights that resonated with attendees, fostering strategic partnerships and enhancing the learning experience. By focusing on localized content, Swiss GRC not only addressed the direct challenges of the Middle Eastern GRC landscape but also reinforced its role as a key influencer in advancing regional GRC practices. Swiss GRC is dedicated to enhancing the expertise of GRC professionals in the Middle East, promoting a deeper understanding of complex compliance issues and encouraging the implementation of best practices across the region.
##### Keynote Addresses and Expert Panels
The GCC GRC Day 2024 kicked off with an insightful keynote address from **Rajeev Dutt**, General Manager MEA and APAC at Swiss GRC, who underscored the critical importance of integrated GRC frameworks in today’s increasingly digital and interconnected business environment. Dutt highlighted the essential need for advanced tools that offer comprehensive visibility into risks, thereby empowering organizations to adapt quickly to regulatory changes and maintain continuous operations amidst potential disruptions.

Following Dutt’s keynote, **Besfort Kuqi**, Co-founder and CEO of Swiss GRC, took the stage to offer an overview of the GRC Toolbox. This segment highlighted Swiss GRC’s commitment to expanding its product offerings in response to the growing demands of its Middle East clientele. Kuqi outlined the introduction of additional modules to the GRC Toolbox, which now includes components ranging from risk management and audit to data protection and internal controls. This expansion has led to the Toolbox comprising 12 integrated modules that provide a robust framework for managing various aspects of governance, risk, and compliance. The enhancement of the GRC Toolbox is particularly tailored to meet the complex needs of both government entities and the private sector within the region. By incorporating these additional modules, Swiss GRC not only strengthens its presence in the MEA & APAC regions but also effectively positions itself to address and mitigate the unique challenges faced by its diverse client base. This strategic development underscores Swiss GRC’s dedication to delivering comprehensive, cutting-edge solutions that enhance the resilience and compliance capabilities of organizations operating in these dynamic markets.

The conference featured an expert panel that brought together leading voices in the field of governance, risk, and compliance. The panel included **Evita Faustina Francis**, Head of Business Resilience for the Middle East and India at Marsh, **Srihari Upadhya**, AGM of IS Risk and Compliance at Aster DM Healthcare, and **Mohamad Gholoom**, Governance and Risk Expert at Ministry of Health and Prevention UAE. This panel delved into several pressing issues facing the GRC community today.
The panelists discussed the impact of emerging technologies like AI and blockchain on GRC frameworks, highlighting both the challenges and opportunities these technologies present. They explored how these advancements could drive more efficient compliance processes and risk management strategies, but also how they necessitate updates to existing frameworks to accommodate new kinds of risks.

Additionally, the importance of cross-functional collaboration was a major theme, with panelists agreeing that breaking down silos within organizations is crucial for effective risk management. They discussed strategies for fostering an organizational culture that promotes ongoing communication and cooperation across departments, which is essential for a holistic approach to GRC. Lastly, the panel addressed the evolving skills required for GRC leaders in this dynamic landscape. They pointed out the need for a combination of technical knowledge and soft skills, such as the ability to navigate complex organizational structures and influence change, which are vital for leading successful GRC initiatives in modern businesses. These discussions provided attendees with a rich tapestry of insights and actionable strategies, reinforcing the importance of staying ahead in the ever-evolving domain of governance, risk, and compliance.
##### Dynamic Participation and Tangible Outcomes
The GCC GRC Day was characterized by its dynamic interactions and the active participation of attendees who engaged in discussions on a variety of topics including cyber security, operational resilience, and strategic business planning. The presentations and panels not only provided insights into current trends and challenges but also offered practical solutions and strategies for navigating the complex GRC landscape.
The event excelled in providing networking opportunities, allowing attendees to forge new connections and strengthen existing ones. These interactions are vital for fostering collaboration and innovation in the field of GRC, with many participants commenting on the invaluable contacts they made during the event.
The GCC GRC Day 2024 set a new benchmark for GRC conferences in the region, effectively addressing the specific needs and challenges faced by Middle Eastern enterprises. The event underscored the growing importance of robust governance, risk management, and compliance strategies in an increasingly complex global market.
As we reflect on the successes and insights garnered during GCC GRC Day 2024, it is evident that such forums are vital for the continuous evolution and effectiveness of GRC practices in the global business arena.
**Catégories:** Events, Industry News
---
### [Chief Risk Officers Outlook 2024: Navigating Risks in a Volatile Landscape](https://swissgrc.com/fr/chief-risk-officers-outlook-2024-navigating-risks-in-a-volatile-landscape/)
**Published:** octobre 15, 2024
**Author:** Faruk Türk
**Excerpt:** The Chief Risk Officers Outlook 2024 published by the World Economic Forum paints a clear picture of an increasingly volatile global landscape. Chief Risk Officers (CROs) are facing unprecedented challenges, from economic instability to rapidly evolving cyber threats.
**Content:**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://swissgrc.com/en/discoverycall/)
**The Chief Risk Officers Outlook 2024, released by the World Economic Forum, paints a clear picture of an increasingly volatile global landscape. Chief Risk Officers (CROs) are facing unprecedented challenges, from economic instability to rapidly evolving cyber threats. As the custodians of organizational resilience, CROs must now think strategically about risk, balancing the need for innovation with the imperative to safeguard against uncertainty. In this blog post, we explore key insights from the report and reflect on the evolving role of risk management in ensuring business sustainability.**
A fractured global landscape: Navigating risk in 2024
The global risk landscape is increasingly characterized by **geopolitical tensions**, **macroeconomic instability**, and **digital vulnerabilities**. According to the report, 96% of risk officers expect ongoing geopolitical disruptions. Regional conflicts, shifting global alliances, and tensions in trade relations are intensifying, creating an unpredictable environment for businesses across sectors.
The global economy continues to be under strain. Rising **inflation**, interest rate hikes, and liquidity challenges are expected to persist well into 2024, with markets still recovering from the shocks of recent years. In this environment, businesses must reassess their growth strategies, seeking out flexibility and resilience in the face of economic turbulence.
One of the most pressing risks is the continued rise of **cyber threats**. With 71% of CROs expecting a surge in criminal cyber activity, businesses find themselves increasingly vulnerable to attacks. The integration of new technologies, particularly artificial intelligence, has expanded the digital footprint of many organizations, increasing the exposure for cyber vulnerabilities.
CROs must now adopt a multifaceted approach to risk management, one that not only addresses these traditional risks but also anticipates emerging threats in the digital and geopolitical arenas.
The external forces shaping corporate strategy
The external risks identified by the report—macroeconomic pressures, cyber threats, and regulatory changes—are pushing businesses to rethink their corporate strategies.
1. **Macroeconomic pressures**: As economies grapple with inflationary pressures and interest rate fluctuations, businesses face tough decisions on investments, operational costs, and growth trajectories. Long-term planning becomes more complex in a world where macroeconomic variables are constantly shifting.
2. **Technological and cyber threats**: The rapid development of AI and other advanced technologies brings new opportunities, but it also heightens the risk of sophisticated cyber-attacks. Companies must now invest in stronger and more efficient cybersecurity measures to protect themselves from these evolving digital threats.
3. **Regulatory scrutiny**: Governments worldwide are tightening regulatory frameworks, particularly around data privacy, AI, and sustainability. For businesses, this means keeping pace with regulatory changes and staying compliant in an ever-evolving environment.
Businesses must view [risk management](https://swissgrc.com/en/risk-management-software/) not as a separate function but as an integral part of their corporate strategy. By staying ahead of macroeconomic trends and regulatory changes, organizations can adapt more quickly and maintain a competitive advantage.
Balancing risk and innovation in a competitive environment
The Outlook 2024 highlights an ongoing tension: the need to innovate while mitigating increasing risks. Many businesses are seeking growth through innovation, particularly in technology, but this comes with heightened risks, including cybersecurity threats and operational disruptions.
In this environment, CROs are tasked with creating frameworks that **balance risk and innovation**. Rather than viewing risk as a barrier to growth, forward-thinking organizations are leveraging risk management as a tool to facilitate innovation. This requires an integrated approach, where risk considerations are embedded in strategic decision-making processes, enabling businesses to pursue growth opportunities while remaining resilient.
Effective risk management should empower innovation. Risk functions need to evolve from being reactive to proactive, ensuring that organizations can innovate with confidence and resilience.
The role of CROs in 2024: From guardians to growth enablers
The role of the Chief Risk Officer is undergoing a transformation. Traditionally seen as protectors or « guardians » of the organization, CROs are increasingly being viewed as **strategic partners**. Their expertise in understanding and mitigating risk is now recognized as a critical component of long-term growth strategies.
The report emphasizes that 95% of organizations expect their risk functions to contribute not just to operational resilience but to **shaping organizational strategy**. This shift reflects a broader realization: risk management isn’t simply about avoiding potential pitfalls; it’s about **creating value** by steering the organization toward opportunities while managing the risks associated with them.
As CROs take on this expanded role, they will need to harness dynamic tools that provide real-time insights into emerging risks. The ability to foresee and act on these risks will position risk management as a driver of innovation and growth, rather than a limitation.
Conclusion and recommendations
The Chief Risk Officers Outlook 2024 provides a critical overview of the risks facing businesses, but managing these risks requires more than just awareness—it demands action. An **integrated approach** to risk management is no longer optional; it’s indispensable in today’s complex environment. Leveraging technology, such as a comprehensive GRC (Governance, Risk, and Compliance) platform, enables organizations to centralize risk data, streamline compliance, and maintain real-time oversight. This holistic view fosters **proactive decision-making**, ensuring that risk management becomes a core part of strategic planning rather than a reactive measure.
At Swiss GRC, we believe that technology, when thoughtfully applied, can transform risk functions from operational safeguards into **growth enablers**. Our GRC Toolbox allows organizations to integrate risk insights across all levels, ensuring alignment between risk management, regulatory compliance, and business objectives. By consolidating these functions into one platform, businesses can anticipate emerging risks, maintain agility, and ensure resilience while pursuing innovation.
As businesses look to the future, embracing an integrated, technology-driven approach will be key to navigating uncertainty with confidence. By combining strategic foresight with robust risk management tools, organizations can turn potential threats into opportunities for sustainable growth.
References
World Economic Forum (2024). Chief Risk Officers Outlook 2024
This report outlines the global risks that CROs anticipate for 2024, including economic instability, cybersecurity threats, and regulatory challenges.
[Link to report](https://www3.weforum.org/docs/WEF_Chief_Risk_Officers_Outlook_2024.pdf)
Informa Connect (2023). The Evolving Role of the Chief Risk Officer
A publicly accessible report that explores the transformation of the CRO role in recent years and their increasing importance as strategic partners.
[Link to report](https://informaconnect.com/uploads/025f4bf7-b07f-469f-b1a9-6a074e064003_RiskMinds365_The_Evoling_Role_of_a-CRO.pdf)
Deloitte (2023). Innovation Risk Management
This report describes how businesses can use risk management techniques to foster innovation and mitigate risks.
[Link to report](https://www2.deloitte.com/us/en/insights/industry/public-sector/public-sector-innovation-risk-management.html)
PwC (2023). Global Digital Trust Insights 2024
PwC provides a comprehensive overview of global cybersecurity threats and their impact on businesses.
[Link to report](https://www.pwc.com/gx/en/news-room/press-releases/2023/digital-trust-insights.html)
**Catégories:** Industry News
---
### [GRC as a Business Enabler: Why Technology is Essential](https://swissgrc.com/fr/grc-as-a-business-enabler-why-technology-is-essential/)
**Published:** novembre 12, 2024
**Author:** Gentian Ajeti
**Excerpt:** At Swiss GRC, we see firsthand how technology transforms GRC into a business asset. Clients in finance, healthcare, and public sectors leverage our software solutions to enhance security, efficiency, and adaptability within their risk landscapes.
**Content:**
**Once seen as mechanisms to fulfill regulatory requirements, Governance, Risk and Compliance (GRC) processes were often managed in silos, leading to inefficiencies, limited visibility, and minimal strategic impact. However, recent insights from sources like McKinsey and Gartner highlight a transformative shift: GRC is no longer merely a regulatory imperative. Today, GRC frameworks—particularly those enabled by software solutions—are transforming into strategic drivers of efficiency, resilience, and competitive advantage, rather than just tools to meet compliance.**
At [Swiss GRC](https://swissgrc.com/en/embedding-risk-in-corporate-dna-lessons-from-ferma-global-risk-manager-survey-report-2024/), we see firsthand how technology transforms GRC into a business asset. Clients in finance, healthcare, and public sectors leverage our software solutions to enhance security, efficiency, and adaptability within their risk landscapes. An effective GRC technology framework empowers companies to transition from reactive, compliance-driven processes to proactive, integrated risk management, aligned with broader business goals. This article explores how advanced GRC technology drives efficiency, informs decision-making, and turns compliance into a strategic advantage.
Breaking down silos and increasing visibility
One of the primary challenges in traditional GRC implementation has been fragmentation. Companies that rely on outdated or manual systems typically manage GRC activities in silos, leading to inefficiencies, duplicated efforts, and limited visibility across the organization. Technology solves these issues by consolidating compliance, governance, and risk data into a centralized platform. This integrated approach not only reduces redundancies but also provides leadership with overall visibility into the organization’s risk landscape.
A research by Forrester reveals that organizations leveraging integrated GRC software make more informed and effective decisions. By providing a unified view of risks and compliance status, GRC platforms empower leaders to proactively identify potential threats, allocate resources efficiently, and address issues before they escalate. In high-compliance industries like financial services, where regulatory demands are particularly intricate, a GRC software is invaluable. It streamlines compliance tracking and auditing across departments, enabling faster response times and enhancing strategic decision-making—ultimately helping institutions navigate regulatory complexities with agility and confidence.
Transitioning from reactive to proactive risk management
Historically, GRC practices have been largely reactive, focusing on compliance and addressing risks only after they arise. GRC technology has shifted this approach by enabling organizations to take proactive measures, identifying and addressing risks before they escalate. The graphic below illustrates key regional trends in the Enterprise Governance, Risk, and Compliance (eGRC) market, with North America leading as the largest market, holding a 30% revenue share as of 2022 (source: Grand View Research). Meanwhile, the Asia-Pacific region is emerging as the fastest-growing market, driven by increasing regulatory complexities and the rising adoption of GRC technology across industries. This global expansion highlights the crucial role of GRC technology in enabling organizations to transition from reactive compliance practices to proactive risk management, supporting resilience and strategic alignment in diverse regulatory environments.

Enterprise Governance, Risk & Compliance (eGRC) Market Growth Trends 2024 (Source: Grand View Research)
Gartner highlights proactive risk management as a hallmark of modern GRC software, enabling organizations to respond to emerging risks with agility and precision. This proactive approach is particularly transformative for industries with frequent regulatory changes, such as insurance. By leveraging GRC technology, insurers can continuously monitor regulatory updates, identify risk trends, and adjust their strategies promptly. This capability not only minimizes financial impact but also promotes resilience and adaptability in highly regulated markets. According to a 2017 [McKinsey report](https://www.mckinsey.com/business-functions/risk-and-resilience/our-insights/the-future-of-risk-management-in-the-digital-era), technology-driven, proactive risk management gives companies a critical advantage in volatile environments, helping them safeguard assets and respond swiftly to evolving risks.
In adapting to complex regulations like the [NIS2 Directive](https://swissgrc.com/en/network-information-security-directive-nis2/) and the [Digital Operational Resilience Act (DORA)](https://swissgrc.com/en/digital-operational-resilience-act-dora/), GRC technology enables companies across high-compliance industries to respond efficiently to these emerging regulatory demands:
- **Financial services:** GRC platforms support multi-jurisdictional compliance, reducing human error and centralizing tracking of AML standards and regulatory requirements, thereby improving strategic decision-making.
- **Insurance:** GRC software provides a centralized system for managing compliance with regulations like Solvency II, while predictive analytics helps detect fraud, monitor updates, and proactively adjust policies to protect financial health.
- **Healthcare:** Advanced GRC technology consolidates compliance data, enabling real-time updates and continuous tracking of HIPAA and GDPR requirements, ultimately reducing audit time and data breach risks.
- **Public sector:** Government entities use GRC technology to enhance transparency, centralize data, and improve accountability, supporting efficient resource allocation and fostering public trust.
As regulatory demands around cybersecurity and operational resilience grow, GRC platforms offer centralized data management, real-time risk assessment, and automated compliance tracking. This not only helps companies stay compliant but also enhances resilience, turning risk management into a source of value that supports growth and strategic alignment across industries.
Conclusion: Turning GRC into a driver of strategic value
As illustrated by today’s dynamic industry examples, GRC is no longer simply about compliance. An integrated GRC framework empowers organizations to enhance transparency, streamline critical processes, and align risk management with overarching business goals. These shifts make GRC an indispensable tool for navigating today’s complex business landscape, characterized by evolving risks, emerging regulatory mandates, and the heightened expectations for cybersecurity and operational resilience.
With new regulations such as the **NIS2 Directive** and **Digital Operational Resilience Act (DORA)** reshaping compliance requirements, adopting advanced GRC technology has become essential for any organization aiming to maintain a competitive edge. GRC platforms not only support regulatory adherence but also enable companies to anticipate risks, leverage predictive analytics, and make more agile, data-driven decisions that drive long-term resilience and success. These capabilities allow organizations to stay ahead of risks, adapt rapidly to regulatory shifts, and ultimately create business value through compliance—a transformation that was previously challenging with traditional, siloed risk management practices.
At Swiss GRC, we understand the current regulatory landscape and the pressures organizations face across sectors. Our expertise lies in designing GRC solutions that integrate seamlessly with existing operational frameworks, supporting proactive risk management and fostering sustainable growth. By empowering clients with real-time insights, predictive analytics, and centralized compliance monitoring, we enable them to harness GRC as a business enabler that aligns with strategic objectives. Our advanced solutions are developed to enhance not only compliance but also adaptability, security, and operational efficiency—capabilities crucial to thriving in today’s regulatory climate.
Whether your organization operates in finance, insurance, healthcare, the public sector, or another sector, our GRC solutions empower you to turn compliance into a source of competitive advantage. We’re constantly updating our platform to ensure they align with the latest regulatory changes and industry best practices, allowing our clients to remain resilient and forward-looking. [Reach out to Swiss GRC](https://swissgrc.com/en/discoverycall/) to learn how we can help you leverage GRC as a driver of strategic value in today’s increasingly complex and dynamic business environment.
**Catégories:** Industry News
---
### [FINMA Risk Monitor 2024: Addressing Cyber Threats and Market Volatility](https://swissgrc.com/fr/finma-risk-monitor-2024-addressing-cyber-threats-and-market-volatility/)
**Published:** décembre 6, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Switzerland's financial sector is under considerable pressure from an increasingly complex and interconnected risk landscape. The FINMA Risk Monitor 2024 has identified several risks facing financial institutions, from rising cyber threats and geopolitical tensions to ongoing vulnerabilities in the real estate market.
**Content:**
**Switzerland’s financial sector is under considerable pressure from an increasingly complex and interconnected risk landscape. The Swiss Financial Market Supervisory Authority (FINMA) Risk Monitor 2024 has identified several risks facing financial institutions, from rising cyber threats and geopolitical tensions to ongoing vulnerabilities in the real estate market. This report is a clear call to action, urging financial institutions to prioritize resilience in the face of mounting uncertainties.**
The findings of the report come at a pivotal time. Cyberattacks are on the rise, particularly against smaller financial institutions, with their frequency and sophistication growing year over year. Vulnerabilities in the real estate market, heightened by structural changes such as remote work, continue to pose systemic risks. Meanwhile, navigating international sanctions and combating money laundering are becoming ever more challenging in today’s volatile geopolitical climate. Against this backdrop, financial institutions must adopt an integrated and forward-looking approach to ensure both compliance and resilience.
Understanding the Risk Landscape
The [FINMA Risk Monitor 2024](https://www.finma.ch/en/~/media/finma/dokumente/dokumentencenter/myfinma/finma-publikationen/risikomonitor/20241118-finma-risikomonitor-2024.pdf?sc_lang=en&hash=1EABA096CB06AABA7CFDC5F7AB64260F) highlights the following key risks that demand immediate attention from financial institutions:
1. **Real Estate and Mortgage Risks:** Persistent vulnerabilities in the real estate market, including risks of overheating and structural shifts like remote work, affecting both residential and commercial properties.
2. **Credit Risks:** Broader credit risks beyond mortgages, particularly in non-mortgage loan segments, exacerbated by economic uncertainties and inflationary pressures.
3. **Market Risk – Credit Spread Risk:** Volatility in credit spreads can lead to devaluations in fixed-income portfolios, posing significant risks to financial stability.
4. **Liquidity and Funding Risks:** Sudden market disruptions or reliance on short-term funding expose institutions to potential liquidity crises.
5. **Cyber Risks:** A significant rise in cyberattacks across all categories, with smaller institutions experiencing the sharpest increase.
6. **Sanctions Compliance:** Geopolitical tensions increase the complexity of navigating international sanctions, requiring enhanced compliance efforts.
7. **Money Laundering Risks:** As financial crime methods evolve, institutions face heightened expectations for AML frameworks to prevent and detect illicit activities.
8. **Outsourcing Risks:** The reliance on [third-party](https://www.swissgrc.com/en/tprm-software) providers for critical functions introduces operational, data security, and compliance risks that require careful management.
9. **Market Access Challenges:** Geopolitical shifts and regulatory changes threaten institutions’ ability to maintain seamless access to international markets.
These risks are interrelated, creating a compounded challenge for financial institutions. Addressing them requires not just compliance with regulatory frameworks but a proactive and integrated approach to risk governance.
The GRC Perspective: Turning Challenges into Opportunities
The risks outlined in the FINMA Risk Monitor 2024 may appear daunting, but they also present financial institutions with an opportunity to transform their approach to [governance, risk, and compliance (GRC)](https://swissgrc.com/en/grc-as-a-business-enabler-why-technology-is-essential/). By leveraging robust and integrated GRC frameworks, institutions can not only address these risks effectively but also turn them into strategic advantages. This perspective emphasizes a shift from reactive compliance to proactive resilience and adaptability.
**Integrated Risk Management: Gaining a Centralized View**
One of the most pressing challenges for financial institutions is the fragmented nature of [risk management](https://swissgrc.com/en/risk-management-software/). Cyber threats, real estate vulnerabilities, credit exposures, and regulatory compliance often operate in silos, making it difficult to gain a comprehensive understanding of risk exposure. A cohesive GRC framework can change that dynamic by integrating risk data into a single, centralized platform. This holistic view allows institutions to identify, monitor, and address risks in real time, enhancing decision-making and reducing the likelihood of blind spots. With integrated dashboards and analytics, decision-makers can prioritize risks and allocate resources more effectively, aligning their actions with both regulatory expectations and strategic goals.
**Compliance Automation: Meeting Regulatory Demands with Precision**
As geopolitical tensions drive evolving sanctions and anti-money laundering (AML) requirements, compliance has become increasingly complex. Manual processes, once the norm, are no longer sufficient to keep pace with rapidly changing regulatory frameworks. GRC tools powered by advanced automation can ensure institutions remain compliant without overburdening their resources. Such automation not only reduces the risk of non-compliance but also enhances operational efficiency, freeing up resources to focus on strategic priorities.
**Resilience Building: Preparing for the Unpredictable**
The interconnected nature of today’s risks—ranging from geopolitical tensions to market disruptions—makes resilience a critical capability. Predictive analytics and scenario planning, key components of modern GRC platforms, allow institutions to anticipate potential disruptions and prepare accordingly. By embedding these tools into their risk management practices, institutions can navigate uncertainty with confidence, ensuring business continuity and safeguarding stakeholder trust.
The Growing Cybersecurity Challenge
The sharp rise in cyberattacks, as highlighted in FINMA’s report, underscores the urgent need for institutions to prioritize cybersecurity. Smaller institutions, categorized as category 5, have been particularly vulnerable, experiencing the highest increases in reported incidents between 2020 and 2024. This trend aligns with global patterns, where attackers target less-resourced entities, often exploiting gaps in defenses.

The chart above illustrates the progression of reported cyberattacks across supervisory categories over the last four years. Notably, category 5 institutions have seen a steep rise, indicating that attackers are focusing on entities perceived to have fewer resources or less robust defenses. This trend is a stark reminder of the need for comprehensive cybersecurity strategies across all segments of the financial sector.
The consequences of a successful cyberattack extend far beyond financial losses. Operational disruptions, data breaches, and reputational damage can undermine trust in an institution and, by extension, the broader financial system. Addressing these risks requires a multi-pronged approach:
- **Robust Cybersecurity Frameworks**: Institutions must integrate cybersecurity into their broader GRC strategies, ensuring alignment with regulatory expectations and industry best practices.
- **Incident Response Planning**: Effective response plans can minimize downtime and mitigate the impact of an attack.
- **Continuous Monitoring**: Real-time tools that detect and respond to threats are essential for staying ahead of increasingly sophisticated attackers.
The upward trend in cyber incidents is a wake-up call for the sector. Institutions must treat cybersecurity as a core pillar of their risk management strategy, ensuring that they are well-equipped to protect both their operations and their stakeholders’ trust.
Conclusion: Adapting to a Dynamic Risk Landscape
Switzerland’s financial institutions have long been recognized for their stability and innovation. However, maintaining this leadership position requires a commitment to evolving with the risk landscape. The FINMA Risk Monitor 2024 serves as a call to action for Swiss financial institutions. The interconnected risks of today—cyber threats, geopolitical uncertainties, and market vulnerabilities—require a strategic and integrated response. Institutions must move beyond compliance to embrace GRC frameworks that enable agility, resilience, and long-term success.
As the challenges intensify, so do the opportunities. By investing in GRC solutions, financial institutions can not only meet regulatory expectations but also secure their competitive edge. To explore how integrated GRC solutions can help your institution thrive in this dynamic environment, [**reach out to Swiss GRC**](https://swissgrc.com/en/discoverycall/). Together, we can turn challenges into opportunities and build a resilient future for Switzerland’s financial sector.
**Catégories:** Industry News
---
### [Basel III from 2025: What the Finalization Means for Banks](https://swissgrc.com/fr/basel-iii-from-2025-what-the-finalization-means-for-banks/)
**Published:** décembre 12, 2024
**Author:** Gentian Ajeti
**Excerpt:** The final Basel III standards bring significant innovations, particularly in the area of operational risks and loss data analysis. These reforms not only strengthen the stability of the Swiss financial center, but also promote a modern risk culture and create the basis for sustainable resilience.
**Content:**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://swissgrc.com/en/discoverycall/)
**The final Basel III standards will come into force in Switzerland on January 1, 2025, as announced in a recent [press release from the Federal Department of Finance (FDF)](https://www.admin.ch/gov/de/start/dokumentation/medienmitteilungen.msg-id-99067.html).**
The amendment to the Capital Adequacy Ordinance (CAO) implements the final component of this comprehensive reform, which aims to make the banking system more resilient and enable a more transparent calculation of capital adequacy. The final Basel III standards bring significant innovations, particularly in the area of operational risks and loss data analysis. These reforms not only strengthen the stability of the Swiss financial center, but also promote a modern risk culture and create the basis for sustainable resilience in an increasingly digital financial environment.
Looking back: The development of Basel III
The Basel III reforms were developed in response to the 2008 financial crisis in order to eliminate weaknesses in the banking system. The aim was to tighten capital and liquidity requirements and minimize systemic risks. Since their introduction in 2010, the Basel III standards have been implemented in stages, with the final phase – postponed until 2025 due to the pandemic – concluding the reform process.
The most important changes in the final phase concern:
- **Restriction of internal models:** The use of internal models to calculate own funds is regulated by the introduction of an output floor. This means that capital requirements based on internal models may not be less than 72.5% of the standardized calculations.
- **Standardized approaches for operational risks: The Standardized Measurement Approach (SMA)** replaces the previous models and makes loss data a central element of the calculation. In future, capital requirements will be based more on the banks’ loss histories and business indicators.
These changes are intended to increase the transparency and stability of the banking system. At the same time, they will encourage banks to modernize their [risk management systems](https://swissgrc.com/en/risk-management-software/) and address systemic weaknesses in a targeted manner.
New requirements for loss data: Focus on operational risks
Operational risks have been an established part of the regulatory framework since Basel II, but the final Basel III standards, which will come into force from 2025, will significantly specify this area. Central to this is the recording and use of loss data (“loss events”), which form a crucial basis for calculating capital requirements in accordance with the new **Standardized Measurement Approach (SMA)**.
The requirements for loss databases will therefore be significantly tightened by the final Basel III standards. In addition to recording historical loss events, the new standard also requires the proactive use of this data in risk management. This offers banks the opportunity to take preventative measures and systematically minimize recurring problems.
The following aspects in particular are coming into focus:
- **Quality and scope:** Banks must significantly expand their loss databases in order to record detailed information on financial effects, causes and accompanying measures.
- **Uniform standards:** Comparability and validity of the data are ensured by clear guidelines for collection and management.
- **Integration of new risks:** In addition to traditional loss data, new types of risks such as cyber risks and [third-party problems](https://swissgrc.com/en/tprm-software/) are gaining in importance.
The final Basel III standards also require the consideration of cyber risks, which are becoming increasingly important in light of growing digitalization. FINMA emphasizes that such scenarios must be integrated into loss data and risk models.
Significance for the Swiss financial center
By amending the Capital Adequacy Ordinance, Switzerland is not only implementing international standards, but also strengthening the stability of its banking system. The Federal Department of Finance emphasizes that the changes are intended to increase transparency and promote the resilience of the financial centre. On average, there will be no significant changes to capital requirements. However, the requirements could increase for larger institutions, making targeted adjustments necessary.
While the new Basel III requirements will undoubtedly entail additional work for banks, they also offer opportunities to optimize systems and processes. In particular, they enable institutions to:
1. **Improved risk transparency:** By systematically collecting and analyzing loss data, banks gain a clearer insight into their risk landscape. This strengthens their ability to take preventive measures and ensure long-term stability.
2. **Standardization and comparability:** The new requirements create a basis for standardized calculation approaches, which meets both regulatory requirements and the expectations of international investors.
3. **Strategic resilience:** The integration of new types of risk such as cyber attacks or third-party problems strengthens banks’ resilience to external shocks.
Recommended actions for banks
The final Basel III standards present banks with new challenges, but also offer them the opportunity to optimize their risk management and strengthen their resilience. As an integral part of the Swiss financial center, it is crucial not only to meet these requirements, but also to use them as an opportunity for strategic development. Banks should use the remaining time until implementation to align their systems and processes with the new requirements in a targeted manner. The following steps are of particular importance here:
- **Checking the loss databases:** Is all relevant data complete, of high quality and standardized? A robust database is essential in order to meet regulatory requirements and make well-founded decisions.
- **Integration of new risks:** Banks should ensure that cyber risks and third party issues are systematically integrated into their models. This requires close coordination between the risk management and IT departments.
- **Raising awareness and training:** Employees should be trained in the new requirements and prepared to use new tools. Regular workshops and training courses increase awareness of new risks.
- **Technological adaptations:** Investments in modern GRC (Governance, Risk, and Compliance) technology can create decisive competitive advantages. Tools such as the GRC Toolbox, which are specifically designed to record and analyze loss data, enable efficient implementation of regulatory requirements.
The Basel III standards are more than just a regulatory hurdle – they are an opportunity to actively shape the future of the banking system. If you would like to find out more about the new requirements or need support in adapting your processes, [reach out to our experts](https://swissgrc.com/en/discoverycall/).
**Catégories:** Industry News
---
### [Global Risks Report 2025: A GRC perspective on the World Economic Forum’s Insights](https://swissgrc.com/fr/global-risks-report-2025-a-grc-perspective-on-the-world-economic-forums-insights/)
**Published:** janvier 21, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** The annual Global Risks Report offers a comprehensive view of the challenges shaping our future. The 2025 edition, marking two decades of global risk tracking, highlights the interconnected nature of today’s most pressing issues—from geopolitical tensions and environmental crises to technological vulnerabilities.
**Content:**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://swissgrc.com/en/discoverycall/)
**The annual Global Risks Report by the World Economic Forum is one of the most anticipated publications for leaders across industries, offering a comprehensive view of the challenges shaping our future. The 2025 edition, marking two decades of global risk tracking, highlights the interconnected nature of today’s most pressing issues—from geopolitical tensions and environmental crises to technological vulnerabilities.**
For businesses, governments, and institutions, this era of heightened volatility underscores the critical role of governance, risk, and compliance (GRC). GRC frameworks enable businesses to move beyond reactive measures, offering the tools to anticipate risks, navigate uncertainties, and adapt to evolving challenges with agility. At Swiss GRC, we review this report with great interest each year, providing a summary and perspective to help organizations understand these risks through the lens of GRC. This article explores the key findings from the report, offering insights for leaders seeking resilience in an unpredictable world.
The State of Risk in 2025
The 2025 report outlines a global environment where risks are not just escalating but are deeply interconnected. The interplay of geopolitical conflicts, environmental crises, and technological vulnerabilities highlights the need for a systemic, proactive approach to governance and risk management. For businesses and leaders, these risks are both a warning and a call to action. Here are the most pressing themes shaping the global outlook:

**1. Geopolitical Fragmentation and Economic Tensions**
The report’s findings highlight a world divided. State-based armed conflict has surged to the top of immediate global concerns, reflecting a deteriorating geopolitical environment driven by unresolved tensions and waning multilateral cooperation. Meanwhile, **geoeconomic confrontation**—manifesting through trade wars, sanctions, and resource nationalism—is creating new fault lines in the global economy.
For organizations, this geopolitical volatility is more than a headline; it’s a call to action. Businesses operating across borders face an increasingly fragmented regulatory landscape, where compliance isn’t just about avoiding fines—it’s about maintaining trust and continuity. Integrated GRC frameworks provide the tools to track and adapt to evolving regulations, helping organizations mitigate risks and protect their operations.
**2. Environmental Risks: From Future Concerns to Present Realities**
Environmental risks have been a consistent theme in the Global Risks Report for years, but their urgency has reached new heights. From extreme weather events to biodiversity loss and pollution, the effects of environmental degradation are no longer just long-term challenges—they’re immediate crises with cascading impacts. For businesses, this is a moment to rethink sustainability not as a “nice-to-have” but as a core component of risk management. **Environmental, Social, and Governance (ESG)** initiatives are increasingly integrated into GRC systems, enabling organizations to not only comply with regulations but also to lead on sustainability and resilience.
**3. Cybersecurity and Technological Vulnerabilities**
The digital frontier presents unparalleled opportunities—but also unprecedented risks. This year’s report underscores the challenges:
- **Supply Chain Risks**: 54% of Fortune 500 companies identify supply chain vulnerabilities as a critical challenge.
- **AI Preparedness Gap**: While 66% see AI transforming cybersecurity, only 37% feel prepared to secure these tools.
- **Cyber Skills Shortages**: Two-thirds of organizations report critical talent gaps in their cybersecurity teams.
Cybersecurity is no longer an IT issue; it’s a governance priority. GRC systems enable organizations to address these vulnerabilities by embedding cybersecurity governance into broader risk management strategies. From regulatory compliance to real-time threat assessment, a robust GRC framework is key to navigating the digital age securely.
**4. The Role of Technology in Misinformation and Polarization**
Generative AI, while transformative, has exacerbated the spread of misinformation—a top-ranked risk for 2025. Frontier technologies like biotechnology also remain underappreciated risks, with their impacts expected to grow significantly over the next decade. Organizations that proactively integrate emerging risks into their GRC frameworks are better positioned to navigate these challenges. Monitoring technological risks and ensuring compliance with evolving regulations are essential for staying ahead in an era of rapid innovation.
The GRC Imperative: Building Resilience in a Fragmented World
The **Global Risks Report 2025** highlights a critical insight: today’s challenges are deeply interconnected, requiring systemic and forward-looking solutions. Governance, risk, and compliance (GRC) frameworks are essential for navigating this complexity, enabling organizations to:
- **Connect Risks**: Unify perspectives across geopolitical, environmental, and technological domains for more effective decision-making.
- **Simplify Compliance**: Manage regulatory complexity across fragmented jurisdictions through integrated systems.
- **Enhance Third-Party Risk Management (TPRM)**: [Mitigate vulnerabilities in supply chains and external partnerships](https://www.swissgrc.com/en/tprm-software), a growing priority in an era of cyber threats and regulatory pressures.
- **Drive Strategic Resilience**: Embed adaptability and foresight into decision-making processes to respond proactively to volatility.
GRC frameworks provide a robust foundation for organizations to navigate uncertainty, strengthen resilience, and lead with confidence in a fragmented world.
Two Decades of Insights: Lessons for Today
The **Global Risks Report 2025** offers more than a catalogue of challenges—it serves as a wake-up call for decisive, forward-thinking leadership. Over the past two decades, risks once considered long-term—like climate change and technological disruption—have become immediate threats. Addressing these interconnected challenges demands a shift from reactive responses to proactive governance.
Organizations that embrace integrated **governance, risk, and compliance (GRC)** frameworks are better positioned to navigate this complexity. By linking compliance, risk management, and strategic decision-making, GRC empowers businesses to move beyond crisis management, build resilience, and seize opportunities in a volatile world.
The future will be shaped by leaders who can see beyond the risks to the opportunities they present. For those ready to lead, adapt, and innovate, the time to act is now.
**Catégories:** Industry News
---
### [FINMA on Artificial Intelligence: Widespread Use, Limited Governance](https://swissgrc.com/fr/finma-on-artificial-intelligence-widespread-use-limited-governance/)
**Published:** avril 25, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Artificial intelligence has arrived in the financial sector - but according to FINMA, there is often a lack of clear governance. This article shows why institutions need to act now to manage risks, meet regulatory requirements, and integrate AI into their governance for the long term. Responsibility begins with a structured approach.
**Content:**
**With its latest survey, FINMA has issued a clear signal: Artificial Intelligence (AI) has become a firmly embedded part of day-to-day operations in the Swiss financial market – particularly within banks and insurance companies. It’s most commonly used for process optimisation, claims handling, front-office tasks, and risk management. The spectrum ranges from rule-based systems to self-learning models that increasingly influence decisions.**
Progress is evident – but uneven. While technological innovation moves ahead and initial use cases go live, governance often lags behind. [FINMA](https://www.finma.ch/en/news/2025/04/20250424-mm-umfrage-ki/) is direct in its assessment: Many institutions lack [clear internal frameworks](https://swissgrc.com/en/ai-grc/), responsibilities are undefined, and the implications of AI on risk exposure, accountability, and regulatory compliance are not being addressed in a structured way.
The result is a structural gap – between technological potential and institutional control. AI is being deployed, but often without formal integration into organisational oversight. Control mechanisms are fragmented, reactive, or siloed within specific departments, with little alignment to overarching [GRC structures](https://swissgrc.com/en/solutions/). This poses significant operational, reputational, and regulatory risks, particularly for critical use cases.
Widespread Adoption, Limited Structure
Despite the growing use of AI, many institutions still lack a comprehensive management model. According to FINMA, around 50% have embedded AI into an explicit strategy – yet implementation remains inconsistent. Existing governance frameworks typically focus on data protection, cybersecurity, or data management, while specific challenges related to algorithmic systems – such as explainability, bias, or automation risks – are often overlooked.
The following chart from the FINMA report illustrates which areas AI is currently being used in – with banks leading the way, and a strong concentration in process optimisation and broadly defined “Other Applications”.

**Chart:** Number of AI applications by area and type of institution. Source: 187 institutions with approved AI use cases.
This broad and partly undefined pattern of use highlights the pressing need for a structured, institution-specific AI governance framework – one that goes beyond IT or data protection, and addresses the full organisational, ethical, and regulatory dimensions of AI.
Governance Is Not Optional – It’s Fundamental
FINMA has made it clear: it is closely monitoring how institutions handle AI and will increasingly factor this into its supervisory activities. At the same time, the upcoming [EU AI Act](https://swissgrc.com/en/the-eus-ai-dilemma-innovation-or-over-regulation/) is set to introduce a binding regulatory framework – one that will also affect Swiss companies with cross-border operations.
In this evolving landscape, organisations face critical questions:
- How can AI-related risks be identified and managed at an early stage?
- How can AI be embedded into existing GRC structures?
- How can transparency and auditability be ensured for AI-driven decisions?
- How can regulatory requirements be met in a fast-moving environment?
These are not just technical questions. They go to the heart of organisational control and must therefore be addressed at the management level.
An Integrated Approach: Swiss GRC and AI Governance
At Swiss GRC, we’ve long been focused on how governance structures must evolve to keep pace with technological developments. In our view, AI does not require a separate governance world – it needs to be embedded into existing enterprise control systems.
Swiss GRC’s [**AI GRC Module**](https://swissgrc.com/en/ai-grc/) is a fully integrated component of our established **GRC Toolbox**, and works seamlessly with:
- Enterprise Risk Management
- Internal Control System (ICS)
- Business Continuity Management (BCM)
- Third Party Risk Management (TPRM)
- Data Protection & Information Security (ISMS)
- Internal Audit
This integrated approach provides a **360-degree view of AI-related risks** – methodologically robust, practically tested, and fully aligned with current and upcoming regulatory frameworks.

**Abbildung:** Dashboard des AI GRC Moduls in der GRC Toolbox
Conclusion: Use AI – But Keep It Under Control
The FINMA survey makes one thing clear: AI is already in widespread use – but governance has not caught up. The challenge is real: AI deployment is accelerating, but risk management, control mechanisms, and oversight structures are not developing at the same pace. This creates a tension between technological advancement and corporate accountability – with potential consequences for system integrity, regulatory compliance, and trust in automated decision-making.
**Now is the time to rethink governance** – not as an afterthought, but as a strategic foundation for secure, transparent, and future-ready AI implementation.
Swiss GRC helps organisations establish exactly this foundation: integrated, practice-oriented, and seamlessly connected to their existing GRC structures.
**Curious how AI Governance could look in your organisation?**
Book a conversation with our expert team today. [**Schedule a meeting**](https://swissgrc.com/en/discoverycall/).
**Catégories:** Industry News
---
### [Review of SWISS GRC DAY 2025: GRC as a strategic compass in dynamic times](https://swissgrc.com/fr/review-of-swiss-grc-day-2025-grc-as-a-strategic-compass-in-dynamic-times/)
**Published:** mai 19, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** The SWISS GRC DAY 2025 has once again proven that Governance, risk, and compliance are key building blocks for resilience, innovative strength, and sustainable corporate management, not mere control mechanisms. In a world of constant change, we need responsible structures that create clarity, enable collaboration, and actively shape change, not just checkbox compliance.
**Content:**
**SWISS GRC DAY 2025, which took place on May 14 at the Radisson Blu Hotel at Zurich Airport, was once again one of the most important conferences for governance, risk and compliance (GRC) professionals. With participants from the entire DACH region, the event impressively underlined how crucial resilience, proactive management and responsible innovation have become for sustainable corporate governance.**
The focus was on the role of GRC as a strategic enabler – far beyond traditional compliance aspects. The participants not only gained insights into current challenges and developments, but also discussed in practical terms how GRC structures, new technologies and a strong risk culture can support organizations in a dynamic world.

**Besfort Kuqi**, CEO and co-founder of Swiss GRC AG, opened the event with a clear appeal: GRC is not a control instrument, but a management system that makes companies more resilient, agile and capable of acting. He emphasized the importance of controllability, adaptability and a robust structure as the cornerstones of a future-oriented understanding of GRC.
His special thanks went to the Swiss GRC team for the organization of the SWISS GRC DAY 2025 as well as to the partners SecurityScorecard, Swiss Infosec, CRIF, Securix, Drata and the Lucerne University of Applied Sciences and Arts (HSLU) for their support.
**Historical example as a timeless lesson**
Nikolai Tsenov, Head Strategy & Business Development at Swiss GRC and moderator of the event, took the participants on an impressive journey back to the year 1755. On November 1, a massive earthquake, followed by a tsunami and days of fires, destroyed large parts of Lisbon. Within minutes, tens of thousands of people lost their lives and 85% of the city lay in ruins. While the Portuguese king froze, Prime Minister Marquês de Pombal resolutely took the lead. He organized evacuations, emergency supplies and reconstruction – with a clear plan, innovative approaches and a pragmatic approach to decision-making. Under his leadership, new building regulations, industrial mass production of construction elements and the first approaches to state-controlled education and scientific disaster research were developed. His famous quote: « What now? Let’s bury the dead and look after the living. » – is emblematic of a resilient, proactive attitude.
Tsenov’s conclusion: even in today’s GRC world, proactive thinking, innovative strength, strategic management and adaptability are decisive success factors – especially in times of uncertainty and complexity.

With a large number of top-class presentations, the SWISS GRC DAY 2025 offered a multifaceted program that impressively combined theory, strategy and practical implementation. The speakers brought in different perspectives from business, law, technology and public institutions – and made it clear that effective GRC is far more than the sum of its parts. The spectrum of topics ranged from real-life crisis scenarios and cyber risks in supply chains to the ethical management of AI, providing not only food for thought but also concrete impetus for action.
**From risk to crisis: The day Swiss airspace came to a standstill – Crisis management at first hand – Christian Weiss, Head Enterprise Risk, Skyguide**
Christian Weiss provided an exclusive insight into the real-life crisis scenario of a complete airspace shutdown over Switzerland – caused by a system failure. He described in detail the escalation dynamics from a recognized risk to a tangible crisis and explained how control was quickly regained through structured decision-making processes, predefined roles and emergency plans.

He particularly emphasized the relevance of a crisis-proof governance structure, forward-looking scenario planning and transparent communication with authorities, airlines and the public, and made it clear how an identified risk can develop into a real crisis within a very short space of time. He demonstrated in a practical way how crisis organization, clear communication and trained interaction between all players are crucial – not just in an emergency, but already in the preparation phase.
**> [Link](https://swissgrc.com/wp-content/uploads/2025/05/Swiss-GRC-Day-Vom-Risiko-zur-Krise-V1.0.pdf) to the presentation**
**Out of nowhere: cyber threats in the supply chain – and how to protect against them – Marc Etienne Cortesi, Group Chief Information Security Officer (CISO), Baloise Group**
Marc Etienne Cortesi used a specific cyber attack on an IT service provider of Baloise to show how external dependencies can become systemic threats. He presented the challenges in terms of transparency along digital supply chains and illustrated how the NIST Cyber Supply Chain Risk Management (C-SCRM) framework can help to prioritize suppliers, monitor risks in a targeted manner and build resilience through clear processes and well thought-out contract design. The presentation emphasized that cyber security is no longer just a technical task, but increasingly a strategic management task.

Using a real-life incident, Cortesi impressively demonstrated how often underestimated vulnerabilities in modern supply chains can become entry points for cyberattacks – and how important it is to ensure transparency, prioritization and resilience along the value chain with the right framework (NIST C-SCRM).
**> [Link](https://swissgrc.com/wp-content/uploads/2025/05/2_Marc-Ettiene-Cortesi_BALOISE_2025-05-14-Swiss-GRC-Day.pdf) to the presentation**
**Artificial intelligence (AI) in the GRC world: use cases and where the journey is heading – Marinela Bilic-Nosic, Partner – Regulatory, Risk & Compliance Transformation, EY in Germany**
Marinela Bilic-Nosic showed how artificial intelligence (AI) is already transforming GRC processes today – for example through the automation of internal controls, the analysis of large amounts of data in monitoring or the use of generative AI for regulatory monitoring. However, she emphasized that the use of agent-based AI also requires a rethink of governance issues: clear guidelines, ethical frameworks and sharpened role models are necessary to ensure trust, effectiveness and security.

She advocated organization-wide governance models with defined risk and responsibility allocation. and challenges when using artificial intelligence in the GRC context. She emphasized that agent-based AI is increasingly making autonomous decisions and therefore needs a sustainable ethical and regulatory framework. In her view, the establishment of clear responsibilities and governance structures is crucial for trustworthy AI applications.
**Governance and risk management for artificial intelligence – a balancing act between innovation and control – David Rosenthal, Team Head / Partner, VISCHER AG**
David Rosenthal analyzed the increasing complexity of regulatory requirements in the context of AI – particularly in light of the EU AI Act. He showed how companies can use a staged, risk-based approval process and trained decision-makers in the first line to ensure legally compliant yet innovation-friendly implementation.

Using specific case studies, for example from the insurance sector, he illustrated how pragmatic governance processes can create trust, minimize legal risks and at the same time enable innovation potential. and clear, practical approval processes, the balancing act between innovation and regulation can be achieved. His approach: governance as an enabler, not a stumbling block – provided that the first line of defense is trained, processes are tiered and responsibilities are clearly defined.
**> [Link](https://swissgrc.com/wp-content/uploads/2025/05/4_David-Rosenthal_VISCHER_KI-Innovation-und-Governance.pdf) to the presentation**
**End-to-end assurance: How internal audit and GRC work together and create added value – Marc Gröflin, Head of Internal Audit, Swiss National Bank (SNB)**
Marc Gröflin highlighted the role of internal audit as an integral part of an overarching assurance model. He showed how an efficient, redundancy-free assurance landscape can be created through coordinated audit plans, methodological consistency and close cooperation with risk management, ICS and compliance.

His presentation focused on specific practical examples from the SNB, which illustrated how trust, transparency and impact can be increased through structured coordination and a shared understanding of risk. He also explained how end-to-end assurance can only succeed if internal audit, compliance and risk management work closely together. The basis for this is a consistent understanding of terms, coordinated audit plans and a respectful dialog between the lines.
**> [Link](https://swissgrc.com/wp-content/uploads/2025/05/SwissGRC-Day-2025-Wie-die-IR-und-GRC-zusammenarbeiten-Final.pdf) to the presentation**
**Culture as an enabler: The invisible force for effective risk management and compliance – with real examples – Sandra Middel, Chief Ethics and Compliance Officer, Axpo Group**
In her presentation, Sandra Middel emphasized that a strong GRC culture is not created by policies, but by living values in everyday life – especially at management level. She used examples to show how organizations can create an environment in which responsibility, transparency and risk awareness are promoted through targeted cultural work, empowerment of employees and a clear attitude in communication.

Culture is not a soft factor, but the decisive lever for the long-term effectiveness and acceptance of GRC measures: An effective GRC culture is not created on paper, but through daily behavior. Especially in management, role models are needed who live integrity, create transparency and take responsibility. This is the only way to anchor risk awareness in the organization in the long term.
**Thank you very much and see you again:** At the end of the event, moderator Nikolai Tsenov thanked all the speakers, partners and the committed participants for their interest, their contributions and the inspiring discussions. The day provided numerous impulses for the GRC practice of tomorrow and produced key insights:
- **Resilience can be shaped:** organizations must learn not only to react to crises, but also to systematically prepare for them.
- **GRC is not an end in itself:** governance, risk and compliance contribute to a company’s success when they are strategically conceived and put into practice.
- **Technology needs responsibility:** the use of artificial intelligence requires clear ethical guidelines and reliable governance structures.
- **Cooperation is crucial:** internal audit, risk management, compliance and operational areas must work together more closely than ever.
- **Culture as a foundation:** Integrity, transparency and responsibility are the cornerstones of any sustainable GRC culture.
The SWISS GRC DAY 2025 has once again proven that Governance, Risk and Compliance are not mere control mechanisms, but central building blocks for resilience, innovative strength and sustainable corporate management. In a world of constant change, what is needed is not checkbox compliance, but responsible structures that create clarity, enable collaboration and actively shape change. With openness to new approaches, the courage to change and a strong foundation of responsibility and trust, GRC is more than ever a key to future viability.
### **Photo Gallery**
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01716-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01699-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01215-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01186-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01167.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC00405-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC00404.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC00397-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC00362-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC00236-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/C0492.00_00_38_88.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC00308-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/C0492.00_00_41_81.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC00220-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC02054-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC02033-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01740-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01737-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01718-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01219-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01649-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01659-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/05/DSC01681-1.jpg)
**Catégories:** Events, Industry News
---
### [Looking back on our 2025 summer event: Montreux as a place for exchange, strategy, and team culture](https://swissgrc.com/fr/looking-back-on-our-2025-summer-event-montreux-as-a-place-for-exchange-strategy-and-team-culture/)
**Published:** juillet 3, 2025
**Author:** Shayeste Afzaly
**Excerpt:** This year's Swiss GRC Summer Event took place in inspiring Montreux. Our team from Lucerne took the opportunity to reflect on strategic issues, exchange ideas, and strengthen the corporate culture.
**Content:**
**This year’s Swiss GRC summer event took place in the inspiring surroundings of Montreux. Against an impressive backdrop, our entire team from Lucerne came together to discuss strategic issues, promote internal exchange, and actively develop our corporate culture.**
After lunch together, **Besfort Kuqi, our CEO**, opened the first item on the agenda and took us on an exciting journey through the milestones achieved so far, the strategic goals for 2025, and planned developments at Swiss GRC. His presentation not only provided a well-founded overview of the company’s performance to date, but also highlighted the opportunities and initiatives that await us in the near future. He proudly presented impressive figures, developments, and visions that further strengthen our position as an innovative company.
This was followed by an interactive workshop with **Ueli Gerber**, which focused specifically on our corporate culture. We worked in small groups on the topics of cooperation, customer focus, and innovation. The aim was to gather concrete ideas and perspectives on how we can further strengthen our cooperation within the company and actively shape cultural development. The intensive examination of our values and daily actions generated many valuable insights.
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04902.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04918.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04923.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04900.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04885.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04876.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04891.png)
In the evening, we gathered for dinner together. In a relaxed atmosphere, many took the opportunity to get to know each other better across departmental boundaries and to end the day together.
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04976.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04971.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04934.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC04928.png)
The second day was devoted to culture and team building. Two groups explored the vineyards around Montreux and Chillon Castle in parallel. Both activities offered interesting insights, new perspectives, and opportunities for informal discussions.
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/20c12f97-3841-4f04-92b3-a13dfae086fb.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC05075.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/6691d9ad-5d19-4314-a3e8-0bbd1002027e.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/46f1022c-3824-4d2a-96aa-91026b2cb86d.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/91cf3c3f-f7da-45ca-bef1-8b25cbde48ba.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/9f306568-3c2f-4cda-9ce4-8436d47c1f70.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/56acfc5d-7584-42ea-b52b-2cfe0c3ef4a0_.png)
Finally, the route led back to Zell, where we took part in the regional soccer tournament in the evening. Even though we didn’t come first, the focus was on having fun – and the shared experience rounded off the summer event in a special way.
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC05172.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC05159.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC05145.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC05144.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC05123.png)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2025/07/DSC05079-scaled-1.jpg)
**Conclusion:** The 2025 summer event was characterized by strategic exchange, active cultural work, and shared experiences. Two intense days that strengthened our team and provided important impetus for the future.
**Catégories:** Events
---
### [TPRM under new rules: EBA, DORA and MaRisk explained](https://swissgrc.com/fr/tprm-under-new-rules-eba-dora-and-marisk-explained/)
**Published:** juillet 14, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** The regulatory landscape for Third-Party Risk Management (TPRM) is undergoing a fundamental transformation. With the new EBA Guideline, the DORA Regulation, and the anticipated revision of MaRisk, financial institutions are required to strategically realign their outsourcing and risk governance practices. The Deggendorf Note 2025/06 delivers a thorough analysis of this shift and leaves no doubt: Excel spreadsheets and siloed solutions are no longer sufficient.
**Content:**
**The regulatory landscape for Third-Party Risk Management (TPRM) is undergoing a fundamental transformation. With the new EBA Guideline, the DORA Regulation, and the anticipated revision of MaRisk, financial institutions are required to strategically realign their outsourcing and risk governance practices. The Deggendorf Note 2025/06 delivers a thorough analysis of this shift and leaves no doubt: Excel spreadsheets and siloed solutions are no longer sufficient.**
The foundation of the [Deggendorf Note 2025/06 by Prof. Dr. Andreas Igl](https://th-deg.de/Fakult%C3%A4ten/ai/bdo-stiftungsprofessur/deggendorfer-notiz/Deggendorfer%20Notiz%202025-06%20-%20Auswirkungen%20der%20EBA-Guidelines%20zum%20Third-Party%20Risk%20Management.pdf) is the [Consultation Paper published by the European Banking Authority (EBA) in July 2025](https://www.eba.europa.eu/sites/default/files/2025-07/33a0ee15-9601-4c2b-828e-1b09201a6e9f/CP%20on%20Draft%20Guidelines%20on%20sound%20management%20of%20third%20party%20risk.pdf). This document is the first to clearly outline the comprehensive regulatory requirements for managing risks arising from non-ICT third-party arrangements, and it directly complements the [DORA Regulation (EU 2022/2554)](https://swissgrc.com/dora), which came into force in January 2025. In combination with the existing MaRisk AT 9 framework in Germany, this creates substantial implications for third-party and outsourcing governance in the financial sector.
A three-pillar regulatory model: EBA guideline, DORA and MaRisk
With the publication of the new EBA Guideline on the management of third-party risks (non-ICT) and the now fully applicable DORA Regulation, for the first time there is a clearly structured European framework for TPRM.
- DORA targets ICT third-party providers and their resilience.
- The EBA Guideline focuses on non-ICT third-party providers, particularly when delivering critical or important functions.
- The German MaRisk AT 9, long used as a national standard, will likely be revised in alignment with these European developments.
**Key insight from the Deggendorf Note:** Managing outsourcing only from an operational or administrative perspective is no longer sufficient. Going forward, functional criticality will take centre stage — regardless of ICT involvement or contractual formalities.
The first strategic decision: ICT or non-ICT?
According to the Deggendorf Note, the distinction between ICT and non-ICT services will now be the initial decision point in any third-party risk assessment. This classification determines:
- which regulatory framework applies (DORA vs. EBA Guideline),
- how third parties must be assessed and documented,
- and which monitoring, governance, and reporting obligations arise.
This distinction requires robust governance structures that enable risk-based classification across the entire organisation. The responsibility increasingly lies at the **executive level**, as identifying critical functions has now become a strategic task.
From outsourcing to function-based risk: TPRM becomes strategic
A paradigm shift is taking place: The legal concept of outsourcing is no longer at the core — instead, the focus is now on the function being supported by the third party. This change has a significant impact on how risk is assessed and managed:
- Evaluation is function-based, not contract-based.
- Criticality is defined by the importance to the business model, not by time sensitivity or volume alone.
- The principle of proportionality allows tailored implementation, based on institution type and risk exposure.
**Conclusion from the Deggendorf Note:**
The traditional operational view must give way to a strategic and risk-oriented governance model for third-party risk.
Excel no longer enough: Stronger oversight and reporting required
The Deggendorf Note openly criticises the fact that many institutions continue to manage third-party relationships using Excel spreadsheets and fragmented documentation. This approach is no longer sufficient to meet the new regulatory expectations, which include:
Under DORA:
- A central ICT third-party register (Art. 28),
- Resilience testing and audits of ICT providers,
- Mandatory incident reporting to supervisors (Art. 19).
Under the EBA Guideline (non-ICT):
- Comprehensive contract requirements, including KPIs and audit rights,
- Emphasis on function-based risk assessment,
- Governance expectations that cover the entire third-party supply chain.
The message is clear: **Institutions are strongly encouraged to professionalise and digitise their third-party risk management processes.**
From regulation to implementation: Technology as enabler
Although the Deggendorf Note maintains a technology-neutral tone, its analysis implies a clear course of action:
Third-party risk governance must transition to structured, tool-supported systems. Only with such systems can institutions ensure transparency, auditability, traceability, and scalability.
Swiss GRC offers a modular TPRM solution that:
- Provides an integrated, centralised Third-Party Information Register,
- Supports risk-based classification and governance workflows,
- Enables consistent documentation and automated reporting.
Learn more about Swiss GRC’s TPRM Solution: [**Manage third-party risk securely and with confidence**](https://swissgrc.com/en/tprm-software)
A governance priority: TPRM as a core discipline
The Deggendorf Note 2025/06 clearly shows that managing third-party relationships is becoming a core governance competency in the financial industry.
The regulatory expectations from DORA, the new EBA Guideline, and upcoming revisions to MaRisk require organisations to completely rethink their outsourcing strategies — strategically, systematically, and risk-based.
Those who act now will not only strengthen their regulatory resilience, but also ensure their long-term digital and organisational viability.
**Catégories:** Industry News
---
### [Governing AI in the Era of Intelligent Risk: What GRC Professionals Need to Know](https://swissgrc.com/fr/ai-governance-in-the-era-of-intelligent-risk-what-grc-professionals-need-to-know/)
**Published:** août 4, 2025
**Author:** Vaishali Moitra
**Excerpt:** The regulatory landscape for Third-Party Risk Management (TPRM) is undergoing a fundamental transformation. With the new EBA Guideline, the DORA Regulation, and the anticipated revision of MaRisk, financial institutions are required to strategically realign their outsourcing and risk governance practices. The Deggendorf Note 2025/06 delivers a thorough analysis of this shift and leaves no doubt: Excel spreadsheets and siloed solutions are no longer sufficient.
**Content:**
**Artificial Intelligence (AI) is reshaping how organizations operate, make decisions, and manage risk. From intelligent automation to predictive analytics, AI offers tremendous potential—but it also introduces a new set of risks that many GRC (Governance, Risk, and Compliance) professional are still learning to navigate. For GRC professionals, this moment represents both a challenge and an opportunity: how do we govern AI responsibly while maintaining regulatory alignment, ethical standards, and business agility?**
The Expanding Scope of GRC: Why AI Governance Matters Now
Traditionally, GRC platforms have been designed to manage risk and compliance around human behaviour—policies, processes, access controls, and regulatory obligations. But AI brings a new layer of complexity. Models can change over time, decisions are often opaque, and outcomes may be difficult to audit.
As noted by [OCEG](https://www.oceg.org/the-rise-of-ai-in-grc-are-you-prepared/), a leading nonprofit in governance standards: « AI changes not just how we automate decisions, but how we assign responsibility for them. »
Similarly, [Deloitte’s](https://www.deloitte.com/content/dam/assets-zone2/uk/en/docs/industries/technology-media-telecommunications/2024/deloitte-ai-risk-and-approaches-to-global-regulatory-compliance-pov-v2.pdf) recent analysis emphasizes the growing need for organizations to align AI use with global regulatory expectations, including transparency, fairness, and accountability. In other words, governance is no longer optional for AI—it’s essential.
Common Challenges GRC Teams Face in AI Governance
While the value of AI is widely recognized, many organizations are encountering practical hurdles when it comes to governing it effectively:
**1. Oversight Silos:** AI often operates outside the reach of existing risk systems, with little integration between data science, compliance, and legal teams.
**2. Unclear Accountability:** As AI models become more autonomous, it becomes harder to track who is responsible for key decisions and outcomes.
**3. Regulatory Uncertainty:** With frameworks like the EU AI Act and regional guidelines still evolving, many organizations are unsure how to build future-proof AI governance.
**4. Manual Monitoring:** Risk reviews and model validations are often performed periodically—yet AI operates continuously, making real-time oversight difficult.
These gaps are not unique to any one industry or platform—they reflect a broader shift in how technology must be governed in the modern enterprise.
What GRC Professionals Are Looking For
Based on survey trends and industry engagement, end users of GRC platforms are seeking solutions that:
- Connect AI governance into existing risk and compliance workflows
- Provide clear roles and responsibilities across AI lifecycle stages
- Offer regulatory mapping for emerging AI laws and ethical guidelines
- Enable continuous monitoring and model risk assessment
- Support collaboration across departments—from data science to audit
How Swiss GRC Supports Responsible AI Governance
Swiss GRC has introduced an [**AI GRC Module**](https://swissgrc.com/en/ai-grc/) especifically designed to help organizations embed AI oversight into their broader GRC programs.
Here’s how it aligns with the needs of today’s GRC professionals:
- **Integrated Oversight:** The module allows risk, compliance, legal, and IT teams to manage AI systems through a shared governance framework.
- **Accountability Mapping:** Users can define responsibilities across AI development, deployment, and monitoring stages.
- **Regulatory Alignment:** The platform is pre-configured with global frameworks such as the **EU AI Act**, **UAE AI Ethics Charter**, and **SDAIA principles**, helping organizations stay ahead of evolving requirements.
- **Continuous Monitoring:** Automated tools flag performance changes, track bias, and support real-time alerts—shifting governance from reactive to proactive.
- **Audit-Ready Documentation:** From risk registers to usage logs, the platform ensures a clear, defensible trail for audit, board, or regulatory reviews.
Importantly, the AI GRC module does not require organizations to replace their entire GRC setup. It is built to extend and enhance existing workflows—supporting maturity at each stage, whether teams are just beginning their AI governance journey or already implementing advanced frameworks.

Dashboard of Swiss GRC’s AI GRC Module
Looking Ahead: AI Governance as a Core GRC Capability
AI is transforming industries—but with transformation comes responsibility. As AI becomes more embedded in operations and decision-making, its governance will need to be just as intelligent and adaptive.
GRC professionals are uniquely positioned to lead this effort—not just as risk mitigators, but as enablers of ethical, scalable, and compliant innovation. With the right tools and frameworks, organizations can build trust in their AI systems, align with global standards, and stay resilient in a fast-moving landscape.
**Catégories:** Industry News
---
### [Operational Resilience in 2025: From Regulatory Mandate to Strategic Muscle](https://swissgrc.com/fr/operational-resilience-in-2025-from-regulatory-mandate-to-strategic-muscle/)
**Published:** août 26, 2025
**Author:** Vaishali Moitra
**Excerpt:** In 2025, the organizations that lead will not be those with the most detailed compliance policies. They will be the ones that can absorb shocks, protect operations, and regain momentum faster than their peers. Resilience is not about avoiding disruption. It is about preparing for it, navigating it, and learning from it. This is the moment to move beyond reactive compliance.
**Content:**
**Looking back, 2023 was the year of adaptation. 2024 marked the year of acceleration, when operational resilience moved from being a compliance checkbox to a board-level priority. Now, in 2025, resilience has become the backbone of trust and continuity.**
Extreme climate events, cyberattacks, geopolitical volatility, and widespread IT disruptions converged to expose the fragility of even the most digitally advanced enterprises. What once felt like isolated risks became systemic and cross-border in nature, impacting supply chains, customer trust, and business continuity. The lesson was clear: resilience is no longer optional-it’s foundational.
The regulatory wake-up call
In response, regulators across Europe, the Middle East, and Asia-Pacific raised the bar. One of the most defining regulations is the EU’s [**Digital Operational Resilience Act (DORA)**](https://swissgrc.com/en/digital-operational-resilience-act-dora/), effective since January 2025. DORA sets a rigorous standard for financial institutions and ICT providers to withstand, respond to, and recover from disruptions, both digitally and operationally.
DORA’s five pillars—ICT risk management, incident reporting, resilience testing, third-party oversight, and information sharing—are increasingly echoed in other jurisdictions. The **UAE Central Bank’s Operational Risk Management Framework**, **Singapore’s MAS Guidelines**, and the **UK’s FCA/PRA frameworks** all converge on a unified message: resilience must be embedded, tested, and continuously monitored as part of governance, risk, and compliance.
And even beyond the financial sector, momentum is building. Switzerland’s federal government recently announced plans for a [**cyberresilience law**](https://swissgrc.com/bundesrat-plant-gesetz-zur-cyberresilienz-ein-wichtiger-schritt-fuer-die-schweiz/). It’s a signal that resilience is becoming a national policy priority, not just an industry obligation.
What this means for GRC programs
Traditional GRC systems designed for policy tracking, audits, and reactive compliance-are no longer sufficient. To meet today’s resilience expectations, GRC programs must be proactive, integrated, and continuous.
This shift requires organizations to:
- Map and monitor critical business services
- Test impact tolerances through simulated scenarios
- Respond to incidents with real-time workflows
- Embed third-party oversight into resilience plans
- Align resilience objectives across business and IT silos
The Swiss GRC advantage: Turning mandates into momentum
At Swiss GRC, we understand that building resilience is about more than just regulatory alignment-it’s about operational clarity, cross-functional coordination, and continuous readiness.
Our platform enables organizations to:
- Align with DORA and global regulatory frameworks through structured control libraries and modular configuration
- Unify risk, compliance, audit, and [ICT controls](https://www.globalcompliancenews.com/2025/02/21/https-insightplus-bakermckenzie-com-bm-financial-institutions_1-spain-navigating-the-new-eu-regulation-on-digital-operational-resilience-dora_02122025/) into a centralized GRC ecosystem
- Automate incident reporting and escalation workflows, ensuring audit-ready traceability
- Simulate disruption scenarios and validate recovery capabilities across services and third parties
- Continuously monitor resilience metrics to identify risk exposure before it escalates
Swiss GRC’s modular architecture means you don’t have to rip and replace your systems-we integrate with what you have, and scale as your resilience strategy matures.
Resilience is the new competitive edge
In 2025, the organizations that lead will not be those with the most detailed compliance policies. They will be the ones that can absorb shocks, protect operations, and regain momentum faster than their peers. Resilience is not about avoiding disruption. It is about preparing for it, navigating it, and learning from it. With global regulations converging, such as DORA in the European Union and new initiatives like Switzerland’s planned cyberresilience law, the message is unmistakable: resilience must be embedded at the core of governance, risk, and compliance.
This is the moment to move beyond reactive compliance. Organizations that invest in smarter and integrated GRC platforms are not just managing risk. They are building trust, continuity, and long term competitiveness.
**Catégories:** Industry News
---
### [GRC Industry Insights for 2025: What’s Actually Shifting?](https://swissgrc.com/fr/grc-industry-insights-for-2025-whats-actually-shifting/)
**Published:** septembre 16, 2025
**Author:** Vaishali Moitra
**Excerpt:** In 2025, the organizations that lead will not be those with the most detailed compliance policies. They will be the ones that can absorb shocks, protect operations, and regain momentum faster than their peers. Resilience is not about avoiding disruption. It is about preparing for it, navigating it, and learning from it. This is the moment to move beyond reactive compliance.
**Content:**
**For years, governance, risk, and compliance (GRC) functions have been seen primarily as safeguards-important, but often reactive and focused on ensuring organizations did not step outside regulatory boundaries. In 2025, however, the role of GRC is being redefined. Far from being a back-office function, GRC is now central to strategic decision-making.**
This shift is driven by an environment of accelerating regulatory complexity, rising cyber threats, global uncertainty, and disruptive technologies such as artificial intelligence. Organizations no longer ask only «*what do we need to comply with?»* The bigger questions now are: «*how do we build resilience into our operations?»* and «*how do we strengthen trust with regulators, customers, and stakeholders when the ground beneath us keeps shifting?»*
The answers lie in recognizing the key industry shifts shaping GRC in 2025.
1\. Privacy leaders are expanding into resilience
Today, the role of privacy leaders extends well beyond safeguarding personal data. Their responsibilities now encompass cyber-resilience and broader organizational risk management- a transformation fueled by rising regulatory demands. Directives such as NIS2, [Europe’s Digital Operational Resilience Act (DORA)](https://swissgrc.com/en/digital-operational-resilience-act-dora/), and the SEC’s cybersecurity disclosure requirements in the United States are redefining accountability. As a result, privacy officers are no longer merely guardians of information; they are emerging as architects of enterprise-wide resilience. This evolution highlights a broader truth: data protection is inseparable from business continuity. A privacy breach is no longer just a compliance failure-it can disrupt operations, damage brand trust, and create financial instability.
2\. Regulation has become a global convergence challenge
In the past, compliance teams often managed regulations within regional silos. Today, organizations face a convergence of global regulatory pressures. Boards and compliance leaders must navigate:
- Geopolitical instability disrupting supply chains and governance standards
- AI ethics and accountability requirements emerging across jurisdictions
- Real-time cyber disclosure rules, which reduce the margin for error
- Data sovereignty regulations, making cross-border information flows harder to manage
This convergence means compliance is no longer about ticking boxes-it is about building regulatory agility into the organization’s DNA. Companies that fail to adapt risk not only penalties but also operational paralysis. Boards, in particular, are under pressure. They must oversee not just compliance with regulations, but also the strategic integration of regulatory readiness into business planning. In other words, governance is no longer reactive, it is anticipatory.
3\. SaaS has become a strategic partner in resilience
The rise of SaaS in GRC is not new. What is new is how SaaS platforms are now positioned-not just as tools, but as guardians of enterprise resilience.
Forward-looking SaaS providers are making resilience a core value proposition by embedding:
- Hybrid architectures that ensure continuity even during outages or disruptions
- Continuous audit readiness, enabling organizations to demonstrate compliance in real time rather than in periodic cycles
- AI-secure frameworks that protect against adversarial risks and algorithmic vulnerabilities
This shift reflects a new trust dynamic. Organizations are no longer choosing SaaS providers only for features-they are selecting them as strategic partners in governance and resilience. The best SaaS solutions are enabling businesses to reduce uncertainty, simplify complexity, and gain real-time visibility into risks.
4\. Vendor Risk is moving to real-time Models
The global economy is more interconnected than ever. While that has enabled innovation and efficiency, it has also introduced new vulnerabilities. In fact, a significant share of supply chain disruptions today can be traced back to [vendors and third parties](https://contraqto.com/en/). As a result, organizations are moving toward:
- Continuous monitoring of vendors, using technology to track risks in near real time
- Automated risk scoring, ensuring that emerging threats are flagged before they escalate
- Proactive resilience modeling, where organizations stress-test the impact of potential vendor failures
In this context, [vendor risk management](https://swissgrc.com/en/vrmwhitepaper/) has matured into a core business discipline. It is no longer a compliance checkbox. It is a strategic capability essential for sustaining operations and protecting reputational trust.
5\. Unified GRC Is the New Imperative
Perhaps the most significant shift is the recognition that siloed compliance and risk management functions are unsustainable in a global, fast-moving regulatory landscape.
Organizations are increasingly investing in integrated, cloud-based GRC platforms that provide:
- End-to-end visibility of risk, compliance, and governance activities across regions and business units
- Collaboration across functions, eliminating information silos that slow down decision-making
- Agility to respond quickly to regulatory changes, geopolitical shocks, or emerging risks
The trend toward [unified GRC](https://swissgrc.com/en/solutions/) reflects a structural reality: fragmented compliance creates fragility. By contrast, unified GRC creates resilience, transparency, and accountability.
Conclusion: From Compliance Burden to Strategic Advantage
The insights shaping GRC in 2025 make one thing clear: governance, risk, and compliance are no longer just about preventing penalties. They are about creating trust and resilience in an environment defined by uncertainty.
The shifts are profound:
- Privacy leaders have become resilience leaders.
- Regulation has become a global convergence challenge.
- SaaS has evolved into a strategic resilience partner.
- Vendor risk requires real-time oversight.
- Unified GRC is now the foundation of organizational strength.
Organizations that understand and act on these changes will find that GRC is not a burden but a strategic advantage one that enables them to compete with confidence, build trust with stakeholders, and thrive amid complexity.
**Catégories:** Industry News
---
### [AI Governance in India: Inside the 4-Tier Model](https://swissgrc.com/fr/ai-governance-in-india-inside-the-4-tier-model/)
**Published:** septembre 17, 2025
**Author:** Vaishali Moitra
**Excerpt:** AI Governance in India sets new benchmarks with a 4-tier framework that ensures privacy, security, and trust in AI systems. The model introduces clear rules for risk classification, system inventory, and continuous monitoring to strengthen transparency, fairness, and accountability. By embedding DPDP and CERT-In requirements across the AI lifecycle, it offers enterprises practical guidance to align compliance with innovation and to deploy AI responsibly.
**Content:**
**AI Governance in India is becoming critical as the country’s AI revolution accelerates across digital payments, healthcare, and citizen services. With such large-scale deployment, failures or bias in AI systems can affect millions and undermine public trust. Recent regulations – the Data Protection and Digital Privacy (DPDP) Act and stringent CERT-In cybersecurity rules – have raised expectations for privacy and security by design. Enterprises now face a dual mandate: adopt AI responsibly, comply with evolving regulations, and remain audit-ready, while sustaining innovation.**
India’s AI Governance Framework
To address these challenges, the National Cyber and AI Centre (NCAIC) released the AI Governance Framework (2025), a risk-based blueprint tailored to India.
The framework introduces a taxonomy classifying AI from *prohibited* (e.g., social scoring) to *high*, *medium*, and *low risk*. High-risk AI – such as credit scoring, hiring tools, and critical infrastructure – require stricter controls and oversight. Core design principles include privacy-by-design, security-by-design, transparency, fairness, and accountability, embedding DPDP and CERT-In requirements throughout the AI lifecycle.
The framework aligns with international standards like ISO 42001, ISO/IEC 23894, and the NIST AI Risk Management Framework, facilitating interoperability and third-party assurance.
Structurally, it mandates clear governance roles. Boards or apex committees set AI risk appetite, while an AI Risk and Ethics Committee (AIREC) oversees inventories, risk classifications, and approvals for high-risk systems. Operational roles (data stewards, model owners) ensure traceability, creating a four-tier governance model spanning leadership, committees, officers, and technical teams.
Core Components
- **Risk Classification:** Prohibited and high-risk AI require extensive safeguards, while medium- and low-risk systems have lighter controls.
- **AI System Inventory:** All AI applications – including third-party and “shadow” systems – must be logged in a central registry, with metadata on ownership, lineage, and risk level. High-risk AI demand detailed documentation and approvals.
- **Lifecycle Controls:** Governance covers data, models, applications, and operations. This includes embedding DPDP rights (consent, deletion, purpose limitation), bias testing on diverse datasets, pseudonymization, and secure development practices.
- **Assurance & Monitoring:** Pre-deployment testing and continuous audits are mandated. Organizations must maintain monitoring dashboards, incident logs, and third-party conformity assessments, especially for high-risk AI.
Together, these provisions establish a unified governance architecture aligned with India’s regulatory landscape.
Challenges for Enterprises
While the framework provides clarity, implementation is complex. Organizations must inventory large portfolios of AI systems, many spanning legacy and new technologies. Few have matured risk taxonomies or formal AI governance policies, leading to fragmented compliance. Balancing innovation speed with regulatory rigor requires resources and cultural change.
Manual processes – from tracking AI use cases to compiling audit evidence – are slow, error-prone, and unsustainable. Without automation and integration, compliance risks becoming a burden rather than a foundation for trust.
Swiss GRC: Operationalizing AI Governance
The AI Governance Framework sets ambitious standards. Swiss GRC’s [**AI GRC Module**](https://swissgrc.com/en/ai-grc/) is designed to help organizations translate these requirements into practice, embedding governance across the AI lifecycle.
**AI System Inventory & Classification** Swiss GRC maintains a centralized, always-updated inventory of AI models and applications. Each system is classified using India’s taxonomy, with metadata on ownership, purpose, data sources, and compliance status. This provides the authoritative registry the framework requires and ensures full visibility across the AI landscape.
**Risk Assessment & Controls** The module supports structured assessments of AI-specific risks such as bias, fairness, explainability, and adversarial robustness. Workflows assign responsibilities, while dashboards highlight high-risk areas and gaps. This embeds fairness-, privacy-, and security-by-design practices into day-to-day operations and ensures alignment with DPDP obligations.
**Conformity & Assurance** With built-in templates aligned to ISO 42001, ISO/IEC 23894, and NIST AI RMF, Swiss GRC simplifies audits and certification processes. Organizations can schedule recurring assessments, capture evidence, and generate audit-ready reports, reducing compliance workload and strengthening accountability.
**Monitoring & Oversight** Continuous monitoring features track model drift, anomalies, and deviations in real time. Alerts and automated escalation workflows align directly with CERT-In’s reporting requirements. Independent validation and calibration further enhance assurance for high-risk AI systems.
**Data Governance & Transparency** Swiss GRC operationalizes privacy and transparency through data lineage tracking, PII masking, and explainability tools like model cards. Linking AI systems with risks, incidents, and vendors provides a holistic governance view, embedding compliance with DPDP and sectoral regulations into the AI lifecycle.
Turning Compliance into Advantage
By aligning directly with the framework’s **100-day, 12-month, and 24-month milestones**, Swiss GRC enables enterprises to accelerate compliance and reduce manual effort. The platform consolidates AI governance with broader GRC functions (ERM, ISMS, TPRM, BCM, and Audit), transforming compliance from an administrative task into a driver of resilience and competitiveness.
Conclusion
AI Governance in India is a landmark step toward safe, accountable, and trustworthy AI. It provides both a challenge and an opportunity for enterprises: to comply rigorously while enabling innovation. Swiss GRC empowers organizations to meet these expectations by unifying AI governance, risk management, and compliance in one platform. The result is not just adherence to rules, but the ability to build AI systems that are responsible, resilient, and trusted – turning governance into a strategic advantage for India’s AI-driven future.
**Catégories:** Regulation, AI
---
### [DORA Compliance: GRC as a Competitive Advantage](https://swissgrc.com/fr/dora-compliance-grc-as-a-competitive-advantage/)
**Published:** septembre 22, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** The digital transformation of the financial sector has accelerated innovation while simultaneously creating new operational risks and dependencies. Financial institutions now face unprecedented demands on their resilience. The increasing complexity of IT infrastructures, combined with ever more sophisticated cyber threats, requires a robust framework to ensure business continuity and security. This is precisely where the Digital Operational Resilience Act (DORA) comes in.
**Content:**
**The digital transformation of the financial sector has accelerated innovation while simultaneously creating new operational risks and dependencies. Financial institutions now face unprecedented demands on their resilience. The increasing complexity of IT infrastructures, combined with ever more sophisticated cyber threats, requires a robust framework to ensure business continuity and security. This is precisely where the Digital Operational Resilience Act (DORA) comes in.**
DORA is a comprehensive regulatory framework introduced by the European Union to strengthen the digital operational resilience of financial institutions. The regulation promotes a more interconnected system, as companies recognize their direct impact on other businesses, sectors, and economies. By setting strict requirements for risk management, incident reporting, and third-party risk management, DORA underscores the need for a secure and resilient financial sector.
BaFin provides practical guidance in two phases
In July 2024, [BaFin](https://www.bafin.de/DE/Startseite/startseite_node.html) published its first set of implementation guidelines, offering detailed recommendations for the adoption of DORA ([read more here](https://swissgrc.com/news/bafin-veroeffentlicht-umsetzungshinweise-zu-dora-was-bedeutet-das-fuer-finanzunternehmen/)). Key points included:
- **ICT Risk Management:** Regular risk analyses and effective controls to identify, assess, and manage ICT risks.
- **ICT Third-Party Risk Management:** Clear minimum requirements for contracts with service providers, including termination and audit rights, as well as continuous monitoring.
- **Regular Testing & Contingency Plans:** Comprehensive digital resilience tests and robust business continuity measures to ensure swift responses to incidents.
These guidelines helped banks, insurers, and other financial institutions prepare for the 17 January 2025 compliance deadline.
A year later, BaFin issued a [second supervisory notice](https://swissgrc.com/bafin-veroeffentlicht-zweite-aufsichtsmitteilung-zu-dora/) focusing on **simplified requirements for smaller and less complex institutions**. Around 1,100 companies in Germany – including small investment firms and occupational pension institutions – benefit from the principle of proportionality. Key simplifications include:
- No obligation to develop a comprehensive resilience strategy
- No annual documentation requirement and no separate control function
- No mandatory appointment of an information security officer
- Reduced detail requirements for ICT change processes
Despite these simplifications, core elements remain mandatory: a functioning ICT risk management framework, ongoing monitoring of third-party risks, and a current information register.
Information register: The heart of DORA compliance
An often underestimated but crucial element of DORA is the [**information register**](https://swissgrc.com/informationsregister-gemaess-dora-was-ist-es-und-wie-erstellt-man-es-richtig/?utm_source=chatgpt.com). It records all contracts with ICT third-party providers and assigns each service to the critical business and operational functions it supports:
- - **Transparency of Dependencies:** The register provides regulators and companies with a clear view of critical ICT relationships—essential for identifying systemic risks.
- **Structured Approach over Excel Chaos:** Many institutions start with Excel but quickly hit limitations such as lack of version control, security gaps, and high manual effort.
- **Best Practice:** A dedicated GRC platform enables automated maintenance, secure data storage, and standardized reporting, transforming the information register from a static obligation into a dynamic management tool.
Strengthening resilience with DORA
Implementing DORA is demanding but offers opportunities that extend well beyond mere compliance. Financial institutions can significantly enhance their operational resilience and professionalize their processes. The diverse requirements call for an integrated **Governance, Risk, and Compliance (GRC)** approach, making specialized software indispensable.
GRC software provides the tools needed to efficiently manage regulatory obligations. It streamlines processes, improves risk transparency, and ensures that all requirements are met on time. In addition, it supports the identification, assessment, and mitigation of risks, strengthening the trust of customers, partners, and supervisory authorities.
The five pillars of DORA
1. **ICT Risk Management:** Identification, assessment, and mitigation of all ICT-related risks.
2. **Incident Reporting:** Standardized processes for recording and reporting significant ICT incidents.
3. **Digital Resilience Testing:** Regular penetration and scenario-based testing to uncover vulnerabilities.
4. **ICT Third-Party Risk Management:** Continuous monitoring of external service providers and clear contractual mechanisms.
5. **Information Sharing:** Structured exchange of threat and incident information between financial institutions and supervisory authorities.
GRC software as a strategic advantage
Integrating comprehensive ICT risk management and reporting processes into existing systems demands significant personnel and financial resources. Ongoing third-party monitoring and maintenance of the information register remain challenging—even for institutions benefiting from simplified rules.
However, those who view the regulatory framework as an opportunity can modernize their structures, enhance digital resilience, and build trust with both customers and regulators.
A modern GRC platform unifies all risk management activities within a central framework:
- **Automated compliance workflows** reduce administrative effort and ensure consistent documentation.
- **Continuous monitoring and analytics** enable early detection of emerging risks and proactive management.
- **Centralized reporting** simplifies the audits and evidence required under DORA.
This makes DORA a catalyst for modern, proactive risk management—and positions GRC software as a strategic key to sustainable resilience.
Conclusion
DORA is far more than a regulatory checkbox. BaFin’s guidance from 2024 and 2025 shows that clear guardrails exist to support organizations of all sizes in implementation. Institutions that now adopt integrated GRC solutions can turn regulatory requirements into a competitive advantage, ensuring greater security, trust, and sustainable growth in the digital financial sector.
**Catégories:** Digital, Regulation
---
### [Integrated BCM: Building Resilience and Competitive Strength](https://swissgrc.com/fr/integrated-business-continuity-bcm-building-resilience-and-competitive-strength/)
**Published:** septembre 29, 2025
**Author:** Vaishali Moitra
**Excerpt:** Business continuity is no longer a side project for disaster recovery. It is now a strategic capability that underpins organizational resilience. Real strength arises when continuity, enterprise risk, compliance, cyber, and third-party oversight are interconnected, and the resulting synergies yield measurable outcomes.
**Content:**
**Business continuity is no longer a side project for disaster recovery. It is now a strategic capability that underpins organizational resilience. Real strength arises when continuity, enterprise risk, compliance, cyber, and third-party oversight are interconnected, and the resulting synergies yield measurable outcomes. The aim is not merely to survive an incident but to maintain operations, preserve reputation, and uphold stakeholder trust across a turbulent, evolving risk landscape.**
The urgency of integration is underscored by recent disruptions and regulatory shifts. [The cyberattack on Jaguar Land Rover in September 2025](https://www.reuters.com/business/retail-consumer/uks-jaguar-land-rover-cyber-attack-shutdown-hit-four-weeks-2025-09-23/) forced an extended production shutdown and rippled across the entire supply chain—a stark reminder that digital dependency magnifies systemic fragility. [Supply-chain attacks continue to surge, up over 400 % in recent years, making containment and third-party visibility critical.](https://www.insurancebusinessmag.com/us/news/cyber/supply-chain-cyber-attacks-surge-over-400-expected-to-continue-rising--cowbell-report-525369.aspx) At the same time, regulations such as the EU’s Digital Operational Resilience Act (DORA) formalize expectations for operational resilience, compelling firms to integrate continuity into governance and regulatory compliance, not relegate it to yearly exercises. Together, these trends demand that continuity be embedded into strategy, governance, and daily operations-not remain a dormant artifact.
What integrated continuity looks like
Integrated continuity requires shared data, shared decision making, and shared accountability. A single source of truth with dynamic dependency maps and unified taxonomies aligns assessments of service criticality and supplier tiers. Scenario based planning and continuous stress testing enable organisations to prioritise mitigation efforts and allocate capital with precision. Cross functional playbooks synchronise the responses of cyber, operations, legal, human resources, and communications teams, while controls are mapped directly to regulatory obligations so that boards and auditors can evaluate resilience outcomes rather than mere activity. Equally important, the preparedness of people and leadership is recognised as a fundamental element of organisational resilience.
Technology enables – governance decides
Technology provides the means for rapid detection, impact analysis, and coordinated response, yet it is governance that determines whether these capabilities translate into organisational resilience. Effective business continuity management requires a clear governance structure that defines decision authority, escalation paths, and accountability at every level. Technology should support the full BCM lifecycle-from business impact analysis and risk assessment to plan development, exercising, and continual improvement-by supplying accurate data, real-time monitoring, and integrated workflow management. The critical objective is to embed these tools within a governed framework that ensures decisions are timely, evidence-based, and aligned with the organisation’s continuity strategies and risk appetite, rather than relying on isolated solutions that create new operational silos.
Integrated business continuity as a strategic advantage
Regulation continues to raise the minimum standards for operational resilience, but integration enables organisations to transform that baseline into competitive strength. Boards and investors increasingly view resilience metrics such as validated recovery times, tested runbooks for critical services, and enforceable third-party recovery service levels as essential elements of strategic due diligence. Organisations that measure and report these outcomes consistently protect revenue and reputation more effectively than those that treat continuity as a compliance obligation. [Swiss GRC’s solution for Business Continuity Management](https://swissgrc.com/en/bcm-software/) embeds business continuity across risk, compliance, and third-party oversight within a single standard aligned framework. It consolidates dependency mapping, business impact analysis, recovery planning, evidence collection, and control testing to remove duplication and provide continuous visibility of resilience performance.
Business continuity is ultimately judged not by documents but by an organisation’s capacity to make rapid, well-founded decisions under pressure. Integrated resilience that unites governance, people, processes, and technology becomes a strategic capability that safeguards value, maintains stakeholder confidence, and differentiates enterprises in volatile markets.
**Catégories:** Software, BCM
---
### [FINMA overhauls insolvency rules for financial institutions](https://swissgrc.com/fr/finma-overhauls-insolvency-rules-for-financial-institutions/)
**Published:** octobre 1, 2025
**Author:** Gentian Ajeti
**Excerpt:** Switzerland’s financial sector approaches a major regulatory milestone as FINMA introduces a new Insolvency Ordinance that unifies and updates all requirements for handling bank and financial institution failures, fundamentally reshaping governance, risk, and compliance frameworks.
**Content:**
**Switzerland’s financial sector approaches a major regulatory milestone. Today, on 1 October 2025, the Swiss Financial Market Supervisory Authority (FINMA) has introduced a new Insolvency Ordinance that consolidates and modernizes all existing rules for handling the failure of banks and other financial institutions.**
This sweeping reform is more than a technical update: it reshapes how governance, risk, and compliance (GRC) must operate, setting a global benchmark for resolution planning and signaling to boards everywhere that preparedness for failure is now an essential measure of financial strength.
A new era for financial stability
When the global financial crisis of 2008 struck, it exposed a hard truth: many institutions had never planned for failure. Regulators responded with stress tests, “living wills,” and recovery plans to ensure that a single bank’s collapse would not destabilize the financial system. Now Switzerland is writing the next chapter. The new [FINMA Insolvency Ordinance](https://www.finma.ch/en/news/2025/09/20250904-mm-insolvenzverordnung/?utm_source=chatgpt.com) will sweep away three separate rulebooks—BIO-FINMA, IBO-FINMA, and CISBO-FINMA—and replace them with a single, modern framework for the orderly resolution of banks and other supervised institutions. This is far more than a technical consolidation. It signals that **resolution readiness is a board-level responsibility and a core element of governance, risk, and compliance (GRC).**
What the ordinance changes
The ordinance harmonizes and modernizes Switzerland’s approach to financial-sector insolvency. By unifying disparate regulations, FINMA provides a clearer and faster process for handling distressed institutions.
- **Consistency and speed.** One framework eliminates conflicting rules, enabling regulators and firms to act decisively during a crisis.
- **Legal certainty.** Creditors and counterparties gain a transparent path, reducing panic and market contagion ([FINMA announcement](https://www.finma.ch/en/news/2025/09/20250904-mm-insolvenzverordnung/?utm_source=chatgpt.com)).
- **Global alignment.** Switzerland now matches the rigor of EU Bank Recovery and Resolution Directive standards and the U.S. Dodd-Frank “living will” requirements, reinforcing its reputation as a stable, trusted financial center.
For executives and directors, the message is unmistakable: planning for failure can no longer be delegated to a specialist team or reviewed once a year. Boards must actively oversee resolution plans, while management ensures operational resilience—identifying critical functions, mapping third-party dependencies, and stress-testing their ability to continue operations or wind down safely. FINMA also expects real-time access to accurate data; scattered spreadsheets will not suffice.
Implications beyond Switzerland
Although this is a Swiss regulation, its relevance reaches far beyond national borders. Regulators in the European Union and the United Kingdom are tightening requirements for recovery and resolution planning, while the U.S. Federal Reserve continues to refine its own “living will” regime. Switzerland’s move therefore sends a global signal: **every financial institution must prove it can exit the market without destabilizing it.** Institutions that delay may find themselves scrambling as international partners and stakeholders begin demanding equivalent readiness everywhere.
Building integrated GRC for resolution readiness
Meeting these expectations requires more than a new policy document. Effective resolution planning draws on multiple disciplines—risk management, business continuity, third-party oversight, and regulatory reporting—and succeeds only when they are interconnected.
Integrated GRC frameworks enable organizations to:
- **Centralize risk and compliance data** to provide leadership and regulators a single source of truth.
- **Automate critical workflows** such as incident reporting, contingency planning, and board-level updates.
- **Embed resilience testing** into day-to-day operations so crisis playbooks remain current and actionable.
Rather than adding yet another siloed system, a unified GRC approach allows governance, risk, and compliance to work together seamlessly—precisely what a modern resolution framework demands. Institutions that embrace this approach will also discover benefits that go beyond compliance: greater efficiency from streamlined processes, stronger stakeholder trust, and the confidence to innovate and expand knowing their risk and governance structures can scale.
As the **FINMA Insolvency Ordinance** takes effect on **1 October 2025**, the real story is not merely regulatory change but a shift in mindset. Resolution planning is evolving from a defensive exercise to a defining element of strategic leadership. Institutions that embrace this perspective will do more than satisfy supervisors; they will set the standard for responsible growth and sustainable success in the financial sector’s next chapter.
**Catégories:** Industry News, Regulation
---
### [What Third-Party Cyber Risk Management can learn from established security functions](https://swissgrc.com/fr/what-third-party-cyber-risk-management-can-learn-from-established-security-functions/)
**Published:** octobre 5, 2025
**Author:** Marc Etienne Cortesi
**Excerpt:** In today’s interconnected economy, an organization’s resilience depends not only on its own security posture but on the strength of its extended ecosystem. While third-party cyber risk management (TPCRM) is evolving, physical and supply chain security have long established mature frameworks. The question is: What can TPCRM learn from them?
**Content:**
**In today’s interconnected economy, the resilience of an organization is no longer defined only by its own security posture, but by the strength of its extended ecosystem. While third-party cyber risk management (TPCRM) has gained momentum in recent years, it is still evolving. Other domains, however – such as physical security and supply chain security – have already built mature frameworks and practices.**
**The question we should ask is: *What can TPCRM learn from these established third-party security functions?***
Looking beyond cyber: Learning from mature models
Organizations have long faced third-party risks in the physical and supply chain realm. To manage these, entire standards and frameworks have been developed that embed **risk-based approaches, certification schemes, and industry-wide trust models**.
Some examples include:
- **ISO 28000** – A standard focusing on security management systems for the supply chain. It defines how to identify critical assets, assess risks, and build resilience across logistics networks.
- **TAPA FSR (Transported Asset Protection Association – Facility Security Requirements)** – A framework widely used in logistics and warehousing to protect high-value goods, with a strong focus on auditable controls and certifications.
- **CTPAT (Customs Trade Partnership Against Terrorism)** – A US government–business initiative that ensures importers and supply chain partners implement rigorous security practices to safeguard global trade.
These frameworks have one thing in common: they **don’t just rely on questionnaires** or self-attestations. They embed **standardized controls, verification mechanisms, and industry trust networks**.
There’s no need for cybersecurity to reinvent the wheel
Too often, [third-party](https://swissgrc.com/en/tprm-software) cyber risk management programs rely heavily on spreadsheets, lengthy questionnaires, and inconsistent monitoring. Compared to physical security, this feels immature.
Drawing inspiration from ISO 28000, TAPA FSR, and CTPAT, we can identify three lessons:
1. **Risk-Based Tiering:** Not all suppliers are equal. Just as CTPAT differentiates risk tiers in supply chains, TPCRM should define differentiated assurance levels – high-risk vendors require continuous monitoring and certification, low-risk vendors require lighter oversight.
2. **Independent Validation:** Physical security frameworks rely on accredited audits and certifications. Cybersecurity can follow this model by integrating **independent attestation standards** (e.g., ISO 27001, ISAE 3000, SOC 2) and industry consortia that reduce redundancy across assessments.
3. **Shared Responsibility Networks:** TAPA and CTPAT thrive because they are **industry communities**: members share intelligence and benchmarks. Cyber TPCRM should evolve towards similar **collaborative ecosystems** (cf. [Swiss FS-CSC](https://fscsc.ch/en/)), where risk intelligence is pooled, rather than every company reinventing the wheel.
Towards an integrated view of security
The lesson is clear: Third-party cyber risk management should **not be an isolated silo**. It should be seen as part of a broader [**Enterprise Security Risk Management**](https://asisonline.org/security-news/security-topics/esrm/) **(ESRM)** approach, where logical, physical, and personnel security are converged.
If we align cyber TPCRM with established physical and supply chain models, we can accelerate maturity, reduce redundancy, and – most importantly – build real trust across the value chain.
Conclusion
Cybersecurity leaders don’t need to start from scratch. Decades of experience in **physical and supply chain third-party security** have already shown what works: risk-based tiering, independent validation, and trusted communities.
As CISOs and risk advisors, our task is not just to protect the digital perimeter, but to embed **cyber resilience into the same trust frameworks that already safeguard goods, people, and supply chains**.
**What about you, do you see further lessons TPCRM can learn from already established functions?**
**Catégories:** Information Security, TPRM
---
### [Rethinking cyber resilience through the lens of NIS2](https://swissgrc.com/fr/rethinking-cyber-resilience-through-the-lens-of-nis2/)
**Published:** novembre 6, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** As the NIS2 Directive continues to shape Europe’s digital security landscape, the conversation around cybersecurity is shifting. What began as a regulatory framework is now driving a broader rethink of how organizations manage risk, build resilience, and maintain trust in an increasingly volatile environment.
**Content:**
**As the NIS2 Directive continues to shape Europe’s digital security landscape, the conversation around cybersecurity is evolving. What began with NIS1 in 2016, the European Union’s first attempt to harmonize network and information security standards, has now matured into a far more comprehensive framework.**
With NIS2, the EU has not only expanded the scope of its regulation but also raised expectations for governance, accountability, and resilience. What started as a policy response to fragmented cybersecurity practices has become a driving force for cultural and structural change, pushing organizations to link digital risk with leadership and long-term sustainability.
A continental shift in cyber governance
The rollout of [NIS2](https://digital-strategy.ec.europa.eu/en/policies/nis2-directive) across the European Union has redefined what it means to operate securely in a connected world. It sets clear obligations for risk management, supply chain oversight, and incident reporting—within just 24 hours of detection.
That benchmark now resonates beyond the EU. In [Switzerland](https://www.handelszeitung.ch/insurance/neue-meldepflichten-setzen-schweizer-unternehmen-unter-druck-877416), comparable reporting duties came into effect on April 1, 2025, under the revised Information Security Act. Organizations failing to report major cyber incidents to the Federal Office for Cybersecurity (BACS) risk fines of up to CHF 100,000.
As *Handelszeitung’s* [HZ Insurance](https://www.handelszeitung.ch/insurance/neue-meldepflichten-setzen-schweizer-unternehmen-unter-druck-877416) recently noted, Switzerland’s move reflects a wider European alignment. Cyber threats know no border, and neither can the frameworks designed to manage them. Whether through NIS2 or national equivalents, Europe is converging on a shared model of cyber accountability where resilience is a collective responsibility.
Measuring maturity and closing the gaps
A new study by **Kessler**, *Cyber Message 2025*, provides a timely snapshot of cyber maturity. Swiss organizations continue to perform well: industrial firms achieved a resilience score of **2.71**, while service providers such as IT and financial institutions reached **2.91** on a four-point scale—both above EU averages.
Yet the data also highlight persistent gaps. Many companies still rely on manual reporting processes, fragmented governance, and inconsistent incident response protocols. The 24-hour reporting rule, central to both NIS2 and Swiss law, has become a real-world test of coordination and operational readiness.
NIS2’s significance lies not in the regulatory text itself but in the shift it represents. Cybersecurity has moved from the server room to the boardroom. The question has changed from *“Are we compliant?”* to *“Are we resilient?”*
Across Europe, forward-thinking organizations are taking this moment to connect cybersecurity with governance, enterprise risk, and business continuity. Rather than treating NIS2 as a compliance checklist, they view it as a catalyst for stronger processes, clearer accountability, and greater trust with stakeholders.
Technology as an enabler, not a shortcut
Meeting these expectations requires structure and visibility. The [**GRC Toolbox**](https://swissgrc.com/en/network-information-security-directive-nis2/) supports organizations in operationalizing the principles of NIS2 and comparable frameworks such as Switzerland’s Information Security Act. It brings governance, risk, and compliance together in one environment, helping companies document controls, track incidents, and demonstrate regulatory alignment efficiently.
Technology alone cannot create resilience, but it can make it achievable. In a landscape where cyberattacks unfold across sectors and borders within hours, the ability to respond quickly and coherently is what defines real strength.
From **NIS1 to NIS2**, Europe’s cybersecurity evolution tells a clear story: resilience is not built through technology alone, but through shared responsibility and leadership.
The next phase will be defined not by who complies first, but by who leads best. The organizations that turn frameworks like NIS2 into everyday governance, anticipate risk, and recover stronger when disruptions occur.
👉 [Learn more about achieving NIS2 compliance with the GRC Toolbox](https://swissgrc.com/en/network-information-security-directive-nis2/)
**Catégories:** Information Security, Regulation
---
### [NIS2 decision in the Bundestag: Pressure on companies to act](https://swissgrc.com/fr/nis2-decision-in-the-bundestag-pressure-on-companies-to-act/)
**Published:** novembre 17, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** The NIS2 Directive (Directive (EU) 2022/2555) represents the EU’s primary legal instrument to enhance cybersecurity and cyber resilience. The implementation of the EU NIS2 Directive into German law fundamentally reshapes the cybersecurity requirements for thousands of organizations across the country. Those who act now will not only secure compliance, but also significantly strengthen their overall cyber resilience.
**Content:**
**The implementation of the EU NIS2 Directive into German law fundamentally reshapes the cybersecurity requirements for thousands of organizations across the country. Those who act now will not only secure compliance, but also significantly strengthen their overall cyber resilience.**
With the adoption of the law transposing the NIS2 Directive, the German Bundestag has laid a decisive foundation for the modernisation of the national cybersecurity framework. On 13 November 2025, the so-called Implementation and Cybersecurity Strengthening Act was passed — a measure that raises security requirements for a vast share of the German economy to an unprecedented level ([bundestag.de](https://www.bundestag.de/dokumente/textarchiv/2025/kw46-de-nis-2-1123138?utm_source=chatgpt.com)). Not only operators of critical infrastructure are affected; NIS2 expands the scope dramatically and introduces explicit supervisory, reporting, and governance obligations.
Why NIS2 matters
The NIS2 Directive (Directive (EU) 2022/2555) represents the EU’s primary legal instrument to enhance cybersecurity and cyber resilience. It is a response to an evolving threat landscape characterised by interconnected supply chains, geopolitical tension, and increasingly strategic cybercrime. The Directive demands modern security, governance, and risk management structures — with clear accountability at senior management level and significant sanctions in the event of non-compliance ([de.wikipedia.org](https://de.wikipedia.org/wiki/NIS-2-Richtlinie?utm_source=chatgpt.com)).
Put simply: cybersecurity is no longer seen as a purely technical issue, but as a central leadership and governance priority.
New legal requirements and why time is short
With the Bundestag decision, NIS2 is formally integrated into German law. The core elements of the legislation include:
- **Significant expansion of scope:** An estimated 29,000–30,000 companies and public institutions will fall under the regulation — more than twice as many as before
([security-insider.de](https://www.security-insider.de/bundestag-beschliesst-nis-2-umsetzungsgesetz-a-6b67d5b503bf7404553cc5de4f0dbbb0/?utm_source=chatgpt.com)).
- **Tightened reporting requirements:** 24-hour early warning notice, 72-hour interim report, and a final report within 30 days
(csoonline.com).
- **Stronger supervision and enforcement:** The Federal Office for Information Security (BSI) receives expanded authority.
- **New “CISO for the Federal Government”:** A centralised function to support information security within federal administration
([bundestag.de](https://www.bundestag.de/dokumente/textarchiv/2025/kw46-de-nis-2-1123138?utm_source=chatgpt.com)).
- **New entity classifications:** “Important” and “highly important” entities — affecting many organisations previously outside the regulatory perimeter.
Experts warn that organisations face intense time pressure because the implementation deadline at EU level has already been exceeded
([becon.de](https://www.becon.de/bundestag-beschliesst-verspaetetes-nis-2-umsetzungsgesetz-auswirkungen-chancen-und-klare-handlungsempfehlungen-fuer-unternehmen/?utm_source=chatgpt.com)).
Obligations — but also opportunities
Organisations that view NIS2 as a purely regulatory burden risk missing the strategic benefits. The Directive supports a resilient, holistic security culture and opens opportunities for long-term competitive advantage:
Regulatory challengeStrategic benefit when implemented effectivelyReporting & notification obligationsFaster incident response & reduced business impactRisk management requirementsStructured prioritisation & transparency in security postureBoard-level accountabilityClear ownership & long-term investment securitySupply chain securityResilience across the entire value ecosystemCatalogue of technical & organisational measuresHigher cyber defence capacity & reduced operational risk
NIS2 demands what many organisations already need: **integrated cybersecurity, governance, risk and compliance — not isolated technical controls.**
The path to cyber resilience: beyond compliance
The key challenge is not simply achieving NIS2 conformity, but embedding cybersecurity permanently into processes, organisational structures, and technology. This requires:
- Visible executive accountability and governance structures
- Strategic integration of cybersecurity with risk and compliance management
- Digitalisation and automation of security processes
- Reportable, audit-ready documentation at any time
- Continuous monitoring rather than periodic assessments
Success depends not on the quantity of technical security tools — but on a **platform that connects all security, governance, risk, and compliance elements in one system**.
NIS2 compliance with a system: How Swiss GRC supports organisations
The implementation of the NIS2 Directive is not just a regulatory development. It is an essential step toward future-proofing organisations in an increasingly hostile cyber landscape. Those who invest early strengthen not only compliance but resilience, competitiveness and ultimately, the security of the wider economy. Swiss GRC enables companies to comply with the EU NIS2 Directive efficiently and without organisational overload, while establishing a foundation for long-term cybersecurity excellence. The **GRC Toolbox** provides:
- Clear governance and accountability structures
- Risk assessment and monitoring aligned with NIS2 requirements
- Incident and reporting workflows with full transparency
- Continuous compliance evidence and audit-readiness
- Seamless integration into existing security and IT ecosystems
In other words: compliance becomes not a hurdle, but a driver of cyber resilience and sustainable security.
👉 Learn more:
****
**Catégories:** Industry News, Regulation
---
### [FINMA Supervisory Notice 05/2025 as a wake-up call for Resilience by Design](https://swissgrc.com/fr/finma-supervisory-notice-05-2025-as-a-wake-up-call-for-resilience-by-design/)
**Published:** novembre 26, 2025
**Author:** Gentian Ajeti
**Excerpt:** FINMA 05/2025 sets the strategic direction for strengthening operational resilience across the Swiss financial sector. The updated requirements coming into effect from 2026 reshape how institutions must prepare for disruptions and ensure continuity. Those who take action now will not only meet regulatory expectations, but also reinforce their long-term stability and resilience.
**Content:**
**FINMA is tightening its expectations regarding operational resilience. Starting in 2026, institutions must demonstrably define and implement their critical functions, disruption tolerances, and testing procedures.**
With [Supervisory Notice 05/2025](https://www.finma.ch/en/~/media/finma/dokumente/dokumentencenter/myfinma/4dokumentation/finma-aufsichtsmitteilungen/20251110-finma-aufsichtsmitteilung-05-2025.pdf?hash=FD26ED4215AEADD03F8D50B0BCCF66F0&sc_lang=en&utm_source=chatgpt.com), FINMA places operational resilience at the center of its supervisory practice.
From 1 January 2026, all institutions, regardless of their size or supervisory category, must have implemented concrete measures to ensure their ability to withstand disruptions.
FINMA’s analysis of 267 institutions shows significant differences in maturity, with notable gaps in the definition of critical functions, disruption tolerances, and the integration of existing frameworks.
Critical functions: focus instead of fragmentation
According to FINMA, the average number of identified critical functions is 3.5. While larger institutions define more, some exceed a reasonable scope with up to 36 critical functions. FINMA calls for clarity: a critical function is not every process but an activity whose failure has immediate effects on clients or the stability of the financial market.
Many institutions confuse processes (e.g., back office, IT operations) or resources (e.g., core banking system) with critical functions. What matters is a top-down perspective that considers strategic relevance and dependencies within the supply chain.
**Practical recommendation:**
A robust inventory of critical functions forms the foundation for a holistic «front-to-back» perspective, as required by FINMA. This inventory should map functions, processes, resources, and interdependencies in a transparent manner.
Disruption tolerances: from technical limits to the board’s tolerance level
FINMA criticises that many institutions define their disruption tolerances «backwards» – starting from technical recovery capability («reverse engineering») instead of from the tolerance level set by the governing body. As a result, the resilience question is viewed too operationally instead of strategically.
Most institutions define disruption tolerances between 24 and 72 hours. Values that are too low indicate a confusion with BCM metrics (RTO/RPO), while values that are too high suggest an uncritical definition of functions.
**Practical recommendation:**
A well-designed governance process supported by traceable data, visualisations, and clear decision logic helps to anchor disruption tolerances at a strategic level. Combining a clear methodology, structured documentation, and suitable tools creates transparency and strengthens executive involvement.
Testing: from cyber defence to end-to-end resilience
According to FINMA, 85% of institutions in supervisory categories 1 to 3 have not yet carried out any testing. Frequently mentioned scenarios include «successful cyberattack» or «supply chain disruption» – yet non-cyber-related threats often remain untested.
**Practical recommendation:**
Regular, scenario-based testing forms the backbone of a learning organisation. Using structured test frameworks and suitable platforms simplifies planning, execution, and evaluation, ensuring that results can be directly translated into improvement measures – a crucial step toward continuous advancement.
Operational resilience framework: time for integration
According to FINMA, only 12–15% of institutions have established an integrated framework that coordinates risk management, ICT and cyber risks, BCM, emergency planning, and third-party management. As a result, most institutions still lack the organisational foundation for a consistent «resilience-by-design» approach.
With regard to European developments such as DORA and the [NIS2 Directive (EU) 2022/2555](https://eur-lex.europa.eu/eli/dir/2022/2555/oj/eng?utm_source=chatgpt.com), this integration is essential. Both regulatory frameworks require tightly interconnected oversight of cyber, IT, and operational risks – marking a shift from silo thinking to risk-based end-to-end management.
**Practical recommendation:**
Institutions should view their operational resilience framework as an overarching steering instrument. This includes:
• Defining suitable metrics (KPIs/KRIs)
• Integrating risk management, BCM, ICT, and third-party oversight
• Automated monitoring of dependencies and interfaces
From compliance to strategic resilience
Operational resilience is more than a regulatory obligation – it is a **strategic success factor.** It not only protects against disruptions but also increases the capability to use crises as opportunities for learning and adaptation. With the mandatory implementation of FINMA’s requirements from 2026 onward and the harmonisation with European standards, institutions gain a unique opportunity: resilience can become a true differentiator.
**Practical recommendation:**
A data-driven view of risks and dependencies enables active steering of resilience. Dashboards, metrics, and analyses form the foundation for fact-based decisions – whether implemented through internal methods or supported by dedicated tools.
How technology can help without losing control
Implementing the requirements for resilience, critical functions, and tolerance definitions is complex, especially when done through Excel and manual processes. Many institutions recognise that **tool-supported approaches** create transparency, automation, and traceability. The GRC Toolbox from Swiss GRC enables institutions to systematically record critical functions and dependencies, define disruption tolerances, plan tests, and centrally evaluate results – all embedded in an overarching framework for operational resilience.
The focus is not on the tool itself but on the added value: **an end-to-end perspective, consistent governance, and a sustainable contribution to a resilience-by-design culture.**
Conclusion
[Supervisory Notice 05/2025](https://www.finma.ch/en/~/media/finma/dokumente/dokumentencenter/myfinma/4dokumentation/finma-aufsichtsmitteilungen/20251110-finma-aufsichtsmitteilung-05-2025.pdf?hash=FD26ED4215AEADD03F8D50B0BCCF66F0&sc_lang=en&utm_source=chatgpt.com) marks a milestone in strengthening the Swiss financial market infrastructure. For institutions, this means: consolidating structures, clarifying responsibilities, and approaching resilience from a strategic perspective.
DORA, NIS2, and international best practices make it clear: **resilience is not a project – it is a guiding principle.** Institutions that invest today in an integrated, data-driven, and governance-oriented implementation will, in the long term, not only be compliant with regulations but also commercially robust and future-proof.
*Swiss GRC supports institutions in implementing regulatory requirements for operational resilience – from the identification of critical functions to holistic management. Our experts combine regulatory know-how with technological implementation capabilities to build a resilience-by-design culture that delivers real impact. **Book an appointment now: [swissgrc.com/discoverycall](https://swissgrc.com/discoverycall/).***
**Catégories:** Regulation
---
### [GCC GRC Day 2025: Are Organizations Ready to Strengthen Their GRC Programme Amid New Risks? ](https://swissgrc.com/fr/gcc-grc-day-2025-are-organizations-ready-to-strengthen-their-grc-programme-amid-new-risks/)
**Published:** novembre 30, 2025
**Author:** Vaishali Moitra
**Excerpt:** GCC GRC Day 2025 shows that AI governance, resilience and integrated risk management are becoming central to effective GRC across the GCC. The conference highlights how organizations must strengthen their GRC programmes to navigate accelerating risks and support sustainable decision-making.
**Content:**
**Dubai/Lucerne – On 20 November 2025, the GCC GRC Day 2025 in Dubai brought together [governance, risk and compliance (GRC)](https://swissgrc.com/en/solutions/) professionals from across the region at Address Sky View Dubai. Organized by Swiss GRC in collaboration with Khaleej Times Events, the one day conference addressed a broad range of topics – from corporate governance and internal controls (ICS) to cybersecurity, ESG, AI governance, compliance automation and business continuity.**
The annual conference continues to build on its strong foundation as a premier platform for dialogue and knowledge exchange across the GCC. It event convened board members, C-suite executives, compliance officers and regulators to address pressing priorities in the evolving risk landscape. Keynote speeches set the tone for the day. [Schneider Electric’s](https://www.se.com/ww/en/) Senior VP- Programs & Transformation **Dallal Slimani** opened with a presentation on operational and organizational resilience. Swiss GRC’s MEA/APAC General Manager **Rajeev Dutt** followed with insights on «GRC in Transition: Building Resilience in Uncertain Times». [Google’](https://blog.google/)s **Akshay Dalal** Head of Risk & Compliance, MEA/TA delivered a keynote on AI Governance & Ethical Risk Management, underscoring the need to balance innovation with accountability. Other speakers included **Adnan Ibrahim Alhashmi** Senior Associate Operations Manager, **Tawazun Council** for Defence Enablement on enterprise-wide assurance, and **Fadi Bouz** Director of Internal Audit & Risk Department,Sunbulah Group on the transformative role of internal audit.
Interactive panels and forums were highlights of the agenda. The **«Guardians of Trust: Security, Regulation & Privacy by Design»** panel brought together security and privacy experts – including **Faisal Khan** Associate Director – Information Security & Compliance,Dubai World Trade Centre and Hessa Al **Humaid Almatrooshi** information Security Leader, Free Zones Authority of Ajman to discuss how organizations can build trust and resilience into their digital systems. Another major session, **«Bridging Academia & Practice: Elevating GRC Dialogue in the GCC»** featured **Nikolai Tsenov** Head Solutions & Innovation, Swiss GRCalongside academic and government figures. They explored how universities and industry can collaborate on GRC education and research, helping to close skills gaps and align curricula with market needs. According to organizers, these panels and others on topics like supply-chain risk and regulatory technology – emphasized practical frameworks over theory, giving delegates actionable insights for their organizations.
At the **GCC GRC Day**, experts and participants underscored several key outcomes from the conference. One clear takeaway was the rising importance of AI and advanced analytics in GRC. Speakers noted that artificial intelligence is transforming risk management, making its governance more critical than ever. As Swiss GRC CEO **Besfort Kuqi** observed, the GCC is experiencing «an impressive pace of transformation» with «AI and automation accelerating rapidly, and regulatory expectations, increasing at a remarkable pace».
Another major theme was **strengthening the culture of compliance and risk awareness**. Panellists emphasized that effective GRC must be driven from the top and rooted in organizational culture. Rajeev Dutt General Manager MEA & APAC, Swiss GRC stressed that many GRC initiatives «fail because they’re not driven from the top down,» making leadership commitment and clear tone-at-the-top critical. This echoed industry research showing the payoff of a trust infused culture: organizations with «trusted GRC cultures move faster, adapt more easily, and earn the confidence of regulators, partners and customers». In practice, experts encouraged reframing GRC as a shared language and value system rather than a mere checkbox exercise.
Participants at GCC GRC DAY also highlighted the value of **integrated risk-management tools and automation**. Modern GRC platforms that link audit, risk, compliance and IT systems can create a «single source of truth» streamlining processes and eliminating duplicate tasks. Swiss GRC demonstrated that such solutions take a holistic, integrated approach – combining risk management, internal controls (ICS), information security, data protection, business continuity management, third-party risk and other disciplines into one unified system. With these tools, organizations can gain 360° visibility of their risk exposures and rapidly respond to issues. As one panel noted, connecting people, data and processes makes it possible to «see risk from all angles» align risk indicators to strategic objectives, and take smarter, more timely decisions.
On behalf of Swiss GRC, CEO **Besfort Kuqi** emphasized the strategic significance of the new platform. «The GCC GRC Day reflects our commitment to advancing the regional GRC agenda through meaningful dialogue and shared expertise» he said. Kuqi noted that partnering with Khaleej Times Events has allowed these important conversations to reach a broader professional audience across the Gulf. Looking ahead, organizers intend to maintain the event as an annual fixture: Swiss GRC affirmed that the GCC GRC Day will build on the legacy of its established Swiss GRC conferences, ensuring the company’s continued engagement in the region’s GRC community.
The **GCC GRC Day 2025** was covered by multiple media outlets and is expected to be a recurring highlight in the regional GRC calendar. By blending expert keynotes, practitioner panels and networking opportunities, the conference showcased the latest thought leadership and best practices. Executives and regulators in attendance valued the mix of high-level strategy and practical guidance concluding that the forum has set a strong precedent for future events focused on governance, risk and compliance in the Gulf
**Catégories:** Industry News
---
### [FINMA Risk Monitor 2025 reveals key risks for Swiss finance](https://swissgrc.com/fr/finma-risk-monitor-2025-reveals-key-risks-for-swiss-finance/)
**Published:** décembre 2, 2025
**Author:** Gentian Ajeti
**Excerpt:** FINMA Risk Monitor 2025 outlines the most significant risks currently shaping the Swiss financial centre. The risk landscape is evolving rapidly across both financial and non-financial areas, increasing the pressure on institutions to enhance their resilience. Understanding these developments is now essential for strategic decision-making, not just compliance.
**Content:**
**The Swiss Financial Market Supervisory Authority (FINMA) outlines in its Risk Monitor 2025 the most significant risks currently shaping the Swiss financial centre. The risk landscape is evolving rapidly across both financial and non-financial areas, increasing the pressure on institutions to enhance their resilience. Understanding these developments is now essential for strategic decision-making, not just compliance.**
The FINMA Risk Monitor 2025 presents a clear picture of the structural vulnerabilities and emerging threats affecting banks and insurers in Switzerland. It not only reflects supervisory oversight, but also the broader context in which the Swiss financial system operates, shaped by economic uncertainty, technology advances and geopolitical tension.
The real estate and mortgage market remains a central point of concern. With CHF 1.24 trillion in domestic mortgages, overheating continues to pose a systemic threat. Elevated household debt and imbalances in property prices leave institutions exposed should a correction take place.
Credit risk also remains high. Corporate lending, particularly to SMEs, leveraged finance and Lombard loans, reacts quickly to changes in economic conditions. A downturn in activity could lead to a rapid deterioration in asset quality across several portfolios at once.
Liquidity has become a priority. FINMA notes that digital withdrawals and mobile banking have significantly accelerated the speed at which bank runs can develop. What once unfolded over days can now escalate within hours, requiring more dynamic stress testing and real-time liquidity monitoring.
The shift toward interconnected risk
Geopolitical and sanctions-related risk has intensified, and the consequences of non-compliance have become faster and more severe. For cross-border business models this increases both legal and reputational exposure.
Cyber threats continue to grow, and an increasing number of successful attacks are launched through external service providers. This development mirrors findings from the [World Economic Forum’s Global Cybersecurity Outlook](https://www.weforum.org/agenda/2025/01/cybersecurity-global-risks), which highlights supply-chain cyber attacks among the most relevant global risks.
Outsourcing is another area drawing attention. FINMA warns that reliance on a small number of dominant cloud and IT service providers creates dependency risks for the financial sector as a whole. The topic aligns with supervisory concerns described in the [European Central Bank’s analysis of ICT and cloud concentration](https://www.ecb.europa.eu/press/pr/date/2024/html/ecb.pr240920~pressrelease), signalling a European-wide shift toward stricter expectations.
Across all risk categories, one conclusion stands out: demonstrating operational resilience is now a decisive supervisory expectation. Institutions must show they are able to absorb, respond to and recover from disruptions — not only document controls.
What this means for financial institutions
The FINMA Risk Monitor 2025 makes one development clear: resilience has become a strategic requirement. The focus is shifting from identifying individual risks to creating an integrated understanding that links financial and non-financial risk drivers, improves transparency and enables controlled and consistent response.
Institutions that establish resilience as a core capability, supported by data, governance and timely information, will be better positioned to navigate regulatory expectations as well as real-world shocks.
How Swiss GRC supports the path to resilience
Swiss GRC helps financial institutions strengthen governance, risk management and operational resilience with an integrated platform aligned with supervisory expectations. The GRC Toolbox provides structured control frameworks, automated workflows and complete evidence trails for operational resilience across first and second line functions.
Organisations exploring how to operationalise resilience can connect with our experts here:
[Book a discovery call with Swiss GRC](https://swissgrc.com/en/discoverycall/).
**Catégories:** Industry News
---
### [ERM Report 2025: Why Most Crises Start Within](https://swissgrc.com/fr/erm-report-2025-why-most-crises-start-within/)
**Published:** décembre 5, 2025
**Author:** Shayeste Afzaly
**Excerpt:** The ERM Report 2025 reveals that internal weaknesses remain the primary drivers of major corporate crises across the DACH region. Strategic failures, governance gaps and operational issues make organizations vulnerable long before external shocks appear. Strengthening Enterprise Risk Management and resilience is now essential for sustainable performance and confident strategic decision-making.
**Content:**
The [**ERM Report 2025**](https://www.google.com/url?sa=t&rct=j&q=&esrc=s&source=web&cd=&cad=rja&uact=8&ved=2ahUKEwiGscm-o6aRAxWUhv0HHVjsBk4QFnoECBsQAQ&url=https%3A%2F%2Fwww.hslu.ch%2F-%2Fmedia%2Fcampus%2Fcommon%2Ffiles%2Fdokumente%2Fh%2F1-medienmitteilungen-und-news%2F2025%2Fw%2Ferm-report-2025.pdf%3Fsc_lang%3Dde-ch&usg=AOvVaw1OQjdme4F6GGc9Jz_cqcU4&opi=89978449), published by the Lucerne University of Applied Sciences and Arts (HSLU) in cooperation with HAW Kiel, delivers a clear message to boards and executives across the DACH region: severe corporate crises are far more common—and far more internal—than many leaders assume. The study analyzes 669 publicly listed companies from 2018 to 2024 and finds that nearly one in three experienced a share-price collapse of 25% or more within a single month. Recovery is slow and costly; on average, affected firms require almost two years to return to pre-crisis levels, trailing significantly behind the broader market.
The Silent Drivers: Strategy Missteps and Internal Weaknesses
What stands out most in the data is that **the majority of crises originate inside the organisation**.
The report attributes:
- **41% of crises to strategic failures**, including excessive leverage, flawed capital allocation, overreliance on key customers, or misjudged market dynamics.
- **19% to preventable internal shortcomings**—reporting delays, governance lapses, compliance failures, and operational mismanagement.
These findings confront a long-standing misconception in corporate risk discussions: that crises are primarily triggered by unpredictable external shocks. Instead, the *ERM Report 2025* shows that internal decisions—not the macroeconomic environment—pose the greatest threat to corporate stability. Even more telling, roughly one-third of affected firms suffer repeated crises, indicating vulnerabilities that remain unresolved over years.
External Shocks Reveal What Was Already Weak
External risks—geopolitical tensions, inflation, supply chain disruptions, financial-market volatility—certainly matter. They account for about 40% of crisis events and are especially visible during periods such as 2022, when inflation spiked and the war in Ukraine intensified pressures across industries. But the report makes clear: external shocks become catastrophic only when internal resilience is weak.
The sector comparison illustrates this vividly. Technology companies were significantly overrepresented among severe declines, while industrials displayed notable stability thanks to diversified structures, disciplined governance, and long-term project management. Swiss companies overall demonstrated greater resilience than German peers, supported by more stable sector composition and stronger governance frameworks.
A Strategic Imperative: Elevate ERM Beyond Compliance
Taken together, the findings point to a decisive conclusion: Enterprise Risk Management must evolve from a compliance-driven activity to a strategic leadership instrument.
High-performing organisations increasingly use ERM to refine capital allocation, test strategic assumptions, understand [customer](https://swissgrc.com/en/clients/) dependencies, and prepare for geopolitical and macroeconomic shifts. ERM becomes valuable not when it documents risks, but when it influences decisions.
This strategic lens is also reflected in the guest contribution included in the *ERM Report 2025*, authored by **Gentian Ajeti**, Chief Customer & Commercial Officer and Member of the Board of Directors at Swiss GRC, and **Yahya Mohamed Mao**, Chief Marketing Officer and Member of the Board of Directors at Swiss GRC. Their essay, «*Strategic Value Creation Through Organizational Resilience,»* extends the report’s empirical findings into practice, arguing that resilience must be viewed not only as protection against downturns but as a driver of long-term competitiveness.
Ajeti and Mao highlight that organisations capable of anticipating disruption, adapting quickly, and maintaining strong governance structures do more than survive crises—they use uncertainty to strengthen customer trust, accelerate strategic clarity, and unlock new opportunities. Their perspective reinforces a central theme of the report: resilience is not a defensive posture; it is a strategic capability that shapes performance over time.
A Call to Boards and Executives
The *ERM Report 2025* arrives at a moment when volatility has become the norm rather than the exception. Its findings urge leaders to reassess long-held assumptions about [risk](https://swissgrc.com/en/risk-management-software/). Crises are seldom sudden. They build slowly—in the blind spots of strategy, governance, and culture.
The organisations that prosper in this environment will be those that treat ERM as a forward-looking discipline and resilience as a strategic investment. As the report and Swiss GRC’s contribution jointly emphasise, value creation and risk management are no longer separate conversations. They are one and the same.
**Catégories:** Industry News
---
### [GRC 2026: Accountability, Resilience, and Constant Pressure](https://swissgrc.com/fr/grc-2026-accountability-resilience-and-constant-pressure/)
**Published:** janvier 8, 2026
**Author:** Vaishali Moitra
**Excerpt:** As organizations approach 2026, Governance, Risk, and Compliance (GRC) is undergoing a fundamental transformation. What was once viewed primarily as a compliance obligation is now emerging as a strategic capability-one that enables resilience, informed decision-making, and long-term trust. For business leaders, the focus is no longer on whether governance frameworks are in place.
**Content:**
As organizations approach 2026, Governance, Risk, and Compliance (GRC) is undergoing a fundamental transformation. What was once viewed primarily as a compliance obligation is now emerging as a strategic capability-one that enables resilience, informed decision-making, and long-term trust. For business leaders, the focus is no longer on whether governance frameworks are in place, but on whether they are adaptive, intelligent, and aligned with the realities of a rapidly changing risk landscape. Several converging trends are driving this shift. Artificial intelligence, evolving regulations, cyber threats, and supply chain volatility are collectively redefining how organizations think about governance and risk.
2026 is a key year for AI Governance
In 2026, artificial intelligence has moved from experimentation to institutionalization, and governance is where this shift is most visible. While AI has already demonstrated its value in automating controls, analysing large datasets, and accelerating risk identification, the defining development of 2026 is not technological capability, but regulatory and supervisory enforcement of AI accountability.
The European Union provides a clear reference point. With the [EU Artificial Intelligence Act](https://swissgrc.com/en/the-eus-ai-dilemma-innovation-or-over-regulation/) entering its practical implementation phase, organizations are now required to move beyond high-level principles and demonstrate how AI systems are classified, governed, monitored, and controlled in practice. Risk-based categorisation, transparency obligations, human oversight requirements, and documentation standards are no longer theoretical constructs; they are becoming operational expectations that will be tested through audits, supervisory reviews, and enforcement actions. Importantly, this shift is not confined to Europe. Other regions are advancing their own approaches to AI governance, reflecting different regulatory philosophies but converging similar expectations around accountability and control. India is progressing toward a framework that emphasises responsible AI use, transparency, and alignment with sectoral regulation, particularly in financial services and public-sector applications. In the United Arab Emirates, AI governance is being embedded into national digital strategies, with strong focus on ethical use, security, and state oversight. Saudi Arabia is advancing AI governance as part of its broader economic transformation agenda, linking AI deployment to national standards, data governance, and risk management requirements.
Taken together, these developments signal a global reality for 2026: organizations operating across regions must navigate multiple AI governance regimes simultaneously, each with distinct legal structures but shared expectations around explainability, risk management, and human accountability. The challenge is no longer whether AI can be governed, but whether governance models are sufficiently mature to operate across jurisdictions and withstand regulatory scrutiny. In this environment, effective AI governance requires a clear separation between automation and accountability. AI systems can support faster and more informed decision-making, but they cannot replace responsibility. Organizations must be able to explain how AI-driven outcomes are generated, who is accountable for their use, and how risks such as bias, error, and unintended consequences are identified and mitigated. Human oversight is not a safeguard of last resort; it is a core design principle.
Adaptive Governance: Agility as a Core Capability
The pace of regulatory change, digital transformation, and systemic risk has exposed the limitations of static, review-cycle-driven models. Annual assessments and policy updates are increasingly misaligned with supervisory expectations-particularly as regulators shift from implementation guidance to active auditing and sanctioning.
This shift is evident across key regions. In Switzerland, the Crypto-Asset Reporting Framework (CARF) will enter into force on 1 January 2026, introducing new transparency and reporting obligations that span tax, compliance, data, and IT functions. In the European Union and the DACH region, the extension of Corporate Sustainability Reporting Directive (CSRD) requirements to large, unlisted companies significantly expands the scope and depth of disclosure expectations, raising the bar for internal controls, data quality, and management accountability. At the same time, supervisory authorities overseeing the [Digital Operational Resilience Act (DORA)](https://swissgrc.com/en/digital-operational-resilience-act-dora/) and the [Network and Information Security Directive (NIS2)](https://swissgrc.com/en/network-information-security-directive-nis2/) are moving beyond rollout phases toward structured audits and enforcement actions. The emphasis is no longer on whether frameworks exist, but on whether they are operational, effective, and demonstrably embedded in day-to-day processes.
Similar enforcement-driven dynamics are emerging beyond Europe. In the United Kingdom, regulatory expectations around operational resilience, third-party risk, and cyber oversight-driven by the [Operational Resilience Framework](https://www.bankofengland.co.uk/financial-stability/operational-resilience-of-the-financial-sector) and sector-specific supervisory guidance-are increasingly assessed through thematic reviews and supervisory interventions rather than self-attestation. In the United States, regulators are intensifying scrutiny around cybersecurity disclosures, data protection, and third-party risk management, with growing emphasis on executive accountability and evidence-based controls. Across the Middle East, Africa, and Asia-Pacific regions, regulatory maturity is accelerating rapidly. Authorities are strengthening requirements related to cybersecurity, data protection, outsourcing, and operational resilience, while shifting toward more active supervision and enforcement.
Privacy Compliance in a Data-Driven World and the Expanding Role of Technology
Privacy compliance remains one of the most critical and closely scrutinized areas of enterprise risk management as organizations move toward 2026 in increasingly data-driven operating environments. This shift is already evident in current investment behavior. According to [PwC’s Global Compliance Study 2025](https://www.pwc.com/gx/en/issues/risk-regulation/pwc-global-compliance-study-2025.pdf), 82% of companies plan to invest more in technology to drive compliance activities, with cybersecurity and data protection identified among the top compliance risk priorities. These findings provide a clear leading indicator for 2026: organizations recognize that manual and fragmented approaches to privacy compliance are no longer sustainable in the face of growing data volumes and regulatory complexity.
In practice, the expanding role of technology is reshaping how privacy compliance is executed in 2026. Organizations are strengthening data governance frameworks, implementing structured consent management, enforcing role-based access controls, and enabling continuous auditability through integrated systems. Privacy-by-design is increasingly embedded into business processes and technology architectures, shifting compliance earlier in the lifecycle of products, services, and data usage.
Business Resilience as a Board-Level Imperative
Business resilience has become a defining capability for organizations entering 2026. Cyber threats, geopolitical uncertainty, regulatory pressure, and increasingly fragile supply chains have elevated resilience from an operational concern to a board-level responsibility. Disruptions are no longer viewed as exceptional events, but as a recurring feature of today’s risk landscape, requiring structured, forward-looking preparedness.
This shift is reflected in both practice and research. Recent industry insights, including those highlighted in the [ERM Report 2025](https://swissgrc.com/en/erm-report-2025-why-most-crises-start-within/), point to a growing recognition that resilience cannot be managed in isolation or addressed through static continuity plans. Instead, organizations are expected to integrate resilience into their broader risk management and governance structures, linking it directly to strategic decision-making and value protection., point to a growing recognition that resilience cannot be managed in isolation or addressed through static continuity plans. Instead, organizations are expected to integrate resilience into their broader risk management and governance structures, linking it directly to strategic decision-making and value protection.
Cybersecurity governance remains a critical pillar of this evolution. Continuous monitoring, regular risk assessments, and tested incident response and recovery capabilities are now baseline expectations rather than advanced practices. At the same time, third-party risk management is gaining increased attention, as organizations acknowledge that operational resilience extends beyond their own perimeter. Disruptions at suppliers, service providers, or technology partners can have immediate and material consequences for service continuity, regulatory compliance, and customer trust.
In 2026, resilient organizations are those that combine preparedness, adaptability, and coordinated execution. By embedding resilience into risk management, governance, and day-to-day decision-making, organizations are better positioned to navigate uncertainty, protect stakeholders, and sustain operations in an increasingly volatile environment.
Conclusion
In 2026, Governance, Risk, and Compliance is no longer in transition. The operating environment has already shifted, and expectations from regulators, boards, and stakeholders are now firmly established. What differentiates organizations today is not whether GRC frameworks exist, but whether they are fit for execution in real time-capable of supporting decision-making, withstanding supervisory scrutiny, and enabling resilience under sustained pressure. Across industries and regions, GRC is being tested simultaneously on multiple fronts. Artificial intelligence is accelerating insight and automation while raising new accountability requirements. Regulatory regimes are moving decisively from implementation to enforcement, demanding evidence of effectiveness rather than intent. Privacy and data protection have become visible indicators of trust, and resilience is assessed by an organization’s ability to continue operating through disruption, not simply recover after the fact.
For leaders in 2026, the challenge is no longer balancing innovation and control. It is ensuring that innovation is governed with clarity, speed, and accountability. Effective GRC now functions as an operating capability, one that connects risk insight, regulatory compliance, and strategic execution across the enterprise. Organizations that embed governance, risk, and compliance into daily decision-making, supported by reliable data, appropriate technology, and clear ownership, are better positioned to navigate uncertainty, respond confidently to regulatory scrutiny, and sustain performance in an increasingly complex global environment.
In 2026, **GRC is not about preparing for the future-it is about performing in the present**.
**Catégories:** Industry News
---
### [Global Risks Report 2026: How geoeconomics, AI and societal fractures are reshaping risk](https://swissgrc.com/fr/global-risks-report-2026-how-geoeconomics-ai-and-societal-fractures-are-reshaping-risk/)
**Published:** janvier 14, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** The annual Global Risks Report published by the World Economic Forum remains one of the most closely followed publications for leaders in business, government, and civil society. Drawing on the perspectives of more than 1,300 global experts, the 2026 edition captures a world entering an “Age of Competition”.
**Content:**
**The annual Global Risks Report published by the World Economic Forum remains one of the most closely followed publications for leaders in business, government, and civil society. Drawing on the perspectives of more than 1,300 global experts, the 2026 edition captures a world entering an “Age of Competition,” where geoeconomic rivalry, rapid technological acceleration, and deepening societal fragmentation are reshaping the global risk landscape.**
More than a snapshot of individual threats, the report highlights how risks are increasingly interconnected, compounding, and unfolding at a pace that challenges traditional governance and risk management approaches. Taken together, these findings point to a broader shift in the nature of global risk. The [Global Risks Report 2026](https://www.weforum.org/publications/global-risks-report-2026/) arrives at a moment when uncertainty is no longer episodic but structural. Based on insights from more than 1,300 global leaders and experts, the report depicts a world entering what it defines as an “Age of Competition”. The latter is characterized by intensified geoeconomic rivalry, accelerating technological change, and deepening societal fragmentation.
Beyond individual risk rankings, the report reveals a more consequential development: risks are compounding faster than governance and decision-making structures are adapting. For organizations operating across jurisdictions, technologies, and value chains, this shift fundamentally alters how risk must be understood and managed.

Geoeconomic confrontation moves to the centre of the risk landscape
For the first time, **geoeconomic confrontation** ranks as the most severe short-term global risk, identified by 18% of respondents as the risk most likely to trigger a material global crisis in 2026. It also holds the top position in the two-year outlook to 2028, reflecting sustained concern rather than a temporary spike.
The significance of this finding lies not only in its ranking, but in its breadth. Geoeconomic confrontation encompasses sanctions, export controls, investment screening, subsidies, and supply-chain restrictions. These are measures increasingly deployed in pursuit of national security and strategic autonomy.
For organizations, this translates into heightened exposure across multiple dimensions simultaneously: regulatory compliance, third-party dependencies, data flows, technology access, and market participation. Risk is no longer confined to operational failure or financial volatility; it is increasingly shaped by policy-driven fragmentation of the global economy.
Economic risks are rising sharply in the near term
The report identifies economic risks as the category with the sharpest increase in perceived severity over the next two years. Compared with the previous edition:
- Economic downturn rises eight positions to rank 11th
- Inflation rises eight positions to 21st
Asset bubble burst rises seven positions to 18th
These shifts reflect concerns around high debt burdens, volatile markets, and the interaction between economic stress and geopolitical tensions. Importantly, the report shows that economic risks are closely interconnected with inequality, which remains the most interconnected global risk for the second consecutive year. This reinforces an important insight: economic shocks do not occur in isolation. Their impact is magnified where social trust is fragile and institutional capacity is strained.
Technology risks accelerate, with AI emerging as a long-term concern
Technological risks continue to rise in prominence. In the two-year outlook, **misinformation** and **disinformation** rank second overall, while **cyber insecurity** ranks sixth. Both are already shaping the operational and reputational risk landscape for organizations. More notably, adverse outcomes of AI technologies show the largest increase in ranking between the short-term and long-term horizons, moving from near the bottom of the two-year ranking to fifth place in the 10-year outlook.
This trajectory reflects growing awareness that AI-related risks, ranging from biased decision-making and opaque algorithms to large-scale misinformation, will intensify as adoption accelerates. The report positions AI not as a standalone risk, but as a cross-cutting amplifier of societal, economic, and security challenges. From a governance perspective, this reinforces the importance of structured oversight, clear accountability, and lifecycle-based risk management for AI systems. These are issues increasingly addressed through emerging regulatory frameworks.
Societal polarization and inequality act as risk multipliers
Societal risks remain a defining feature of the global outlook. **Societal polarization** ranks fourth in the current risk landscape, while **inequality** ranks tenth in the short term and seventh in the 10-year outlook.
What distinguishes these risks is their **degree of interconnectedness.** The report’s interconnections analysis shows inequality influencing a wide range of other risks, including economic downturn, misinformation, erosion of civic freedoms, and social unrest. For organizations, this has direct implications. Operating environments marked by declining trust and heightened polarization tend to experience:
- Faster escalation of reputational incidents
- Greater regulatory scrutiny
- Reduced tolerance for opaque or inconsistent decision-making
Societal context, therefore, becomes a material factor in enterprise risk exposure, not merely a background condition.
Infrastructure and resilience under growing pressure
Another key theme in the report is the vulnerability of **critical infrastructure**, both physical and digital. **Disruptions to critical infrastructure** rise four positions in the short-term outlook, reflecting concerns over cyberattacks, ageing systems, climate-related stress, and geopolitical targeting. The report highlights infrastructure as an increasingly contested domain, where failures can cascade rapidly across sectors and borders. This reinforces the need for organizations to understand not only their own resilience, but also their dependencies on third parties, service providers, and interconnected systems.
A demanding outlook for decision-makers
The overall sentiment captured in the report is sobering. 50% of surveyed leaders and experts expect a turbulent or stormy global outlook over the next two years, rising to 57% over the next decade. Only 1% anticipate a calm outlook across either time horizon.
This reflects a recognition that traditional risk models, often linear, siloed, and retrospective, are increasingly misaligned with today’s risk dynamics. The challenges ahead are not defined by single shocks, but by the interaction of multiple stressors unfolding at speed.
Conclusion
The Global Risks Report 2026 underscores a fundamental shift: risk has become more interconnected, more politicised, and more accelerated than the systems traditionally used to manage it. Geoeconomic rivalry, technological acceleration, and societal fragmentation are no longer parallel developments; they are mutually reinforcing forces reshaping the global risk landscape.
For organizations, this places a premium on integrated governance, forward-looking risk management, and resilience-oriented decision-making. The ability to understand interdependencies across domains, anticipate compounding effects, and demonstrate consistent oversight will increasingly differentiate those that can navigate uncertainty from those that merely react to it.
In this context, the evolution of risk governance is inseparable from the evolution of the tools that support it. Fragmented spreadsheets, isolated controls, and static reporting are poorly suited to a risk environment defined by speed, connectivity, and regulatory complexity. Platforms such as the [GRC Toolbox](https://swissgrc.com/en/solutions/), designed to integrate governance, risk, and compliance across domains, reflect how organizations are beginning to operationalise the kind of holistic, adaptive risk management that the report implicitly calls for.
Seen this way, the Global Risks Report 2026 is not only a diagnosis of global risk, but a clear signal: **the way risk is governed and the systems that underpin it must evolve just as rapidly as the risks themselves**.
**Catégories:** Industry News
**Étiquettes:** First
---
### [Swiss GRC Joins G[P]RC Summit 2026 as Platinum Sponsor](https://swissgrc.com/fr/swiss-grc-joins-gprc-summit-2026-as-platinum-sponsor/)
**Published:** janvier 27, 2026
**Author:** Vaishali Moitra
**Excerpt:** Swiss GRC participated as a Platinum Sponsor at the G[P]RC Summit 2026 in Riyadh, co-sponsoring with StorIT. The company contributed to strategic discussions on integrating GRC with performance and resilience, aligning risk management with Vision 2030 ambitions in a rapidly evolving, hyperconnected business environment.
**Content:**
**Riyadh, Saudi Arabia – 2026 – Swiss GRC participated as a Platinum Sponsor at the G\[P\]RC Summit 2026, held in Riyadh, Saudi Arabia. The summit convened senior leaders, regulators, and practitioners from across the globe to explore how organizations can strengthen governance, risk, compliance, and resilience in an increasingly complex and interconnected business environment.**
The Riyadh edition of the G\[P\]RC Summit 2026 took place at a pivotal moment for organizations across the Kingdom, as Saudi Arabia continues to advance its ambitious Vision 2030 agenda. Accelerated digital transformation, heightened regulatory expectations, and growing interdependencies across technology, supply chains, and third parties are reshaping how enterprises approach risk and strategic execution. Against this backdrop, Swiss GRC contributed to key discussions on aligning GRC with business objectives and long-term performance.
As part of its Platinum engagement, Swiss GRC co-sponsored the summit alongside StorIT, reinforcing a shared commitment to advancing integrated, outcome-driven approaches to governance, risk management, and operational resilience across the Middle East region.
During the summit, **Rajeev Dutt**, **General Manager – MEA & APAC, Swiss GRC**, delivered a keynote session titled **«Enabling Strategic Risk & Resilience.»** His presentation emphasized the shift from reactive, compliance-driven GRC models toward integrated, strategy-aligned operating frameworks that support confident decision-making in volatile environments.
Framing today’s operating landscape through the VUCA lens-volatility, uncertainty, complexity, and ambiguity-Rajeev highlighted that disruption is no longer an exception but a constant. He stressed that strategic risk is the category most likely to generate enterprise-level impact and therefore must be explicitly linked to organizational objectives. Without this linkage, risk management risks becoming an exercise in measuring activity rather than managing impact.
Swiss GRC was represented in Riyadh by a strong leadership team, underscoring the company’s strategic commitment to the Middle East. Rajeev Dutt was joined by **Babu Manickan**, Head of Presales – MEA & APAC (GRC), and **Yahya Mohamed Mao**, Chief Marketing Officer, who successfully represented Swiss GRC on the ground. They were accompanied by **Besfort Kuqi**, Chief Executive Officer, **Gentian Ajeti**, Chief Customer & Commercial Officer. This strong leadership presence reinforced Swiss GRC’s long-term focus on the region while highlighting its growing global footprint and ability to address diverse GRC needs worldwide.
Swiss GRC’s Platinum participation at the G\[P\]RC Summit 2026 in Riyadh marks another important milestone in the company’s journey toward establishing itself as a global leader in the GRC space. Through its co-sponsorship with StorIT and active engagement with regulators, industry experts, and decision-makers, Swiss GRC continues to elevate conversations around GRC best practices, regulatory compliance, and strategic risk management. As demand for integrated GRC solutions continues to grow, Swiss GRC remains well positioned to support organizations in navigating complexity with confidence, resilience, and strategic foresight.
About G\[P\]RC Summit 2026
The G\[P\]RC Summit is the world’s largest summit focused on GPRC–Governance, Performance, Risk, and Compliance–bringing together C-level executives, GRC experts, and professionals from industry and academia worldwide. The summit serves as a global platform for sharing insights, innovative solutions, and best practices required to drive organizational success and resilience.
The 2026 edition is centred around the theme **«Driving Success: Integrating GRC with Strategy Execution in a Hyperconnected World»** with a strong emphasis on aligning governance and risk management with performance, strategy, and sustainable growth–particularly in the context of large-scale transformation initiatives such as Saudi Arabia’s Vision 2030.
**Catégories:** Industry News
**Étiquettes:** First
---
### [When Risk Enters Through the Front Door: Rethinking Vendor Risk Management ](https://swissgrc.com/fr/when-risk-enters-through-the-front-door-rethinking-vendor-risk-management/)
**Published:** mars 23, 2026
**Author:** Vaishali Moitra
**Excerpt:** Modern enterprises rely on extensive vendor ecosystems to drive innovation and growth. However, these relationships also introduce significant risks. Without integrated governance and visibility, vendor disruptions, cyber incidents, or compliance failures can quickly escalate into enterprise-wide challenges.
**Content:**
## The Expanding Enterprise
Modern organizations no longer operate within clearly defined boundaries. Business operations today rely on a vast ecosystem of vendors, suppliers, cloud providers, and technology partners that enable organizations to innovate, scale, and deliver services faster than ever before.
But with this interconnected ecosystem comes a new reality: risk now travels through these relationships.
Third parties are increasingly embedded in critical processes, operational infrastructures, and data environments. As organizations grow more dependent on external partners, the risks associated with these relationships grow just as quickly. Disruptions, cybersecurity incidents, compliance failures, or operational breakdowns within a vendor ecosystem can quickly cascade into enterprise-wide challenges.
Vendor relationships are no longer simply operational partnerships -they are now a central component of the organization’s risk landscape.
## Data and Technology: The Missing Foundation
Another key insight from the survey highlights a fundamental challenge: data quality.
Only [17% of organizations](https://kpmg.com/de/de/dienstleistungen/audit/forensic/global-third-party-risk-management-survey-2026.html)report having fully reliable and integrated data supporting their third-party risk management decisions, which directly affects the effectiveness of automation, analytics, and risk assessments.
At the same time, organizations are increasingly exploring the use of artificial intelligence and advanced technologies within TPRM processes. More than half of organizations report experimenting with AI for activities such as risk assessments, reporting, and supplier data analysis, yet only a small portion believe these technologies are currently delivering significant value.
The lesson is clear: technology alone is not enough.
Without strong data governance and integrated risk processes, organizations struggle to turn vendor data into meaningful risk insights.
## Moving Toward Connected Vendor Governance
To address these challenges, organizations are increasingly shifting toward connected governance models where vendor risk is embedded directly within enterprise risk and compliance frameworks.
Vendor Risk Management must evolve beyond onboarding questionnaires or vendor inventories. It must become a continuous governance capability that connects vendor relationships with enterprise risks, internal controls, compliance obligations, and operational resilience.
Within the Swiss GRC platform, [Vendor Risk Management](https://swissgrc.com/en/tprm-software/)is integrated into a broader Connected GRC ecosystem. This enables organizations to link vendor relationships directly with enterprise risk management, internal control systems, and governance workflows, creating a unified perspective of third-party risk.
This integrated approach helps organizations move from fragmented oversight toward a structured and transparent view of their extended enterprise.
## Governing The Extended Enterprise
As digital ecosystems continue to expand, vendor relationships will only become more complex and more critical to organizational resilience.
Organizations that treat Vendor Risk Management as an isolated process will struggle to keep pace with this complexity. Those that integrate vendor oversight into a broader governance framework will gain something far more valuable -visibility.
Because in today’s interconnected world, risk rarely stays confined within organizational boundaries.
It moves through the ecosystems that organizations build every day.
And managing that ecosystem effectively has become one of the defining priorities of modern governance.
**Catégories:** Industry News, TPRM
---
### [When GRC Stopped Being Periodic - and Became Everyday Work ](https://swissgrc.com/fr/when-grc-stopped-being-periodic-and-became-everyday-work/)
**Published:** mars 31, 2026
**Author:** Vaishali Moitra
**Excerpt:** GRC has shifted from periodic reviews to continuous oversight. Risks emerge daily, evidence must be immediate, and decisions depend on connected context. When risk, controls, and compliance operate as one system, governance becomes embedded in everyday work enabling faster decisions and sustained organizational confidence.
**Content:**
“***It used to be enough to review risk once a year.***
***Now risk reviews happen before lunch***.”
It’s just past 9 a.m.
Before the first meeting of the day, the questions begin:
- A business team wants to onboard a new vendor-*does this require a risk review?*
- IT flags a control exception but can’t say how critical it is
- Legal asks for evidence that a policy was followed-not just approved
None of this feels extraordinary anymore.
What feels different is the pace.
Governance, Risk and Compliance has quietly shifted from a scheduled activity to a daily conversation. And most organizations are still catching up to what that really means.
GRC No Longer Moves in Cycles
For years, GRC followed a predictable rhythm: annual risk assessments, planned audits, quarterly reporting. That rhythm gave teams time-time to prepare, to document, to reconcile.
That time is mostly gone.
Risks now emerge mid-project. Controls fail in execution, not documentation. Regulatory expectations evolve faster than internal processes can adapt.
As one compliance leader put it:
“We didn’t lose control. The environment just stopped waiting for us.”
The challenge today isn’t a lack of effort or intent. It’s that the operating model behind GRC hasn’t evolved at the same speed as the world around it.
The Quiet Cost of ‘Mostly Under Control’
On paper, many organizations are doing fine.
Policies exist. Risk registers are maintained. Audits get completed.
But beneath the surface, GRC teams experience a different reality:
- The same risk is assessed multiple times by different teams
- Evidence lives in systems that don’t align
- Decisions are delayed because data must be validated first
This doesn’t create dramatic failure. It creates friction.
And friction has a cost-missed signals, slower decisions, and teams spending more time reconciling information than interpreting it.
As one risk manager described it:
“The work isn’t hard. The coordination is.”
The Real Challenge isn’t Risk- It’s Connected
Most organizations don’t suffer from a lack of GRC data. They suffer from a lack of connection.
Risk data sits in one place. Control evidence in another. Audit findings somewhere else.
Each dataset tells a partial truth. But the full story only emerges when someone manually connects the dots.
That manual effort is where GRC loses momentum-and credibility.
When leaders ask simple questions like *“Is this risk under control?”* or *“What changed since last quarter?”*, the answer often takes longer than it should. Not because teams don’t know-but because the information isn’t designed to speak together.
When GRC Works, It Feels Almost Invisible
Interestingly, the most mature GRC environments don’t feel heavy or restrictive.
They feel calm.
Issues surface early. Exceptions are visible, not buried. Conversations are grounded in shared facts.
In these environments, GRC doesn’t slow the business down. It allows decisions to move forward with confidence.
As one executive noted:
“Good GRC doesn’t shout. It reassures.”
That shift doesn’t come from more policies or more reports. It comes from treating GRC as a living system, not a checklist to be revisited once a year.
How Swiss GRC Helps Make This Possible
Organizations that move toward this calmer, more connected state often rethink how GRC information is structured and shared. This is where platforms such as Swiss GRC help quietly shape the journey.
Rather than treating risk, controls, compliance, audit, and security as separate activities, [Swiss GRC](https://swissgrc.com/en/) supports a unified approach-where these elements are linked by design. Risk assessments inform controls, controls feed audit readiness, and evidence is generated as part of daily work instead of being reconstructed later. The value is not automation for its own sake, but continuity: fewer handovers, clearer ownership, and better context when decisions need to be made. For many organizations, this reduces the constant reconciliation effort and allows GRC teams to focus on insight and action rather than coordination.
The Question GRC Leaders Are Asking Now
The most important GRC question today isn’t:
“Are we compliant?”
It’s:
“If something changes tomorrow, will we see it-and know what to do?”
That question cuts across compliance, security, legal, and leadership. And it can’t be answered with static reports or periodic reviews.
It requires visibility, continuity, and shared understanding-every day, not just during audits.
A Closing Thoughts
The future of GRC won’t be louder, stricter, or more complex.
It will be:
- Quieter
- Clearer
- Embedded into everyday decisions
When GRC stops feeling like an interruption-and starts feeling like infrastructure-you know the journey is moving in the right direction.
**“The best governance doesn’t control the business. It gives the business confidence to move.”**
**Catégories:** Industry News
**Étiquettes:** First
---
### [When Security Work Exists -But Security Confidence Doesn’t ](https://swissgrc.com/fr/when-security-work-exists-but-security-confidence-doesnt/)
**Published:** mai 5, 2026
**Author:** Vaishali Moitra
**Excerpt:** Modern enterprises rely on extensive vendor ecosystems to drive innovation and growth. However, these relationships also introduce significant risks. Without integrated governance and visibility, vendor disruptions, cyber incidents, or compliance failures can quickly escalate into enterprise-wide challenges.
**Content:**
Most organizations today already *do* information security.
They maintain asset lists. They run vulnerability scans. They review access rights. They write policies.
Yet the uncomfortable moment still happens:
“Can we prove this was controlled last quarter?”
Silence.
Not because the work wasn’t done – but because the work lives in different places.
Security emails sit in inboxes. Risk registers sit in spreadsheets. Controls sit in documents. Ownership sits in people’s heads.
So, when an audit, incident, or customer questionnaire arrives, teams don’t check security -they **reconstruct it.**
That gap between performing security and demonstrating it is where many Information Security Management Systems (ISMS) fail in practice.
The Real Problem Isn’t Missing Controls
It’s Missing Continuity
In theory, an ISMS is simple: identify assets, assess risks, apply controls, review regularly.
Security is continuous while documentation is periodic.
Teams assess risks when projects start, but not when environments change. Assets are listed during onboarding, but not during shadow IT growth. Controls are defined, but their operation isn’t visible over time.
So, the organization becomes compliant at points -not secure over time.
An ISMS software helps only if it changes how security work happens daily, not only during audits.
What an ISMS Should Actually Enable
**1. Security should follow the asset -not the spreadsheet**
When a vulnerability appears, the key questions are always operational:
- What system is affected?
- Who owns it?
- What data does it handle?
- What risk does it create?
If answers require three meetings and two exports, the ISMS is documentation, not management.
A practical ISMS connects assets, risks, controls, and ownership so the impact is visible immediately -not compiled later.
**2. Evidence should be a by-product of work**
Security teams often spend more time proving actions than performing them.
A mature ISMS approach means:
You don’t prepare evidence. Evidence accumulates automatically as work happens.
Reviews, approvals, risk assessments, and control checks leave a trail without someone consciously “creating audit proof.”
**3. Security is cross-functional -the system should reflect that**
Information security isn’t only IT’s responsibility:
- HR trigger’s identity lifecycle events
- Procurement introduces vendor risks
- Business units classify data
- Legal defines obligations
If security depends on one department collecting updates from others, it becomes periodic. If each team works within a shared structure, it becomes continuous.
**4. Monitoring matters more than documentation**
Many organizations have perfectly written policies and still face incidents.
Because the real question is not:
“Was the control designed?”
But:
“Was the control working last Tuesday?”
Continuous visibility -not policy completeness -defines operational security maturity.
Where Tools Like Swiss GRC Fit In
When security exists only as documentation, confidence depends on memory. When security exists as a system, confidence depends on records.
That difference shows up during:
- audits
- incidents
- customer due diligence
- regulatory reviews
Organizations don’t struggle because they lack security work. They struggle because they cannot see it over time.
An [effective ISMS](https://swissgrc.com/en/information-security-management-isms-software/) doesn’t make a company “more secure” overnight. It makes security observable -and once something is observable, it becomes manageable.
And that’s usually the point where security stops feeling like a yearly project and starts functioning like an everyday operation.
The Practical Outcome
When security exists only as documentation, confidence depends on memory. When security exists as a system, confidence depends on records.
That difference shows up during:
- audits
- incidents
- customer due diligence
- regulatory reviews
Organizations don’t struggle because they lack security work. They struggle because they cannot see it over time.
An effective ISMS doesn’t make a company “more secure” overnight. It makes security observable -and once something is observable, it becomes manageable.
And that’s usually the point where security stops feeling like a yearly project and starts functioning like an everyday operation.
**Catégories:** Industry News
---
### [NIS2 Is Not an IT Project: Why Businesses Need to Rethink Cybersecurity](https://swissgrc.com/fr/nis2-is-not-an-it-project-why-businesses-need-to-rethink-cybersecurity/)
**Published:** mai 6, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** When people talk about NIS2 today, one comparison comes up repeatedly:
“This will be the GDPR of cybersecurity.” The comparison sounds logical, but it is misleading and pushes many organizations in the wrong direction. NIS2 is not simply another compliance regulation. The directive fundamentally changes how organizations must manage digital risk.
**Content:**
**When people talk about NIS2 today, one comparison comes up repeatedly: “This will be the GDPR of cybersecurity.” The comparison sounds logical, but it is misleading and pushes many organizations in the wrong direction.**
The [NIS2 Directive](https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX%3A32022L2555) is not simply a compliance regulation. It fundamentally changes how organisations must approach digital risk — shifting the focus away from documentation and towards resilience, operational stability, and accountability at the management level.
Many organisations underestimate precisely this distinction — and in doing so, risk not only regulatory consequences, but operational disruptions, reputational damage, and significant financial exposure. For a broader perspective on how this shift affects day-to-day governance work, see our article [When GRC Stopped Being Periodic and Became Everyday Work](https://swissgrc.com/en/when-grc-stopped-being-periodic-and-became-everyday-work/).
## Why the GDPR Comparison Falls Short
GDPR has established a well-worn playbook in many organisations — and that thinking runs deep:
Criterion GDPR Approach NIS2 Requirement Focus Documentation & evidence Effectiveness & resilience Goal Pass the audit Remain operational under attack Accountability Data Protection Officer Senior management directly Nature Static documentation Dynamic risk management Response React to requests Actively report & manage incidents The focus shifts from "compliance" to "cyber resilience" — and that is not a gradual evolution, but a fundamental change of direction.
## NIS2 Makes Cybersecurity a Management Responsibility
One of the most significant changes introduced by NIS2 concerns the executive level. Cybersecurity can no longer be treated as the sole responsibility of the IT department. According to [BSI guidance on NIS2 implementation](https://www.bsi.bund.de/EN/Themen/Unternehmen-und-Organisationen/Informationen-und-Empfehlungen/Empfehlungen-nach-Angriffszielen/NIS2/NIS2_node.html), senior management must approve security measures, oversee their execution, and receive regular updates on the organisation's security posture.
This fundamentally reshapes [governance structures](https://swissgrc.com/en/risk-management-software/) across many organisations:
**Corporate Governance** Cyber risks become part of the strategic management agenda
**Strategic Relevance** Security decisions escalate to board level
**Personal Liability** Legal exposure for executives moves sharply into focus
**Budget & Priorities** Security investments are reassessed and reprioritised
**Resilience as a Competitive Advantage** Cyber strength becomes a measurable differentiator in the market
Cybersecurity is evolving from a technical discipline into a question of sound corporate governance.
## Mid-Market Companies Face Particular Pressure
Many organisations still assume that NIS2 applies exclusively to operators of critical infrastructure. The reality is considerably broader:
30,000
**companies in Germany alone** are estimated to fall under the new NIS2 requirements — far more than were previously regulated under KRITIS.
[Source: ENISA – NIS2 Overview](https://www.enisa.europa.eu/topics/cybersecurity-policy/nis-directive-new)
Affected organisations span a wide range of sectors:
Industry & Manufacturing Healthcare Logistics & Transport IT & Cloud Services Food Industry Energy Supply Digital Services
The Supply Chain Effect
Even organisations not directly regulated are coming under increasing pressure — because their customers, partners, and principals demand higher security standards. NIS2 explicitly requires the [management of supply chain risks](https://swissgrc.com/en/tprm-software/), extending its reach well beyond directly regulated entities. For a deeper look: [Rethinking Vendor Risk Management →](https://swissgrc.com/en/when-risk-enters-through-the-front-door-rethinking-vendor-risk-management/)
## The Real Problem: Lack of Visibility
In many organisations, IT infrastructure has grown organically over the years. Cloud solutions, external service providers, hybrid working models, and complex system landscapes create new dependencies — while a complete overview of the following is often absent:
- Which systems are business-critical?
- Where are the greatest risks and vulnerabilities?
- Who is responsible for what?
- Which third parties have access to sensitive data?
- What happens in an emergency — and who runs the response?
This is precisely where NIS2 intervenes. The directive demands organisational transformation — not merely the addition of individual security measures.
Concretely, the directive requires structured [risk management](https://swissgrc.com/en/risk-management-software/), incident reporting processes, incident response capabilities, business continuity planning, and supply chain risk consideration. The [BSI provides concrete implementation guidance](https://www.bsi.bund.de/EN/Themen/Unternehmen-und-Organisationen/Informationen-und-Empfehlungen/Empfehlungen-nach-Angriffszielen/NIS2/NIS2_node.html) to support organisations through this process.
---
## Why Spreadsheets and Siloed Tools Are Not Enough
Many organisations are still attempting to address NIS2 with spreadsheets, shared document folders, and isolated tools. The fundamental problem with this approach:
The Core Problem
Cyber resilience is **dynamic**. Risks shift continuously. Suppliers change. Vulnerabilities emerge daily. Reporting obligations demand speed and transparency — neither of which static documentation can deliver.
Organisations need [integrated Governance, Risk and Compliance structures](https://swissgrc.com/en/solutions/) that bring risks, measures, controls, processes, and accountabilities together in one place. Only then is it possible to:
- Continuously prioritise and manage risks
- Implement and track measures effectively
- Produce evidence at any time and in full
- Manage incidents efficiently and within required timeframes
- Meet regulatory requirements on an ongoing basis
## NIS2 Changes the Way Organisations Think About Cybersecurity
Perhaps the most important point is consistently overlooked in the debate: **NIS2 is not simply a regulatory burden.** The directive compels organisations to take a structured, honest look at their digital resilience — and that, in the long run, is precisely where the strategic advantage lies.
Organisations with strong cyber resilience benefit from:
- More stable operations
- Reduced risk of outages
- Greater trust from customers and partners
- Better insurability
- Stronger competitive positioning
- Higher regulatory certainty
According to the [ENISA Threat Landscape 2024](https://www.enisa.europa.eu/publications/enisa-threat-landscape-2024), the frequency and sophistication of cyberattacks targeting European organisations continue to rise. Cybersecurity is becoming an increasingly decisive factor in long-term enterprise value and future viability.
---
## Now Is the Right Time to Act
Many organisations are still waiting for full clarity on national transposition laws or specific regulatory guidance. That is a risky stance: the threat landscape evolves faster than regulatory processes — and the expectations of customers, partners, insurers, and supervisory authorities are rising continuously.
Rather than waiting for regulatory pressure to force action, organisations should move proactively. A practical starting point is the [NIS2 Readiness Check](https://nis2compliant.app) — it shows where your organisation stands in just a few minutes. Or speak directly with our experts in a [Discovery Call](https://swissgrc.com/en/discoverycall/):
1. Assess applicability — are you directly or indirectly regulated?
2. Define governance structures — who owns accountability internally?
3. Systematically evaluate risks — where are the critical gaps?
4. Establish processes — reporting channels, incident response, BCM
5. Clarify responsibilities — up to and including senior management
6. Anchor resilience strategically — as a permanent organisational objective
Because ultimately, NIS2 is not just about compliance. It is about an organisation's ability to remain operational — even under active digital attack.
**Catégories:** Industry News
---
### [Europe’s 2026 Regulatory Direction Sends a Clear Message: Operational Resilience Can No Longer Be Fragmented](https://swissgrc.com/fr/europes-2026-regulatory-direction-sends-a-clear-message-operational-resilience-can-no-longer-be-fragmented/)
**Published:** mai 7, 2026
**Author:** Vaishali Moitra
**Excerpt:** The European Supervisory Authorities (ESAs) have made one thing very clear in their 2026 agenda: financial institutions are entering a new era of governance where digital operational resilience, ICT oversight, incident management, and accountability are becoming central regulatory priorities.
**Content:**
**A technology outage is now a regulatory event. A third-party failure is now a governance failure. Europe’s 2026 regulatory direction makes one thing clear: operational resilience can no longer be treated as someone else’s problem.**
The European Supervisory Authorities (ESAs) have sent a clear message with their 2026 agenda: financial institutions are entering a new era of governance in which digital operational resilience, ICT oversight, incident management, and executive accountability are no longer peripheral concerns — they are central regulatory priorities.
This shift is not simply about adding more regulations. It reflects a broader transformation in how regulators view operational risk across a digitally interconnected financial ecosystem. And for organisations still managing governance in silos, the adjustment will be significant.
## From Fragmented Domains to Integrated Governance
For years, organisations treated cybersecurity, third-party risk, compliance, operational resilience, and business continuity as separate disciplines — managed by different teams, using disconnected systems, with fragmented reporting structures and siloed oversight models.
Digital transformation has fundamentally changed the nature of risk itself. A technology outage can become a regulatory event overnight. A third-party failure can cascade across multiple business functions. A cyber incident can escalate swiftly into reputational damage and financial instability.
£48.65MFCA FINE
**TSB Bank — a governance failure, not just an IT failure.** UK regulators fined TSB £48.65 million following a major IT migration failure that evolved into a full operational resilience breakdown — impacting customers, business continuity, and regulatory confidence. The case set a precedent: technology incidents are now judged as governance events.
[Source: Financial Conduct Authority (FCA)](https://www.fca.org.uk/)
Operational resilience is no longer just an IT responsibility — it is a governance responsibility. Regulators are demanding stronger integration, clearer accountability, and continuous oversight across all governance functions.
## DORA Is Redefining Governance Expectations
At the centre of the ESA's 2026 agenda is the continued operationalisation of the **Digital Operational Resilience Act (DORA)**. Regulators are no longer focused on preparing organisations for DORA compliance in theory — they are actively moving toward supervision, oversight, incident analysis, resilience testing, and enforcement.
Governance Area Previous Expectation DORA-Era Expectation ICT Risk Internal self-assessment Supervised oversight with demonstrable controls Third-Party Risk Contractual due diligence Continuous monitoring & regulatory visibility Incident Reporting Internal logging Structured reporting within strict regulatory timeframes Resilience Testing Periodic, siloed testing Formal TLPT frameworks with cross-entity coordination Accountability IT department responsibility Executive-level governance and personal liability EU-SCICF — Cross-Border Cyber Crisis Coordination
The ESAs are strengthening the EU Systemic Cyber Incident Coordination Framework (EU-SCICF) — a collaborative mechanism for coordinated responses during large-scale cyber incidents affecting the financial ecosystem. Organisations are no longer expected to manage isolated incidents internally. They must demonstrate structured escalation, operational transparency, and coordinated resilience within interconnected digital ecosystems.
In many ways, DORA is reshaping governance from a compliance-driven activity into a **continuous operational discipline**. For a broader view of how this connects to day-to-day GRC practice, see our article [When GRC Stopped Being Periodic and Became Everyday Work](https://swissgrc.com/en/when-grc-stopped-being-periodic-and-became-everyday-work/).
---
## The Rise of Continuous Governance
Traditional governance models were designed for slower-moving operational environments. Periodic audits, annual risk reviews, static controls, and fragmented reporting structures are no longer adequate where digital operations evolve continuously. The ESAs' 2026 focus reflects this reality directly — organisations are now expected to demonstrate six interconnected governance capabilities:
01
**Enterprise-Wide Visibility** A complete, current picture of operational risks across the whole organisation
02
**Third-Party Monitoring** Continuous tracking of dependencies on external ICT providers and vendors
03
**Incident Response** Structured, tested capabilities — not just documented procedures on a shelf
04
**Resilience Testing** Formal TLPT frameworks with evidenced outcomes and cross-entity coordination
05
**Regulatory Reporting** Accurate, timely incident and risk reporting to supervisory authorities
06
**Leadership Accountability** Governance accountability demonstrable at executive and board level
Governance is no longer operating quietly in the background as a compliance function. It is becoming a strategic business capability — directly tied to operational trust, customer confidence, and long-term resilience.
## Why Integrated GRC Is Becoming Essential
As regulatory expectations evolve, organisations are confronting a hard truth: fragmented governance creates dangerous blind spots. Disconnected systems make it difficult to identify emerging risks, coordinate responses, manage incidents efficiently, or maintain enterprise-wide visibility across compliance, operational resilience, cybersecurity, and [third-party oversight](https://swissgrc.com/en/tprm-software/).
An [integrated GRC platform](https://swissgrc.com/en/solutions/) closes these gaps by unifying what today is typically scattered across multiple teams and tools:
- Operational Risk Management
- Compliance Management
- Information Security (ISMS)
- Internal Controls
- Business Continuity Management
- Audit Management
- Third-Party Risk Management
- Incident Reporting & Tracking
Instead of relying on isolated spreadsheets and fragmented reporting, organisations gain centralised visibility, structured governance workflows, audit-ready documentation, and continuous monitoring — across all critical risk and compliance domains simultaneously.
From Reactive to Resilient
Integrated governance helps organisations move away from reactive issue management toward **continuous resilience maturity** — the state regulators increasingly expect as a baseline, not a destination. This is particularly relevant in the context of the risk dynamics explored in our analysis of the [ERM Report 2025: Why Most Crises Start Within](https://swissgrc.com/en/erm-report-2025-why-most-crises-start-within/).
---
## Governance Will Define the Next Generation of Financial Institutions
The regulatory direction emerging across Europe reflects a much larger transformation taking place globally. The future of financial services will not be defined solely by innovation speed, AI adoption, or digital transformation initiatives.
It will increasingly be defined by how effectively organisations govern complexity — connecting risk intelligence, operational oversight, third-party accountability, and leadership responsibility into a coherent, continuous whole. As explored in our article on [when security work exists but security confidence doesn't](https://swissgrc.com/en/when-security-work-exists-but-security-confidence-doesnt/), the gap between effort and assurance is precisely where governance frameworks must close.
In today's digital economy, resilience is no longer a technical objective. It is becoming a defining measure of governance maturity itself — and regulators are starting to treat it as such.
If your organisation is assessing its readiness under DORA or broader ESA expectations, our team is available for a [Discovery Call](https://swissgrc.com/en/discoverycall/) to explore how an integrated GRC approach can support your governance transformation.
**Catégories:** Industry News
---
### [SWISS GRC DAY 2026: Understanding Uncertainty, Making Better Decisions](https://swissgrc.com/fr/swiss-grc-day-2026-review/)
**Published:** mai 24, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** More than 300 executives, risk professionals, academics and public sector representatives gathered at the Radisson Blu Hotel Zurich Airport on 20 May 2026 to discuss the future of GRC management. The central question of the day was clear: How can organizations better understand uncertainty and make more informed decisions in an increasingly complex world?
**Content:**
**More than 300 specialists and executives from the business, public sector and academic worlds gathered at the SWISS GRC DAY 2026 at the Radisson Blu Hotel at Zurich Airport to discuss current challenges and developments in the field of governance, risk and compliance. The event focused on the impact of global uncertainties, the importance of a strong risk culture, and how organisations can better understand risks and make more informed decisions.**
The [SWISS GRC DAY 2026](https://swissgrc.com/swissgrcday) was officially opened by **Besfort Kuqi**, Founder and CEO of Swiss GRC AG. In his welcome address, he thanked the Swiss GRC team for organizing the event and acknowledged the partners who contributed to its success: Silver Partners [Swiss Infosec](https://www.infosec.ch/), [SecurityScorecard](https://securityscorecard.com/), [SNV](https://www.snv.ch/) and [CRIF](https://www.crif.ch/), Knowledge Partner [RiskNET](https://www.risknet.de/), Academic Partner [Lucerne University of Applied Sciences and Arts (HSLU)](https://www.hslu.ch/), and Media Partners [Computerworld](https://www.computerworld.ch/), [GRC Report](https://www.grc-report.de/) and [StrategicRISK](https://www.strategic-risk-global.com/).
Kuqi emphasized the importance of knowledge sharing and collaboration at a time when organizations face growing geopolitical uncertainty, increasing regulatory demands, cyber threats and technological disruption.

Besfort Kuqi
Founder & CEO, Swiss GRC AG
Events such as SWISS GRC DAY provide an opportunity to exchange ideas, challenge assumptions and develop new approaches to managing uncertainty and building resilience.
---
## From Quarantine to Modern Risk Management
The conference was hosted by **Nikolai Tsenov**, Head Solutions & Innovation at Swiss GRC. He opened the event with a historical perspective on the origins of risk management.

Nikolai Tsenov
Head Solutions & Innovation, Swiss GRC AG
During the plague epidemics of the Middle Ages, arriving ships were required to remain isolated for forty days before unloading. The term quarantine originates from the Italian word quaranta, meaning forty. **The underlying principles remain remarkably consistent today: identify risks, structure risks, document risks.**
What has changed is the nature of the challenge. Organizations no longer suffer from a lack of information. Instead, they must determine how to translate vast amounts of information into better decisions.
---
## How Risky Is Our World?
This question formed the basis of the keynote delivered by **Prof. Dr. Werner Gleißner**, CEO of [FutureValue Group AG](https://www.futurevalue.de/) and Professor of Risk Management at TU Dresden.

Prof. Dr. Werner Gleißner
CEO, FutureValue Group AG | Professor of Risk Management, TU Dresden
**Risk management should not focus solely on identifying risks.** Organizations must understand how uncertainty affects strategy, planning and corporate value. Modern approaches such as risk aggregation, scenario analysis and quantitative risk assessment provide important support for this objective.
Drawing on current research and international studies, Gleißner demonstrated that public perception often differs significantly from actual risk exposure. While certain threats dominate headlines, many strategically relevant risks receive comparatively little attention. Geopolitical instability, macroeconomic uncertainty and potential financial crises continue to pose substantial challenges.
He also stressed that while artificial intelligence will increasingly support risk analysis, it cannot replace human judgment. Models and algorithms remain dependent on the quality of assumptions, data and expert interpretation.
[ ↓ Download presentation ](https://swissgrc.com/Downloads/Swiss%20GRC%20Day/1.%20Swiss_GRC_Day%202026_Werner_Gleissner.pdf)---
## Quantifying Risk to Improve Decision-Making
**Florian Worm**, Head of Enterprise Risk Management at the HARTMANN GROUP, demonstrated how quantitative methods can help organizations better understand uncertainty.

Florian Worm
Head of Enterprise Risk Management, HARTMANN GROUP
**Quantification does not eliminate uncertainty, nor does it predict the future.** Instead, it provides greater transparency regarding possible outcomes and their potential impact on organizational objectives.
Particularly in large and complex organizations, risks cannot be assessed in isolation. Understanding interactions and dependencies between risks is essential for evaluating overall exposure and resilience. The presentation highlighted how quantitative approaches support better-informed decisions by making uncertainty more visible and measurable.
---
## Looking Beyond Risk Lists
In her session on black swans, grey rhinos and green dragons, **Alexandra Burns**, Partner and Head Risk & Regulatory Consulting at [PwC](https://www.pwc.ch/), examined the increasing complexity of today's risk landscape.

Alexandra Burns
Partner & Head Risk and Regulatory Consulting, PwC
Resilience depends not only on control mechanisms but also on an organization's ability to anticipate and adapt. Methods such as horizon scanning, strategic foresight and scenario analysis play a critical role in identifying weak signals before they become major disruptions.
She argued that organizations must move beyond static risk registers and begin focusing on interconnected developments and emerging patterns. Geopolitical events, technological innovation, regulatory change and economic uncertainty influence one another and create increasingly complex risk environments.
[ ↓ Download presentation ](https://swissgrc.com/Downloads/Swiss%20GRC%20Day/3.%20Swiss_GRC_Day%202026_Alexandra_Burns.pdf)---
## Why Risk Management Is Ultimately a Question of Culture
Following the networking break, **Michael Niedermann**, Head Consulting at Swiss GRC, shifted the focus from systems and processes to people.

Michael Niedermann
Head Consulting, Swiss GRC AG
**Risk culture cannot be implemented through policies alone.** It is shaped by leadership, trust and the willingness to discuss uncomfortable issues openly.
Despite mature frameworks, policies and technologies, organizations continue to experience failures and unexpected events. The reason often lies not in the absence of controls, but in human behavior — optimism bias, conformity pressure, groupthink and a lack of psychological safety all influence how risks are perceived and communicated.
A live audience survey conducted during the session highlighted that many organizations still face challenges in fostering open communication, leadership accountability and meaningful integration of risk management into decision-making processes.
[ ↓ Download presentation ](https://swissgrc.com/Downloads/Swiss%20GRC%20Day/4.%20Swiss_GRC_Day%202026_Michael_Niedermann.pdf)---
## Science Meets Practice
One of the most engaging sessions of the day featured a debate between **Prof. Dr. Stefan Hunziker** of [Lucerne University of Applied Sciences and Arts](https://www.hslu.ch/) and **Dr. Alexander Hilsbos** of Insel Gruppe.
Prof. Dr. Stefan Hunziker & Dr. Alexander Hilsbos
Lucerne University of Applied Sciences and Arts (HSLU) & Insel Gruppe
Drawing from both academic research and practical experience, they examined which risk management approaches genuinely support decision-making and which methods may create only an illusion of control. **The value of risk management lies not in reports or documentation, but in its ability to improve decisions under uncertainty.**
[ ↓ Download presentation ](https://swissgrc.com/Downloads/Swiss%20GRC%20Day/5.%20Swiss_GRC_Day%202026_Hunziker_Hilsbos.pdf)---
## The Human Side of Uncertainty
The conference concluded with an inspiring keynote by **Zoya Miari**, Founder of Waves to Home. Through personal experiences and powerful storytelling, she brought a human perspective to a day largely focused on governance, strategy and risk.

Zoya Miari
Founder, Waves to Home
Her message served as a reminder that behind every risk, crisis and decision are real people whose lives are affected by uncertainty. **Trust, empathy and human connection remain essential elements of resilience, both within organizations and across society.**
---
## Key Takeaway
[SWISS GRC DAY 2026](https://swissgrc.com/swissgrcday) demonstrated that modern [risk management](https://swissgrc.com/risikomanagement-software/) extends far beyond compliance and documentation.
The organizations that will thrive in the future are not those that eliminate risk, but those that understand uncertainty, recognize interdependencies, encourage open dialogue and use risk insights to make better decisions.
Because the ultimate question is not whether risks exist. The question is how prepared we are to navigate them.
---
Save the Date
SWISS GRC DAY 2027
Wednesday, 5 May 2027
Switzerland's leading conference for Governance, Risk & Compliance returns for its next edition. Mark your calendar now and stay informed.
[Add to calendar →](https://swissgrc.com/swissgrcday)
---
Impressions from Swiss GRC Day 2026


× ‹ ![]() ›
**Catégories:** Events, Industry News
---
### [The Hidden Costs of Process Silos: Why the Future of BPM Lies in Integration with GRC](https://swissgrc.com/fr/the-hidden-costs-of-process-silos-why-the-future-of-bpm-lies-in-integration-with-grc/)
**Published:** juillet 9, 2026
**Author:** Shayeste Afzaly
**Excerpt:** Many companies understand their business processes. They have process maps, documented procedures, and clearly defined responsibilities. At the same time, they assess risks, manage controls, and implement regulatory requirements. Yet what is often missing is the most important element: the big picture.
**Content:**
Processes are not the problem today. Missing connections are.
Many companies know their business processes. They have process maps, documented workflows and clearly defined responsibilities. At the same time, risks are assessed, controls are managed and regulatory requirements are implemented. Yet the essential piece is often missing: the connection.
Business processes are documented in a BPM system, risks are managed in a separate GRC solution, and compliance requirements are maintained in further applications or spreadsheets. Each discipline serves its purpose. At the same time, however, it often operates in isolation from the others.
The result is process silos.
For a long time, that was enough. But the demands placed on companies have changed fundamentally. The question today is no longer whether processes are documented. The decisive question is instead whether companies understand how their processes connect with risks, controls, regulatory requirements and organisational dependencies.
## The world has become more complex. So have processes.
New regulatory requirements such as [DORA](https://swissgrc.com/dora) or [NIS2](https://swissgrc.com/nis2), rising cyber risks, complex supply chains and the increasing use of artificial intelligence are changing the way companies work.
Business processes are long past being isolated workflows. They are directly related to IT systems, third parties, internal controls, policies and regulatory requirements. Every change to a process can affect numerous other areas of the organisation. Yet many companies still view these connections separately.
This is exactly where blind spots arise.
## The real problem is not the process, but the lack of transparency.
### Imagine the following situation:
A critical supplier drops out at short notice. The challenge is not identifying the affected business process. The harder part is understanding the consequences of this change quickly and reliably.
- Which risks does this create?
- Which regulatory requirements are affected?
- Which internal controls no longer take effect?
- Which other business processes depend on it?
- Which systems support these processes?
- And who needs to act now?
Anyone who cannot answer these questions within a short time rarely has a process problem. Much more often, what is missing is the **transparency** around the relationships between processes, risks and compliance.
## Why classic business process management is no longer enough today
Business process management has helped companies for many years to document, standardise and continuously improve their workflows. These foundations remain indispensable in the future as well.
But modern companies need more than well documented processes. They need context. A business process only unfolds its true value once it becomes visible
- which risks are associated with it,
- which controls safeguard it,
- which regulatory requirements apply,
- which systems and third parties are involved,
- and what impact changes have on other areas of the business.
Without these connections, process management often remains static documentation. It does not become an instrument that supports companies in making well founded decisions.
BPM + GRC
## grow together, into a **connected understanding** of the organisation
BPM creates transparency over business workflows, GRC adds risks, controls and regulatory requirements. Processes are no longer viewed in isolation. They become part of an intelligently connected business model.
This is exactly why the boundaries between business process management and governance, risk and compliance are increasingly blurring. While BPM creates transparency over business workflows, GRC adds risks, controls, policies and regulatory requirements to this view. Together, a connected understanding of the organisation emerges.
As a result, companies can not only optimise processes. They can assess the impact of changes faster, meet regulatory requirements more efficiently and make better founded decisions. Processes are thereby no longer viewed in isolation. They become part of an intelligently connected business model.
## From efficiency to resilience
In a time of growing uncertainty, operational efficiency alone is no longer enough.
Organisations need to recognise changes early, assess risks faster and make decisions based on connected information. Resilience therefore does not arise solely through additional controls or new policies. Resilience arises through transparency.
Companies that understand how processes, risks, controls, systems and responsibilities are connected respond faster to change and can develop their organisation in a targeted way.
## Conclusion
The future of business process management does not lie in documenting processes in ever greater detail. It lies in making connections visible. Only when business processes are intelligently linked with risks, controls, regulatory requirements and responsibilities does the transparency emerge that companies need today. The separation between BPM and GRC is thereby losing importance. In its place comes [an integrated approach](https://www.computerworld.ch/themen/pressemeldungen/swiss-grc-stellt-neue-ai-native-prozessmanagement-software-vor) that not only makes processes more efficient, but also helps companies become more resilient, more transparent and more future ready.
**Catégories:** Industry News
---
### [What the 2026 Cyber Threat Landscape Means for GRC and Cyber Resilience](https://swissgrc.com/fr/what-the-2026-cyber-threat-landscape-means-for-grc-and-cyber-resilience/)
**Published:** août 14, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** The cyber threat landscape in Switzerland in the first half of 2026 presents an apparent paradox: While the number of reported incidents is declining, certain types of attacks that are particularly relevant to businesses are increasing significantly. A total of 27,054 cyber incidents were reported to the Federal Office for Cybersecurity (BACS) in the first half of the year.
**Content:**
**The cyber threat landscape in Switzerland presents a seemingly paradoxical situation in the first half of 2026: the number of reported incidents is decreasing, while specific attack forms that are particularly relevant for businesses are increasing significantly.**
27,054 cyber incidents were reported to the Federal Office for Cybersecurity (BACS), a decrease of 6.8 percent compared to the second half of 2025. At the same time, phishing reports rose by 41 percent and reports of malware surged by 85 percent. This is highlighted in a recent [Threat Intelligence Briefing by n’guard.swiss](https://nguard.swiss/cyber-whitepaper/) based on publicly available BACS weekly statistics.
Thus, the key insight does not lie in the overall volume. **The risk profile is changing. And with it, the requirements for governance, risk management, and cyber resilience are evolving.**
The threat may not necessarily increase, but it becomes more challenging
The decline in total reports is largely due to fewer traditional fraud attempts. At the same time, other attack methods are gaining significance. Phishing accounted for 32.7 percent of the analyzed reports in the first half of 2026. Spoofing increased by 42 percent, while malware grew by 85 percent from a significantly smaller initial base.
The quality of attacks is also changing. The n’guard briefing points to AI-driven phishing variants and increasingly credible campaigns targeting corporate access points like Microsoft 365. Meanwhile, methods like ClickFix demonstrate how attackers strategically integrate human behavior into the attack chain: users are prompted to execute harmful commands themselves.
However, these numbers need to be properly contextualized. The BACS statistics capture reported incidents, not the actual total number of cyberattacks in Switzerland. Particularly with more technically sophisticated attacks, there is likely a significant dark figure.
For companies, it is less important whether the number of attacks is statistically rising or falling. What matters is how external threats impact their own risk profile.
Threat Intelligence must become Risk Intelligence
This is exactly where the GRC perspective begins.
An increase in phishing by 41 percent is initially information about the external threat landscape. For management, this information only becomes relevant when it is connected to the company’s own context.
Which identities and systems are exposed? Which critical business processes depend on them? What controls are in place? Which third parties have access? What regulatory obligations could be triggered by an incident? And what impact would an outage have on business operations?
From a GRC perspective, a chain is formed:
**Threat → Asset → Business Process → Risk → Requirement → Control → Incident → Action**
This is how Threat Intelligence becomes [**Risk Intelligence**](https://swissgrc.com/third-party-intelligence-center/).
It is precisely this connection that many organizations still lack. Security Operations, risk registers, compliance requirements, third-party risk management, and business continuity each have valuable information. However, if they are managed in isolation, the crucial overall view remains fragmented.
A cybersecurity incident should not only generate a security ticket. It should also raise the question of whether an existing risk needs to be reassessed, a control adjusted, a third party reviewed, or a resilience scenario updated.
Regulation makes cybersecurity a governance task
The fact that cyber risks can no longer be considered exclusively a technical issue is also demonstrated by regulatory developments.
With the [**NIS2**](https://swissgrc.com/eu-nis2-richtlinie-fuer-cyber-sicherheit/), the EU explicitly places responsibility at the management level. The governing bodies of the affected companies must approve cybersecurity risk management measures and oversee their implementation. The directive connects risk analysis with incident management, business continuity, supply chain security, vulnerability management, and the assessment of the effectiveness of security measures.
In 2026, an important additional element will be introduced: the [**Cyber Resilience Act (CRA)**](https://swissgrc.com/cyber-resilience-act-cra/). Starting from **September 11, 2026**, manufacturers will be required to report actively exploited vulnerabilities and serious security incidents in products with digital components. Among other things, early warning is expected within 24 hours and a follow-up report within 72 hours.
The CRA illustrates a fundamental shift: cybersecurity becomes a task subject to control and testing throughout the entire product lifecycle. Risk assessment, vulnerability management, incident reporting, and responsibilities must be integrated.
Switzerland is also following this development. From **April 1, 2025**, operators of critical infrastructures will have the obligation to report certain cyberattacks. After the discovery of a reportable incident, a report to the BACS must, in principle, be made within 24 hours.
The common direction is clear: **Cybersecurity is increasingly understood regulatorily as a governance and risk management task.**
Cyber resilience begins with connections
The consequence is not to introduce an additional isolated control for every new threat.
Companies must understand how threats, risks, processes, controls, third parties, and regulatory requirements interact. This is where GRC becomes the connecting element between Cyber Security and Cyber Resilience.
Cyber Resilience ultimately means more than just preventing attacks. Organizations must anticipate risks, detect and manage incidents, limit impacts, and be able to restore critical business functions.
A holistic GRC approach provides the necessary transparency: Which critical processes are at risk? What controls protect them? How effective are these controls? What dependencies exist with third parties? What regulatory requirements apply? And where do new threats create additional risks?
The relevant question is not the number of attacks
The 27,054 reported cyber incidents of the first half of 2026 are primarily a signal.
The threat landscape is changing, while CRA, NIS2, and the Swiss reporting obligation simultaneously impose higher demands on risk management, accountability, and traceability.
For companies, one capability becomes crucial: **rapidly translating changes in the external threat environment into their own risk context and making decisions from that.**
The central question is therefore no longer just: *How do we protect ourselves from cyberattacks?*
But rather: **Do we understand which cyber risks actually threaten our business, and can we effectively manage them?**
It is precisely here that GRC and cyber resilience intersect.
**Catégories:** Industry News
---
### [ISO 27001 Certified: Why It Is No Longer Enough Today](https://swissgrc.com/fr/iso-27001-certified-why-it-is-no-longer-enough-today/)
**Published:** août 18, 2026
**Author:** Shayeste Afzaly
**Excerpt:** ISO 27001 provides an important foundation for information security. However, certification alone is no longer enough today. Cyber threats, regulatory requirements, and new dependencies are constantly changing the risk landscape. It is therefore crucial to continuously identify, assess, and effectively manage risks.
**Content:**
ISO 27001 certification is recognised worldwide as one of the most important standards for information security management. It helps organisations protect information assets, systematically assess risks, and establish clear processes for handling security incidents.
For many organisations, certification marks the end of an extensive project. In practice, however, it is only the beginning. The requirements for [Information Security](https://swissgrc.com/informationssicherheit-isms-software/) are constantly evolving. Cyberattacks are becoming more complex, regulatory requirements are increasing, and companies are working with a growing number of suppliers, cloud providers, and digital services. The key question is therefore no longer whether a company is ISO 27001 certified. Much more important is whether risks can be continuously identified, assessed, and managed.
What matters is not the certification alone, but whether risks are continuously identified, assessed, and managed.
## Information security is an ongoing process.
Many companies rely on internal or external audits when managing information security. Risks are assessed regularly, controls are documented, and evidence is collected.
However, the reality changes much faster. New vulnerabilities, cyberattacks, or regulatory changes can create new risks within just a few days. If risks are only reviewed at fixed intervals, developments can remain unnoticed for too long.
A modern information security management system should therefore operate continuously rather than being focused solely on audits.
## Suppliers and service providers need to be actively monitored.
Hardly any company operates without external partners today. Cloud providers, software vendors, and service providers often handle business-critical tasks or process sensitive information.
This creates additional risks that cannot be adequately controlled through a one-time assessment.
### Companies should ask themselves the following questions, among others:
- Which suppliers have access to critical data?
- How high is the risk associated with our key service providers?
- Do our partners continue to meet all security requirements?
- How do we respond to changes in a supplier's risk profile?
Structured Third Party Risk Management creates **transparency** and enables the continuous assessment of all relevant third parties.
## Regulatory requirements are becoming increasingly comprehensive
In addition to ISO 27001, companies today must comply with numerous other legal and regulatory requirements.
These include, for example:
- DORA
- NIS2
- GDPR
- ISO 27701
- Industry-specific requirements
The real challenge is to connect these requirements with existing risks, controls, and responsibilities. If this is managed across different systems or spreadsheets, the effort increases significantly and important connections can easily be lost.
## Artificial Intelligence Creates New Requirements
The use of Artificial Intelligence is continuously increasing in companies. At the same time, new questions are emerging around governance and compliance.
Companies should be able to answer the following questions at any time:
- Which AI applications are being used?
- What data does the AI process?
- Who is responsible?
- What risks arise from this?
- Are regulatory requirements being met?
AI Governance is therefore becoming an important component of modern Governance, Risk, and Compliance Management.
## Management Decisions Require Up-to-Date Information
Today, management needs far more than audit reports or checklists. What matters is having up-to-date information about risks, their impact, and the actions required. Modern dashboards and automated reports help companies identify risks at an early stage, set priorities, and make informed decisions.
## How Swiss GRC Supports Companies
The Swiss GRC Toolbox combines information security management, Enterprise [Risk Management](https://swissgrc.com/risikomanagement-software/), Third Party Risk Management, Internal Control System, Data Protection, Business Continuity Management, and Compliance on a central platform. Risks, controls, processes, and regulatory requirements are interconnected, creating a unified data foundation for the entire organisation. Automated workflows, intuitive dashboards, and flexible reporting help organisations continuously monitor risks and efficiently implement regulatory requirements.
## Conclusion
ISO 27001 certification remains an important milestone for every company. It creates clear structures and provides the foundation for effective information security management.
However, in the face of new cyber threats, increasing regulatory requirements, and growing dependencies on third parties, certification alone is no longer sufficient. Companies need an integrated approach that connects risks, processes, controls, and compliance.
Only in this way can organisations achieve the transparency required to make informed decisions, strengthen cyber resilience, and secure long-term business success.
**Catégories:** Information Security, Industry News
---
### [Embedding Risk in Corporate DNA: Lessons from FERMA Global Risk Manager Survey Report 2024](https://swissgrc.com/fr/embedding-risk-in-corporate-dna-lessons-from-ferma-global-risk-manager-survey-report-2024/)
**Published:** octobre 31, 2024
**Author:** René Schüttel
**Excerpt:** The 2024 FERMA survey highlights a pivotal shift in risk management, with 91% of risk managers now involved in strategic decision-making—moving their role from compliance-focused oversight to an essential driver of business direction.
**Content:**
**In a world of relentless change, organizations must acknowledge that risk management is not a flawless science. Risk is dynamic, often unpredictable, and impossible to control perfectly. However, by adopting a resilient, adaptable approach, companies can embed flexibility and human judgment into their core identity. The FERMA Global Risk Manager Survey Report 2024 emphasizes this need, showing the value of risk management as a guiding force within corporate strategy.**
Effective risk management goes beyond tools; [it empowers people at all levels to make informed, timely decisions in uncertainty](https://www.handelszeitung.ch/insurance/fedpol-perfektes-risikomanagement-gibt-es-nie-383940). This human factor—the ability to interpret and adapt in real time—is essential because today’s complex risk landscapes often exceed the capabilities of any model. By embedding risk awareness into daily operations, organizations create a culture that fosters responsiveness to unexpected challenges. This article explores how [FERMA’s insights](https://www.ferma.eu/publication/global-risk-manager-survey-report-2024/) can help shift risk management from compliance to a core part of corporate DNA, enabling organizations to thrive amid uncertainty.
Risk as a strategic driver and the need for a risk-aware culture
Environmental, Social, and Governance (ESG) risks are now essential components of modern risk management. According to FERMA’s 2024 survey, **57% of risk managers are actively involved in ESG risk analysis**, reflecting regulatory pressures and rising stakeholder expectations. Issues like climate adaptation, carbon neutrality, and social governance have become central to business resilience, underscoring that long-term viability increasingly depends on sustainable practices. Integrating ESG risks into risk management frameworks helps organizations anticipate emerging challenges while aligning with global sustainability goals. Furthermore, by extending the scope from core management of risks to an integrated management of ESG, risk management is able to shift its point of view from the rather retroperspective approach to the more prospective, positive one. Doing so, risk management will move to an integrated management system not only for the management of risks but also for chances and opportunities.
Despite these strides, translating ESG ambitions into actionable results remains challenging. Many organizations struggle with **data limitations and the difficulty of quantifying sustainability risks**, which complicates efforts to integrate ESG within traditional risk structures. Effective ESG risk management requires not only identifying potential threats but also investing in data analytics and collaboration across functions. By building a foundation of reliable ESG data and enabling cross-departmental collaboration, organizations can transform high-level sustainability aspirations into operational strategies that make a measurable impact.
Digital transformation and technology-enabled risk management
Parallel to ESG, digital transformation is reshaping the risk landscape, with **over 50% of organizations leveraging digital tools like predictive analytics, AI, and data visualization** to enhance risk functions. These technologies provide risk managers with greater accuracy and real-time insights for proactive decision-making. According to the FERMA Global Risk Manager Survey Report 2024, organizations are increasingly adopting a range of digital tools to support their risk management efforts (see graphic below).

Technology-backed ERM activities (Source: FERMA Global Risk Manager Survey Report 2024)
The survey indicates that **77% of organizations rely on risk analysis and assessment tools**, with a strong emphasis on interactive visualization for improved monitoring. Other commonly adopted tools include action plan monitoring (71%), risk reporting processes (70%), and quantification of risk impact (70%). As shown, technologies that enable scenario analysis, predictive insights, and Key Risk Indicator (KRI) monitoring are also integral to supporting decision-making in dynamic environments. However, rapid digital adoption introduces significant new risks—particularly cybersecurity threats, which FERMA ranks as a top concern. The surge in [AI and data-driven operations](https://swissgrc.com/en/ai-assistant/), along with expanded interconnectivity, makes robust cybersecurity a critical priority. To manage these digital risks, companies need adaptable frameworks that evolve with technological advancements, combining human oversight with digital insights to preserve strategic judgment. By integrating digital tools as part of a holistic risk framework, organizations can enhance resilience while guarding against potential vulnerabilities. Balancing technological adaptability with a robust cybersecurity approach transforms digital risk management into a proactive, value-driven part of the corporate identity, positioning companies to thrive in an increasingly digital and environmentally conscious world.
Conclusion and recommendations
The FERMA Global Risk Manager Survey Report 2024 underscores that in an era of escalating risks, organizations need more than awareness—they need action. Embedding risk into the corporate DNA requires a proactive, integrated approach that leverages risk management as a strategic asset rather than a compliance exercise. In today’s complex landscape, risk management must be woven into every layer of the organization, empowering companies to anticipate disruptions, make agile decisions, and build resilience into the fabric of their operations.
At [Swiss GRC](https://swissgrc.com/en/), we believe that technology, applied strategically, can transform risk management from a reactive function into a cornerstone of organizational growth. Our [GRC platform](https://swissgrc.com/en/solutions/) enables organizations to centralize risk data, streamline compliance, and gain a comprehensive view of emerging risks. This unified perspective supports informed, forward-looking decision-making and ensures that risk management aligns seamlessly with business goals.
**Ready to make risk a driving force in your organization’s success?** Explore how Swiss GRC’s solutions can transform your risk management strategy into a growth-enabling asset. [Contact us today](https://swissgrc.com/en/discoverycall/) to learn more about integrating comprehensive GRC solutions into your corporate DNA and building a resilient, future-ready organization.
**Catégories:** Industry News
---
### [From Awareness to Action: How GRC Integration Strengthens Cyber Resilience](https://swissgrc.com/fr/from-awareness-to-action-how-grc-integration-strengthens-cyber-resilience/)
**Published:** octobre 24, 2024
**Author:** Bujar Surdulli
**Excerpt:** Cyber resilience requires translating awareness into action by fostering a proactive culture, adopting the right attitude towards risk, and equipping organizations with effective tools. It’s not just about knowing the risks; it’s about embedding that knowledge into every layer of the organization.
**Content:**
**As we approach the end of the Cybersecurity Awareness Month, it’s important to emphasize that while awareness is a crucial first step, it is not enough to tackle today’s sophisticated and evolving threats. Cyber resilience requires translating awareness into action by fostering a proactive culture, adopting the right attitude towards risk, and equipping organizations with effective tools. It’s not just about knowing the risks; it’s about embedding that knowledge into every layer of the organization and ensuring that cybersecurity becomes a shared responsibility.**
Achieving true resilience demands the seamless integration of cybersecurity within a comprehensive Governance, Risk Management, and Compliance (GRC) framework. This approach transcends mere compliance, encouraging a continual assessment of risks and vulnerabilities. By adopting a unified GRC platform, organizations can centralize risk data, streamline compliance, and maintain real-time oversight. Cultivating a culture of awareness and providing teams with the right tools are essential in translating awareness into action. It’s about fostering a proactive mindset throughout the organization, ensuring cybersecurity is not a one-time effort, but a sustained, strategic priority. In doing so, risk management becomes an integral part of business strategy, enabling organizations to remain resilient and prepared in an increasingly complex threat landscape.
Moving beyond compliance-driven cybersecurity
Primary cybersecurity objectives are aligned with the [Network & Information Security Directive (NIS2)](https://swissgrc.com/en/network-information-security-directive-nis2/), the [EU Digital Operational Resilience Act (DORA)](https://swissgrc.com/en/digital-operational-resilience-act-dora/), and other industry-specific regulations. However, these standards often represent the bare minimum and leave organizations vulnerable to emerging threats that compliance frameworks may not fully address. In fact, authentic cyber resilience goes beyond a compliance checklist. It involves creating a proactive risk management culture where security is embedded across the organization. When cybersecurity aligns with GRC, businesses can adopt a comprehensive approach that continuously evaluates risks and mitigates them before they escalate. This shift from reactive compliance to proactive risk management enhances overall security, ensuring organizations remain resilient against evolving threats. As a result, GRC systems should be viewed as the backbone of organizational resilience, supporting both proactive risk management and responsive security strategies.
The role of IT in enabling GRC integration
GRC and cybersecurity must not exist in separate silos. While GRC frameworks establish the governance and policies for risk management, IT provides the tools and infrastructure needed to enforce those policies across the organization. This interdependency highlights the need for a collaborative approach, where IT and risk management work in tandem to achieve security objectives. However, this relationship is more than just the implementation of IT controls or the use of security tools. The real value of GRC lies in its ability to inform decision-making at all levels, ensuring that risks are not only identified but also mitigated through actionable insights. This is where IT’s role becomes vital—not just in monitoring and defending against threats but also in providing the real-time data needed for informed, proactive risk management. By integrating GRC into the IT environment, organizations can automate compliance, streamline governance processes, and centralize risk data. This allows for a more agile response to emerging threats, where risks are continuously assessed and mitigated before they can escalate into full-blown crises.
Managing third-party risks with confidence
Third-party vendors and suppliers are often key entry points for cybercriminals, as breaches in the supply chain can have devastating ripple effects across organizations. According to recent studies, [61% of data breaches](https://www.prevalent.net/blog/2024-third-party-risk-management-study/) involve third-party vendors. Managing these risks is increasingly crucial as businesses become more reliant on external partners.
Integrating GRC into cybersecurity simplifies the management of [third-party risks](https://swissgrc.com/en/tprm-software/) by providing a centralized system to assess, monitor, and manage vendor relationships. Key benefits of GRC integration include:
- **Taxonomy framework:** Managing third-party risks requires transparency about vulnerabilities, cross-organizational dependencies, subprocesses, and third-party involvement. A comprehensive taxonomy framework helps organizations identify and mitigate risks tied to external partners.
- **Automated vendor assessments**: GRC platforms automate the risk assessment process for vendors, ensuring that they meet necessary cybersecurity standards.
- **Continuous monitoring**: Businesses can continuously monitor third-party compliance and address any vulnerabilities before they lead to a breach.
This streamlined approach helps mitigate supply chain risks, ensuring that external partners don’t compromise internal security.
Turning awareness into action with Swiss GRC’s solutions
Contrary to the common belief that cyber resilience can be achieved through a single solution or module, true resilience requires a comprehensive, integrated system of well-structured organizational processes. It involves embedding proactive risk management across the entire organization. At Swiss GRC, we offer a holistic approach by integrating key disciplines such as [Risk Management](https://swissgrc.com/en/risk-management-software/), [Internal Controls (ICS)](https://swissgrc.com/en/internal-control-software-ics/), [Information Security (ISMS)](https://swissgrc.com/en/information-security-management-isms-software/), [Data Protection](https://swissgrc.com/en/data-protection-management-software/), [Business Continuity Management (BCM)](https://swissgrc.com/en/bcm-software/), and [Third-Party Risk Management (TPRM)](https://swissgrc.com/en/tprm-software/) into a robust, organization-wide solution.

This graphic highlights key modules within the GRC Toolbox, showcasing a selection of tools offered by Swiss GRC to enhance governance, manage risks, and ensure compliance—for a resilient and sustainable organization.
Achieving operational resilience, as outlined by standards like **DORA** and **NIS2**, demands more than isolated measures. It requires a consistent identification and classification of critical processes and functions across the organization. By providing the necessary transparency—spanning risk exposures, cross-organizational dependencies, subprocesses, and third parties—Swiss GRC’s solutions help businesses implement a comprehensive taxonomy framework that ensures a clear understanding of risks, vulnerabilities, and assets.
Starting with these classifications and inventories, an organization can better assess the protection needs **related to critical processes and related assets along the typical ISMS protection object categories: authenticity, confidentiality, integrity, availability, and traceability**. Based on this, an organization can assure either adherence with minimal standard defined or conduct more comprehensive Cyber Security Maturity Analysis and calculate the corresponding ratings **along the lines of the five 5 Cyber Security framework functions: Identify, Protect, Detect, Respond and Recover**. From the Data Protection perspective the **categorization and classification of data and persons, processing activities, and recipients** allows for a comprehensive **Data Protection Impact Assessment**, which belongs to a unified and integrated Risk Management view. In this context, **Business Continuity Management (BCM)** is indispensable, ensuring that organizations not only bounce back from adverse events but also emerge stronger and more resilient. Regular **Business Impact Analyses** (BIAs) define criticality through key indicators like **Maximum Tolerable Period of Disruption** and **Recovery Time Objectives**, preparing organizations for a well-structured response to any crisis.
Moreover, resilience is about taking a **proactive stance**. Organizations must identify risks and vulnerabilities before they materialize. Swiss GRC’s solutions support **real-time cyber monitoring** and proactive management, empowering businesses to prevent incidents rather than simply reacting to them. By embedding these best practices into a unified and integrated GRC system, organizations can ensure they remain resilient, adaptable, and prepared in today’s increasingly complex threat landscape.
Cyber resilience, as Swiss GRC demonstrates, involves the seamless integration of various GRC disciplines, ensuring that risks are continuously identified, assessed, and mitigated within a consistent and unified framework. In this way, GRC becomes not only a safeguard but also a strategic enabler of long-term resilience.
[Contact us today](https://swissgrc.com/en/discoverycall/) to learn how our solutions can help your business move from cyber awareness to meaningful action.
Authors: Bujar Surdulli (Swiss GRC), Nikolai Tsenov (Swiss GRC), October 2024
**Catégories:** Software, Information Security
---
### [Pathologists vs. Economists](https://swissgrc.com/fr/pathologists-vs-economists/)
**Published:** juin 6, 2024
**Author:** Nikolai Tsenov
**Excerpt:** "Do you know what is common between economists and pathologists?" This was the question our Behavioural Finance professor asked us in his farewell speech during our graduation ceremony many years ago. Without awaiting any answers, he said: “Economists can always explain everything. What happened, why did it happen and what were the exact causes and reasons?...”
**Content:**
**“*Do you know what is common between economists and pathologists*?” This was the question our Behavioural Finance professor asked us in his farewell speech during our graduation ceremony many years ago. Without awaiting any answers, he said: *“Economists can always explain everything. What happened, why did it happen and what were the exact causes and reasons? They will show you very sophisticated and convincing graphs, will slice and dice data, will provide you with a mount of evidence confirming their explanations … the same as a pathologist will do … but unfortunately, when the patient is already dead.”***
##### The Evolution and Pitfalls of Data Analytics
In the last decades, we have learned to use and take advantage of advanced data analytics, ML, and AI in areas such as Compliance, Risk, and Performance Management. We are modeling the behavior of our business partners, counterparts, and clients based on their actions in the past trying to predict how they will interact and behave in the future. The use of probabilistic approaches to identify risks, threats, and opportunities has become the new normal in the GRC space.
However, if you look around and take a closer look at how this is done, you will realize that the main, and in many cases the only, source of data is the past. The past, which is mainly represented by incidents and losses, performance figures from past financial statements, executed financial transactions, questionnaires, and assessments, in rare cases combined with purely static data describing the relevant circumstances in detail.
Reinforced by our operational blindness (there is a nice and very expressive German word for this phenomenon called “Betriebsblindheit”) we would spend enormous efforts to seek, find, and advocate newer, more sophisticated quantification techniques, and algorithms … invented and used by NASA, Google & Co … and which promise to improve analytical performance such as accuracy and stability of forecasts and quantifications by a few marginal percentage points. In recent years, I have often been sucked in and absorbed by such kind of egocentric exercises and have witnessed these kinds of ego-driven discussions far too often.
##### A Wake-Up Call: The Client’s Feedback
I remember quite well the feedback we received from a customer after one of those exercises a few years ago. I seem to remember it was about modeling and predicting the risk and probability of customer attrition. Quite a disappointing and discouraging statement, that in my humble opinion, sums it up and explains a lot. The client said: “That wouldn’t be anything I wouldn’t see, explain and conclude based on common sense”.
Although we were driven, motivated, and spurred on by the innovative spirit and work we were doing, with the firm conviction that we represented an avant-garde in the Risk Management industry, at that moment I remembered the words of our professor … and really felt like a pathologist, or at least not like someone who is going to “save someone’s life” with his findings and insights.
##### Shifting Focus: The Forward-Looking Approach
This case has affirmed my previously suppressed suspicion that we have been focusing on the wrong place. Not because analyzing past incidents and losses, financial statements, transactions, or questionnaires and assessments are not important or not useful, on the contrary, they are a very important source of data … nor because it is not important to apply the latest and most powerful quantification techniques and algorithms, of course, it is, … but because our analysis has been almost entirely Backward Looking, one-dimensional, and focused exclusively on the past.
The questions popped up in my head: How can we change this? … How can we make our quantification, modeling, and analysis more Forward-Looking?
My team and I were convinced that in order to make our analysis and modeling (of whatever type) more Forward Looking we had to: 1) break out of the one-dimensionality and cover more dimensions of our counterparts, 2) start to capture, measure and analyze the “Present” of our counterpart’s actions and interactions instead of only the “Past”, and 3) apply a holistic, 360° concept, which we called the “Understand Your Counterpart – UYC approach.
So, besides all the historical data available, we started to analyze how our counterparts behave in real-time, what the media writes about them, what their digital, cyber, social, business integrity and environmental fingerprints look like, how they talk to us, what kind of words and expressions they use, how their voices sound, how they behave in all digital channels we give them access to, how they use their devices during these interactions, what they read and what they focus on when they visit our platforms, what worries them, what they are interested in, what and how they write to us when they chat or email with us, how they are connected to their environment, what their spillover risk is, etc.
By proactively analyzing all this data of the “Present”, of the “Now”, in a Forward-Looking manner, we are not only dealing with much broader, more diverse and insightful data dimensions, but we have also managed to significantly reduce the number of False Positives (compared to the traditional one-dimensional analysis) and generate a variety of immediate and highly reliable Early Warning signals for a wide range of Compliance, Risk, and Performance Management topics and issues.
##### The Future: An Exciting Journey Ahead
Where are we heading? … Where are the boundaries?
Well, I don’t know exactly, but I am sure of one thing: since the world we live in and human behavior are so diverse, dynamic, and multifaceted, this must and will be an exciting journey!
At the end of his speech, our professor said: “Try to be smart economists and not pathologists!”
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://swissgrc.com/en/discoverycall/)
**Catégories:** Industry News
---
### [The GRC Evolution driven by its natively inherited privilege](https://swissgrc.com/fr/the-grc-evolution-driven-by-its-natively-inherited-privilege/)
**Published:** avril 3, 2024
**Author:** Nikolai Tsenov
**Excerpt:** When hearing the acronym GRC, practitioners familiar with the term, which stands for Governance Risk and Compliance, intuitively associate a heavy regulatory burden, formal and rather cumbersome compliance procedures and deadlines, painful internal and external audits, and huge costs.
**Content:**
**When hearing the acronym GRC, practitioners familiar with the term, which stands for Governance Risk and Compliance, intuitively associate a heavy regulatory burden, formal and rather cumbersome compliance procedures and deadlines, painful internal and external audits, and huge costs.**
Nevertheless, following the emergence and adoption of internationally recognized ERM standards such as COSO in the mid-1980s, and regulatory driven topics such as Operational Risk Management (BASEL II) in the early 2000s, over the years GRC has emerged as the most widely used, recognized, and globally adopted standard for corporate governance.
The GRC domain has gone through various stages of development and is constantly evolving. It has succeeded in improving its image in recent years and is just about to get out of the shadow of his unjustified bad reputation from the past mentioned above.
**In this management summary we will take a brief look on what has changed, what are the main driving forces in this “Next-Gen” GRC and will focus on the most appealing and promising GRC developments and trends going forward.**
##### The Unique Position of GRC
As its name suggests, GRC aims to consolidate, streamline, and visualize all topics relevant to the transparent, compliant, secure, resilient, and successful management of an organization. Compared to other stand-alone domains in this filed, such as the management of different types of risks, KYC, AML, Fraud Detection and Prevention, Business Continuity and Performance Management, etc., which are unfortunately often seen, treated, and practiced as isolated silos, GRC has this **“natively inherited privilege”** of serving as THE unifying information and management platform. Starting with users at the lowest levels of an organizational structure, up to the highest level, the management, and C-level users.
##### Core Characteristics of NextGen GRC
Consequently, this exceptional position and privileged status of a GRC platform within an organisation, compared to other decision support and executive information systems and platforms, implies, and evokes much higher expectations on the one hand and a considerable degree of credit, trust, and reliance on the other. Which without any doubts obliges to higher reliability, quality, and performance standards.
Based on this the first three main characteristics of a mature next-gen GRC platform, which emerge almost naturally as a matter of course are: **Adequacy**, **Relevancy** and **Actionability**.
So, let’s start with the first two. Adequacy and Relevancy are often and unjustly being used interchangeably, representing the main GRC characteristics since day one with their implicitness and self-explanatory nature.
**Adequacy** means that the generated GRC insights, followed by triggered actions and decisions, are based on the right and sufficient data and inputs. This is one of the basic characteristics of any decision support or executive management system, serving as reliable fundament, on which you can build up the rest.
**Relevancy**, on the other hand, means that the generated GRC insights are correctly distributed and reach the right audience and the right recipients at the right places. So, that managers and decision makers can take well-founded and informed decisions.
Mastering these two, is a prerequisite, it’s simply the baseline, a must.
**Actionability**, what does it mean? Traditionally executive information systems and dashboards were there just to visualize consolidated figures. They were primarily there to inform the right recipients on the right places of the organization, hopefully with the right and sufficient data. Gradually, distribution of tasks and actions, initiation of workflows and their monitoring – the Actionability of GRC insights, has become an indispensable requisite of any GRC platform. In the meantime, it Is not a secret that many GRC providers have originated from the BPM industry extending their business process management platforms into the GRC domain.
##### Timeliness and Forward-Looking: Key Differentiators
So far so good. As we continue exploring, we will notice that the following characteristics start playing a decisive role in the context of the perceived and effectively occurring GRC image “improvement”, the evolution and establishment of the Next-Gen GRC, accompanied by its even wider adoption.
Having described these first three characteristics of a GRC platform we have reached a point where with relatively high level of confidence we can say that 1) the vast majority of GRC platforms available today on the market, to a different extend of course, support these three MUST criteria, and 2) that unfortunately, for many of those providers the GRC innovation journey has got stuck here.
So now it starts getting interesting, because the following characteristics represent THE main differentiators in the GRC industry and perfectly foster, facilitate, highlight, and underscore this unique and natively inherited privilege of GRC and its importance to a maximum.
##### Innovation and Competitive Advantage through Timeliness
**Timeliness** addresses the aspect of WHEN, of the timing and how fast the GRC insights and the following actions reach their recipients and decisionmakers. Looking back in time the traditional and still widespread understanding of the GRC concepts has represented, and for many unfortunately it is still representing, a rather static universe. Data gathering, analysis of information, generation of insights and distribution of actions has followed a formal and rather “comfortable” time pattern. This fact is one of the main reasons accountable for the widely spread perception of GRC being “just” a collection of compulsory and cumbersome procedures to be followed on regular basis.
This GRC aspect undergoes significant changes as we speak and offers at the same time a tremendous potential for innovation, differentiation, and competitive advantages.
As we live in a very dynamic world with constantly changing behavioral patterns, where new risks and threats are emerging almost every single day, we cannot afford to act (or rather REact) following this “comfortable” time pattern of data gathering, data analysis and generation of valuable insights. To be fair we need to recognize that also in the past there were attempts of bringing more dynamic in this static world, by extending for example the usage of KRI’s and KPI’s. But unfortunately, this has been done not even nearly in the manner and pace, which would correspond to the pace and dynamics of the real world with its real and highly dynamic threats and risks.
##### The Future of GRC: Combining Timeliness with Forward-Looking Insights
Innovative GRC platform providers have recognized these deficits and shortcomings in the traditional concepts and are already now successfully implementing modern Next-Gen GRC approaches where Timeliness plays a key role and represents a major success factor for them and their customers.
There is, however, one more important factor to consider. Timeliness has its “twin sibling” without which the positive effects of Timeliness alone diminish significantly.
So, let’s talk about the next key characteristic of the Next-Gen GRC platforms. It relates to the **PERSPECTIVE** or the **DIRECTION** of the data gathering, data analysis, and generation of insights. Traditional GRC concepts are mainly focused on historical, Backward-Looking data, data analysis, quantification, and generation of insights.
Is Backward-Looking data and data analysis important? Of course, it is! … Is it sufficient in our modern and highly dynamic and complex world? Definitely not!
So, what we are looking for is also the so important Forward-Looking way of data gathering, data analysis and generation of insights.
**Forward-Looking** means constantly reflecting and analyzing the NOW and the PRESENT and being able to generate timely insights for the FUTURE based not only on historical, past, or simulated data, but on real data of the present, of the now. This gives the necessary perspective, directions, and hints of what is coming ahead, of the dynamics of our complex world, so that we can proactively act, decide, and adjust, long before risks and threats materialize.
The high pilotage and the master discipline of combining Timeliness with Forward-Looking mechanisms in the GRC space, along with the usage of all traditional and well established GRC methods and approaches, is the core success factor for every GRC practitioner dedicated and committed to excellence.
##### Join the Swiss GRC Community
If you are interested in understanding how exactly companies and GRC professionals striving for excellence are managing this transformation from a traditional to a NextGen GRC setup, what new methods, approaches and technologies they are using, how they are adapting existing processes and defining new ones, how their mindset is evolving during this exciting journey of innovation and discovery, then join our Swiss GRC community, follow and participate actively in our discussions, [webinars](https://swissgrc.com/en/webinars) and [events](http://swissgrc.com/swissgrcday). We would be glad to hear from you!
**Catégories:** Industry News
---
### [Ensuring Healthcare Resilience with Governance, Risk & Compliance (GRC)](https://swissgrc.com/fr/ensuring-healthcare-resilience-with-governance-risk-compliance-grc/)
**Published:** décembre 10, 2024
**Author:** Thomas Schneeberger
**Excerpt:** The importance of a holistic GRC strategy in the healthcare sector can hardly be overestimated. GRC creates the infrastructural basis that enables hospitals to work safely, efficiently and compliantly. It is a kind of “invisible infrastructure” that forms the foundation for modern, transparent and forward-looking healthcare.
**Content:**
**In the complex world of healthcare, hospitals are not only places of healing, but also organisations that must meet high regulatory requirements, strict data protection regulations and comprehensive risk management needs.**
The challenges of the healthcare system call for a structured governance, risk and compliance (GRC) strategy that not only meets today’s requirements, but is also future-proof. But what does this mean for hospitals? What specific pain points need to be addressed to ensure safe and transparent healthcare? The [Association of Zurich Hospitals (VZK)](https://www.vzk.ch/) and Swiss GRC recently announced their [collaboration](https://swissgrc.com/en/news/vzk-and-swiss-grc-join-forces-to-strengthen-grc-in-zurich-hospitals/) to strengthen GRC in Zurich hospitals. This article highlights the key issues hospitals face in implementing effective GRC strategies – and how a well-designed solution can help make operations not only secure and compliant, but also efficient and resilient.
The key challenges in healthcare – and how a good GRC strategy can help
Hospitals face a variety of challenges when it comes to implementing GRC strategies:
**1 – Mastering complex regulatory requirements**
The healthcare sector is characterized by strict and extensive regulations designed to ensure that patient safety and data integrity are maintained. These regulatory requirements are not static: they are constantly evolving, particularly in response to technical innovations and increasing data protection requirements. Hospitals must not only ensure that they comply with current requirements, but must also be flexible enough to adapt to new regulations.
A well-founded GRC strategy can provide support here by creating structures that enable dynamic adaptation. Digital tools that recognize regulatory changes and integrate them into existing processes can relieve the burden on day-to-day operations in hospitals and ensure that compliance is guaranteed at all times.
**2 – Managing sensitive patient data securely**
Protecting sensitive data is one of the key tasks in the healthcare sector. Patient data is subject to the highest security requirements, as breaches not only have legal consequences but also result in a loss of patient trust. Effective data protection management is therefore an indispensable part of any GRC strategy.
Modern data management ensures that personal information is protected at all times, both in everyday life and during storage and transmission. Automated security systems can also detect potential threats at an early stage and initiate appropriate countermeasures so that hospitals can respond quickly and effectively to incidents.
**3 – Recognize and manage risks at an early stage**
The healthcare sector is inherently risky. Whether it’s medical incidents, unforeseen crises or technological challenges, risks need to be identified early and managed strategically to ensure both patient safety and operational stability. As part of a comprehensive GRC strategy, [risk management](https://swissgrc.com/en/risk-management-software/) is therefore one of the most important functions.
A data-driven risk analysis offers hospitals the opportunity to categorize and prioritize risks in order to be able to react preventively. By implementing appropriate measures, risks can be minimized and costs can be saved that would otherwise have to be spent on ad hoc reactions. This proactive approach creates greater planning security and protects the integrity of hospital processes.
**4 – More efficient use of resources in a resource-intensive environment**
In the healthcare industry, resources are often scarce, while the need for high-quality care remains constantly high. Many hospitals are therefore faced with the challenge of using their resources as efficiently as possible in order to manage both administrative requirements and operational tasks.
A well-structured GRC framework can help to optimize processes in a hospital and reduce the administrative burden. With a systematic use of resources, hospitals can deploy staff and financial resources in a more targeted manner in order to provide more time and capacity for patient care. This is not just about increasing efficiency, but also about giving healthcare organizations more room for manoeuvre in a challenging environment.
**5 – Transparency as a foundation of trust**
Transparency in operational processes is a decisive factor for the trust that patients, employees and supervisory authorities place in a healthcare facility. Transparency means that processes are designed and documented in a comprehensible manner so that stakeholders always know what steps are being taken and why.
A GRC strategy that focuses on transparency provides hospitals with a tool to make their processes traceable. A centralized system for documentation and reporting makes it possible to design processes in a uniform manner and to be accountable to the various stakeholders. In this way, hospitals not only create a high level of security and trust, but also improve internal communication and accountability.
By implementing a well thought-out GRC strategy, healthcare facilities can not only strengthen their compliance, but also significantly improve the quality of patient care and ensure transparent, secure operations.
GRC as a central infrastructure for a resilient healthcare system
The importance of a holistic GRC strategy in the healthcare sector can hardly be overestimated. GRC creates the infrastructural basis that enables hospitals to work safely, efficiently and compliantly. It is a kind of “invisible infrastructure” that forms the foundation for modern, transparent and forward-looking healthcare. By automating and structuring many GRC processes, hospitals can not only reduce their administrative workload, but also react more quickly and flexibly to challenges.
Swiss GRC has many years of experience and specialized GRC solutions that are precisely tailored to the needs of hospitals and enable flexible, secure and efficient operational management. **If you would like to find out more, talk to our team of experts in a no-obligation [discovery call](https://swissgrc.com/en/discoverycall/).**
**Catégories:** Industry News
---
### [Register of information according to DORA: What is it and how to create it correctly?](https://swissgrc.com/fr/register-of-information-according-to-dora-what-is-it-and-how-to-create-it-correctly/)
**Published:** octobre 7, 2024
**Author:** Dr. Fino Scholl
**Excerpt:** DORA is currently the dominant topic in the industry - as demonstrated by the great response to the BaFin conference “IT supervision in the financial sector: What does DORA mean in practice?”. A key instrument in the practical implementation of DORA is the information register.
**Content:**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://swissgrc.com/en/discoverycall/)
**The countdown is on: The [Digital Operational Resilience Act (DORA)](https://swissgrc.com/digital-operational-resilience-act-dora/) comes into force on January 17, 2025, and the financial sector is preparing intensively for the new requirements. DORA is currently the dominant topic in the industry – as demonstrated by the great response to the BaFin conference “IT supervision in the financial sector: What does DORA mean in practice?” on September 26, 2024. Thousands of participants learned about the final steps towards implementation. A central instrument in the practical implementation of DORA is the register of information. In this article, you will learn what the register of information is all about, how to create it and why the right approach is crucial to meeting the requirements efficiently and on time.**
What is the DORA register of information?
The register of information under [DORA](https://swissgrc.com/en/dora) is a standardized central database that records all contractual agreements of a financial company with ICT third-party service providers. It contains detailed information about the ICT services utilized, the providers, and the supported business and operational functions. The register enables systematic monitoring of dependencies and risks arising from the use of ICT third-party providers and serves to provide this information to the relevant supervisory authorities. It encompasses all ICT services; however, particularly critical or important functions must be listed in more detail.
**Main Benefits:**
- **For financial companies**: The register of information helps companies systematically capture and monitor all contractual dependencies related to ICT services. This facilitates risk management, enhances transparency regarding critical ICT third-party providers, and enables better preparation for potential ICT-related incidents.
- **For the entire financial sector**: The register of information allows supervisory authorities to comprehensively monitor the dependencies of financial institutions on ICT third-party providers and identify critical service providers. This ensures that systemic risks are recognized early and coordinated measures are implemented to maintain digital resilience throughout the financial sector.
How do you create a DORA-compliant register of information?
The creation of a DORA-compliant register of information involves four main steps:
1. **Identification of critical and important functions**: First, determine which operational and business functions are essential for maintaining business operations and meeting regulatory requirements.
2. **Documentation of ICT third-party service providers**: Identify all providers delivering ICT services, and document the contractual details and dependencies.
3. **Documentation of ICT services**: Record all ICT services and associate them with the identified critical or important functions.
4. **Consolidation of information**: Enter the collected information into the standard templates specified by DORA to ensure uniform reporting.
Why Excel is not enough
Many companies initially rely on Excel to manage the register of information, as it appears to be a quick and cost-effective solution. However, practice shows that Excel quickly reaches its limits for the long-term management of such a complex and dynamic register:
- **Limited scalability:** as the complexity of the company grows, maintaining a register of information in Excel becomes confusing and difficult to manage (PwC, 2023).
- **Security risks:** DORA requires strict security measures to protect sensitive data. However, Excel only offers rudimentary security functions (EBA, 2023).
- **Lack of versioning and consistency:** In Excel, it is difficult to track changes and ensure consistency, especially if several people are working on it at the same time (BaFin, 2024b).
- **High manual effort and susceptibility to errors:** Merging and consolidating data from different sources is time-consuming and prone to human error.
The advantages of our tool-based solution
In order to meet the requirements of DORA and manage the information register efficiently, companies should rely on a tool-supported solution. This offers the following advantages:
- **Automation:** Reduce manual input and minimize errors through automated processes.
- **Central data management:** Instead of working in different Excel files, all parties involved can access the current information register via a central platform.
- **Increased security:** Tool-based solutions such as the GRC Toolbox offer advanced security features to ensure the protection of sensitive data in accordance with DORA (European Commission, 2023)
Conclusion
The information register is an essential component of the DORA requirements and will be the focal point for the digital resilience of financial service providers. In light of the upcoming enforcement of DORA and the increasing relevance of this topic, it is crucial for companies to take the right steps now. Those who invest early in a structured and efficient solution will be well-prepared not only to meet the new regulatory requirements but also to benefit in the long term from the insights gained.
**Would you like to learn more about how to efficiently and DORA-compliantly design your information register?** Feel free to contact us for more information about the solutions from Swiss GRC. You can also book a Discovery Call directly to find out how we can support your company: [swissgrc.com/discoverycall](https://www.swissgrc.com/discoverycall).
**Catégories:** Industry News
---
### [Top 2024 Trends in Governance, Risk & Compliance (GRC)](https://swissgrc.com/fr/top-2024-trends-in-governance-risk-compliance-grc/)
**Published:** mai 28, 2024
**Author:** Rajeev Dutt
**Excerpt:** Dive into this comprehensive analysis to discover how emerging technologies, integrated GRC frameworks, and a renewed focus on cybersecurity and operational resilience are defining the future of GRC. Equip your organization with the knowledge to not only face the challenges of today but to leverage them into tomorrow’s opportunities.
**Content:**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://swissgrc.com/en/discoverycall/)
**In an age defined by rapid technological change and complex regulatory environments, the importance of an effective Governance, Risk, and Compliance (GRC) framework cannot be overstated. The 2024 GRC Trends Report provides forward-thinking insights into the evolving landscape of risk and compliance, helping organizations adapt and thrive in these dynamic times.**
Today’s globalized business environment presents a complex web of interconnected challenges and opportunities. Organizations that fail to adapt to these rapid changes risk falling behind, suffering reputational damage, or facing stringent penalties from non-compliance. Whether you are a seasoned expert or new to the field of GRC, our 2024 GRC Trends Report is designed to help you stay ahead of the curve and make informed decisions for your organization. It provides valuable insights and strategies that empower organisations to pursue resilience, integrity, and sustainable growth in these challenging times. Dive into this comprehensive analysis to discover how emerging technologies, integrated GRC frameworks, and a renewed focus on cybersecurity and operational resilience are defining the future of GRC. Equip your organization with the knowledge to not only face the challenges of today but to leverage them into tomorrow’s opportunities.
##### Key Insights
- **Technological Integration:** With the advent of regulatory technologies and AI, organisations are poised to enhance their GRC processes significantly. Automation will play a central role in compliance and risk management, making operations more efficient and responsive.
- **Interconnected GRC Strategies:** The year 2024 sees a shift towards integrated GRC platforms. These systems facilitate better communication and data sharing across various organisational domains, essential for managing the increasingly interconnected risks.
- **Rising Cybersecurity Concerns:** As reliance on third-party vendors grows, so does the cybersecurity risk. Our report discusses strategies to mitigate these risks through advanced cyber risk management and continuous monitoring.
- **Supply Chain and Operational Resilience:** In light of recent global disruptions, strengthening supply chain and operational resilience has become paramount. We delve into methods for improving resilience through proactive risk management and crisis response strategies.
- **Focus on Sustainability:** The integration of Environmental, Social, and Governance (ESG) factors into GRC strategies reflects the growing demand for sustainability and transparency in business practices.
This report furnishes leaders and GRC professionals with in-depth insights and strategic guidance essential for developing proactive, robust GRC frameworks. These frameworks are designed not only to withstand today’s dynamic pressures but also to capitalize on them to propel organizational success. By grasping these pivotal trends, your organization can enhance decision-making, optimize risk management, and maintain compliance—capabilities increasingly vital in today’s environment. Grounded in practical experience and enriched by comprehensive discussions with clients, partners, and industry leaders, the report offers actionable, forward-thinking strategies that address real-world GRC challenges and opportunities.
###### **[Download the full report to learn more about harnessing these trends for your organisation’s advantage.](https://free.qrplanet.com/grctrends)**
**Catégories:** Industry News
---
### [ESG Risk Management: Trend or Necessity?](https://hub.hslu.ch/financialmanagement/2022/08/22/esg-risk-management-modeerscheinung-oder-notwendigkeit/#new_tab)
**Published:** novembre 15, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** Over 15 years ago, Kofi Annan, then Secretary-General of the UN, called on the board chairmen of 50 global corporations to commit to greater sustainability...
**Content:**
Over 15 years ago, Kofi Annan, then Secretary-General of the UN, called on the board chairmen of 50 global corporations to commit to greater sustainability…
**Catégories:** Digital, Software
---
### [Current initiatives on climate-related financial risks](https://www.finextra.com/blogposting/23350/current-initiatives-on-climate-related-financial-risks#new_tab)
**Published:** décembre 5, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** In the last week of November, the Swiss Financial Market Supervisory Authority FINMA published a supervisory notice on climate risk disclosure. According to this supervisory notice, the leading banks and insurance companies...
**Content:**
In the last week of November, the Swiss Financial Market Supervisory Authority FINMA published a supervisory notice on climate risk disclosure. According to this supervisory notice, the leading banks and insurance companies…
**Catégories:** Digital
---
## Pages
### [GRC intégrée. Une plateforme intelligente.](https://swissgrc.com/fr/)
**Published:** novembre 15, 2022
**Author:** superadmin
**Content:**
Pragmatique. Orienté métier.# GRC intégrée.
Une plateforme intelligente.
Swiss GRC réunit risques, conformité, sécurité et processus sur une plateforme native IA, alignée sur les réalités de votre entreprise. Cela transforme la GRC d'une obligation de conformité en un véritable outil de pilotage.
[Contactez-nous](#kontakt) Bilan de maturité GRC
GRC Toolboxdemo.grctoolbox.ch
**Grace AI**
Comprend votre contexte GRC en temps réel
×
Bonjour ! Choisissez une invite et j'analyserai vos **218 risques** en quelques secondes.
[Actualités](https://swissgrc.com/fr/news)Chargement des actualités...
[Toutes les actualités](https://swissgrc.com/fr/news)
Bilan de maturité GRC ×
## Quel est le niveau de maturité de votre GRC ?
Répondez à cinq questions courtes pour découvrir où en sont aujourd'hui votre gouvernance, vos risques et votre conformité, et quelle étape vous apportera le plus grand bénéfice.
Gouvernance Culture Processus Technologie Reporting
Démarrer le testMéthodologie basée sur le modèle de maturité OCEG pour une GRC intégrée. Les résultats sont donnés à titre indicatif et ne remplacent pas un conseil individuel.
·
← Retour
## Votre résultat est prêt.
Où pouvons-nous vous envoyer vos résultats personnalisés ?
Prénom
Nom
Email professionnel
Organisation
J'accepte le traitement de mes données conformément à la [politique de confidentialité](https://swissgrc.com/fr/privacy-policy/). Veuillez vérifier vos informations.
← Retour
Afficher le résultat Nous ne vous contacterons qu'avec des informations pertinentes pour vous. Pas de spam.
Niveau
Votre maturité GRC
### Votre prochaine étape
[En savoir plus →](#)
[Réserver un appel découverte](#) Contactez-nous
Méthodologie basée sur le modèle de maturité OCEG pour une GRC intégrée. Les résultats sont donnés à titre indicatif et ne remplacent pas un conseil individuel.
I agree to the privacy policy.
Adopté par des organisations leaders à travers le monde
[Voir tout ](https://swissgrc.com/fr/clients/)
Témoignages clients [Voir tout ](https://swissgrc.com/fr/customer-stories/)
Solutions## Vous décidez par où commencer.
Du risque à la protection des données en passant par l'audit : choisissez une solution et découvrez ce que la GRC lui apporte. La gestion des processus (BPM) et la gestion des contrats (CLM) complètent la plateforme.
Pourquoi Swiss GRC## Une base de données unique. Sans silos.
Configurable plutôt que programmable, disponible sur le web, triple certification ISO et élue « Produit GRC de l'année » par Risk.net : la GRC Toolbox réunit toutes les disciplines GRC sur une base de données commune.
01### Une plateforme unique plutôt que des silos
Toutes les disciplines GRC sur une base de données commune. Une vision cohérente plutôt que des outils dispersés.
02### Configuration plutôt que code
Des ajustements sans développement coûteux. La plateforme évolue avec vos besoins.
03### Reconnue et établie
Recommandée par les analystes, triple certification ISO, avec des serveurs situés régionalement.
04### Opérationnel rapidement
Déploiement rapide, exploitable dans le cloud ou sur site, utilisateurs illimités par module.
Swiss GRC en action## Découvrez ce qui est possible.
De l'analyse basée sur l'IA aux rapports de risques prêts pour la décision, en passant par la vue d'ensemble des tiers. Des vues réelles de la solution, choisies pour ce qui compte au quotidien.
Grace AI Reporting des risques Gestion des processus Renseignement sur les tiers Intégration et support
Grace AI
### Une IA qui comprend votre contexte GRC.
- Répond aux questions sur les risques, les contrôles et les processus en langage naturel.
- Fonctionne directement sur vos données, sans export ni changement d'outil.
- Résume les sujets complexes et propose les prochaines étapes.
[Découvrir la plateforme ](https://swissgrc.com/fr/platform)

Reporting des risques
### Une vue d'ensemble, prête pour la décision et en temps réel.
- Risques quantifiés par simulation de Monte-Carlo et distribution des pertes.
- Une vue agrégée destinée aux instances de décision, toujours à jour.
- Des recommandations d'action claires plutôt que de l'intuition.
[Découvrir RiskQuant ](https://swissgrc.com/fr/risk-quantification/)

Gestion des processus
### Les processus et leurs dépendances en un coup d'œil.
- Un inventaire central des processus, lié aux risques, contrôles et obligations.
- Processus critiques et leurs dépendances visibles instantanément.
- L'impact des changements directement traçable.
[Découvrir la gestion des processus ](https://swissgrc.com/fr/bpm-software/)

Renseignement sur les tiers
### Du criblage jusqu'à la proposition de décision.
- Évaluez fournisseurs et tiers de manière structurée et surveillez-les en continu.
- Répartition des risques, tendances et tiers critiques en un coup d'œil.
- Résultats préparés pour les instances de décision.
[Découvrir Third-Party Intelligence ](https://swissgrc.com/fr/third-party-intelligence/)

Intégration et support
### Une expertise qui porte ses fruits. Un succès qui dure.
- Des consultants expérimentés en gestion des risques, conformité et fonctions dirigeantes.
- Une expertise approfondie de la GRC Toolbox et des exigences réglementaires.
- Ancrés sur le marché suisse, actifs en Suisse, en Allemagne et en Europe.
[Demander un entretien ](#kontakt)

Chiffres clés## Une confiance qui se prouve.
Conçue en Suisse, triple certification ISO et reconnue à l'international : les organisations font confiance à la GRC Toolbox parce que la substance prime sur les promesses.
Témoignage clientEn travaillant main dans la main avec l'équipe Swiss GRC, nous avons construit un système qui non seulement répond à nos objectifs de gouvernance, mais qui permet aussi à chaque filiale de s'approprier et d'améliorer ses processus de gestion des risques et de HSE. Cette initiative est devenue l'un des piliers de la transformation numérique de NEQSOL Holding.
Samir Karimov
Responsable de la gestion des risques et du développement durable, NEQSOL Holding
[Lire le témoignage client ](https://swissgrc.com/en/success_story/harmonizing-governance-and-risk-across-neqsol-holding-with-swiss-grc/)
0
Projets clients réussis dans divers secteurs et domaines
0
Certifié ISO
0
Utilisateurs de la GRC Toolbox pour la gouvernance, le risque et la conformité
0
Clients de tous secteurs
Reconnu par Forrester GRC Platforms Landscape Q4 2025 SPARK Matrix Leader 2025 Risk.net Award
Paroles de clients## Ce que disent nos clients
Pourquoi les responsables risque, conformité et sécurité font confiance à la GRC Toolbox.
“
La collaboration avec Swiss GRC a été professionnelle et orientée solutions dès le départ. Nous avons particulièrement apprécié que nos besoins soient pris au sérieux et mis en œuvre efficacement.
Regula Schneider
Responsable du développement d'entreprise et membre de la direction générale, IB Langenthal AG
“
Swiss GRC est un véritable partenaire. Nous apprécions la simplicité, l'évolutivité et la flexibilité de la GRC Toolbox, ainsi que le support personnalisé et orienté client.
Kevin Helfer
Corporate Risk Manager, La Poste Suisse
“
Swiss GRC propose un logiciel GRC modulaire, facile à intégrer et à la tarification transparente. Nous nous réjouissons d'en élargir encore l'utilisation.
Dominik Mutter
Senior Information Security Officer, Groupe Baloise
“
Swiss GRC allie une expertise approfondie à des solutions fiables et flexibles. Leur équipe et leur logiciel ont dépassé nos attentes.
Martin Kanwar
Risk & Compliance Officer, Toa Re
“
Aux côtés de l'équipe Swiss GRC, nous avons construit un système qui permet à chaque filiale de façonner et de développer ses propres processus de gestion des risques et HSE en toute autonomie.
Samir Karimov
Responsable de la gestion des risques et du développement durable, NEQSOL Holding
“
Avec la GRC Toolbox, nous disposons d'un outil efficace et pratique qui est rentable pour nous et, surtout, pour nos contribuables.
Heinrich Furrer
Responsable des services, Canton d'Uri
“
La collaboration s'est déroulée d'égal à égal dès le départ, grâce à une compréhension mutuelle tant sur le plan professionnel que personnel.
Mirko Hegi
Expert GRC, PostFinance
“
La GRC Toolbox offre un large éventail de fonctionnalités spécifiquement adaptées aux besoins des organisations aux exigences complexes.
Tolga Ece
Responsable du centre de compétences en gestion des risques et des assurances, Ville de Zurich
“
Grâce à la GRC Toolbox, la Mobilière a pu rendre ses évaluations des risques et des contrôles plus efficaces et les adapter aux exigences actuelles.
Christian Grundt
Responsable du contrôle des risques et des affaires réglementaires, la Mobilière
Analyses## Restez à jour sur le marché de la GRC.
Analyses actuelles, notre événement phare et sessions en direct, à la source.
[ Blog### Analyses et savoir-faire pratique
Articles d'experts sur le risque, la conformité et la réglementation dans le monde entier.
Accéder au blog
](https://swissgrc.com/fr/blog/) [ Événement phare### SWISS GRC DAY
Notre conférence annuelle sur la gouvernance, le risque et la conformité.
Accéder à SWISS GRC DAY
](https://swissgrc.com/swissgrcday/) [ Webinaires### Webinaires et sessions en direct
Expertise et sessions produit en direct sur nos solutions.
Accéder aux webinaires
](https://swissgrc.com/fr/webinars/)
Contact et démo## Découvrez la plateforme SwissGRC®
en action
Gestion des risques, système de contrôle interne, sécurité de l'information, continuité d'activité, protection des données ou conformité : lors d'une démo personnalisée, nous vous présentons la plateforme et répondons à vos questions.
[Demander une démo](https://swissgrc.com/fr/demo)[Contacter les ventes](https://swissgrc.com/fr/sales)
Nous vous répondons généralement sous un jour ouvré.
---
### [Advisory Board](https://swissgrc.com/fr/advisory-board/)
**Published:** décembre 20, 2022
**Author:** superadmin
**Content:**
# Notre conseil d'administration et notre conseil consultatif
Notre conseil d'administration et notre conseil consultatif réunissent des personnalités issues de la recherche, de l'entrepreneuriat, du conseil et de nombreuses années de pratique à des postes de direction. Cette diversité de perspectives constitue notre caisse de résonance : elle comble nos lacunes, nous met au défi et affine nos décisions. Notre conseil consultatif combine en particulier une expertise éprouvée en gouvernance, risques et conformité, ce qui nous aide à repenser continuellement et à faire évoluer délibérément la trajectoire de notre entreprise.
Conseil d'administration

### Reto Zbinden
Président du conseil d'administration
Voir la biographie → [ ](https://www.linkedin.com/in/retozbinden/)
Avocat, Reto C. Zbinden est propriétaire de Swiss Infosec AG et cofondateur de Swiss GRC AG. Depuis 30 ans, il exerce comme consultant et formateur en parallèle de la direction de son entreprise. Dans les domaines de la sécurité intégrale, de la sécurité de l'information, de la protection des données et de la sécurité informatique, il est reconnu comme un spécialiste accompli et un fin connaisseur de « l'état de l'art » et des meilleures pratiques.
Ses domaines d'expertise sont la sécurité et l'organisation, la certification dans le domaine de la sécurité de l'information, ainsi que les aspects juridiques de la sécurité de l'information, tels que l'archivage, la protection des données et le droit des contrats dans le domaine de l'IT/sécurité de l'information. Son expertise des dernières évolutions en matière de sécurité et de protection des données, en Suisse comme à l'étranger, est appréciée au-delà des frontières du pays. Dans son travail, il privilégie toujours la conformité pratique et l'efficacité économique.

### Besfort Kuqi
CEO et membre du conseil d'administration
Voir la biographie → [ ](https://www.linkedin.com/in/besfort-kuqi-306346111/)
Besfort Kuqi est le fondateur et directeur général de Swiss GRC AG. Il travaille sur les thématiques de gouvernance, risques et conformité (GRC) depuis plus de 10 ans. Il se concentre sur la digitalisation, l'intégration et l'optimisation des systèmes de gestion et de contrôle au sein des entreprises et organisations. Il traite plus particulièrement des questions liées à la gestion des risques, aux systèmes de contrôle interne (SCI) et à la gestion de la conformité et de la sécurité.
Titulaire de la certification Project Management Professional (PMP), Besfort Kuqi accompagne des entreprises et organisations actives au niveau national et international dans l'élaboration, la mise en œuvre et la présentation d'analyses et de concepts propres à chaque entreprise, afin de résoudre les problématiques organisationnelles et techniques des processus GRC. Il a coconçu depuis ses débuts la GRC Toolbox de Swiss GRC, une solution logicielle pour la cartographie et la gestion systématiques des nombreuses disciplines de la GRC, l'a déployée avec succès dans de nombreuses entreprises et organisations, et a ainsi contribué à une meilleure efficacité, transparence et acceptation en matière de systèmes de gestion et de contrôle.
Conseil consultatif

### Prof. Dr. Stefan Hunziker
Conseil consultatif
Voir la biographie → [ ](https://www.linkedin.com/in/profdrstefanhunziker/)
Le Prof. Dr. Stefan Hunziker est professeur de gestion des risques d'entreprise et de systèmes de contrôle interne à la Haute école de gestion de Lucerne, à l'Institut des services financiers de Zoug (IFZ). Il est membre du comité de direction de l'institut et dirige le centre de compétences Risk & Compliance Management de l'IFZ. Depuis plus de 15 ans, il s'engage à faire progresser la gestion des risques dans la pratique, en tenant toujours compte des dernières avancées scientifiques.
Stefan Hunziker dirige les programmes de formation continue CAS Governance, Risk and Compliance (CAS GRC) ainsi que le cours spécialisé Corporate Risk Management à la Haute école spécialisée de Lucerne. En tant que responsable du MSc International Financial Management, il forme également des étudiants internationaux à la gestion des risques et au contrôle interne. Le Prof. Hunziker assure divers enseignements dans les domaines de la gestion des risques, des systèmes de contrôle interne et de la gestion financière.
Il accompagne et conseille des organisations dans la mise en place et le fonctionnement de la gestion des risques. Stefan Hunziker est l'auteur de nombreux ouvrages et articles, notamment sur la gestion globale des risques et les systèmes de contrôle interne. Il est fortement impliqué dans la recherche orientée vers la pratique et dirige d'importants projets financés par la Confédération (Innosuisse). Il intervient régulièrement lors de conférences nationales et internationales, ce qui le maintient en contact étroit avec la communauté internationale de la gestion des risques.

### Anuschka Küng
Conseil consultatif
Voir la biographie → [ ](https://www.linkedin.com/in/anuschka-k%C3%BCng-4a699319/)
Anuschka Küng est propriétaire et directrice générale d'Acons Governance & Audit AG depuis 2007. Elle conseille des entreprises de nombreux secteurs en matière de gouvernance d'entreprise, d'audit interne, de gestion des risques, de systèmes de contrôle interne (SCI), de conformité et de gestion des processus.
Dans le domaine de l'audit interne, elle intervient comme responsable de l'audit interne pour des mandats externalisés. Elle accompagne également des organisations dans le cadre d'évaluations qualité externes et propose des services de conseil et de coaching aux dirigeants et aux conseils d'administration. En gestion des risques, contrôle interne et gestion des processus, elle accompagne ses clients depuis la conception initiale jusqu'à la mise en œuvre opérationnelle, y compris en tant que Risk Manager ou spécialiste désignée du contrôle interne. Parmi ses autres domaines d'expertise figurent la mise en œuvre d'exigences de conformité spécifiques et l'accompagnement des organisations face aux constats réglementaires et aux mesures correctives.
Anuschka Küng siège au conseil d'administration d'une compagnie d'assurance-vie suisse. Elle enseigne également dans des hautes écoles spécialisées sur divers thèmes de gouvernance d'entreprise. Avant de rejoindre Acons, elle a travaillé plusieurs années comme Risk & Compliance Officer au sein d'une société de gestion d'actifs, avant de siéger huit ans à son conseil d'administration. Auparavant, elle dirigeait des mandats de conseil et d'audit ainsi que des missions d'audit interne au sein d'un cabinet Big Four.

### Dr. Patrick Wegmann
Conseil consultatif
Voir la biographie → [ ](https://www.linkedin.com/in/patrickwegmann/)
Le Dr Patrick Wegmann est président du conseil d'administration et COO de Lifetec AG, basée à Dietikon (ZH), un prestataire global spécialisé dans les premiers secours en entreprise et la gestion intégrale des risques. Il a étudié et obtenu son doctorat en théorie des marchés financiers à l'Université de Saint-Gall, et possède plus de 20 ans d'expérience en logiciels et conseil dans le domaine de la gestion des risques.
En 1999, le Dr Patrick Wegmann a cofondé Avanon AG, un éditeur de logiciels de référence pour la gestion des risques opérationnels. Après le rachat d'Avanon AG par Thomson Reuters, il a occupé le poste de Head of Product Business for Enterprise Risk chez Thomson Reuters jusqu'au début de 2019. Patrick Wegmann enseigne la gestion des risques à l'Université de Bâle, à la Haute école de gestion de Lucerne, à la Haute école spécialisée du nord-ouest de la Suisse, à la Kalaidos UAS et à l'Institut de planification financière.
![]()
[ Profil LinkedIn ](#)
---
### [À propos](https://swissgrc.com/fr/about-us/)
**Published:** décembre 15, 2022
**Author:** superadmin
**Content:**
À propos# Un logiciel pour la gouvernance, les risques et la conformité. Utilisé dans le monde entier.
**Swiss GRC** développe une plateforme intégrée pour la GRC, le BPM et le CLM. Plus de 250 organisations dans le monde l'utilisent, soutenues par nos propres entités sur le terrain et par plus de 120 spécialistes au sein du groupe.
Portée mondiale, excellence locale
[*01* Qui nous sommes](#beliefs) [*02* Histoire](#history) [*03* Reconnaissance](#recognition) [*04* Équipe et organes de direction](#team) [*05* Implantations](#locations) [*06* Travailler avec nous](#working)
**250+**Organisations utilisent notre plateforme
**500+**Projets réalisés
**120+**Spécialistes au sein du groupe
**6**Entités propres en Europe, MEA et APAC

*SWISS GRC DAY* Là où la gouvernance, les risques et la conformité se rencontrent pour réussir
Qui nous sommes## Trois phrases
qui nous engagent.
Notre but, notre vision et notre mission ne sont pas une affiche sur un mur. Ce sont eux qui décident quelles fonctionnalités nous développons, et lesquelles nous ne développons pas.
Notre but Notre vision Notre mission
Notre but
Permettre aux organisations de bâtir la confiance et la résilience pour un succès durable.
La confiance ne vient pas des documents. Elle vient de décisions qui restent traçables. C'est pourquoi nous regroupons risques, contrôles, mesures et contrats sur une base de données commune plutôt que de les gérer dans des outils séparés.
Une seule base de données pour toutes les disciplines GRC Chaque évaluation avec ses preuves et son historique Prêts à répondre aux superviseurs et aux auditeurs
Notre vision
Être le partenaire de référence, le plus fiable au monde, pour des solutions de gestion intégrées.
La fiabilité ne se proclame pas, elle se prouve au fil des années. Nos clients restent parce que nos versions sont prévisibles, parce que leurs interlocuteurs maîtrisent eux-mêmes le domaine, et parce que nous nous appliquons à nous-mêmes les normes que nous cartographions pour eux.
Certifiés ISO 27001, ISO 27017 et ISO 27701 Nos propres entités plutôt que de simples partenaires commerciaux Une feuille de route discutée ouvertement avec notre communauté
Notre mission
Fournir un logiciel excellent et innovant pour la GRC, le BPM et le CLM.
La gestion produit et l'ingénierie sont internalisées, pas confiées à des fournisseurs. L'intelligence artificielle fait partie de l'architecture et non un bouton ajouté en périphérie, du support intégré dans les modules jusqu'à un module dédié à la gouvernance de l'IA.
GRC, BPM et CLM sur une seule plateforme Ingénierie et gestion produit internalisées Une architecture nativement IA plutôt que des fonctionnalités ajoutées après coup
> “Chez Swiss GRC, notre équipe d'experts dédiée porte l'innovation technologique dans le domaine de la GRC. Ensemble, nous fixons de nouveaux standards pour la gouvernance, les risques et la conformité.”
**Besfort Kuqi***Fondateur et CEO, Swiss GRC AG*
*Portée mondiale, excellence locale*Plus notre présence est mondiale, plus les particularités et exigences locales comptent. C'est pourquoi nous travaillons avec nos propres entités en Europe, au Moyen-Orient et en Asie plutôt que via un réseau de partenaires commerciaux.
Notre histoire## L'idée est plus ancienne
que l'entreprise.
Une solution de gestion de la sécurité est devenue, au fil des années, une plateforme GRC complète. Chaque année est cliquable.
Origines 1989 à 2012 Structuration 2016 à 2020 Croissance 2022 à aujourd'hui
1989*Origines* 1993*Origines* 2005*Origines* 2012*Origines* 2016*Structuration* 2017*Structuration* 2019*Structuration* 2020*Structuration* 2022*Croissance* 2024*Croissance* 2025*Croissance* 2026*Croissance*
**1989***Origines*D'où vient l'idée
1. #### Fondation de Swiss Infosec AG
Reto Zbinden, avocat et aujourd'hui président de notre conseil d'administration, fonde Swiss Infosec AG. C'est de son activité de conseil qu'est née l'idée de la future toolbox.
**1993***Origines*Notre premier outil maison
1. #### Développement de l'outil SMSI
Un prototype de gestion de la sécurité de l'information est développé, faute de solution sur le marché répondant aux exigences. La première version est mise en service la même année.
**2005***Origines*D'un outil à un produit
1. #### ISMS Toolbox
L'outil est reconstruit sous forme d'application web. Pour la première fois, les organisations gèrent elles-mêmes leur sécurité, sans mandat de conseil en arrière-plan.
**2012***Origines*De la sécurité à la GRC
1. #### GRC Toolbox v1
Des modules tels que le SCI, l'ERM et la gestion des politiques viennent s'y ajouter. La solution de gestion de la sécurité devient une solution GRC complète.
**2016***Structuration*L'année de notre fondation
1. #### Fondation de Swiss GRC AG
Swiss GRC AG est fondée pour porter le développement du logiciel GRC de façon cohérente : notre propre équipe, notre propre feuille de route, notre propre responsabilité. La gestion des contrats s'ajoute comme nouveau module.
**2017***Structuration*Des clients à une communauté
1. #### Le premier SWISS GRC DAY
Le premier SWISS GRC DAY se tient sous la devise là où la gouvernance, les risques et la conformité se rencontrent pour réussir. L'événement devient le rendez-vous annuel de nos clients, partenaires et prospects.
**2019***Structuration*Former nos propres talents
1. #### Swiss GRC AG devient entreprise formatrice
Nous sommes agréés pour former des développeurs de logiciels et des spécialistes ICT dans le cadre du système suisse d'apprentissage. Depuis lors, nous formons nous-mêmes nos professionnels plutôt que de nous contenter de les recruter.
**2020***Structuration*Troisième génération
1. #### GRC Toolbox v3
La troisième génération de la plateforme est lancée. Des rapports standards prédéfinis et des tableaux de bord raccourcissent le chemin entre la saisie des données et l'analyse.
**2022***Croissance*Faire la preuve de nos propres standards
1. #### Triple certification ISO
Certification ISO 27001 pour le SMSI, ISO 27017 pour le cloud et ISO 27701 pour la protection des données. Nous nous appliquons à nous-mêmes les standards que nous cartographions pour nos clients.
**2024***Croissance*Trois jalons
1. #### Swiss GRC Germany GmbH
Une entité propre pour le marché allemand, avec notre propre équipe plutôt que des partenaires commerciaux.
2. #### Strong Contender dans le SPARK Matrix
Quadrant Knowledge Solutions positionne Swiss GRC dans la catégorie des plateformes GRC.
3. #### Label Top Company
Ce label kununu repose sur les évaluations de nos propres collaborateurs.
**2025***Croissance*Reconnaissance internationale
1. #### GRC Product of the Year
Aux Risk Technology Awards 2025 de Risk.net, Swiss GRC est nommé GRC Product of the Year, face aux acteurs mondiaux établis.
2. #### Leader dans le SPARK Matrix 2025
QKS Group positionne Swiss GRC comme Leader, pour les plateformes GRC et pour la gestion des risques informatiques.
**2026***Croissance*Où nous en sommes aujourd'hui
1. #### Une plateforme nativement IA
L'intelligence artificielle devient partie intégrante de l'architecture plutôt qu'un ajout en périphérie : du support intégré dans les modules jusqu'à un module dédié à la gouvernance de l'IA et à la gestion des risques liés à l'IA.
Reconnaissance## Comment analystes et
médias spécialisés nous évaluent.
Des analystes indépendants, des médias spécialisés et nos clients évaluent régulièrement notre plateforme. Voici une sélection de leurs conclusions.

Product of the Year 2025### Meilleur produit GRC de l'année
Aux Risk Technology Awards 2025 de Risk.net, l'une des publications les plus respectées au monde en matière de gestion des risques, de conformité et de technologie financière, Swiss GRC a été nommé GRC Product of the Year.
Avant nous, ce titre avait été décerné à des noms tels que **MetricStream**, **SAI360** et **IBM OpenPages**.

Leadership Status#### Leader dans le SPARK Matrix 2025
Positionné comme Leader par QKS Group, à la fois pour les plateformes GRC et pour la gestion des risques informatiques.

Representative Vendor#### Dans le GRC Landscape Report
Forrester recense Swiss GRC à plusieurs reprises dans son GRC Landscape Report, à ce jour comme seule entreprise de la région DACH.

Market Leader#### Aux côtés des leaders mondiaux du marché
BARC présente Swiss GRC aux côtés des leaders mondiaux de la gouvernance, des risques et de la conformité.

Best of Technology 2025#### Noté « Excellent »
WirtschaftsWoche a noté notre solution de gestion des risques tiers « Excellent » en 2025.

Representative Vendor#### Dans le RMIS Panorama
L'association française de gestion des risques AMRAE recense Swiss GRC dans son RMIS Panorama en continu depuis 2024.

Clients’ Favorite#### Très bien noté par les clients
Sur les plateformes Gartner Digital Markets, nos solutions reçoivent d'excellentes évaluations clients dans le monde entier.
Notre équipe## Des personnes qui ne se contentent pas de vendre la GRC, mais qui la comprennent.
Beaucoup d'entre nous viennent du conseil, de l'audit ou de la surveillance, et connaissent les questions de nos clients par notre propre pratique.
Choisissez un groupe
Direction générale Responsables d'équipe Entités et régionsEntités Conseil d'administration Conseil consultatif
Direction générale

Besfort Kuqi
Fondateur et CEO

Daniel Arnold
Chief Product Officer (CPO)

Fari Ganji
Chief Information Officer (CIO)

Gentian Ajeti
Chief Customer & Commercial Officer (CCO)

Yahya Mohamed Mao
Chief Marketing Officer (CMO)
Responsables d'équipe

Natalie Metry
Responsable Administration, RH et Finance

Nikolai Tsenov
Responsable Solutions et Innovation

Johannes Weiser
Responsable Customer Success et Support

Matthias Graf
Responsable Ingénierie logicielle

Michael Niedermann
Responsable Conseil

Shankar Omandhu
Responsable Conseil MEA et APAC

Bujar Surdulli
Responsable Transformation IA
Entités et régions

Dr. Fino Scholl
Directeur général, Swiss GRC Germany GmbH

Rajeev Dutt
Directeur général, Swiss GRC Dubai, MEA et APAC

Gentian Ajeti
Directeur général, Swiss GRC Kosovo L.L.C.
Conseil d'administration

Reto Zbinden
Président du conseil d'administration

Besfort Kuqi
Membre du conseil, Fondateur et CEO
Conseil consultatif

Prof. Dr. Stefan Hunziker
Conseil consultatif

Anuschka Küng
Conseil consultatif

Dr. Patrick Wegmann
Conseil consultatif
Implantations## Des équipes locales, partout dans le monde.
Six entités propres en Europe, au Moyen-Orient et en Asie. Cliquez sur une implantation et le globe s'y tourne.
**Lucerne *Siège****Swiss GRC AG*Suisse
**Munich***Swiss GRC Germany GmbH*Allemagne
**London***Swiss GRC UK*Royaume-Uni
**Pristina***Swiss GRC L.L.C.*Kosovo
**Dubai***Swiss GRC MEA/APAC*Émirats arabes unis
**Mumbai***Swiss GRC India*Inde
Travailler chez Swiss GRC## Des circuits courts,
de vraies responsabilités.
Nos clients sont des banques, des assureurs, des autorités publiques et des entreprises industrielles. Cela exige de la précision et rend votre propre travail visible.
*Ingénierie*Lucerne, à cinq minutes à pied de la gare
*Horaires de travail*Semaine de 40 heures, horaires flexibles, télétravail possible
*Formation*Entreprise formatrice agréée depuis 2019 pour les développeurs de logiciels et les spécialistes ICT
- **01**#### Décider plutôt qu'escalader
Des hiérarchies plates, des circuits courts. Les décisions se prennent là où se trouve l'expertise, pas quatre niveaux au-dessus.
- **02**#### Des responsabilités dès le premier projet
Quiconque nous rejoint travaille immédiatement sur des solutions clients et prend en charge un domaine qui évolue avec sa propre expérience.
- **03**#### Un domaine exigeant
Réglementation, risques et processus dans un seul produit. Si vous aimez faire des liens, vous trouverez ici un travail qui ne s'épuise pas après deux ans.
- **04**#### Formation en interne
Nous formons nos propres professionnels depuis 2019 et misons sur le développement plutôt que sur le turnover. Poser des questions est considéré ici comme une force.
- **05**#### Des salaires alignés sur le marché
Justifiés de façon transparente. Des objectifs partagés ne fonctionnent que sur des bases équitables.
- **06**#### Un cadre international
Des projets et des collègues en Europe, au Moyen-Orient et en Asie, avec nos propres entités sur le terrain.
Carrières chez Swiss GRC## Postes ouverts et
candidatures spontanées
Nous recherchons en continu des spécialistes en ingénierie, conseil, produit et Customer Success. Si aucun poste ne correspond, une candidature spontanée est expressément la bienvenue.
[Voir les postes ouverts](https://swissgrc.com/fr/jobs/) [Postuler spontanément](mailto:hr@swissgrc.com)
---
### [Demande de démo pour la SwissGRC® Platform](https://swissgrc.com/fr/demo/)
**Published:** juin 30, 2026
**Author:** superadmin
**Content:**
# En savoir plus sur Swiss GRC.
Vous voulez voir comment Swiss GRC peut vous accompagner ? Demandez une démo et découvrez la SwissGRC® Platform, nativement IA. Gérez les risques avec précision, mettez la conformité en pratique et réunissez vos processus en un seul endroit.
[ sales@swissgrc.com](mailto:sales@swissgrc.com) [ +41 41 220 75 00](tel:+41412207500)
Vous préférez choisir un créneau tout de suite ? [ Réserver un rendez-vous](https://swissgrc.com/fr/discoverycall)
## Demander une démo
Les champs marqués d'un \* sont obligatoires. Nous traitons vos informations de manière confidentielle.
Prénom \*
Nom \*
E-mail professionnel \*
Société \*
Fonction \*Veuillez sélectionnerGestion des risques / ERMConformité / GouvernanceAudit interneIT / Sécurité de l'informationProtection des donnéesGestion des processus / BPMGestion des contrats / CLMDirection générale / Conseil d'administrationAutre
Pays \*Veuillez sélectionnerSuisseAllemagneAutricheAfghanistanAlbanieAlgérieAndorreAngolaAntigua-et-BarbudaArgentineArménieAustralieAzerbaïdjanBahamasBahreïnBangladeshBarbadeBiélorussieBelgiqueBelizeBéninBhoutanBolivieBosnie-HerzégovineBotswanaBrésilBruneiBulgarieBurkina FasoBurundiCap-VertCambodgeCamerounCanadaRépublique centrafricaineTchadChiliChineColombieComoresCongo (République démocratique)Congo (République)Costa RicaCôte d'IvoireCroatieCubaChypreTchéquieDanemarkDjiboutiDominiqueRépublique dominicaineÉquateurÉgypteSalvadorGuinée équatorialeÉrythréeEstonieEswatiniÉthiopieFidjiFinlandeFranceGabonGambieGéorgieGhanaGrèceGrenadeGuatemalaGuinéeGuinée-BissauGuyanaHaïtiHondurasHongrieIslandeIndeIndonésieIranIrakIrlandeIsraëlItalieJamaïqueJaponJordanieKazakhstanKenyaKiribatiKosovoKoweïtKirghizistanLaosLettonieLibanLesothoLiberiaLibyeLiechtensteinLituanieLuxembourgMadagascarMalawiMalaisieMaldivesMaliMalteÎles MarshallMauritanieMauriceMexiqueMicronésieMoldavieMonacoMongolieMonténégroMarocMozambiqueMyanmarNamibieNauruNépalPays-BasNouvelle-ZélandeNicaraguaNigerNigeriaCorée du NordMacédoine du NordNorvègeOmanPakistanPalaosPanamaPapouasie-Nouvelle-GuinéeParaguayPérouPhilippinesPolognePortugalQatarRoumanieRussieRwandaSaint-Kitts-et-NevisSainte-LucieSaint-Vincent-et-les-GrenadinesSamoaSaint-MarinSao Tomé-et-PrincipeArabie saouditeSénégalSerbieSeychellesSierra LeoneSingapourSlovaquieSlovénieÎles SalomonSomalieAfrique du SudCorée du SudSoudan du SudEspagneSri LankaSoudanSurinameSuèdeSyrieTadjikistanTanzanieThaïlandeTimor orientalTogoTongaTrinité-et-TobagoTunisieTurquieTurkménistanTuvaluOugandaUkraineÉmirats arabes unisRoyaume-UniÉtats-UnisUruguayOuzbékistanVanuatuCité du VaticanVenezuelaVietnamYémenZambieZimbabwe
Votre message
J'accepte la [politique de confidentialité](https://swissgrc.com/fr/privacy-policy/).
## La confiance de grandes organisations dans le monde entier.
Autorités publiques, banques, assureurs et industriels pilotent leur gouvernance, leurs risques et leur conformité sur
Swiss GRC.
0
Clients dans tous les secteurs
0
Projets clients menés à bien, tous secteurs et thématiques confondus
0
Utilisateurs de GRC Toolbox en gouvernance, risques et conformité
---
### [SwissGRC® Platform Sales Team](https://swissgrc.com/fr/sales/)
**Published:** juin 30, 2026
**Author:** superadmin
**Content:**
# Découvrez la SwissGRC® Platform.
Vous vous renseignez, comparez ou souhaitez simplement en savoir plus ? Dites-nous ce que vous recherchez. Vous recevrez les bonnes informations, une fourchette de prix et les bons contacts pour la SwissGRC® Platform, nativement IA.
[ sales@swissgrc.com](mailto:sales@swissgrc.com) [ +41 41 220 75 00](tel:+41412207500)
Vous préférez en parler directement ? [ Réserver un rendez-vous](https://swissgrc.com/fr/discoverycall)
## Contact commercial
Les champs marqués d'un \* sont obligatoires. Nous traitons vos informations de manière confidentielle.
Prénom \*
Nom \*
E-mail professionnel \*
Société \*
Fonction \*Veuillez sélectionnerGestion des risques / ERMConformité / GouvernanceAudit interneIT / Sécurité de l'informationProtection des donnéesGestion des processus / BPMGestion des contrats / CLMDirection générale / Conseil d'administrationAutre
Pays \*Veuillez sélectionnerSuisseAllemagneAutricheAfghanistanAlbanieAlgérieAndorreAngolaAntigua-et-BarbudaArgentineArménieAustralieAzerbaïdjanBahamasBahreïnBangladeshBarbadeBiélorussieBelgiqueBelizeBéninBhoutanBolivieBosnie-HerzégovineBotswanaBrésilBruneiBulgarieBurkina FasoBurundiCap-VertCambodgeCamerounCanadaRépublique centrafricaineTchadChiliChineColombieComoresCongo (République démocratique)Congo (République)Costa RicaCôte d'IvoireCroatieCubaChypreTchéquieDanemarkDjiboutiDominiqueRépublique dominicaineÉquateurÉgypteSalvadorGuinée équatorialeÉrythréeEstonieEswatiniÉthiopieFidjiFinlandeFranceGabonGambieGéorgieGhanaGrèceGrenadeGuatemalaGuinéeGuinée-BissauGuyanaHaïtiHondurasHongrieIslandeIndeIndonésieIranIrakIrlandeIsraëlItalieJamaïqueJaponJordanieKazakhstanKenyaKiribatiKosovoKoweïtKirghizistanLaosLettonieLibanLesothoLiberiaLibyeLiechtensteinLituanieLuxembourgMadagascarMalawiMalaisieMaldivesMaliMalteÎles MarshallMauritanieMauriceMexiqueMicronésieMoldavieMonacoMongolieMonténégroMarocMozambiqueMyanmarNamibieNauruNépalPays-BasNouvelle-ZélandeNicaraguaNigerNigeriaCorée du NordMacédoine du NordNorvègeOmanPakistanPalaosPanamaPapouasie-Nouvelle-GuinéeParaguayPérouPhilippinesPolognePortugalQatarRoumanieRussieRwandaSaint-Kitts-et-NevisSainte-LucieSaint-Vincent-et-les-GrenadinesSamoaSaint-MarinSao Tomé-et-PrincipeArabie saouditeSénégalSerbieSeychellesSierra LeoneSingapourSlovaquieSlovénieÎles SalomonSomalieAfrique du SudCorée du SudSoudan du SudEspagneSri LankaSoudanSurinameSuèdeSyrieTadjikistanTanzanieThaïlandeTimor orientalTogoTongaTrinité-et-TobagoTunisieTurquieTurkménistanTuvaluOugandaUkraineÉmirats arabes unisRoyaume-UniÉtats-UnisUruguayOuzbékistanVanuatuCité du VaticanVenezuelaVietnamYémenZambieZimbabwe
Votre demande \*Veuillez sélectionnerInformations généralesTarifs / DevisDémo à une date ultérieurePartenariatAutre
Votre message
J'accepte la [politique de confidentialité](https://swissgrc.com/fr/privacy-policy/).
## La confiance de grandes organisations dans le monde entier.
Autorités publiques, banques, assureurs et industriels pilotent leur gouvernance, leurs risques et leur conformité sur
Swiss GRC.
0
Clients dans tous les secteurs
0
Projets clients menés à bien, tous secteurs et thématiques confondus
0
Utilisateurs de GRC Toolbox en gouvernance, risques et conformité
---
### [Standards & Frameworks on the SwissGRC® Platform](https://swissgrc.com/fr/standards-frameworks/)
**Published:** juillet 14, 2026
**Author:** superadmin
**Content:**
Normes & référentiels# Votre paysage réglementaire, couvert dans le monde entier
Du droit suisse et européen aux États-Unis et à la région du Golfe, jusqu'à l'Inde : la SwissGRC® Platform cartographie les réglementations qui vous concernent, avec une offre complète dédiée à la gouvernance de l'IA.
Voici une sélection des normes et référentiels que nous couvrons.
Catégories
## Voyez-le en action sur la SwissGRC® Platform
Lors d'une démo personnalisée, découvrez comment la SwissGRC® Platform cartographie concrètement vos exigences réglementaires, de l'évaluation aux preuves prêtes pour l'audit. Demandez votre démo ou échangez directement avec notre équipe commerciale.
Demander une démo Parler aux ventes
Demander une démo Contacter les ventes
---
### [Directive sur la sécurité des réseaux et de l'information (NIS2)](https://swissgrc.com/fr/network-information-security-directive-nis2/)
**Published:** juin 18, 2024
**Author:** superadmin
**Content:**
Directive (UE) 2022/2555 · NIS2# Une conformité NIS2 que vous pouvez prouver.
De l'analyse de périmètre aux dix mesures minimales, jusqu'au signalement à votre autorité de surveillance : la SwissGRC® Platform rend votre mise en œuvre du NIS2 structurée, traçable et prête pour l'audit.
[Vérifiez si vous êtes concerné](#sgnis2-betroffenheit) [Demander une démo](#sgnis2-cta)
Vérification du périmètre## Le NIS2 s'applique-t-il à votre organisation ?
Trois informations suffisent pour une première évaluation structurée : localisation, secteur et taille de l'entreprise. Directement ici, sans formulaire.
1 · Localisation
2 · Secteur
3 · Taille
Résultat
Où votre organisation opère-t-elle principalement ?
Ce qui compte, c'est l'endroit où vous fournissez vos services ou où vous êtes établi.
AllemagneNIS2UmsuCG, en vigueur depuis le 6 déc. 2025 AutricheNISG 2026, s'applique à partir du 1er oct. 2026 SuisseHors UE, mais indirectement concernée Autre pays de l'UELa transposition nationale s'applique
Dans quel secteur opérez-vous ?
Le NIS2 distingue les secteurs hautement critiques (annexe I) et les autres secteurs critiques (annexe II).
Annexe I · **Hautement critique**
Énergie Transport Banque et marchés financiers Santé Eau potable et eaux usées Infrastructure numérique Services TIC (B2B) Administration publique Espace
Annexe II · **Autres secteurs critiques**
Services postaux et d'expédition Gestion des déchets Chimie Alimentation Industrie manufacturière Fournisseurs numériques Recherche
Ou
Aucun de ces secteurspar ex. commerce de détail, conseil, tourisme
Quelle est la taille de votre organisation ?
Selon la définition PME de l'UE : effectif, chiffre d'affaires ou total de bilan.
PetiteMoins de 50 employés et chiffre d'affaires max. de 10 millions d'euros MoyenneDe 50 à 249 employés ou chiffre d'affaires de 10 à 50 millions d'euros Grande250 employés ou plus, ou chiffre d'affaires supérieur à 50 millions d'euros
Retour Suivant
Cette première évaluation se base sur les critères principaux de la directive (UE) 2022/2555 et de ses transpositions nationales. Les cas particuliers, comme les entités couvertes indépendamment de leur taille (par ex. services de confiance, DNS, TLD, réseaux de communication publics) et la législation sectorielle spécifique (par ex. le DORA dans le secteur financier), nécessitent un examen séparé. Elle ne remplace pas un conseil juridique.
Échéances et feuille de route## Le NIS2 dans la région DACH : le compte à rebours est lancé.
Trois pays, trois rythmes. Choisissez votre pays et découvrez quelles échéances sont déjà en cours et ce qui arrive ensuite.
Compte à rebours : NISG 2026 en Autriche
0Jours
0Heures
0Min
0Sec
🇩🇪 Allemagne 🇦🇹 Autriche 🇨🇭 Suisse 🇪🇺 UE
06.12.2025
La loi de transposition du NIS2 entre en vigueur
Le NIS2UmsuCG s'applique sans période de transition. Les exigences sont ancrées dans la loi BSI révisée. Environ 29 500 entreprises sont concernées.
En vigueur
06.03.2026
Enregistrement obligatoire auprès du BSI
Le délai légal d'enregistrement auprès du BSI (portail actif depuis le 6 janv. 2026) est dépassé. Le BSI accorde aux retardataires une période de tolérance jusqu'au 31 juillet 2026, mais un enregistrement tardif reste passible d'amendes.
Période de tolérance jusqu'au 31 juil. 2026
En continu
Gestion des risques, obligations de signalement, preuves
Les mesures au titre de l'art. 21 et l'obligation de signalement en trois étapes (24h, 72h, 1 mois) s'appliquent. L'autorité de surveillance peut exiger des preuves, et la direction est responsable de la mise en œuvre.
Actif
Décembre 2028
Échéance de preuve pour les entités particulièrement importantes
Les entités particulièrement importantes doivent démontrer au BSI la mise en œuvre des mesures de gestion des risques dans les trois ans suivant l'entrée en vigueur de la loi.
À préparer
23.12.2025
Promulgation de la NISG 2026
L'Autriche adopte sa transposition du NIS2. Une nouvelle autorité centrale est créée, l'Office fédéral de la cybersécurité. Environ 4 000 entreprises sont directement concernées.
Adoptée
01.10.2026
Entrée en vigueur : toutes les obligations s'appliquent
Les mesures de gestion des risques, les obligations de signalement et l'obligation de formation des organes de direction deviennent contraignantes. L'ancienne NISG 2018 est abrogée.
Date clé
31.12.2026
Délai d'enregistrement
Les entités essentielles et importantes doivent être enregistrées auprès de l'Office fédéral de la cybersécurité. La classification se fait par auto-évaluation, et il n'existe pas de privilège de groupe.
30.09.2027
Auto-déclaration
Dans les douze mois suivant la naissance de l'obligation d'enregistrement, une auto-déclaration structurée doit être soumise : mesures mises en œuvre, résultats de l'analyse de risque, sécurité de la chaîne d'approvisionnement.
01.10.2028
Audits réglementaires possibles
À partir de deux ans après l'entrée en vigueur, l'autorité de cybersécurité peut exiger des preuves et ordonner des audits par des organismes indépendants, pour les entités importantes sur une base réactive, déclenchée par des événements.
À préparer
01.04.2025
Obligation de signalement au titre de la LSI
Les cyberattaques contre les infrastructures critiques doivent être signalées à l'Office fédéral de la cybersécurité (OFCS) dans un délai de 24 heures. La Suisse suit sa propre voie, dans un esprit proche du NIS2.
En vigueur
En continu
Le NIS2 se transmet via la chaîne d'approvisionnement
Les entreprises suisses ayant des clients ou des établissements dans l'UE reçoivent les exigences du NIS2 de façon indirecte : via des questionnaires de sécurité, des clauses contractuelles et des obligations de preuve émanant de leurs partenaires commerciaux concernés.
Pertinent pour les exportateurs et fournisseurs
16.01.2023
La directive (UE) 2022/2555 entre en vigueur
Le NIS2 remplace la directive NIS de 2016, étend le périmètre à 18 secteurs et renforce la surveillance et les sanctions.
18.10.2024
Début de l'application
Les États membres devaient transposer la directive en droit national avant le 17 oct. 2024. Beaucoup s'y sont pris tardivement, et la mise en œuvre progresse depuis, pays par pays.
En continu
Transpositions nationales et actes d'exécution
Pour certains services numériques, le règlement d'exécution de la Commission précise en détail les exigences de sécurité. Au niveau national, les délais, les autorités et la terminologie diffèrent, ce qui est particulièrement exigeant pour les groupes présents dans plusieurs pays de l'UE.
Situation en juillet 2026. Les échéances et la pratique réglementaire évoluent en continu ; les textes juridiques respectifs et les communications officielles font foi.
Art. 21(2) · Les mesures obligatoires## Dix mesures, un seul système.
Le NIS2 exige de chaque entité concernée la mise en œuvre de dix mesures minimales, de l'analyse de risque à l'authentification multifacteur. Parcourez-les : ce que la directive exige et comment vous le mettez en œuvre sur la SwissGRC® Platform.
Art. 23 · Obligation de signalement pour les incidents importantsTrois délais à respecter le moment venu.
24hAlerte précoce
Sans délai injustifié après en avoir eu connaissance : notification initiale à l'autorité compétente ou au CSIRT, y compris tout soupçon d'acte illicite ou d'impact transfrontalier.
72hNotification
Évaluation structurée de l'incident : gravité, impact et, si disponibles, indicateurs de compromission.
1 moisRapport final
Description détaillée de l'incident, de ses causes et des mesures correctives prises. Rapports intermédiaires sur demande.
FAQ## Foire aux questions
Les questions que les entreprises nous posent le plus souvent lors de la mise en place de leur solution NIS2. Des réponses directes, sans détour.
Qui est concerné par NIS2 ?En principe, les moyennes et grandes entreprises (50 employés ou plus, ou plus de 10 millions d'euros de chiffre d'affaires) des **18 secteurs des annexes I et II**, de l'énergie et de la santé à l'industrie manufacturière. Certains services tels que le DNS, les TLD ou les services de confiance sont couverts quelle que soit leur taille, et les obligations relatives à la chaîne d'approvisionnement étendent aussi les exigences aux fournisseurs qui ne sont pas directement réglementés. Le moyen le plus rapide de vous situer est la [vérification du périmètre](#sgnis2-betroffenheit) en haut de cette page.
Quelles sont les obligations de signalement en cas d'incident de sécurité ?Les incidents importants doivent être signalés en trois étapes (art. 23) : une **alerte précoce dans les 24 heures**, une notification détaillée dans les 72 heures et un rapport final au plus tard un mois après l'alerte précoce. Sur la SwissGRC® Platform, vous définissez le processus de signalement sous forme de workflow avec délais, responsables et modèles, afin que le moment venu, personne n'ait à se demander qui signale quoi et à quelle échéance.
À quelle vitesse pouvons-nous démarrer ?Plus vite que ce que la plupart imaginent. La SwissGRC® Platform est livrée avec un **contenu NIS2 pré-structuré**, vous ne partez donc pas de zéro. Les premiers résultats, comme l'évaluation de référence et un plan d'action priorisé, sont visibles en quelques jours, et un déploiement type prend quelques semaines selon le périmètre et les modules. Notre onboarding vous guide étape par étape.
Comment fonctionnent les preuves et la piste d'audit ?Les preuves sont rattachées **directement à l'exigence ou à la mesure** : documents, comptes-rendus, captures d'écran, références. Chaque version est conservée, et chaque modification est journalisée avec l'utilisateur et l'horodatage. Le résultat est une piste complète, à l'épreuve de l'audit. Lorsque l'autorité de surveillance ou un auditeur demande des preuves, vous exportez l'état actuel en un clic au lieu de fouiller dans des dossiers et des boîtes mail.
Quel en est le coût ?La licence est **modulaire et transparente** : vous payez pour les modules que vous utilisez, à l'échelle de la taille de votre organisation. Il n'y a pas de coûts cachés ni d'obligation d'acheter la suite complète. Comme la configuration adaptée dépend du point de départ, nous préparons un devis concret après un court entretien. [Contacter les ventes](/fr/sales/)
Pour la directive elle-même, y compris les secteurs, les sanctions et les délais, consultez la [vérification du périmètre](#sgnis2-betroffenheit) et la [feuille de route](#sgnis2-fristen) ci-dessus.
## N'implémentez pas seulement NIS2.
Prouvez-le.
Découvrez comment des organisations à travers l'Europe structurent, mettent en œuvre et documentent leurs obligations NIS2 avec la SwissGRC® Platform, prêtes pour les autorités et les auditeurs.
[Demander une démo](/fr/demo/) [Contacter les ventes](/fr/sales/)
---
### [Digital Operational Resilience Act (DORA)](https://swissgrc.com/fr/digital-operational-resilience-act-dora/)
**Published:** juin 14, 2024
**Author:** superadmin
**Content:**
Conformité DORA
# Le DORA fait désormais partie de votre quotidien. *Nous l'allégeons.*
Tenir à jour le registre d'informations, signaler les incidents dans les délais, garder une vue sur les tiers : vous savez exactement ce qu'il faut faire. Ce qui manque souvent, c'est un système qui relie tout cela. La SwissGRC® Platform réunit vos sujets DORA en un seul endroit : structurés, connectés et prêts à répondre à tout moment.
[Demander une démo](#sgdora-cta) [Démarrer le contrôle de préparation DORA](#sgdora-readiness)
Registre d'informations prêt Incidents signalés dans les délais Tiers sous contrôle
Le DORA en 2026
## De la préparation à la surveillance en pratique
Le DORA n'est plus un sujet d'avenir. Les autorités de surveillance examinent, le registre d'informations est transmis chaque année, et les prestataires TIC tiers critiques sont sous surveillance européenne directe. Quiconque travaille encore avec des tableurs prend du retard.
**19**prestataires TIC tiers critiques désignés par les AESAES, novembre 2025
**600*+***incidents TIC majeurs signalés en Allemagne depuis l'entrée en application du DORABaFin, 2026
**63*%***des incidents signalés en Autriche liés à des prestataires TIC externesFMA, un an de DORA
**4*h***délai pour la notification initiale après classification d'un incident majeurProcessus de signalement DORA
**2023**Entrée en vigueur **Janv. 2025**Le DORA s'applique **Nov. 2025**Liste des prestataires critiques publiée **2026**Surveillance opérationnelle **Perspectives**Approfondissement et extension
2023
### Le DORA entre en vigueur
Le règlement (UE) 2022/2554 entre en vigueur le 16 janvier 2023. Les entités financières et les prestataires TIC disposent de deux ans pour aligner leur gouvernance, leurs processus et leurs contrats sur les cinq piliers de la résilience opérationnelle numérique. En parallèle, les AES précisent les exigences dans des normes techniques de réglementation et d'exécution (RTS et ITS).
Ce que cela signifie aujourd'hui : la période de transition est terminée. Les autorités de surveillance attendent des processus opérationnels, pas des concepts.
2025
### Le DORA s'applique : les obligations de signalement et le registre d'informations deviennent réalité
Le DORA s'applique depuis le 17 janvier 2025. Les entités financières signalent les incidents TIC majeurs dans des délais stricts et transmettent pour la première fois leur registre d'informations couvrant tous les accords contractuels avec les prestataires TIC tiers. Dès le premier cycle de transmission, les autorités de surveillance identifient des erreurs récurrentes : registres incomplets, stratégies de sortie manquantes et contrats pas encore alignés sur le contenu minimal des RTS.
Ce que cela signifie aujourd'hui : la qualité des données du registre d'informations est un axe de contrôle prioritaire des autorités. Des listes tenues manuellement ne tiennent pas la route.
2025
### Les AES désignent 19 prestataires TIC tiers critiques
Le 18 novembre 2025, l'ABE, l'AEMF et l'AEAPP publient la première liste des prestataires TIC tiers critiques, incluant de grandes plateformes cloud, des exploitants de réseaux et de centres de données ainsi que des fournisseurs de données financières spécialisés. Ces prestataires passent désormais sous surveillance européenne directe. Point important : la responsabilité opérationnelle du risque lié aux tiers reste entièrement du ressort de l'entité financière.
Ce que cela signifie aujourd'hui : vous devez rendre transparentes vos dépendances envers ces prestataires critiques, évaluer le risque de concentration et prouver vos stratégies de sortie.
2026
### Le début de la surveillance opérationnelle
Les AES mettent en place des équipes d'examen conjointes et désignent un contrôleur principal pour chaque prestataire TIC tiers critique, doté de pouvoirs étendus d'information, de contrôle et d'inspection. Parallèlement, le deuxième cycle de transmission du registre d'informations est en cours, le registre étant désormais transmis chaque année aux AES. Des autorités nationales comme la BaFin organisent des ateliers pour que les erreurs du premier cycle ne se reproduisent pas.
Ce que cela signifie aujourd'hui : votre registre, vos données d'incidents et vos évaluations des tiers doivent être cohérents et accessibles à tout moment. C'est exactement ce pour quoi la SwissGRC® Platform a été conçue.
2027+
### Une surveillance plus approfondie et un périmètre en expansion
La pratique de surveillance s'approfondit : examens élargis, listes de prestataires critiques mises à jour chaque année et attention croissante portée aux tests d'intrusion basés sur la menace (TLPT) pour les établissements importants. En Allemagne, le FinmadiG élargit en outre le périmètre. Les organisations qui traitent le DORA comme un processus continu plutôt que comme un projet en tirent l'avantage.
Ce que cela signifie aujourd'hui : construisez votre conformité DORA comme un processus permanent et outillé, pas comme un exercice annuel dans l'urgence.
Les cinq piliers du DORA
## Cinq piliers, une seule plateforme
Le DORA répartit ses exigences sur cinq champs d'action. La SwissGRC® Platform les relie dans un modèle de données intégré : risques, incidents, tests et tiers s'imbriquent au lieu de rester dans des silos séparés. Choisissez un pilier pour voir à quoi ressemble sa mise en œuvre concrète.
1 **Gestion des risques liés aux TIC**Art. 5 à 16 2 **Gestion des incidents et signalement**Art. 17 à 23 3 **Tests de résilience opérationnelle numérique**Art. 24 à 27 4 **Risque lié aux prestataires TIC tiers**Art. 28 à 44, y compris le registre d'informations 5 **Partage d'informations**Art. 45
Pilier 1 · Fondation
### Gestion des risques liés aux TIC
Les entités financières doivent exploiter un dispositif de gestion des risques TIC solide et documenté : inventorier systèmes et actifs, identifier, évaluer, traiter et surveiller en continu les risques, avec une responsabilité clairement établie au niveau de l'organe de direction.
#### Comment le mettre en œuvre avec la SwissGRC® Platform
- **Inventaire TIC connecté :** recensez les actifs protégés, systèmes et processus, et reliez-les aux risques, contrôles et prestataires.
- **SMSI intégré :** sécurité de l'information et risques TIC dans un seul modèle de données, avec suivi des mesures.
- **Reporting pour l'organe de direction :** tableaux de bord et rapports qui répondent aussi bien aux exigences des autorités qu'aux attentes du conseil d'administration.
Pilier 2 · Réactivité
### Gestion et signalement des incidents liés aux TIC
Les incidents doivent être détectés et classifiés, et les cas majeurs signalés à l'autorité compétente dans des délais stricts : notification initiale, rapport intermédiaire et rapport final, de façon cohérente et traçable.
#### Comment le mettre en œuvre avec la SwissGRC® Platform
- **Gestion des incidents de bout en bout :** de la saisie à l'analyse des causes profondes, en passant par la classification, dans un seul flux de travail.
- **Délais maîtrisés :** des processus de signalement structurés avec des responsabilités claires, pour que la notification initiale parte à temps.
- **Relié à la gestion des risques :** chaque incident alimente la chaîne cause-événement-impact et affine votre vision du risque.
Pilier 3 · Résilience
### Tests de résilience opérationnelle numérique
Des tests réguliers, des évaluations de vulnérabilités aux tests d'intrusion basés sur la menace (TLPT) pour les établissements importants, garantissent que les capacités de protection, de détection et de reprise fonctionnent réellement.
#### Comment le mettre en œuvre avec la SwissGRC® Platform
- **Planification et suivi des tests :** documentez de façon centralisée les types de tests, les cycles et les résultats, et gérez les constats sous forme de mesures.
- **PCA intégré :** créez et testez des plans de continuité, et réinjectez directement les enseignements dans les risques et contrôles.
- **Preuves prêtes pour l'audit :** un historique complet de tous les tests et mesures pour l'audit et la surveillance.
Pilier 4 · Priorité de surveillance 2026
### Gestion du risque lié aux prestataires TIC tiers
Le registre d'informations couvrant tous les accords contractuels avec les prestataires TIC tiers est transmis chaque année aux autorités de surveillance. S'y ajoutent la diligence raisonnable, le contenu contractuel minimal, le risque de concentration et les stratégies de sortie pour les fonctions critiques. Avec la surveillance des prestataires critiques par les AES, ce pilier occupe le devant de la scène en 2026.
#### Comment le mettre en œuvre avec la SwissGRC® Platform
- **Registre d'informations DORA :** recensez-le de façon structurée, tenez-le à jour et gardez-le prêt à être transmis.
- **Gestion du risque lié aux tiers :** évaluez et surveillez les prestataires et rendez visible le risque de concentration, y compris les dépendances envers les prestataires critiques.
- **Stratégies de sortie documentées :** consignez les plans de sortie pour les services critiques et tenez-les à jour.
Pilier 5 · Défense collective
### Partage d'informations sur les cybermenaces
Le DORA encourage l'échange volontaire de renseignements sur les menaces entre entités financières, au sein de communautés de confiance et dans le respect de la protection des données. Ceux qui partagent et reçoivent ces informations détectent plus tôt les schémas d'attaque.
#### Comment le mettre en œuvre avec la SwissGRC® Platform
- **Documenter le paysage des menaces :** recensez les renseignements externes de façon structurée et reliez-les à vos propres risques et scénarios.
- **La connaissance devient action :** les alertes se transforment en tâches suivies plutôt qu'en e-mails oubliés.
- **Une vision commune :** menaces, incidents et risques dans une vue cohérente unique, pour les spécialistes comme pour la direction.
La solution
## La conformité DORA avec la SwissGRC® Platform
Six fonctionnalités, un seul modèle de données intégré. Chaque exigence du DORA trouve une place claire dans la SwissGRC® Platform, et chaque élément est relié aux autres. Cela réduit le travail en double, et lorsque les autorités posent leurs questions, la réponse est déjà là.
01
### Contrôle de conformité DORA
Suivez la mise en œuvre de chaque exigence du règlement (UE) 2022/2554, y compris les RTS et ITS associés. Les écarts deviennent visibles, les mesures sont attribuées, et l'avancement reste transparent pour l'organe de direction.
Analyse des écartsSuivi des mesures
02
### Gestion des risques TIC et SMSI
Recensez et reliez l'ensemble de votre écosystème informatique. Identifiez, évaluez et surveillez les risques TIC dans un SMSI intégré et prenez des décisions fondées pour améliorer votre niveau de sécurité.
Pilier 1Actifs protégésMatrice des risques
03
### Registre d'informations au titre du DORA
Constituez et tenez à jour le registre de tous les accords contractuels avec les prestataires TIC tiers : saisie structurée, mises à jour régulières et traçabilité complète, prêt pour la transmission annuelle.
Pilier 4Transmission annuelleQualité des données
04
### Gestion des incidents
Détectez, classifiez et signalez les incidents conformément au DORA. Parfaitement intégré à la gestion des risques, couvrant toute la chaîne cause-événement-impact jusqu'au rapport final.
Pilier 2Délais de signalementAnalyse des causes profondes
05
### Gestion de la continuité d'activité
Planifiez et testez des mesures de continuité afin que votre organisation reste opérationnelle même en cas de crise. Les résultats des tests réalimentent directement les risques et les mesures, renforçant votre résilience dans la durée.
Pilier 3Plans de continuité
06
### Gestion du risque lié aux tiers
Adoptez une approche centrée sur les données pour l'ensemble du risque lié aux prestataires TIC tiers : diligence raisonnable, surveillance continue, risque de concentration et stratégies de sortie, y compris vos dépendances envers les prestataires critiques sous surveillance des AES.
Pilier 4Dépendances envers les prestataires critiquesStratégies de sortie
Interactif · 2 minutes
## Votre organisation est-elle prête pour le DORA ?
Six questions suivant les priorités d'examen des autorités de surveillance. Vous obtenez immédiatement une évaluation, de façon anonyme et sans inscription.
Question **1** / 6
Registre d'informations### Comment tenez-vous à jour votre registre d'informations sur les prestataires TIC tiers ?
Nous n'avons pas encore de registre complet. Dans des feuilles Excel, tenues manuellement et à différents endroits. Dans un outil central, mais sans lien avec les risques et les contrats. Centralisé, à jour et relié aux risques, contrats et fonctions.
Signalement des incidents### Pourriez-vous signaler un incident TIC majeur à votre autorité de surveillance dans les quatre heures suivant sa classification ?
Non, notre processus de signalement n'est pas défini. Le processus existe sur le papier mais n'a jamais été testé en conditions réelles. Oui, mais avec beaucoup de travail manuel et des incertitudes sur le contenu. Oui, le processus est outillé, testé et appuyé par des rôles clairement définis.
Risque lié aux tiers### Connaissez-vous vos dépendances envers les 19 prestataires TIC tiers critiques sous surveillance des AES ?
Nous n'avons pas encore examiné cette question. Approximativement, mais sans évaluation systématique du risque de concentration. Oui, les dépendances sont documentées ; certaines stratégies de sortie manquent encore. Oui, y compris les risques de concentration évalués et les stratégies de sortie.
Gestion des risques TIC### Dans quelle mesure votre inventaire TIC, vos risques et vos contrôles sont-ils reliés entre eux ?
Il n'existe pas d'inventaire TIC tenu à jour. Inventaire, risques et contrôles se trouvent dans des listes séparées. Partiellement reliés, mais pas systématiquement à jour. Entièrement reliés dans un seul système, mis à jour en continu.
Tests de résilience### Avec quelle rigueur testez-vous votre résilience opérationnelle numérique ?
Pas du tout jusqu'à présent, ou seulement lorsqu'un incident survient. Des tests occasionnels ; les résultats ne sont pas suivis de façon centralisée. Des tests réguliers, mais certains constats restent sans suite. Un programme de tests avec planification, suivi et gestion des mesures.
Gouvernance### Votre organe de direction reçoit-il régulièrement des rapports fiables sur la mise en œuvre du DORA ?
Non, le sujet n'est pas ancré au niveau de la direction. Seulement sur demande, et avec beaucoup d'efforts manuels. Régulièrement, mais les données sous-jacentes sont fragmentées. Régulièrement, en un clic, à partir d'un jeu de données cohérent unique.
0sur 100 points
[Demander une démo](#sgdora-cta) Refaire le contrôle
Le contrôle de préparation est une auto-évaluation non contraignante qui ne remplace pas un conseil réglementaire. Aucune réponse n'est enregistrée ni transmise.
Questions fréquentes
## Comprendre le DORA, situation 2026
Les questions essentielles sur le Digital Operational Resilience Act, mises à jour avec les derniers développements : de la surveillance des prestataires critiques à la transmission annuelle du registre d'informations.
Qu'est-ce que le Digital Operational Resilience Act (DORA) ?Le DORA est le règlement (UE) 2022/2554. Il est entré en vigueur le 16 janvier 2023 et s'applique depuis le 17 janvier 2025. Il harmonise les exigences de résilience opérationnelle numérique pour une vingtaine de types d'entités financières dans l'UE, des banques et assureurs aux établissements de paiement et prestataires de services sur crypto-actifs, et fait entrer directement les prestataires TIC tiers dans son champ d'application.
L'objectif : le secteur financier européen doit pouvoir détecter, gérer et se remettre de perturbations numériques graves sans mettre en péril la stabilité du système financier.
Quels sont les cinq piliers du DORA ?- **Gestion des risques liés aux TIC :** un dispositif documenté pour identifier, évaluer, gérer et surveiller le risque TIC.
- **Gestion des incidents et signalement :** les incidents TIC majeurs sont classifiés et signalés à l'autorité compétente dans les délais impartis.
- **Tests de résilience numérique :** des tests réguliers, jusqu'aux tests d'intrusion basés sur la menace (TLPT) pour les établissements importants.
- **Gestion du risque lié aux prestataires TIC tiers :** y compris le registre d'informations, le contenu contractuel minimal, le risque de concentration et les stratégies de sortie.
- **Partage d'informations :** échange volontaire de renseignements sur les cybermenaces entre entités financières.
Qu'est-ce qui a changé avec la liste des prestataires critiques de novembre 2025 ?Le 18 novembre 2025, les autorités européennes de surveillance ABE, AEMF et AEAPP ont désigné pour la première fois 19 prestataires TIC tiers comme critiques, des hyperscalers aux exploitants de réseaux et de centres de données, en passant par des fournisseurs spécialisés de données et services financiers. Depuis 2026, ces prestataires sont sous surveillance directe des AES, avec des contrôleurs principaux et des équipes d'examen conjointes.
**Important pour les entités financières :** la responsabilité opérationnelle reste de votre ressort. Si vous utilisez un prestataire critique, cette dépendance doit apparaître dans votre propre registre et votre évaluation du risque de concentration, et les enseignements de la surveillance des AES doivent alimenter votre propre gestion des risques TIC. Si un prestataire critique ne donne pas suite aux recommandations des autorités, les autorités nationales peuvent, en dernier recours, exiger des entités financières qu'elles suspendent ou mettent fin à l'utilisation de ses services.
Qu'est-ce que le registre d'informations et que prévoit-on à partir de 2026 ?Le registre d'informations documente tous les accords contractuels avec les prestataires TIC tiers, en signalant spécifiquement les services qui soutiennent des fonctions critiques ou importantes. Il est transmis chaque année aux AES via l'autorité de surveillance nationale.
Dès le premier cycle de transmission, les autorités ont relevé des faiblesses typiques : registres incomplets (pensez au shadow IT), plans de sortie manquants, et contrats encore en retard sur le contenu minimal des normes techniques. Pour les cycles en cours, la qualité des données est le facteur décisif. Un registre outillé, relié aux contrats, aux risques et aux fonctions, réduit considérablement les erreurs et l'effort nécessaire.
Quels sont les délais de signalement pour les incidents TIC majeurs ?Une fois qu'un incident est classifié comme majeur, la notification initiale doit intervenir dans les quatre heures, et au plus tard 24 heures après sa détection. Elle est suivie d'un rapport intermédiaire au plus tard 72 heures après la notification initiale, puis d'un rapport final, incluant l'analyse des causes profondes, au plus tard un mois après le dernier rapport intermédiaire. Les délais sont stricts, c'est pourquoi un processus de signalement testé, outillé et doté de rôles clairs est décisif. La pratique le confirme : depuis l'entrée en application du DORA, plusieurs centaines d'incidents TIC majeurs ont été signalés rien qu'en Allemagne, dont une large part liée à des prestataires externes.
Le DORA concerne-t-il aussi les entreprises suisses ?Le DORA est un règlement de l'UE, mais ses effets dépassent les frontières de l'UE. Les entreprises financières suisses ayant des filiales ou une activité commerciale dans l'UE sont concernées, tout comme les prestataires TIC suisses au service d'entités financières de l'UE : leurs clients exigent des contrats conformes au DORA, la capacité à fournir des preuves, et une coopération sur le registre d'informations. La pratique de surveillance suisse s'aligne elle aussi de plus en plus sur des principes de résilience opérationnelle comparables. Quiconque met en œuvre dès aujourd'hui la logique du DORA est bien positionné sur les deux marchés.
Quelles sont les différences entre le DORA et le NIS2 ?Le NIS2 est une directive au champ d'application large et transsectoriel, couvrant les entités essentielles et importantes. Le DORA est un règlement qui s'applique spécifiquement et directement au secteur financier. Pour les entités financières, le DORA prévaut sur le NIS2 en tant que régime sectoriel spécifique. De nombreuses organisations doivent néanmoins garder les deux référentiels à l'œil, par exemple dans des groupes comportant des entreprises financières et non financières. La SwissGRC® Platform cartographie les deux référentiels sur une seule plateforme, de sorte que les preuves ne doivent être produites qu'une seule fois.
Comment Swiss GRC soutient-elle la conformité au DORA ?La SwissGRC® Platform couvre les exigences du DORA comme un ensemble cohérent : un contrôle de conformité DORA avec suivi des mesures, la gestion des risques TIC et le SMSI, le registre d'informations au titre du DORA, une gestion des incidents de bout en bout avec processus de signalement, la gestion de la continuité d'activité, et la gestion du risque lié aux tiers, y compris les stratégies de sortie et les dépendances envers les prestataires critiques.
En tant que solution évolutive, elle grandit avec vous : commencez par les sujets DORA essentiels et étendez progressivement vos processus GRC à d'autres domaines. En option avec hébergement des données en Suisse, et accompagné par notre équipe, qui connaît le marché réglementé DACH pour l'avoir pratiqué pendant des années.
SwissGRC® Platform
## Les autorités demandent. *Vous répondez.*
Découvrez comment gérer votre registre d'informations, le signalement des incidents et le risque lié aux tiers avec la SwissGRC® Platform.
[ Demander une démo ](/fr/demo/) [Contacter l'équipe commerciale](https://swissgrc.com/fr/sales/)
---
### [EU Cyber Resilience Act (CRA) Compliance](https://swissgrc.com/fr/cyber-resilience-act-cra/)
**Published:** juillet 17, 2026
**Author:** superadmin
**Content:**
EU Cyber Resilience Act
# Devenez conforme au CRA, *sans perdre la vue d'ensemble.*
Le Cyber Resilience Act rend la cybersécurité obligatoire pour tout produit comportant des éléments numériques. La SwissGRC® Platform réunit vos processus CRA en un seul endroit, afin que vous restiez prêt à fournir des preuves à tout moment.
[Contactez-nous](#sgcra-cta) [Démarrer l'analyse des écarts](#sgcra-gap)
Première obligation de signalement à partir du **11 septembre 2026**
Chronologie
## Deux échéances 2026 qui comptent dès maintenant
Beaucoup pensent que tout se joue en 2027. C'est faux. La première obligation entre en vigueur en septembre 2026 et s'applique à tous les fabricants.
11 juin 2026
Principalement classes I et II### Désignation des organismes notifiés
Les États membres de l'UE désignent des organismes d'évaluation de la conformité accrédités. Aucune action immédiate n'est nécessaire pour les produits de catégorie standard utilisant l'auto-déclaration. Les fabricants de produits de classe I et II devraient prendre contact dès maintenant pour anticiper les goulots d'étranglement de capacité.
11 septembre 2026
S'applique à tous les fabricants### Obligations de signalement des vulnérabilités et incidents
L'obligation centrale et la plus immédiate. Les vulnérabilités activement exploitées et les incidents de sécurité graves doivent être signalés à l'autorité CSIRT nationale et à l'ENISA dans des délais stricts :
- **24 h**alerte précoce au CSIRT et à l'ENISA
- **72 h**rapport de suivi plus détaillé
- **14 jours**rapport final après correctif ou contournement
- **30 jours**rapport final pour les incidents graves
La chronologie complète en un coup d'œil
10 décembre 2024
**Le CRA entre en vigueur**La période de transition commence.
11 juin 2026
**Organismes notifiés actifs**Principalement pertinent pour les classes I et II.
11 septembre 2026
**Obligations de signalement des vulnérabilités et incidents**Tous les fabricants sont concernés. Les processus de signalement doivent être opérationnels.
11 décembre 2026
**Nombre suffisant d'organismes notifiés dans l'UE**Planification des capacités de certification.
11 décembre 2027
**Application intégrale de toutes les exigences du CRA**Le marquage CE devient obligatoire.
Classification
## Les quatre catégories de produits
Le CRA classe les produits selon leur risque. La catégorie détermine si l'auto-déclaration suffit ou si une évaluation par un organisme notifié est requise.
01
### Catégorie standard
environ 90 % de tous les produits
Logiciels métier courants, électronique grand public et appareils IoT standards.
Auto-déclaration du fabricant (module A)
02
### Classe I : produits importants
Risque élevé
Gestionnaires de mots de passe, antivirus, VPN, pare-feux, navigateurs.
Évaluation de conformité renforcée requise
03
### Classe II : produits critiques
Risque important
Systèmes de gestion de réseau, contrôles industriels, passerelles de compteurs intelligents.
Certification par un organisme notifié obligatoire
04
### Produits critiques essentiels
Niveau le plus élevé
Un groupe très restreint soumis aux exigences les plus strictes.
Évaluation externe obligatoire
Vous ne savez pas dans quelle catégorie se situent vos produits ? Faites notre **analyse gratuite des écarts CRA** plus bas sur cette page. Six questions vous donnent une première évaluation de votre niveau de préparation, de façon anonyme et sans inscription.
Exigences
## Les obligations techniques essentielles
Le CRA exige que la cybersécurité soit intégrée et prouvée tout au long du cycle de vie du produit. Cinq obligations sont centrales.
01### Sécurité dès la conception et par défaut
La sécurité dès le départ : paramètres par défaut sécurisés, pas de mots de passe universels, surfaces d'attaque minimales, données chiffrées.
02### Gestion des vulnérabilités
Mises à jour de sécurité pendant au moins cinq ans, ainsi qu'un processus PSIRT qui traite les vulnérabilités tout au long du cycle de vie.
03### Software Bill of Materials
Un inventaire complet et à jour de tous les composants logiciels par produit, y compris les composants tiers et open source.
04### Documentation technique et marquage CE
À partir de fin 2027, les produits concernés doivent disposer d'une déclaration de conformité UE et du marquage CE. Sans cela, aucune importation dans l'UE n'est possible.
05### Résilience et maîtrise des incidents
Les produits doivent résister aux attaques. Les fabricants doivent maîtriser rapidement les incidents et en informer les utilisateurs.
Livre blanc
## Cyber Resilience Act : ce que les fabricants suisses doivent faire dès maintenant
Un guide pratique de Swiss Infosec AG et Swiss GRC. Toutes les échéances, les quatre catégories de produits et une feuille de route concrète jusqu'à septembre 2026.
10 pages Toutes les échéances et obligations de signalement Feuille de route pour les équipes de développement
Télécharger le livre blanc Gratuit. Le téléchargement s'affiche immédiatement et est également envoyé par e-mail. Le livre blanc est en allemand.
### Cyber Resilience Act : ce que les fabricants suisses doivent faire dès maintenant
De l'analyse d'applicabilité aux quatre catégories de produits, jusqu'à une feuille de route concrète pour septembre 2026.
- Toutes les échéances et obligations de signalement en un coup d'œil
- Les quatre catégories de produits et leur signification
- Une feuille de route priorisée pour les équipes de développement
- Sanctions et mandat de représentant UE expliqués
Livre blanc conjoint de **Swiss Infosec AG** et **Swiss GRC**, avril 2026. Disponible en allemand.
### Téléchargement gratuit
Merci de renseigner vos coordonnées. Le téléchargement s'affiche immédiatement et vous est également envoyé par e-mail. Le livre blanc est rédigé en allemand.
First name
Last name
Business email
Organisation
I have read the [privacy policy](https://swissgrc.com/fr/privacy-policy/) and consent to the processing of my data.
### Merci, votre livre blanc est prêt
Le téléchargement démarre via le bouton ci-dessous. Une copie du lien se trouve également dans votre boîte de réception. Le livre blanc est en allemand.
[ Ouvrir le livre blanc (PDF) ](https://swissgrc.com/Downloads/Whitepaper/CRA_Whitepaper_SwissGRC_SwissInfosec.pdf)Rien ne s'est ouvert ? [Cliquez ici directement.](https://swissgrc.com/Downloads/Whitepaper/CRA_Whitepaper_SwissGRC_SwissInfosec.pdf)
Analyse des écarts gratuite
## Votre sécurité produit est-elle prête pour le CRA ?
Une auto-évaluation basée sur le modèle de maturité ENISA pour les PME : 25 questions réparties sur cinq domaines. Vous obtenez immédiatement un niveau de maturité par domaine et un niveau global, de façon anonyme et sans inscription.
Basé sur l'**ENISA SME Cyber Resilience Maturity Assessment Model**. Une auto-évaluation qui ne remplace pas une analyse de risque spécifique au produit, une analyse juridique ou une évaluation formelle de conformité au CRA.
**25** questions **5** domaines **5** minutes
Pour chaque question, choisissez la description la plus proche de votre pratique actuelle. Il n'y a pas de bonne ou de mauvaise réponse, juste un état des lieux honnête.
Démarrer l'analyse
Question **1** / 25
Retour Passer la question
0sur 5
### Résultat
#### Demander le rapport détaillé et la liste d'actions
Facultatif. Nous vous envoyons par e-mail une évaluation structurée avec votre maturité par domaine et une liste d'actions priorisées. Vos réponses restent anonymes tant que vous ne demandez pas le rapport.
First name
Last name
Business email
Organisation
I have read the [privacy policy](https://swissgrc.com/fr/privacy-policy/) and consent to the processing of my data.
**Merci.** Votre rapport est en cours d'envoi et arrivera bientôt dans votre boîte de réception.
[Demander une démo](/fr/demo/) Recommencer l'analyse
L'analyse des écarts est une auto-évaluation non contraignante basée sur le modèle de maturité ENISA et ne remplace pas une analyse de risque spécifique au produit, une analyse juridique ou une évaluation formelle de conformité au CRA.
Le rôle de la plateforme
## Structure et preuves pour votre conformité CRA
Le CRA exige non seulement un produit sécurisé, mais aussi des processus robustes et des preuves complètes. C'est exactement là qu'intervient la SwissGRC® Platform.
01
### Applicabilité et périmètre
Recensez votre portefeuille, attribuez à chaque produit une classe de risque, consignez l'action nécessaire. L'analyse devient un plan d'action suivi.
02
### Gestion des risques et SMSI
Évaluez et gérez les risques produit dans un modèle de données intégré. De nombreuses exigences du CRA correspondent à des contrôles ISO 27001 que vous couvrez déjà ici.
03
### Vulnérabilités et signalement
Modélisez votre processus PSIRT et gérez les délais de signalement stricts (24 h, 72 h, 14 jours) avec des rôles clairs et un historique complet.
04
### Le SBOM au niveau de la gouvernance
Reliez votre SBOM aux produits et aux risques. Lorsqu'un composant devient vulnérable, vous voyez immédiatement quels produits sont concernés.
05
### Documentation technique
Analyses de risque, mesures et dossiers de conformité en un seul endroit, versionnés et accessibles à tout moment.
06
### CRA, NIS2 et DORA réunis
CRA, NIS2 et DORA sur une seule plateforme. Vous produisez les preuves une fois, pas trois fois.
Questions fréquentes
## Comprendre le CRA
Les questions essentielles sur le Cyber Resilience Act, avec un focus particulier sur les fabricants suisses et la future législation nationale.
Qu'est-ce que le Cyber Resilience Act (CRA) ?Le CRA (règlement (UE) 2024/2847) est la première loi horizontale de l'UE à fixer des exigences de cybersécurité contraignantes pour tous les produits comportant des éléments numériques. Il complète des cadres tels que la directive NIS2 et le RGPD, mais s'adresse directement aux fabricants de produits et s'étend sur toute la chaîne d'approvisionnement. Il est entré en vigueur le 10 décembre 2024 et s'appliquera pleinement à partir du 11 décembre 2027.
Le CRA s'applique-t-il aussi aux entreprises suisses ?Oui. Le CRA est un règlement de marché de l'UE : quiconque met des produits comportant des éléments numériques sur le marché de l'UE doit respecter ces exigences, quel que soit le lieu d'implantation de l'entreprise. Cela concerne les fabricants qui vendent dans l'UE, les importateurs, les distributeurs et, sous certaines conditions, les fournisseurs cloud suisses. Les entreprises suisses sans établissement dans l'UE doivent également désigner un **représentant autorisé dans l'UE**.
Quelles échéances s'appliquent en 2026 et 2027 ?Trois dates sont centrales : à partir du **11 juin 2026**, les organismes notifiés d'évaluation de la conformité sont désignés (principalement pertinent pour les classes I et II). À partir du **11 septembre 2026**, les obligations de signalement des vulnérabilités activement exploitées et des incidents graves s'appliquent, et ce pour tous les fabricants. À partir du **11 décembre 2027**, le CRA s'applique pleinement, y compris le marquage CE et l'évaluation de conformité.
Quels sont les délais de signalement pour les vulnérabilités et les incidents ?À partir du 11 septembre 2026, les vulnérabilités activement exploitées et les incidents de sécurité graves doivent être signalés dans des délais stricts : une alerte précoce à l'autorité CSIRT nationale et à l'ENISA sous **24 heures**, un suivi plus détaillé sous **72 heures**, un rapport final sous **14 jours** après un correctif ou un contournement, et sous **30 jours** pour les incidents graves. Le signalement s'effectue via une plateforme centrale de l'ENISA.
Dans quelle catégorie se situe mon produit ?Le CRA comporte quatre niveaux : la **catégorie standard** (environ 90 % de tous les produits, l'auto-déclaration suffit), la **classe I** (produits importants tels que gestionnaires de mots de passe, VPN, pare-feux), la **classe II** (produits critiques tels que contrôles industriels, systèmes de gestion de réseau) et les **produits critiques essentiels** soumis aux exigences les plus strictes. Les classes I, II et les produits essentiels nécessitent une évaluation de conformité renforcée ou externe. Une analyse des écarts permet de clarifier la classification.
Quelles sont les sanctions en cas de non-conformité ?Pour les infractions graves, les autorités de surveillance du marché peuvent imposer des amendes allant jusqu'à **15 millions d'euros ou 2,5 % du chiffre d'affaires annuel mondial**, le montant le plus élevé étant retenu. Pour les infractions moins graves, le plafond est de 10 millions d'euros ou 2 %. Les autorités peuvent également interdire les ventes, ordonner des rappels ou retirer des produits du marché.
La Suisse introduit-elle sa propre législation ?Oui, cela se dessine. Le Conseil fédéral a chargé l'Office fédéral de la cybersécurité (OFCS) d'élaborer d'ici l'automne 2026 un projet de consultation pour une législation suisse sur la cyber-résilience des produits numériques, explicitement calquée sur le CRA de l'UE. Les fabricants suisses doivent donc s'attendre à une double vague réglementaire : le CRA de l'UE dès maintenant, et un pendant suisse attendu à partir de 2027 ou 2028. Quiconque met en œuvre dès aujourd'hui la logique du CRA est bien positionné pour les deux.
Comment la SwissGRC® Platform soutient-elle la conformité au CRA ?La plateforme apporte structure et preuves aux obligations organisationnelles du CRA : analyse d'applicabilité et périmètre, gestion des risques et SMSI, processus de vulnérabilités et de signalement avec leurs délais stricts, SBOM au niveau de la gouvernance, et documentation technique prête pour l'audit. Comme le CRA, le NIS2 et le DORA sont cartographiés sur une seule plateforme, les preuves ne doivent être produites qu'une seule fois. La sécurité dès la conception au niveau du produit lui-même reste une tâche de développement, pour laquelle Swiss GRC et son partenaire Swiss Infosec AG vous accompagnent.
## Le 11 septembre 2026 approche. *Préparez-vous de façon structurée.*
Découvrez comment gérer l'applicabilité, les vulnérabilités, les processus de signalement et la documentation technique avec la SwissGRC® Platform. Ou commencez par le livre blanc de Swiss Infosec AG et Swiss GRC.
[Demander une démo](/fr/demo/) [Télécharger le livre blanc](#sgcra-whitepaper)
---
### [AI Assistant ](https://swissgrc.com/fr/ai-assistant/)
**Published:** août 13, 2024
**Author:** Gent Krasniqi
**Content:**
GRACE AI · GRC NATIVEMENT IA
# Un nouveau niveau de l'intelligence GRC
Grace AI est l'assistant intégré à la SwissGRC® Platform. Posez vos questions avec vos propres mots. Grace travaille dans votre contexte GRC, relie risques, contrôles, politiques et incidents, et appuie chaque affirmation sur sa source.
[Demander une démo](#sgai-cta) [Contacter l'équipe commerciale](#sgai-cta)
Grace AI *SwissGRC® Platform* prêt
Posez une question à Grace
Reconstitution d'interface. Toutes les données sont fictives.
DANS LA PLATEFORME
## Grace travaille là où vous êtes déjà
Pas de deuxième outil, pas de changement de vue. Grace s'ouvre à côté de l'objet sur lequel vous travaillez et en connaît déjà le contexte.
Vue standard Arabe, droite à gauche
SwissGRC® Platform
 Grace connaît l'objet que vous avez ouvert et suggère des questions adaptées.  La même fonctionnalité en arabe, avec une mise en page entièrement de droite à gauche.
LES QUESTIONS
## Quatre questions, quatre réponses prouvées
Cliquez sur une question. Vous verrez ce que Grace répond et sur quoi repose la réponse.
Quels risques dépassent la tolérance ? Quels contrôles n'ont pas été testés ? Quelles politiques arrivent à expiration ? Résumez l'incident I-0233.
Grace AI*SwissGRC® Platform* prêt
Posez une question à Grace
Envie de poser la même question sur vos propres données ?
[Demander une démo](#sgai-cta)
Environnement de démonstration avec 128 risques, 341 contrôles et 26 politiques.
COMMENT SE FORME UNE RÉPONSE
## Ce qui se passe entre la question et la réponse
Grace n'invente rien. Elle répond à partir du contexte qui lui est transmis au moment où vous posez la question.
1. 01### Question
Vous posez votre question avec vos propres mots, dans le contexte de l'objet que vous avez ouvert.
2. 02### Contexte
Grace rassemble les objets liés en respectant vos rôles et vos droits d'accès.
3. 03### Raisonnement
Le modèle de langage compose la réponse à partir du contexte fourni, et non à partir de suppositions.
4. 04### Preuves
La réponse cite chaque objet qu'elle a utilisé. Vérifiable, citable, traçable.
RESPONSABILITÉ
## Une IA dont vous pouvez répondre
- ### Vos droits d'accès s'appliquent
Grace ne voit que ce que la personne connectée est autorisée à voir.
- ### Aucun entraînement sur vos contenus
Le contenu de votre environnement ne sert pas à entraîner des modèles de langage.
- ### Les décisions restent humaines
Grace propose, les personnes responsables valident.
- ### Les limites sont assumées
Lorsque les données ne permettent pas de répondre, Grace le dit au lieu de deviner.
QUESTIONS EN SUSPENS
## Ce que nos clients demandent en premier
Qu'est-ce que Grace AI ?Grace AI est l'assistant intégré à la SwissGRC® Platform. Vous posez des questions sur vos risques, contrôles, politiques et incidents en langage naturel et obtenez une réponse qui renvoie aux objets qu'elle a utilisés.
D'où viennent les réponses ?Du contexte transmis à Grace au moment où vous posez la question, c'est-à-dire les objets de votre environnement que vous êtes autorisé à voir. Le modèle de langage aide à formuler et structurer la réponse, il ne se substitue pas à vos données.
Que se passe-t-il quand Grace ne sait pas ?Elle le dit. Si un risque n'a par exemple aucune mesure enregistrée, Grace signale ce manque et suggère ce qui devrait normalement s'y trouver, plutôt que d'inventer une réponse.
Grace répond-elle dans la langue de mon équipe ?Oui. Grace reprend la question telle qu'elle est posée et répond dans la même langue. Pour l'arabe, cela inclut un sens de lecture entièrement de droite à gauche.
Grace remplace-t-elle le travail de nos responsables de risques ?Non. Grace prend en charge le travail préparatoire, la recherche et la rédaction. L'évaluation, l'approbation et la responsabilité restent entre les mains des personnes qui les détiennent aujourd'hui.
Comment obtenir Grace AI ?Lors d'une démonstration, nous vous montrons Grace sur vos propres sujets. Nous définissons ensuite ensemble, avec votre équipe, le périmètre, les rôles et le déploiement.
CONTACT ET DÉMO
## Découvrez Grace AI
sur votre propre paysage de risques
Lors d'une démonstration personnalisée, nous vous présentons Grace AI à partir de vos propres sujets et questions.
[Demander une démo](/fr/demo) [Contacter l'équipe commerciale](/fr/sales)
---
### [Operational Resilience Software](https://swissgrc.com/fr/operational-resilience-software/)
**Published:** août 21, 2025
**Author:** superadmin
**Content:**
Résilience opérationnelle# Une résilience par discipline,
ou par service métier ?
Identifiez les services métier importants, définissez des tolérances d'impact, cartographiez les dépendances et testez-les par des scénarios : Swiss GRC rend votre résilience opérationnelle prouvée.
[Demander une démo](https://swissgrc.com/fr/operational-resilience-software/#kontakt) [Découvrir les fonctionnalités](https://swissgrc.com/fr/operational-resilience-software/#funktionen)
Service métier important Traitement des paiements Tolérance d'impact 4 h testé 6 h Processus Traitement des transactions Réconciliation des transactions Applications Plateforme de paiement Système bancaire central Données Données de transaction Données clients Sites Centre de données Centre d'exploitation Tiers Prestataire de services de paiement fournisseur unique, pas de substitution Service métier important Traitement des paiements Tolérance d'impact 4 h testé 6 h Dépendances Processus 2 ressources Applications 2 ressources Données 2 ressources Sites 2 ressources Tiers 1 ressource fournisseur unique, pas de substitution
Approuvé par des organisations de premier plan
Ce qui fait la différence## De disciplines séparées
à une vision du service
PCA, SMSI, TPRM et gestion des risques sont bien établis. La résilience opérationnelle demande ce qu'ils signifient ensemble pour un service métier précis.
Le point de départ habituel### Des silos bien gérés, un service non testé
Chaque discipline est correctement documentée de son côté. Si un service critique reste dans sa tolérance d'impact ne se révèle que lors de l'incident.
- Services métier importants jamais formellement définis
- Dépendances envers l'IT, les collaborateurs et les prestataires éparpillées
- Tolérances d'impact absentes ou jamais testées
- Les preuves ne sont rassemblées qu'à l'occasion du contrôle prudentiel
Avec la SwissGRC® Platform### Un service, toutes les dépendances prouvées
Chaque service important reste relié aux processus, aux collaborateurs, aux systèmes, aux sites, aux prestataires et aux données. Les tolérances d'impact sont définies, testées et prouvées à tout moment.
- Services importants définis avec une tolérance d'impact
- Dépendances cartographiées pour chaque type de ressource
- Tests de scénarios avec résultats documentés
- Même base que la PCA, le SMSI, le TPRM et la gestion des risques
La SwissGRC® Platform en un coup d'œil## Votre résilience opérationnelle,
en un seul endroit
Cartographier, définir des tolérances, évaluer, tester et améliorer. Six blocs qui s'articulent les uns sur les autres.
01
### Cartographie complète des services
Identifiez et documentez les services métier clés avec toutes leurs dépendances critiques, jusqu'à la ressource individuelle.
- Services reliés aux processus, systèmes et prestataires
- Vue complète de la chaîne de service
- Vulnérabilités et dépendances uniques rendues visibles
02
### Gestion des tolérances d'impact
Définissez, surveillez et testez des seuils de perturbation clairs afin d'éviter tout préjudice inacceptable.
- Tolérance d'impact par service important
- Tolérance comparée à la reprise testée
- Dépassements identifiés précocement
03
### Évaluations de résilience
Identifiez tôt les faiblesses des ressources et processus critiques et priorisez les mesures correctives.
- Évaluation par type de ressource
- Actions avec responsable clair et échéance
- Priorisées selon l'impact sur le service
04
### Tests de scénarios
Testez la résilience dans des conditions sévères mais plausibles et validez vos stratégies de reprise.
- Planifiez et exécutez des scénarios
- Résultats et constats entièrement documentés
- Preuve que les tolérances sont respectées
05
### Conformité réglementaire
Gouvernance, revues régulières et processus documentés conformes aux attentes prudentielles.
- Auto-évaluation en tant que document vivant
- Preuves conservées, prêtes pour l'audit
- Analyses pour les autorités de surveillance et le conseil d'administration
06
### Amélioration continue
Les enseignements tirés des incidents, tests et évaluations alimentent en retour les stratégies et les actions.
- Les constats se transforment en actions suivies
- Tolérances et cartographie restent à jour
- Maturité renforcée de façon mesurable
Basé sur des **normes reconnues et des attentes prudentielles** en matière de résilience opérationnelle, de la Suisse à l'UE en passant par le Royaume-Uni.
DORA FINMA 2023/1 Basel Principles ISO 22301 NIS2
Statut réglementaire 2026## Les autorités regardent de plus près,
vos preuves tiennent la route
La résilience opérationnelle est passée d'une déclaration d'intention à une obligation auditée. Ces quatre évolutions marquent 2026.
UE
DORA
Applicable depuis janvier 2025. Le 18 novembre 2025, les autorités européennes de surveillance ont désigné les premiers prestataires TIC tiers critiques et les ont placés sous surveillance directe.
Suisse
Circulaire FINMA 2023/1
En vigueur depuis le 1er janvier 2024. La période transitoire pouvant aller jusqu'à deux ans pour le chapitre sur la résilience opérationnelle est arrivée à son terme.
Royaume-Uni
Résilience opérationnelle PRA et FCA
Depuis le 31 mars 2025, les établissements doivent rester dans leurs tolérances d'impact. La FCA critique surtout une cartographie incomplète des tiers et des preuves de test insuffisantes.
UE
Directive REC
Les États membres achèvent la désignation des entités critiques au cours de 2026. Les exigences de résilience touchent donc des organisations bien au-delà du secteur financier.
Normes et référentiels
Découvrez dans notre aperçu quelles normes, lois et référentiels la plateforme couvre.
[Voir les normes et référentiels](https://swissgrc.com/fr/standards-frameworks/)
Avantages et valeur ajoutée## Plus de résilience,
moins d'angles morts
À la fois complet et simple. Cela favorise l'adoption et rend la résilience mesurable.
#### Intégré à un système GRC connecté
La résilience opérationnelle s'appuie sur la même base que la PCA, le SMSI, le TPRM, le SCI et la gestion des risques, sans double saisie de données.
#### Substituabilité des services
Évaluez les canaux et prestataires alternatifs afin que les services critiques restent disponibles même lors d'une perturbation majeure.
#### Résilience des données
Préservez la confidentialité, l'intégrité et la disponibilité de vos informations les plus critiques, structurées et non structurées.
#### Planification de la reprise
Des plans de reprise qui ramènent les services critiques dans les tolérances d'impact définies.
#### Auto-évaluation réglementaire
Révisez régulièrement votre propre pratique de résilience et documentez-la comme un document vivant.
#### Gouvernance continue
Maintenez à jour les services importants, les tolérances et les responsabilités à mesure que votre paysage de risques évolue.
Contact et démo## Découvrez la plateforme
lors d'une démonstration en direct
Lors d'une démonstration personnalisée en direct, nous vous présentons la solution, de la cartographie des services jusqu'aux preuves, et répondons à vos questions.
[Demander une démo](https://swissgrc.com/fr/demo) [Contacter l'équipe commerciale](https://swissgrc.com/fr/sales)
---
### [Internal Audit Software](https://swissgrc.com/fr/internal-audit-software/)
**Published:** août 20, 2025
**Author:** superadmin
**Content:**
Audit interne# Votre plan d'audit couvre beaucoup de choses.
Mais couvre-t-il les bonnes ?
Planifiez, réalisez et suivez vos audits internes.
**De l'univers d'audit à l'action clôturée**, dans un seul système.
[Demander une démo](https://swissgrc.com/fr/internal-audit-software/#contact)[Découvrir les fonctionnalités](https://swissgrc.com/fr/internal-audit-software/#features)
Impact sur l'ensemble du cycle d'auditillustratifavantavec la plateforme50100 %Couverture des entités à haut risque68 %+2694 %Actions clôturées dans les délais52 %+3587 %Temps consacré au travail d'audit réel55 %+3085 %Le rapport d'audit est généré en un clic, pas en cinq jours de travail manuelImpact sur le cycle d'auditillustratifavantavec la plateformeCouverture des risques élevés+2694 %Actions clôturées dans les délais+3587 %Temps sur le travail d'audit+3085 %Le rapport d'audit est généré en un clic,pas en cinq jours de travail manuel
Approuvé par des organisations de premier plan
Ce qui fait la différence## Du rapport d'audit
à l'impact prouvé
Auditer est la partie facile. Ce qui distingue une fonction, c'est si les constats se traduisent, de façon prouvée, en changement réel.
Le point de départ habituel### Le plan annuel vit dans un tableur
Plan d'audit dans Excel, dossiers de travail sur un lecteur partagé, preuves dans la boîte mail. Le rapport est finalisé et le suivi s'estompe.
- Plan d'audit dans Excel, dossiers de travail sur un lecteur partagé
- Preuves éparpillées entre e-mails, captures d'écran et dossiers
- Le rapport au comité prend des jours de travail manuel
- Les actions ouvertes disparaissent de la vue une fois le rapport publié
Avec la SwissGRC® Platform### Un cycle d'audit unique, connecté de bout en bout
Univers d'audit, planification, dossiers de travail, constats et actions vivent dans un seul système. Le statut actuel peut être consulté à tout moment.
- Plan annuel dérivé du risque de chaque entité auditable
- Dossiers de travail et preuves rattachés à la mission
- Rapport d'audit et tableau de bord en un clic
- Actions avec responsable et échéance, suivies jusqu'à leur clôture
La SwissGRC® Platform en un coup d'œil## Tout votre cycle d'audit,
en un seul endroit
Structurez l'univers d'audit, menez vos missions, produisez vos rapports. Parcourez les trois vues.
01 Univers d'audit02 Processus d'audit et dossiers de travail03 Tableau de bord et reporting
Planification basée sur les risques### L'univers d'audit structuré par le risque
Chaque entité auditable dans un seul inventaire, avec notation de risque, fréquence d'audit et date du dernier audit. **Le plan annuel suit le risque**.
- Entités auditables avec notation de risque et fréquence d'audit
- Entités à haut risque répertoriées séparément
- Date du dernier audit et processus liés par entité

Travail de terrain### De la mission au dossier de travail
Le processus d'audit est modélisé sous forme de flux, avec des rôles allant du directeur d'audit jusqu'à l'audité. **Tests de contrôle, checklists et preuves sont rattachés à la mission**.
- Processus d'audit avec rôles, revues et validations
- Tests de contrôle et checklist d'audit en tant que dossiers de travail
- Une piste d'audit complète, de la planification au rapport

Reporting### Statut des audits et constats en un coup d'œil
Statut des audits, constats par statut et notation, ainsi que l'état des actions de gestion dans un seul tableau de bord. **Le rapport est généré en un clic**.
- Statut de l'audit, de la planification à la clôture
- Constats par statut et par gravité
- Rapport d'audit provisoire et final sous forme d'analyses prêtes à l'emploi

Basé sur des **normes reconnues**, de la planification basée sur les risques jusqu'au suivi des actions de gestion.
Global Internal Audit StandardsIPPFISO 19011Univers d'auditPlanification basée sur les risquesSuivi
Du rapport à l'impact## Audité, ce n'est pas résolu.
Résolu, c'est résolu.
Les Global Internal Audit Standards exigent explicitement, dans le Principe 15, que les résultats soient communiqués et les plans d'action suivis. C'est exactement là que le tableur s'arrête et que la plateforme commence.
Planification annuelle basée sur les risques
La fréquence d'audit de chaque entité découle de son risque. Plan, avancement et couverture sont visibles à tout moment, y compris pour le comité d'audit.
Dossiers de travail et tests de contrôle
Preuves, checklists et tests de contrôle sont rattachés à la mission plutôt qu'à un lecteur partagé. La piste d'audit se construit d'elle-même.
Constats et actions
Les constats sont notés et transformés en actions avec un responsable et une échéance. Les éléments en retard ressortent au lieu de disparaître.
Assurance qualité
Une approche cohérente pour chaque audit, documentée et analysable. La base du programme qualité interne.
Une seule base de données, plusieurs disciplines
Les constats agissent directement sur les risques et les contrôles. Audit interne, SCI et sécurité de l'information travaillent à partir de la même base.
[Système de contrôle interne](https://swissgrc.com/fr/internal-control-software-ics/)[Sécurité de l'information](https://swissgrc.com/fr/information-security-management-isms-software/)[Gestion des risques](https://swissgrc.com/fr/risk-management-software/)
Avantages et valeur ajoutée## Plus d'impact,
moins de travail manuel
À la fois complet et simple. C'est ce qui favorise l'adoption et fait progresser la maturité.
#### Des audits cohérents
Une approche standardisée garantit que chaque audit se déroule selon la même qualité et la même méthodologie.
#### Intégré à un système GRC connecté
Les audits partagent une même base avec le SCI, la gestion des risques, le SMSI et la conformité. Les constats produisent leurs effets là où ils doivent.
#### Prêt pour l'audit à tout moment
Des dossiers d'audit à jour et accessibles. Les inspections externes et les certifications cessent d'être des événements exceptionnels.
#### Moins de travail manuel
Les workflows et les analyses prêtes à l'emploi remplacent les e-mails de collecte et le travail manuel, laissant place au véritable travail d'audit.
#### Vision transversale des missions
Identifiez des tendances sur plusieurs audits et plusieurs années et tirez-en des améliorations ciblées.
#### Plus proche de la direction
Une vision d'ensemble défendable pour la direction générale et le comité d'audit fait de l'audit interne un conseiller de confiance.
Contact et démo## Découvrez notre solution
d'audit interne en action
Lors d'une démonstration personnalisée, nous vous présentons la SwissGRC® Platform et montrons comment planification d'audit, travail de terrain, constats et actions s'articulent.
[Demander une démo](https://swissgrc.com/fr/demo)[Contacter l'équipe commerciale](https://swissgrc.com/fr/sales)
---
### [AI Governance, Risk & Compliance (GRC)](https://swissgrc.com/fr/ai-grc/)
**Published:** février 4, 2025
**Author:** Yahya Mohamed Mao
**Content:**
Gouvernance, risque et conformité de l'IA# Vous déployez de l'IA.
Pouvez-vous en répondre ?
Cinq disciplines déterminent si votre usage de l'IA reste démontrablement responsable. Le module AI GRC de la SwissGRC® Platform les couvre toutes, **de façon complète et connectée**, du cas d'usage jusqu'à la métrique du modèle.
[Demander une démo](#contact) [Découvrir le module](#features)
EU AI ActISO 42001NIST AI RMFFINMA 08/2024
Gouvernance & contrôle Gouvernance& contrôle Gestion des risques & de la sécurité Risques &sécurité Conformité & référentiels réglementaires Conformité Protection des données & vie privée Données &vie privée Performance & transparence Performance AI GRC Sélectionnez une discipline
01*/05* Gouvernance & contrôle *Base*ISO 42001*·*EU AI Act Art. 4*·*FINMA 08/2024
### Qui décide, qui en est responsable, qui vérifie
Chaque cas d'usage et chaque modèle a un propriétaire responsable, un cycle de vie et une cadence de révision. Rien n'avance sans décision, aucune décision sans trace.
[Voir dans le module ](#features)
1. Principes et contrôles de gouvernance
2. Politiques et lignes directrices éthiques
3. Rôles et responsabilités
4. Gouvernance des fournisseurs et tiers
5. Gestion du cycle de vie
6. Surveillance continue
7. Audits internes IA basés sur les risques
8. Culture IA et formation
02*/05* Gestion des risques & de la sécurité *Base*NIST AI RMF*·*ISO 42005*·*ISO 27001
### Risques IA évalués, sécurisés, surveillés
Les risques IA rejoignent le même registre des risques que vos autres risques d'entreprise, avec les mêmes contrôles, incidents et actions. Pas de registre séparé, pas de processus séparé.
[Voir dans le module ](#features)
1. Risques IA dans le registre d'entreprise
2. Évaluations d'impact et de risques
3. Contrôles de sécurité pour les systèmes d'IA
4. Intégrité des modèles d'IA
5. Résilience et continuité d'activité
6. Renseignement sur les menaces et surveillance
03*/05* Conformité & référentiels réglementaires *Principe*Une seule cartographie*·*Vue des écarts par exigence*·*Preuves à la demande
### Évaluer une fois, prouver la conformité pour chaque référentiel
Un cas d'usage, de nombreuses obligations. La plateforme indique, par exigence, ce qui est couvert et ce qui reste ouvert. Une nouvelle réglementation signifie une nouvelle cartographie, pas une nouvelle collecte de données.
[Voir dans le module ](#features)
1. Système de management ISO 42001
2. EU AI Act avec classes de risque
3. Attentes de la FINMA
4. NIST AI RMF
5. Gestion du risque de modèle OCC
6. Principes d'éthique IA de la SDAIA
7. Vos propres référentiels et référentiels propriétaires
8. Évaluations de conformité
04*/05* Protection des données & vie privée *Base*Suisse nLPD*·*RGPD Art. 35*·*ISO 27701
### Données personnelles maîtrisées dans les processus d'IA
Les données d'entraînement et d'inférence sont le point sensible de toute initiative IA. L'analyse d'impact, la conservation et l'anonymisation sont directement rattachées au cas d'usage et au modèle.
[Voir dans le module ](#features)
1. Référentiels de protection des données
2. Analyses d'impact relatives à la protection des données
3. Contrôles de sécurité des données
4. Contrôles de confidentialité au niveau du modèle
5. Gouvernance des données sur l'ensemble du flux
6. Conservation et anonymisation
05*/05* Performance & transparence *Base*EU AI Act Art. 13*·*OCC 2011-12*·*SR 11-7
### Qualité du modèle mesurable, explicable, prouvée
C'est ici que la gouvernance rencontre la data science. Précision et stabilité avec des seuils, analyse des biais et validation indépendante. Une métrique devient une preuve.
[Voir dans le module ](#features)
1. Transparence et responsabilité
2. Explicabilité et documentation
3. Suivi de la performance avec seuils
4. Équité et analyse des biais
5. Validation et calibration indépendantes
6. Optimisation du modèle
Approuvé par des organisations de premier plan
Ce qui compte## D'une liste d'IA
à une gouvernance prouvable
Un inventaire, une politique et quelques évaluations sont vite mis en place. Ce qui distingue les organisations, c'est si cela tient encore une fois en exploitation.
Le point de départ habituel### Inventaire dans des tableurs, preuves éparpillées
Qui gère l'IA dans des tableurs connaît le statut d'hier. Classification, évaluations et métriques de modèle vivent dans des mondes séparés et ne se rejoignent qu'au moment de l'audit.
- Inventaire incomplet, IA fantôme non détectée
- Classification au cas par cas, sans preuve
- Évaluations dans des documents, métriques de modèle chez l'équipe spécialisée
- Efficacité prouvée à la mise en service, pas en exploitation
Avec la SwissGRC® Platform### Chaque décision IA appuyée par des preuves
Cas d'usage, modèles et outils figurent dans l'inventaire en tant qu'objets gouvernés, avec classification, évaluations, risques, contrôles et échéances de révision rattachés. Un statut qui tient à tout moment.
- Cas d'usage, modèles et outils dans un cycle de vie unique
- Classification selon l'EU AI Act, ISO 42001 et le NIST AI RMF
- Risques et contrôles ancrés dans le processus réel
- Évaluations, audits et validations planifiés et documentés
Le module AI GRC en un coup d'œil## Du cas d'usage à la
métrique du modèle, en un seul endroit
Inventorier, classifier, évaluer, surveiller. Parcourez les quatre vues.
01 Cas d'usage IA 02 Processus, risques et contrôles 03 Modèles IA 04 Supervision et surveillance
Inventaire et classification### Chaque cas d'usage gouverné et classifié
Cas d'usage, outils utilisés et modèles dans un cycle de vie unique, de la demande jusqu'à la désactivation. À partir de vos données, la plateforme dérive la classe de risque, la classe du modèle et les obligations qui en découlent, **visibles par référentiel**.
- Cycle de vie de la demande à la mise en production, en passant par la révision
- Outils avec criticité, internes ou externes
- Bibliothèque d'évaluations, de GAIRA à l'AIPD

Ancré dans le processus### Risques et contrôles sur le processus IA réel
Le cas d'usage est modélisé sous forme de diagramme de processus. Modèles, outils et flux de données portent leurs risques et contrôles **exactement là où ils s'appliquent**. Les lacunes de couverture ressortent immédiatement.
- Modèles, outils et flux de données dans le diagramme
- Risques et contrôles directement sur l'étape du processus
- Connecté à la gestion des risques et au SCI

Performance et transparence### La qualité du modèle comme métrique de gouvernance
Précision et stabilité avec seuil, historique et responsable désigné. AuROC, Gini et KS deviennent un **chiffre qui tient devant le conseil d'administration**, appuyé par la documentation et la logique de décision.
- Métriques de précision et de stabilité avec seuils
- Transparence, explicabilité et documentation du modèle
- L'assistant explique les métriques en contexte

Surveillance continue### Révisions planifiées, historique complet
Évaluations, audits, validations et calibrations avec échéance et responsable. L'historique prouve **qui a révisé quoi et quand**, sans que personne n'ait à rassembler des documents.
- Évaluations, audits et validations à échéance en un coup d'œil
- Historique complet de supervision par cas d'usage
- Preuves disponibles à la demande pour l'audit et la surveillance

Basé sur des **référentiels reconnus**, de la classification jusqu'à la preuve de conformité.
EU AI Act ISO 42001 NIST AI RMF FINMA 08/2024
Réglementation## Le report n'est pas un blanc-seing,
c'est votre fenêtre de mise en œuvre
Les obligations de transparence de l'EU AI Act s'appliquent depuis le 2 août 2026. Les obligations pour l'IA à haut risque ont été reportées à décembre 2027. Construisez maintenant et vous arriverez préparés, pas dans l'urgence.
2 février 2025
En vigueur
Pratiques d'IA interdites et culture IA du personnel
2 août 2025
En vigueur
Obligations pour les modèles d'IA à usage général (GPAI)
2 août 2026
En vigueur
Obligations de transparence au titre de l'art. 50, y compris l'étiquetage des contenus IA
2 décembre 2027
À venir
IA à haut risque autonome selon l'annexe III
2 août 2028
À venir
IA à haut risque intégrée dans des produits réglementés selon l'annexe I
**Important pour la planification :** Les échéances reportées allègent l'évaluation de conformité, pas les fondations. Inventaire, classification, rôles et preuves doivent être en place avant cela, sinon un report se transforme en retard accumulé. Les échéances de l'EU AI Act ont été modifiées en 2026, veuillez confirmer avec votre service juridique le statut qui vous concerne.
Référentiels et normes## Collecter une fois,
prouver pour tous
Le module intègre les principaux référentiels et prend aussi en charge les vôtres. Une seule collecte de données, de multiples preuves.
Union européenne
#### EU AI Act
Classes de risque, rôles de fournisseur ou de déployeur et obligations qui en découlent, par cas d'usage.
International
#### ISO/IEC 42001
Système de management de l'intelligence artificielle, comme structure pour les politiques, contrôles et audits.
International
#### ISO/IEC 42005
Analyse d'impact pour les systèmes d'IA, comme méthode derrière vos analyses d'impact.
États-Unis
#### NIST AI RMF
Govern, Map, Measure et Manage comme structure pour évaluer et piloter les risques IA.
Suisse
#### FINMA 08/2024
Attentes prudentielles en matière de gouvernance et de gestion des risques pour l'utilisation de l'IA dans le secteur financier.
Secteur financier
#### OCC Model Risk Management
Pratique éprouvée de validation des modèles, reliée à vos métriques et calibrations.
Complémentaire
#### SDAIA and MIT AI Risk Repository
Principes éthiques et taxonomies de risques issues de la recherche, pour les organisations à vocation internationale.
Vos exigences
#### Vos propres référentiels
Les politiques de groupe et vos propres taxonomies sont cartographiées et évaluées comme n'importe quel autre référentiel.
Avantages et bénéfices## Maîtrisez votre IA
sans en freiner le rythme
Une gouvernance qui laisse la place au rythme. C'est ce qui favorise l'adoption dans les métiers et la confiance au conseil d'administration.
#### L'IA fantôme devient visible
Un parcours de demande guidé fait entrer chaque nouveau cas d'usage dans l'inventaire, au lieu de contourner la gouvernance.
#### Évaluer une fois, prouver plusieurs fois
Une seule collecte de données, plusieurs référentiels : EU AI Act, ISO 42001, NIST AI RMF et vos propres exigences à partir de la même base.
#### La gouvernance rencontre la data science
Métriques de modèle, validations et calibrations se trouvent là où résident les politiques, risques et contrôles.
#### Prêt pour l'audit, pour les autorités et les auditeurs
Classification, évaluation, approbation et révision sont enregistrées avec date, responsable et preuve.
#### Pas de registre IA isolé
Risques, contrôles et actions liés à l'IA figurent dans le même catalogue que le reste de votre gouvernance, plutôt que dans un silo à part.
#### Pas d'arrêt sur image de la conformité
La surveillance continue remplace l'approbation ponctuelle. Dérives, échéances et écarts se signalent d'eux-mêmes.
Contact et démo## Nous vous présentons
le module AI GRC en direct
Lors d'une démonstration personnalisée, nous vous présentons l'ensemble du module : inventaire, classification, évaluations, ancrage dans le processus, métriques de modèle et preuves. Sur un exemple concret de bout en bout, sans aucune préparation de votre part.
[Demander une démo](https://swissgrc.com/fr/demo) [Contacter l'équipe commerciale](https://swissgrc.com/fr/sales)
---
### [Logiciel de gestion de la protection des données](https://swissgrc.com/fr/data-protection-management-software/)
**Published:** février 27, 2023
**Author:** superadmin
**Content:**
Gestion de la protection des données# Des lois sur la protection des données plus strictes chaque année.
Où sont vos preuves ?
Registres des traitements, AIPD, TIA, violations de données et droits des personnes concernées sur une seule plateforme : Swiss GRC rend votre programme de protection des données documenté dans chaque juridiction pertinente.
[Demander une démo](https://swissgrc.com/fr/data-protection-management-software/#kontakt) [Découvrir les fonctionnalités](https://swissgrc.com/fr/data-protection-management-software/#funktionen)
Registre des traitements Données clients CRM l'une des 214 activités de traitement RGPD UE Art. 30, AIPD, notification sous 72 heures Suisse nLPD Registre des traitements, notification au PFPDT UK Data (Use and Access) Act 2025 Registre des traitements, demandes d'accès, transferts India DPDP Rules 2025 gestionnaire de consentement, notices d'autres juridictions dans le catalogue Registre des traitements Données clients CRM RGPD UE Suisse nLPD UK Data (Use and Access) Act 2025 India DPDP Rules 2025 d'autres juridictions dans le catalogue
Approuvé par des organisations de premier plan
Ce qui fait la différence## D'un silo dédié à la protection des données
à une conformité prouvée
Les registres, les AIPD et la gestion des violations sont déjà bien établis. La différence réside dans leur capacité à fonctionner ensemble, à travers les juridictions et les disciplines.
Le point de départ habituel### Des outils côte à côte, des preuves à la main
Un outil de protection des données séparé, à côté du SMSI et du TPRM, entraîne une duplication des données de référence et des preuves qui ne se rassemblent qu'au moment de l'audit.
- Registres, AIPD et contrats dans des systèmes séparés
- Chaque nouvelle juridiction implique de repartir de zéro manuellement
- Des échéances comme les 72 heures reposent sur des personnes individuelles
- Les flux de données vers les sous-traitants ne sont pas visibles de bout en bout
Avec la Plateforme SwissGRC®### Un seul registre, chaque obligation prouvée
Les activités de traitement restent reliées aux bases légales, aux risques, aux sous-traitants, aux contrats et aux actions. Les preuves sont disponibles à tout moment, pour chaque juridiction applicable.
- Le registre des traitements constitue la base commune pour chaque obligation
- Les juridictions proviennent du catalogue, pas d'un travail manuel
- Échéances et chemins de notification pilotés par des workflows
- Même base que le SMSI, le TPRM, le SCI et la gestion des contrats
La Plateforme SwissGRC® en un coup d'œil## Toute votre gestion de la protection des données,
en un seul endroit
Enregistrez, évaluez, notifiez, répondez et générez vos rapports. Parcourez les six vues.
01 Registres 02 AIPD 03 Transferts 04 Violations 05 Droits des personnes concernées 06 Reporting
Registre des activités de traitement### Chaque activité de traitement documentée et reliée
Toutes les activités de traitement dans une seule structure, avec finalité, base légale, catégories de données, destinataires et durée de conservation. **Prêt à répondre aux autorités et aux personnes concernées**.
- Registre complet conforme à l'art. 30 du RGPD et à la nLPD
- Catégories de données, destinataires et durée de conservation consignés
- Relié aux sous-traitants, aux contrats et aux systèmes

Analyse d'impact relative à la protection des données### Risque élevé identifié avant le début du traitement
L'AIPD en tant qu'évaluation structurée des risques avant le début du traitement, avec des critères librement définissables et des **actions rattachées au risque**.
- Analyse de seuil et AIPD complète
- Matrice des risques avec évaluation brute et nette
- Actions avec responsable clair et échéance

Analyse d'impact des transferts (TIA)### Transferts vers des pays tiers évalués et justifiés
Pour chaque transfert vers un pays tiers, une évaluation documentée du pays destinataire, des garanties et des **mesures supplémentaires**.
- TIA par pays destinataire et par sous-traitant
- Garanties et clauses contractuelles types consignées
- Mesures supplémentaires documentées et traçables

Gestion des violations de données### Délais de notification respectés sans improvisation
Enregistrez, évaluez et notifiez les violations, avec rappels et rapports destinés aux autorités de contrôle et aux personnes concernées. **Le délai de 72 heures sous contrôle**.
- Évaluation de l'obligation de notification avec justification
- Délais et rappels surveillés automatiquement
- Analyse des causes profondes et actions rattachées à la violation

Demandes des personnes concernées### Demandes traitées dans les délais et documentées
Accès, rectification, effacement et portabilité sous forme de processus guidé, de la vérification d'identité jusqu'à la **réponse documentée**.
- Chaque type de demande dans un seul workflow
- Vérification d'identité et contrôle des délais
- Réponse et preuves conservées, prêtes pour l'audit

Reporting protection des données### L'état de votre programme en un coup d'œil
Une vue claire pour la direction, le délégué à la protection des données et les auditeurs : **couverture, échéances ouvertes et position de risque**.
- Couverture des registres, AIPD et TIA rendue visible
- Demandes ouvertes, violations et échéances visualisées
- Analyses pour l'audit et la direction

Basé sur des **normes reconnues et un catalogue de juridictions tenu à jour**, de la législation suisse et européenne aux lois internationales sur la protection des données.
ISO/IEC 27701:2025 ISO 27001 RGPD UE nLPD lois internationales sur la protection des données
Situation réglementaire 2026## La loi continue d'évoluer,
vos preuves restent à jour
Le droit de la protection des données ne cesse de croître et d'évoluer. Ces quatre développements marquent l'année 2026 en la matière.
UE
Digital Omnibus
La Commission négocie des amendements au RGPD, notamment sur la définition des données à caractère personnel et la pseudonymisation. Un accord politique est visé pour 2026.
Royaume-Uni
Data (Use and Access) Act 2025
Les dispositions relatives à la protection des données sont entrées en vigueur le 5 février 2026, introduisant des intérêts légitimes reconnus et un assouplissement des règles relatives à la prise de décision automatisée.
Inde
DPDP Rules 2025
Notifiées le 14 novembre 2025. La période de transition court jusqu'en novembre 2026, avec une application intégrale à partir de mai 2027.
ISO
ISO/IEC 27701:2025
Depuis le 14 octobre 2025, la norme relative aux systèmes de management de l'information privée est certifiable de manière autonome et ne nécessite plus l'ISO 27001 comme base.
Juridictions et normes
Découvrez dans notre aperçu quelles normes, lois et référentiels la plateforme couvre.
[Voir les normes et référentiels](https://swissgrc.com/fr/standards-frameworks/)
Avantages et valeur ajoutée## Plus de preuves,
moins d'outils
Complet et simple à la fois. Cela favorise l'adoption et rend la protection des données défendable.
#### Un seul registre pour chaque obligation
Saisissez les activités de traitement une seule fois : les registres, AIPD, TIA et droits des personnes concernées s'appuient tous dessus.
#### Élément d'un système GRC connecté
La protection des données partage la même base que le SMSI, le TPRM, le SCI, la conformité et la gestion des contrats, sans silo séparé.
#### International, pas seulement le RGPD
De la nLPD et du RGPD à d'autres législations internationales sur la protection des données : les obligations par juridiction applicable.
#### Flux de données et sous-traitants visualisés
Activités de traitement reliées aux systèmes, aux sous-traitants et aux contrats, y compris les transferts à l'étranger.
#### Certifié ISO 27001, 27017 et 27701
Nous exploitons la plateforme selon les mêmes normes que celles que nous cartographions pour votre système de management de la protection des données.
#### Délais respectés de manière fiable
Délais de notification, demandes des personnes concernées et actions avec responsable, échéance et rappels automatiques.
Contact et démo## Découvrez la plateforme
lors d'une démonstration en direct
Lors d'une démonstration personnalisée en direct, nous vous présentons la solution, des registres aux preuves, et répondons à vos questions.
[Demander une démo](https://swissgrc.com/fr/demo) [Contacter les ventes](https://swissgrc.com/fr/sales)
---
### [BCM Software](https://swissgrc.com/fr/bcm-software/)
**Published:** février 7, 2023
**Author:** superadmin
**Content:**
Gestion de la continuité d'activité# Des plans de continuité sur le papier,
ou une résilience quand cela compte ?
Cartographiez les processus critiques, définissez des objectifs de reprise, testez vos plans et rendez compte de la maturité : Swiss GRC rend votre PCA défendable.
Conforme à l'ISO 22301.
[Demander une démo](https://swissgrc.com/fr/bcm-software/#kontakt) [Découvrir les fonctionnalités](https://swissgrc.com/fr/bcm-software/#funktionen)
avec la plateforme SwissGRC® avec un PCA dans des documents et tableurs 100% 0 Capacité opérationnelle Temps ▶ Perturbation RTO MTPD RPO 1 2 3 Fonctionnement minimal évité grâce à la plateforme 1 Plan disponible instantanément, rôles et escalade consignés 2 Reprise dans les délais, plans testés et documentés 3 Maturité et lacunes ouvertes reportables à tout moment avec la plateforme SwissGRC® avec un PCA dans des documents et tableurs 100% Perturbation RTO MTPD évité grâce à la plateforme 1 Plan disponible instantanément, rôles et escalade consignés 2 Reprise dans les délais, plans testés et documentés 3 Maturité et lacunes ouvertes, reportables à tout moment
Approuvé par des organisations de premier plan
Ce qui fait la différence## Des plans archivés
à une résilience prouvée
La plupart des organisations disposent déjà d'une BIA, de plans et d'exercices. La différence réside dans leur actualité et leur mise en relation.
Le point de départ habituel### De bons plans, des fondations obsolètes
Lorsque la BIA, les plans et les résultats des exercices vivent dans des documents et des tableurs, ils deviennent obsolètes entre deux cycles de révision.
- BIA dans des tableurs, plans dans des documents séparés
- Les dépendances envers l'IT, les sites et les fournisseurs restent floues
- Les constats des exercices ne remontent jamais dans les plans
- La maturité n'apparaît que lors de l'audit
Avec la Plateforme SwissGRC®### Reprise connectée et documentée
Les processus critiques restent reliés aux ressources, aux plans, aux exercices et aux actions. Chaque engagement de reprise est documenté à tout moment, pas seulement affirmé.
- BIA, plans et exercices dans un seul système
- Dépendances envers l'IT, les sites et les fournisseurs reliées
- Les constats deviennent des actions d'amélioration suivies
- Intégré à la gestion des risques, au SMSI et au TPRM
La Plateforme SwissGRC® en un coup d'œil## Tout votre PCA,
en un seul endroit
Analysez, planifiez, testez, connectez et générez vos rapports. Parcourez les cinq vues.
01 Analyse d'impact (BIA) 02 Plans de continuité 03 Exercices et tests 04 Intégration 05 Reporting PCA
Analyse d'impact sur l'activité### Processus critiques et leurs dépendances
Recensez et évaluez les fonctions et processus critiques de façon structurée : impact dans le temps, ressources nécessaires et **MTPD, RTO et RPO** par processus.
- Impact évalué selon des horizons temporels définis
- Dépendances envers l'IT, les collaborateurs et les fournisseurs
- Objectifs de reprise déduits par processus

Plans de continuité et de reprise### Des plans que vous retrouvez réellement quand cela compte
Créez vos plans directement dans la plateforme ou gérez-les de façon centralisée, avec rôles, actions immédiates et chemins d'escalade. **Toujours à jour et versionnés**.
- Plans structurés dans la solution ou sous forme de document
- Rôles, contacts et chemins d'escalade consignés
- Validation et gestion des versions entièrement traçables

Exercices et tests### Efficacité prouvée en situation
Planifiez, réalisez et documentez vos exercices. Les constats se transforment en **actions d'amélioration suivies**, avec un responsable clair et une échéance.
- Planification des exercices sur le cycle annuel
- Résultats et constats entièrement documentés
- Actions déduites directement de l'exercice

Résilience intégrée### PCA connecté au SMSI, au TPRM et au SCI
Données de référence partagées pour les processus, les systèmes et les fournisseurs. Un même risque de perturbation devient **visible dans toutes les disciplines**.
- Base commune pour les processus, les actifs et les fournisseurs
- Workflows transversaux entre les divisions
- Résilience opérationnelle dans une vue d'ensemble unique

Reporting### Maturité et lacunes en un coup d'œil
Une vue claire pour la direction et le conseil d'administration : **couverture, actualité et lacunes ouvertes** sur l'ensemble du programme PCA.
- Couverture des processus critiques rendue visible
- Actualité des plans et des exercices visualisée
- Analyses prêtes pour le conseil d'administration

Basé sur des **méthodes et normes reconnues**, de l'analyse d'impact sur l'activité jusqu'à la reprise documentée.
ISO 22301 ISO 22317 BSI Standard 200-4 résilience opérationnelle
Comment ça fonctionne## Du premier processus
à un SMCA que vous vivez réellement
La continuité d'activité est un cycle, pas un projet. La plateforme vous guide à travers les quatre phases, à votre propre rythme.
01
Analyser
Recensez les fonctions critiques, les dépendances et les objectifs de reprise dans une BIA structurée.
02
Planifier
Définissez des stratégies et des plans par scénario, avec rôles, ressources et chemins d'escalade.
03
Tester
Testez des scénarios, documentez les constats et déduisez des actions d'amélioration.
04
Améliorer
Maintenez les plans, objectifs et dépendances à jour et augmentez la maturité de façon mesurable.
Un pas de plus
Évaluez et quantifiez le risque de perturbation et le risque opérationnel sur notre page dédiée à la gestion des risques.
[Découvrir la gestion des risques](https://swissgrc.com/fr/risk-management-software/)
Avantages et valeur ajoutée## Plus de résilience,
moins d'improvisation
Complet et simple à la fois. Cela favorise l'adoption et rend la résilience mesurable.
#### Visibilité sur les processus critiques
Fonctions et processus critiques, ainsi que leurs dépendances, recensés et évalués de façon systématique.
#### Élément d'un système GRC connecté
Le PCA partage la même base que la gestion des risques, le SCI, le SMSI, le TPRM et la gestion des contrats.
#### Menaces identifiées tôt
Recensez et surveillez les menaces pesant sur votre résilience, reliées à vos analyses de risques.
#### Des plans qui tiennent sous pression
Des plans de continuité et de reprise à jour, faciles à retrouver et testés en situation.
#### Une maturité plus élevée grâce aux normes
Mettez en place et exploitez un SMCA conforme à l'ISO 22301 : une approche cohérente à l'échelle de l'organisation.
#### Une maturité mesurable
Couverture, actualité et lacunes ouvertes visibles à tout moment et reportables jusqu'au conseil d'administration.
Contact et démo## Découvrez la plateforme
lors d'une démonstration en direct
Lors d'une démonstration personnalisée en direct, nous vous présentons la solution, des enregistrements aux preuves, et répondons à vos questions.
[Demander une démo](https://swissgrc.com/fr/demo) [Contacter les ventes](https://swissgrc.com/fr/sales)
---
### [Logiciel de contrôle interne / SCI](https://swissgrc.com/fr/internal-control-software-ics/)
**Published:** février 7, 2023
**Author:** superadmin
**Content:**
Système de contrôle interne# Votre contrôle est décrit.
Mais est-il efficace ?
Réduisez les risques, améliorez les processus.
**Exécutez, documentez et évaluez vos contrôles en continu.** Existence et efficacité prouvées.
[Demander une démo](https://swissgrc.com/fr/internal-control-software-ics/#contact)[Découvrir les fonctionnalités](https://swissgrc.com/fr/internal-control-software-ics/#features)
Cockpit de contrôlemis à jour en continu
**84***%*
efficacité prouvée
+12 points sur un an
**100**contrôles dans l'inventaire
**9**constats ouverts
**7**pas encore testés
Ce dont la plateforme se charge
- Contrôles distribués automatiquement, avec échéance et rappel
- Les preuves sont produites pendant l'exécution, pas après coup
- Efficacité prouvée, prêt pour l'audit à tout moment
*fini les tableurs envoyés par e-mail·audits en jours plutôt qu'en semaines·les lacunes de contrôle apparaissent tôt*
Approuvé par des organisations de premier plan
Ce qui fait la différence## D'une course annuelle contre la montre
à un pilotage continu des contrôles
Les processus, les risques et les contrôles sont documentés dans la plupart des organisations. Ce qui les distingue, c'est de savoir si les contrôles sont réellement exécutés au quotidien.
Le point de départ habituel### Un SCI qui ne se réveille qu'en saison
La matrice des risques et contrôles vit dans Excel et les preuves arrivent par e-mail. Peu avant l'audit, tout est testé d'un coup.
- Matrice de contrôle dans Excel, preuves par e-mail
- Les responsables de contrôle ne savent pas ce qui est dû et quand
- Les tests ont lieu juste avant l'audit, tous en même temps
- Les constats sont enregistrés mais ne sont pas suivis jusqu'au bout
Avec la Plateforme SwissGRC®### Un SCI qui continue de fonctionner toute l'année
Les contrôles sont distribués, confirmés et documentés automatiquement. L'efficacité se construit tout au long de l'année, pas en décembre.
- Contrôles distribués automatiquement, avec échéance et rappel
- Preuves jointes directement à l'exécution du contrôle
- Tests et évaluations des contrôles répartis sur toute l'année
- Constats avec action, responsable et échéance
La Plateforme SwissGRC® en un coup d'œil## Tout votre SCI,
en un seul endroit
Modélisez, reliez, exécutez, évaluez, testez et générez vos rapports. Parcourez les six vues.
01 Documentation des processus02 Matrice des risques et contrôles03 Exécution des contrôles04 Évaluations des contrôles05 Tests des contrôles06 Reporting SCI
BPMN 2.0### Processus, risques et contrôles réunis dans une seule vue
Processus de management, cœur de métier et support modélisés, avec les rôles répartis en couloirs (swimlanes). **Les risques et contrôles sont positionnés directement sur l'étape du processus**.
- Hiérarchie des processus, du management aux processus de support
- Risques indiqués sur l'étape du processus, pas dans une liste séparée
- Export PDF, validation et version conservés sur le processus

MRC### Chaque risque avec son contrôle
La matrice réunit processus, risque et contrôle, avec responsable, fréquence et pertinence. **La conception et l'efficacité du contrôle sont visibles dans une seule colonne**.
- Regroupés par processus, contrôles clés signalés
- Fréquence de contrôle, du quotidien à l'événementiel
- Adéquation et efficacité en un coup d'œil

Exécution des contrôles### Le contrôle arrive à la bonne personne
La plateforme distribue automatiquement les contrôles dus à leurs responsables et leur rappelle les échéances. **L'exécution est confirmée et documentée**.
- Notification automatique avec un lien vers la tâche
- Tâche avec échéance, attribution et statut
- Preuves et constats joints à la tâche

Adéquation et efficacité### Adéquat et efficace, évalué
Les contrôles sont évalués régulièrement quant à leur adéquation et leur efficacité. **Le tableau de bord montre où cela ne fonctionne pas**, par processus et par unité organisationnelle.
- Contrôles évalués par processus et par efficacité
- Filtrage par unité organisationnelle, catégorie et processus
- Contrôles clés évalués séparément

Tests et constats### Efficacité testée, déficiences documentées
Walkthrough, test de conception et évaluation globale structurés par contrôle. **Les constats et recommandations apparaissent pendant le test**, pas après coup.
- Questionnaire de test organisé par domaine et par contrôle
- Walkthrough, test de conception et évaluation globale documentés
- Constats et recommandations saisis directement

Reporting### Les résultats des contrôles pour le bon public
Statut d'exécution, adéquation et efficacité réunis dans un seul tableau de bord. **Une vue unique sur laquelle la direction et l'organe de révision peuvent s'appuyer**.
- Statut d'exécution : ouvert, en cours et terminé
- Adéquation et efficacité par période
- Rapport SCI et matrice des risques et contrôles disponibles sous forme d'analyses prêtes à l'emploi

Basé sur des **méthodes et normes reconnues**, de la modélisation des processus jusqu'au test de contrôle.
COSO Contrôle interneArt. 728a CONAS 890[BPMN 2.0](https://swissgrc.com/fr/bpm-software)Contrôles clésSéparation des tâches
Preuves et audit## L'existence est obligatoire.
L'efficacité est rentable.
Lors d'un audit légal, l'organe de révision vérifie l'existence d'un SCI (art. 728a al. 1 ch. 3 CO, NAS 890). Prouver l'efficacité au-delà de cela raccourcit l'audit et produit des informations sur lesquelles vous pouvez piloter.
Preuves conservées sur le contrôle
Les enregistrements, horodatages, responsabilités et historique sont produits pendant l'exécution. La documentation du SCI est prête à être présentée à tout moment.
Existence prouvée, efficacité testée
La conception et l'exécution du contrôle sont documentées, le walkthrough et le résultat du test figurent sur le contrôle. Vous êtes prêt pour des audits d'efficacité volontaires.
Constats et actions
Les déficiences sont évaluées, assorties d'un responsable et d'une échéance, et suivies jusqu'à leur clôture. Rien ne reste en attente sur une liste.
Gestion documentaire
Documentation des processus, directives et manuels versionnés, révisés et validés, référencés depuis le processus et depuis le contrôle.
Un seul ensemble de contrôles, plusieurs disciplines
Les mêmes processus et contrôles alimentent le SCI, l'audit interne et la gestion des risques. Maintenez une fois, utilisez plusieurs fois.
[Modélisation des processus](https://swissgrc.com/fr/bpm-software)[Audit interne](https://swissgrc.com/fr/internal-audit-software)[Gestion des risques](https://swissgrc.com/fr/risk-management-software/)
Avantages et valeur ajoutée## Plus d'efficacité,
moins de pression en fin d'année
Complet et simple à la fois. C'est ce qui favorise l'adoption et fait progresser la maturité.
#### Processus, risque et contrôle connectés
Chaque contrôle est rattaché à l'étape du processus et au risque. Le lien peut être interrogé, pas reconstitué.
#### Fonctionnement continu plutôt qu'une course de fin d'année
Les contrôles sont distribués et confirmés automatiquement. L'efficacité se construit tout au long de l'année.
#### Prêt pour l'audit à tout moment
Les preuves sont produites pendant l'exécution. L'organe de révision trouve ce dont il a besoin sans semaines de relances.
#### Élément d'un système GRC connecté
Le SCI partage une base commune avec la gestion des risques, le SMSI, le PCA, la conformité et l'audit interne.
#### Responsables de contrôle impliqués au quotidien
Les workflows et rappels amènent le contrôle jusqu'au responsable, sans relances par e-mail.
#### Une maturité plus élevée grâce aux normes
Basé sur COSO : une approche cohérente et automatisée sur l'ensemble des processus et des unités.
Contact et démo## Découvrez notre solution SCI
en action
Lors d'une démonstration personnalisée, nous vous présentons la Plateforme SwissGRC® et vous montrons comment processus, risques, contrôles et preuves fonctionnent ensemble.
[Demander une démo](https://swissgrc.com/fr/demo)[Contacter les ventes](https://swissgrc.com/fr/sales)
---
### [Solution logicielle pour la gestion des risques liés aux tiers (TPRM)](https://swissgrc.com/fr/tprm-software/)
**Published:** juin 11, 2025
**Author:** Gent Krasniqi
**Content:**
Gestion des risques tiers# Vous connaissez vos tiers.
Connaissez-vous vos dépendances ?
Recensez vos fournisseurs et prestataires, classez-les par criticité, surveillez-les en continu et rapportez avec preuves à l'appui : Swiss GRC rend votre risque tiers maîtrisable. **Sur l'ensemble du cycle de vie**, de l'intégration à la sortie.
[Demander une démo](#contact) [Voir comment ça fonctionne](#how-it-works)
Ils nous font confiance
Ce qui compte## D'une liste de fournisseurs
à un portefeuille pilotable
Chaque organisation dispose d'un registre de contrats. Ce qui les distingue, c'est qu'il se transforme en une vue des risques qui reste valable aujourd'hui.
Le point de départ habituel### Contrats connus, risques estimés
Les prestataires se trouvent dans des tableurs, les questionnaires reviennent par courrier, les revues ont lieu au renouvellement du contrat. Qui dépend de qui ne se révèle qu'en cas de panne.
- Liste de fournisseurs dans des tableurs, services non attribués
- Questionnaires par courrier, réponses sans preuves
- Évaluation à l'entrée, aucune réévaluation par la suite
- Concentrations et sous-traitants invisibles
Avec la plateforme SwissGRC®### Un registre qui suit le rythme
Prestataires, services, contrats, risques et contrôles sont liés entre eux. Les évaluations ont des échéances, les signaux externes arrivent, les constats se transforment en actions.
- Prestataires et services liés dans un seul registre
- Évaluations avec workflow, échéance et preuves
- Surveillance continue plutôt qu'une photographie ponctuelle
- Externalisations critiques documentées à tout moment
Comment ça fonctionne## Cinq étapes,
une boucle fermée
De la première demande à l'action, puis retour vers l'évaluation suivante. Choisissez une étape.
01 Intégration Prestataires et services intégrés au registre 02 Évaluation Criticité et due diligence 03 Surveillance Signaux et échéances contrôlés en continu 04 Reporting Analyses pour le conseil et les autorités de surveillance 05 Actions et sortie Action, escalade, sortie
Continu, pas ponctuel
01*/05* Intégration et enregistrement *Phases*Cadrage*·*Identification*·*Classification de l'externalisation
### Chaque tiers enregistré, chaque service attribué
Fournisseurs, prestataires et leurs services entrent dans le registre via un parcours de demande guidé. La classification par catégorie de service, région et criticité se fait en chemin, pas des mois plus tard.
[Voir toutes les phases ](#phases)
1. Inventaire central des prestataires et services
2. Parcours de demande et d'approbation guidé
3. Cadrage et identification
4. Classification de l'externalisation
5. Lié aux contrats et responsables
6. Import des listes de fournisseurs existantes
02*/05* Évaluation et classification *Phases*Analyse des risques*·*Due diligence
### Du risque inhérent à une criticité démontrée
Sécurité, conformité, continuité d'activité et stabilité financière dans un seul jeu de questionnaires. Les réponses produisent un profil de risque par prestataire et par service, pas seulement par contrat.
[Voir toutes les phases ](#phases)
1. Analyse et évaluation des risques
2. Due diligence complète
3. Questionnaires avec auto-attestation du prestataire
4. Évaluation par service et par prestataire
5. Externalisations critiques identifiées
6. Lié aux risques et contrôles
03*/05* Surveillance continue *Phases*Surveillance*·*Gestion des contrats
### Le statut de risque ne vieillit pas
Signaux externes et échéances internes se rejoignent. Si la notation cyber, la situation en matière de sanctions ou la situation financière d'un prestataire évolue, le registre le signale de lui-même.
[Voir le filtrage ](#intelligence)
1. Revue continue du statut de risque
2. Sources de données externes connectées
3. Alertes en cas de changements critiques
4. Réévaluations récurrentes selon le niveau de risque
5. Conditions contractuelles et échéances suivies
6. Réévaluations planifiées et documentées
04*/05* Reporting automatisé *Phases*Reporting*·*Analyse
### Prêt pour l'audit sans semaine de préparation
Portefeuille, concentrations et externalisations critiques dans une seule analyse. Ce que les autorités de surveillance veulent voir est déjà réuni, pas encore à assembler.
[Découvrir le produit en détail ](#inside)
1. Tableaux de bord sur la performance et le risque
2. Analyses pour les autorités de surveillance et l'audit
3. Vue des concentrations et dépendances
4. Registre d'informations sur les externalisations critiques
5. Reporting par unité et par prestataire
6. Preuves avec date et personne
05*/05* Actions et sortie *Phases*Actions*·*Planification de la sortie et de la transition
### Les constats se transforment en action
Chaque constat donne lieu à une action avec un responsable et une échéance. Et lorsqu'une relation prend fin, la sortie est planifiée avant d'en avoir besoin.
[Demander une démo ](#contact)
1. Actions avec responsable et échéance
2. Attribution automatique des tâches
3. Escalade en cas de retard
4. Planification de la sortie et de la transition
5. Alternatives et dépendances documentées
6. Efficacité des actions démontrée
À l'intérieur du produit## Ce que vous voyez en premier
le matin
Aucun chemin de clics à travers des menus, trois vues qui répondent en quelques secondes à l'état de votre portefeuille de tiers.

01
#### Portefeuille en un coup d'œil
Nombre de prestataires critiques, répartition des classes de risque et revues en cours, agrégés sur l'ensemble du registre.
02
#### Des services, pas seulement des prestataires
Le registre montre quel service dépend de quel prestataire, et quel processus métier en dépend.
03
#### Criticité et conformité
Statut, criticité et notation de conformité côte à côte par service, filtrables par unité et région.
Connecté à des **sources de données externes** pour que les évaluations ne reposent pas uniquement sur l'auto-déclaration. Les signaux de ces sources alimentent la surveillance de vos tiers.
Analyse prédictive et aide à la décision basées sur l'IA.
Notation systématique de la posture de cybersécurité des prestataires.
Analyse et notation du risque cyber à partir de signaux externes.
Synesgy de CRIF, spécialisé dans les notations ESG des entreprises.
Le cycle de vie en détail## Neuf phases,
neuf résultats démontrés
Les cinq étapes se décomposent en neuf phases. Chacune a un responsable, une échéance et un résultat qui peut être présenté à un auditeur.
Étape 1 . phases 01 à 03
Prise en charge et cadrage
Qui entre seulement en ligne de compte ?
1. #### Inventaire des tiers et des services
Fournisseurs, prestataires et leurs services enregistrés de manière centralisée et liés aux responsables, contrats et risques associés.
*Résultat***Registre des prestataires et services**, exploitable à tout moment pour le reporting
2. #### Cadrage et identification
Définissez le périmètre de la gestion des risques tiers et identifiez les prestataires et services concernés.
*Résultat***Périmètre documenté** avec justification
3. #### Classification de l'externalisation
Catégorisez les externalisations et distinguez celles qui sont significatives de celles qui ne le sont pas, selon des critères documentés.
*Résultat***Évaluation de la matérialité** par externalisation
Étape 2 . phases 04 à 06
Évaluation et contrat
Quelle est l'ampleur réelle du risque ?
1. #### Analyse et évaluation des risques
Déterminez le profil de risque par prestataire et par service, inhérent et après effet des contrôles convenus.
*Résultat***Profil de risque brut et net** par service
2. #### Due diligence complète
Examinez les pratiques commerciales, la conformité et les normes de sécurité de vos prestataires, avec questionnaire, preuves et approbation.
*Résultat***Dossier de due diligence** avec preuves
3. #### Gestion des contrats
Surveillez les conditions contractuelles, les délais de résiliation et les obligations convenues, et détectez les lacunes tôt.
*Résultat***Vue d'ensemble des contrats** avec échéances et obligations
Étape 3 . phases 07 à 09
Exploitation et résiliation
Cela reste-t-il maîtrisé ?
1. #### Surveillance continue
Maintenez le statut de risque à jour, intégrez les signaux externes et réagissez aux écarts plutôt qu'au renouvellement.
*Résultat***Statut de risque actuel** et les alertes qu'il a déclenchées
2. #### Reporting et analyse
Performance et risque des prestataires dans des tableaux de bord, adaptés à l'unité, à l'audit interne et au conseil d'administration.
*Résultat***Rapport pour le conseil et les autorités de surveillance** à la demande
3. #### Planification de la sortie et de la transition
Planifiez les sorties de manière structurée, documentez les alternatives et effectuez les transitions sans interrompre les processus.
*Résultat***Plan de sortie** avec étapes de transition et alternatives
Construit sur les **attentes réglementaires en matière d'externalisation**, du test de matérialité jusqu'à la preuve.
DORA art. 28 à 30 Circ. FINMA 2018/3 Lignes directrices EBA ISO/IEC 27036
Third-Party Intelligence CenterFiltrage propulsé par l'IA pour l'ensemble de votre registre
Une couverture large, une profondeur ciblée : l'Intelligence Center filtre chaque tiers pour les sanctions, les PPE et les médias négatifs, et n'escalade vers une due diligence plus poussée que lorsqu'un signal le justifie.
**Niveau 1**Analyse rapide **Niveau 2**Douze catégories de risque **Niveau 3**Réseau et quatrièmes parties
[Découvrir l'Intelligence Center](https://swissgrc.com/fr/third-party-intelligence/)
Qui en profite## Pour qui notre module TPRM
fait la différence
Le risque lié aux tiers concerne plusieurs fonctions à la fois. Chaque rôle dispose de sa propre vue, tous travaillent sur le même registre et ne posent la même question qu'une seule fois.
#### Conformité
Surveillez les sanctions et les exigences anti-corruption par prestataire et évitez les relations d'affaires à risque avant qu'elles ne débutent.
#### ESG
Intégrez les critères environnementaux, sociaux et de gouvernance dans l'évaluation des fournisseurs et suivez les évolutions via des sources externes.
#### Achats et gestion des fournisseurs
Accélérez l'intégration des nouveaux fournisseurs grâce à une évaluation des risques et surveillez les fournisseurs existants pour détecter les changements qui touchent la chaîne d'approvisionnement.
#### Cybersécurité et protection des données
Vérifiez la posture de sécurité des prestataires TIC par rapport à vos exigences, repérez les faiblesses et contrôlez les flux de données vers les tiers.
#### Résilience opérationnelle
Évaluez le risque tiers pesant sur les fonctions critiques et démontrez que les prestataires critiques disposent de plans de continuité opérationnels.
#### Audit interne et conseil d'administration
Consultez les externalisations critiques, les concentrations et les constats ouverts sans analyse spéciale, toujours sur le même statut.
Avantages et bénéfices## Moins d'effort par prestataire,
plus de vue d'ensemble sur tous
Le module retire du processus le travail récurrent et vous laisse le jugement.
- **Les tiers critiques repérés tôt**La matérialité et la criticité découlent de la classification, pas d'un ressenti isolé dans chaque unité.
- **Des évaluations sans échanges de courriels**Les questionnaires se déroulent en workflow, avec rappels, escalade et réponse documentée, au lieu de pièces jointes dans une boîte mail.
- **Une surveillance plutôt qu'une photographie ponctuelle**Des réévaluations récurrentes selon le niveau de risque et des signaux issus de sources externes maintiennent le statut à jour.
- **Les dépendances deviennent visibles**Les concentrations sur un seul prestataire, une région ou des sous-traitants apparaissent dans le portefeuille, pas dans l'incident.
- **Des preuves à la demande**L'évaluation, l'approbation et la revue sont enregistrées avec date, personne et preuves, et produites en quelques minutes.
- **Un seul processus pour chaque fonction**Conformité, achats, sécurité et résilience travaillent sur le même registre sans jamais poser deux fois la même question.
Contact et démo## Nous vous montrons
le module TPRM en direct
Lors d'une démo personnalisée, nous vous présentons l'ensemble du cycle de vie : intégration, classification, due diligence, surveillance, reporting et sortie. Sur un exemple concret de bout en bout, sans aucune préparation nécessaire de votre part.
[Demander une démo](https://swissgrc.com/fr/demo) [Contacter les ventes](https://swissgrc.com/fr/sales)
---
### [Gestion de la sécurité de l'information / Logiciel SMSI](https://swissgrc.com/fr/information-security-management-isms-software/)
**Published:** février 23, 2023
**Author:** superadmin
**Content:**
Sécurité de l'information (ISMS)# Sécurisé sur le papier.
Et quand ça compte vraiment ?
Élevez votre niveau de sécurité, renforcez votre résilience cyber.
**Actifs, contrôles, risques et preuves connectés**, pour ISO 27001, NIS2 et DORA.
[Demander une démo](https://swissgrc.com/fr/information-security-management-isms-software/#contact)[Découvrir les fonctionnalités](https://swissgrc.com/fr/information-security-management-isms-software/#features)
Impact d'un incident de sécuritéFonctionnement normalIncident de sécuritéavec un ISMS connectéavec des systèmes séparésImpact d'un incident de sécuritéFonctionnement normalIncident de sécuritéavec un ISMS connectéavec des systèmes séparés
Ils nous font confiance
Ce qui fait la différence## D'un ISMS documenté
à un ISMS efficace
Les politiques, les inventaires d'actifs et les catalogues de contrôles existent dans la plupart des organisations. Ce qui les distingue, c'est le fait qu'ils soient connectés.
Le point de départ habituel### Un ISMS qui ne vit que pour l'auditeur
Les actifs dans Excel, les contrôles dans un catalogue Word, les risques sur une liste séparée. Le lien n'est établi que pendant l'audit, manuellement.
- Actifs, contrôles et risques sur des listes séparées
- Les preuves sont rassemblées juste avant l'audit
- Chaque norme est cartographiée et maintenue séparément
- Les dérogations expirent sans que personne ne s'en aperçoive
Avec la plateforme SwissGRC®### Un ISMS qui fonctionne au quotidien
Les besoins de protection, les contrôles, les risques, les incidents et les actions restent liés à l'actif. Les preuves s'accumulent en continu dans le processus, pas lors d'un sprint final.
- Besoins de protection et contrôles liés à l'actif
- Les preuves s'accumulent en continu, l'ISMS reste prêt pour l'audit
- Un seul ensemble de contrôles pour ISO 27001, NIS2, DORA et plus
- Dérogations, échéances et actions surveillées automatiquement
La plateforme SwissGRC® en un coup d'œil## Tout votre ISMS,
en un seul endroit
Saisissez, évaluez, traitez, surveillez et rapportez. Parcourez les six vues.
01 Actifs et besoins de protection02 Hiérarchie des actifs03 Évaluation des contrôles04 Risques et actions05 Incidents et vulnérabilités06 Reporting ISMS
Analyse des besoins de protection### Chaque actif avec son besoin de protection
Processus, informations, systèmes et applications dans un seul inventaire. La confidentialité, l'intégrité et la disponibilité sont évaluées, **et le besoin de protection en découle**.
- Inventaire complet des actifs avec responsabilité claire
- Besoin de protection dérivé de la confidentialité, l'intégrité et la disponibilité
- Intégration avec SNOW, LeanIX et d'autres sources
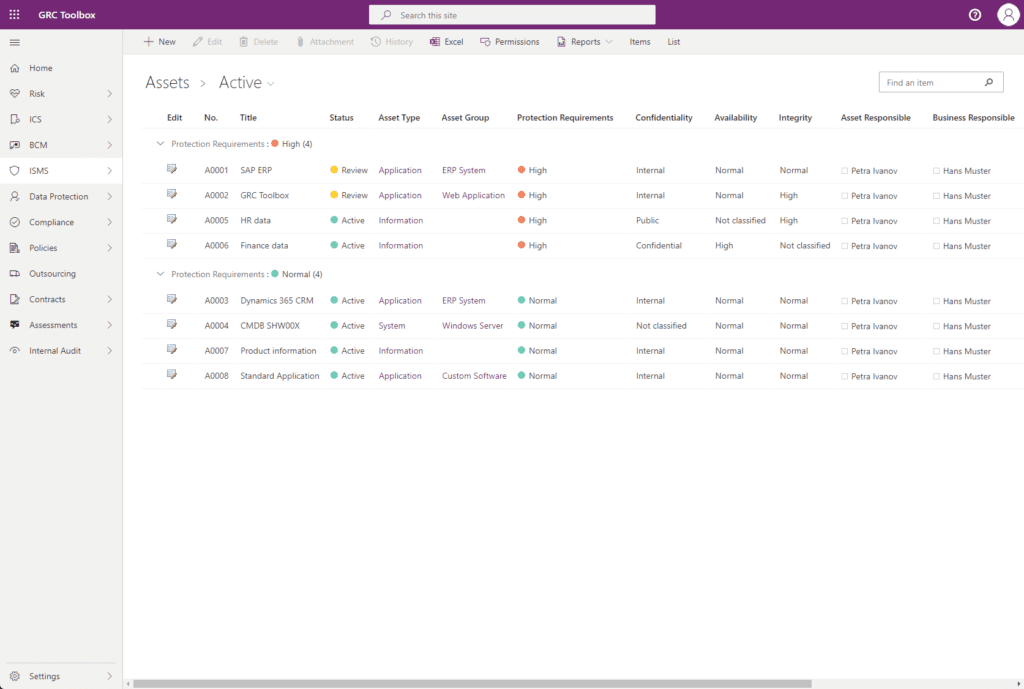
Dépendances### Voyez ce qui dépend de quel actif
Retracez les liens entre processus, informations, systèmes et applications et identifiez **comment un seul changement se répercute**.
- Dépendances sous forme de graphe plutôt que de tableau
- Besoins de protection traçables tout au long de la chaîne
- Points de défaillance uniques et goulots d'étranglement détectés tôt
Évaluation des contrôles### Statut de mise en œuvre par contrôle, avec preuves
Des questionnaires et des workflows déterminent le statut de mise en œuvre de chaque contrôle, avec dossier de preuves, responsable et échéance. **La couverture devient visible**.
- Évaluations pour ISO 27001, IT-Grundschutz et plus
- Preuves jointes directement au contrôle
- Les écarts génèrent des actions ou des dérogations documentées
Gestion des risques selon ISO 27005### Risques évalués, actions suivies
Saisissez, analysez, évaluez et priorisez les risques liés à la sécurité de l'information. Le traitement se déroule **via des workflows avec des responsables et des échéances clairs**.
- Matrice des risques et tableaux de bord par unité organisationnelle
- Actions avec responsable, échéance et avancement
- Liées aux actifs, contrôles et incidents

Gestion des incidents et vulnérabilités### De l'événement à la cause, et retour
Les événements de sécurité, incidents et vulnérabilités sont saisis et évalués de manière centralisée, avec **l'intégralité de la chaîne de cause à effet** jusqu'à l'actif concerné.
- Tableau de bord des incidents par gravité et dans le temps
- Vulnérabilités liées à la source, à l'actif et au risque
- Traitement suivi via des workflows
Reporting### Posture de sécurité communiquée au bon public
Actifs, statut des contrôles, résultats d'audit et risques dans un seul tableau de bord. **Une vue unique sur laquelle la direction et l'auditeur peuvent s'appuyer**.
- Statut des contrôles et couverture par norme
- Risques, incidents et constats côte à côte
- Rapports personnalisés pour chaque comité
Construit sur des **normes et référentiels reconnus**, un seul ensemble de contrôles pour toutes les obligations de preuve.
ISO/IEC 27001:2022ISO/IEC 27005[NIS2](https://swissgrc.com/fr/nis2/)[DORA](https://swissgrc.com/fr/dora/)NIST CSFBSI IT-GrundschutzCIS ControlsPCI-DSS
Audit et preuve## De la déclaration d'applicabilité
à une preuve solide
La certification n'est pas un projet, c'est un cycle. La plateforme l'accompagne, de la politique jusqu'à la revue de direction.
Support à la certification
Exigences normatives et contrôles de l'Annexe A couverts. La déclaration d'applicabilité est produite avec justification et référence à la politique correspondante.
Audit interne
Planifiez les audits, menez-les via des évaluations, documentez les constats et les actions d'amélioration, et suivez-les jusqu'à leur clôture.
Gestion des politiques
Gestion documentaire intégrée avec versioning, workflow de révision et d'approbation, ainsi qu'un rappel planifié pour vérifier que les politiques restent actuelles et adaptées.
Gestion des dérogations
Évaluez, approuvez et limitez dans le temps les dérogations aux exigences de sécurité. La plateforme surveille les échéances et signale l'expiration avant qu'elle ne devienne un risque.
Nouvelles obligations de preuve
NIS2 et DORA exigent des preuves qui vont au-delà de la certification. Les deux s'appuient sur la même base de contrôles.
[NIS2](https://swissgrc.com/fr/nis2/)[DORA](https://swissgrc.com/fr/dora/)[Normes et référentiels](https://swissgrc.com/fr/standards-frameworks)
Avantages et valeur ajoutée## Plus d'efficacité,
moins d'effort
Complet et simple à la fois. C'est ce qui favorise l'adoption et élève la maturité.
#### Tout est connecté à l'actif
Besoins de protection, contrôles, risques, incidents et actions sont tous rattachés à l'actif. Le lien peut être consulté, pas reconstitué.
#### Un seul ensemble de contrôles, plusieurs normes
Évaluez une fois, documentez plusieurs fois : ISO 27001, NIS2, DORA, NIST CSF, IT-Grundschutz et CIS sur la même base.
#### Prêt pour l'audit à tout moment
Les preuves s'accumulent en continu dans le processus. Les audits internes et externes cessent d'être des événements exceptionnels.
#### Partie intégrante d'un système GRC connecté
La sécurité de l'information partage une base commune avec le SCI, la gestion des risques, le BCM, la protection des données et le TPRM.
#### Une culture de la sécurité renforcée
Les workflows impliquent les responsables des actifs et des processus dans leur travail quotidien, pas seulement une fois par an.
#### Une maturité accrue grâce aux normes
Standardisé selon ISO/IEC 27001 et 27005 : une approche cohérente et automatisée dans toute l'organisation.
Contact et démo## Découvrez notre solution
ISMS en action
Lors d'une démo personnalisée, nous vous présentons la plateforme SwissGRC® et vous montrons comment actifs, contrôles, risques et preuves fonctionnent ensemble.
[Demander une démo](https://swissgrc.com/fr/demo)[Contacter les ventes](https://swissgrc.com/fr/sales)
---
### [Quantification des risques au service des décisions du conseil d'administration](https://swissgrc.com/fr/risk-quantification/)
**Published:** juin 11, 2026
**Author:** superadmin
**Content:**
# L’incertitude devient une décision.
RiskQuant calcule jusqu'à 100'000 scénarios à partir de votre registre des risques, les agrège en une distribution des pertes et les confronte à la capacité de prise de risque de votre entreprise.
[Contactez-nous](#demo) [Voir le Board Risk Reporting](#brr)
Incident cyber *Log-normale* Personnel clé *PERT* Défaillance technologique *Gamma* Risque de change *Triangulaire*
Distribution des pertes agrégée, corrélée par copule n = 0
Perte attendue
CHF0
Année rare (P95)
CHF0
Capacité de prise de risque
CHF9'004'940
Capacité utilisée
0%
Ils nous font confiance
Pourquoi maintenant## Des estimations aux preuves
En Suisse comme dans le reste de l’Europe, les attentes en matière de gestion des risques évoluent : on s’éloigne des évaluations isolées pour aller vers une vue connectée qui capture les dépendances et l’exposition agrégée.
**Vos évaluations existantes portent déjà l’expertise nécessaire.** Il ne manque que le moteur qui transforme fréquence et gravité en un chiffre solide, et la traduction qui en fait une décision pour le conseil d’administration.
C’est exactement ce qu’est RiskQuant : une quantification prête pour la production, associée à un reporting pour le conseil d’administration qui répond à la bonne question.
#### Du faible/moyen/élevé à une fourchette
Au lieu de trois niveaux, toute l’étendue des résultats possibles, chaque risque avec sa distribution correspondante.
Log-normaleGammaPERTTriangulaireWeibull
#### Des dépendances plutôt que des risques isolés
La corrélation basée sur les copules montre ce qui se passe lorsque plusieurs pertes surviennent simultanément.
CopuleMatrice de corrélationStress
#### Aucun nouveau modèle, aucune double maintenance
RiskQuant calcule directement à partir des données déjà présentes dans votre registre des risques.
jusqu'à 100k en < 500 msVaRCVaR
Ce qui distingue RiskQuant## Board Risk Reporting : un chiffre devient une décision
Un conseil d’administration décide du budget, des réserves, de l’assurance et du risque résiduel qu’il assume consciemment. RiskQuant traduit la simulation exactement dans ce langage. Cinq vues, une seule simulation continue.
Vue d’ensemble . Résumé de direction### Une conclusion en deux phrases, pas un graphique
La page destinée au conseil d’administration commence par une conclusion claire plutôt que par un histogramme : perte attendue de CHF 3,38 M, dans 95 % des scénarios inférieure à CHF 6,19 M, dans le pire un pour cent supérieure à CHF 7,61 M. Les statistiques sont là, mais elles ne s’imposent pas.
Juste en dessous, les trois leviers du conseil sous forme de **points clés pour le conseil d’administration** : réserve, assurance et risque résiduel assumé consciemment, chacun avec un montant concret en francs.
*RiskQuant . Vue d’ensemble*

Solvabilité et capacité### Le risque face à la capacité
Le risque agrégé face à la capacité de prise de risque, avec un montant concret en francs plutôt qu’une couleur de feu tricolore. Le risque agrégé utilise 69 % de la capacité, avec une marge de CHF 2'814'940. La position reste clairement dans la capacité, la probabilité d’insolvabilité est inférieure à 1 % (environ 1 fois tous les 417 ans).
Le vrai message pour le conseil d’administration, c’est la tendance : **la valeur à risque augmente.** Supportable aujourd’hui, à surveiller demain.
*RiskQuant . Solvabilité et capacité*

Facteurs de risque### Trois risques expliquent les deux tiers
Tous les risques n’ont pas le même poids. La simulation montre d’où vient réellement la perte attendue, triée par contribution. Les trois principaux facteurs représentent ensemble 68 %. C’est précisément là que se porte en premier l’attention du conseil.
- Défaillance technologique, environ 23 %
- Perte de personnel clé, environ 23 %
- Incident cyber, environ 22 %
- Risque de queue et atténuation visibles par facteur
*RiskQuant . Facteurs de risque*

Réseau de dépendances### Les risques n’évoluent pas isolément
Les pertes surviennent rarement de manière isolée. RiskQuant modélise, à l’aide de copules, quels risques évoluent ensemble et lesquels évoluent en sens opposé. Des évaluations isolées deviennent une vue connectée, la base de toute agrégation robuste.
*RiskQuant . Réseau de dépendances*

Journal des décisions### La décision fait partie du rapport
La décision, sa justification et les mesures qui en découlent sont enregistrées directement sur la même simulation. Dans l’exemple, acceptée dans les limites de l’appétit pour le risque, avec une mesure et une échéance, prochaine revue le trimestre suivant. Lors de la prochaine simulation, vous voyez non seulement les nouveaux chiffres, mais aussi ce qui a été décidé la dernière fois et si cela a fonctionné.
Cela transforme le reporting en une **piste de gouvernance traçable et auditable**.
*RiskQuant . Journal des décisions*

Cœur quantitatif## Conçu pour la quantification des risques en entreprise
Tout ce qu’il faut pour passer des évaluations qualitatives à une simulation de Monte Carlo prête pour la production. Puissant en coulisses, clair et traçable dans le reporting au conseil d’administration. Le même moteur réinjecte aussi les facteurs dans votre cartographie des risques habituelle, la heatmap servant de test de cohérence.
#### Plus de 15 distributions
Normale, log-normale, PERT, Gamma, Weibull, triangulaire, Poisson et bien d’autres, y compris des distributions composées pour la fréquence et la gravité.
#### Schémas de dépendance
Modélisez si les risques restent indépendants, évoluent ensemble sous stress, ou surviennent simultanément dans les scénarios extrêmes.
#### jusqu’à 100k simulations en < 500 ms
Moteur vectorisé, conçu pour la rapidité. Simulations complètes du portefeuille en temps réel, pas en traitement de nuit.
#### Test de résistance
Identifiez les risques qui déterminent les scénarios extrêmes. Analyses de contribution au-delà d’un seuil de stress librement paramétrable.
#### Valeur attendue, VaR et CVaR
Perte attendue, Value at Risk et VaR conditionnelle, traduites en réserve, transfert et risque résiduel assumé consciemment.
#### Piste auditable
Chaque simulation, chaque hypothèse et chaque décision reste traçable. Une gouvernance là où les décisions sont prises.
Moteur quantitatif de notre partenaire [ ](https://volatilis.org)
Contact et démo## Parlez à notre équipe risques
Montrez-nous votre registre des risques, et nous vous montrerons comment RiskQuant le transforme en base de décision pour votre conseil d’administration. En direct, sur vos propres hypothèses.
- Personnalisé, adapté à votre registre des risques
- Un aperçu de la simulation, de la capacité et du reporting au conseil d’administration
- Des réponses d’experts, pas un argumentaire commercial
Vous préférez discuter directement ? [Réservez un Discovery Call](https://swissgrc.com/discoverycall) ou
Envoyer la demande
Nous vous répondrons sous un jour ouvré.
Prénom \*
Nom \*
E-mail professionnel \*
Entreprise \*
Fonction \*Veuillez sélectionner\*Gestion des risques / ERMConformité / GouvernanceAudit interne / AuditFinance / Fonction CFOActuariat / AssuranceDirection générale / Conseil d'administrationAutre
Pays \*Veuillez sélectionner\*SuisseAllemagneAutricheAfghanistanAlbanieAlgérieAndorreAngolaAntigua-et-BarbudaArgentineArménieAustralieAzerbaïdjanBahamasBahreïnBangladeshBarbadeBiélorussieBelgiqueBelizeBéninBhoutanBolivieBosnie-HerzégovineBotswanaBrésilBruneiBulgarieBurkina FasoBurundiCap-VertCambodgeCamerounCanadaRépublique centrafricaineTchadChiliChineColombieComoresCongo (République démocratique)Congo (République)Costa RicaCôte d'IvoireCroatieCubaChypreTchéquieDanemarkDjiboutiDominiqueRépublique dominicaineÉquateurÉgypteSalvadorGuinée équatorialeÉrythréeEstonieEswatiniÉthiopieFidjiFinlandeFranceGabonGambieGéorgieGhanaGrèceGrenadeGuatemalaGuinéeGuinée-BissauGuyanaHaïtiHondurasHongrieIslandeIndeIndonésieIranIrakIrlandeIsraëlItalieJamaïqueJaponJordanieKazakhstanKenyaKiribatiKosovoKoweïtKirghizistanLaosLettonieLibanLesothoLiberiaLibyeLiechtensteinLituanieLuxembourgMadagascarMalawiMalaisieMaldivesMaliMalteÎles MarshallMauritanieMauriceMexiqueMicronésieMoldavieMonacoMongolieMonténégroMarocMozambiqueMyanmarNamibieNauruNépalPays-BasNouvelle-ZélandeNicaraguaNigerNigeriaCorée du NordMacédoine du NordNorvègeOmanPakistanPalaosPanamaPapouasie-Nouvelle-GuinéeParaguayPérouPhilippinesPolognePortugalQatarRoumanieRussieRwandaSaint-Christophe-et-NiévèsSainte-LucieSaint-Vincent-et-les-GrenadinesSamoaSaint-MarinSao Tomé-et-PrincipeArabie saouditeSénégalSerbieSeychellesSierra LeoneSingapourSlovaquieSlovénieÎles SalomonSomalieAfrique du SudCorée du SudSoudan du SudEspagneSri LankaSoudanSurinameSuèdeSyrieTadjikistanTanzanieThaïlandeTimor orientalTogoTongaTrinité-et-TobagoTunisieTurquieTurkménistanTuvaluOugandaUkraineÉmirats arabes unisRoyaume-UniÉtats-UnisUruguayOuzbékistanVanuatuCité du VaticanVenezuelaViêt NamYémenZambieZimbabwe
Votre demande \*Veuillez sélectionner\*Réserver une démonstrationPlanifier un appel de découverteDemander un tarif / un devisÉvaluer RiskQuantDiscuter d'un partenariatAutre
Votre message
J'accepte la [Politique de confidentialité](https://swissgrc.com/fr/privacy-policy/).
---
### [Logiciel de gestion des risques](https://swissgrc.com/fr/risk-management-software/)
**Published:** novembre 28, 2022
**Author:** superadmin
**Content:**
Gestion des risques# Réagissez-vous face aux risques,
ou les pilotez-vous ?
Identifiez, évaluez, quantifiez et rapportez au conseil d’administration : Swiss GRC rend votre gestion des risques prête pour la décision.
Qualitative et quantitative.
[Demander une démo](#contact) [Découvrir les fonctionnalités](#features)
◀ Risque à la baisse Atténuation ▶ Scénario de base Panne technologique -1.9M +1.2M Incident cyber -1.6M +1.3M Personnel clé -1.5M +0.9M Chaîne d’approvisionnement -0.9M +0.7M Fraude et conformité -0.5M +0.8M Risque de change -0.7M +0.4M ◀ Baisse Atténuation ▶ Scénario de base Panne technologique -1.9M +1.2M Incident cyber -1.6M +1.3M Personnel clé -1.5M +0.9M Chaîne d’approvisionnement -0.9M +0.7M Fraude et conformité -0.5M +0.8M Risque de change -0.7M +0.4M
Ils nous font confiance
Ce qui fait la différence## Du registre des risques
au pilotage efficace
Les registres, les évaluations et les contrôles existent depuis longtemps. Ce qui distingue les organisations, c’est la manière dont ils fonctionnent ensemble.
Le point de départ habituel### Des éléments solides, mais des systèmes séparés
Lorsque les risques, les contrôles et les événements vivent dans des outils séparés, la vue d’ensemble arrive tardivement et doit être assemblée manuellement.
- Risques, contrôles et incidents dans des outils séparés
- La vue d’ensemble est assemblée manuellement dans le reporting
- Les dépendances sont difficiles à tracer
- L’actualité des données dépend des personnes
Avec la plateforme SwissGRC®### Des risques connectés et maîtrisés
Les risques restent liés aux contrôles, aux événements et aux actions, pour tous les types de risques, à l’échelle de l’entreprise ou par domaine. Une vue cohérente à tout moment, chaque décision étayée par des preuves.
- Identification, évaluation et reporting en un seul endroit
- Contrôles et incidents liés directement au risque
- Intégré avec le SCI, la conformité, la sécurité et le BCM
- La simulation rend les évaluations solides face au conseil d’administration
La plateforme SwissGRC® en un coup d’œil## Toute votre gestion des risques,
en un seul endroit
Identifiez, évaluez, surveillez, traitez et rapportez. Parcourez les cinq vues.
01 Vue d’ensemble des risques 02 Évaluation des risques 03 Gestion des incidents 04 Actions 05 Reporting des risques
Inventaire des risques### Tous les risques en vue, classés systématiquement
Tous les types de risques dans une seule structure : statut, catégorie, notation brute et nette, et risques principaux côte à côte, **prêts à être priorisés**.
- Inventaire complet des risques en un seul endroit
- Notation brute et nette en un coup d’œil
- Filtrez librement par catégorie et statut

Évaluation des risques et des contrôles### Évaluez les risques et les contrôles de manière structurée
Évaluez de manière qualitative ou quantitative. L’auto-évaluation et les tests de contrôle démontrent **l’efficacité des contrôles**, en brut et en net, dans une seule matrice.
- Matrice des risques avec valeurs brute, nette et ESG
- Auto-évaluation des risques et contrôles (RCSA) et tests de contrôle
- Critères d’évaluation définissables librement

Gestion des événements et incidents### Incidents et pertes rattachés directement au risque
Enregistrez les événements et les données de pertes (loss events) directement sur le risque concerné, avec l’intégralité de la **chaîne de cause à effet** et les actions qui en découlent.
- Tableau de bord des incidents par gravité
- Évolution dans le temps visualisée
- Cause et effet reliés de bout en bout

Traitement des risques### Des actions avec un responsable et une échéance clairs
Chaque action a un responsable désigné et une échéance. La plateforme surveille l’avancement et les délais, **de l’attribution à la clôture**.
- Vue d’ensemble par statut et priorité
- Échéances et avancement en un coup d’œil
- Responsabilités claires grâce aux workflows

Reporting### Des risques communiqués au bon public
Une vue d’ensemble claire pour le conseil d’administration : **risque agrégé face à la capacité de prise de risque**, et si l’organisation reste dans son appétit pour le risque.
- Risque agrégé face à la capacité de prise de risque
- VaR 95 et utilisation de la capacité dans le temps
- Analyses prêtes pour le conseil d’administration

Basé sur des **méthodes et normes reconnues**, de l’évaluation qualitative à la simulation quantitative.
ISO 31000 COSO ERM Analyse Bow-tie qualitative et quantitative
Cœur quantitatif## De l’évaluation
à un chiffre défendable
Là où les notations qualitatives s’arrêtent, la plateforme continue de calculer : la probabilité et l’impact deviennent un chiffre solide.
Simulation de Monte Carlo
Des dizaines de milliers de scénarios par risque, avec la perte annuelle attendue ainsi que la VaR 95 et 99.
Agrégation des risques
De nombreux risques individuels condensés en une position globale, avec la contribution de chaque risque.
Un pas de plus
Le reporting des risques et la quantification complète sont couverts sur notre page dédiée RiskQuant.
[Découvrir RiskQuant](https://swissgrc.com/fr/risk-quantification/)
Avantages et valeur ajoutée## Plus de maîtrise,
de meilleures décisions
Complet et simple à la fois. C’est ce qui favorise l’adoption et élève la maturité.
#### Tous les risques de l’entreprise
Risques d’entreprise, risques opérationnels, risques informatiques et cyber ou conformité : tout dans une seule solution, à l’échelle de l’entreprise ou par domaine.
#### Partie intégrante d’un système GRC connecté
La gestion des risques partage une base commune avec vos disciplines connexes telles que le SCI, l’ISMS, le BCM, la conformité, la protection des données et le TPRM.
#### Risques et opportunités réunis
Bien plus que se protéger contre les risques : les opportunités sont également saisies, évaluées et exploitées de manière délibérée.
#### Une culture du risque renforcée
La bonne information entre les bonnes mains : les workflows impliquent les responsables directement dans leur travail quotidien.
#### Une maturité accrue grâce aux normes
Standardisé selon ISO 31000 et COSO ERM : une approche cohérente et automatisée dans toute l’organisation.
#### De meilleures décisions
Une vue claire et consolidée de la situation des risques, qualitative et quantitative, solide jusqu’au conseil d’administration.
Contact et démo## Découvrez la plateforme
appliquée à votre propre paysage de risques
Lors d’une démo personnalisée, nous vous présentons la plateforme à partir de vos propres sujets et questions.
[Demander une démo](https://swissgrc.com/fr/demo) [Contacter les ventes](https://swissgrc.com/fr/sales)
---
### [Logiciel BPM - Gestion des processus métier](https://swissgrc.com/fr/bpm-software/)
**Published:** janvier 30, 2024
**Author:** superadmin
**Content:**
[ Nouveau Logiciel BPM › ](#)# La gestion des processus
à un niveau supérieur
Un seul endroit pour tous vos processus métier : modélisés, documentés, gouvernés. Responsabilités, documents, applications informatiques, données, risques et contrôles. Reliés de bout en bout. Avec en plus une IA qui réfléchit avec vous.
[Contactez-nous](#demo) [Essayez par vous-même ](#prototyp)
Démo interactive### La démo en direct ne peut pas être intégrée pour le moment.
Un paramètre réseau ou de sécurité bloque peut-être l'intégration. Vous pouvez ouvrir la démo directement ou nous contacter.
[Contactez-nous](#demo) [Ouvrir dans un nouvel onglet ](#)
Réessayer
Adopté par des organisations leaders
Swiss GRC | Évaluation de maturité de la gestion des processus Bilan de maturitéOù en est votre gestion des processus ?
Auto-évaluation gratuite en 2 minutes, six dimensions, résultat instantané.
Démarrer l'évaluation →
Évaluation de maturité
## Où en est votre gestion des processus ?
Une auto-évaluation compacte sur cinq niveaux de maturité et six dimensions. En quelques minutes seulement, vous obtenez une vision claire de votre maturité actuelle et des prochaines étapes de développement.
La méthodologie s'appuie sur le **guide MINT sur la maturité de la gestion des processus** (modèle de maturité selon CMMI V2.0 et les six éléments centraux du Business Process Management de Rosemann et vom Brocke). Vous trouverez le guide complet ici : [Évaluation de la maturité MINT pour votre gestion des processus](https://mint-processes.hubspotpagebuilder.com/mint-reifegrad-assessment).
Dimension 1 sur 6
Retour Suivant
Votre maturité globale
0.0 / 5
Initial
Atteignable avec le Process Center Swiss GRC
#### Votre profil par dimension
Touchez une dimension pour voir l'état actuel et la prochaine étape.
#### De la maturité à l'action
Cette auto-évaluation constitue une première orientation. Lors d'une évaluation structurée, nous validons ce constat avec un regard extérieur, un benchmark sectoriel et une feuille de route priorisée avec des responsabilités claires.
[Réserver un premier entretien →](#demo) [Télécharger le guide MINT](https://mint-processes.hubspotpagebuilder.com/mint-reifegrad-assessment)
↺ Recommencer l'évaluation
La question décisive
## Vos processus sont-ils cartographiés ou pilotés ?
Cartographies de processus, descriptions, standards de modélisation, peut-être même un outil BPM : une grande partie est déjà en place. Mais une gestion des processus efficace ne commence véritablement que là où la documentation devient pilotage.
Simplement documenté
### Des processus en silos, statiques et déconnectés
La documentation est créée une fois puis devient obsolète. Dépendances, systèmes, responsabilités et risques restent invisibles ou vivent dans des outils séparés.
- Cartographie des processus déconnectée de la réalité
- Aucune transparence sur les dépendances critiques
- Risques et contrôles séparés du processus
- Les besoins d'action restent invisibles
Véritablement piloté
### Une gestion des processus vivante et intégrée
Les processus sont reliés aux activités, documents, responsabilités, interfaces, systèmes et données, et enrichis par la gouvernance, le risque et la conformité.
- Cartographie des processus, modélisation et profils de processus unifiés
- Dépendances envers les systèmes informatiques et les données rendues transparentes
- Risques et contrôles directement liés
- L'IA détecte les lacunes, les risques et les potentiels d'optimisation
Le logiciel BPM en un coup d'œil
## Tout pour une gestion des processus efficace
Cartographie des processus, modélisation BPMN, profils de processus, indicateurs et tâches, reliés aux risques, aux contrôles et à l'IA. Cliquez pour explorer.
01 Centre de processusVotre point d'entrée quotidien 02 Modélisation BPMNModélisez selon les standards BPMN 03 Profils de processusProfils de processus interactifs 04 Gestion documentaireGérez vos documents en contexte 05 Risques et contrôlesRisques et contrôles liés au processus 06 Tâches et pilotageDe la vue d'ensemble au pilotage quotidien 07 Tableau de bord et indicateursStatut, tendances et alertes en temps réel 08 Assistance IAAccélérez vos processus grâce à l'IA 09 Assistant d'importationMigrez vos processus, étape par étape
![]()
01 Centre de processusVotre point d'entrée quotidien 
L'écran d'accueil réunit les tâches à venir, les revues échues et les activités récentes. Chacun voit en un coup d'œil ce qu'il reste à faire.
- Vue personnelle des tâches échues
- Actions rapides : ouvrir un processus, en créer un, cartographie des processus
- Fil d'activité pour toute l'équipe
02 Modélisation BPMNModélisez selon les standards BPMN 
Modélisation BPMN 2.0 avec couloirs (swimlanes), sous-processus, validation et simulation, reliée aux responsabilités, risques et contrôles.
- BPMN 2.0 avec validation et simulation
- Versionnement et workflows de validation
- Risques et contrôles ancrés directement à chaque étape
03 Profils de processusProfils de processus interactifs 
Les profils de processus réunissent toutes les informations pertinentes sur un processus : responsabilités, classifications, évaluations de pertinence et indicateurs. Commentaires, tâches et revues permettent une collaboration directe dans le contexte du processus.
- Toutes les informations du processus au même endroit, faciles à modifier
- Commentaires et collaboration directement sur le processus
- Revues et validations traçables
- Classification par risque, conformité, protection des données et PCA
04 Gestion documentaireGérez vos documents en contexte 
La gestion documentaire intégrée et centrée sur l'utilisateur apporte le contenu pertinent là où il est nécessaire : directement dans le processus concerné. Les utilisateurs voient en un coup d'œil quels documents existent, leur statut et qui en est responsable.
- Instructions de travail, listes de contrôle et formulaires dans le contexte du processus
- Transparence sur le statut, les versions et les responsabilités
- Moins de temps passé à chercher, plus de certitude au quotidien
05 Risques et contrôlesRisques et contrôles liés au processus 
Les risques et les contrôles sont directement liés au processus concerné. Cela permet de voir où naissent les risques, quels contrôles s'appliquent et qui est responsable de leur mise en œuvre.
- Saisissez les risques dans le contexte du processus
- Reliez les contrôles directement aux processus
- Suivez les responsabilités et l'efficacité
- Une base pour l'ICS, la conformité et les audits
06 Tâches et pilotageDe la vue d'ensemble au pilotage quotidien 
Tâches à venir, revues et validations, regroupées par statut de processus. Les unités métier et les responsables de processus voient immédiatement les besoins d'action, les échéances et les responsabilités.
- Tâches par statut et type de processus
- Éléments en retard et échéances en un coup d'œil
- Gérez les revues et validations de façon structurée
07 Tableau de bord et indicateursStatut, tendances et alertes en temps réel 
Indicateurs sur les processus, le niveau de maturité, la couverture BPMN et le statut. Répartition par niveau, par statut et par responsable de processus, transparente et toujours à jour.
- Niveau de maturité et couverture BPMN par catégorie
- Répartition des statuts, du brouillon à la mise en production
- Analyse par niveau et par responsable
08 Assistance IAAccélérez vos processus grâce à l'IA 
L'IA analyse les documents existants, propose des processus et des modèles, et détecte les lacunes, les risques et les potentiels d'optimisation, le tout intégré dans une gouvernance auditable.
- Analyse les documents et propose des processus
- Détecte les lacunes, les dépendances et les risques
- Suggère des optimisations, intégrées au BPM et à la GRC
09 Assistant d'importationMigrez vos processus, étape par étape 
Le plus grand obstacle de tout projet BPM est la migration. L'assistant d'importation en fait un parcours guidé, étape par étape : votre documentation, vos structures et vos cartographies de processus existantes sont reprises et réutilisées plutôt que reconstruites de zéro.
- Import guidé, étape par étape, du contenu existant
- Le paysage de processus existant est réutilisé, pas recréé
- Validation et mise en correspondance tout au long du parcours
- Un chemin clair et à faible risque pour quitter vos outils actuels
Assistance IA
## Une IA qui accélère réellement le travail sur les processus
De l'analyse des documents existants à la génération de propositions de processus, en passant par l'identification des lacunes, des dépendances, des risques et des potentiels d'optimisation.
#### Analyser les documents
Les descriptions de processus existantes sont évaluées et reprises de façon structurée. Pas besoin de repartir de zéro.
#### Proposer des processus
L'IA génère des propositions de processus et des ébauches de modélisation comme point de départ pour vos unités métier.
#### Identifier les lacunes et dépendances
Les étapes manquantes, les dépendances envers les systèmes et les données, ainsi que les incohérences sont mises en évidence.
#### Détecter risques et contrôles
L'IA identifie les risques inhérents aux processus et les contrôles correspondants. La gouvernance là où elle naît.
#### Suggérer des optimisations
Les goulots d'étranglement et les potentiels d'optimisation sont identifiés, pour une amélioration continue.
#### Intégrée au BPM et à la GRC
Toutes les fonctionnalités d'IA opèrent dans une gouvernance auditable, connectées de façon transparente aux risques et aux contrôles.
Contact et démo
## Parlez à notre équipe BPM
Que ce soit pour une démo en direct, un appel de découverte, un devis concret ou un partenariat : dites-nous de quoi il s'agit. Un expert de notre équipe BPM vous contactera et répondra à votre question spécifique.
- Personnalisé, adapté à votre paysage de processus
- Un aperçu de la modélisation, du pilotage, des risques et de l'IA
- Des réponses de spécialistes, pas un argumentaire commercial
Vous préférez échanger directement ? [Réservez un appel découverte](https://swissgrc.com/fr/discoverycall) ou
Envoyer la demande
Nous vous répondons sous un jour ouvré.
Prénom \*
Nom \*
E-mail professionnel \*
Entreprise \*
Fonction \*Veuillez sélectionner\*Gestion des processus / Développement organisationnelGestion de la qualité / Excellence opérationnelleGestion des risques / SCIConformité / GouvernanceSécurité de l'informationDirection générale / Conseil d'administrationAutre
Pays \*Veuillez sélectionner\*SuisseAllemagneAutricheAfghanistanAlbanieAlgérieAndorreAngolaAntigua-et-BarbudaArgentineArménieAustralieAzerbaïdjanBahamasBahreïnBangladeshBarbadeBiélorussieBelgiqueBelizeBéninBhoutanBolivieBosnie-HerzégovineBotswanaBrésilBruneiBulgarieBurkina FasoBurundiCap-VertCambodgeCamerounCanadaRépublique centrafricaineTchadChiliChineColombieComoresCongo (République démocratique)Congo (République)Costa RicaCôte d'IvoireCroatieCubaChypreTchéquieDanemarkDjiboutiDominiqueRépublique dominicaineÉquateurÉgypteSalvadorGuinée équatorialeÉrythréeEstonieEswatiniÉthiopieFidjiFinlandeFranceGabonGambieGéorgieGhanaGrèceGrenadeGuatemalaGuinéeGuinée-BissauGuyanaHaïtiHondurasHongrieIslandeIndeIndonésieIranIrakIrlandeIsraëlItalieJamaïqueJaponJordanieKazakhstanKenyaKiribatiKosovoKoweïtKirghizistanLaosLettonieLibanLesothoLiberiaLibyeLiechtensteinLituanieLuxembourgMadagascarMalawiMalaisieMaldivesMaliMalteÎles MarshallMauritanieMauriceMexiqueMicronésieMoldavieMonacoMongolieMonténégroMarocMozambiqueMyanmarNamibieNauruNépalPays-BasNouvelle-ZélandeNicaraguaNigerNigeriaCorée du NordMacédoine du NordNorvègeOmanPakistanPalaosPanamaPapouasie-Nouvelle-GuinéeParaguayPérouPhilippinesPolognePortugalQatarRoumanieRussieRwandaSaint-Christophe-et-NiévèsSainte-LucieSaint-Vincent-et-les-GrenadinesSamoaSaint-MarinSao Tomé-et-PrincipeArabie saouditeSénégalSerbieSeychellesSierra LeoneSingapourSlovaquieSlovénieÎles SalomonSomalieAfrique du SudCorée du SudSoudan du SudEspagneSri LankaSoudanSurinameSuèdeSyrieTadjikistanTanzanieThaïlandeTimor orientalTogoTongaTrinité-et-TobagoTunisieTurquieTurkménistanTuvaluOugandaUkraineÉmirats arabes unisRoyaume-UniÉtats-UnisUruguayOuzbékistanVanuatuCité du VaticanVenezuelaViêt NamYémenZambieZimbabwe
Votre demande \*Veuillez sélectionner\*Réserver une démonstrationPlanifier un appel de découverteDemander un tarif / un devisÉvaluer la solutionDiscuter d'un partenariatAutre
Votre message
J'accepte la [Politique de confidentialité](https://swissgrc.com/fr/privacy-policy/).
---
### [Plateforme SwissGRC®](https://swissgrc.com/fr/platform/)
**Published:** juillet 2, 2026
**Author:** superadmin
**Content:**
La plateforme SwissGRC®# Une plateforme. *Toutes les disciplines GRC.*
Gouvernance, risque et conformité sur une seule plateforme, de la première analyse de risque jusqu'aux preuves prêtes pour l'audit. Configuration plutôt que programmation, disponible sur le web, triple certification ISO et utilisée par des organisations leaders dans le monde entier.
[Réserver une démo](#sgpdemo) [Découvrir les solutions](#sgpmodule)
0Utilisateurs de la
GRC Toolbox
0Clients de
tous secteurs
0Projets
réussis
[Plateforme](#sgpprinz) [Solutions](#sgpmodule) [Assistant IA](#sgpai) [Renseignement sur les tiers](#sgptpic) [Technologie](#sgptechnik) [Distinctions](#sgpawards) [Témoignages](#sgpvoices)
Pourquoi une seule plateforme## Une base de données commune plutôt que des outils dispersés
La plateforme SwissGRC® réunit toutes les disciplines GRC sur une seule plateforme. Elle évolue avec vos besoins, s'exploite dans le cloud ou sur site, et offre une vision cohérente sur l'ensemble de l'organisation.
01
### Une plateforme unique plutôt que des silos
Toutes les disciplines GRC sur une base de données commune. Une vision cohérente plutôt que des outils dispersés.
02
### Configuration plutôt que code
Des ajustements sans programmation complexe. La plateforme évolue avec vos besoins.
03
### Normes de sécurité élevées
Swiss Made Software, triple certification ISO et recommandée par les analystes du secteur.
04
### Opérationnel rapidement
Déploiement rapide, exploitation dans le cloud ou sur site, utilisateurs illimités par module.
Solutions## Vous décidez par où commencer.
Du risque à la protection des données en passant par l'audit : choisissez une solution et découvrez ce que la GRC lui apporte. La gestion des processus (BPM) et la gestion des contrats (CLM) complètent la plateforme.
Grace AI## Interrogez vos données GRC en langage naturel
L'assistant IA travaille directement sur votre base de données au sein de la plateforme SwissGRC®. Il résume les risques, identifie les mesures ouvertes et prépare des réponses.
Langage naturelSur vos donnéesRespecte les droits d'accèsSwiss Made Software
[Découvrir l'assistant IA →](/ai-assistant/)
Q
Quels risques majeurs n'ont pas de contrôle efficace ?
AI
Trois des douze risques majeurs n'ont actuellement pas de contrôle efficace. Deux concernent la chaîne d'approvisionnement, un concerne la sécurité informatique. Voulez-vous que je vous montre les mesures ?
Q
Oui, et préparez une courte note pour le conseil d'administration.
Centre de renseignement sur les tiers## Une surveillance continue de vos tiers, pas seulement une fois par an
Le centre de renseignement sur les tiers surveille en continu vos fournisseurs et prestataires. Les signaux externes sur la situation financière, la cybersécurité, les sanctions et la réputation alimentent directement votre gestion des risques tiers et déclenchent des mesures.
Surveillance continueCyber et financeSanctionsRéputation
[Découvrir Third-Party Intelligence →](/third-party-intelligence/)
Signaux tiersEn direct
Cyber
Stable
Finance
À surveiller
Sanctions
À examiner
Réputation
Stable
Technologie## Fonctionnalités techniques et interfaces
La plateforme SwissGRC® s'intègre dans votre paysage applicatif au lieu de le remplacer. Interfaces ouvertes, modèles de données standardisés et exploitation flexible.
### Fonctionnalités techniques
- Triple certification ISO (27001, 27017, 27701)
- Hébergement des données en Suisse (Microsoft Azure)
- Application web, cloud public ou sur site
- Moteur de workflow avec fonction d'alerte
- Générateur de rapports et de tableaux de bord
- Notifications pour les tâches et rappels
### Interfaces et intégration
- API REST ouverte pour votre paysage applicatif
- Intégration avec Microsoft Office
- Systèmes tiers via adaptateurs et connecteurs
- Authentification unique (SSO)
- Fonctions complètes d'import et d'export
- Modèles de données et référentiels standardisés
Distinctions## Reconnue de manière indépendante
Risk.net
#### GRC Product of the Year
Risk Technology Awards 2025
QKS Group
#### Leader, SPARK Matrix
GRC Platforms 2025
Forrester
#### GRC Platforms Landscape
T4 2025, seul fournisseur DACH
WirtschaftsWoche
#### Best of Technology 2025
Noté Excellent, TPRM
Certifications## Triple certification ISO
27001
**ISO 27001**SMSI, sécurité de l'information
27017
**ISO 27017**Cloud, sécurité du cloud
27701
**ISO 27701**Vie privée, protection des données
Témoignages## Pourquoi les décideurs font confiance à la GRC Toolbox
Témoignages de terrain de responsables risque, conformité et sécurité qui travaillent avec Swiss GRC.
“> En travaillant main dans la main avec l'équipe Swiss GRC, nous avons construit un système qui non seulement répond à nos objectifs de gouvernance, mais qui permet aussi à chaque filiale de s'approprier et d'améliorer ses processus de gestion des risques et de HSE. Cette initiative est devenue l'un des piliers de la transformation numérique de NEQSOL Holding.
**Samir Karimov**Responsable de la gestion des risques et du développement durableNEQSOL Holding
“
Grâce à la GRC Toolbox, la Mobilière a pu rendre ses évaluations des risques et des contrôles plus efficaces et les adapter aux exigences actuelles.
**Christian Grundt**Responsable du contrôle des risques et des affaires réglementairesLa Mobilière
“
La collaboration a été professionnelle et orientée solutions dès le départ. Nos besoins ont été pris au sérieux et mis en œuvre efficacement.
**Regula Schneider**Responsable du développement d'entreprise, membre de la direction généraleIB Langenthal AG
Démo personnalisée## Découvrez la plateforme SwissGRC® lors d'une démo personnalisée
Nous vous présentons la plateforme en fonction de vos cas d'usage, de la première analyse de risque jusqu'aux preuves prêtes pour l'audit.
[Réserver une démo](/fr/demo/) [Télécharger la fiche technique](https://swissgrc.com/wp-content/uploads/2026/07/SwissGRC_Platform_Factsheet_EN.pdf)
---
### [Third-Party Intelligence Center](https://swissgrc.com/fr/third-party-intelligence/)
**Published:** juin 16, 2026
**Author:** superadmin
**Content:**
Aperçu L'écart Essayer Le moteur Toujours actif Portefeuille Conseil d'administration Ce qui change Commencer
Third-Party Intelligence Filtrage propulsé par l'IA, par Swiss GRC# Filtrez tout le monde. Enquêtez sur ce qui compte.
Le Third-Party Intelligence Center filtre l'ensemble de votre registre et n'escalade vers une due diligence approfondie que lorsqu'un signal le justifie. Couverture complète, décisions défendables, aucun angle mort.
[Contactez-nous](#demo) [Voir en action](#try)
Filtrage du portefeuille, en directn = 20
Filtrés
0 / 20
Signaux critiques
0
Couverture
0%
Analyse médiane
~40s
Filtrage à travers des sources ouvertes et commerciales faisant autorité
OpenSanctionsOFACGLEIFSHABGDELTBundesanzeigerSecurityScorecardBitSight
Approuvé par des organisations de premier plan
L'écart de risque lié aux tiersVous ne pouvez pas approfondir *chaque tiers*. Alors, lesquels choisir ?
La plupart des programmes n'examinent en profondeur qu'une fraction de leurs tiers et acceptent le reste sur la base de la confiance. L'exposition qui apparaît lors d'un audit se situe presque toujours dans la partie que personne n'a examinée.
Filtrer plus intensément sur l'ensemble du portefeuille n'est pas viable à grande échelle. Ce qui l'est, c'est d'orienter l'examen là où le risque se situe réellement, et de documenter la décision.
Où va réellement l'examen
Tiers dans votre registre
des centaines
Évalués selon une norme significative
une fraction
Soumis à une due diligence approfondie
une poignée
Exposition qui vous touche réellement
inconnue
L'écart entre ce que vous pouvez vérifier et ce que vous devriez vérifier est là où se concentre le risque résiduel.
Démonstration interactive## Lequel laisseriez-vous passer ?
Six tiers. Chacun paraît irréprochable au vu de ses données de base. Choisissez les deux que vous examineriez en profondeur, puis filtrez les six.
Sélectionné **0 / 2** pour un examen approfondi
En attente de votre sélection Lancer le filtrage automatisé des six
Toutes les sociétés présentées sont des exemples fictifs basés sur des schémas de filtrage typiques. Toute ressemblance avec des sociétés réelles serait fortuite.
Le verdict
6
filtrés automatiquement
2
signaux critiques détectés
0
manqués, avec ou sans vous
[Testez-le sur votre propre registre](#demo) Réessayer
Le moteur de filtrage## Un nom en entrée, un verdict en sortie
Chaque tiers passe par un filtrage à paliers. L'IA n'escalade vers une due diligence approfondie qu'en cas de signal significatif, et chaque constat est sourcé, noté et auditable.
Niveau 1
Analyse rapide
Sanctions, PPE et médias négatifs, sur chaque tiers.
30 s à 3 min.
en cas de signal
Niveau 2
Standard
Douze catégories de risque, le profil OSINT complet.
~3 min.
si sérieux
Niveau 3
Analyse approfondie
Le réseau et les quatrièmes parties. Profondeur maximale.
~10 à 15 min.
Plus des modes dédiés à la cybersécurité et des modes personnalisés entièrement configurables, lorsque le périmètre est déjà défini.

Le verdict### Un verdict qui tient la route
DuLac Capital ressemble à un gérant de fortune suisse ordinaire. Une analyse rapide a détecté une correspondance de sanctions et a escaladé automatiquement vers une analyse approfondie, avant même qu'un analyste n'ouvre le dossier.
- Sanctionné, score de risque 100, quinze constats, dont trois critiques
- Correspondance de sanctions faisant autorité, distinguée des preuves notées
- Chaque constat sourcé, avec une chaîne de raisonnement complète et un dossier exportable
Toujours actif## Il n'attend jamais qu'on le lui demande
Un filtrage qui dépend de quelqu'un qui pense à le lancer n'est qu'une bonne intention. Le Center se déclenche de lui-même, à chaque moment où cela compte, sur des données dont l'origine est traçable.
À l'intégration
### Avant que la relation ne soit réelle
Filtré dès son entrée dans votre registre, pas après la signature du contrat.
Récurrent
### Selon une cadence définie par niveau
Vos tiers les plus critiques sont surveillés de plus près, les autres selon un rythme raisonnable.
Ponctuel
### Dès qu'un nom fait la une
Quand vous devez savoir immédiatement si vous êtes exposé, vous lancez le filtrage et vous savez.
Chaque constat remonte à une source faisant autorité
Sanctions et PPE
OFACOpenSanctions
Registres et entités
GLEIFSHABZefixBundesanzeiger
Médias et cyber
GDELTSecurityScorecardBitSight
Analytique du portefeuille## D'une liste à une carte
Une liste vous dit de qui vous dépendez, pas où vous êtes exposé. Chaque filtrage alimente l'analytique du portefeuille, où apparaissent des schémas qu'aucun dossier isolé ne révèle.
Classement du portefeuille### Chaque tiers, classé par risque
Une vue ordonnée de l'ensemble du registre. Les priorités sont explicites, pas enfouies à la ligne quatorze d'un tableur.
- Vingt tiers filtrés, couverture complète
- Deux au score de risque maximal
- Triés par score pondéré, avec accès direct aux preuves


Concentration### Une dépendance qu'aucun dossier isolé ne révèle
Chaque dossier fournisseur paraissait sain pris isolément. Le risque n'apparaît qu'une fois tous les filtrages réunis.
- Soixante pour cent du portefeuille dans une seule juridiction
- Mesuré par rapport à un seuil de trente pour cent
- Signalé automatiquement, avant de devenir un constat
Réseau### Les connexions entre les tiers
Un point de défaillance unique porte souvent plusieurs noms différents. Le Center les cartographie sous forme d'un réseau que vous pouvez réellement visualiser.
- Sociétés mères et bénéficiaires effectifs partagés
- Infrastructures, sites et aéroports partagés
- Dépendances cachées envers des quatrièmes parties mises en évidence

Reporting et surveillance## Conçu pour le conseil d'administration
Les analystes ont besoin de profondeur. Les conseils d'administration ont besoin d'une position. Le Center sert les deux à partir des mêmes données, et vous informe avant même que l'idée de demander ne vous vienne.

Reporting des risques### Une page unique que le conseil lira
Combien de tiers sont critiques, où va la tendance du risque et quels noms nécessitent une décision ce trimestre. Le détail reste à un clic.
- Tiers critiques et tendance du risque en un coup d'œil
- Les quelques noms qui nécessitent une décision maintenant
- Couverture complète, avec le détail à un clic
Conseiller IA### Un analyste qui vous informe en premier
Le Conseiller IA n'attend pas les questions. Il ouvre votre matinée avec ce qui a changé pendant la nuit, et montre son raisonnement.
- Interroge le portefeuille en direct et cite ses sources
- Fait remonter les nouveaux signalements critiques et les revues en retard
- Il conseille. Vous décidez.

Ce qui change réellement## Posez une meilleure question
Mêmes briques de base : sanctions, OSINT, notations cyber, concentration. Ce qui change, c'est la question à laquelle vous pouvez enfin répondre.
Avant
Ai-je filtré tout le monde de façon suffisamment approfondie ?
Aucune réponse réaliste, et aucune que vous puissiez pleinement justifier.
Maintenant
Ai-je examiné de près exactement là où cela comptait, et puis-je prouver pourquoi ?
Une réponse intégrée par conception, avec chaque étape traçable et documentée.
Commencer## Voyez-le avec vos propres données
Envoyez-nous un échantillon de votre registre. Nous exécuterons l'Intelligence Center sur vos propres tiers et vous guiderons à travers le filtrage, l'analytique du portefeuille et la vue destinée au conseil d'administration.
- Personnalisé, adapté à votre registre de tiers
- D'une analyse rapide à trente centimes à une cartographie complète du portefeuille
- Des réponses d'experts, pas un argumentaire commercial
Vous préférez en discuter directement ? [Réservez un Discovery Call](https://swissgrc.com/discoverycall) ou
Demander une démonstration
Nous vous répondrons sous un jour ouvré.
Prénom \*
Nom \*
E-mail professionnel \*
Entreprise \*
Fonction \*Veuillez sélectionner\*Risque tiers / Risque fournisseurGestion des risques / ERMConformité / GouvernanceAudit interne / AuditAchats / SourcingDirection générale / Conseil d'administrationAutre
Pays \*Veuillez sélectionner\*SuisseAllemagneAutricheAfghanistanAlbanieAlgérieAndorreAngolaAntigua-et-BarbudaArgentineArménieAustralieAzerbaïdjanBahamasBahreïnBangladeshBarbadeBiélorussieBelgiqueBelizeBéninBhoutanBolivieBosnie-HerzégovineBotswanaBrésilBruneiBulgarieBurkina FasoBurundiCap-VertCambodgeCamerounCanadaRépublique centrafricaineTchadChiliChineColombieComoresCongo (République démocratique)Congo (République)Costa RicaCôte d'IvoireCroatieCubaChypreTchéquieDanemarkDjiboutiDominiqueRépublique dominicaineÉquateurÉgypteSalvadorGuinée équatorialeÉrythréeEstonieEswatiniÉthiopieFidjiFinlandeFranceGabonGambieGéorgieGhanaGrèceGrenadeGuatemalaGuinéeGuinée-BissauGuyanaHaïtiHondurasHongrieIslandeIndeIndonésieIranIrakIrlandeIsraëlItalieJamaïqueJaponJordanieKazakhstanKenyaKiribatiKosovoKoweïtKirghizistanLaosLettonieLibanLesothoLiberiaLibyeLiechtensteinLituanieLuxembourgMadagascarMalawiMalaisieMaldivesMaliMalteÎles MarshallMauritanieMauriceMexiqueMicronésieMoldavieMonacoMongolieMonténégroMarocMozambiqueMyanmarNamibieNauruNépalPays-BasNouvelle-ZélandeNicaraguaNigerNigeriaCorée du NordMacédoine du NordNorvègeOmanPakistanPalaosPanamaPapouasie-Nouvelle-GuinéeParaguayPérouPhilippinesPolognePortugalQatarRoumanieRussieRwandaSaint-Christophe-et-NiévèsSainte-LucieSaint-Vincent-et-les-GrenadinesSamoaSaint-MarinSao Tomé-et-PrincipeArabie saouditeSénégalSerbieSeychellesSierra LeoneSingapourSlovaquieSlovénieÎles SalomonSomalieAfrique du SudCorée du SudSoudan du SudEspagneSri LankaSoudanSurinameSuèdeSyrieTadjikistanTanzanieThaïlandeTimor orientalTogoTongaTrinité-et-TobagoTunisieTurquieTurkménistanTuvaluOugandaUkraineÉmirats arabes unisRoyaume-UniÉtats-UnisUruguayOuzbékistanVanuatuCité du VaticanVenezuelaViêt NamYémenZambieZimbabwe
Votre demande \*Veuillez sélectionner\*Demander une démonstration en directLancer un filtrage sur notre registreTarification et licencesIntégration avec notre processus GRCAutre
Votre message
J'accepte la [politique de confidentialité](https://swissgrc.com/fr/privacy-policy/).
---
### [Compliance Software for Better Control and Less Risk](https://swissgrc.com/fr/compliance-software/)
**Published:** août 25, 2026
**Author:** superadmin
**Content:**
Gestion de la conformité# Quand le régulateur demande,
à quelle vitesse pouvez-vous répondre ?
Attribuez, mettez en œuvre et documentez vos obligations réglementaires.
**De la réglementation à la preuve**, dans un seul système.
[Demander une démo](#contact)[Découvrir les fonctionnalités](#features)
Boîte de réception réglementaireillustratifMise en œuvre2 août 2026EU AI Actnouveau5 unités concernées, 22 obligations dérivées41 %17 janv. 2025DORA6 unités concernées, 31 obligations dérivées87 %17 oct. 2024NIS24 unités concernées, 18 obligations dérivées79 %1er janv. 2024Circulaire FINMA 2023/13 unités concernées, 9 obligations dérivées100 %1er sept. 2023LPD suisse révisée12 unités concernées, 24 obligations dérivées100 %Pour chaque ligne, quelques minutes suffisent pour prouver qui est concerné, qui met en œuvre et ce qui est respecté.Boîte de réception réglementaireillustratif2 août 2026nouveau41 %EU AI Act5 unités, 22 obligations17 janv. 202587 %DORA6 unités, 31 obligations17 oct. 202479 %NIS24 unités, 18 obligations1er janv. 2024100 %Circulaire FINMA 2023/13 unités, 9 obligations1er sept. 2023100 %LPD suisse révisée12 unités, 24 obligationsPour chaque ligne, quelques minutes suffisent pourprouver qui est concerné, qui met en œuvre et ce qui est respecté.
Ils nous font confiance
Ce qui fait la différence## De la réglementation connue
à l'obligation démontrée
Connaître la réglementation est le métier. Ce qui distingue une fonction, c'est que chaque obligation ait un responsable, un contrôle et une preuve à jour.
Le point de départ habituel### Le registre des obligations vit dans Excel
Les réglementations sur un lecteur réseau, les obligations dans un tableur, les preuves dans la boîte mail. Quand une nouvelle règle arrive, la recherche recommence à zéro.
- Réglementations et obligations dispersées entre feuilles et dossiers
- Rien n'indique qui est responsable d'une obligation
- Politiques, formations et lancement d'alerte gérés séparément
- Une demande du régulateur déclenche des jours de travail manuel
Avec la plateforme SwissGRC®### Un seul registre des obligations, connecté de bout en bout
Réglementation, chapitre, obligation, responsable, contrôle et preuve se trouvent dans un seul modèle. L'état de conformité peut être consulté à tout moment.
- Réglementations décomposées jusqu'à l'obligation individuelle
- Chaque obligation avec un responsable, une échéance et une unité organisationnelle
- Contrôles, politiques et formations rattachés à l'obligation
- Lancement d'alerte, incidents et dossiers dans le même réseau
La plateforme## La conformité telle
qu'elle se vit au quotidien
Cinq vues du module Compliance de la plateforme SwissGRC®, le long de la chaîne réglementation, évaluation, risque, incident et signalement.
01 Réglementations et obligations02 Évaluation de conformité03 Risque de conformité04 Incidents et dossiers05 Lancement d'alerte
Registre des obligations### Chaque réglementation jusqu'à l'obligation individuelle
Les réglementations sont classées par autorité de régulation, thème et juridiction, puis décomposées en chapitres, sous-chapitres et obligations individuelles. **Chaque obligation porte un responsable.**
- Autorité de régulation, thème et juridiction par réglementation
- Décomposition en chapitres, sous-chapitres et obligations
- Contenu réglementaire saisi manuellement ou via un fournisseur de contenu
- Responsable, échéance et unité organisationnelle sur l'obligation

Évaluation### Maturité par exigence, avec preuves
Les normes et réglementations sont évaluées article par article, avec maturité, constats et preuves jointes. **La progression reste visible en permanence.**
- Évaluation selon la structure des articles de la norme
- Maturité et état de conformité par exigence
- Constats saisis directement sur l'article
- Preuves jointes au moment de l'évaluation

Risque et contrôle### Risque de conformité évalué et surveillé
Les risques de conformité sont évalués par catégorie, unité organisationnelle et thème réglementaire, puis liés à des contrôles et des actions. **L'état de remédiation se lit en un coup d'œil.**
- Évaluation par catégorie, unité et thème réglementaire
- Registre des risques lié aux contrôles et actions
- Actions par statut, avec escalade et échéances
- Cartographie des risques de conformité pour la direction et les comités

Gestion des dossiers### Du signalement au dossier clôturé
Les manquements, comportements fautifs et suspicions de fraude sont traités comme des dossiers, avec catégorie, gravité, responsable et date de l'incident. **Traçable de la détection à la résolution.**
- Catégorie, sous-catégorie et gravité par dossier
- Statut de la détection jusqu'à la résolution
- Responsable et unité organisationnelle concernée
- Lien avec le risque, le contrôle et l'action

Signalement confidentiel### Un canal de signalement qui inspire confiance
Un canal confidentiel guide les lanceurs d'alerte à travers le signalement en trois étapes, entièrement anonyme s'ils le souhaitent. **Le canal de réponse fonctionne avec un code d'accès, sans identité.**
- Signalement guidé en trois étapes, avec sélection de catégorie
- Code d'accès anonyme pour les questions de suivi et le statut
- Aucune donnée de connexion n'est enregistrée
- Les signalements arrivent directement dans la gestion des dossiers

Construit le long des normes et réglementations courantes. **Un seul registre des obligations** qui répond à plusieurs exigences à la fois.
ISO 37301ISO 37001[DORA](https://swissgrc.com/fr/digital-operational-resilience-act-dora/)[NIS2](https://swissgrc.com/fr/network-information-security-directive-nis2/)RGPD et LPDLBADirective UE sur les lanceurs d'alerte[Toutes les normes](https://swissgrc.com/fr/standards-frameworks/)
Preuve et surveillance## Ce qu'un système de conformité
doit pouvoir démontrer
ISO 37301 a rendu la gestion de la conformité certifiable pour la première fois. L'article 4.5 exige l'identification des obligations de conformité, l'article 4.6 leur évaluation des risques et l'article 8.3 un processus de signalement des préoccupations. La plateforme couvre exactement ces trois points.
Identifier et attribuer les obligations
Les exigences légales, réglementaires et contractuelles ainsi que les règles internes sont saisies, structurées et attribuées à une unité organisationnelle. C'est la base sur laquelle repose l'ISO 37301.
Évaluer le risque de conformité
Pour chaque obligation, la question de la probabilité et de l'impact, évaluée par catégorie, unité et thème réglementaire. C'est ce qui révèle où des contrôles et des actions sont réellement nécessaires.
Signaler des préoccupations sans risque
La Suisse n'a pas d'obligation légale générale de disposer d'un canal de signalement interne ; la révision correspondante du Code des obligations a finalement été rejetée en 2020. Les groupes disposant d'entités dans l'EEE relèvent de la directive (UE) 2019/1937, et l'ISO 37301 exige ce processus dans tous les cas.
Documenter les politiques et les formations
Attestations de lecture des politiques et formations obligatoires par rôle, avec date et personne. Qui a confirmé quoi et quand est prouvé, non affirmé.
À travers le GRC
La conformité est la plus solide là où contrôles, risques
et données se trouvent dans un même modèle.
[Système de contrôle interne](https://swissgrc.com/fr/internal-control-software-ics/)[Protection des données](https://swissgrc.com/fr/data-protection-management-software/)[Gestion des risques](https://swissgrc.com/fr/risk-management-software/)
Avantages## Ce que vous en retirez
Pas plus de conformité, mais une conformité démontrable. Avec moins de travail manuel.
#### Un seul registre des obligations
Chaque réglementation décomposée jusqu'à l'obligation individuelle, avec autorité, thème et juridiction. Une seule source au lieu de cinq tableurs.
#### Conformité prouvée
Pour chaque obligation, le contrôle, la preuve et la date. Toujours lisible longtemps après le changement de responsable.
#### Veille réglementaire
Les nouvelles règles sont saisies, évaluées et attribuées au lieu d'être découvertes par hasard. La charge de travail reste planifiable.
#### Responsabilités visibles
Responsable, échéance et unité organisationnelle sur chaque obligation. Personne n'a besoin de demander qui est responsable.
#### Détecter les problèmes tôt
Les signalements, incidents et conflits d'intérêts se rejoignent dans le même dossier. Les tendances apparaissent avant de devenir coûteuses.
#### À travers le GRC
La conformité partage le modèle organisationnel, les contrôles et les actions avec la gestion des risques, le contrôle interne et l'audit interne. Rien n'est maintenu deux fois.
Contact et démo## Découvrez notre solution
de conformité en action
Lors d'une démo personnalisée, nous vous présentons le registre des obligations, l'évaluation, la gestion des dossiers et le canal de signalement. Vous voyez comment une obligation unique se déroule, de la réglementation jusqu'à la preuve.
[Demander une démo](https://swissgrc.com/fr/demo)[Contacter les ventes](https://swissgrc.com/fr/sales)
---
### [Legal](https://swissgrc.com/fr/legal/)
**Published:** septembre 2, 2026
**Author:** superadmin
**Content:**
## Legal Basis for Our Services
This page contains all relevant legal and contractual documents for our services. The following materials include our General Terms and Conditions as well as product-specific provisions, definitions, support guidelines, and information on subcontractors. Please read the respective documents carefully, as they form the basis for the use of our products and services.
## Global Documents
[Aktuelle Allgemeine Geschäftsbedingungen (v2510)](/wp-content/uploads/2026/01/Swiss-GRC-AGB-DE-2510.pdf)
## Product-Specific Documents
**Contraqto**
[Definitionen (v2510)](/wp-content/uploads/2026/01/Contraqto-Anh_1_DE_Definitionen_v2510.pdf)
[Support-Richtlinien (v2510)](/wp-content/uploads/2026/01/Contraqto-Anh_3_DE_Support_v2510.pdf)
[Unterbeauftragte (v2510)](/wp-content/uploads/2026/01/Contraqto-Anh_4_DE_Unterbeauftragte_v2510.pdf)
---
### [Privacy policy](https://swissgrc.com/fr/privacy-policy/)
**Published:** novembre 15, 2022
**Author:** superadmin
**Content:**
## Data protection is important to us
We take the protection of your personal data very seriously. In this Privacy Notice, we inform you about how we collect and otherwise process your personal data (hereinafter also referred to as « data ») in connection with the processing activities described below. In addition to this Privacy Notice, we may inform you separately about the processing of your data (e.g., in forms or contract terms).
We are committed to handling your data responsibly. Consequently, we consider it a matter of course to comply with the Swiss Federal Act on Data Protection (FADP), the associated Ordinance (FADP) and other applicable data protection regulations, in particular the provisions of the EU General Data Protection Regulation (GDPR).
This Privacy Notice covers the collection of personal data both online and offline, including personal data that we have received from various sources, e.g., website visitors, contractual partners, service providers, and authorities.
## Description and scope of data processing
Visiting our websiteWhen you visit our website, our servers temporarily store the following data in a log file, known as a server log file:
- IP address of the requesting computer
- Date and time of access/retrieval
- Name and URL of the retrieved data
- Operating system of your computer and the browser you are using
- Country from which our website is accessed
- Name of your Internet service provider
- Time zone difference from Greenwich Mean Time (GMT)
- Content of the request (specific page)
- Access status/HTTP status code
- Amount of data transferred
- Last website visited
- Browser settings
- Language and version of browser software
- Activated browser plug-ins
The purpose of processing this information is to display our website and its content and offers correctly and to ensure data traffic, to optimize our website, content, and offers, to ensure the stability and security of our website and systems on an ongoing basis, and to enable the investigation, defense, and prosecution of cyberattacks, spam, and other illegal activities in relation to our website and systems and to enforce related claims.
We delete your personal data as soon as it is no longer required for the purpose for which it was collected. In the case of data collection for the provision of our website, deletion takes place when the respective session is ended.
ContactIf you contact us via our contact addresses and channels (e.g., by email, telephone, or contact form), your personal data will be processed. The data you have provided us with (e.g., your name, email address, or phone number and your request) will be processed. The data collected in the case of a contact form can be seen on the respective form. In addition, the time of receipt of the request is documented. Mandatory fields in contact forms are marked with an asterisk (\*).
We process this data exclusively for the purpose of responding to your request (e.g., providing information about our GRC software, assisting with contract processing, such as questions about your license, incorporating your feedback into the improvement of our services, etc.). The basis for this data processing is our legitimate interest in processing your request. If the purpose of the contact is to fulfill a contract to which you are a party or to carry out pre-contractual measures, this is an additional basis for the processing of your personal data.
CalendlyWe use Calendly to schedule appointments with you. This is a service provided by Calendly LLC, 115 E Main St, Ste A1B, Buford, GA 30518, USA.
If you click the corresponding button on our website or wish to schedule an appointment through a link we provided (such as in an email), you will be connected to our scheduling account with Calendly. After selecting your appointment, confirming it, and entering your contact details, you will receive an email with the appointment confirmation from Calendly. The following personal data will be processed: name, email address, possibly phone number, as well as your inquiry and appointment details.
The basis for data processing is our legitimate interest in efficient appointment handling. The use of the Calendly function is voluntary. If you do not wish to submit your data through Calendly, you can alternatively reach us via email or phone.
Calendly uses cookies and similar technologies when embedding the appointment booking tool on our website. These can be managed and declined through our cookie consent banner.
We have concluded a Data Processing Agreement with Calendly, including EU standard contractual clauses, along with Switzerland-specific adjustments. Calendly also relies on additional subprocessors (including for infrastructure, support, and product analysis) that are also based in the USA.
Calendly is also certified under the Swiss-U.S. Data Privacy Framework (Swiss-US DPF).
Your data provided in the Calendly form will be stored as long as necessary for the processing of your request or due to an existing contractual relationship. After the purpose has been fulfilled, your data will be deleted, subject to contractual or legal retention periods.
For more information on data protection at Calendly, please visit [calendly.com/privacy](https://calendly.com/privacy).
Newsletters and marketing mailingsOn our website, you have the option to subscribe to our newsletter as well as to the newsletter covering similar offers and services provided by our affiliated company, Swiss Infosec AG (see section «Transfer of personal data»). When you register for one of our newsletters, various data will be collected from you (e.g., your email address), depending on the newsletter. Mandatory fields in the registration form are marked with an asterisk (\*). With these newsletters and marketing mailings, we inform you about current specialist topics, new products, services, events, and the like.
In addition, where permitted by law, you may also receive information about similar offers and services from our affiliated companies (see section «Transfer of personal data»; generally Swiss Infosec AG). You acknowledge that the affiliated Swiss GRC AG and Swiss Infosec AG, as well as their respective group companies, operate within a shared economic context and may exchange your contact details with one another for this purpose.
Some information is sent by our affiliated companies or third parties. By registering, you agree that we may process your data and transfer it to affiliated companies or third parties located abroad (including outside Switzerland), that we may track your clicking and opening behavior, that we combine your data and information about your use of our services, as well as any information about you received from you or third-party sources or already stored by us, in a user profile and evaluate it individually in order to address you with tailored and relevant advertising, and that we contact you directly in individual cases. Where required by law, we will obtain your consent in advance, unless we have obtained your contact details in the course of providing our services and you have not expressly refused to receive such marketing measures. If you no longer wish to receive such communications from us, you can unsubscribe at any time using the contact details provided. You can unsubscribe from newsletters and marketing mailings at any time; there is an unsubscribe link at the end of each email.
For information about the Swiss Infosec AG newsletter, please refer to their privacy policy.
Job applicationsIf you apply for a job with us, we will process the personal data that we receive from you as part of the application process. In addition to your personal details, education, work experience, and skills, this includes the usual correspondence data such as postal address, email address, and telephone number. In addition, all documents submitted by you in connection with the application, such as cover letters, resumes, and references, will be processed.
We use this and other data you voluntarily provide to review your application. Application documents from unsuccessful applicants will be deleted after the application process has been completed, unless you explicitly agree to a longer retention period or we are legally obliged to retain them for a longer period. Your application data is processed in order to fulfill our (pre)contractual obligations within the framework of the application process.
Specialist eventWhen we hold events (such as SWISS GRC DAY), we also process personal data. This includes the name and postal or e-mail address of participants or interested parties and, depending on the event, other data such as photographs taken during the event. We process this information for the preparation, implementation, and follow-up of the events. Data relevant to the implementation may also be passed on to third parties. The basis for data processing is your consent or our legitimate interest in the smooth administration and implementation of the respective event.
We will include your name and details of your role in the organization or company you work for in a list of participants. We will make this list available to other participants. Please let us know if you do not want this.
Provision of contractual servicesWe process the data of our contractual partners and interested parties as well as other clients, customers, and clients (« contractual partners ») in order to provide them with our contractual or pre-contractual services. The data processed in this context, the type, scope, and purpose of the processing, and the necessity of the processing are determined by the underlying contractual relationship.
The data processed includes the master data of our contractual partners (e.g., names and addresses), contact details (e.g., email addresses and telephone numbers), contract data (e.g., services used, contract content, contractual communication, names of contact persons), and payment data (e.g., bank details, payment history).
The legal basis for processing your data for this purpose is the fulfillment of a contract.
Administration, financial accounting, office organization, contact managementWe process data in the context of administrative tasks and the organization of our business, financial accounting, and in compliance with legal obligations, such as archiving. In doing so, we process the same data that we process in the context of providing our contractual services. Customers, interested parties, business partners, and website visitors are affected by this processing.
The purpose and our interest in processing lies in administration, financial accounting, office organization, and data archiving, i.e., tasks that serve to maintain our business activities, perform our duties, and provide our services.
Furthermore, based on our business interests, we store information about suppliers, event organizers, and other business partners, e.g., for the purpose of contacting them at a later date. We generally store this data, most of which is company-related, on a permanent basis.
## Cookies
Cookies usedWe use cookies on our website. Cookies are small text files that are stored on your device (laptop, tablet, smartphone, etc.) with the help of your browser. They serve to make our website more user-friendly and effective overall and to make your visit to our website as pleasant as possible. Cookies do not cause any damage to your device. They cannot execute programs or contain viruses.
Most of the cookies we use are so-called session cookies. These are automatically deleted when you log out or close your browser. Other cookies remain stored on your computer beyond the respective usage process and enable us or our partner companies (third-party cookies) to recognize your browser the next time you visit. If other cookies (e.g., cookies for analyzing your surfing behavior) are stored, these are treated separately in this Privacy Notice.
The basis on which we process your personal data using cookies depends on whether we ask for your consent. If this applies and you consent to the use of cookies, the basis for processing your data is your consent. Otherwise, the personal data processed using cookies is processed on the basis of our legitimate interests (e.g., in analyzing and optimizing our services and offers) or, if the use of cookies is necessary to fulfill our contractual obligations.
Withdrawing consentRegardless of whether processing is based on consent or legal permission, you have the option of revoking your consent at any time or objecting to the processing of your data by cookie technologies. You can set your browser to inform you when cookies are set and only allow cookies in specific cases or exclude them altogether. You can also activate the automatic deletion of cookies when you close your browser. In addition, you can delete cookies that have already been set at any time via an Internet browser or other software programs. You can find out how to manage cookies in your browser in the help menu of your browser.
Completely deactivating cookies may mean that you cannot use all the functions of our website to their full extent.
## Analytics tools
Simple AnalyticsWe use the privacy-friendly analytics service Simple Analytics (Simple Analytics B.V., Netherlands) on our website.
Simple Analytics does not collect any personal data and does not use cookies. Instead, only anonymous usage data such as page views, referrers (if available), or device types used are collected. This information helps us understand how our website is used without creating personal profiles.
The data is stored on servers within the European Union and is subject to the strict requirements of the General Data Protection Regulation (GDPR) and the Swiss Data Protection Act (DSG).
Since Simple Analytics does not process any personal data, explicit consent via a cookie banner is not required for this service.
For more information on data collection and processing by Simple Analytics, please refer to the Simple Analytics Privacy Notice.
Google AnalyticsWe use a web analytics service provided by Google LLC, 1600 Amphitheatre Parkway Mountain View, CA 94043, USA, or, if you are a resident of the European Union (EU), the European Economic Area (EEA), or Switzerland, Google Ireland Limited, Gordon House, Barrow Street, Dublin 4, Ireland (« Google »), on our website.
Google uses cookies. The information generated by the cookie about your use of our website (including your IP address) may be transmitted to and stored by Google on servers in the United States.
Google uses this information to evaluate your use of our website, to compile reports on website activity and to provide us with other services relating to website and internet usage. Pseudonymous user profiles may be created from the processed data.
The IP address transmitted by your browser within the scope of Google Analytics is not merged with other Google data.
We only use Google Analytics with IP anonymization enabled. This means that your IP address will be truncated by Google within Switzerland or the EU/EEA before being transmitted to the USA. Only in exceptional cases will the full IP address be transmitted to a Google server in the USA and truncated there.
You can prevent the storage of cookies by adjusting your browser software settings accordingly. In addition, you can prevent Google from collecting and processing data by downloading and installing the browser add-on to deactivate Google Analytics. An opt-out cookie will be set, which will prevent the future collection of your data when you visit our website. However, we would like to point out that in this case you may not be able to use all the functions of this website to their full extent.
Your personal data will be deleted or anonymized after 14 months.
For further information, please refer to the Google Analytics Terms of Service or Google’s Privacy Policy.
Google RemarketingWe use the Google Marketing Platform (« GMP »), a service provided by Google LLC, 1600 Amphitheatre Parkway Mountain View, CA 94043, USA, or, if you are a resident of the European Union (EU), the European Economic Area (EEA), or Switzerland, Google Ireland Limited, Gordon House, Barrow Street, Dublin 4, Ireland (« Google »).
GMP enables us to show you personalized advertising. For this purpose, a cookie with limited validity is stored on your device. With the help of this cookie, your browser is assigned an identification number (ID) and information about the advertising displayed in your browser and its retrieval is collected. In addition, Google can use cookie IDs to track so-called conversions, i.e., whether a website visitor sees an ad and later visits the advertiser’s website and makes a purchase there. According to Google, these cookies do not contain any personal data.
Your browser automatically establishes a direct connection to Google’s server. We have no influence on the scope and further use of the data collected by Google through the use of this service. According to its own information, Google receives information through the integration of these services that you have accessed the corresponding part of our website or clicked on one of our ads. If you are registered with a Google service, Google can assign the visit to your user account. Even if you are not registered with Google or have not logged in, it is possible that the provider may find out and store your IP address. When using GMP, personal data may also be transferred to the servers of Google LLC. in the USA.
We use GMP on the basis of our legitimate interest in the optimal marketing of our website.
You can refuse the use of cookies by adjusting the settings in your browser. In addition to changing your browser settings, you can permanently disable personalized advertising by installing a browser plug-in (available for Chrome, Firefox, and Internet Explorer). You can also disable personalized advertising for a specific device and browser via Google’s advertising settings.
For more information about the Google Marketing Platform and data protection, please visit: [policies.google.com/technologies/ads](https://policies.google.com/technologies/ads?hl=en).
Google AdsWe use the online advertising program Google Ads, which is part of Google Marketing Services, a service provided by Google LLC, 1600 Amphitheatre Parkway Mountain View, CA 94043, USA, or, if you are a resident of the European Union (EU), the European Economic Area (EEA), or Switzerland, Google Ireland Limited, Gordon House, Barrow Street, Dublin 4, Ireland (« Google »).
Google Ads places a cookie on your device (a so-called « conversion cookie ») if you have accessed our website via a Google ad. These cookies have a limited validity, do not contain any personal data, and therefore do not serve to personally identify you. If you visit certain pages on our website and the cookie has not yet expired, Google and we can recognize that you clicked on the ad and were redirected to our website. Each Google Ads customer receives a different cookie. This means that cookies cannot be tracked across the websites of Ads customers. The information collected using the conversion cookie is used to generate conversion statistics for Ads customers who have opted for conversion tracking. We do not receive any information that can be used to personally identify you.
The information collected by the cookie about your use of our website may be transmitted to a Google server in the USA and stored there. Based on the information collected, your browser is assigned categories relevant to your interests. These categories are used to display interest-based advertising.
You have the option to opt out of interest-based advertising by Google. To do so, visit the following link using the browser you are using and make the desired settings there: [adssettings.google.ch](https://adssettings.google.ch/).
Further information on the terms of use and data protection of Google Ads can be found at [policies.google.com/technologies/ads](https://policies.google.com/technologies/ads?hl=us).
Google Marketing PlatformWe use the Google Marketing Platform (« GMP »), a service provided by Google LLC, 1600 Amphitheatre Parkway Mountain View, CA 94043, USA, or, if you are a resident of the European Union (EU), the European Economic Area (EEA), or Switzerland, Google Ireland Limited, Gordon House, Barrow Street, Dublin 4, Ireland (« Google »).
GMP enables us to show you personalized advertising. For this purpose, a cookie with limited validity is stored on your device. With the help of this cookie, your browser is assigned an identification number (ID) and information about the advertising displayed in your browser and its retrieval is collected. In addition, Google can use cookie IDs to track so-called conversions, i.e., whether a website visitor sees an ad and later visits the advertiser’s website and makes a purchase there. According to Google, these cookies do not contain any personal data.
Your browser automatically establishes a direct connection to Google’s server. We have no influence on the scope and further use of the data collected by Google through the use of this service. According to its own information, Google receives information through the integration of these services that you have accessed the corresponding part of our website or clicked on one of our ads. If you are registered with a Google service, Google can assign the visit to your user account. Even if you are not registered with Google or have not logged in, it is possible that the provider may find out and store your IP address. When using GMP, personal data may also be transferred to the servers of Google LLC. in the USA.
We use GMP on the basis of our legitimate interest in the optimal marketing of our website.
You can refuse the use of cookies by adjusting the settings in your browser. In addition to changing your browser settings, you can permanently disable personalized advertising by installing a browser plug-in (available for Chrome, Firefox, and Internet Explorer). You can also disable personalized advertising for a specific device and browser via Google’s advertising settings.
For more information about the Google Marketing Platform and data protection, please visit: [policies.google.com/technologies/ads](https://policies.google.com/technologies/ads?hl=en).
## Content Management System (CMS)
All in One Search Engine Optimization (SEO)Our website uses the All in One SEO plugin from Awesome Motive Inc., 2701 W. Busch Blvd., Suite 141, Tampa, FL 33618, USA.
The plugin is used for the technical optimization of our website for search engines, thereby increasing our visibility in them. No personal data is processed, collected, or stored in any way by the All in One SEO plugin, either by All in One SEO itself or on its servers.
Further information can be found in the Privacy Notice of Awesome Motive Inc. and in the All in One SEO Help Center.
Defender ProWe use the Defender Pro plugin from WPMU DEV, Inc., LLC, 1309 Coffeen Avenue STE 1200, Sheridan, WY 82801, USA, on our website.
This plugin is used to protect our website. It is a malware scanner and web application firewall for WordPress websites. Defender Pro collects your IP address and other data about your behavior on our website, in particular URLs accessed and header information, to protect against attackers from the Internet. Your IP address is compared with a list of known attackers. Cookies are also set for registered users.
The plugin enables us to block the IP address of individuals who attempt to gain unauthorized access to the administration of our website or attack the website in any other way from further access.
For more information on how user data is handled, please refer to the WPMU DEV Privacy Notice.
## Google reCAPTCHA
FunctionWe use the reCAPTCHA function from Google LLC, 1600 Amphitheatre Parkway, Mountain View, CA 94043, USA, on our website, or if you are a resident of the European Union (EU), the European Economic Area, or Switzerland, Google Ireland Limited, Gordon House, Barrow Street, Dublin 4, Ireland (« Google »).
This function is primarily used to distinguish whether an entry is made by a natural person or abusively by machine and automated processing. The service also includes sending the IP address and, if necessary, other data required by Google for the reCAPTCHA service to Google.
reCAPTCHA is used to verify whether data entry on our website (e.g., in a contact form) is performed by a human or by an automated program. To do this, reCAPTCHA analyzes the behavior of the website visitor based on various characteristics. This analysis begins automatically as soon as the website visitor enters the website. reCAPTCHA evaluates various information for the analysis (e.g., IP address, length of time the website visitor stays on the website, or mouse movements made by the user). The data collected during the analysis is forwarded to Google.
The reCAPTCHA analyses run completely in the background. Website visitors are not notified that an analysis is taking place.
Data processing is based on our legitimate interest in protecting our web offerings from abusive automated spying and spam.
Further informationFurther information about Google reCAPTCHA and Google’s Privacy Notice can be found at: [policies.google.com/privacy](https://policies.google.com/privacy?hl=en).
## Transfer of personal data
Data transferWe treat your personal data as confidential and only pass it on if you have expressly consented to this, if we are legally obliged or entitled to do so (e.g. in the context of order data processing) or if this is necessary to enforce our rights, in particular to enforce claims arising from the contractual relationship. Under no circumstances do we sell your data.
We also disclose your personal data to third parties within the scope of our business activities and for the above-mentioned purposes, insofar as this is permitted and appropriate, either because they process it for us (contract data processing) or because they wish to use it for their own purposes (data disclosure). This applies in particular to:
- Our affiliated companies, i.e., companies of our group (our subsidiaries Swiss GRC (UK) Limited, London, Swiss GRC Germany GmbH, Frankfurt, Swiss GRC Kosovo L.L.C., Prishtina, Swiss GRC Dubai « Branch of a foreign company » (Swiss GRC AG), Dubai, Swiss GRC India « Branch of a foreign company » (Swiss GRC AG), Mumbai) and companies with which we operate in a shared economic context. Affiliated companies are all companies that have one of the following relationships with Swiss GRC AG: (a) companies over which Swiss GRC AG directly or indirectly exercises control; (b) companies that directly or indirectly exercise control over Swiss GRC AG; (c) companies that are directly or indirectly controlled by a company within the meaning of lit. (b); (d) companies in which the same natural person who is directly or indirectly the beneficial owner of Swiss Infosec AG is also directly or indirectly the beneficial owner. Our affiliated companies primarily include Swiss Infosec AG, Lucerne, and its group companies.
- Service providers
- Operators of our IT operating infrastructure
- Business partners
- Suppliers
- Authorities and courts
We may share your personal data, which we receive from you or from third-party sources, with companies in our group for administrative support purposes, but also for marketing activities. In connection with marketing activities, we share the following data, among other things:
- Contact and identification data, contract data, communication data
In doing so, we naturally comply with the legal requirements for the disclosure of personal data to third parties. If we use processors to provide our services, we take appropriate legal precautions and technical and organizational measures to ensure that your personal data is protected in accordance with the relevant legal requirements.
Data transfer abroadWe generally process personal data in Switzerland or in an EU/EEA country or in another country that has an adequate level of data protection. With regard to certain processing operations, you must expect your data to be transferred to other countries within and outside Europe, where some of the IT service providers we use are located. If we disclose data to a country that does not have an adequate level of legal data protection, we require the recipient to take appropriate measures to protect your privacy (e.g., by agreeing to so-called EU standard clauses, the current version of which is available here, other precautions, or based on justifications).
Social mediaIn addition to our website, we also maintain a presence on various social media platforms. If you visit such an online presence, personal data may be transmitted to the social network provider. We would like to point out that user data may also be transmitted to a server in a third country and thus processed outside Switzerland.
Furthermore, user data within social networks is generally processed for market research and advertising purposes. For these purposes, cookies are usually stored on users’ computers, in which the usage behavior and interests of users are stored. Furthermore, data may also be stored in user profiles independently of the devices used by users (in particular if users are members of the respective platforms and are logged in to them).
For a detailed description of the respective forms of processing and the options for objection (opt-out), we refer you to the data protection regulations and information provided by the operators of the respective networks. There you will also find out in which countries they process your data, what rights you have to information, deletion, and other rights of data subjects, and how you can exercise these rights or obtain further information.
## Storage period
Processing and storageUnless expressly stated in this Privacy Notice, we only process and store your personal data for as long as is necessary to fulfill our contractual and legal obligations or otherwise for the purposes pursued with the processing, i.e., for example, for the duration of the entire business relationship (from the initiation and execution to the termination of a contract and the warranty period, as well as a subsequent support phase) and beyond, in accordance with the statutory retention and documentation periods. It is also possible that personal data may be retained for the period during which claims can be asserted against us and insofar as we are otherwise legally obliged to do so or legitimate business interests require this (e.g. for evidence and documentation purposes).
DeletionAs soon as your personal data is no longer required for the above-mentioned purposes or a prescribed retention period expires, your personal data will be deleted or anonymized as a matter of principle and as far as possible.
In addition, we will delete your personal data if you request us to do so and we have no legal or contractual retention or other security obligations with regard to this data or any overriding interests in this regard.
## Data
Security measuresWe take appropriate technical and organizational security measures to protect your personal data and continuously improve these in line with technological developments. This includes protection against accidental or intentional manipulation, loss, destruction, or unauthorized access by third parties, such as the use of recognized encryption methods (e.g., encryption using SSL/TLS).
The measures taken are designed to ensure the confidentiality and integrity of your personal data as well as the availability and resilience of our systems and services when processing your personal data on a permanent basis. They also ensure the rapid restoration of the availability of your personal data and access to it in the event of a physical or technical incident.
We also take our own internal data protection seriously. Our employees and the service providers we commission are obliged to maintain confidentiality and comply with data protection regulations. Furthermore, they are only granted access to your personal data to the extent necessary.
## Your rights as a data subject
RightsYou have the right to obtain information about the personal data we process about you, provided that there is no legal obligation to the contrary. If the relevant legal requirements apply and the conditions are met, you are also free to request data transfer, correction, deletion, or restriction of processing.
You are also free to revoke your consent to the processing of your personal data at any time. Within the framework of the applicable legal requirements, you also have the right to object to certain processing operations, for example if these are based on a balancing of interests. In particular, you have the right to object to the processing of your data in connection with direct marketing.
Where applicable, you also have the right to enforce your claims in court or to lodge a complaint with the competent data protection authority. The competent data protection authority in Switzerland is the Federal Data Protection and Information Commissioner (FDPIC) ([edoeb.admin.ch/en](https://www.edoeb.admin.ch/en)).
LimitationsPlease note that we reserve the right to apply the restrictions provided for by law, for example if we are obliged to store or process certain data, have an overriding interest in doing so (insofar as we are permitted to invoke this) or need it to assert claims.
Please also note that exercising these rights may conflict with contractual agreements and may have consequences such as premature termination of the contract or cost implications. In this case, we will inform you in advance if this is not already regulated in the contract.
ExerciseIf you have any questions regarding our data protection practices or would like information about your rights and how to exercise them, please contact us using the contact details provided in this Privacy Notice. If necessary, we reserve the right to request your identification in order to process your request in an appropriate manner.
## Changes to the Privacy Notice
We expressly reserve the right to amend and supplement this Privacy Notice at any time and at our sole discretion. All changes and additions are at the sole discretion of the company.
## Contact
The responsible party within the meaning of data protection laws is:
**Swiss GRC AG**
Hirschmattstrasse 36
6003 Lucerne
Switzerland
Tel.: [+41 41 220 75 00](tel:+41412207500)
Email:
Website: [www.swissgrc.com](https://www.swissgrc.com)
Our data protection advisor is:
**Swiss Infosec AG**
Meienriesliweg 15
6210 Sursee
Tel.: [+41 41 984 12 12](tel:+41419841212)
Email:
Website: [www.infosec.ch](https://www.infosec.ch)
We have the following data protection representative in accordance with Art. 27 GDPR. The data protection representative serves as an additional point of contact for supervisory authorities and data subjects in the European Union (EU) and the rest of the European Economic Area (EEA) for inquiries relating to the General Data Protection Regulation (GDPR):
**Swiss Infosec (Germany) GmbH**
Unter den Linden 24
10117 Berlin, Germany
Tel.: [+41 41 984 12 12](tel:+41419841212)
Email:
We have the following data protection representative in accordance with Art. 27 UK GDPR. The data protection representative serves as an additional point of contact for supervisory authorities and data subjects in the United Kingdom for inquiries relating to the UK GDPR:
**Swiss GRC (UK) Ltd.**
5th Floor 167-169 Great Portland Street
London W1W 5PF
England
---
### [Imprint](https://swissgrc.com/fr/imprint/)
**Published:** février 13, 2023
**Author:** superadmin
**Content:**
## Headquarters
**Swiss GRC AG**
Hirschmattstrasse 36
6003 Lucerne
Switzerland
Phone: [+41 41 220 75 00](tel:+41412207500)
Email:
Registered in the Commercial Register of the Canton of Lucerne: CHE-145.606.205
Value added tax number: CHE-145.606.205 VAT
## Chief Executive Officer
Besfort Kuqi
## Copyright
The content of this website is protected by copyright. Use of the editorial content, images, graphics and other data is not permitted, or only permitted with the express consent of Swiss GRC AG.
---
### [Swiss GRC for Media: Interviews and Expert Voices](https://swissgrc.com/fr/press/)
**Published:** juillet 14, 2026
**Author:** superadmin
**Content:**
Swiss GRC in the Media | Press and Media Contact Press# When it comes to GRC, the media ask us
Business and trade media across Europe, the Middle East and Asia turn to Swiss GRC for perspective on governance, risk and compliance. For interviews, quotes and expert commentary, our press office is always available.
[Make a press enquiry](#sgpr-kontakt) [See the coverage](#sgpr-medien)
In the media## Swiss GRC in the news
These outlets report on Swiss GRC and quote our experts on current GRC topics.


From the coverage
[Der TagesspiegelCyberattacks that strike via detours](https://background.tagesspiegel.de/it-und-cybersicherheit/briefing/it-angriffe-ueber-umwege)[Börsen-ZeitungNew security directive aims to curb hackers](https://www.boersen-zeitung.de/meinung-analyse/neue-sicherheitsrichtlinie-soll-hackern-das-handwerk-legen)[HandelszeitungGRC is still run reactively](https://www.hzinsurance.ch/interviews/governance-risk-und-compliance-werden-noch-immer-reaktiv-betrieben/cberem9)[Security-InsiderThird-party risks are systematically underestimated](https://www.security-insider.de/lieferkettenrisiken-cybersecurity-third-party-angriffe-a-fc524787c1b7676b663beb3af25496f5/)[ComputerworldGRC becomes a gamechanger](https://www.computerworld.ch/themen/security-und-compliance/grc-wird-zum-gamechanger)[silicon.deSerious gaps in NIS2 implementation](https://www.silicon.de/41722561/es-hapert-gewaltig-in-der-umsetzung-von-nis2)[manage itHow GRC became a leadership task](https://ap-verlag.de/warum-grc-fuer-unternehmen-vom-it-thema-zur-fuehrungsaufgabe-geworden-ist/105089/)[Table.MediaNIS2 in force, yet too few companies act](https://table.media/security/tablestandpunkt/nis-2-ist-in-kraft-doch-zu-wenige-unternehmen-handeln)[it-dailyThird-party risks in focus](https://www.it-daily.net/it-sicherheit/cybercrime/third-party-risiken-fokus)[datensicherheit.deHarmonising GRC with AI](https://www.datensicherheit.de/governance-risk-compliance-grc-ki)[CashHow third-party attacks hit financial firms](https://www.cash-online.de/a/neue-bedrohungslage-wie-third-party-angriffe-finanzunternehmen-treffen-714348/)[Infopoint SecurityMeeting NIS2 with a Swiss GRC solution](https://www.infopoint-security.de/nis2-im-fokus-anforderungen-mit-spezialloesung-von-swiss-grc-umsetzen/a44586/)[all about securityFinance teams must reassess third-party risk](https://www.all-about-security.de/unterschaetztes-sicherheitsrisiko-warum-finanzabteilungen-third-party-risiken-neu-bewerten-muessen/)[Khaleej TimesHow to build a strong GRC programme amid new risks](https://www.khaleejtimes.com/uae/gcc-grc-day-uae-edition)[Gulf NewsSwiss GRC launches GRC software for the MENA region](https://gulfnews.com/technology/swiss-grc-launches-governance-risk-and-compliance-software-designed-for-mena-region-1.1717151149961)[Business StandardSwiss GRC targets the Indian market](https://www.business-standard.com/companies/news/swiss-grc-targets-revenue-of-10-million-from-indian-market-in-fy25-124020601359_1.html)[Risk.netGRC Product of the Year, Risk Technology Awards](https://www.risk.net/risk-technology-awards/winners)[Der TagesspiegelCyberattacks that strike via detours](https://background.tagesspiegel.de/it-und-cybersicherheit/briefing/it-angriffe-ueber-umwege)[Börsen-ZeitungNew security directive aims to curb hackers](https://www.boersen-zeitung.de/meinung-analyse/neue-sicherheitsrichtlinie-soll-hackern-das-handwerk-legen)[HandelszeitungGRC is still run reactively](https://www.hzinsurance.ch/interviews/governance-risk-und-compliance-werden-noch-immer-reaktiv-betrieben/cberem9)[Security-InsiderThird-party risks are systematically underestimated](https://www.security-insider.de/lieferkettenrisiken-cybersecurity-third-party-angriffe-a-fc524787c1b7676b663beb3af25496f5/)[ComputerworldGRC becomes a gamechanger](https://www.computerworld.ch/themen/security-und-compliance/grc-wird-zum-gamechanger)[silicon.deSerious gaps in NIS2 implementation](https://www.silicon.de/41722561/es-hapert-gewaltig-in-der-umsetzung-von-nis2)[manage itHow GRC became a leadership task](https://ap-verlag.de/warum-grc-fuer-unternehmen-vom-it-thema-zur-fuehrungsaufgabe-geworden-ist/105089/)[Table.MediaNIS2 in force, yet too few companies act](https://table.media/security/tablestandpunkt/nis-2-ist-in-kraft-doch-zu-wenige-unternehmen-handeln)[it-dailyThird-party risks in focus](https://www.it-daily.net/it-sicherheit/cybercrime/third-party-risiken-fokus)[datensicherheit.deHarmonising GRC with AI](https://www.datensicherheit.de/governance-risk-compliance-grc-ki)[CashHow third-party attacks hit financial firms](https://www.cash-online.de/a/neue-bedrohungslage-wie-third-party-angriffe-finanzunternehmen-treffen-714348/)[Infopoint SecurityMeeting NIS2 with a Swiss GRC solution](https://www.infopoint-security.de/nis2-im-fokus-anforderungen-mit-spezialloesung-von-swiss-grc-umsetzen/a44586/)[all about securityFinance teams must reassess third-party risk](https://www.all-about-security.de/unterschaetztes-sicherheitsrisiko-warum-finanzabteilungen-third-party-risiken-neu-bewerten-muessen/)[Khaleej TimesHow to build a strong GRC programme amid new risks](https://www.khaleejtimes.com/uae/gcc-grc-day-uae-edition)[Gulf NewsSwiss GRC launches GRC software for the MENA region](https://gulfnews.com/technology/swiss-grc-launches-governance-risk-and-compliance-software-designed-for-mena-region-1.1717151149961)[Business StandardSwiss GRC targets the Indian market](https://www.business-standard.com/companies/news/swiss-grc-targets-revenue-of-10-million-from-indian-market-in-fy25-124020601359_1.html)[Risk.netGRC Product of the Year, Risk Technology Awards](https://www.risk.net/risk-technology-awards/winners)
Press contact## You research, we bring the substance
Interviews, quotes and background on NIS2, DORA, third-party risk and AI in GRC. Fast and well-founded.
[Contact us](https://swissgrc.com/en/contact/)
Or directly: [marketing@swissgrc.com](mailto:marketing@swissgrc.com?subject=Press%20enquiry%20Swiss%20GRC)
---
### [Career](https://swissgrc.com/fr/jobs/)
**Published:** décembre 20, 2022
**Author:** superadmin
**Content:**
Jobs and career# Short paths.
Real ownership.
Banks, insurers, public authorities and industrial companies manage their risk with our software. Built in Lucerne, in use across Europe, the Middle East and Asia.
[View open roles](#sgcar-jobs) [Apply proactively](https://swissgrc.com/en/job/unsolicited-application/)
- 0Organisations work with our platform
- 0Specialists across the group
- 0Own entities in Europe, MEA and APAC
- 0Users of the SwissGRC® Platform worldwide
Working at Swiss GRC## Work that counts when it matters.
Governance, risk and compliance sounds like a rulebook. In truth it is about trust: that a bank knows its risks, that a hospital keeps running in an emergency, that an energy provider can prove its controls work. We build the SwissGRC® Platform that makes this possible: governance, risk and compliance, process management and contract management on one shared data foundation.
Our clients demand precision. That is demanding, and it makes your own work visible. What you build, advise on or sell here does not end up in a drawer. It ends up in processes people use every day.
Confirmed from outside## Not our own assessment.
How good an employer is, its people decide. How good a product is, analysts and clients decide. Both have been assessed.

### Great Place To Work Certified
The certification is based on an anonymous survey of our own employees on trust, pride and camaraderie. Not a ranking you can buy, but the verdict of the people who work here every day.
SwitzerlandJune 2026 to June 2027
-  **GRC Product of the Year** Risk Technology Awards 2025. The title was previously held by names such as MetricStream, SAI360 and IBM OpenPages.
-  **Leader in the SPARK Matrix 2025** Positioned as a Leader, both for GRC platforms and for IT risk management.
-  **In the GRC Landscape Report** Forrester names Swiss GRC repeatedly, so far as the only vendor from the DACH region.
-  **Rated Excellent** WirtschaftsWoche rated our third-party risk management solution "Excellent" in 2025.
 Our team Culture## Decide, do not escalate.
Decisions here are made where the expertise sits, not four levels above it. We are on first-name terms from day one, we keep paths short and agreements binding. If you have an idea, you bring it forward. If you need support, you get it, without a detour through three departments.
- Flat hierarchies and short decision paths
- Ownership from your first client project
- Asking questions counts as a strength here, not a gap
 Project work Substance## A field that does not run out.
Regulation, risk and processes in one product. If you like connecting things, you will find work here that is not exhausted after two years. Product management and engineering are in house, and artificial intelligence is part of the architecture rather than a button on the side.
- GRC, process management and contract management on one platform
- From DORA through NIS2 to the Cyber Resilience Act
- AI-native architecture instead of retrofitted features
Areas## Where you can come in.
Six areas where we are continuously looking for specialists. The current openings are further down.
- 01### Engineering
Platform, modules and interfaces. Modern web and cloud architecture, with artificial intelligence as part of the architecture rather than an add-on.
- 02### Consulting
Implementation at the client, from concept to operation. Many in the team come from audit, risk management or supervision themselves.
- 03### Solutions and Innovation
New modules, prototypes and the question of what belongs in the product next. The interface between market and engineering.
- 04### Customer Success and Support
Clients stay when they make progress. This is where an implementation turns into a long-term partnership, or does not.
- 05### Sales and Marketing
Explaining GRC without simplifying it. Demanding, because the people on the other side are experts themselves.
- 06### Corporate
Administration, HR and finance. The part that keeps everything else running reliably.
In practical terms## Terms without small print.
- ### Working hours
40-hour week, flexible hours, working from home possible.
- ### Location
Engineering in Lucerne, a five-minute walk from the station.
- ### Training
Certified training company since 2019 for IT apprentices and ICT specialists.
- ### Pay
In line with the market and transparently justified.

Global Reach, Local Excellence## Local teams, worldwide.
Six own entities instead of a sales network. For you that means international projects, different markets and regulations, and colleagues across time zones. Plus the SWISS GRC DAY, our annual conference, carried by the whole company.
- **Lucerne**Swiss GRC AG, headquarters
- **Munich**Swiss GRC Germany GmbH
- **London**Swiss GRC UK
- **Pristina**Swiss GRC L.L.C.
- **Dubai**Swiss GRC MEA and APAC
- **Mumbai**Swiss GRC India

> "At Swiss GRC our dedicated team of experts drives technological innovation in the GRC field. Together we set new standards for governance, risk and compliance."
**Besfort Kuqi**Founder and CEO, Swiss GRC AG
How to join us## Four steps, no waiting loop.
- Step 01### Application
Your CV and a few sentences about yourself are enough. References can follow later.
- Step 02### First conversation
30 to 45 minutes, usually online. We find out together whether the direction fits.
- Step 03### Technical interview
On site in Lucerne, with the team you would work with. Substantive and open.
- Step 04### Decision
An answer within one week. Always, including when it is not a fit this time.
Open roles## Find your role.
What is currently open. If nothing fits, a proactive application is expressly welcome.
### Proactive application
If none of the openings fit, a proactive application is expressly welcome. Send us your CV and tell us what you would like to work on, and we will get back to you.
[Apply proactively](https://swissgrc.com/en/job/unsolicited-application/)
---
### [News](https://swissgrc.com/fr/news/)
**Published:** décembre 13, 2022
**Author:** superadmin
---
### [Webinars](https://swissgrc.com/fr/webinars/)
**Published:** février 7, 2023
**Author:** superadmin
**Content:**
# Webinars
Our knowledge for you
- - All
- Upcoming
- Replay
août 5, 2026

#### Upcoming WEBINAR
#### Information Isn’t Intelligence: Connecting the Dots in Third-Party Risk
Data tells you what happened. Connected intelligence tells you what matters. Join us for the exclusive introduction of the new Swiss GRC Third-Party Intelligence Center (TPIC).
[To the Webinar](https://events.teams.microsoft.com/event/28eec8ec-d8aa-4563-ae4a-cc173be51c1e@e19b35f4-f7ad-4fe9-a202-26aeb3f7adb1)
juillet 7, 2026


#### Replay WEBINAR
Recording
#### Modern approaches to risk quantification: How stochastics and simulation make the future tangible
How can risks be made tangible and well-informed decisions be made in the face of uncertainty? Find out more in our webinar on risk quantification.
[To the Webinar](https://events.teams.microsoft.com/event/a18cb3ff-5047-4ffb-aeb5-9bfe9d879c3e@e19b35f4-f7ad-4fe9-a202-26aeb3f7adb1)
décembre 10, 2025

#### Replay WEBINAR
Recording
#### Harmonizing Governance and Risk across NEQSOL Holding with Swiss GRC
During this webinar, Samir Karimov, Head of Risk Management and Sustainability at NEQSOL Holding, will offer an inside look at how the Group built a modern GRC system with Swiss GRC.
[To the Webinar](https://events.teams.microsoft.com/event/432cc9f8-02f5-47cb-978d-b04e4c9ec1eb@e19b35f4-f7ad-4fe9-a202-26aeb3f7adb1)
Page1[Page2](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=2)[Page3](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=3)[Page4](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=4)[](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=2)
### Get the latest news & updates
## Subscribe to our newsletter now
Stay up to date on news and trends in Governance, Risk & Compliance (GRC) with our newsletter. We inform you monthly about current topics, events such as the SWISS GRC DAY and exciting professional articles.
[ Subscribe ](https://swissgrc.com/en/newsletter)
---
### [Blog](https://swissgrc.com/fr/blog/)
**Published:** décembre 14, 2022
**Author:** superadmin
**Content:**
# Swiss GRC Blog
Current blog and technical articles about Governance, Risk & Compliance
## Most read

[ How do you report risks to your board? ](https://swissgrc.com/fr/risk-quantification-how-do-you-report-risks-to-your-board/)
## [ How do you report risks to your board? ](https://swissgrc.com/fr/risk-quantification-how-do-you-report-risks-to-your-board/)
• 11 juin 2026
Risk is usually reported in the language of risk professionals. Sometimes as a heat map that is hard to draw a firm conclusion from. Sometimes as a quantitative analysis, full of distributions and metrics that almost no one in the room truly reads. Neither is wrong. It simply is not the language a board decides in. More often than not, it is not the quality of the numbers. The report answered a question the board never actually asked.
[Read more](https://swissgrc.com/fr/risk-quantification-how-do-you-report-risks-to-your-board/)
[
](https://swissgrc.com/fr/three-lines-one-picture-three-lines-model-iia-guidance/)### [ Three Lines, One Picture: What the New Three Lines Model Changes ](https://swissgrc.com/fr/three-lines-one-picture-three-lines-model-iia-guidance/)
3 septembre 2026
The revised IIA statements of 2026 do not shift responsibility away from the first line, which continues to own and
[ Read more ](https://swissgrc.com/fr/three-lines-one-picture-three-lines-model-iia-guidance/)
[
](https://swissgrc.com/fr/business-continuity-plan-crisis-handover/)### [ Where the Business Continuity Plan Hands Off to the Crisis ](https://swissgrc.com/fr/business-continuity-plan-crisis-handover/)
2 septembre 2026
The handover between a documented business continuity plan and operational crisis management usually does not fail because a plan is
[ Read more ](https://swissgrc.com/fr/business-continuity-plan-crisis-handover/)
[
](https://swissgrc.com/fr/24-hours-to-report-internal-decision-makers/)### [ 24 Hours to Report: Who Needs to Be Part of the Internal Decision ](https://swissgrc.com/fr/24-hours-to-report-internal-decision-makers/)
1 septembre 2026
From 11 September 2026, Article 14 of the Cyber Resilience Act requires an early warning within 24 hours of becoming
[ Read more ](https://swissgrc.com/fr/24-hours-to-report-internal-decision-makers/)
## All Blog posts

[ Three Lines, One Picture: What the New Three Lines Model Changes ](https://swissgrc.com/fr/three-lines-one-picture-three-lines-model-iia-guidance/)
### [ Three Lines, One Picture: What the New Three Lines Model Changes ](https://swissgrc.com/fr/three-lines-one-picture-three-lines-model-iia-guidance/)
[superadmin](https://swissgrc.com/fr/author/superadmin/)
• 3 septembre 2026
• [Regulation & Supervision](https://swissgrc.com/fr/category/regulation-supervision/)
The revised IIA statements of 2026 do not shift responsibility away from the first line, which continues to own and manage risk. They do, however, require closer coordination and documented safeguards wherever internal audit takes on second line tasks or contributes to the five ERM activities of identifying, assessing, managing, monitoring and reporting, without making risk decisions itself.

[ Where the Business Continuity Plan Hands Off to the Crisis ](https://swissgrc.com/fr/business-continuity-plan-crisis-handover/)
### [ Where the Business Continuity Plan Hands Off to the Crisis ](https://swissgrc.com/fr/business-continuity-plan-crisis-handover/)
[superadmin](https://swissgrc.com/fr/author/superadmin/)
• 2 septembre 2026
• [Regulation & Supervision](https://swissgrc.com/fr/category/regulation-supervision/)
The handover between a documented business continuity plan and operational crisis management usually does not fail because a plan is missing, but because of shift changes and role handovers in the crisis team that classic tests rarely simulate. Regulatory requirements such as FINMA Circular 2023/1 do require tests based on severe but plausible scenarios, but these primarily verify that a plan exists, not whether the organisation can actually act under time pressure.

[ 24 Hours to Report: Who Needs to Be Part of the Internal Decision ](https://swissgrc.com/fr/24-hours-to-report-internal-decision-makers/)
### [ 24 Hours to Report: Who Needs to Be Part of the Internal Decision ](https://swissgrc.com/fr/24-hours-to-report-internal-decision-makers/)
[superadmin](https://swissgrc.com/fr/author/superadmin/)
• 1 septembre 2026
• [Regulation & Supervision](https://swissgrc.com/fr/category/regulation-supervision/)
From 11 September 2026, Article 14 of the Cyber Resilience Act requires an early warning within 24 hours of becoming aware of an actively exploited vulnerability, submitted simultaneously to the competent CSIRT and to ENISA. To meet this deadline, CSIRT assignment, named primary and secondary contacts with a backup rule, and internal triage must already be established before an incident occurs.
1[2](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=2)[3](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=3)…[20](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=20)[ »](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=2)
---
### [Customer Stories](https://swissgrc.com/fr/customer-stories/)
**Published:** décembre 23, 2023
**Author:** Yahya Mohamed Mao
**Content:**
### Customer Stories
# Find out why leading companies rely on our solutions

## See all customer stories
#### Filter by
-
- [Reset filters](#)
- #### Industry
- Automobile
- Education
- Energy
- Financial Services
- Healthcare
- Industry & Trade
- Insurance
- Media
- NPO
- Other services
- Public Sector
- Real Estate
- Technology
- Transportation & Logistics
- #### Solutions
- Business Continuity Management (BCM)
- Business Process Modelling (BPM)
- Compliance
- Contract Management
- Data Protection Management
- Information Security (ISMS)
- Internal Control System (ICS)
- Risk Management
- Third-Party Risk Management (TPRM)
[  ](https://swissgrc.com/fr/success_story/modernizing-risk-management-at-ib-langenthal-ag/)

##### [Modernizing Risk Management at IB Langenthal AG](https://swissgrc.com/fr/success_story/modernizing-risk-management-at-ib-langenthal-ag/)
Energy
[  ](https://swissgrc.com/fr/success_story/benefits-journey-to-combined-assurance-with-swiss-grc/)

##### [BENEFIT’s Journey to Combined Assurance with Swiss GRC](https://swissgrc.com/fr/success_story/benefits-journey-to-combined-assurance-with-swiss-grc/)
Financial Services
[  ](https://swissgrc.com/fr/success_story/system-supported-and-cross-functional-risk-management-at-visana-with-swiss-grc/)

##### [System-Enabled, Cross-Functional Risk Management at Visana with Swiss GRC](https://swissgrc.com/fr/success_story/system-supported-and-cross-functional-risk-management-at-visana-with-swiss-grc/)
Insurance
[  ](https://swissgrc.com/fr/success_story/integrated-risk-and-business-continuity-management-at-zurich-university-hospital/)

##### [Integrated Risk and Business Continuity Management at Zurich University Hospital](https://swissgrc.com/fr/success_story/integrated-risk-and-business-continuity-management-at-zurich-university-hospital/)
Healthcare
[  ](https://swissgrc.com/fr/success_story/harmonizing-governance-and-risk-across-neqsol-holding-with-swiss-grc/)

##### [Harmonizing Governance and Risk across NEQSOL Holding](https://swissgrc.com/fr/success_story/harmonizing-governance-and-risk-across-neqsol-holding-with-swiss-grc/)
Energy
Technology
[  ](https://swissgrc.com/fr/success_story/paul-scherrer-institute-psi-strengthens-risk-and-control-management-with-swiss-grc/)

##### [Paul Scherrer Institute (PSI) strengthens Risk and Control Management with Swiss GRC](https://swissgrc.com/fr/success_story/paul-scherrer-institute-psi-strengthens-risk-and-control-management-with-swiss-grc/)
Education
Public Sector
Page1[Page2](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=2)[Page3](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=3)[](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=2)
### GET THE LATEST NEWS & UPDATES
## Subscribe to our newsletter now
Stay up to date on news and trends in Governance, Risk & Compliance (GRC) with our newsletter. We inform you monthly about current topics, events such as the SWISS GRC DAY and exciting professional articles.
[ Subscribe ](https://swissgrc.com/newsletter)
---
### [Clients](https://swissgrc.com/fr/clients/)
**Published:** décembre 20, 2022
**Author:** superadmin
**Content:**
### REFERENCES
# Our clients
Below, we present a selection of references. Companies from all over the world rely on our solutions and our know-how. You too can put your trust in Swiss GRC, just like many other satisfied companies.
All
Automotive
Education
Energies
Banks & Financial Services
Healthcare
Real Estate
Industry & Trade
NPO
Public Sector
Technology
Transportation & Logistics
Insurances
Others
All



































































Automotive



Education




Energies







Banks & Financial Services























[](https://www.ajil.com/)
[](https://www.creditreform.de/)
[](https://gscbank.co.in/)
[](https://www.bybit.com/)


[](https://www.faisalbank.com.eg/en/)
Healthcare





Real Estate


Industry & Trade










NPO


Public Sector












Technology











[](https://www.netcetera.com/de/home.html)
[](https://www.azerconnect.az/)
[](https://www.vodafone.ua/en)
[](https://www.bakcell.com/en)

[](https://www.crif.ch/)
[](https://www.eraneos.com/ch/ch/)
[](https://www.caisseavsvaud.ch/)
[](https://www.psideo.com/CommunityPortal/ProgressivePortal/PSIDEO_3/App/Views/InformationPage/View.aspx?informationpageid=906)
Transportation & Logistics


Insurances




































Others





---
### [Partner](https://swissgrc.com/fr/partner/)
**Published:** février 3, 2023
**Author:** superadmin
**Content:**
Partner programme# Partnerships that move
both sides forward.
For **Swiss GRC**, partner management is the foundation of business development. We build long term relationships that rest on openness, collaboration and mutual economic benefit. From technology and data through consulting and implementation to sales.
[Become a partner](https://swissgrc.com/en/sales/) [The five partner types](#types)
*What you bring*- Market access and knowledge of your industry
- Subject matter or technical expertise in GRC
- Commitment over years rather than a one off deal
*What we bring*- Commission on licence revenue, graded by tier
- Training, certification and a demo environment of your own
- Joint marketing and qualified enquiries
Core principles## What our partnerships
are built on.
Three principles we settle before any collaboration begins and measure it against later on.
### Openness
We are open about how we work, what we expect and how a collaboration will be measured. **Maximum transparency, respect, honesty and integrity.** That is what we offer, and what we expect from our partners in return.
### Collaboration
Joint events and webinars, talks and workshops on each other’s stages, articles written together and reference visits. **We run marketing and business development together**, not side by side.
### Mutual benefit
A partnership only holds if it pays off economically for both sides. That is why we **put roles, services and remuneration in writing from the start**, instead of settling them mid project.
**Five types of partnership, combinations expressly possible.** Many of our partners advise, implement and refer at the same time.
[Types in detail ](#types)
Partner types## Five ways to work
together with us.
Select the role that fits you. Depending on how closely we work together, different terms and requirements apply.
**Technology partner***Building together* 01 **Data provider***Data and insight* 02 **Consulting partner***Subject matter guidance* 03 **Implementation partner***Technical delivery* 04 **Sales partner***Selling across five tiers* 05
Building together### Technology partner
We build solutions together. This is about **innovative technology or entire software modules** that are integrated into the Swiss GRC solutions and taken to market with them. Two products become one that the customer experiences as a whole.
*Requirements* Technological and strategic fitInnovation and future readinessScalabilityIndependence
Data and insight### Data provider
We use data, or data together with the insight drawn from it, in development and in the market. **Your content reaches our customers’ GRC processes at the point where decisions are made**, instead of sitting in a separate portal.
*Requirements* Depth and breadth of the dataUniqueness of the insightTechnological and strategic fit
Subject matter guidance### Consulting partner
You contribute **subject matter resources and know how to rollout projects** and guide customers on content, alongside the technical implementation by our team. Method and industry understanding come from you, the platform from us.
*Requirements* Industry knowledge and subject matter expertiseRegular certificationTechnical understanding an advantage
Technical delivery in your own hands### Implementation partner
You take responsibility for the **independent technical implementation** of the Swiss GRC solutions and for running the rollout projects. The path there is defined: through the training blocks up to the certificate with exam. On your first independent implementation we take on at least 20 per cent of the work alongside you.
*Requirements* Sound technical skillsExperience with complex rollout projectsRegular technical certificationIndustry knowledge an advantage
[To the certification path ](#certification)
Selling across five tiers### Sales partner
The range is wide: from a simple referral all the way to a collaboration in which you run the entire sales cycle, deliver the rollout project including consulting on your own, and take responsibility for support and account management. **For a successful referral we pay a commission on licence revenue**, graded by tier.
*Requirements* A strong network in the industryExperience and subject matter expertisePresales or technical certification, depending on the tier
[View the five tiers ](#tiers)
Combinations of these partnerships are possible and, in practice, the norm.
Partner tiers## From referral partner
to gold partner.
With every tier you take on more of the sales cycle and receive more of the return. The table below shows what each tier includes.
**Less responsibility****More responsibility, more commission**
*Tier 1***Referral partner**You refer us on.
*Tier 2***Sales partner tier 1**Plus sales presentations.
*Tier 3***Sales partner tier 2**Plus presales workshops.
*Tier 4***Silver partner**Plus the implementation.
*Tier 5***Gold partner**Plus support and account management.
Select a tier
Referral Tier 1 Tier 2 Silver Gold
Partner tier
Referral partner
Sales partner tier 1
Sales partner tier 2
Silver partner
Gold partner
Steps in the sales cycle
Referral
Sales presentations
Presales workshops
Implementation
Support
Account Management
Certification
Requirement
None
None
Presales
Presales and technical
Presales and technical
**Commission on licence revenue rises with the tier**, and from silver upwards it also applies to renewals of existing licence agreements. We set the actual rates and your tier in a personal conversation, to match your market, your role and the volume you plan for.
[Discuss terms](https://swissgrc.com/en/sales/)
Our support## What Swiss GRC brings
to the partnership.
Nine services along the three phases of the partner business. Available from day one, not only above a certain revenue.
**1***Phase one*### Create demand
Before anything is sold, the market needs to know us both.
#### Marketing
Joint campaigns, webinars, articles and press releases. Material that carries your name, not only ours.
#### Lead generation
Qualified enquiries from our channels, passed on to the partner who knows the market best.
#### Events
At the SWISS GRC DAY and at other occasions, partners come first when it comes to stage time and exhibition space.
**2***Phase two*### Sell together
In the customer meeting we sit on the same side of the table.
#### Sales and presales
Our specialists join you in the meeting, from the first conversation through to the tender.
#### Sales enablement
Positioning, objection handling and pricing logic for your sales team, with material ready to use.
#### References and demo
Access to reference customers in your industry and a demo environment of your own after the first certification.
**3***Phase three*### Deliver successfully
A project that holds is the best reference for the next one.
#### Training and certification
Five training blocks that build on each other, from the product introduction to the expert certification.
#### Software implementation
We implement together with you, for as long as it takes until you want to and can take over yourself.
#### Project management
Experienced project leadership drawn from more than 500 completed projects, as a safeguard for your first rollouts.
Certification## Five blocks to your own
implementation.
The path from first product knowledge to independent rollout is laid down. At any point you know what the next step brings.
1. ### Product training, basics
Out of the box solutionUse casesBenchmarks
*Delivered by*GRC consultants or presales
2. **Certificate**Personal access to a demo environment. You run your sales demos yourself.
3. ### Admin training, basic
Lists and viewsFormsUser administrationNavigationImport and exportAssessmentsCustomising guidelines
*Delivered by*Solution consultants
4. **Certificate**You accompany a technical implementation alongside our team.
5. ### Admin training, advanced
Permissions at list levelPermissions at item levelAction planner
*Delivered by*Solution consultants
6. ### Admin training, reporting
DashboardsReports
*Delivered by*Solution engineers
7. ### Admin training, expert
Underlying conceptsWorkflowsForm logic
*Delivered by*Solution engineers
8. **Certificate with exam**You carry out implementations independently. On the first one, Swiss GRC takes on at least 20 per cent of the work.
Our partners## Who already
works with us.
Technology providers, data providers, consultancies, implementation partners and a university. Across Europe, the Middle East and Asia.
Aamin Data
Acons Governance & Audit
Alpha DS
BitSight
CAAS
CRIF
Cybrius
Eraneos Switzerland
Lucerne University
iExperts
Natural Group
Prospero
Refocus
SAM Corporate
SecurityScorecard
Spitch
StorIT
Swiss Infosec
Synesgy
Tjdeed Technology
Partner programme## Let us talk about
the right form.
Tell us which market and which role you are strong in. We will propose the type of partnership and the tier that fits, and put services and terms in writing.
[Become a partner](https://swissgrc.com/en/sales/)
---
### [Newsletter on Governance, Risk & Compliance](https://swissgrc.com/fr/newsletter/)
**Published:** novembre 7, 2023
**Author:** superadmin
**Content:**
Swiss GRC Newsletter
# The newsletter for Governance, Risk and Compliance.
Webinars, events such as the Swiss GRC Day, the latest news and practical know-how from the world of Governance, Risk and Compliance. Kept concise and delivered straight to your inbox.
Webinars Events News Insights
## Subscribe to our newsletter
Fields marked with \* are required. We treat your information confidentially.
First Name \*
Last Name \*
Business Email \*
Company \*
Job Title \*
I agree to the [privacy policy](https://swissgrc.com/en/privacy-policy/).
Subscribe now You can unsubscribe at any time by clicking on the link in the footer of our emails. You can find information on our data protection practices in our [privacy policy](https://swissgrc.com/en/privacy-policy/).
We use Mailchimp as our marketing platform. By clicking below to subscribe, you acknowledge that your information will be transferred to Mailchimp for processing. Learn more about Mailchimp's [privacy practices](https://mailchimp.com/legal/terms).
### Almost there.
Please confirm your subscription using the link we just sent to your inbox.
---
### [Discovery Call Booking Page](https://swissgrc.com/fr/discoverycall/)
**Published:** février 1, 2024
**Author:** superadmin
**Content:**
Discovery Call# In 15 minutes, you'll know whether *Swiss GRC* is right for you.
In a short, no-obligation call we get to know your organisation, show you the modules and standards that matter most to you, and agree on the right next step together.
15 minutes
· Free
· No obligation
Prefer to talk directly? [ sales@swissgrc.com](mailto:sales@swissgrc.com) [ +41 41 220 75 00](tel:+41412207500)
Loading calendar ...
Calendar not showing? Open the booking page in a new window:
[ Open ](https://outlook.office.com/book/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/?ismsaljsauthenabled) [ Contact ](https://swissgrc.com/en/contact/)
## Trusted by leading organisations worldwide.
Public authorities, banks, insurers and industry run governance, risk and compliance on
Swiss GRC.
0
Customers across every industry
0
Successful customer projects across industries and topics
0
GRC Toolbox users across governance, risk & compliance
---
### [Contact](https://swissgrc.com/fr/contact/)
**Published:** décembre 20, 2022
**Author:** superadmin
**Content:**
# Contact us.
Have questions? Fill in our contact form and we will forward your request to the right person as quickly as possible. You can also reach us by phone or email. We look forward to hearing from you.
General contact
[ office@swissgrc.com](mailto:office@swissgrc.com) [ +41 41 220 75 00](tel:+41412207500)
Sales
[ sales@swissgrc.com](mailto:sales@swissgrc.com) [ +41 41 220 75 00](tel:+41412207500)
Press & Media
[ marketing@swissgrc.com](mailto:marketing@swissgrc.com) [ +41 41 220 75 15](tel:+41412207515)
Events
[ events@swissgrc.com](mailto:events@swissgrc.com) [ +41 41 220 75 15](tel:+41412207515)
Customer Support
[ support@swissgrc.com](mailto:support@swissgrc.com) [ +41 41 220 75 00](tel:+41412207500)
## Write to us
Fields marked with \* are required. We treat your information confidentially.
First name \*
Last name \*
Email \*
Company \*
Your request \*Please selectGeneral enquirySalesPress & MediaEventsCustomer SupportOther
Your message \*
I agree to the [Privacy Policy](https://swissgrc.com/fr/privacy-policy/).
## Local teams, worldwide.
Six locations across Switzerland, Europe, the Middle East and Asia.
**Lucerne**Headquarters
Swiss GRC AG
Hirschmattstrasse 366003 LucerneSwitzerland
**Munich**
Swiss GRC Germany GmbH
Karlsplatz 380335 MunichGermany
**London**
Swiss GRC UK
167-169 Great Portland StreetLondon W1W 5PFEngland
**Dubai**
Swiss GRC MEA/APAC
Building 5, Ground FloorDubai Media CityDubaiUnited Arab Emirates
**Mumbai**
Swiss GRC India
Unit No. B-501/A, 5th Floor, B-WingSupreme Business ParkMumbai 400076India
**Pristina**
Swiss GRC L.L.C.
Rruga e Tiranes10000 PristinaKosovo
---
### [Whitepaper: Modern Contract Lifecycle Management: Driving Value and Compliance](https://swissgrc.com/fr/whitepaper-clm/)
**Published:** février 23, 2026
**Author:** Yahya Mohamed Mao
**Content:**
Download Whitepaper
## Modern Contract Lifecycle Management
Driving Value and Compliance

First Name\*
Last Name\*
Company\*
Job Title\*
Business Email\*
By clicking the button below, you consent to Swiss GRC storing and processing your personal information to provide the requested content and to contact you about our products. For details, see our [Privacy Policy.](https://swissgrc.com/fr/privacy-policy/)
Download Whitepaper
## Modern Contract Lifecycle Management
Driving Value and Compliance

First Name\*
Last Name\*
Company\*
Job Title\*
Business Email\*
By clicking the button below, you consent to Swiss GRC storing and processing your personal information to provide the requested content and to contact you about our products. For details, see our [Privacy Policy.](https://swissgrc.com/fr/privacy-policy/)
---
### [GCC GRC DAY](https://swissgrc.com/fr/gccgrcday/)
**Published:** avril 26, 2024
**Author:** Yahya Mohamed Mao
**Content:**

## UAE Edition
# GCC GRC DAY
# 2025
## 20 November 2025
## Address Sky View Dubai
#### 08:30 AM - 3:00 PM
[ Register now ](#register)
[ Sponsoring ](#partners)
[ Twitter ](https://twitter.com/swissgrc) [ Linkedin-in ](https://ch.linkedin.com/company/swissgrc) [ Youtube ](https://www.youtube.com/channel/UCy4QuXYekCQrA4n5oEwJSJg) [ Instagram ](https://www.instagram.com/swissgrc/)
### [EVENT OVERVIEW](#overview)
### [SPEAKERS](#speakers)
### [AGENDA](#agenda)
### [PARTNERS](#partners)
### [REGISTRATION](#register)
### [REVIEW 2024](https://swissgrc.com/en/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/)
## Secure your spot now!
The GCC GRC DAY 2025 starts in
Jours
Heures
Minutes
Secondes
Swiss GRC is once again bringing its renowned governance, risk, and compliance conference to Dubai. The **GCC GRC DAY**, taking place on **20 November 2025 at Address Sky View Dubai** is set to be a landmark event for GRC leaders and professionals across the GCC region.
This year’s edition introduces a powerful media collaboration with **Khaleej Times**, extending the reach of conference insights across the region. Attendees will gain exclusive access to cutting-edge strategies, proven best practices, and thought leadership shaping the future of governance, risk, and compliance.
Don’t miss the opportunity to connect with peers, expand your professional network, and play an active role in shaping resilient, future-ready organizations. Participation is free of charge, but registration is mandatory.
## Event Overview
GRC professionals from across the GCC region will come together for a pivotal conference, uniting thought leaders, seasoned experts, and industry practitioners to delve into the multifaceted world of governance, risk, and compliance (GRC). This event offers a unique opportunity to network, share insights, and explore the latest developments, fostering a collaborative approach to tackle the challenges of an evolving business landscape, integrating technology, strategic planning, and regulatory demands.
## Topics
- Corporate Management
- Risk Management
- Internal Controls (ICS)
- Cybersecurity & Data Protection
- Business Continuity & Resilience
- Compliance Management
- Environmental, Social & Governance (ESG)
- Third-Party Risk Management
- Artificial Intelligence (AI)
- Operational Efficiency
- Regulatory Technology (RegTech)
## Target Audience
Among the participants are:
- **Governance & Compliance:** Compliance Officer, Head of Governance, Paralegals.
- **Risk Management:** Risk Controllers, Managers, Information Security Officers.
- **IT & Cybersecurity:** Cybersecurity Consultants, IT Security Officers, CISOs.
- **Business Continuity:** BCM Managers, Emergency Specialists.
- **Audit & Control:** Internal Auditors, ICS Managers.
- **Executives:** Board Members, CEOs, CFOs, CIOs, COOs, etc.
## Welcome Address

Besfort Kuqi
### Founder & CEO, Swiss GRC
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjM5MDMiLCJ0b2dnbGUiOmZhbHNlfQ%3D%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjM5MDMiLCJ0b2dnbGUiOmZhbHNlfQ%3D%3D)

## Speakers
### Visionaries shaping the future of GRC

Dallal Slimani
### Senior Vice President Programs & Transformation, Schneider Electric
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDY1IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDY1IiwidG9nZ2xlIjpmYWxzZX0%3D)


Akshay Dalal
### Head of Regional Risk & Compliance - Middle East, Turkey & Africa at Google

[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTIzIiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTIzIiwidG9nZ2xlIjpmYWxzZX0%3D)

Ricardo Vasconcelos Dias
Senior Director, Enterprise Risk Management, e& Risk & Assurance
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MjEwIiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MjEwIiwidG9nZ2xlIjpmYWxzZX0%3D)


Maram Habash
### Executive Vice President, Head Operational Risk & Resilience, Mashreq
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDc2IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDc2IiwidG9nZ2xlIjpmYWxzZX0%3D)


Dr. Ebrahim Al Alkeem
National Risk & Policies Director, AML & CTF, UAE Government
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDk1IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDk1IiwidG9nZ2xlIjpmYWxzZX0%3D)


Samir Karimov
Head of Risk Management and Sustainablity, NEQSOL Holding
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDcxIiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDcxIiwidG9nZ2xlIjpmYWxzZX0%3D)


Dr. Sona Saha Dash
### Data Strategy Governance & Analytics Lead, Confidential Government Entity KSA
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDkwIiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDkwIiwidG9nZ2xlIjpmYWxzZX0%3D)

Fadi El Bouz
Director of Internal Audit & Risk Department, Sunbulah Group
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjQzNzA0IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjQzNzA0IiwidG9nZ2xlIjpmYWxzZX0%3D)


Rajeev Dutt
### General Manager MEA & APAC,
Swiss GRC
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTM0IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTM0IiwidG9nZ2xlIjpmYWxzZX0%3D)


Adnan Ibrahim Alhashmi
### Senior Associate Operations Manager, Tawazun Council for Defence Enablement
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1NDIyIiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1NDIyIiwidG9nZ2xlIjpmYWxzZX0%3D)


Nikolai Tsenov
### Head Solutions & Innovation,
Swiss GRC
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTI3IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTI3IiwidG9nZ2xlIjpmYWxzZX0%3D)


Oma Martins
### Group Head of IT GRC, IHS Towers
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1NDI3IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1NDI3IiwidG9nZ2xlIjpmYWxzZX0%3D)


Laura Roche
### Emcee & Moderator
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MjUwIiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MjUwIiwidG9nZ2xlIjpmYWxzZX0%3D)
## Panelists
### Conversations that drive perspective

Lt. Col. Saeed M. AlShebli
### Deputy Director – Digital Security Department, Ministry of Interior UAE
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTE1IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTE1IiwidG9nZ2xlIjpmYWxzZX0%3D)


Mansoor AlAlwan
Chief Audit Executive,
The BENEFIT Company
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDg1IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDg1IiwidG9nZ2xlIjpmYWxzZX0%3D)


Hessa Humaid Almatrooshi
Information Security Leader, Free Zones Authority of Ajman
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0ODgxIiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0ODgxIiwidG9nZ2xlIjpmYWxzZX0%3D)


Rohit Bajpai
### Head of Internal Audit, Gulf Islamic Investments Group
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTE5IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU0OTE5IiwidG9nZ2xlIjpmYWxzZX0%3D)


Prof. Dr. Hossam AlShenraky
### Head of the Police Management Department, Dubai Police Academy
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDAzIiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MDAzIiwidG9nZ2xlIjpmYWxzZX0%3D)


Faisal Khan
### Director of Information Security, Risk Management & Regulatory Compliance, Dubai World Trade Centre
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MTAzIiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MTAzIiwidG9nZ2xlIjpmYWxzZX0%3D)


Prof. Dr. Fatma Taher
### Professor & Assistant Dean, College of Technological Innovation, Zayed University
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MTA4IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MTA4IiwidG9nZ2xlIjpmYWxzZX0%3D)


Prince Rana
### Head of Information Security, Risk & Governance, Seddiqi Holding
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MjA0IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MjA0IiwidG9nZ2xlIjpmYWxzZX0%3D)


Hussain Al Khalsan
### Chief Information Security Officer,
Zand Bank
[ ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MjQ1IiwidG9nZ2xlIjpmYWxzZX0%3D)
[ View Bio ](#elementor-action%3Aaction%3Dpopup%3Aopen%26settings%3DeyJpZCI6IjU1MjQ1IiwidG9nZ2xlIjpmYWxzZX0%3D)

## Agenda
### A conference dedicated to Governance, Risk & Compliance (GRC)
[ Morning ](#morning)
[ Afternoon ](#afternoon)
### 8:00 – 9:00 | Registration & Networking Coffee
### 9:00 – 9:15

##### Opening Ceremony
##### Welcome Address
###### **Besfort Kuqi**
Founder & CEO, Swiss GRC
### 9:15 – 9:30

##### Opening Keynote
##### Organizational and Operational Resilience: Protecting Critical Sectors
###### **Dallal Slimani**
Senior Vice President - Programs & Transformation, Schneider Electric
### 9:30 – 9:45

##### Presentation
##### GRC in Transition: Building Resilience in Uncertain Times
###### **Rajeev Dutt**
General Manager MEA & APAC,
Swiss GRC
### 9:45 – 10:00

##### Keynote
##### AI Governance & Ethical Risk Management: Balancing Innovation with Accountability
###### **Akshay Dalal**
Head of Regional Risk & Compliance - Middle East, Turkey & Africa, Google
### 10:00 – 10:40

##### Panel Discussion
##### Guardians of Trust: Security, Regulation & Privacy by Design
###### **Faisal Khan**, Associate Director - Information Security & Compliance,
Dubai World Trade Centre
###### **Hessa Humaid Almatrooshi**, Information Security Leader, Free Zones Authority of Ajman
###### **Lt. Col. Saeed M. AlShebli**, Deputy Director – Digital Security Department, Ministry of Interior, UAE
###### **Hussain Al Khalsan**, Chief Information Security Officer, Zand Bank
###### **Oma Martins**, Group Head of IT GRC, IHS Towers
###### **Mansoor AlAlwan**, Chief Audit Executive, The BENEFIT Company
### 10:40 – 10:55

##### Spotlight
##### Combined Assurance: Delivering Enterprise-Wide Risk Insight and Value
###### **Adnan Ibrahim Alhashmi**,
Senior Associate Operations Manager, Tawazun Council for Defence Enablement
### 11:00 – 11:30 | Networking Coffee Break
### 11:30 – 11:45

##### Presentation
##### Risk as a Source of Confidence
###### **Samir Karimov**
Head of Risk Management and Sustainablity, NEQSOL Holding
### 11:45 – 12:25

##### Panel Discussion
##### Bridging Academia & Practice: Elevating GRC Dialogue in the GCC
###### **Nikolai Tsenov**, Head Solutions & Innovation, Swiss GRC
###### **Prof. Dr. Fatma Taher**, Professor & Assistant Dean, Zayed University
###### **Prof. Dr. Hossam Alshenraky**, Head of the Police Management Department, Dubai Police Academy
###### **Dr. Ebrahim Al Alkeem** , National Risk & Policies Director, UAE Government
###### **Rohit Bajpai**, Head of Internal Audit, Gulf Islamic Investments Group
### 12:25 – 12:35

##### Sponsor Session
##### Mindfire Technologies
###### **Rejeesh Kumar**
Chief Technology Officer, Mindfire Technologies
### 12:35 – 12:55

##### Spotlight
##### From Oversight to Insight: The Transformative Role of Internal Audit
###### **Fadi Bouz**
Director of Internal Audit & Risk Department, Sunbulah Group
### 12:55 – 13:30

##### Fireside Chat
##### Risk Leadership & Organizational Culture: Tone at the Top
###### **Ricardo Vasconcelos Dias**, Senior Director, Enterprise Risk Management,
e& Risk & Assurance
###### **Maram Habash**, Executive Vice President, Head Operational Risk & Resilience, Mashreq
###### **Dr. Sona Saha Das**, Data Strategy Governance & Analytics Lead, Ceer Motors
###### **Prince Rana**, Head of Information Security, Risk & Governance, Seddiqi Holding
### 13:30 – 13:50

##### Closing Keynote
##### Leading Through the Unknown
###### **Nikolai Tsenov**
Head Solutions & Innovation,
Swiss GRC
### 14:00 – 15:00 | Luncheon & End of Summit
Download PDF
## Partner with us
The GCC GRC DAY provides a distinguished platform to engage with the latest developments, proven strategies, and innovative approaches in governance, risk, and compliance. Participants will benefit from the expertise of leading professionals through keynote presentations and interactive discussions, gaining both strategic insights and practical guidance.
Sponsorship offers organizations the opportunity to strengthen brand visibility and reputation while generating qualified business leads. As one of the region’s premier industry gatherings, the GCC GRC DAY delivers an exceptional platform for thought leadership, professional networking, and sustainable business growth.

[ Contact us ](mailto:events@swissgrc.com)
## Powered by
## Organised by
[  ](https://www.swissgrc.com/)
[  ](https://khaleejtimesevents.com/)
## Sponsors
## GOLD PARTNERS
[  ](https://mindfireit.com/)
## SILVER PARTNERS
[  ](https://aamindata.com/)
[  ](https://storit.ae/)
[  ](https://www.intertecsystems.com/)
## BRONZE PARTNERS
[  ](https://tjdeed.com/)
[  ](https://www.alphads.net/)
[  ](https://www.promatas.com/)
## KNOWLEDGE PARTNER
[  ](https://engage.isaca.org/uaechapter/home)
A perfect platform for exchanging best practices and making new contacts. The GCC GRC DAY exceeded my expectations in every respect.
I leave this day with a backpack full of new ideas and solutions for our GRC strategy. A big thank you to the Swiss GRC organization team!
An excellently organized conference with a perfect blend of expertise, networking, and inspiration.
The Apéro Riche was the perfect way to round off an informative day. The opportunity to chat with industry colleagues in a relaxed atmosphere was priceless.
An indispensable event for anyone who wants to be at the forefront of governance, risk, and compliance.
## Impressions


## Register now for GCC GRC DAY 2025!
[ Register now ](#kontakt)
## 300+ Teilnehmende aus führenden Unternehmen



## Past events
[
](https://swissgrc.com/fr/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/)### [ GCC GRC Day 2024: Navigating the Complexities of GRC in the Middle East ](https://swissgrc.com/fr/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/)
27 mai 2024
The GCC GRC DAY 2024 brought together leading industry experts who engaged in rich discussions about the most pressing GRC challenges, sharing insights and strategies to effectively navigate the complex landscape of governance, risk and compliance (GRC).
[ Read more ](https://swissgrc.com/fr/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/)
# Registration
**GCC GRC DAY 2025**
## Complete the form
and save your spot now!
### +971 50 728 7247
### events@swissgrc.com
**Address Sky View**
Emaar Square Area
Downton Dubai
Dubai
United Arab Emirates
[ Twitter ](https://x.com/swissgrc) [ Linkedin ](https://www.linkedin.com/company/swissgrc/posts/?feedView=all) [ Youtube ](https://www.youtube.com/channel/UCy4QuXYekCQrA4n5oEwJSJg) [ Instagram ](https://www.instagram.com/swissgrc/)
Title\*Dr.Mr.Mrs.Ms.Prof.Prof. Dr.
Country\*AfghanistanAlbaniaAlgeriaAndorraAngolaAntigua and BarbudaArgentinaArmeniaAustraliaAustriaAzerbaijanBahamasBahrainBangladeshBarbadosBelarusBelgiumBelizeBeninBhutanBoliviaBosnia and HerzegovinaBotswanaBrazilBruneiBulgariaBurkina FasoBurundiCabo VerdeCambodiaCameroonCanadaCentral African RepublicChadChileChinaColombiaComorosCongoCosta RicaCroatiaCubaCyprusCzech RepublicDemocratic Republic of the CongoDenmarkDjiboutiDominicaDominican RepublicEcuadorEgyptEl SalvadorEquatorial GuineaEritreaEstoniaEswatiniEthiopiaFijiFinlandFranceGabonGambiaGeorgiaGermanyGhanaGreeceGrenadaGuatemalaGuineaGuinea-BissauGuyanaHaitiHondurasHungaryIcelandIndiaIndonesiaIranIraqIrelandIsraelItalyIvory CoastJamaicaJapanJordanKazakhstanKenyaKiribatiKuwaitKyrgyzstanLaosLatviaLebanonLesothoLiberiaLibyaLiechtensteinLithuaniaLuxembourgMadagascarMalawiMalaysiaMaldivesMaliMaltaMarshall IslandsMauritaniaMauritiusMexicoMicronesiaMoldovaMonacoMongoliaMontenegroMoroccoMozambiqueMyanmarNamibiaNauruNepalNetherlandsNew ZealandNicaraguaNigerNigeriaNorth MacedoniaNorwayOmanPakistanPalauPalestinePanamaPapua New GuineaParaguayPeruPhilippinesPolandPortugalQatarRomaniaRussiaRwandaSaint Kitts and NevisSaint LuciaSaint Vincent and the GrenadinesSamoaSan MarinoSao Tome and PrincipeSaudi ArabiaSenegalSerbiaSeychellesSierra LeoneSingaporeSlovakiaSloveniaSolomon IslandsSomaliaSouth AfricaSouth KoreaSouth SudanSpainSri LankaSudanSurinameSwedenSwitzerlandSyriaTaiwanTajikistanTanzaniaThailandTimor-LesteTogoTongaTrinidad and TobagoTunisiaTurkeyTurkmenistanTuvaluUgandaUkraineUnited Arab EmiratesUnited KingdomUnited StatesUruguayUzbekistanVanuatuVatican CityVenezuelaVietnamYemenZambiaZimbabwe
I agree with the [privacy policy](https://swissgrc.com/fr/privacy-policy/)
---
### [Media Search](https://swissgrc.com/fr/media-search/)
**Published:** août 16, 2024
**Author:** Gent Krasniqi
**Content:**
Media Search Screening
# Conduct media analyses, identify risks early on
Powered by Prospero technology and seamlessly integrated with a next generation sanction screening, our media search solution provides high quality insights uncovering hidden connections, risks, and threats in a timely and forward-looking manner.
[ Contact us ](#Contact)

Media Search Screening
## NextGen Media Analytics
Based on the most innovative technologies and groundbreaking concepts, enriched with unique optimization algorithms and Large Language Models, seamlessly integrated with world-class sanction screening, and connected to the richest range of data sources in the industry, our Media Search Screening provides you with the highest possible quality and accuracy in insights, backgrounds, hidden relationships, risks, threats, and opportunities.
[ Get started ](#Contact)
Media Search Screening
## NextGen Media Analytics
Based on the most innovative technologies and groundbreaking concepts, enriched with unique optimization algorithms and Large Language Models, seamlessly integrated with world-class sanction screening, and connected to the richest range of data sources in the industry, our Media Search Screening provides you with the highest possible quality and accuracy in insights, backgrounds, hidden relationships, risks, threats, and opportunities.

MEDIA SEARCH SCREENING
## Holistic 360° View
Detection of hidden connections to risk persons and organizations within a holistic and context driven case analysis, considering all internally and externally available information. Building, visualizing, and extracting the essence, by applying advanced Link Analysis techniques, complementing the known and official, but incomplete data, by uncovering the hidden, not yet publicly known insights. Constructing a unique in its nature puzzle of facts, filling the gaps, for better and comprehensive analysis and decision making.
[ Get started ](#Contact)
MEDIA SEARCH SCREENING
## Holistic 360° View
Detection of hidden connections to risk persons and organizations within a holistic and context driven case analysis, considering all internally and externally available information. Building, visualizing, and extracting the essence, by applying advanced Link Analysis techniques, complementing the known and official, but incomplete data, by uncovering the hidden, not yet publicly known insights. Constructing a unique in its nature puzzle of facts, filling the gaps, for better and comprehensive analysis and decision making.

MEDIA SEARCH SCREENING
## Real-Time Analysis and Insights
Whether screening of partners, subcontractors, clients, transactions, or instant payments, all these processes are directly supported and enriched with our extremely powerful real-time Media Search analysis. Helping you to make well-founded decisions and taking proactive action in a timely and forward-looking manner. It builds and integral part of our unique Dynamic Risk & Opportunity based Profiling, helping you in dynamic identification of risks, threats, and opportunities, associated to your counterparts.
[ Get started ](#Contact)
MEDIA SEARCH SCREENING
## Real-Time Analysis and Insights
Whether screening of partners, subcontractors, clients, transactions, or instant payments, all these processes are directly supported and enriched with our extremely powerful real-time Media Search analysis. Helping you to make well-founded decisions and taking proactive action in a timely and forward-looking manner. It builds and integral part of our unique Dynamic Risk & Opportunity based Profiling, helping you in dynamic identification of risks, threats, and opportunities, associated to your counterparts.

## Technology Partners


## Advantages and added value of Media Search
#### 360° view
Comprehensive and holistic insights on complex cases and data
#### Contextual results
Provides comprehensive contextual insights based on all available data.
#### Integration with Sanction Screening
Seamless integration with world-class Sanction Screening
#### Data sources
Unparalleled variety of supported data sources
#### Real-time analysis
Updates and delivers insights in real time for better decisions and timely actions.
#### Intuitive and user-friendly
Intuitive operation for a quick and easy search.
## Frequently asked questions
#### What is Media Search?
Media Search is an AI-based technology that finds relevant content from a variety of media sources, and provides you with contextual insight information about relationships, exposures, risks, threats and opportunities.
#### How does contextual search work?
Contextual search analyses all internally and externally available information to deliver the most relevant search results that best match your use case.
#### Can Media Search be integrated into other systems?
Yes, our Media Search can be integrated into existing systems, or used as a standalone functionality
#### Which data sourced does our Media Search support?
Our Media Search supports more than two dozen of media sources, such as LexisNexis Media Database, Google Media Database, OpenSanctions, OpenCorporates, RavenPack, Bloomberg, and many more.
#### Can your Media Search also analyze transactions?
Yes, our Media Search can be fully integrated in the processes of monitoring and screening of transactions and instant payments, as well as Dynamic Risk & Opportunity based Profiling, based on transaction monitoring.

### MEDIA SEARCH SCREENING
## Learn more about our Media Search
See for yourself how our Media Search Screening solution helps you to better understand networks, identify risks at an early stage and make strategic decisions.

Fill out and submit the form, and we will contact you shortly.
**Erreur :** Formulaire de contact non trouvé !
---
### [Whitepaper: The State of Vendor Risk Management (VRM) 2025](https://swissgrc.com/fr/vrmwhitepaper/)
**Published:** juillet 24, 2025
**Author:** Yahya Mohamed Mao
**Content:**
Download Whitepaper
## The State of Vendor Risk
Management (VRM) 2025
From reactive compliance
to strategic resilience

First Name\*
Last Name\*
Company\*
Job Title\*
Business Email\*
By clicking the button below, you consent to Swiss GRC storing and processing your personal information to provide the requested content and to contact you about our products. For details, see our [Privacy Policy.](https://swissgrc.com/fr/privacy-policy/)
Download Whitepaper
## The State of Vendor Risk Management (VRM) 2025
From reactive compliance to strategic resilience

First Name\*
Last Name\*
Company\*
Job Title\*
Business Email\*
By clicking the button below, you consent to Swiss GRC storing and processing your personal information to provide the requested content and to contact you about our products. For details, see our [Privacy Policy.](https://swissgrc.com/fr/privacy-policy/)
---
### [Whitepaper: Leveraging GRC for Resilience and Innovation](https://swissgrc.com/fr/grcwhitepaper/)
**Published:** janvier 8, 2025
**Author:** Gent Krasniqi
**Content:**
Download Whitepaper
## Leveraging GRC for
Resilience and Innovation
Strategic insights for 2025 and
beyond

First Name\*
Last Name\*
Company\*
Job Title\*
Business Email\*
By clicking the button below, you consent to Swiss GRC storing and processing your personal information to provide the requested content and to contact you about our products. For details, see our [Privacy Policy.](https://swissgrc.com/fr/privacy-policy/)
Download Whitepaper
## Leveraging GRC for Resilience and Innovation
Strategic insights for 2025 and beyond

First Name\*
Last Name\*
Company\*
Job Title\*
Business Email\*
By clicking the button below, you consent to Swiss GRC storing and processing your personal information to provide the requested content and to contact you about our products. For details, see our [Privacy Policy.](https://swissgrc.com/fr/privacy-policy/)
---
### [2025 SPARK Matrix: IT Risk Management by QKS Group](https://swissgrc.com/fr/2025-spark-matrix-it-risk-management-by-qks-group/)
**Published:** mai 8, 2025
**Author:** Yahya Mohamed Mao
**Content:**
Analyst Report by QKS Group
## Swiss GRC Positioned as a Leader in the 2025 SPARK Matrix™: IT Risk Management
In the **2025 SPARK Matrix™: IT Risk Management**, QKS Group evaluated and ranked the top IT Risk Management vendors globally. The report highlights:
- Why **Swiss GRC** ranks highly for **customer impact**.
- Why **Swiss GRC** stands out for **technology excellence**.
- Key insights into the current state of the **IT Risk Management market**.
**Request the full report to learn more.**

First Name\*
Last Name\*
Company\*
Job Title\*
Business Email\*
Country\*AfghanistanAlbaniaAlgeriaAndorraAngolaAntigua and BarbudaArgentinaArmeniaAustraliaAustriaAzerbaijanBahamasBahrainBangladeshBarbadosBelarusBelgiumBelizeBeninBhutanBoliviaBosnia and HerzegovinaBotswanaBrazilBruneiBulgariaBurkina FasoBurundiCabo VerdeCambodiaCameroonCanadaCentral African RepublicChadChileChinaColombiaComorosCongoCosta RicaCroatiaCubaCyprusCzech RepublicDemocratic Republic of the CongoDenmarkDjiboutiDominicaDominican RepublicEcuadorEgyptEl SalvadorEquatorial GuineaEritreaEstoniaEswatiniEthiopiaFijiFinlandFranceGabonGambiaGeorgiaGermanyGhanaGreeceGrenadaGuatemalaGuineaGuinea-BissauGuyanaHaitiHondurasHungaryIcelandIndiaIndonesiaIranIraqIrelandIsraelItalyIvory CoastJamaicaJapanJordanKazakhstanKenyaKiribatiKuwaitKyrgyzstanLaosLatviaLebanonLesothoLiberiaLibyaLiechtensteinLithuaniaLuxembourgMadagascarMalawiMalaysiaMaldivesMaliMaltaMarshall IslandsMauritaniaMauritiusMexicoMicronesiaMoldovaMonacoMongoliaMontenegroMoroccoMozambiqueMyanmarNamibiaNauruNepalNetherlandsNew ZealandNicaraguaNigerNigeriaNorth MacedoniaNorwayOmanPakistanPalauPalestinePanamaPapua New GuineaParaguayPeruPhilippinesPolandPortugalQatarRomaniaRussiaRwandaSaint Kitts and NevisSaint LuciaSaint Vincent and the GrenadinesSamoaSan MarinoSao Tome and PrincipeSaudi ArabiaSenegalSerbiaSeychellesSierra LeoneSingaporeSlovakiaSloveniaSolomon IslandsSomaliaSouth AfricaSouth KoreaSouth SudanSpainSri LankaSudanSurinameSwedenSwitzerlandSyriaTaiwanTajikistanTanzaniaThailandTimor-LesteTogoTongaTrinidad and TobagoTunisiaTurkeyTurkmenistanTuvaluUgandaUkraineUnited Arab EmiratesUnited KingdomUnited StatesUruguayUzbekistanVanuatuVatican CityVenezuelaVietnamYemenZambiaZimbabwe
By clicking the button below, you consent to Swiss GRC storing and processing your personal information to provide the requested content and to contact you about our products. For details, see our [Privacy Policy.](https://swissgrc.com/fr/privacy-policy/)
---
### [2025 SPARK Matrix: Governance, Risk and Compliance Platform by QKS Group](https://swissgrc.com/fr/2025-spark-matrix-governance-risk-and-compliance-platform-by-qks-group/)
**Published:** mai 8, 2025
**Author:** Yahya Mohamed Mao
**Content:**
Analyst Report by QKS Group
## Swiss GRC Positioned as a Leader in the 2025 SPARK Matrix™: Governance, Risk, and Compliance Platform
In the **2025 SPARK Matrix™: Governance, Risk, and Compliance Platforms**, QKS Group evaluated and ranked the top GRC technology providers globally. The report highlights:
- Why **Swiss GRC** ranks highly for **customer impact**.
- Why **Swiss GRC** stands out for **technology excellence**.
- Key insights into the current state of the **GRC market**.
**Request the full report to learn more.**

First Name\*
Last Name\*
Company\*
Job Title\*
Business Email\*
Country\*AfghanistanAlbaniaAlgeriaAndorraAngolaAntigua and BarbudaArgentinaArmeniaAustraliaAustriaAzerbaijanBahamasBahrainBangladeshBarbadosBelarusBelgiumBelizeBeninBhutanBoliviaBosnia and HerzegovinaBotswanaBrazilBruneiBulgariaBurkina FasoBurundiCabo VerdeCambodiaCameroonCanadaCentral African RepublicChadChileChinaColombiaComorosCongoCosta RicaCroatiaCubaCyprusCzech RepublicDemocratic Republic of the CongoDenmarkDjiboutiDominicaDominican RepublicEcuadorEgyptEl SalvadorEquatorial GuineaEritreaEstoniaEswatiniEthiopiaFijiFinlandFranceGabonGambiaGeorgiaGermanyGhanaGreeceGrenadaGuatemalaGuineaGuinea-BissauGuyanaHaitiHondurasHungaryIcelandIndiaIndonesiaIranIraqIrelandIsraelItalyIvory CoastJamaicaJapanJordanKazakhstanKenyaKiribatiKuwaitKyrgyzstanLaosLatviaLebanonLesothoLiberiaLibyaLiechtensteinLithuaniaLuxembourgMadagascarMalawiMalaysiaMaldivesMaliMaltaMarshall IslandsMauritaniaMauritiusMexicoMicronesiaMoldovaMonacoMongoliaMontenegroMoroccoMozambiqueMyanmarNamibiaNauruNepalNetherlandsNew ZealandNicaraguaNigerNigeriaNorth MacedoniaNorwayOmanPakistanPalauPalestinePanamaPapua New GuineaParaguayPeruPhilippinesPolandPortugalQatarRomaniaRussiaRwandaSaint Kitts and NevisSaint LuciaSaint Vincent and the GrenadinesSamoaSan MarinoSao Tome and PrincipeSaudi ArabiaSenegalSerbiaSeychellesSierra LeoneSingaporeSlovakiaSloveniaSolomon IslandsSomaliaSouth AfricaSouth KoreaSouth SudanSpainSri LankaSudanSurinameSwedenSwitzerlandSyriaTaiwanTajikistanTanzaniaThailandTimor-LesteTogoTongaTrinidad and TobagoTunisiaTurkeyTurkmenistanTuvaluUgandaUkraineUnited Arab EmiratesUnited KingdomUnited StatesUruguayUzbekistanVanuatuVatican CityVenezuelaVietnamYemenZambiaZimbabwe
By clicking the button below, you consent to Swiss GRC storing and processing your personal information to provide the requested content and to contact you about our products. For details, see our [Privacy Policy.](https://swissgrc.com/fr/privacy-policy/)
---
### [Contract Management Software](https://swissgrc.com/fr/contract-management-software/)
**Published:** février 27, 2023
**Author:** superadmin
**Content:**
### Solution for Contract Management
# Manage and monitor contracts throughout your company
GRC Toolbox simplifies the contract lifecycle and improves the efficiency of contract management. With its user-friendly and intuitive usability, you can centralise your contractual assets and monitor the the contract lifecycle.
[ Contact us ](#contact)


## Leading companies use our contract management solution
### GRC Toolbox Insights
## Features
Here you get a first insight into the possibilities of our contract management solution.
#### Central Contract Register and Search
Gain a comprehensive insight into your company’s existing contractual relationships, including key data such as contractual partners, term, notice periods, conditions and risks.

#### Structured Contract Metadata
Enter and store contract data centrally in the GRC Toolbox. Capture all relevant information such as contracting parties, contract terms, duration, notice periods and important dates.

#### Automatic Contract Reminders
Make sure you don’t miss important events and take action in time. Automated monitoring of dates and deadlines helps you avoid contractual penalties, renew or terminate contracts in time and identify bottlenecks.

#### Workflow-based Contract Review
The GRC Toolbox offers the possibility via workflows to handle the creation, review and approval of contracts and to view the status at any time.

#### Contract Management Reporting
Improve the productivity, efficiency and compliance of your contract management. The contract management dashboard serves as a valuable tool for decision-making and shows you all contract-relevant information in a visually appealing and intuitive way.


### Advantages and added value for your organisation
## Contract Management with the GRC Toolbox
#### Central repository of all contracts and documents
Keeping track of your contracts and quickly finding important information such as deadlines and terms.
#### Automatic monitoring of dates and deadlines
Ensuring that contracts are always up to date and being informed about important deadlines at all times.
#### Contract Risk Management
Complying with legal and regulatory requirements by renewing or terminating contracts in time.
#### Electronic archiving
Secure storage of contracts with complete documentation and tracking of modifications and versions.
#### Comprehensive Contract Access control
Define roles and permissions to ensure that access to sensitive contract data is only possible with the required authorisation.
#### Contract Management Overview
Get an overview of the status and performance of your contracts so you can act in time and optimise your contract management.

As one of the world’s leading universities, ETH Zurich attaches great importance to standards and quality. When looking for a GRC solution, it was crucial for us to find a partner who could meet our requirements and provide an intuitive tool with self-explanatory functions. Swiss GRC has proven to be a reliable partner that understands and fulfills these requirements. We appreciate the quality of service and the high flexibility of this GRC solution. It has significantly improved the way we work and we are very satisfied with the results.
Yannic Kälin
Risk & Compliance Controlling, ETH Zurich
# Discover all our solutions around GRC
Create the foundation for a successful GRC strategy. With the GRC Toolbox, you can gradually extend your digital governance, risk and compliance processes to all other GRC areas.

## Information Security (ISMS)

## Risk Management

## Internal Control (ICS)

## Third-Party Risk Management (TPRM)
[ Other solutions ](https://swissgrc.com/en/solutions/)
[ Contact Sales ](#contact)
### GRC TOOLBOX
## Learn more about our contract management software
Convince yourself and test all functions of the GRC Toolbox, the user-friendly software for your GRC management.


**Mirko Hegi**, GRC Expert, PostFinance AG
Right from the start, the cooperation was at eye level and we understood each other, not only on a professional but also on a human level.
Fill out and submit the form, and we will contact you shortly.
**Erreur :** Formulaire de contact non trouvé !
---
### [Events](https://swissgrc.com/fr/events/)
**Published:** avril 10, 2024
**Author:** shayeste
**Content:**
### EVENTS & WEBINARS
# Meet us worldwide at an event near you
### Our team of experts is present at industry events all over the world.


SWISS GRC DAY
WEBINARS
EVENTS
## SWISS GRC DAY 2025
On May 14, 2025 at the Radisson Blu Hotel, Zurich Airport, everything will revolve around the future of governance, risk and compliance. At a time when technological, regulatory, economic and geopolitical conditions are changing rapidly, it is crucial not only to manage change, but to actively shape it. Top-class speakers will present innovative strategies for the challenges of tomorrow. Take the opportunity for inspiring presentations, exciting discussions and valuable contacts.
[ Register now ](https://swissgrc.com/swissgrcday)
août 5, 2026

#### Upcoming WEBINAR
#### Information Isn’t Intelligence: Connecting the Dots in Third-Party Risk
Data tells you what happened. Connected intelligence tells you what matters. Join us for the exclusive introduction of the new Swiss GRC Third-Party Intelligence Center (TPIC).
[To the Webinar](https://events.teams.microsoft.com/event/28eec8ec-d8aa-4563-ae4a-cc173be51c1e@e19b35f4-f7ad-4fe9-a202-26aeb3f7adb1)
juillet 7, 2026


#### Replay WEBINAR
Recording
#### Modern approaches to risk quantification: How stochastics and simulation make the future tangible
How can risks be made tangible and well-informed decisions be made in the face of uncertainty? Find out more in our webinar on risk quantification.
[To the Webinar](https://events.teams.microsoft.com/event/a18cb3ff-5047-4ffb-aeb5-9bfe9d879c3e@e19b35f4-f7ad-4fe9-a202-26aeb3f7adb1)
[ More webinars ](https://swissgrc.com/webinare/)
## UPCOMING EVENTS
- Theme Data Protection Digital Transformation GRC Information Security Risk Management
- Region Americas Asia Europe Middle East and North Africa Pacific Sub-Saharan Africa
- Year 2023 2024 2025

mai 26, 2025
### IT GRC Congress 2025, 26 – 27 May 2025
Location: **Cologne, Germany**
Theme: **GRC**
The IT GRC Congress 2025 will take place on 26 and 27 May in Cologne and is dedicated to the latest developments in IT governance, information security, IT auditing, regulation, compliance and risk management. In addition, the ISACA specialist groups will present relevant future topics. Swiss GRC is a sponsor of the congress and will be actively on site to discuss current challenges and solutions in the field of IT GRC with fellow experts.
[Learn more](https://www.grc-kongress.de/)

mai 14, 2025
### SWISS GRC DAY 2025, 14 May 2025
Location: **Zurich, Switzerland**
Theme: **GRC**
The SWISS GRC DAY is the central meeting point for experts and interested parties from all over Switzerland and neighbouring countries. Organised by Swiss GRC AG, the annual conference offers a unique platform for exchanging views on the latest news, challenges and trends in the areas of governance, risk and compliance (GRC). Participants can look forward to an exciting programme with top-class speakers.
[Learn more](https://www.swissgrc.com/swissgrcday)

mai 11, 2025
### Risk-!n Conference 7th Edition, 11 – 13 May 2025
Location: **Zurich, Switzerland**
Theme: **GRC**
Risk-!n 2025 is the leading event for risk management, resilience, insurance, compliance and security. From 11 to 13 May 2025 in Zurich, the conference will bring together over 300 experts to discuss current challenges and innovations. One highlight is the premiere appearance of Michael Rasmussen, one of the leading GRC experts. Swiss GRC is a Silver Sponsor.
[Learn more](https://www.risk-in.com/)

mai 6, 2025
### Austrian GRC Day 2025, 6 May 2025
Location: **Vienna, Austria**
Theme: **GRC**
The motto of the Austrian GRC Day 2025 is ‘GRC Reloaded: Risk Intelligence as the Key to Value Creation’ and shows how governance, risk and compliance enable strategic value creation beyond pure compliance. Experts will discuss ESG, AI-supported risk analyses and geopolitical risks. Swiss GRC is a Gold Sponsor and is presenting an exciting customer use case together with ÖBB.
[Learn more](https://www.controller-institut.at/de/konferenzen/details/austrian-grc-day/)
Page1[Page2](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=2)[Page3](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=3)…[Page5](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=5)[](https://swissgrc.com/fr/webinars/?doing_wp_cron=1789375752.4891390800476074218750&sf_paged=2)
### GET THE LATEST NEWS & UPDATES
## Subscribe to our newsletter now
Stay up to date on news and trends in Governance, Risk & Compliance (GRC) with our newsletter. We inform you monthly about current topics, events such as the SWISS GRC DAY and exciting professional articles.
[ Subscribe ](https://swissgrc.com/en/newsletter)
---
### [GRC DAY INDIA 2025](https://swissgrc.com/fr/grcdayindia/)
**Published:** janvier 14, 2025
**Author:** Yahya Mohamed Mao
**Content:**

# GRC DAY INDIA
# 2025
## February 11, 2025
## The Leela Mumbai – Resort Style Business Hotel, Mumbai
#### 6:00 PM - 9:00 PM
[ Register now ](#register)
[ Sponsoring ](#sponsoring)
[ Twitter ](https://twitter.com/swissgrc) [ Linkedin-in ](https://ch.linkedin.com/company/swissgrc) [ Youtube ](https://www.youtube.com/channel/UCy4QuXYekCQrA4n5oEwJSJg) [ Instagram ](https://www.instagram.com/swissgrc/)
### [EVENT OVERVIEW](#overview)
### [SPEAKERS](#speakers)
### [AGENDA](#agenda)
### [PARTNERS](#partners)
### [REGISTRATION](#register)
### [GCC GRC DAY 2024](https://swissgrc.com/en/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/)
## Secure your spot now!
The GRC DAY INDIA 2025 starts in
Jours
Heures
Minutes
Secondes
Building on the success of our flagship events in Zurich and Dubai, we are excited to bring our renowned conference to India. The inaugural **GRC DAY INDIA**, set to take place on **11 February 2025** at The Leela, Mumbai, promises to be a premier platform for professionals and leaders to explore the latest in Governance, Risk, and Compliance (GRC).
This exclusive event will showcase actionable insights, innovative strategies, and best practices in **Risk Management**, **Compliance**, **Cybersecurity**, **Data Protection**, **Business Continuity**, and more. With contributions from global experts, including a special session by a prominent leader from the **Bombay Stock Exchange (BSE)**, attendees will gain practical knowledge on integrating AI compliance with **DPDPA** requirements and advancing governance standards.
Don’t miss the opportunity to connect with peers, gain actionable insights, and explore the latest strategies to tackle today’s most pressing GRC challenges. Participation at the event is free, but registration is compulsory. Secure your spot now!
## Event Overview
GRC professionals from across India will convene at **GRC DAY INDIA 2025**, bringing together thought leaders, industry experts, and practitioners to explore the evolving landscape of governance, risk, and compliance (GRC). This premier event offers a platform to network, exchange insights, and uncover the latest advancements, fostering collaboration to address challenges at the intersection of innovation, strategy, and regulation.
## Event Highlights
- **Keynote Session:** Align GRC with innovation, regulatory frameworks, and resilience.
- **Interactive Panel:** Insights into risk management, digital transformation, DPDPA, and AI innovations.
- **Expert Masterclass:** Rajeev Dutt, General Manager MEA & APAC, Swiss GRC, on future-proofing your GRC framework.
- **Case Studies:** Global strategies for trust and resilience.
- **Special Session:** BSE leader on AI compliance and DPDPA-driven governance.
## Target Audience
Among the participants are:
- **Governance & Compliance:** Compliance Officer, Head of Governance, Paralegals.
- **Risk Management:** Risk Controllers, Managers, Information Security Officers.
- **IT & Cybersecurity:** Cybersecurity Consultants, IT Security Officers, CISOs.
- **Business Continuity:** BCM Managers, Emergency Specialists.
- **Audit & Control:** Internal Auditors, ICS Managers.
- **Executives:** Board Members, CEOs, CFOs, CIOs, COOs, etc.
## Speakers
### Insights from Leading Minds

Rajeev Dutt
### General Manager MEA & APAC,
Swiss GRC


Narayan Gokhale
### Vice-President and Principal Analyst,
QKS Group


Ritesh Bhatia
### Founder, V4WEB Cybersecurity


Jyant Kohli
Founder and CEO, Lawrbit


Kaveri Venkataraman
Head Governance Risk and Compliance, Writer Corporation


Milind Khamkar
Group CIO, Super-Max


Prof. Ajay Singh
Former CEO and Award Winning Author


Hiten Sinha
Ad GM Information Security,
Bombay Stock Exchange


Rachit Chhokera
Partner, Cyber Strategy and Governance, KPMG in India


Prof. Ajay Singh
Former CEO and Award Winning Author


Supriya Rai
Editor-in-Chief, Tech Achieve Media


Hiten Sinha
Ad GM Information Security,
Bombay Stock Exchange

## Agenda for GRC Day India
### A conference dedicated to Governance, Risk & Compliance (GRC)
[ Morning ](#)
[ Afternoon ](#)
### 6:00 PM - 6:25 PM Registration & Networking
### 6:30 PM - 6:35 PM

##### Welcome Address & Introduction
###### **Supriya Rai**, Editor-in-Chief, Tech Achieve Media
### 6:40 PM - 6:55 PM

##### Governance
###### **Narayan Gokhale**, Vice-President and Principal Analyst, QKS Group
### 6:55 PM - 7:10 PM

##### The Illusion of Preparedness: The Hidden Gaps in Your Incident Response Strategy
###### **Ritesh Bhatia**, Founder, V4WEB Cybersecurity
### 7:10 PM - 7:25 PM

##### Data Governance, Cybersecurity and DPDP - Boardroom Lens
###### **Rachit Chhokera**, Partner, Cyber Strategy and Governance, KPMG India
### 7:25 PM - 7:40 PM

##### DPDP, Regulatory Compliance and Regulatory Change
###### **Jyant Kohli**, Founder and CEO, Lawrbit
### 7:40 PM - 8:10 PM

##### Risk and Resilience
###### **Rajeev Dutt**, General Manager, MEA and APAC, Swiss GRC
### 8:10 PM - 8:25 PM

##### Risk Management
###### **Kaveri Venkataraman**, Head Governance Risk and Compliance, Writer Corporation
### 8:25 PM - 8:35 PM

##### Product Demo
###### **Babu Manikan**, Senior Manager, Swiss GRC
### 8:35 PM - 9:05 PM

##### Panel Discussion on "Navigating the Convergence of GRC and Emerging Technologies: Challenges and Opportunities"
###### **Milind Khamkar**, CIO, Super-Max
**Prof. Ajay Singh**, Award Winning Author
**Hiten Sinha**, Ad GM Information Security, BSE
### 9:05 PM - 9:10 PM

##### Closing Note and Thank You
###### **Rajeev Dutt**, General Manager, MEA and APAC, Swiss GRC
### 6:00 PM – 6:15 PM Networking Break
### 6:15 PM - 6:30 PM

##### Governance Trends in the Region
###### Osama Al Rahma
### 6:30 PM - 6:45 PM

##### Implementing Effective Risk Management Frameworks
###### Waqas Haider
### 6:45 PM - 7:00 PM

##### Holistic Approach to Risk Management
###### Khalid Jalal
### 7:00 PM - 7:30 PM

##### Closing Note
###### Khalid Jalal
### 7:30 PM Onwards Dinner
Download PDF
## Gestalten Sie den SWISS GRC DAY mit uns!
Der SWISS GRC DAY bietet Ihnen die Möglichkeit, in die GRC-Welt einzutauchen. Erfahren Sie von renommierten Expertinnen und Experten die neuesten Entwicklungen, bewährte Strategien und innovativen Ansätze in den Bereichen Governance, Risikomanagement und Compliance. Freuen Sie sich auf spannende Vorträge und interaktive Diskussionen, die Ihnen wertvolles Wissen und praktische Tipps vermitteln.
Event-Sponsoring verbindet Markenpräsenz und Image Ihres Unternehmens mit der Möglichkeit, eine Vielzahl qualifizierter Leads zu generieren. Wir bieten mit diesem Fachevent eine grossartige Plattform für mehr Visibilität, Vernetzung und Kundengewinnung.

## Interessiert, Sponsor zu werden?
[ Jetzt kontaktieren ](mailto:events@swissgrc.com)
## Powered by
[  ](https://www.swissgrc.com)
[  ](https://www.swissgrc.com/)
## Presented by
[  ](https://www.gecmediagroup.com/)
[  ](https://www.gecmediagroup.com/)
## Werden Sie Medienpartner des SWISS GRC DAY!
Als Medienpartner des SWISS GRC DAY 2024 erhalten Sie exklusive Zugänge zu hochwertigen Inhalten, erstklassigen Expertinnen und Experten sowie spannenden Diskussionen rund um Governance, Risk und Compliance (GRC).
Präsentieren Sie Ihre Inhalte und Expertise einer engagierten Zielgruppe, die sich für die neuesten Trends, Best Practices und Lösungen in GRC interessiert. Nutzen Sie unsere Plattform, um Ihren Einfluss in der GRC-Community zu stärken und wertvolle Verbindungen mit GRC-Experten, Branchenführern und Entscheidungsträgern aufzubauen.
Kontaktieren Sie uns noch heute unter und erfahren Sie mehr über die Vorteile einer Medienpartnerschaft.
## Unser Medienpartner
[  ](https://computerworld.ch/)
Eine perfekte Plattform für den Austausch von Best Practices und das Knüpfen neuer Kontakte. Der SWISS GRC DAY hat meine Erwartungen in jeder Hinsicht übertroffen.
Ich verlasse diesen Tag mit einem Rucksack voll neuer Ideen und Lösungsansätze für unsere GRC-Strategie. Ein grosses Dankeschön an das Organisationsteam der Swiss GRC AG!
Eine hervorragend organisierte Konferenz mit einer perfekten Mischung aus Fachwissen, Networking und Inspiration.
Der Apéro Riche war die perfekte Abrundung eines informativen Tages. Die Möglichkeit, sich in lockerer Atmosphäre mit Branchenkollegen auszutauschen, war unbezahlbar.
Ein unverzichtbares Event für alle, die in Governance, Risk und Compliance vorne dabei sein wollen.
## Impressions

Hochkarätiges Speaker Lineup 
300 Teilnehmende 


## Seats are limited – Secure your spot today for the
GRC DAY INDIA 2025!
[ Register now ](#register)
## Past events
[
](https://swissgrc.com/fr/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/)### [ GCC GRC Day 2024: Navigating the Complexities of GRC in the Middle East ](https://swissgrc.com/fr/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/)
27 mai 2024
The GCC GRC DAY 2024 brought together leading industry experts who engaged in rich discussions about the most pressing GRC challenges, sharing insights and strategies to effectively navigate the complex landscape of governance, risk and compliance (GRC).
[ Read more ](https://swissgrc.com/fr/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/)
## Registration GRC DAY INDIA 2025 (free of charge)
### Swiss GRC MEA & APAC (Host)
Building 5, Ground Floor
Dubai Media City
Dubai
United Arab Emirates
Phone: +971 50 728 7247
### The Leela Mumbai - Resort Style Business Hotel (Venue)
Sahar Airport Road, Andheri – Kurla Rd, near Mumbai International Airport
Mumbai
India
[rso.mumbai@theleela.com](mailto:rso.tlpc@theleela.com)
Secure your spot now!
Title\*Mr.Ms.
I agree with the [privacy policy](https://swissgrc.com/fr/privacy-policy/)
---
### [Risk Concentration & Spillover](https://swissgrc.com/fr/risk-concentration-spillover/)
**Published:** août 19, 2024
**Author:** Gent Krasniqi
**Content:**
Risk Concentration & Spillover
# Identify and manage risk concentrations in real-time
Powered by Prospero’s advanced technology, we offer the possibility to identify, reduce and prevent concentrations of risk to third parties in real time. Act proactively and optimize your risk management.
[ Contact us ](#kontakt)

RISK CONCENTRATION & SPILLOVER
## TPRM at its next level
The ability to analyze complex and multi-level risk structures of third parties and subcontractors, taking into account dynamic mechanisms of risk spillover and exposure, has become an indispensable part of modern third-party risk management. The continuous analysis and early identification of risks, risk concentrations, and increasing risk exposures in a highly dynamic and complex environment is the basis for timely and forward-looking insights and high-quality decisions and measures.
[ Get started ](#kontakt)
RISK CONCENTRATION & SPILLOVER
## TPRM at its next level
The ability to analyze complex and multi-level risk structures of third parties and subcontractors, taking into account dynamic mechanisms of risk spillover and exposure, has become an indispensable part of modern third-party risk management. The continuous analysis and early identification of risks, risk concentrations, and increasing risk exposures in a highly dynamic and complex environment is the basis for timely and forward-looking insights and high-quality decisions and measures.

RISK CONCENTRATION & SPILLOVER
## Dynamic Third-Party Profiling
The application of traditional third-party due diligence assessment techniques alone is no longer sufficient to identify and analyze risks in our highly dynamic and complex world. The Dynamic Third-Party Profiling, where the new world of external Business Intelligence meets the foundation of established assessments techniques, and dynamic risk spillover, exposure and concentration analysis play a crucial role, is the rising superstar in the TPRM domain.
[ Get started ](#kontakt)
RISK CONCENTRATION & SPILLOVER
## Dynamic Third-Party Profiling
The application of traditional third-party due diligence assessment techniques alone is no longer sufficient to identify and analyze risks in our highly dynamic and complex world. The Dynamic Third-Party Profiling, where the new world of external Business Intelligence meets the foundation of established assessments techniques, and dynamic risk spillover, exposure and concentration analysis play a crucial role, is the rising superstar in the TPRM domain.

RISK CONCENTRATION & SPILLOVER
## Comprehensive Transparency
Modern Risk Management is not about reducing, simplifying, or even ignoring the complexity of what is happening around us. It’s about reducing complexity of dealing with complexity. Using innovative world-class technology and methodology, we help you gain full transparency of all your third-party exposures, relationships, and risks, with all their complexity, interconnectedness, and hidden cause-and-effect relationships, without making any compromises.
[ Get started ](#kontakt)
RISK CONCENTRATION & SPILLOVER
## Comprehensive Transparency
Modern Risk Management is not about reducing, simplifying, or even ignoring the complexity of what is happening around us. It’s about reducing complexity of dealing with complexity. Using innovative world-class technology and methodology, we help you gain full transparency of all your third-party exposures, relationships, and risks, with all their complexity, interconnectedness, and hidden cause-and-effect relationships, without making any compromises.

## Technology Partners


## Advantages and added value of Risk Concentration & Spillover Analysis
#### Next Generation TPRM
Responding to the challenges of our dynamic world.
#### World-class Innovation
Based on innovative technology and methodology
#### Uncovers hidden Insights
For better Risk Management and better decisions.
#### Dynamic Analysis
Ongoing analysis of all available static and dynamic data.
#### Intuitive and comprehensible
Complexity digested, analyzed, and explained
#### Your personal Superhero
Keeps your back free, while analyzing and processing.
## Frequently asked questions
#### What is Risk Concentration?
Risk concentration refers to the accumulation of similar or related risks within a specific area, company, or portfolio. This concentration can lead to greater impacts from unexpected events compared to a situation where risks are more evenly distributed.
#### What are Spillover Effects?
Spillover effects occur when a risk or an unexpected event in one sector or area affects other sectors, companies, or countries. This often happens in highly interconnected systems or markets, where the failure of one part impacts other parts.
#### Why is Risk Concentration Dangerous?
When risks are highly concentrated, negative events can have far-reaching consequences and potentially trigger systemic crises. For example, a company that relies heavily on a single supplier may be severely impacted if that supplier experiences a problem, jeopardizing the company’s entire operations.
#### Can Spillover Effects Be Predicted?
Spillover effects are difficult to predict due to the complex interactions between different actors and markets. However, early warning systems and scenario analyses can help identify potential chain reactions.

### RISK CONCENTRATION & SPILLOVER
## Find out more about our Risk Concentration & Spillover
Experience how our Risk Concentration & Spillover optimizes your GRC processes with smart automation, valuable insights and an intuitive chat interface.

Fill out and submit the form, and we will contact you shortly.
**Erreur :** Formulaire de contact non trouvé !
---
### [Speech & Voice Analytics](https://swissgrc.com/fr/speech-voice-analytics/)
**Published:** août 19, 2024
**Author:** Gent Krasniqi
**Content:**
Speech & Voice Analytics
# Identify risks and opportunities with Speech Analytics
In cooperation with Spitch, Swiss GRC offers integrated functions for the timely identification of risks, threats and opportunities in relation to third parties based on language and speech. Optimize your processes and make informed decisions.
[ Contact us ](#Contact)

SPEECH & VOICE ANALYTICS
## Immediate Insights
Based on one of the most advanced technologies in the industry you can get immediate, authentic, and the most direct insights possible on potential risks, threats, and opportunities to act upon. Monitor in real-time how your outsourcing partners, customer support agents, and customers speak to one another. Conduct advanced risk and sentiment analysis and act before risks and threats materialize, or opportunities vanish.
[ Get started ](#)
SPEECH & VOICE ANALYTICS
## Immediate Insights
Based on one of the most advanced technologies in the industry you can get immediate, authentic, and the most direct insights possible on potential risks, threats, and opportunities to act upon. Monitor in real-time how your outsourcing partners, customer support agents, and customers speak to one another. Conduct advanced risk and sentiment analysis and act before risks and threats materialize, or opportunities vanish.

SPEECH & VOICE ANALYTICS
## Sophisticated Analysis
Whether in Arabic, English or Swiss German, the system recognizes critical words, phrases, and statements, it conducts a sophisticated contextual sentiment analysis on the fly, highlights the most relevant and risky findings, and summarizes the use case in a comprehensive and easy to understand way. Whether customer attrition, compliance issues, or cross and up-selling, the system identifies the relevant context and sends you early warning notifications in real-time for immediate and proactive actions.
[ Get started ](#)
SPEECH & VOICE ANALYTICS
## Sophisticated Analysis
Whether in Arabic, English or Swiss German, the system recognizes critical words, phrases, and statements, it conducts a sophisticated contextual sentiment analysis on the fly, highlights the most relevant and risky findings, and summarizes the use case in a comprehensive and easy to understand way. Whether customer attrition, compliance issues, or cross and up-selling, the system identifies the relevant context and sends you early warning notifications in real-time for immediate and proactive actions.

SPEECH & VOICE ANALYTICS
## Risks and Performance Management
By using advanced Speech Analytics management of Risks, Threats, and Opportunities rises to a completely new level. Immediate, timely, and forward-looking insights are generated opening and tapping from a completely new data dimension, which uncovers hidden possibilities and enormous opportunities for Next Generation Risk, Compliance and Performance Management of a modern organization.
[ Get started ](#)
SPEECH & VOICE ANALYTICS
## Risks and Performance Management
By using advanced Speech Analytics management of Risks, Threats, and Opportunities rises to a completely new level. Immediate, timely, and forward-looking insights are generated opening and tapping from a completely new data dimension, which uncovers hidden possibilities and enormous opportunities for Next Generation Risk, Compliance and Performance Management of a modern organization.

## Technology Partners


## Advantages and added value of Speech and Voice Analytics
#### World-class Technology
Best-of-bread technology for Speech and Voice analysis
#### Multilingual
Accurate analysis of multiple languages and dialects.
#### Hidden Insights
Provides insights from a neglected dimension of data
#### Risk and Performance
Simultaneous management of Risks and Opportunities
#### Easy to Integrate
Fast and easy integration and into legacy systems
#### Dynamic Profiling
Integral part of Risk & Opportunity based Profiling
## Frequently asked questions
#### What is Speech & Voice Analytics?
Speech & Voice Analytics is a technology that analyzes speech and voices to gain valuable insights. This can be done through transcription, voice and sentiment analysis, keyword recognition and much more. It is often used in call centers and customer service departments to improve customer satisfaction and increase operational efficiency.
#### How does Speech & Voice Analytics work?
Speech & Voice Analytics uses machine learning and natural language processing (NLP) to convert spoken language into text and analyze the content and tone of voice. The technology can recognize patterns and trends, such as frequent customer complaints or the customer’s mood during a call.
#### What advantages does Speech & Voice Analytics offer?
Improved customer experience: By analyzing customer interactions, companies can identify and solve problems more quickly.
**Increased efficiency:** Companies can optimize processes and make employee training more targeted.
**Compliance with regulations:** The technology helps to ensure that call content complies with legal requirements.
**Market research:** By analyzing customer feedback, valuable insights can be gained for product and service improvements.
#### What data is collected by Speech & Voice Analytics?
Speech & Voice Analytics captures spoken language, which is then converted into text. This data includes the content of conversations, tonality, volume and speed of speech. Analyzing this data provides insights into customer satisfaction, emotions and topics discussed during the conversation.
#### What are the future prospects for speech & voice analytics?
The technology is expected to be further developed and increasingly used in various industries. With the further development of artificial intelligence and machine learning, speech & voice analytics is becoming increasingly precise and powerful, opening up new fields of application.

### SPEECH & VOICE ANALYTICS
## Learn more about Speech & Voice Analytics
Find out how you can optimize your processes and make informed decisions thanks to Speech & Voice Analytics.

Fill out and submit the form, and we will contact you shortly.
**Erreur :** Formulaire de contact non trouvé !
---
### [Sanctions Screening](https://swissgrc.com/fr/sanctions-screening/)
**Published:** août 27, 2024
**Author:** Gent Krasniqi
**Content:**
Sanctions Screening
# Act safely and avoid sanctioned parties
Powered by Prospero technology, our sanctions screening solution enables you to detect and avoid exposure to sanctioned counterparts while ensuring full legal compliance. Safeguard your business, minimize penalties, and protect your reputation with confidence.
[ Contact us ](#Contact)

SANCTIONS SCREENING
## Extensive screening process
In a highly automated, multi-stage and dynamic process, seamlessly integrated with new generation Media Search functionality, your third parties, outsourcing and business partners, subcontractors, customers and transactions are continuously checked in detail for critical links to sanctioned, monitored or politically exposed persons and companies. High-quality hit signals are generated with a precision and scope of insight that is outstanding in the industry.
[ Get started ](#Contact)
SANCTIONS SCREENING
## Extensive screening process
In a highly automated, multi-stage and dynamic process, seamlessly integrated with new generation Media Search functionality, your third parties, outsourcing and business partners, subcontractors, customers and transactions are continuously checked in detail for critical links to sanctioned, monitored or politically exposed persons and companies. High-quality hit signals are generated with a precision and scope of insight that is outstanding in the industry.

SANCTIONS SCREENING
## Cutting-edge technology
Based on a sophisticated combination of state-of-the-art processes, methods and technologies such as artificial intelligence, machine and evolutionary learning, media search, NLP, dynamic link and sentiment analysis, as well as through the use of innovative and unique optimization processes, critical and high-risk business relationships are identified in a timely and precise manner, and deep and detailed insights are generated that you can rely on.
[ Get started ](#Contact)
SANCTIONS SCREENING
## Cutting-edge technology
Based on a sophisticated combination of state-of-the-art processes, methods and technologies such as artificial intelligence, machine and evolutionary learning, media search, NLP, dynamic link and sentiment analysis, as well as through the use of innovative and unique optimization processes, critical and high-risk business relationships are identified in a timely and precise manner, and deep and detailed insights are generated that you can rely on.

SANCTION SCREENING
## Extensive data sources
With a flexible use of turnkey adapters tailored to your needs to the world’s most widely used list suppliers such as Dow Jones FACTIVA, LSEG World Check, or Info4C, as well as the world’s largest media databases such as LexisNexis, or Google, and enriched by tailor-made connections to more than two dozen business intelligence suppliers specializing in specific topics or geographical areas, no white spot remains open for you.
[ Get started ](#Contact)
SANCTIONS SCREENING
## Extensive data sources
With a flexible use of turnkey adapters tailored to your needs to the world’s most widely used list suppliers such as Dow Jones FACTIVA, LSEG World Check, or Info4C, as well as the world’s largest media databases such as LexisNexis, or Google, and enriched by tailor-made connections to more than two dozen business intelligence suppliers specializing in specific topics or geographical areas, no white spot remains open for you.

## Technology Partners


## Advantages of our Sanctions Screening Solution
#### Extensive data sources
Checking data against myriads of national and international sanctions lists and data providers.
#### Real-time monitoring
Ongoing monitoring and detection of risky relationships for immediate action in the event of hits.
#### Risk assessment
Evaluation of customers and partners based on hit results.
#### Integration with Media Search
Seamless integration with last generation Media Search for high quality 360° insights.
#### Updates
Automatic updating of sanctions lists for the latest regulations and sanctions.
#### Easy to use
Easily integrated for efficient and intuitive easy to use screening.
## Frequently asked questions
#### What is sanctions screening?
Sanctions screening is a process by which companies check their customers, transactions and business partners for possible violations of national and international sanctions lists. This serves to ensure compliance with regulations and minimize the risk of fines or legal consequences.
#### What are the main differentiators of your Sanctions Screening functionality?
Our Sanctions Screening functionality is built on unique in its nature multilayer optimization processes using the advantages of AI, Machine Learning, Evolutionary Learning, NLP, just to name a few, and combining them with proprietary developed Next Generation Advanced Analytics methods. This approach assures highest analytical and technical performance, accuracy and reliability of generated insights.
#### Why is sanctions screening important?
Sanctions screening is crucial to ensure that companies do not inadvertently do business with sanctioned individuals, organizations or countries. Violations of sanctions can lead to significant fines, reputational damage and legal consequences.
#### How does the sanctions screening process work?
The process usually involves several steps:
**Data matching:** customer, transaction or business partner data is matched against entries on the relevant sanctions lists.
**Match evaluation:** Potential matches are evaluated to determine whether they are actual matches (true matches) or whether they are false positives due to similar names or other factors.
**Reporting:** Genuine matches are reported and appropriate action is taken, such as blocking transactions or terminating business relationships.
#### Which technologies are used for sanctions screening?
Modern sanctions screening systems use technologies such as artificial intelligence (AI), machine learning and big data to automate the comparison of data and improve the accuracy of the hit assessment.
#### What are the consequences of non-compliance with sanction regulations?
Failure to comply with sanctions regulations can lead to significant penalties, including heavy fines, criminal prosecution and serious reputational damage. In some cases, this can even lead to a ban on operating in certain markets.

### SANCTIONS SCREENING
## Learn more about our solution for Sanctions Screening
See for yourself how our sanctions screening solution can help you avoid sanctioned parties and run your business safely.

Fill out and submit the form, and we will contact you shortly.
**Erreur :** Formulaire de contact non trouvé !
---
## News
### [Industry Findings Show 9% Revenue Risk from Ineffective Contract Management](https://swissgrc.com/fr/news/industry-findings-show-9-revenue-risk-from-ineffective-contract-management/)
**Published:** février 23, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** A newly released whitepaper by Swiss GRC highlights structural gaps in enterprise contract lifecycle practices, identifying measurable financial and compliance risks linked to ineffective contract management. Despite rapid digital transformation across finance, operations and customer processes, contract management remains one of the least modernized enterprise functions.
**Content:**
**A newly released whitepaper by Swiss GRC highlights structural gaps in enterprise contract lifecycle practices, identifying measurable financial and compliance risks linked to ineffective contract management. Despite rapid digital transformation across finance, operations and customer processes, contract management remains one of the least modernized enterprise functions.**
Many organizations continue to manage legally binding agreements through spreadsheets, email correspondence and decentralized storage systems, creating operational blind spots and financial exposure. Limited visibility into obligations and renewals can erode up to 9% of annual revenue through missed deadlines, overlooked commitments and inconsistent negotiation outcomes. At the same time, nearly half of compliance failures stem not from intentional misconduct but from insufficient tracking and documentation.
Contracts typically span legal, procurement, finance and business operations, yet responsibility often remains fragmented across systems and individuals. Without central coordination, organizations struggle to determine which obligations are active, who approved contractual deviations and when critical renewals occur. As regulatory scrutiny intensifies, demonstrable oversight is becoming as important as compliance itself.
According to Swiss GRC, this imbalance reflects a broader governance challenge within enterprise risk management. Gentian Ajeti, Chief Customer & Commercial Officer at Swiss GRC, comments: “The challenge does not lie in the digital storage of documents, but in the governance of the entire contract lifecycle. That is why we developed Contraqto with the objective of making contract management more transparent and structurally controllable through AI-powered automation.”

The whitepaper outlines a structured maturity path for contract lifecycle practices, beginning with centralized repositories and progressing toward workflow automation, analytics-driven insights, cross-functional collaboration and embedded governance controls. It further distinguishes between document digitization and lifecycle digitalization, emphasizing that storing agreements electronically does not automatically provide transparency or compliance assurance. Effective modernization requires structured workflows, role-based approvals, automated alerts and comprehensive audit trails. As organizations operate in increasingly regulated and data-driven environments, strengthening contract lifecycle governance is shifting from operational improvement to executive priority.
The full Whitepaper is available for download now:
**[Modern Contract Lifecycle Management: Driving Value and Compliance](https://www.swissgrc.com/Downloads/Whitepaper/Whitepaper%20Modern%20CLM%20Driving%20Value%20and%20Compliance.pdf)**
---
### [Review SWISS GRC DAY 2022](https://swissgrc.com/fr/news/swiss-grc-day-2022/)
**Published:** mai 11, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** Anyone interested in GRC or specifically concerned with governance, risk, ICS, compliance, data protection, security, BCM and audit was at the SWISS GRC DAY 2022 at the Radisson Blu Hotel in Zurich Airport on May 4, 2022.
**Content:**
**Wer sich für GRC interessiert oder sich spezifisch mit Governance, Risk, IKS, Compliance, Datenschutz, Security, BCM und Audit befasst, war am 4. Mai 2022 am SWISS GRC DAY 2022 im Radisson Blu Hotel in Zürich Flughafen anzutreffen. Die Veranstaltung, bei der die Swiss Infosec AG und Data Governance als Partner auftraten, wurde von Yahya Mohamed Mao, Head Business Development & Marketing der Swiss GRC AG, moderiert. Mit mehr als 220 Personen liessen sich von den Best Practice-Beispielen der Referentinnen und Referenten begeistern und inspirieren. Es sind gerade diese Erfahrungen mit unterschiedlichen Herausforderungen, die den Teilnehmenden echten Mehrwert bringen und die unterstützende Rolle der GRC Toolbox im komplexen Umfeld herausheben. Für interessante Gespräche in der Pause und beim abschliessenden Apero war damit gesorgt.**
**Yahya Mohamed Mao**, Head Business Development & Marketing Swiss GRC AG, welcomes the audience, speakers and event partners to the 5th SWISS GRC DAY. He promises them an interesting journey through exciting topics in the field of government, risk management and compliance and looks forward to interesting presentations and stimulating discussions during the break and over drinks.
**« Are you Ransom ready? »**, asks **Tom Schmidt**, Partner Ernst & Young AG, EMEIA FSO Cybersecurity Competency Leader & Switzerland FSO Cybersecurity Leader. He describes current cyber threats and future challenges and what (and how) companies need to prepare for.
Ransomware is the focus of his presentation. In this form of cyber attack, cyber criminals encrypt data and servers. As part of double extortion, they not only demand money for decryption, but also for not publishing the captured data in a way that attracts media attention. The « industry », which has now formed actual cyber syndicates and operates in a large network, generated around 20 billion US dollars in 2020 alone (compared to around 11 billion in 2019). Ransomware is therefore a highly lucrative business and one of the reasons for the rapid rise in these cyberattacks. Tom Schmidt shows the different steps of a ransomware attack and how companies can arm themselves against it.
>[ Link](https://swissgrc.com/en/wp-content/uploads/2022/12/01_Tom-Schmidt_EY-Cybersecurity-Presentation.pdf) to the presentation
**Dr. Susanna Lüthi-Walter**, Chief Risk Officer ZRe, Zurich Insurance Company, and **Eva Severa-Züger**, Chief Compliance Officer ZRe, Zurich Insurance Company, know the building blocks, challenges and success factors in setting up a holistic ICS from a risk and compliance perspective.
While the scope of an internal control system (ICS) traditionally focuses on financial reporting, the increasing importance of monitoring systems in today’s environment is leading to a holistic view of the ICS. The speakers shed light on this trend and describe a holistic ICS as an integral part of company-wide risk management, which maps all significant operational and financial company risks and also incorporates compliance risks. From the speakers’ point of view, this requires a pragmatic approach, an integrative ICS strategy (including implementation planning), coordinated instruments and tools and – very importantly – sufficient resources and a strong involvement of the first line.
>[ Link](https://swissgrc.com/en/wp-content/uploads/2022/12/02_Susanna-Luethi_Eva-Severa_Zuerich-Versicherung-Aufbau-ganzheitliches-IKS.pdf) to the presentation
**Dr. Iur. Jean-Pierre Méan**, lawyer and former board member of Transparency International Switzerland, will share his experience of compliance management and show how an integral compliance culture can help remedy compliance and integrity risks.
A holistic approach is also the focus of this presentation. Such an approach also proves its worth when it comes to the complex topic of compliance. The very fact that compliance is part of the ISO Governance family of standards shows the close links to governance, anti-corruption, whistleblowing, etc. The anti-corruption standard is used as an example to show how a compliance culture can be implemented, what needs to be taken into account and where the standard is most helpful. In any case, the commitment of top management is crucial to the success of a company’s compliance culture. And it goes without saying that there is still room for improvement when it comes to compliance. Dr. Méan identifies this in the role and positioning of the compliance officer, conflicts of interest and compliance for SMEs, among other things.
> [Link](https://swissgrc.com/en/wp-content/uploads/2022/12/03_Jean-Pierre-Mean_Eigenmann-Associes-Compiance-und-Integritaetsrisiken.pdf) to the presentation
**Tolga Ece**, Head of the Risk and Insurance Management Competence Center of the City of Zurich, presents the City of Zurich’s opportunity and risk management and its comprehensive approach to better decision-making – a practical report on the success factors.
The City of Zurich has had risk and insurance regulations in place since 2011. As a result, risk management has become widespread, but there was a lack of a common system and a consolidated view. The CHARM project (from opportunity and risk management), which aims to identify and manage opportunities as well as risks, is intended to change this. The aim is to create a comprehensive opportunity and risk policy that will, for example, ensure the performance and functionality of the city administration, which has almost 30,000 employees, and promote awareness of opportunities and risks among employees. Tolga Ece describes the specific procedure in the project (workshops, bottom-up), names success factors (simple approach, clear boundaries), stumbling blocks (risk consolidation and quantification) and steps for further development (early warning indicators, cross-cutting risks).
> [Link](https://swissgrc.com/en/wp-content/uploads/2022/12/04_Tolga-Ece_Stadt-Zuerich-Risikomanagement.pdf) to the presentation
**Angela Hunziker**, Head of Corporate Risk Management, SBB CFF FFS, shows what integrated assurance looks like in practice and the challenges of cooperation between different assurance functions.
Assurance is understood as the entirety of the existing monitoring and control functions in a company, while combined assurance is the coordinated and integrated cooperation of all functions that are directly or indirectly related to risk and can contribute to improving the governance structure. Angela Hunziker shows approaches in connection with integrated assurance (ISO 37000, three-line model of the IIA), names advantageous framework conditions and current obstacles. In the second part of her presentation, she will take a practical look at integrated assurance (IA) at SBB by outlining the company’s corporate objectives, the organizational embedding of IA and cooperation. Finally, she reveals where SBB stands in terms of the regular exchange of information, joint processing of topics, coordinated processes, a consistent tool landscape and a holistic management system, and where there is potential for improvement.
> [Link](https://swissgrc.com/en/wp-content/uploads/2022/12/05_Angela-Hunziker_SBB-Integrierte-Assurance.pdf) to the presentation
**René Schüttel**, Risk Manager, fedpol, explains current and new (intelligent) approaches to situation and risk assessment and poses the question « What is the future and what is already reality? ».
New technologies open up new opportunities, but also bring new (digital) risks that need to be managed. The changes to risk management (RM) in the age of digitalization are explained using a graphic. On the other hand, the results of a survey conducted in 2018 provide indications of changes expected in the short term (e.g. increasing degree of automation, improved data processing) and in the long term (e.g. increasing use of big data and AI, growing threat of cyberattacks). These changes mean that strategic and business considerations must be made in connection with RM, as well as operational and procedural ones. Management/leadership considerations are also an issue. There is no lack of concrete approaches for the further digital development of fedpol risk management. Risk quantification and an early warning system are just two of them.
## PICTURE GALLERY
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/7-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/22-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/5-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/21-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/20-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/19-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/18-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/23-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/15-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/14-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/13-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/10-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/9-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/8-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/6-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/4-scaled-1.jpg)
[](https://swissgrc.com/fr/wp-content/uploads/sites/3/2022/05/3-scaled-1.jpg)
[ Feedback form for the SWISS GRC DAY 2022 ](https://forms.office.com/Pages/ResponsePage.aspx?id=9DWb4a336U-iAiaus_etsY2Wl0G5GupGrfRDNluwFHhUN0I5Q0dUUkUwME5PTjJNTjk5WUwwOEFNVi4u&wdLOR=c5F2CB2FF-1B54-4507-9651-A00B1AC00F05)
### Rely on the GRC TOOLBOX, your risk management software
Contact us for a non-binding initial consultation or for an online or live demonstration at your premises and rely on the GRC software from Swiss GRC AG. +41 41 220 75 00,
Would you like more information about the solutions from Swiss GRC AG? Contact us for a non-binding initial consultation or for an online or live demonstration at your premises. We will get in touch with you as soon as possible. Thank you very much!
**Erreur :** Formulaire de contact non trouvé !
---
### [Adaptive approach to risk management](https://www.csoonline.com/de/a/adaptiver-ansatz-fuer-das-risk-management,3674099#new_tab)
**Published:** août 17, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** The rapid pace of technological progress has resulted in complex, interlinked risks and is thus contributing to a reorientation of risk management.
**Content:**
The rapid pace of technological progress has resulted in complex, interlinked risks and is thus contributing to a reorientation of risk management.
---
### [Governance, Risk and Compliance are still operated reactively](https://www.handelszeitung.ch/insurance/governance-risk-und-compliance-werden-noch-immer-reaktiv-betrieben-540959#new_tab)
**Published:** octobre 28, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** For Besfort Kuqi, CEO of the software and consulting company Swiss GRC, governance, risk and compliance can no longer be isolated solutions...
**Content:**
For Besfort Kuqi, CEO of the software and consulting company Swiss GRC, governance, risk and compliance can no longer be isolated solutions…
---
### [Swiss GRC has been certified as Great Place to Work®](https://www.greatplacetowork.ch/workplace/item/5872/Swiss+GRC+AG#new_tab)
**Published:** novembre 21, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC AG is a leading software company in developing and implementing GRC solutions "Swiss made" at companies worldwide...
**Content:**
Swiss GRC AG is a leading software company in developing and implementing GRC solutions « Swiss made » at companies worldwide…
---
### [Swiss GRC is triple ISO certified](https://swissgrc.com/fr/news/swiss-grc-ist-dreifach-iso-zertifiziert/)
**Published:** décembre 6, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** At the close of November, we proudly received three ISO certificates. Swiss GRC has implemented an information security and data protection management system and has been successfully certified according to ISO 27001 (ISMS), ISO 27017 (Cloud) and ISO 27701 (Privacy)...
**Content:**
**At the close of November, we proudly received three ISO certificates. Swiss GRC has implemented an information security and data protection management system and has been successfully certified according to ISO 27001 (ISMS), ISO 27017 (Cloud) and ISO 27701 (Privacy).**
*« ISO certification guarantees continuous improvement of our solutions and services to meet the latest information security and privacy standards. Meeting our customers’ expectations takes a central role in this. » – Besfort Kuqi, CEO, Swiss GRC.*
### With the integrated ISMS, we are pursuing the following goals:
- We know and secure our assets end-to-end, namely business processes, information, services and also the supporting assets such as software, hardware, networks, personnel, locations.
- We provide information and services according to the required time and quality.
- We develop safe solutions and services that comply with data protection principles (Security & Privacy by Design).
- We are prepared for events and incidents and ensure that our central business processes and services can also be provided in extraordinary situations.
### Rely on the GRC TOOLBOX, your ISMS software
Contact us for a non-binding initial consultation, or directly for an online or live demonstration at your site and rely on the GRC software of Swiss GRC AG. +41 41 220 75 00,
Would you like to receive more information about the solutions of Swiss GRC AG? Contact us for a non-binding initial consultation or immediately for an online or live demonstration at your site. We will get in touch with you as soon as possible. Thank you very much!
---
### [Enterprise Risk Management: Climate change still not a priority](https://www.handelszeitung.ch/insurance/klimawandel-risiken-werden-von-den-chefs-nicht-prioritar-behandelt-546112#new_tab)
**Published:** décembre 29, 2022
**Author:** Yahya Mohamed Mao
**Excerpt:** The ERM Report 2022 of IFZ and Kiel University of Applied Sciences has investigated how climate risks can be integrated into corporate risk...
**Content:**
The ERM Report 2022 of IFZ and Kiel University of Applied Sciences has investigated how climate risks can be integrated into corporate risk.
---
### [Swiss GRC included in GRC Landscape Report Q2 2023](https://swissgrc.com/fr/news/swiss-grc-included-in-grc-landscape-report-q2-2023/)
**Published:** juin 27, 2023
**Author:** Yahya Mohamed Mao
**Content:**
**Swiss GRC, Switzerland’s leading governance, risk and compliance technology company, is pleased to announce that it has been listed among notable vendors for GRC Software 2023 in an independent research firm’s latest Landscape Report on the market. The report provides a comprehensive overview of the 33 GRC software vendors.**
Forrester, a renowned research and advisory firm, has recognized Swiss GRC among notable GRC solutions. Swiss GRC believes the report underscores the growing importance of holistic GRC management in the face of rising risks and regulatory changes. Moreover, the rise of systemic risks requires a reassessment of risk identification and mitigation in organizations. In this context, GRC software vendors play a crucial role by providing solutions to companies to improve their risk, compliance and security management activities, increase risk awareness and strengthen the organization’s resilience capabilities.
« We are proud to be listed as a notable vendor in Forrester’s Landscape Report for GRC Software Vendors 2023, » enthused Besfort Kuqi, CEO of Swiss GRC. « This recognition validates for us our long-standing expertise and position as an established GRC solutions provider. »
Swiss GRC offers a comprehensive range of governance, risk and compliance functions, including risk management, information security management, operational and cyber resilience, business continuity management and more. By continuously developing its solutions, Swiss GRC strives to enable its customers to achieve a high level of efficiency and accuracy in their GRC processes and to make GRC an integral part of modern and digital business management.
Forrester’s Landscape Report is an authoritative resource for organizations in selecting GRC software providers that meet their specific needs. Swiss GRC is proud to be included in this prestigious report and will continue to work to develop innovative solutions to meet the ever-changing demands of the GRC market.
For the full Landscape Report for GRC Software Vendors 2023 from Forrester, please see the following link: **[Link to report](https://www.forrester.com/report/the-governance-risk-and-compliance-platforms-landscape-q2-2023/RES179181).**
Swiss GRC AG is recognized in Switzerland as a leading software company in the development and implementation of GRC solutions. With over 30 years of experience in this field, Swiss GRC has built up extensive expertise. As a result of these years of experience, Swiss GRC offers the GRC Toolbox, an innovative software solution that helps organizations effectively manage governance, risk and compliance. Swiss GRC’s GRC Toolbox is based on proven methodologies and best practices and offers tailored solutions for an efficient and comprehensive GRC implementation. Customers can rely on Swiss GRC’s long-standing expertise to successfully manage their GRC requirements.
**Press contact:**
Yahya Mohamed Mao
Head Business Development & Marketing
Swiss GRC AG
Hirschmattstrasse 36
6003 Luzern, Switzerland
Tel: +41 41 220 75 00
[www.swissgrc.com](https://www.swissgrc.com)
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC at #RISK London 2023](https://swissgrc.com/fr/news/swiss-grc-at-risk-london-2023/)
**Published:** octobre 13, 2023
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC will be exhibiting at #RISK London 2023, Europe’s leading expo on governance, risk, compliance, ESG and workplace culture, on 18 and 19 October 2023 at ExCel London. With 5,000 attendees, 150+ exhibitors, 300+ expert keynotes, and interactive sessions, it is a hub of industry insights. Swiss GRC is seizing this opportunity, ensuring we are part of the action.
**Content:**
**Swiss GRC will be exhibiting at #RISK London 2023, Europe’s leading expo on governance, risk, compliance, ESG and workplace culture, on 18 and 19 October 2023 at ExCel London. Speak to us about how our solutions empower organizations to masterfully navigate governance, risk, and compliance (GRC).**
[\#RISK London 2023](https://www.grcworldforums.com/risk/risk-london-2023) unites the entire risk community for learning, networking, debate, collaboration, and informed decision-making. With 5,000 attendees, 150+ exhibitors, 300+ expert keynotes, and interactive sessions, it is a hub of industry insights. Swiss GRC is seizing this opportunity, ensuring we are part of the action.
[ Register for #RISK ](https://www.tickettailor.com/events/grcworldforums/874113/r/grcwf-risk-london-microsite)
How to join us at #RISK London
\#RISK takes place at [ExCel London](https://www.excel.london/visitor/getting-here), one stop away from Canary Wharf and just 12 minutes from the City of London.
**Location:** Stand 87, ExCel London
**Dates:** 18th and 19th October 2023
Visit our stand to explore how Swiss GRC provides a comprehensive suite of governance, risk, and compliance capabilities. This includes, among other things:
- **[Risk Management](https://swissgrc.com/en/risk-management-software/)**
- **[Information Security Management](https://swissgrc.com/en/information-security-management-isms-software/)**
- **[Operational and Cyber Resilience](https://swissgrc.com/blog/2023/05/24/staerkung-der-digitalen-resilienz-das-informationssicherheitsgesetz-des-bundes-isg/)**
- [**Third Party Risk Management**](https://swissgrc.com/en/risk-management-software/)
- **[Business Continuity Management](https://swissgrc.com/en/bcm-software/)**
- **[Data Protection Management](https://swissgrc.com/en/data-protection-management-software/)**
Through the ongoing enhancement of its [solutions](https://swissgrc.com/en/solutions/), Swiss GRC empowers its clients to achieve heightened efficiency and precision in their GRC processes, seamlessly integrating GRC into modern and digitally-driven business management practices.
We strongly encourage you to engage in informative discussions with our distinguished experts, **Dr. Christoph Jan Hasenkamp** and **Rajeev Dutt**, at our stand. They are well-equipped to provide you with a comprehensive understanding of our solutions and how they can elevate the operational excellence of your organization.
Who attends #RISK London?
Many organizations still adopt a fragmented approach to risk management, with multiple departments such as legal, sales, finance, compliance, HR, audit, and procurement, each playing a role in managing risks. The primary objective of this event is to dismantle these organizational silos and foster a more integrated approach to risk management.
Swiss GRC plays a pivotal role in promoting this integration. As a leading provider of governance, risk, and compliance solutions, we understand the importance of breaking down these silos and facilitating collaboration across various departments. Our expertise and solutions help organizations streamline their GRC processes and ensure a cohesive and efficient approach to managing governance, risk, and compliance functions.
The event attracts a diverse range of professionals from different areas, including compliance, risk, and various other functions. Attendees include Chief Compliance Officers (CCOs), Regulatory Risk Directors, Heads of Internal Controls, Heads of Assurance, Heads of ESG, Money Laundering Reporting Officers (MLROs), and Data Protection Officers (DPOs).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC opens Dubai office to support company growth in the region](https://swissgrc.com/fr/news/swiss-grc-opens-dubai-office-to-support-company-growth-in-the-region/)
**Published:** novembre 5, 2023
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC, the leading software company in Switzerland specializing in developing and implementing Governance, Risk, and Compliance (GRC) solutions, has strategically expanded its global footprint by establishing a new office in Dubai.
**Content:**
**Dubai, UAE — Swiss GRC, the leading software company in Switzerland specializing in developing and implementing Governance, Risk, and Compliance (GRC) solutions, has strategically expanded its global footprint by establishing a new office in Dubai.**
Swiss GRC has developed a deep understanding of the GRC sector because of its longstanding expertise. The GRC Toolbox, a cornerstone of its offerings, encapsulates this understanding. Built upon proven methodologies and best practices, this premier software solution equips enterprises to manage Governance, Risk, and Compliance with precision and efficacy. Our customers reflect a variety of industry verticals, including those in highly regulated high-risk sectors like BFSI, Manufacturing, Retail, Energy and Utilities, Transport and logistics, Public sector, Healthcare, Media and Technology.
The Middle East has emerged as a key region for GRC adoption, driven by heightened cybersecurity threats, complex regulatory landscapes, and an increasing awareness of the value of data protection. As more Middle Eastern enterprises recognise the importance of robust and integrated GRC frameworks, opening the Dubai office underscores Swiss GRC’s readiness to meet this growing demand and commitment to the region with deployment models of On-Premise, Private Cloud, and SaaS in line with the local Regulatory standards and framework.
Considering the expansion, Besfort Kuqi, CEO of Swiss GRC, said, “Our Dubai office signifies more than just geographical growth—it represents our proactive approach to a region rapidly recognizing the significance of rigorous GRC structures. Our comprehensive suite of Governance, Risk, and Compliance functions, encompassing areas like Risk management, Information security management, Data Protection, Operational and Cyber Resilience, and Business Continuity Management, is primed to assist these enterprises in elevating their GRC practices to international standards.”
Reinforcing the Dubai office’s strategic direction is the appointment of a seasoned General Manager. Renowned for his track record of spearheading GRC product offerings to various verticals and significantly contributing to the growth of some of the world’s leading GRC software providers in the Middle East, he will be a pivotal asset for Swiss GRC’s regional aspirations.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Global ICT Trailblazer Award for Swiss GRC Co-Founder & CEO](https://swissgrc.com/fr/news/global-ict-trailblazer-award-for-swiss-grc-co-founder-ceo/)
**Published:** novembre 8, 2023
**Author:** Yahya Mohamed Mao
**Excerpt:** Besfort Kuqi, Co-founder and CEO of Swiss GRC, has been honored with the Global ICT Trailblazer Award by GEC Media Group in Dubai on October 16, 2023. This prestigious award reflects his outstanding contributions to the ICT industry, particularly in the Governance, Risk & Compliance (GRC) technology sector.
**Content:**
**Dubai, UAE — Besfort Kuqi, Co-founder and CEO of Swiss GRC, has been honored with the Global ICT Trailblazer Award by GEC Media Group in Dubai on October 16, 2023. This prestigious award reflects his outstanding contributions to the ICT industry, particularly in the Governance, Risk & Compliance (GRC) technology sector.**
The [Global Enterprise Connect Awards (GEC Awards)](https://www.gecmediagroup.com/all-events/gec-awards/) has grown into the ICT industry’s premier awards ceremony, serving as a celebration of achievement and progress. Key criteria for this award include leadership impact, long-term company commitment and global industry recognition. With an judging panel renowned for its expertise and impartiality, the awards, having attracted over 500 nominations this year, undergo a rigorous evaluation process. Besfort Kuqi’s distinction as one of the five recipients of the Global ICT Trailblazer Award underscores his pivotal role in Swiss GRC’s success in the EMEA market, marked by a portfolio of successful projects and a robust global customer base within the region.
Expressing his gratitude for the award, Besfort Kuqi remarked, “This recognition is a testament to the dedication of the Swiss GRC team and our unwavering commitment and consistency to excellence in the GRC industry, achieved through our holistic and simple GRC platform.”
Besfort Kuqi stands as an expert in the GRC industry, boasting a career spanning over a decade devoted to the digitalization, integration, and optimization of management and control systems within organizations worldwide. His visionary leadership has been the driving force behind Swiss GRC’s success over the years, marked by the development and successful implementation of the GRC Toolbox—a comprehensive [software solution](https://swissgrc.com/en/solutions/) that encompasses modules such as Risk Management, Internal Controls Management, Business Continuity Management, Information Security Management, Data Protection Management, Audit Management, Compliance Management, Third-Party Risk Management, Contract Management, and Business Process Management.
---
### [Exclusively in the Tages-Anzeiger: Swiss GRC on the importance of Governance, Risk & Compliance](https://swissgrc.com/fr/news/exclusively-in-the-tages-anzeiger-swiss-grc-on-the-importance-of-governance-risk-compliance/)
**Published:** janvier 8, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** A special feature published in the renowned Tages-Anzeiger newspaper shows how Swiss GRC is shaping the industry and what role the company plays in the development of innovative GRC solutions.
**Content:**
**In a themed special curated by Smart Media and published in the renowned Tages-Anzeiger on January 5, 2024, CEO Besfort Kuqi and Head Marketing & Communications Yahya Mohamed Mao of Swiss GRC highlight the importance of governance, risk and compliance (GRC) for companies in today’s world. This exclusive feature highlights how Swiss GRC is shaping the industry and the role the company plays in developing innovative GRC solutions.**
In this [feature](https://issuu.com/smart_media/docs/2312_tag_agb_business_success_2024_1), our CEO, Besfort Kuqi, emphasizes Swiss GRC’s central goal of creating a framework that enables companies to optimize their risk management and compliance activities. He explains that the continuous development and improvement of our solutions is aimed at meeting the increasingly complex requirements in these areas and helping companies to achieve their goals safely and efficiently.
He also emphasizes the importance of strong governance in creating sustainability and security, which « ultimately create competitive advantage ». This realization is reflected in the international expansion of Swiss GRC. With offices in Germany, the UK and the [United Arab Emirates](https://swissgrc.com/en/news/swiss-grc-opens-dubai-office-to-support-company-growth-in-the-region/), Swiss GRC is increasing its presence in both the DACH and MEA/APAC regions.
Yahya Mohamed Mao, our Head of Marketing & Communications, emphasizes Swiss GRC’s close connection to the GRC community in his contribution. He emphasizes the importance of exchange and collaboration to drive best practices in the industry. He takes the opportunity to invite to SWISS GRC DAY 2024, an event that serves as a platform for professionals, executives and interested parties to share the latest trends and developments in governance, risk management and compliance.
The SWISS GRC DAY 2024 will take place on May 8, 2024 at the Radisson Blu, Zurich Airport. The event promises to be a landmark event for industry experts and stakeholders to share knowledge, network and discuss future challenges and opportunities.
For more information about the SWISS GRC DAY 2024, please visit our website **[www.swissgrcday.ch](http://www.swissgrcday.ch)** or contact us directly.
---
### [G[P]RC Summit 2024: Swiss GRC sponsors Riyadh and Dubai events](https://swissgrc.com/fr/news/gprc-summit-2024-swiss-grc-sponsors-riyadh-and-dubai-events/)
**Published:** janvier 16, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC announces its major sponsorship of the G[P]RC Summit 2024. This sponsorship covers two key events in the MEA/APAC region: in Riyadh, KSA, and Dubai, UAE, aligning with Swiss GRC's strategic growth and its recent establishment of a Dubai office.
**Content:**
**Swiss GRC announces its major sponsorship of the G\[P\]RC Summit 2024, showcasing its commitment to industry innovation and global expansion. This sponsorship covers two key events in the MEA/APAC region: in Riyadh, KSA, and Dubai, UAE, aligning with Swiss GRC’s strategic growth and its recent establishment of a Dubai office.**
The [G\[P\]RC summit](https://gprcsummit.com/), focusing on the integration of GRC with Performance and Strategy, represents a pivotal moment in the industry, and Swiss GRC’s presence underscores its role as a leader in the field. Swiss GRC’s sponsorship of this premier event is a testament to its innovative approach and expertise in the GRC domain. Known for designing solutions that prioritize efficiency and efficacy, Swiss GRC stands at the forefront of helping organizations navigate increasingly complex regulatory landscapes and manage risks effectively. The company’s [suite of tools](https://swissgrc.com/en/solutions/) and services is tailored to meet the nuanced needs of modern enterprises, enabling them to stay ahead of the curve in a rapidly evolving business world. The recent establishment of its [Dubai office](https://swissgrc.com/en/news/swiss-grc-opens-dubai-office-to-support-company-growth-in-the-region/) is a testament to its dedication to being closer to its clients in these regions, understanding their unique needs, and delivering tailored GRC solutions.
How to join us at the G\[P\]RC Summit 2024
Join Swiss GRC at the G\[P\]RC Summit 2024, a gathering of industry leaders and experts in Riyadh and Dubai. Here’s how you can be part of this pivotal event:
**Register Online:** Secure your spot by registering on the GPRC Summit 2024 official website. Early registration often comes with benefits, so don’t miss out!
**Event Dates and Venues:**
- Riyadh, KSA: January 24-25, at the Crowne Plaza.
- Dubai, UAE: January 29-30, at the JW Marriott Marina.
**Meet Swiss GRC’s Team:** Visit our booth to interact with our experts, including General Manager MEA/APAC **Rajeev Dutt** and Head of Product & Business Development **Nikolai Tsenov**. Explore how Swiss GRC provides a comprehensive suite of governance, risk, and compliance capabilities. This includes, among other things:
- **[Risk Management](https://swissgrc.com/en/risk-management-software/)**
- **[Information Security Management](https://swissgrc.com/en/information-security-management-isms-software/)**
- [**Third Party Risk Management**](https://swissgrc.com/en/tprm-software/)
- **[Business Continuity Management](https://swissgrc.com/en/bcm-software/)**
- **[Data Protection Management](https://swissgrc.com/en/data-protection-management-software/)**
About the G\[P\]RC Summit 2024
The G\[P\]RC Summit 2024 is more than a conference; it is a convergence of ideas and innovations in the world of GRC. Swiss GRC’s sponsorship and active participation reflect its role as a thought leader, eager to drive the conversation forward in governance, risk management, and compliance. The presence of Rajeev Dutt and Nikolai Tsenov further enhances Swiss GRC’s contribution to these vital discussions.
With a sense of excitement and anticipation, Swiss GRC looks forward to the G\[P\]RC Summit 2024. This event represents a unique opportunity for Swiss GRC to not only showcase its solutions but also to engage with other thought leaders and decision-makers in the industry. The company is prepared to make a significant impact, reaffirming its dedication to excellence and innovation in the GRC sphere.
Swiss GRC’s sponsorship and participation in the G\[P\]RC Summit 2024 highlight the company’s commitment to leading the way in Governance, Risk, and Compliance. The summit promises to be a transformative experience, with Swiss GRC at the forefront, shaping the future of the industry.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC receives kununu Top Company Seal 2024](https://swissgrc.com/fr/news/swiss-grc-receives-kununu-top-company-seal-2024/)
**Published:** janvier 19, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The employer rating platform kununu recognizes Swiss GRC as a Top Company 2024. The award is based on the independent ratings of employees on the platform. Swiss GRC is therefore one of the companies with the best working environment in Switzerland. As only around five percent of companies meet the qualification criteria, this is a very select group.
**Content:**
**The employer rating platform kununu recognizes Swiss GRC as a Top Company 2024. The award is based on the independent ratings of employees on the platform. Swiss GRC is therefore one of the companies with the best working environment in Switzerland.**
Swiss GRC is Switzerland’s leading software company in the development and implementation of [GRC solutions](https://swissgrc.com/en/solutions/). The Lucerne-based company now also operates internationally and is expanding within the DACH and MEA/APAC regions with offices in Germany, the UK and the United Arab Emirates. The [Top Company](https://www.kununu.com/ch/swiss-grc2) award underlines Swiss GRC’s outstanding achievements in creating an exemplary working environment. The kununu platform, known for its transparent and authentic employer reviews, ensures that only companies with the highest standards in terms of employee satisfaction and work culture receive this award.
« We congratulate Swiss GRC on receiving the Top Company Seal 2024 », says Nina Zimmermann, CEO of kununu. « The award is given to employers with particularly good ratings on kununu. As only around five percent of companies meet the qualification criteria, this is a very select group. Employers who are awarded the seal not only distinguish themselves through recognition and appreciation, but also send a strong signal to talented people who are looking for the right company, » Zimmermann continues.
« We are proud to be recognized by kununu as a Top Company 2024. This award is a confirmation of our tireless efforts to create a working environment in which our employees feel valued, motivated and supported, » says Besfort Kuqi, Co-Founder and CEO of Swiss GRC.
---
### [The future of IT: insights and forecasts in the CIO Yearbook 2024](https://swissgrc.com/fr/news/the-future-of-it-insights-and-forecasts-in-the-cio-yearbook-2024/)
**Published:** février 6, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The importance of governance, risk and compliance (GRC) in the digital age cannot be overstated, especially in the context of the advanced insights and predictions highlighted in the CIO Yearbook 2024. At this point, the relevance of GRC technologies, such as the GRC Toolbox from Swiss GRC, becomes particularly clear.
**Content:**
**The importance of governance, risk and compliance (GRC) in the digital age cannot be overstated, especially in the context of the advanced insights and predictions highlighted in the CIO Yearbook 2024.**
The CIO Yearbook 2024 marks the 13th year that leading minds in the IT industry in Germany have shared their fascinating visions and ground-breaking bets on the future of information technology. [This year](https://www.cio.de/a/die-it-fakten-der-groessten-deutschen-konzerne,2933083), the editors have once again compiled an impressive range of opinions and predictions from some of the industry’s most influential CIOs and experts.
In this context, the importance of [governance, risk management and compliance (GRC)](https://www.handelszeitung.ch/insurance/governance-risk-und-compliance-werden-noch-immer-reaktiv-betrieben-540959) in the digital age becomes even clearer. The CIO Yearbook 2024 takes a look at the specific challenges and opportunities facing the German market. The predictions from leading CIOs are nothing short of revolutionary: quantum computing will revolutionize pharmaceutical research by 2029, generative artificial intelligence (AI) will become the norm in companies and in the private sector, and even every public authority in Germany will have a CIO by 2029.
The rapid development of the technology landscape not only opens up significant opportunities, but also harbors new risks and challenges. This is where the relevance of GRC technologies, such as Swiss GRC’s GRC Toolbox, becomes particularly clear. These [solutions](https://swissgrc.com/en/solutions/) not only enable companies and authorities to adapt quickly to new technologies, but also ensure that they operate in line with the latest trends and technologies without neglecting governance, risk management and compliance aspects.
Tobias Regenfuß’ prediction about the evolution of the CIO role to C-AI-Os underlines the increasing importance of GRC strategies. The integration of AI into business processes requires comprehensive monitoring, control and compliance, and the ethical aspects, data protection and security must not be ignored.
In this context, the CIO Yearbook 2024 is not just a source of information, but a guide to the future of technology. It is an indispensable tool for taking a deep dive into the visions and trends that are shaping the IT world. Make sure you get a copy: .
---
### [Swiss GRC strengthens market presence with German subsidiary in Frankfurt](https://swissgrc.com/fr/news/swiss-grc-strengthens-market-presence-with-german-subsidiary-in-frankfurt/)
**Published:** mars 11, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC, Switzerland's leading provider of governance, risk and compliance (GRC) software solutions, is strengthening its commitment to the German market with the establishment of Swiss GRC Germany GmbH in Frankfurt am Main. This strategic initiative specifically addresses the growing demand for advanced GRC technologies among German companies.
**Content:**
**Frankfurt am Main, 11.03.2024 – Swiss GRC, Switzerland’s leading provider of governance, risk and compliance (GRC) software solutions, is strengthening its commitment to the German market with the establishment of Swiss GRC Germany GmbH in Frankfurt am Main. This strategic initiative not only signals the geographical expansion of Swiss GRC, but also specifically addresses the growing demand for advanced GRC technologies among German companies.**
Swiss GRC, known for its many years of expertise in the GRC sector, is bringing [innovative and effective solutions](https://swissgrc.com/en/solutions/) to Germany with its GRC Toolbox, one of the company’s core products. Based on proven methods and best practices, this software enables companies to manage their governance, risk management and compliance tasks precisely and effectively. With intuitive, configurable and scalable solutions, Swiss GRC aims to reduce the complexity of GRC processes for companies of all sizes. SMEs, as the backbone of the economy, particularly benefit from this approach, which allows them to focus on their core business while ensuring security and compliance in the background.
Besfort Kuqi, Co-Founder and CEO of Swiss GRC, comments on the importance of the expansion: « The establishment of Swiss GRC Germany GmbH is a significant step in our global growth strategy. Our presence here enables us to be closer to our German customers and offer GRC solutions tailored to their needs. »
Dr. Fino Scholl, now Managing Director of Swiss GRC Germany GmbH, emphasizes: « At Swiss GRC, we understand that topics such as risk management, business continuity management, [information security](https://swissgrc.com/en/information-security-management-isms-software/) and data protection are essential not only for large companies, but also for SMEs. Our aim is therefore to support companies of all sizes and industries with lean, tailor-made and cost-effective solutions. »
The increasing demand for GRC solutions in Germany and Europe reflects the importance of key regulations such as the GDPR (General Data Protection Regulation), MiFID II (Markets in Financial Instruments Directive II), Solvency II, NIS2 (Network and Information Systems Directive 2) and DORA (Digital Operational Resilience Act). However, the use of GRC systems goes beyond pure regulatory compliance. They are an essential management tool that enables companies to proactively identify risks and take preventive measures. This approach reflects Swiss GRC’s conviction that effective GRC solutions create real added value by strengthening organizational resilience, improving decision-making and helping to ensure the long-term success of the company.
---
**Contact for media requests:**
Dr. Fino Scholl
Managing Director
Swiss GRC Germany GmbH
Schumannstraße 27
60325 Frankfurt am Main
[www.swissgrc.com](http://www.swissgrc.com)
---
### [Focus on new technologies and AI at SWISS GRC DAY 2024](https://swissgrc.com/fr/news/focus-on-new-technologies-and-artificial-intelligence-at-swiss-grc-day-2024/)
**Published:** mars 19, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** SWISS GRC DAY returns in 2024 to provide governance, risk management and compliance (GRC) professionals with a unique platform for knowledge transfer, networking and innovation. Organized by Swiss GRC, the annual conference is expected to attract around 300 participants from Switzerland and nearby countries.
**Content:**
**Lucerne, 19.03.2024 – Swiss GRC Day returns in 2024 to provide governance, risk management and compliance (GRC) professionals with a unique platform for knowledge transfer, networking and innovation. Organized by Swiss GRC, Switzerland’s leading software company in the development and implementation of GRC solutions for companies worldwide, the conference will take place on 8 May 2024 at the Radisson Blu Hotel at Zurich Airport.**
The [Swiss GRC Day 2024](http://swissgrc.com/swissgrcday) will focus on new technologies and artificial intelligence (AI). A high-caliber speaker lineup will guide you through the latest developments in the risk landscape, from the increasing relevance of artificial intelligence in risk management to the complex challenges in cybersecurity and the essential importance of ESG for future-oriented corporate governance. Around 300 participants from Switzerland and neighboring countries are expected to attend.
Over the years, the Swiss GRC Day has established itself as a central meeting for GRC professionals and offers a platform that focuses on knowledge transfer, networking and the presentation of best practices and innovations. This year, participants can expect a wide range of presentations and discussions led by a first-class speaker line-up. These experts from industry and academia will provide insights into the latest trends and challenges facing the industry, including the role of artificial intelligence in risk management, recent developments in cyber security and the increasing importance of [environmental, social and governance (ESG)](https://www.synesgy.ch/) factors in corporate strategy.
With participants from Switzerland and neighboring countries, Swiss GRC Day 2024 offers a unique opportunity to network with like-minded individuals, form strategic partnerships and learn from the experiences of leading experts in the field. The event promises to be a catalyst for innovation and growth by providing participants with practical solutions to tackle current and future challenges.
---
**Contact for media requests:**
Yahya Mohamed Mao
Head Marketing & Communications
Swiss GRC AG
Hirschmattstr. 36
6003 Lucerne
[www.swissgrc.com](http://www.swissgrc.com)
---
### [Swiss GRC is positioned as a Strong Contender in the 2024 SPARK Matrix™ for GRC Platforms](https://swissgrc.com/fr/news/swiss-grc-strong-contender-in-the-2024-spark-matrix-for-grc-platforms/)
**Published:** avril 19, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Quadrant Knowledge Solutions has positioned Swiss GRC as a strong contender in the 2024 SPARK Matrix™ for Governance, Risk, and Compliance (GRC) Platforms. The Quadrant Knowledge Solutions SPARK Matrix™ provides competitive analysis and ranking of the world's leading GRC Platforms vendors. Swiss GRC has received strong ratings across the parameters of technology excellence and customer impact.
**Content:**
**Lucerne, April 19, 2024 – Quadrant Knowledge Solutions has positioned Swiss GRC as a strong contender in the 2024 SPARK Matrix™ for Governance, Risk, and Compliance (GRC) Platforms. The Quadrant Knowledge Solutions SPARK Matrix™ provides competitive analysis and ranking of the world’s leading GRC Platforms vendors. Swiss GRC, with its comprehensive technology and customer experience management, has received strong ratings across the parameters of technology excellence and customer impact.**
The [Quadrant Knowledge Solutions’ SPARK Matrix™](https://quadrant-solutions.com/report_type/spark-matrix) includes a detailed analysis of global market dynamics, major trends, vendor landscape, and competitive positioning. The study provides competitive analysis and ranking of the leading technology vendors in the form of its SPARK MatrixTM. The study offers strategic information for users to evaluate different provider capabilities, competitive differentiation, and market position.
According to Sahil Dhamgaye, Analyst at Quadrant Knowledge Solutions, « *Swiss GRC’s GRC Toolbox is a highly capable solution, offering a unified platform with integrated modules to simplify GRC management and eliminate data silos. Along with that, Swiss GRC’s focus on developing a resilience module and incorporating a third-party risk management (TPRM) module enhances proactive disruption management, compliance, and operational resilience. Their continuous innovation and expansion into EMEA and APAC regions signal a commitment to delivering a globally impactful GRC platform. »* « *Owing to Swiss GRC’s overall sophisticated Governance, Risk, and Compliance Platforms offerings, the strong value proposition for customers, and robust strategy and roadmap, the company has received strong ratings across the parameters of technology excellence and customer impact and is positioned as a strong contender in the 2024 SPARK MatrixTM: Governance, Risk, and Compliance Platforms.«* adds Sahil.

*« It is an honor for Swiss GRC to be designated as a Strong Contender in the 2024 SPARK Matrix™ for Governance, Risk, and Compliance Platforms, »* states Nikolai Tsenov, Head of Product and Business Development at Swiss GRC*. « This recognition is a testament to our strategic focus on innovation and our commitment to excellence in the GRC industry. It reflects our team’s dedication to developing solutions that not only address current industry challenges but also as a pioneer anticipate and shape future trends of the NextGen GRC domain taking full advantage of AI and Advanced Analytics. Moving forward, this acknowledgment reinforces our resolve to continue enhancing our product offerings and solidifying our position as industry leaders. »*
A GRC platform is a software solution that aids organizations in overseeing governance, risk management, and compliance activities in a unified manner. It includes tools to simplify processes, identify and address risks, maintain regulatory compliance, and enhance overall governance practices. The approach supports strategic business objectives and helps navigate the complexities of the business environment. GRC platforms often include modules for risk, compliance, policy, and audit management, providing a centralized platform for managing all GRC activities.
###### About Swiss GRC
Recognized as the leading software company in Switzerland for GRC (Governance, Risk & Compliance) solutions, Swiss GRC has built a wealth of expertise and experience over the years, resulting in the continuous improvement of the GRC Toolbox — a comprehensive software solution that encompasses modules such as [Risk Management](https://swissgrc.com/en/risk-management-software/), [Internal Controls Management](https://swissgrc.com/en/internal-control-software-ics/), [Business Continuity Management](https://swissgrc.com/en/bcm-software/), [Information Security Management](https://swissgrc.com/en/information-security-management-isms-software/), [Data Protection Management](https://swissgrc.com/en/data-protection-management-software/), Audit Management, Compliance Management, [Third-Party Risk Management](https://swissgrc.com/en/tprm-software/), [Contract Management](https://swissgrc.com/en/contract-management-software/), and [Business Process Management](https://swissgrc.com/en/bpm-software/). Reflecting its guiding principle of ‘Global Reach, Local Excellence’, Swiss GRC is expanding its global footprint within the DACH and MEA/APAC regions. With a growing global influence, Swiss GRC prioritizes the appreciation of local peculiarities and demands as essential elements of its operations. This expansion initiative encompasses the establishment of offices in [Germany](https://swissgrc.com/en/news/swiss-grc-strengthens-market-presence-with-german-subsidiary-in-frankfurt/), the United Kingdom, and the [United Arab Emirates](https://swissgrc.com/en/news/swiss-grc-opens-dubai-office-to-support-company-growth-in-the-region/).
###### Media contact
Mr. Yahya Mohamed Mao
Head of Marketing & Communications
Hirschmattstrasse 36
6003 Lucerne, Switzerland
Email:
Phone: +41 41 220 75 15
Website: [www.swissgrc.com](http://www.swissgrc.com)
###### About Quadrant Knowledge Solutions
Quadrant Knowledge Solutions is a global advisory and consulting firm focused on helping clients in achieving business transformation goals with Strategic Business and Growth advisory services. At Quadrant Knowledge Solutions, our vision is to become an integral part of our client’s business as a strategic knowledge partner. Our research and consulting deliverables are designed to provide comprehensive information and strategic insights for helping clients formulate growth strategies to survive and thrive in ever-changing business environments.
###### Quadrant contact
Mr. Ajinkya Ingle
Quadrant Knowledge Solutions
Regus Business Center35 Village Road, Suite 100,
Middleton Massachusetts 01949, United States
Email:
Phone: (+1) 978-605-1066
Website: [www.quadrant-solutions.com](https://quadrant-solutions.com/)
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [BENEFIT becomes first in Bahrain to adopt Swiss GRC technology](https://swissgrc.com/fr/news/benefit-becomes-first-in-bahrain-to-adopt-swiss-grc-technology/)
**Published:** septembre 2, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** BENEFIT, the Bahrain’s innovator and leading company in Fintech and electronic financial transactions services, is pleased to announce the signing of a landmark agreement with Swiss GRC to implement their comprehensive RegTech platform, the Governance, Risk, and Compliance (GRC) Toolbox.
**Content:**
**BENEFIT, the Kingdom of Bahrain’s innovator and leading company in Fintech and electronic financial transactions services, is pleased to announce the signing of a landmark agreement with Swiss GRC to implement their comprehensive RegTech platform, the Governance, Risk, and Compliance (GRC) Toolbox. The signing ceremony took place at BENEFIT’s headquarters, marking a milestone as the first company in Bahrain to adopt Swiss GRC’s centralized software solution.**
With its seamlessly integrated, role-based solutions, the Toolbox will enable [BENEFIT](https://benefit.bh/) to track GRC-related matters efficiently across all departments. The platform will produce detailed reports and dashboards to monitor and manage internal GRC issues. Additionally, it will establish a unified risk taxonomy, ensuring consistency and alignment across Internal Audit, Risk Management, Information Security, Legal, and Compliance departments with a shared framework and approach.
By implementing [Swiss GRC](https://swissgrc.com/en)’s holistic platform, BENEFIT aims to enhance its ability to identify, assess, and manage key organizational risks. This integration is expected to strengthen corporate accountability, improve financial, strategic, and operational efficiencies, and reduce risk profiles and incident costs, resulting in more robust overall performance.
On the occasion Abdulwahed AlJanahi, Chief Executive at BENEFIT, stated: “Our pioneering partnership with Swiss GRC represents a significant milestone for BENEFIT and sets a new benchmark for Governance, Risk, and Compliance in Bahrain. As the first company in the Kingdom to adopt this advanced Toolbox, we are not only streamlining our internal processes but also positioning Bahrain as a leader in governance and risk management innovation. This platform will play a key role in enhancing our risk awareness, strengthening organizational resilience, and delivering substantial benefits across our operations.”
“By integrating this comprehensive solution, we aim to fortify our governance framework, ensuring strategic alignment and driving sustainable progress in the financial sector. Ultimately, this underscores BENEFIT’s commitment to excellence and reflects our dedication to enhancing corporate accountability and operational efficiency,” he added.
Reinforcing this perspective, Besfort Kuqi, CEO of Swiss GRC, remarked, “We are very pleased to welcome BENEFIT as a key client in the Middle East. We are especially excited to guide and support BENEFIT on their journey toward Integrated Assurance. Our platform is designed to streamline all GRC activities, providing easy-to-use tools for data management, automation, and reporting to enhance organizational resilience and uphold regulatory standards. We look forward to a successful collaboration that will set new industry benchmarks..”
From his side, Mansoor AlAlwan, Chief of Internal Audit at BENEFIT, commented: “Migrating to Swiss GRC’s Toolbox is a crucial step in refining our internal audit processes and overall [risk management](https://swissgrc.com/en/risk-management-software/). The platform’s robust features will enable us to efficiently track and manage all GRC-related matters, streamline reporting, and maintain consistency across all departments. Additionally, this integration will significantly enhance our ability to identify and mitigate risks in real-time while improving our operational efficiency and helping us uphold the highest standards of compliance. We are confident it will further strengthen our internal controls and audit capabilities.”
By integrating the [holistic solution](https://swissgrc.com/en/solutions), BENEFIT reinforces its commitment to maintaining the highest standards of corporate governance. Guided by its principles of integrity, efficiency, and transparency, BENEFIT continuously strives to add value to Bahrain’s financial ecosystem, supporting long-term prosperity and enduring success.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [CEO’s Message: Global Reach, Local Excellence](https://swissgrc.com/fr/news/ceos-message-global-reach-local-excellence/)
**Published:** septembre 16, 2024
**Author:** Besfort Kuqi
**Excerpt:** 2024 has proven to be a successful year for Swiss GRC AG and I am pleased to provide an overview of our recent developments. Our company continues to show impressive growth momentum. This year we have seen a significant increase in turnover (+43%), expanded our team to around 60 dedicated and talented colleagues and gained many new clients who have placed their trust in us.
**Content:**
**Looking back on a successful year**
2024 has proven to be a successful year for Swiss GRC AG and I am pleased to provide an overview of our recent developments. Our company continues to show impressive growth momentum. This year we have seen a significant increase in revenue (+43%), expanded our team to around 60 dedicated and talented colleagues and gained many new clients who have placed their trust in us. We are particularly proud of the fact that we have succeeded in gaining an international foothold and establishing our presence in strategically important markets. We at Swiss GRC are grateful that our clients have joined us on this journey and have placed their trust in us to fulfill their GRC needs. I would like to thank all our clients and partners for these successes and their continued support.
**Long-term growth through international expansion**
As part of our new strategy, we are now focusing on sustainable growth through targeted market development and geographical expansion. In line with our motto “Global Reach, Local Excellence”, we have opened new branches in London, Frankfurt, Dubai, Mumbai and Pristina. These international locations are not only proof of our steady growth, but also a sign that we have established ourselves as a global player while remaining with our Swiss Headquarters locally rooted. With our new locations, we are now even closer to our customers and partners and can respond more quickly and efficiently to their specific needs – no matter where they are.
Our international client base already includes well-known companies such as Birlasoft (India), Rotana (UAE), Benefit (Bahrain), Neqsol (Azerbaijan), ConnectWise (USA), IAV (Germany) and ÖBB (Austria). This expansion strengthens both our global presence and the continuous development of our products to meet the diverse requirements and expectations of our customers. This benefits all our customers.
**Focus on security and compliance**
Information security and data protection are topics that are very close to our passion. Our expansion course is accompanied by an increased focus on these aspects. As a GRC software provider, information security and data protection are in our DNA. We are proud to be [certified](https://swissgrc.com/en/news/swiss-grc-ist-dreifach-iso-zertifiziert/) in accordance with the highest international standards such as ISO 27001 (information security), ISO 27701 (data protection) and ISO 27017 (cloud security) and to undergo regular independent audits. SOC2 certification is also imminent, which will further increase the security of our solutions. This certification will provide our customers with additional assurance that their data is not only stored securely, but is also subject to the highest standards of risk management. It goes without saying that we comply with all local laws and regulations in the countries in which we operate, thus ensuring the highest level of protection for customer data. We also adhere at all times to the rules agreed with our customers regarding data location and data transfer abroad.
**A look into the future**
Finally, I would like to emphasize that we owe our success above all to our customers, partners and employees. They enable us to turn our vision of “Global Reach, Local Excellence” into reality. Together, we look forward with confidence to a future characterized by innovation, growth and long-term success. We have big plans for the future and look forward to working together to develop innovative solutions that will help our customers and partners move forward.
Sincerely,
Besfort Kuqi
CEO Swiss GRC AG
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Rajeev Dutt honored as the Business Leader of the Year in Software Industry](https://swissgrc.com/fr/news/rajeev-dutt-honored-as-the-business-leader-of-the-year-in-software-industry/)
**Published:** octobre 4, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The Asian-African Economic Forum in Bangkok, Thailand, recognizes Rajeev Dutt’s exceptional leadership and his instrumental role in driving strategic growth and innovation across these dynamic regions for Swiss GRC. His efforts have not only strengthened Swiss GRC’s presence in the Middle East, Africa, and Asia Pacific but have also propelled the company towards new heights of technological innovation and business excellence.
**Content:**
**Lucerne, Switzerland – October 4, 2024 – Rajeev Dutt, General Manager MEA & APAC at Swiss GRC has been honored as the Business Leader of the Year in the Software Industry at the prestigious Business Excellence Leadership Awards 2024 in Bangkok, Thailand.**
With over 25 years of expertise in GRC and Business Continuity Management, Rajeev Dutt has a renowned track record of spearheading innovative GRC product offerings across diverse verticals. His work has significantly contributed to the growth of some of the world’s leading GRC software providers in the EMEA and APAC regions. At Swiss GRC, his role as General Manager for MEA and APAC reflects the company’s proactive approach in regions that are increasingly recognizing the value of [robust GRC structures](https://swissgrc.com/en/solutions).
The award, which was presented at the [Asian-African Economic Forum](https://asianafrican.org/) in Bangkok, Thailand, recognizes Rajeev Dutt’s exceptional leadership and his instrumental role in driving strategic growth and innovation across these dynamic regions for Swiss GRC. His extensive expertise and strategic insights are crucial in strengthening Swiss GRC’s presence and driving expansion in these critical markets.
« We are incredibly proud of Rajeev and his accomplishments, » said Besfort Kuqi, CEO of Swiss GRC. « This award is a testament to his unwavering dedication and vision in steering our operations to success in some of the most promising markets. Rajeev’s leadership not only enhances our technological and business capabilities but also integrates our presence across international landscapes. »
Swiss GRC remains committed to leveraging our leadership and innovative solutions to continue making significant impacts in the governance, risk, and compliance sectors globally.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [StorIT and Swiss GRC join forces to deliver GRC solutions across MENA](https://swissgrc.com/fr/news/storit-and-swiss-grc-join-forces-to-deliver-grc-solutions-across-mena/)
**Published:** octobre 14, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** StorIT, a leading value-added distributor of enterprise IT solutions, has partnered with Swiss GRC, a global provider of Governance, Risk, and Compliance (GRC) software, to expand the availability of Swiss GRC’s innovative solutions across the Middle East and North Africa (MENA).
**Content:**
**Lucerne/Dubai – StorIT, a leading value-added distributor of enterprise IT solutions, has partnered with Swiss GRC, a global provider of Governance, Risk, and Compliance (GRC) software, to expand the availability of Swiss GRC’s innovative solutions across the Middle East and North Africa (MENA). This collaboration will provide businesses with powerful, AI-driven GRC solutions that are simple to use, fast to implement, and tailored to meet the region’s unique regulatory demands.**
The MENA region is emerging as a critical hub for GRC adoption, driven by rising [cybersecurity threats](https://swissgrc.com/en/information-security-management-isms-software/), intricate regulatory frameworks, and a heightened focus on data protection. As organizations in the region recognize the importance of integrated and robust GRC frameworks, the partnership between Swiss GRC and [StorIT](https://storit.ae/) is poised to meet this growing demand. By leveraging Swiss GRC’s advanced GRC Toolbox—offered through deployment models like On-Premise, Private Cloud, and SaaS—businesses can ensure compliance with local regulatory standards while enhancing operational resilience. Additionally, with the support of a local data center in the UAE and full Arabic accessibility, Swiss GRC offers tailored solutions designed to meet the specific needs of the MENA region.
Commenting on the partnership, Suren Vedantham, Managing Director of StorIT, stated: « Our partnership with Swiss GRC will enable us to meet the growing need for comprehensive governance and risk management tools in the MENA region, helping businesses optimize their compliance and operational efficiency. »
Besfort Kuqi, CEO of Swiss GRC, added: « Partnering with StorIT allows us to accelerate our reach in the MENA region and bring our cutting-edge GRC technology to a broader market. Together, we will help businesses strengthen their governance frameworks and manage risks more effectively in today’s complex regulatory environment. »
Rajeev Dutt, General Manager MEA & APAC at Swiss GRC, emphasized the importance of the partnership: “As regulatory challenges evolve across the MENA region, companies need agile and integrated solutions to stay ahead. Our collaboration with StorIT is a key step in delivering those solutions and supporting businesses through these changes.”
The [Swiss GRC platform](https://swissgrc.com/en/solutions/) will equip StorIT’s clients with the tools needed to identify and manage risks effectively, enhancing both corporate accountability and operational resilience. Through its position as a leading IT distributor in the MENA region, StorIT will introduce Swiss GRC’s innovative solutions to a broad client base, driving wider adoption across multiple industries.
**About StorIT:**
StorIT is the Middle East’s leading Value-Added Distributor specialized in digital transformation solutions and services. In partnership with the world’s leading technology vendors, StorIT offers cutting-edge solutions to enterprise businesses across the Middle East & Africa through an extensive network of IT System Integrators and Solution Providers. With more than two decades of unparalleled domain expertise in the areas of Data Management solutions, Network Management & Security, Cyber Security, Cloud Solutions, HyperAutomation and AI, StorIT empowers its reseller channel partners to thrive in a rapidly evolving digital landscape by providing comprehensive turnkey solutions from discovery through deployment.
Visit [www.storit.ae](http://www.storit.ae/) for more information or email
**About Swiss GRC**
Swiss GRC, headquartered in Lucerne, Switzerland, is a leading provider of Governance, Risk, and Compliance (GRC) solutions. Its flagship product, the GRC Toolbox, offers a unified platform for managing risks, ensuring compliance, and fostering resilience across organizations. The company is known for its focus on innovation, integrating AI and advanced analytics into its solutions to stay ahead in the rapidly evolving GRC landscape.
Visit [www.swissgrc.com](https://www.swissgrc.com) for more information or email
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC and CAAS enter strategic partnership for GRC implementation](https://swissgrc.com/fr/news/swiss-grc-and-caas-enter-strategic-partnership-for-grc-implementation/)
**Published:** octobre 17, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** CAAS and Swiss GRC, a global provider of Governance, Risk, and Compliance (GRC) solutions, have joined forces to empower organizations across the Middle East, North Africa, and beyond with a next-generation GRC technology and expert advisory services.
**Content:**
**Lucerne/Dubai – CAAS and Swiss GRC, a global provider of Governance, Risk, and Compliance (GRC) solutions, have joined forces to empower organizations across the Middle East, North Africa, and beyond with a next-generation GRC technology and expert advisory services. This partnership is set to enhance the delivery of Swiss GRC’s GRC solutions across the Middle East and North Africa (MENA), empowering organizations with fast and efficient GRC implementation and localized deployment.**
The MENA region’s growing demand for [GRC solutions](https://swissgrc.com/en/solutions/) stems from increasingly complex regulatory frameworks, a wide range of compliance requirements, rising cybersecurity and privacy threats, and a heightened focus on organizational resilience. To meet these evolving challenges, organizations require simple, integrated solutions to empower companies and their employees to manage GRC activities more easily on a day-to-day basis.. Recognizing this, Swiss GRC has partnered with CAAS, a trusted expert in advisory and IT project execution, to ensure smooth and effective GRC deployments across the region. CAAS’s deep understanding of the local market’s regulatory challenges and their technical expertise make them the ideal implementation partner. Through this collaboration, Swiss GRC’s GRC Toolbox—with flexible deployment options (on-premise, private cloud, or SaaS)—can be seamlessly integrated, leveraging local UAE data centers and full Arabic support to meet users’ needs and the region’s strict data residency requirements. This partnership provides businesses with both cutting-edge technology and the localized expertise needed to navigate MENA’s regulatory and cybersecurity landscape effectively.
Venkatesh Mahadevan , Co-Founder of CAAS, emphasized the significance of the partnership: “As we embark on this strategic partnership with Swiss GRC, we are not just aligning our strengths; we are setting a new standard for Governance, Risk, and Compliance solutions. Together, we will empower organizations to navigate complexities with confidence, ensuring that compliance is not just a requirement but a cornerstone of sustainable growth.”
Besfort Kuqi, CEO of Swiss GRC, highlighted why CAAS was chosen as a strategic implementation partner: “CAAS’s local expertise, combined with their deep understanding of IT and GRC projects, ensures that businesses in MENA can quickly and effectively implement our GRC Toolbox. Their ability to navigate the region’s challenges makes them the ideal partner to help our clients achieve compliance and operational resilience.”
Rajeev Dutt, General Manager MEA & APAC at Swiss GRC, added: “This partnership allows us to combine advanced technology with deep regional knowledge, empowering businesses to stay ahead of compliance challenges.”
This implementation partnership between Swiss GRC and CAAS brings together cutting-edge technology and expert local support, offering businesses in the MENA region a seamless way to implement advanced GRC solutions.
**About CAAS:**
CAAS provides expert IT consultancy, specializing in CIO advisory, strategic planning, and project execution. With decades of experience, CAAS helps organizations implement tailored IT solutions, drive innovation, and meet business objectives. Whether for long-term strategies or specific projects, CAAS ensures optimized IT performance for sustainable growth.
For more information, visit [www.caas.com](http://www.caas.com).
**About Swiss GRC**
Swiss GRC, headquartered in Lucerne, Switzerland, is a leading provider of Governance, Risk, and Compliance (GRC) solutions. Its flagship product, the GRC Toolbox, offers a unified platform for managing risks, ensuring compliance, and fostering resilience across organizations. The company is known for its focus on innovation, integrating AI and advanced analytics into its solutions to stay ahead in the rapidly evolving GRC landscape.
For more information, visit [www.swissgrc.com](https://www.swissgrc.com).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC sponsors Integrity Europe Conference 2024](https://swissgrc.com/fr/news/swiss-grc-sponsors-integrity-europe-conference-2024/)
**Published:** octobre 30, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC is thrilled to announce its sponsorship of the Integrity Europe Conference, a premier event bringing together global experts in compliance, risk management, and ESG governance and held on November 7 and 8, 2024, at Hochschule Luzern’s Zug-Rotkreuz campus.
**Content:**
**Swiss GRC is thrilled to announce its sponsorship of the Integrity Europe Conference 2024, a premier event bringing together experts in compliance, risk management, and ESG governance. Held on November 7 and 8, 2024, at Hochschule Luzern’s Zug-Rotkreuz campus, the conference is anticipated to be a landmark gathering for professionals across industries.**
Organized [Lucerne University of Applied Sciences and Arts (HSLU)](http://www.hslu.ch/) with the support of the KBA NotaSys Integrity Fund, which has championed numerous impactful projects in the GRC space, the [Integrity Europe Conference](https://www.hslu.ch/en/lucerne-school-of-business/calendar/events/2024/11/07/integrity-europe-conference/) aims to advance the latest insights and frameworks essential for resilient corporate practices.
[Swiss GRC](http://www.swissgrc.com/en) will be represented by Besfort Kuqi, CEO, Nikolai Tsenov, Head Strategy & Business Development, Gentian Ajeti, Head Consulting, Yahya Mohamed Mao, Head Marketing & Communications, and Nora Wyss, Sales & Account Manager. They are looking forward to engaging in vibrant discussions, sharing their expertise and vision for the future of governance, risk, and compliance (GRC).
A highlight of the event will be the exclusive release of the ERM Report 2024, a highly anticipated publication developed by Prof. Dr. Stefan Hunziker of Hochschule Luzern and Prof. Dr. Ute Vanini of FH Kiel. For the [second consecutive year](https://swissgrc.com/erm-report-2023-finanzielle-resilienz-im-fokus/), Swiss GRC has contributed valuable insights to this influential report, which will be revealed during the conference.
Participants can expect a rich program, featuring keynotes, panels, and interactive workshops led by industry visionaries, including Dr. Andreas Pleßke of Koenig & Bauer, Nina Stoeckel of Boehringer Ingelheim, and Antonio Hautle of the UN Global Compact Network Switzerland & Liechtenstein. Topics will range from supply chain compliance and export control to cybersecurity under the NIS 2 Directive and the ethical deployment of AI—all highly relevant in today’s rapidly evolving GRC industry.
Join us at the Integrity Europe Conference, taking place on November 7-8, 2024, at Hochschule Luzern’s Zug-Rotkreuz campus, where top experts in compliance, [risk management](https://swissgrc.com/en/risk-management-software/), and ESG governance will gather. This premier event is tailored for CFOs, CEOs, practitioners, and researchers eager to explore the latest industry insights and connect with peers. Don’t miss your chance to gain invaluable knowledge and networking opportunities in the evolving world of GRC.
Secure your spot today to be part of this exceptional experience!
Discover the full program and register [here](https://lnkd.in/ecjkxeRy).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [ERM Report 2024: Swiss companies outperform in resilience](https://swissgrc.com/fr/news/erm-report-2024-swiss-companies-outperform-in-resilience/)
**Published:** novembre 13, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The ERM Report 2024, developed by the Institute of Financial Services Zug IFZ at Lucerne School of Business and the Institute for Controlling at Kiel University of Applied Sciences, highlights the resilience strategies of companies across the DACH region, with Swiss firms emerging as leaders in financial stability.
**Content:**
**In a time of persistent economic uncertainty, the ERM Report 2024 highlights the resilience strategies of companies across the DACH region, with Swiss firms emerging as leaders in financial stability. This year’s report, developed by the Institute of Financial Services Zug IFZ at Lucerne School of Business and the Institute for Controlling at Kiel University of Applied Sciences, provides a comprehensive analysis based on a seven-year study of 500 companies, offering insights into resilience practices that have helped organizations navigate recent “polycrises”—successive economic challenges compounded by global and regional pressures.**
While companies across Germany and Austria continue to grapple with the effects of these challenges, Swiss organizations stand out for their proactive approach to risk management, robust liquidity planning, and adaptive strategic measures. Yet, despite Switzerland’s impressive resilience, the report indicates that economic strains are beginning to impact even the most stable Swiss firms. After a short recovery following the pandemic, new pressures are emerging, putting resilience strategies to the test.
**Key insights from the ERM Report 2024**
The ERM Report identifies three essential pillars for financial resilience that companies in the DACH region can harness to bolster their stability and adaptability: **Enterprise Risk Management (ERM)**, **Strategic Resilience**, and **Resource Management**.
- **Enterprise Risk Management (ERM)**: Swiss companies lead in proactive risk management, incorporating scenario analysis, stress testing, and liquidity planning. This approach enables them to detect emerging risks early and to respond quickly, preserving stability in turbulent times.
- **Strategic Resilience**: The report emphasizes that building resilience goes beyond finances, requiring adaptability within corporate structures and culture. Swiss firms excel here, fostering a “resilience culture” driven by leadership commitment, supply chain diversification, and agile business models that position them to seize opportunities during crises.
- **Resource Management**: Financially resilient companies also manage resources effectively, maintaining high equity ratios, steady revenue growth, and flexible liquidity reserves. While Swiss companies are notable for their liquidity strength, Austrian firms face heightened vulnerabilities due to higher debt levels and less adaptable cost structures. This gap underscores the importance of flexibility in financial management across the region.
**A comparative view of resilience in the DACH region**
The ERM Report 2024 offers a comparative analysis of resilience in the DACH region, highlighting the unique strengths and challenges within each country:
- **Switzerland**: Swiss firms are overrepresented among resilient companies, showcasing strong equity positions, low insolvency risks, and solid revenue growth. However, even these firms are beginning to feel the effects of compounded crises as pressures mount.
- **Germany**: German companies demonstrate moderate resilience, though they remain exposed to vulnerabilities within global supply chains.
- **Austria**: Austrian firms face greater risks due to higher debt burdens and less flexibility in cost structures, signaling an urgent need for enhanced resilience practices.
**Swiss GRC’s contribution to the ERM Report 2024**
Swiss GRC is proud to have contributed to the ERM Report 2024 with a guest article titled **“Financial Sustainability Through Integrated Risk Management and Resilience,”** authored by CEO, Besfort Kuqi, Head Marketing & Communications, Yahya Mohamed Mao, and Head Business Strategy & Business Development, Nikolai Tsenov. The article presents resilience as a cornerstone of sustainable growth, exploring how organizations can achieve long-term financial stability by embedding resilience within their core [risk management](https://swissgrc.com/en/risk-management-software/) frameworks.
Swiss GRC’s piece emphasizes practical strategies, such as building financial buffers, enhancing supply chain resilience, and cultivating a resilience-focused corporate culture. The article underscores that resilience is not only a defensive strategy but a pathway to sustainable growth, helping companies to build trust with stakeholders and navigate today’s complex risk landscape with confidence.
For a deeper dive into the findings and to explore Swiss GRC’s perspectives on resilience, download the full **ERM Report 2024** [here](https://hub.hslu.ch/financialmanagement/wp-content/blogs.dir/488/files/sites/16/2024/11/ERM-Report-2024.pdf).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC recognized by Great Place To Work®: Employer attractiveness at a high level](https://swissgrc.com/fr/news/swiss-grc-recognized-by-great-place-to-work-employer-attractiveness-at-a-high-level/)
**Published:** novembre 19, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC has received another significant recognition: the international organization Great Place To Work® has honored the company as an outstanding employer. With an overall score of 84% in the employee survey, the results highlight the high satisfaction of the workforce – with trust in leadership, rated as exceptionally high by employees, standing out as a key factor.
**Content:**
**Lucerne, November 19, 2024 – Swiss GRC has received another significant recognition: the international organization Great Place To Work® has honored the company as an outstanding employer. With an overall score of 84% in the employee survey, the results highlight the high satisfaction of the workforce – with trust in leadership, rated as exceptionally high by employees, standing out as a key factor.**
Great Place To Work® is a globally recognized institution that helps organizations create high-performing and trustworthy workplace cultures. The award is based on a comprehensive and anonymous employee survey. The goal is to spotlight the best employers while identifying opportunities for improvement. The survey results for Swiss GRC show that the company excels particularly in leadership, workplace safety, and collaboration. These results not only reflect the satisfaction of the workforce but also highlight Swiss GRC’s commitment to supporting the people behind its success.
**Growth and responsibility go hand in hand**
Swiss GRC has experienced impressive growth in recent years. This strong expansion has not only opened new opportunities but also placed a renewed focus on the importance of a positive workplace culture. The recognition by Great Place To Work® is therefore a key milestone. It confirms that employees thrive in an environment built on trust, appreciation, and support – values that establish Swiss GRC as an innovative and responsible employer.
Beyond the acknowledgment, the survey results are a crucial impetus for continuous improvement. Swiss GRC plans to leverage the insights gained to better address employee needs and further enhance working conditions.
« The high level of trust in leadership and the strong overall ratings show that employees feel supported in their work. At the same time, the feedback provides valuable guidance on where there is room for development to maintain a high standard of workplace culture, » explains Natalie Metry, Head Admin, HR & Finance at Swiss GRC.
The recognition by Great Place To Work® underscores that success and responsibility go hand in hand. It provides a clear mandate to continue along this path with determination.
For more information, visit [www.swissgrc.com](http://www.swissgrc.com).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Double Recognition for Swiss GRC at the 2024 Technology Innovator Awards](https://swissgrc.com/fr/news/double-recognition-for-swiss-grc-at-the-2024-technology-innovator-awards/)
**Published:** novembre 29, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC has been honored with two prestigious awards at the 2024 Technology Innovator Awards. The company received the Excellence Award for Governance, Risk, and Compliance Technology and was named the Innovative GRC Solutions Provider of the Year, underscoring its role in delivering practical, customer-focused solutions for modern GRC challenges.
**Content:**
**Swiss GRC, a leading provider of Governance, Risk, and Compliance (GRC) solutions, has achieved a significant milestone by winning two distinguished honors at the 2024 Technology Innovator Awards. The company received the Excellence Award for Governance, Risk, and Compliance Technology and was named Most Innovative GRC Solutions Provider of the Year. These awards recognize Swiss GRC’s ability to deliver practical and effective solutions to the evolving challenges of the GRC landscape.**
Headquartered in Lucerne, Switzerland, Swiss GRC is at the forefront of the GRC industry with its flagship product, the GRC Toolbox. Designed as a unified platform, the GRC Toolbox helps organizations streamline risk management, maintain compliance, and enhance operational resilience. With a commitment to « Global Reach, Local Excellence, » Swiss GRC has established a strong international presence with offices in London, Frankfurt, Dubai, Mumbai, and Pristina. This global network allows the company to deliver tailored solutions while addressing regional requirements effectively.
The [Technology Innovator Awards](https://www.innovationinbusiness.com/awards/technology-innovator-awards/), hosted by the UK-based digital media platform Innovation in Business and supported by AI Global Media, recognize organizations that demonstrate outstanding innovation and leadership. The evaluation process for the awards is rigorous and objective, involving a detailed review of the nominee’s digital presence, customer feedback, media coverage, and supporting documentation. Swiss GRC’s recognition reflects its ability to meet these high standards and deliver solutions that resonate with organizations across industries.
Swiss GRC stands out in a crowded market by prioritizing practical, user-driven solutions over purely theoretical or overly complex approaches. The GRC Toolbox is designed to integrate seamlessly into organizations’ operations, addressing compliance and risk management needs without adding unnecessary complications. By focusing on usability and effectiveness, Swiss GRC ensures its solutions are not only innovative but also actionable and based on best practices.
The dual recognition highlights Swiss GRC’s continued success in providing solutions that address the real-world challenges of governance, risk, and compliance. As businesses face increasingly complex regulatory and operational environments, Swiss GRC remains a trusted partner, delivering tools that empower organizations to navigate these challenges with confidence. For organizations seeking reliable, results-driven GRC solutions, Swiss GRC offers a proven track record of success.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC and OpResONE, Inc. Launch Strategic Partnership for GRC Implementation in North Americas](https://swissgrc.com/fr/news/swiss-grc-and-opresone-inc-launch-strategic-partnership-for-grc-implementation-in-north-americas/)
**Published:** décembre 4, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** OpResONE, Inc., a leading provider of resilience and operational advisory services, has partnered with Swiss GRC to bring advanced Governance, Risk, and Compliance (GRC) solutions to organizations across the United States and Canada.
**Content:**
**Lucerne/New York, December 4, 2024 – OpResONE, Inc., a leading provider of resilience and operational advisory services, has partnered with Swiss GRC to bring advanced Governance, Risk, and Compliance (GRC) solutions to organizations across the United States and Canada.**
This collaboration aims to deliver [Swiss GRC’s](https://www.swissgrc.com) multi-award winning GRC Toolbox with localized expertise and strategic guidance of OpResONE, Inc., enabling organizations to implement robust GRC solutions efficiently and effectively. Renowned for its seamless integration into business operations and its focus on practical, user-centric solutions over overly complex or theoretical approaches, the GRC Toolbox empowers businesses to strengthen their GRC strategies. In addition to GRC, [OpResONE, Inc.](https://opresone.com/) will focus on integration of Operational Resilience with GRC Frameworks, along with Business Continuity Strategies. This alignment will fuel accelerated growth to Operational Resilience.
The U.S. market’s demand for GRC solutions continues to rise due to increasingly stringent regulations, complex compliance requirements, and evolving cybersecurity threats. This partnership addresses these needs by combining Swiss GRC’s innovative technology with OpResONE’s deep-rooted expertise in operational resilience and regulatory advisory, ensuring a seamless deployment experience tailored to U.S. businesses. OpResONE’s understanding of regulatory landscapes, combined with Swiss GRC’s adaptable deployment options (on-premises, private cloud, or SaaS), offers organizations flexibility and confidence in meeting data residency and compliance requirements.
Joseph Brewer, CEO of OpResONE, Inc., shared his perspective on the partnership: “This collaboration with Swiss GRC not only aligns with our mission to provide resilient and compliant solutions, but also empowers organizations to confidently address today’s complex GRC challenges. Together, we are dedicated to delivering an unparalleled level of service and support that enables sustainable growth and long-term operational resilience. THINK INTEGRATION and SINGLE PLATFORM! It’s truly a WIN-WIN.”
Besfort Kuqi, CEO of Swiss GRC, emphasized the strategic value of the partnership: “OpResONE’s expertise in U.S. regulatory requirements and their comprehensive approach to operational resilience make them the ideal partner for delivering our GRC Toolbox. Together, we can offer businesses a faster, more efficient path to achieving compliance and risk mitigation, ultimately developing solid frameworks for resilience.”
This strategic alliance between OpResONE, Inc. and Swiss GRC merges cutting-edge technology with specialized local support, providing U.S.-based organizations with a robust solution to navigate today’s demanding regulatory and cybersecurity landscape.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [VZK and Swiss GRC join forces to strengthen GRC in Zurich hospitals](https://swissgrc.com/fr/news/vzk-and-swiss-grc-join-forces-to-strengthen-grc-in-zurich-hospitals/)
**Published:** décembre 6, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The Association of Zurich Hospitals (VZK), which employs around 40,800 staff at 35 institutions and treats 243,000 inpatients every year, and Swiss GRC, a renowned provider of software solutions in the areas of governance, risk and compliance (GRC), will be working together in future to strengthen GRC in Zurich hospitals. The University Hospital Zurich (USZ) is taking the first step in the collaboration.
**Content:**
**Zurich/Lucerne – The Association of Zurich Hospitals (VZK), which employs around 40,800 staff at 35 institutions and treats 243,000 inpatients every year, and Swiss GRC, a renowned provider of software solutions in the areas of governance, risk and compliance (GRC), will be working together in future to strengthen GRC in Zurich hospitals. The University Hospital Zurich (USZ) is taking the first step in the collaboration.**
The goal of the partnership is to integrate GRC solutions in a practical and efficient way in Zurich hospitals to meet the complex requirements of the healthcare sector. The challenges are many: regulatory requirements, protection of sensitive patient data, proactive risk management and resource-saving operational management. A solid GRC strategy helps hospitals ensure compliance, optimize the quality of patient care, and provide transparency and security. Thanks to [Swiss GRC’s many years of experience](https://swissgrc.com/en/news/double-recognition-for-swiss-grc-at-the-2024-technology-innovator-awards/ "Double Recognition for Swiss GRC at the 2024 Technology Innovator Awards"), Zurich’s hospitals have access to the tools and resources they need to meet these increasing demands and strengthen the resilience of the healthcare system in the long term.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)

André Baumgart, Head of Digitalisation, Quality Management, IT and Patient Safety at VZK, emphasises the importance of the cooperation: “With Swiss GRC as a partner, we can meet the high requirements for governance, risk management and compliance in our hospitals even better.”

Besfort Kuqi, CEO of Swiss GRC, adds: “We are proud to be working with the VZK to further develop the standards for GRC in Zurich hospitals. With our expertise, we support hospitals in creating sustainable and future-proof GRC structures that meet the high demands of the healthcare sector.”
This strategic alliance sends out an impressive signal for the future of healthcare in the Canton of Zurich and far beyond. It lays the foundation for safe, compliant and efficient operational management in the region, allowing the hospitals to concentrate on their essential task – the care of patients.
**About the VZK** The Association of Zurich Hospitals (VZK) represents the interests of 35 hospitals in the canton of Zurich, which employ around 40,800 people and treat 243,000 inpatients every year. The VZK promotes the quality and efficiency of healthcare and supports its members in complying with regulatory requirements and optimizing operational processes.
Further information can be found at: [www.vzk.ch](http://www.vzk.ch).
**About Swiss GRC**
Swiss GRC, based in Lucerne, is a leading provider of governance, risk and compliance (GRC) solutions. The company’s GRC toolbox offers a comprehensive platform with solutions in the areas of risk management, ICS, BCM, information security, data protection, compliance, TPRM and contract management. Swiss GRC is characterized by innovative solutions and a high level of user-friendliness.
Further information can be found at: [www.swissgrc.com](http://www.swissgrc.com).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [NEQSOL Holding selects Swiss GRC to digitalize Risk Management and Compliance Functions](https://swissgrc.com/fr/news/neqsol-holding-selects-swiss-grc-to-digitalize-risk-management-and-compliance-functions/)
**Published:** décembre 23, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** NEQSOL Holding, an international group of companies, has signed a landmark agreement with Swiss GRC to digitalize its comprehensive Governance, Risk, and Compliance (GRC) business functions.
This partnership follows a highly competitive and extensive evaluation, where Swiss GRC's offerings and platform capabilities stood out among prominent market players.
**Content:**
**Lucerne & Baku, Azerbaijan – NEQSOL Holding, an international group of companies, has signed a landmark agreement with Swiss GRC to digitalize its comprehensive Governance, Risk, and Compliance (GRC) business functions. This partnership follows a highly competitive and extensive evaluation, where Swiss GRC’s offerings and platform capabilities secured this partnership, standing out among prominent market players.**
As part of the initial implementation, [NEQSOL Holding](https://www.neqsolholding.com/) will deploy Swiss GRC modules for its already developed frameworks, such as Enterprise Risk Management, Compliance, HSE, Internal Controls, Incident Management, and several others.
This move is a natural progression for NEQSOL Holding and its subsidiaries – Azerconnect Group, Vodafone Ukraine, Bakcell, and Norm – as they strive to enhance their business processes and support continued growth.
Speaking about the partnership, **Imran Ahmadzada, CFO of NEQSOL Holding and Head of NEQSOL Holding Azerbaijan**, said: “This is an important move for the Holding since, as a pioneer in Risk Management, Governance, and Compliance, our maturity level requires the implementation of advanced digital tools. We believe that this partnership with Swiss GRC will help us fully digitalize those systems in all group companies of NEQSOL Holding.”
**Samir Karimov, Head of Risk Management at NEQSOL Holding**, explained: “Implementing Swiss GRC will give us a reliable framework to oversee and control risks across all our various business sectors. The Swiss GRC platform will help us make our processes more efficient, increase transparency, and better handle risks throughout our business.”
**Besfort Kuqi, CEO of Swiss GRC**, emphasized the significance of this milestone: « We are honored to welcome NEQSOL Holding as one of our major multinational clients. The rigorous evaluation process reflects the strength of our platform and services, and we look forward to supporting NEQSOL Holding’s ambitious GRC initiatives. This is a major statement for Swiss GRC as we continue to expand globally. »
**Rajeev Dutt, General Manager MEA & APAC at Swiss GRC**, highlighted the strategic value of the collaboration: « Partnering with a group like NEQSOL Holding is a testament to the versatility and scalability of the GRC Toolbox. This collaboration underscores our commitment to delivering innovative solutions that empower organizations to navigate complex regulatory environments effectively. »
Swiss GRC’s platform empowers NEQSOL Holding to proactively manage risks, enhance accountability, and strengthen operational resilience across the entire group. The use of custom-built modules highlights Swiss GRC’s ability to adapt their solutions to the specific needs of diverse and complex organizations.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
**About NEQSOL Holding**
NEQSOL Holding is an international group of companies operating in 11 countries across the telecommunications, energy, construction, and hi-tech industries. NEQSOL Holding’s commitment to governance, risk management, and compliance is part of its strategy to ensure sustainable and responsible business practices. For more information, visit: [www.neqsolholding.com](http://www.neqsolholding.com).
**About Swiss GRC**
Swiss GRC, headquartered in Lucerne, Switzerland, is a leading provider of Governance, Risk, and Compliance (GRC) solutions. Its flagship product, the GRC Toolbox, offers a unified platform for managing risks, ensuring compliance, and fostering resilience across organizations. With its commitment to « Global Reach, Local Excellence, » Swiss GRC has expanded its presence globally. The company is known for its focus on innovation, integrating AI and advanced analytics into its solutions to stay ahead in the rapidly evolving GRC landscape. For more information, visit: [www.swissgrc.com](http://www.swissgrc.com).


[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [G[P]RC Summit 2025: Swiss GRC Returns as Platinum Sponsor in Riyadh and Dubai](https://swissgrc.com/fr/news/gprc-summit-2025-swiss-grc-returns-as-platinum-sponsor-in-riyadh-and-dubai/)
**Published:** janvier 22, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC has reaffirmed its commitment to the global GRC community by returning as a Platinum Sponsor at the G[P]RC Summit 2025 in Riyadh and Dubai. This marks the second consecutive year the company has supported the prestigious event, further solidifying its leadership in advancing GRC practices across industries.
**Content:**
**Swiss GRC continues to solidify its ever increasing impact in the global GRC space by returning as a Platinum Sponsor at the prestigious G\[P\]RC Summit 2025. The event, held in Riyadh on 19-20 January 2025 and in Dubai on 22-23 January 2025, once again brought together top GRC professionals and decision-makers from around the world to discuss the latest trends and innovations in the field.**
The [G\[P\]RC Summit](https://gprcsummit.com/), a premier gathering of GRC professionals, offered an unparalleled platform for industry leaders, innovators, and decision-makers to explore the evolving challenges and opportunities in risk management and regulatory compliance. As a Platinum Sponsor, Swiss GRC was proud to co-host a booth with its trusted partner, [StorIT](https://storit.ae/), showcasing [integrated GRC solutions](https://swissgrc.com/en/solutions) designed to empower organizations to achieve operational resilience, mitigate risks, and navigate the increasingly complex global regulatory environment.
At both events, Swiss GRC demonstrated its thought leadership through its participation in high-impact discussions and presentations. **Rajeev Dutt**, General Manager for MEA & APAC, was a prominent figure in the summit’s speaker lineup, where he delivered an expert-led session on the critical role of [proactive risk management](https://swissgrc.com/en/risk-management-software/). In his presentation, Rajeev emphasized how organizations can embed integrated GRC frameworks within their strategies to fortify operations against uncertainty and ensure long-term business success. His insights were met with high praise from a distinguished audience, reinforcing Swiss GRC’s reputation as an authority in the GRC space.
While Rajeev Dutt and Babu Manickan, Senior Presales Manager – GRC Solutions, successfully represented Swiss GRC in Riyadh, CEO, Besfort Kuqi, Head Consulting, Gentian Ajeti and Senior GRC Consultant, Faruk Türk joined them in Dubai. This strong leadership presence not only demonstrated Swiss GRC’s commitment to the Middle East region but also highlighted the company’s growing global reach and its ability to cater to the diverse needs of the GRC community worldwide.
Swiss GRC’s engagement at the G\[P\]RC Summit 2025 marks another important milestone in the company’s journey toward establishing itself as a global leader in the GRC space. By co-hosting with StorIT and engaging with industry experts and decision-makers, Swiss GRC continues to elevate the conversation around GRC best practices, regulatory compliance, and risk management, all while expanding its presence across key global markets. As the demand for integrated GRC solutions grows, Swiss GRC is uniquely positioned to lead the way, empowering organizations worldwide to navigate the challenges of a rapidly evolving business landscape with confidence, resilience, and strategic foresight.
About the G\[P\]RC Summit 2025
The G\[P\]RC Summit 2025 marks a defining moment for the global Governance, Risk, and Compliance (GRC) community. This year’s summit goes beyond the traditional conference format, acting as a dynamic convergence of cutting-edge ideas, innovative solutions, and forward-thinking strategies. Swiss GRC’s involvement as a Platinum Sponsor highlights its commitment to staying at the forefront of the GRC landscape, driving the dialogue on how organizations can better navigate today’s complex risk environment. The summit serves as an unparalleled platform for industry leaders, regulators, and decision-makers to come together and share insights on the future of governance, risk, and compliance. Swiss GRC, with its global reach and comprehensive approach to risk management, continues to play a pivotal role in shaping the future of the GRC industry. Through its sponsorship, the company underscores its role as a thought leader in this ever-evolving field.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [India‘s IT Giant Birlasoft selects Swiss GRC to boost Cyber Resilience](https://swissgrc.com/fr/news/indias-it-giant-birlasoft-selects-swiss-grc-to-boost-cyber-resilience/)
**Published:** janvier 26, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Birlasoft has signed a landmark agreement with Swiss GRC to implement their comprehensive Governance, Risk, and Compliance (GRC) Toolbox. This agreement marks Swiss GRC’s first significant win in India, bringing their advanced solutions to one of the country’s top IT companies.
**Content:**
**New Delhi/Lucerne – Birlasoft, a global leader in digital transformation and IT consulting, has signed a landmark agreement with Swiss GRC to implement their comprehensive Governance, Risk, and Compliance (GRC) Toolbox. This agreement marks Swiss GRC’s first significant win in India, bringing their advanced solutions to one of the country’s top IT companies.**
Operating across 29 countries, Birlasoft will initially deploy Swiss GRC’s modules covering Risk, [Third-Party Risk Management (TPRM)](https://www.swissgrc.com/en/tprm-software), Audit, ISMS, Policy Management, and Business Continuity Management (BCM). The implementation will provide Birlasoft with a centralized platform to streamline GRC-related matters across all departments, enhancing risk oversight and compliance efficiency. By adopting Swiss GRC’s [holistic platform](https://www.swissgrc.com/en/solutions), Birlasoft will gain access to detailed reports and dashboards that monitor and manage internal GRC issues, establishing a unified risk framework across various functions like Internal Audit, Risk Management, Information Security, Legal, and Compliance.
Commenting on the partnership, **Cdr Sanjeev Singh, CISO and Data Protection Officer of Birlasoft, and Former Director IT of the Indian Navy** stated: « Our collaboration with Swiss GRC is a critical step in optimizing our GRC framework. The GRC Toolbox will enhance our internal processes, fortify our risk management capabilities, and reinforce our commitment to governance excellence. With Swiss GRC’s innovative solutions, we are confident that Birlasoft will experience operational efficiencies and improved risk mitigation. »
**Aalok Mishra, Associate Director of Birlasoft** added: « Implementing Swiss GRC’s platform is a game-changer for Birlasoft. It not only equips us with the tools to manage risk and compliance more effectively but also positions us to drive greater value for our clients by embedding GRC best practices into our operations. »
**Besfort Kuqi, CEO of Swiss GRC**, expressed excitement about the collaboration: « We are excited to welcome Birlasoft as our first major client in India, marking a crucial moment in our international expansion. Securing this partnership against major competitors is a testament to the strength of Swiss GRC’s platform. We are eager to see the positive impact our solutions will have on Birlasoft’s operations and their clients globally. »
**Rajeev Dutt, General Manager MEA & APAC at Swiss GRC**, emphasized the strategic importance of the partnership: « Birlasoft is a key partner for us as we expand our footprint in India and beyond. Their decision to implement Swiss GRC not only reflects our product’s strength but also opens the door to future collaboration across their client network. We look forward to working closely with them to deliver impactful results. »
The Swiss GRC platform will empower Birlasoft to proactively identify and manage risks, improving corporate accountability and operational resilience. Additionally, as a major player in digital transformation and consulting, Birlasoft’s GRC practice will promote Swiss GRC’s solutions to its clients, paving the way for broader adoption across global markets. This strategic collaboration reinforces Birlasoft’s commitment to maintaining the highest standards of corporate governance, operational efficiency, and risk management, with Swiss GRC poised to deliver substantial long-term benefits.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
**About Birlasoft**
Birlasoft, part of the CK Birla Group, is a global IT services provider specializing in digital transformation solutions. With a presence in 29 countries, Birlasoft delivers technology-led solutions across various industries, driving innovation and business agility through a combination of deep domain expertise and cutting-edge technologies. Their services span enterprise modernization, cloud services, and digital consulting, aimed at helping clients enhance their IT ecosystems and improve operational efficiency. For more information, visit: [www.birlasoft.com](https://www.birlasoft.com).
**About Swiss GRC**
Swiss GRC, headquartered in Lucerne, Switzerland, is a leading provider of Governance, Risk, and Compliance (GRC) solutions. Its flagship product, the GRC Toolbox, offers a unified platform for managing risks, ensuring compliance, and fostering resilience across organizations. With its commitment to « Global Reach, Local Excellence, » Swiss GRC has expanded its presence globally. The company is known for its focus on innovation, integrating AI and advanced analytics into its solutions to stay ahead in the rapidly evolving GRC landscape. For more information, visit: [www.swissgrc.com](http://www.swissgrc.com).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC integrates with Lawrbit for smart Regulatory Change Monitoring](https://swissgrc.com/fr/news/swiss-grc-integrates-with-lawrbit-for-smart-regulatory-change-monitoring/)
**Published:** février 4, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC has joined forces with Lawrbit, a leading regulatory compliance technology and content provider. This collaboration brings together Swiss GRC’s integrated GRC platform and Lawrbit’s expertly curated regulatory content, empowering organizations to navigate and monitor the complexities of regulatory compliance.
**Content:**
**Lucerne – Swiss GRC, a leading provider of Governance, Risk, and Compliance (GRC) solutions, has joined forces with Lawrbit, a leading regulatory compliance technology and content provider. This collaboration brings together Swiss GRC’s integrated GRC platform and Lawrbit’s expertly curated regulatory content, empowering organizations to navigate and monitor the complexities of regulatory compliance.**
The partnership marks a significant milestone in Swiss GRC’s mission to simplify regulatory compliance management. By integrating Lawrbit’s comprehensive content into the GRC Toolbox, Swiss GRC enhances its ability to provide clients with up-to-date, actionable regulatory insights and updates. What sets Lawrbit apart is its approach: each article and section is developed with input from a network of seasoned advocates, lawyers, and legal consultants, ensuring unparalleled depth and accuracy. Unlike solutions that rely solely on AI-generated content, this partnership delivers a blend of human expertise and advanced technology.
**Jyant Kohli, Founder & CEO of Lawrbit**, highlighted the shared vision behind the partnership: « At Lawrbit, we believe that compliance is not just about meeting requirements—it’s about empowering organizations to thrive in a regulated world. Partnering with Swiss GRC allows us to scale our impact, offering businesses a seamless way to integrate expert regulatory content with advanced compliance tools. Together, we’re setting a new standard for regulatory intelligence. »
Commenting on the partnership, **Besfort Kuqi, CEO of Swiss GRC**, stated: « Our collaboration with Lawrbit reinforces our commitment to offering the highest-quality compliance solutions. By combining their expertise with our advanced GRC Toolbox, we provide businesses with a unique capability to manage regulatory compliance in a rapidly evolving landscape. This partnership reflects Swiss GRC’s vision of integrating excellence into every aspect of our solutions. »
**Rajeev Dutt, General Manager MEA & APAC at Swiss GRC**, emphasized the operational impact:
« Regulatory compliance is a cornerstone of effective governance, and this partnership brings unmatched value to our clients. Lawrbit’s human-centered approach to content creation complements our technology, ensuring that organizations not only stay compliant but do so with a deeper understanding of their obligations. We’re excited to see how this collaboration drives success across industries. »
The Swiss GRC platform, now enriched with Lawrbit’s curated content, offers businesses a powerful tool to identify and address regulatory requirements efficiently. This collaboration not only simplifies compliance management but also enhances corporate accountability and operational resilience, paving the way for sustainable success.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
**About Lawrbit**
Lawrbit is a trusted provider of regulatory compliance content, offering a comprehensive and continually updated database of global regulations. Backed by a network of legal experts, Lawrbit ensures businesses have access to reliable, practical insights for navigating the complexities of compliance. For more information, visit: [www.lawrbit.com.](http://www.lawrbit.com)
**About Swiss GRC**
Swiss GRC, headquartered in Lucerne, Switzerland, is a leading provider of Governance, Risk, and Compliance (GRC) solutions. Its flagship product, the GRC Toolbox, offers a unified platform for managing risks, ensuring compliance, and fostering resilience across organizations. With its commitment to « Global Reach, Local Excellence, » Swiss GRC has expanded its presence globally. The company is known for its focus on innovation, integrating AI and advanced analytics into its solutions to stay ahead in the rapidly evolving GRC landscape. For more information, visit: [www.swissgrc.com](http://www.swissgrc.com).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [GRC Day India 2025 Premieres with Industry Leaders and Expert Insights](https://swissgrc.com/fr/news/grc-day-india-2025-premieres-with-industry-leaders-and-expert-insights/)
**Published:** février 18, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** GRC Day India 2025, hosted by Swiss GRC and Tech Achieve Media, successfully premiered in Mumbai, bringing 350+ industry leaders together to explore governance, risk, and compliance. Expert insights, dynamic discussions, and live demos set a new benchmark for GRC innovation and collaboration in India.
**Content:**
**The inaugural GRC Day India 2025, jointly organized by Swiss GRC and Tech Achieve Media, set a new benchmark for Governance, Risk, and Compliance (GRC) events in India. Hosted in Mumbai, the event attracted over 350 participants, including industry leaders such as CROs, Risk Heads, BCM Heads, Compliance Heads, Data Protection Officers, CIOs, CISOs, CTOs, and CHROs, making it a groundbreaking platform for dialogue on the future of GRC.**
**Besfort Kuqi,** Co-founder and CEO, Swiss GRC: “India’s GRC ecosystem is at a pivotal moment, with organizations striving to build resilience in an increasingly complex regulatory environment. The discussions at GRC Day India demonstrated a strong appetite for [solutions](https://swissgrc.com/en/solutions/) that not only ensure compliance but also drive strategic value. We are thrilled by the overwhelming interest in our GRC solutions and look forward to deepening our engagement in this dynamic market.”
The event featured a star-studded lineup of industry experts, offering key insights into emerging trends, technologies, and strategies shaping the Indian GRC ecosystem. The evening unfolded with a compelling presentation by **Narayan Gokhale**, Vice-President and Principal Analyst, QKS Group, who highlighted the foundational principles of governance. “Kudos to Swiss GRC for hosting their first event in India, which was wonderfully organized by all the stakeholders and organizers. The event offered valuable takeaways, shedding light on the current trends in the Indian GRC industry from an end-user perspective and insights from cybersecurity professionals. It was exceptionally well-executed, and we extend our gratitude to Swiss GRC for this remarkable event. We eagerly look forward to more such events in the future,” said Gokhale.
This was followed by **Ritesh Bhatia**, Founder of V4WEB Cybersecurity, who shed light on “The Illusion of Preparedness: The Hidden Gaps in Your Incident Response Strategy.” Bhatia urged attendees to rethink their approaches to cybersecurity preparedness, emphasizing the unseen vulnerabilities that often go unnoticed. Adding to the robust discussions, **Rachit Chhokera**, Partner at KPMG in India, addressed “Data Governance, Cybersecurity, and DPDP – A Boardroom Lens.” He provided critical insights into how the Digital Personal Data Protection Act (DPDP) is reshaping boardroom priorities.
**Jyant Kohli**, Founder and CEO of [Lawrbit](https://swissgrc.com/en/news/swiss-grc-integrates-with-lawrbit-for-smart-regulatory-change-monitoring/), discussed “DPDP, Regulatory Compliance, and Regulatory Change,” a session that was appreciated by the attendees for its insightful inputs. **Kaveri Venkataraman**, Head of Governance, Risk, and Compliance at Writer Corporation, explored evolving risk landscapes through her distinctive session on “Risk Management – Cornerstone of Governance and Compliance.”
**Rajeev Dutt**, General Manager of MEA and APAC at Swiss GRC, brought his global perspective to the table with his session on “Resilience and Governance.” He remarked: “ The energy and engagement at GRC Day India were truly remarkable. It’s clear that businesses are prioritizing governance, risk, and compliance like never before, seeking integrated solutions to navigate regulatory complexities effectively. A big thank you to the team at Tech Achieve Media for flawlessly organizing this event, and to all the speakers and attendees who contributed to the insightful discussions. We are excited to continue supporting organizations across India in their GRC journey.”
Throughout the event, attendees resonated with Swiss GRC’s emphasis on addressing India’s unique challenges. “Many organizations recognize that traditional approaches no longer suffice, and they are actively seeking technology-driven tools to stay ahead,” noted **Gentian Ajeti**, Head of Consulting at Swiss GRC. “The response to our GRC Toolbox has been fantastic, highlighting its flexibility and ability to streamline risk management in today’s evolving regulatory landscape.”
A highlight of the evening was a live demonstration of Swiss GRC’s cutting-edge dashboard by **Babu Manickan**, Senior Manager at Swiss GRC. The interactive demo showcased how technology is revolutionizing risk management, offering attendees a firsthand look at how digital tools can streamline GRC processes. “Governance, Risk, and Compliance were the central themes of today’s fantastic event, where we gained valuable insights from industry experts. The event featured a live demonstration of a GRC dashboard, highlighting how it integrates into the broader landscape of AI-driven digital transformation and the security measures we must adopt. The discussions centered around aligning with the audience’s needs and the larger ecosystem, providing actionable learnings to implement in the future. Finally, it emphasized the importance of strengthening security measures as a critical priority moving forward,” said Balkrishna Shirgaonker, ITSM Availability Manager at Bayer – one of the delegates on GRC Day India 2025.
The day concluded with a lively panel discussion titled “Navigating the Convergence of GRC and Emerging Technologies: Challenges and Opportunities.” Moderated by Supriya Rai, and the participants were industry leaders namely **Milind Khamkar** (CIO, Super-Max), **Prof. Ajay Singh** (Award-winning Cybersecurity Author), and **Hiten Sinha** (Ad GM, Information Security, BSE), the session explored the synergies between GRC frameworks and technological advancements. Reflecting on the discussion, **Milind Khamkar** said: “Gone are the days when GRC was an afterthought; it’s now a vital, organization-wide responsibility! To achieve success and effectiveness in GRC, it’s essential to break down functional silos and foster seamless collaboration across teams followed by good tech adoption. While AI offers incredible potential, it won’t solve all our challenges automatically. We must align our intentions and efforts with these new technologies to truly drive transformation.”
The success of GRC Day India 2025 has undoubtedly set the stage for ongoing conversations and collaborations in the field of Governance, Risk, and Compliance. “Bringing GRC Day to India for the first time was a tremendous effort, requiring months of planning, coordination, and outreach to ensure we delivered a high-impact event. Partnering with [Tech Achieve Media](https://techachievemedia.com/) was instrumental in making this vision a reality, helping us reach the right audience and curate a compelling agenda,” said **Yahya Mohamed Mao**, Head Marketing & Communications, Swiss GRC.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC to Redefine AI Governance with New AI GRC Module](https://swissgrc.com/fr/news/swiss-grc-to-redefine-ai-governance-with-new-ai-grc-module/)
**Published:** février 21, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** As AI becomes deeply embedded in business operations, organizations face increasing regulatory scrutiny and heightened expectations for transparency, security, and ethical oversight. Swiss GRC's AI GRC Module provides businesses with a structured and automated approach to AI risk assessment, compliance management, and governance.
**Content:**
**Swiss GRC, a global leader in Governance, Risk, and Compliance (GRC) solutions, has announced the launch of its AI GRC Module, a solution designed to help organizations navigate the fast-evolving regulatory landscape surrounding artificial intelligence (AI).**
As AI becomes deeply embedded in business operations, organizations face increasing regulatory scrutiny and heightened expectations for transparency, security, and ethical oversight. Swiss GRC’s new [AI GRC Module](https://swissgrc.com/en/ai-grc/) provides businesses with a structured and automated approach to AI risk assessment, compliance management, and governance, ensuring they stay ahead of evolving regulations and industry best practices.
« AI is transforming industries at an unprecedented pace, but with innovation comes responsibility. Our AI GRC Module enables organizations to integrate AI with confidence—ensuring compliance, mitigating risks, and upholding transparency. This is a significant step toward responsible AI governance, » said **Besfort Kuqi**, CEO of Swiss GRC.
**Bringing Structure to AI Governance**
AI’s rapid adoption presents challenges such as bias, opaque decision-making, security risks, and regulatory uncertainty. Many organizations struggle to track AI use cases, evaluate compliance risks, and implement effective oversight mechanisms. Swiss GRC’s AI GRC Module helps address these challenges by offering automated risk assessments, real-time monitoring, and structured governance tools, enabling organizations to manage AI use responsibly and with full regulatory compliance. By integrating AI taxonomy classification, conformity scoring, lifecycle management, and performance monitoring, the module provides a comprehensive framework for AI transparency, accountability, and risk mitigation.
« The regulatory environment around AI is evolving rapidly, making it critical for organizations to have a structured approach to compliance and risk management. Our AI GRC Module is designed to simplify this complexity, providing a future-proof solution that aligns with leading global standards, » said **Nikolai Tsenov**, Head of Strategy & Business Development at Swiss GRC. “With this new module, Swiss GRC is taking a leadership role in ensuring that AI innovation is both ethical and compliant, » he added.

AI GRC Module – Privacy Impact Assessment in AI
**Built for Global AI Compliance**
As AI regulations evolve worldwide, organizations must comply with multiple frameworks. Swiss GRC’s AI GRC Module supports compliance with leading standards, including:
- **EU AI Act** – The most comprehensive AI regulatory framework in Europe
- **NIST AI Risk Management Framework** – U.S. guidelines for responsible AI governance
- **ISO 42001** – The global AI governance standard for compliance and risk management
- **OCC AI Guidance** – AI oversight regulations for financial institutions
- **SDAIA AI Ethics Principles 2.0** – Saudi Arabia’s framework for ethical AI governance
With built-in adaptability, Swiss GRC’s AI GRC Module supports proprietary AI frameworks and taxonomies, ensuring organizations can customize their AI governance approach while maintaining regulatory alignment.
**About Swiss GRC**
Swiss GRC, headquartered in Lucerne, Switzerland, is a leading provider of Governance, Risk, and Compliance (GRC) solutions. Its flagship product, the GRC Toolbox, offers a unified platform for managing risks, ensuring compliance, and fostering resilience across organizations. With its commitment to “Global Reach, Local Excellence,” Swiss GRC has expanded its presence globally. With the introduction of the AI GRC Module, Swiss GRC is setting a new benchmark in AI risk management, ensuring that organizations can harness AI’s potential while maintaining control, compliance, and trust.
To learn more about the AI GRC Module, visit: .
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC Day 2025 with a high-profile program on the future of GRC](https://swissgrc.com/fr/news/swiss-grc-day-2025-with-a-high-profile-program-on-the-future-of-grc/)
**Published:** février 26, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Companies face the challenge of anticipating risks, meeting compliance requirements and future-proofing their governance structures. This is precisely where the Swiss GRC Day 2025 comes in. Under the motto “GRC in transition: strategies for the challenges of tomorrow”, the event will take place on May 14, 2025 at the Radisson Blu at Zurich Airport.
**Content:**
**Lucerne, 26 February 2025 – Swiss GRC, a leading provider of governance, risk and compliance (GRC) solutions, has officially unveiled the program for Swiss GRC Day 2025. The established conference brings together experts and decision-makers every year to discuss the most pressing challenges and future strategies in the GRC world.**
Regulatory requirements are becoming more stringent, cyber threats are increasing and geopolitical uncertainties are shaping the economic environment. Organizations are challenged to anticipate risks, meet compliance requirements and future-proof their governance structures. This is where [Swiss GRC Day 2025](https://swissgrc.com/swissgrcday/) comes in. Under the motto **“GRC in transition: strategies for tomorrow’s challenges”**, the event will bring together around 300 managers, decision-makers and experts from Switzerland and neighboring countries at the **Radisson Blu at Zurich Airport on 14 May 2025**.
The conference offers an exciting program that addresses the industry’s most pressing questions: How can organizations effectively prepare for unexpected crises? What is the role of artificial intelligence in the GRC landscape? And how can the balance between regulatory control and innovation be achieved? Answers to these questions will be provided by high-caliber speakers including Christian Weiss (Head Enterprise Risk, Skyguide), Marc Etienne Cortesi (CISO, Baloise Group), Marinela Bilic-Nosic (Partner – Regulatory, Risk & Compliance Lead, EY Germany), David Rosenthal (Partner / Team Head, VISCHER AG), Marc Gröflin (Head of Internal Audit, SNB) and Sandra Middel (Chief Ethics & Compliance Officer, Axpo Group).
“The Swiss GRC Day has long been more than just a conference – it is the central meeting place for the GRC community in Switzerland. Leading minds come together here to discuss current challenges, make valuable contacts and develop new solutions together. We have been organizing this exchange for many years because we are convinced that knowledge transfer and networking are crucial for a successful GRC strategy. With the [GCC GRC Day](https://swissgrc.com/en/gcc-grc-day-2024-navigating-the-complexities-of-grc-in-the-middle-east/) and the [GRC Day India](https://swissgrc.com/en/news/grc-day-india-2025-premieres-with-industry-leaders-and-expert-insights/), we have now established this proven format internationally,” says Besfort Kuqi, host of the Swiss GRC Day and Co-Founder & CEO of Swiss GRC.
The Swiss GRC Day has established itself as an annual fixture for the GRC community and offers an ideal opportunity for personal exchange and networking with industry colleagues in addition to the specialist presentations.
Participation is **free of charge**, but limited. Early registration is recommended.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC sponsors imh banking congress KURS 2025 in Vienna](https://swissgrc.com/fr/news/swiss-grc-sponsors-imh-banking-congress-kurs-2025-in-vienna/)
**Published:** mars 10, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** At this year's imh Banking Congress KURS in Vienna, everything revolves around the question of how banks and financial institutions can strengthen their cyber resilience in a targeted manner and efficiently meet the requirements of the DORA Regulation. Swiss GRC, one of the leading providers of Governance, Risk & Compliance (GRC) solutions in the DACH region, is supporting this discourse as a sponsor of the event.
**Content:**
**The requirements for cyber resilience and regulatory compliance are increasing. Financial institutions must adapt to the Digital Operational Resilience Act (DORA) in order to manage IT and third-party risks efficiently. Swiss GRC represented as a sponsor at the imh Banking Congress KURS 2025 on March 25-26 in Vienna.**
The imh Banking Congress KURS is one of the most important specialist events for the financial sector in Austria. Executives and decision-makers from the fields of IT, digitalization, compliance and risk management discuss current developments and the future of the banking sector. This year, the event will focus in particular on the [Digital Operational Resilience Act (DORA)](https://swissgrc.com/en/digital-operational-resilience-act-dora/) and the question of how financial institutions can efficiently implement regulatory requirements and strengthen their cyber resilience at the same time.
What role does DORA play in shaping sustainable ICT risk management? How can banks and financial service providers optimize their processes to meet increasing regulatory requirements? And what influence do digitalization and automation have on the fulfillment of reporting obligations?
**Dr. Fino Scholl, Managing Director of Swiss GRC Germany GmbH**, will provide insights into the implementation of an intelligent DORA compliance strategy in his presentation on 26 March 2025 at 1 p.m. in the “IT in banks” stream. The focus will be on practical approaches that companies can use to design their processes efficiently and meet regulatory requirements in the long term.
On both days of the conference, participants will have the opportunity to discuss the practical implementation of an integrated GRC approach with experts at the Swiss GRC stand. Financial institutions in particular face the challenge of efficiently implementing regulatory requirements such as DORA without burdening their operational processes. Swiss GRC offers a powerful platform that supports financial institutions in ensuring compliance, minimizing risks and strengthening their cyber resilience in the long term.
You can find more information about the event on the [imh Banking Congress KURS 2025 website](https://www.imh.at/veranstaltungen/hub/bankenkongress-kurs/).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC to participate at GISEC Global 2025 with StorIT](https://swissgrc.com/fr/news/swiss-grc-to-participate-at-gisec-global-2025-with-storit/)
**Published:** avril 25, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC will be part of GISEC Global 2025, one of the world’s most influential cybersecurity events. Swiss GRC's presence at the StorIT booth highlights the company's commitment to the MENA region and reflects the growing importance of integrated GRC in today’s digital landscape. GISEC brings together global leaders to shape the future of cybersecurity, governance, and compliance.
**Content:**
**Swiss GRC is proud to announce its participation at GISEC Global 2025, the Middle East’s largest and most influential cybersecurity event, held at the Dubai World Trade Centre from 6 to 8 May 2025. Swiss GRC will be present at the booth of its strategic partner, StorIT Distribution, reflecting a shared mission to enhance cyber resilience and regulatory readiness across the region.**
As a premier platform that convenes global cybersecurity leaders, government officials, and industry pioneers, [GISEC Global](https://gisec.ae/) offers unparalleled opportunities for collaboration and innovation in the cybersecurity landscape. During the event, Rajeev Dutt, General Manager MEA & APAC at Swiss GRC, will deliver a series of keynote sessions live at the StorIT booth across all three days. His sessions will address the growing need for agile, AI-powered GRC solutions in the face of increasing cybersecurity threats, complex regulatory requirements, and the demand for operational resilience.
“We are excited to be part of GISEC Global alongside our valued partner StorIT,” said Rajeev Dutt. “Our presence at the event, and the conversations we will lead from the StorIT booth, reflect our deep commitment to supporting organizations in the MENA region with robust and forward-looking GRC capabilities.”
Swiss GRC’s participation at GISEC builds on its [strategic partnership with StorIT](https://swissgrc.com/en/news/storit-and-swiss-grc-join-forces-to-deliver-grc-solutions-across-mena/), a leading value-added distributor of enterprise IT solutions. Together, the companies are expanding access to Swiss GRC’s powerful, AI-driven platform across the Middle East and North Africa (MENA). The collaboration provides businesses with GRC solutions that are intuitive, fast to implement, and tailored to regional compliance standards.
The MENA region is rapidly emerging as a strategic hub for [GRC adoption](https://swissgrc.com/en/solutions/). Growing regulatory complexity, rising cyber threats, and increased focus on data protection are driving demand for integrated and localized solutions. Swiss GRC addresses these needs with its GRC Toolbox, which is available through On-Premise, Private Cloud, or SaaS deployment. The platform is also fully accessible in Arabic and supported by a local data center in the UAE, ensuring compliance with local data residency and security requirements.
**Meet us at GISEC Global 2025 — StorIT’s booth in Hall 7, Stand B50 — to explore how our integrated GRC solutions can drive resilience, ensure compliance, and support sustainable growth.**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Michael Niedermann takes over as Team Lead Consulting Europe](https://swissgrc.com/fr/news/michael-niedermann-takes-over-as-team-lead-consulting-europe/)
**Published:** juin 10, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Michael Niedermann will take over the management of Consulting Europe and overall responsibility for the Solution Engineering team on 1 August 2025. In this role, he will be responsible for the operational development of the consulting business in Switzerland, Germany and other European markets with a team of around 30 people.
**Content:**
**Lucerne, June 10, 2026 — Swiss GRC is sending out a clear signal for further growth and focused customer support: the company’s consulting division is being restructured and will be divided into three specialised teams in future: Consulting Europe, Consulting International and Solution Engineering.**
As part of this realignment, Michael Niedermann will take over the management of Consulting Europe and overall responsibility for the Solution Engineering team on 1 August 2025. In this role, he will be responsible for the operational development of the consulting business in Switzerland, in [Germany](https://www.risknet.de/marktplatz/loesungsanbieter/swiss-grc-integriertes-grc-management/) and other European markets with a team of around 30 people.
Niedermann has been a Senior GRC Consultant at Swiss GRC since March 2024. He previously held various management positions in the finance and technology sector, including Chief Operating Officer and Head of Risk & Compliance at the Avobis Group, Chief Risk Officer at Arizon and Head of Operational Risk Controlling at Raiffeisen Switzerland. In previous roles, he was responsible for the successful introduction of several GRC systems and therefore has a sound customer perspective. He has acquired his in-depth expertise in the application of the [GRC Toolbox](http://swissgrc.com/en/solutions) over the past 14 months as part of customer projects and in close collaboration with product development. He has also been a member of the Board of Directors of Raiffeisenbank Surbtal-Wehntal for several years.
“Since joining Swiss GRC, Michael Niedermann has established himself as a central pillar of our consulting team. With his many years of experience in the Swiss financial and technology market and his deep understanding of risk management and regulatory requirements, he is predestined to take over the management of Consulting Europe,” says Besfort Kuqi, Co-Founder and CEO of Swiss GRC.
Michael Niedermann adds: “I am very pleased about the trust and the new responsibility. I know the needs of our clients from my own experience. I am more than happy to be able to work with the team to further develop our consulting services in a targeted manner and bring Swiss GRC even closer to the market as a strong partner.”
Gentian Ajeti, who as Head Consulting will continue to be responsible for the overall management of the entire consulting division, will in future concentrate more on the strategic development and orientation of the client business.
With this structural development, Swiss GRC is creating the ideal conditions for combining specialist expertise, market proximity and international scalability in an even more targeted manner.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Risk.net Recognizes Swiss GRC as “GRC Product of the Year” at the 2025 Risk Technology Awards](https://swissgrc.com/fr/news/risk-net-recognizes-swiss-grc-as-grc-product-of-the-year-at-the-2025-risk-technology-awards/)
**Published:** juin 23, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC is proud to announce that it has been awarded “GRC Product of the Year” at the 2025 Risk Technology Awards, presented by Risk.net, one of the most trusted global voices in risk, compliance, and financial technology. Widely regarded as one of the most prestigious accolades in the field, the 2025 edition saw over 145 submissions, with more than 70 entries shortlisted across various categories.
**Content:**
**Lucerne/London, June 23, 2025 – Swiss GRC is proud to announce that it has been awarded “GRC Product of the Year” at the 2025 Risk Technology Awards, presented by Risk.net, one of the most trusted global voices in risk, compliance, and financial technology.**
Widely regarded as one of the most prestigious accolades in the field, the 2025 edition saw [over 145 submissions](https://www.risk.net/risk-management/7961707/risk-technology-awards-2025-tariff-turmoil%E2%80%99s-tech-effects), with more than 70 entries shortlisted across various categories. Winners were selected by a distinguished panel of 11 independent industry experts and members of the [Risk.net](https://www.risk.net/) editorial team. Each judge conducted an independent review, followed by a collective evaluation, ensuring a balanced and expert-driven outcome.
The award was officially presented to Besfort Kuqi, Co-founder and CEO of Swiss GRC, during a gala dinner at One Moorgate Place in London on June 18. The ceremony marked a highlight of the Risk Live 2025 conference, bringing together leaders from global financial institutions, technology firms, and regulatory bodies.
“This award is a significant milestone for Swiss GRC,” said Besfort Kuqi. “It reflects the trust our clients place in us and the commitment of our team to providing GRC solutions that are user-centric, forward-looking, and aligned with real market needs.”
At the core of this recognition is the [GRC Toolbox](https://swissgrc.com/en/solutions/), Swiss GRC’s flagship platform. It was praised for its modular architecture, intuitive user experience, and strong adoption among end users. Designed to meet the needs of global organizations navigating complex risk and regulatory environments, the GRC Toolbox also offers a high degree of adaptability and flexible deployment. But it was not only the product itself – it was also Swiss GRC’s vision, consistency, and growing momentum as a company that truly set it apart in this year’s competition. This recognition highlights not just what Swiss GRC has built, but also where the company is headed.
From its strong roots in the DACH region to its expanding presence across the Middle East, Africa, and Asia‑Pacific, Swiss GRC is rapidly emerging as a global partner for integrated GRC solutions, covering a broad spectrum of domains including Risk Management, Compliance, Business Continuity & Resilience, Information Security & Privacy, Third-Party Risk Management, and AI Governance.
With this award, Risk.net affirms Swiss GRC’s mission: to help organizations succeed by building resilience, earning trust, and simplifying complexity with integrated GRC, BPM, and CLM solutions.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC launches new contract management software Contraqto](https://swissgrc.com/fr/news/swiss-grc-launches-new-contract-management-software-contraqto/)
**Published:** juillet 1, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC is expanding its portfolio with a new stand-alone solution in the area of Contract Lifecycle Management (CLM). With the launch of Contraqto, the Lucerne-based company is bringing modern, user-friendly and future-oriented contract management software to the market.
**Content:**
**Lucerne, July 01, 2025 – Swiss GRC, a leading provider of software solutions for governance, risk and compliance, is expanding its product portfolio with a new standalone solution in the area of Contract Lifecycle Management (CLM). With today’s official launch of Contraqto, the Lucerne-based company is bringing modern, user-friendly and future-oriented contract management software to the market.**
Contraqto was developed to provide companies with comprehensive support for the digital transformation of their contract processes. This includes all stages of the process, from creation and negotiation to approval, signing, monitoring, and renewal. The [software](https://contraqto.com/en) combines user-friendliness with functional strength and was developed specifically for organizations that want to manage their contract landscape in a structured, transparent, and future-proof manner.
« With Contraqto, we have developed a comprehensive and forward-thinking solution that enables companies to manage their contract processes with efficiency and strategic foresight, » explains Besfort Kuqi, Co-founder and CEO of Swiss GRC. « Our objective was to develop software that is not only technically impressive, but also highly usable in practice thanks to its clarity and user-friendliness. »
Contraqto impresses with a wide range of practical functions that are specially tailored to the requirements of modern companies. These include multilingual user interfaces that enable smooth collaboration across language barriers, as well as a centrally managed contract archive that is hosted securely and in compliance with [data protection](https://swissgrc.com/en/data-protection-management-software/) regulations in Switzerland. Reporting and analytics functions support well-founded decisions with real-time data. In addition, role-based access ensures clear responsibilities and compliance-compliant collaboration within teams. Thanks to real-time notifications and reminders, users can keep an eye on important deadlines, tasks and obligations at all times. The range of functions is rounded off by customizable templates that can be used to flexibly adapt contract-related fields to company-specific processes.
A key success factor in the development of Contraqto was the close collaboration with stakeholders from science and practice. In-depth market analyses and feasibility studies were carried out in cooperation with the [Lucerne University of Applied Sciences and Arts](https://www.hslu.ch/de-ch/) and the innovation promotion agency [Innosuisse](https://www.aramis.admin.ch/Grunddaten/?ProjectID=53170). “The close collaboration with partners from science and practice helped us to identify real market needs and integrate them into our software development in a targeted manner,” emphasizes Christoph Graf, Head Product Development CLM.
With Contraqto, Swiss GRC is expanding its product portfolio to include a key component of modern company management, thereby strengthening its position as an innovative software provider that meets Swiss quality standards. The solution is continuously being developed, especially in the area of artificial intelligence, to make contract processes more intelligent and predictive in the future. Further information on the solution can be found at: [www.contraqto.com](http://contraqto.com).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [WirtschaftsWoche honors Swiss GRC for its TPRM solution](https://swissgrc.com/fr/news/wirtschaftswoche-honors-swiss-grc-for-its-tprm-solution/)
**Published:** août 28, 2025
**Author:** Shayeste Afzaly
**Excerpt:** Swiss GRC is among this year's winners of the prestigious Best of Technology Award 2025, presented by WirtschaftsWoche and Handelsblatt Media Group. The company received an “Excellent” rating for its third-party risk management (TPRM) solution. The award clearly demonstrates that Swiss GRC is becoming increasingly important in the German market.
**Content:**
**Munich/Lucerne, August 28, 2025 – Swiss GRC is among this year’s winners of the prestigious Best of Technology Award 2025, presented by WirtschaftsWoche and Handelsblatt Media Group. The company received an “Excellent” rating for its third-party risk management (TPRM) solution.**
The independent jury, which included experts from the Fraunhofer Institute for Systems and Innovation Research (ISI) and the Karlsruhe Institute of Technology (KIT), among others, highlighted the innovative strength of the [TPRM solution](https://swissgrc.com/en/tprm-software/) and Swiss GRC’s broad range of solutions. The award recognizes digital technologies that not only impress at first glance, but above all generate tangible benefits for companies and strengthen their future viability in the long term.
“Given the high caliber of participants, this award is an outstanding achievement and important proof of our strength in the German market,” explains Dr. Fino Scholl, Managing Director of Swiss GRC Germany GmbH. The German subsidiary of Lucerne-based Swiss GRC AG is a central component of the growth strategy and has successfully established itself since its foundation.
The award was presented during the *Handelsblatt Media Group Summer Camp* on Wednesday, August 27, 2025, at Munich Urban Colab. It was presented by Christian Ley, CIO at Brose Fahrzeugteile SE & Co. KG and member of the jury, to Yahya Mohamed Mao, Head Marketing & Communications at Swiss GRC.
The [Best of Technology Award](https://www.wiwo.de/technologie/forschung/best-of-technology-award-wenn-im-supermarkt-die-ki-kassiert/100149737.html) is aimed at start-ups, medium-sized companies, and large enterprises from all over Germany. It is supported by strategic partner Capgemini and scientific partners Fraunhofer ISI and KIT. The aim is to raise the profile of companies whose solutions are actively driving digital transformation and thus securing the competitiveness of the German economy.
The award clearly shows that Swiss GRC is becoming increasingly important in the German market. More and more companies are placing their trust in the software provider’s solutions, including well-known customers such as IAV, TEDi, Badische Versicherungen (BGV), and Creditreform.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Flour Mills of Nigeria (FMN) sets new standards in Corporate Governance with Swiss GRC ](https://swissgrc.com/fr/news/flour-mills-of-nigeria-fmn-sets-new-standards-in-corporate-governance-with-swiss-grc/)
**Published:** septembre 5, 2025
**Author:** Shayeste Afzaly
**Excerpt:** Flour Mills of Nigeria (FMN), one of the largest and most diversified food and agro-allied groups in West Africa, has chosen Swiss GRC to strengthen its Governance, Risk, and Compliance (GRC) program. With this strategic move, FMN is taking a pioneering role in advancing GRC practices across the region.
**Content:**
**Flour Mills of Nigeria (FMN), a diversified pan-African consumer-centric food and agro-allied business, has selected Swiss GRC as its trusted solution partner to strengthen its Governance, Risk, and Compliance (GRC) framework. A decision that was made in line with the Group’s unwavering commitment to superior quality outcomes in line with global standards and best practices.**
After a competitive evaluation, FMN selected Swiss GRC’s integrated platform covering Enterprise [Risk Management](https://swissgrc.com/en/tprm-software/), [Internal Controls](https://swissgrc.com/en/internal-control-software-ics/), Corporate Compliance, [Internal Audit](https://swissgrc.com/en/internal-audit-software/), and Incident Management. By implementing the GRC Toolbox, FMN will unify its assurance functions within one integrated, user-friendly system. Designed to deliver lasting value and flexibility, the solution enables FMN to strengthen oversight and address risks more effectively.
Boye Olusanya, Group CEO of FMN, remarked: “Implementing a new Governance, Risk, and Compliance (GRC) solution is essential for our organization as it enhances our ability to navigate regulatory landscapes and mitigate risks effectively. This innovative partnership will provide us with advanced tools for real-time compliance monitoring, improved data analytics for informed decision-making, and a streamlined governance framework that fosters accountability. By strengthening our GRC practices, we not only protect our assets but also enhance our reputation and operational efficiency, ultimately driving long-term value for our stakeholders.’’
Commenting on the partnership, Besfort Kuqi, Founder & CEO of Swiss GRC, said: « This partnership demonstrates FMN’s commitment to transforming GRC into a source of business value. With our platform, FMN will benefit from stronger controls, better decision-making, and greater organizational resilience. »
Rajeev Dutt, General Manager MEA & APAC at Swiss GRC, emphasized: « FMN is a lighthouse project for us in the region. Our focus is on delivering fast, reliable, and flexible implementations, ensuring that clients like FMN can quickly realize value. »
Waltonio Percival-Deigh, Group Director, Business Assurance, FMN stated: “At FMN, we are committed to upholding the highest standards of governance, transparency, and operational excellence. By adopting Swiss GRC’s platform, we are equipping our teams with innovative tools to proactively manage risks, strengthen internal controls, and ensure compliance with international standards. This partnership reflects our dedication to creating sustainable value for all stakeholders while reinforcing our resilience in an evolving business environment.”
The collaboration between FMN and Swiss GRC, made possible through the trusted local partner GCET Limited, highlights the growing importance of advanced GRC solutions in West Africa. As one of the region’s most prominent companies, FMN is setting a benchmark for governance and accountability. Together with GCET, Swiss GRC continues to deliver on its mission to simplify complexity for clients — researching current and future GRC needs, ensuring business models evolve with time, and providing complete solutions dedicated to supporting business KPIs with speed, accuracy, and efficiency. This partnership demonstrates how digital transformation in governance and risk management can provide organizations with a true competitive advantage.
Solomon Awosina, COO & CTO of GCET Limited, commented: “We are proud to have played a key role in bringing Swiss GRC and Flour Mills of Nigeria together. At GCET, our goal is to simplify complexity and enable organizations to embrace the future of governance, risk, and compliance. This partnership is an important step in transforming how businesses in West Africa manage risks and compliance, helping them gain speed, accuracy, and efficiency while building resilience for long-term success. Looking ahead, GCET is committed to further promoting Swiss GRC’s innovative solutions in the region, ensuring more organizations can benefit from their adaptability and impact.”
**About Flour Mills of Nigeria (FMN)**
Incorporated on the 29th of September 1960, as a Limited liability company and pioneer wheat miller in Nigeria, Flour Mills of Nigeria (FMN) started out on a journey that has seen the company evolve into what is now one of the biggest brands in the food and agro allied sector in Africa. The Group has made strategic investments that drive development across its key value chains of Grains, Sugar, Cassava starch, Feeds & Protein, and Edible oil, & fats. For over six decades, FMN has been committed to its purpose of ‘Feeding and Enriching lives, Every Day. The organization has maintained a rich tradition of enhancing the quality of living for millions of families by producing a wholesome portfolio of food options through the company’s iconic food brand, “Golden Penny’, a household name that is trusted by many for good food and for daily nourishment.
For more information, visit: [www.fmnplc.com](http://www.fmnplc.com/)
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC to showcase GRC solutions at GITEX Global 2025](https://swissgrc.com/fr/news/swiss-grc-to-showcase-grc-solutions-at-gitex-global-2025/)
**Published:** septembre 30, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC has confirmed its participation at GITEX Global 2025, taking place at the Dubai World Trade Centre from 13 to 17 October 2025. The company will join its regional distribution partner StorIT at Hall 2, Stand B70, presenting its integrated GRC solutions to a global audience of technology leaders and innovators.
**Content:**
**Dubai, UAE — September 30, 2025 — Swiss GRC has confirmed its participation at GITEX Global 2025, taking place at the Dubai World Trade Centre from 13 to 17 October 2025. The company will join its regional distribution partner StorIT Distribution at Hall 2, Stand B70, presenting its integrated Governance, Risk, and Compliance (GRC) solutions to a global audience of technology leaders and innovators.**
The announcement follows Swiss GRC’s participation earlier this year at [GISEC Global 2025](https://swissgrc.com/en/news/swiss-grc-to-participate-at-gisec-global-2025-with-storit/), where the company highlighted the increasing role of GRC in addressing cybersecurity threats and regulatory requirements. The return to Dubai underlines Swiss GRC’s ongoing commitment to the Middle East and North Africa (MENA) region as a fast-growing hub for digital resilience and compliance solutions.
“Following our successful presence at GISEC, GITEX provides us with another opportunity to engage directly with organizations that are navigating an increasingly complex regulatory and cyber landscape,” said Rajeev Dutt, General Manager MEA & APAC at Swiss GRC. “Together with StorIT, we aim to demonstrate how GRC can evolve from a compliance necessity to a driver of sustainable growth and resilience.”
Swiss GRC’s partnership with StorIT enables organizations across the region to access the company’s [GRC Toolbox](https://swissgrc.com/en/solutions/), a platform designed for rapid implementation and high user adoption. The solution is available through On-Premise, Private Cloud, or SaaS deployment models and offers full Arabic language support, backed by a UAE-based data center to ensure compliance with local data residency and security requirements.
[GITEX Global](https://www.gitex.com/), recognized as the world’s largest technology and startup event, is expected to attract tens of thousands of attendees, including government representatives, industry leaders, and emerging innovators. Swiss GRC’s participation positions the company at the intersection of governance, compliance, and technological innovation, building continuity from its earlier presence at GISEC Global.
Swiss GRC and StorIT will welcome visitors to **Hall 2, Stand B70** at the Dubai World Trade Centre throughout the five-day event.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC to exhibit at #RISK Europe 2025](https://swissgrc.com/fr/news/swiss-grc-to-exhibit-at-risk-europe-2025/)
**Published:** octobre 21, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC will exhibit at #RISK Europe 2025, taking place on 12 and 13 November 2025 at ExCeL London. As Europe’s leading event dedicated to Governance, Risk and Compliance (GRC), #RISK Europe brings together more than 8,000 professionals from across risk, compliance, RegTech, privacy, and security disciplines.
**Content:**
**Swiss GRC will exhibit at #RISK Europe 2025, taking place on 12 and 13 November 2025 at ExCeL London. As Europe’s largest and most influential gathering for the Governance, Risk and Compliance community, the event brings together more than 8,000 professionals from across risk, compliance, RegTech, privacy, and security.**
Now in its fourth year, the event has become the continent’s most influential platform for cross-functional leaders navigating an increasingly complex risk landscape. Over two days, participants will explore world-class content, practical insights, and the latest innovations shaping the future of enterprise resilience.
For Swiss GRC, this marks its second appearance at Europe’s flagship risk event — a milestone that reflects the company’s strong global momentum and continuous expansion across the DACH, MEA, and APAC regions. With its award-winning GRC software and rapidly growing international footprint, Swiss GRC stands among the world’s innovators redefining how organizations approach governance, risk, and compliance.
Visitors can meet the [Swiss GRC team](https://swissgrc.com/en/about-us/#team) at **Booth No. 85**, where the company will showcase its integrated software platform that helps organizations simplify complex processes, enhance operational efficiency, and build resilience for long-term success. Designed to unify governance, risk, and compliance functions, the platform provides a comprehensive suite of tools for Governance, Risk and Compliance.
Representing Swiss GRC at the event will be:
- **Besfort Kuqi**, Founder and CEO
- **Rajeev Dutt**, General Manager MEA & APAC
- **Gentian Ajeti**, Chief Customer & Commercial Officer (CCO)
- **Yahya Mohamed Mao**, Chief Marketing Officer (CMO)
- **Nikolai Tsenov**, Head of Solutions & Innovation.
Together, they will engage with industry peers, discuss emerging trends, and share how Swiss GRC’s technology empowers organizations to turn regulatory challenges into strategic opportunities.
As Swiss GRC continues to expand globally, its participation at [\#RISK Europe](https://www.grcworldforums.com/risk/risk-europe) reinforces the company’s commitment to driving innovation, fostering trust, and helping organizations achieve sustainable growth through strong governance and effective risk management.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC strengthens leadership structure with new Executive Board](https://swissgrc.com/fr/news/swiss-grc-strengthens-leadership-structure-with-new-executive-board/)
**Published:** octobre 27, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** As of October 1, 2025, Swiss GRC has introduced an Executive Management (ExB) for the first time in the company’s history. This step reflects the company’s sustained growth and its expanding international presence. The new leadership structure is designed to ensure clear responsibilities, shorter decision-making paths, and a strong foundation for both operational and strategic management.
**Content:**
*The new Executive Management of Swiss GRC (from left): Yahya Mohamed Mao (CMO), Fari Ganji (CIO), Besfort Kuqi (Founder & CEO), Daniel Arnold (CPO) and Gentian Ajeti (CCO).*
**Lucerne, October 27, 2025 — As of October 1, 2025, Swiss GRC has introduced an Executive Management (ExB) for the first time in the company’s history. This step reflects the company’s sustained growth and its expanding international presence. The new leadership structure is designed to ensure clear responsibilities, shorter decision-making paths, and a strong foundation for both operational and strategic management.**
The Executive Management is led by Besfort Kuqi, Founder and CEO of [Swiss GRC](https://swissgrc.com/en). Its members include Daniel Arnold (Chief Product Officer), Fari Ganji (Chief Information Officer), Gentian Ajeti (Chief Customer & Commercial Officer), and Yahya Mohamed Mao (Chief Marketing Officer). In this composition, the board unites the company’s key business areas – from product development and technology to sales, customer relations, marketing, and communications – and is set to shape the company’s strategic direction for the years ahead.
« With the new leadership structure, we are laying the foundation to further expand our customer success and accelerate innovation in our products and services, » says Besfort Kuqi, Founder and CEO. « It strengthens our organization, consolidates expertise, and enables us to align growth, quality, and customer value in the best possible way. »
Swiss GRC currently employs more than 70 professionals. In addition to its headquarters in Lucerne, the company operates offices in Frankfurt, London, Pristina, Dubai, and Mumbai. Its clients include renowned organizations from various industries and regions. In parallel with its international expansion, Swiss GRC continues to enhance its product portfolio – most recently with the launch of the AI-powered contract management software [Contraqto](https://contraqto.com).
With the establishment of an Executive Board, Swiss GRC is setting a clear milestone in its corporate development. This step underscores the company’s ambition to expand its business internationally while creating the organizational foundation for sustainable growth and long-term success.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC to host GCC GRC Day 2025 with Khaleej Times](https://swissgrc.com/fr/news/swiss-grc-to-host-gcc-grc-day-2025-with-khaleej-times/)
**Published:** novembre 14, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC and Khaleej Times Events will host the GCC GRC Day 2025 on Thursday, 20 November 2025, at Address Sky View Dubai, convening regional leaders to advance governance, risk, and compliance in an AI-enabled economy. The annual conference continues to build on its strong foundation as a premier platform for dialogue and knowledge exchange across the GCC.
**Content:**
*GCC GRC Day is a brand of Swiss GRC and represents the continuation and regional expansion of the long-established and highly renowned Swiss GRC Day, the larges GRC conference in the DACH region.*
**Dubai/Lucerne, November 14, 2025 — Swiss GRC and Khaleej Times Events will host the GCC GRC Day 2025 on Thursday, 20 November 2025, at Address Sky View Dubai, convening regional leaders to advance governance, risk, and compliance in an AI-enabled economy. The annual conference continues to build on its strong foundation as a premier platform for dialogue and knowledge exchange across the GCC.**
This one-day forum will bring together board members, C-suite leaders, compliance and audit heads, data protection officers, and regulators to address the most pressing priorities in today’s governance and risk landscape. Discussions will span operational resilience, third-party and supply-chain risk, AI governance, regulatory transformation, cybersecurity, and data privacy. With GRC evolving from checklists to performance, the conference will focus on actionable frameworks, technology enablement, and measurable outcomes, empowering organizations to strengthen resilience, enhance accountability, and achieve sustainable success.
“The GCC GRC Day reflects our commitment to advancing the regional GRC agenda through meaningful dialogue and shared expertise,” said Besfort Kuqi, Chief Executive Officer at Swiss GRC. “It is inspired by and continues the legacy of the long-established Swiss GRC Day. By collaborating with [Khaleej Times](khaleejtimesevents.com), we are able to bring these important conversations to an even broader professional audience across the GCC.”
The [GCC GRC Day](https://swissgrc.com/en/gccgrcday) provides a distinguished platform to engage with the latest developments, proven strategies, and innovative approaches in governance, risk, and compliance. Participants will benefit from the expertise of leading professionals through keynote presentations and interactive discussions, gaining both strategic insights and practical guidance.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Rethinking risk management for strategic leadership](https://swissgrc.com/fr/news/rethinking-risk-management-for-strategic-leadership/)
**Published:** décembre 11, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Prof. Dr. Stefan Hunziker, Professor of Risk Management and Head of the Competence Center for Risk and Compliance Management at HSLU, as well as Advisory Board Member of Swiss GRC, highlights a key issue that affects many organizations: why risk management must go beyond procedural processes and be understood more as a management task.
**Content:**
*Prof. Dr. Stefan Hunziker is Professor of Enterprise Risk Management and Internal Control Systems at the Lucerne University of Applied Sciences and Arts, Institute of Financial Services Zug IFZ.*
**The evolving landscape of geopolitical tensions, technological innovations, and heightened regulation necessitates a fundamental shift in how organizations perceive and manage risks. This assertion is further corroborated by the recently published ERM Report 2025, a collaborative study conducted by the Lucerne University of Applied Sciences and Arts and the Kiel University of Applied Sciences, with Swiss GRC as a key partner.**
In a recently released analysis, Prof. Dr. Stefan Hunziker, a Professor of Risk Management at the [Lucerne University of Applied Sciences (HSLU)](https://www.hslu.ch/), posits that these developments call for a redefined understanding of the significance of risk management in both leadership and strategic decision-making.
His insights are featured in the second edition of the *GRC Compass*, a quarterly thought leadership publication from Swiss GRC that unites prominent voices within the global governance, risk, and compliance sphere. Hunziker also serves as an Advisory Board Member at Swiss GRC, blending academic insights with practical experience.
Hunziker notes that while numerous organizations have implemented comprehensive risk processes, these often fail to integrate into essential strategic dialogues. Despite the abundance of data, meaningful insights remain elusive. A principal factor in this disconnect is that risks are generally presented in ways that do not align with leaders’ inherent understanding of uncertainty.
Drawing on insights from psychology, cognitive science, and decision-making research, Hunziker highlights that individuals grasp uncertainty through narratives, causal links, and scenarios—rather than through isolated statistics. Distributions offer a more realistic and contextually relevant basis for decision-making, making underlying assumptions transparent. When uncertainty is effectively woven into strategy formulation, performance management, and investment choices, risk management transitions from a mere administrative function to a vital leadership competency.
This viewpoint reinforces the strategic focus of Swiss GRC, a premier Swiss provider of GRC software with an expanding international footprint. Through the GRC Compass, Swiss GRC promotes global professional networking and cultivates a comprehensive understanding of risk as a strategic asset.
The second edition of the GRC Compass is now available for download:
**[When Risk Management Becomes Pure Pleasure: Rethinking a Misunderstood Discipline](https://swissgrc.com/Downloads/TheGRCCompass/Edition2)**
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC included in Global GRC Platforms Landscape Report](https://swissgrc.com/fr/news/swiss-grc-included-in-global-grc-platforms-landscape-report/)
**Published:** janvier 6, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC is included in Forrester Research, Inc.'s Governance, Risk, and Compliance Platforms Landscape, Q4 2025. The Landscape report provides a market overview of technology providers in the global GRC platform environment and classifies them according to key solution areas that address the regulatory, risk, and compliance requirements of organizations in various industries.
**Content:**
*Swiss GRC is the only GRC software company headquartered in the DACH region listed in this report and was already included in the GRC Landscape 2023.*
**Swiss GRC, a leading provider of integrated software solutions for governance, risk, and compliance (GRC), is included in The Governance, Risk, And Compliance Platforms Landscape, Q4 2025, published by Forrester Research, Inc.**
The Landscape report provides a market overview of technology providers operating in the global GRC platforms market and maps them across key solution areas addressing regulatory, risk, and compliance requirements across industries. It highlights the growing importance of integrated, technology-enabled approaches to effective governance, risk, and compliance management in an increasingly complex regulatory and operational environment. As organizations face rising regulatory demands, geopolitical uncertainty, expanding cyber threats, and increasing operational risks, holistic GRC management continues to gain strategic importance. GRC software platforms play a central role in helping organizations structure risk management activities, strengthen compliance processes, enhance transparency, and build sustainable organizational resilience.
Swiss GRC delivers an [integrated software platform](https://swissgrc.com/en/solutions/) covering a broad range of GRC disciplines, including risk management, information security management, operational and cyber resilience, business continuity management, and compliance. The platform is designed to support structured GRC processes and to enable close collaboration across business, risk, compliance, and IT functions.
Commenting on the inclusion in the report, Besfort Kuqi, Founder & CEO of Swiss GRC, said: “Being included in this global GRC platforms landscape is an important milestone for us. From our perspective, it is particularly meaningful that Swiss GRC is the only company headquartered in the DACH region represented in the report. This reflects our ambition to be a leading and well-established GRC software provider and our long-term commitment to supporting organizations in managing complex risk and regulatory requirements in a structured and sustainable way.”
Swiss GRC supports organizations across a wide range of industries and regions in meeting both regional and international regulatory requirements. The company continues to invest in the development of flexible and scalable GRC solutions to address evolving challenges in risk, compliance, and resilience.
The Governance, Risk, And Compliance Platforms Landscape, Q4 2025, Forrester Research, Inc., 2025: [**Link to report**](https://www.forrester.com/report/RES189273).
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Connecting Strategy, Performance, and Risk: Swiss GRC and Profit.co Join Forces](https://swissgrc.com/fr/news/connecting-strategy-performance-and-risk-swiss-grc-and-profit-co-join-forces/)
**Published:** janvier 16, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC has entered into a partnership with US-based Profit.co, a global leader in performance management software. The partnership is focused on offering customers access to both GRC and performance management capabilities as part of a joint offering. The partnership addresses a growing market need for objective-centric risk management, where risks are not assessed in isolation but evaluated based on their impact on strategic goals, operational performance, and execution.
**Content:**
*The partnership addresses a growing market need for objective-centric risk management, where risks are not assessed in isolation but evaluated based on their impact on strategic goals, operational performance, and execution.*
**Texas / Lucerne, 16 January 2026 – Swiss GRC, a leading provider of Governance, Risk, and Compliance (GRC) solutions, has entered into a partnership with US-based Profit.co, a global leader in performance management software. The partnership is focused on offering customers access to both GRC and performance management capabilities as part of a joint offering.**
By combining Swiss GRC’s integrated [GRC platform](https://swissgrc.com/en/solutions/) with Profit.co’s performance management capabilities, the partnership enables organizations to manage risk in alignment with strategic objectives and execution. [Profit.co’s offering](https://www.profit.co/) includes OKR and KPI Management, Strategy Roadmaps, Balanced Scorecards, Project Portfolio Management and employee performance and engagement capabilities, complementing Swiss GRC’s expertise in governance, risk, compliance and resilience.
The partnership addresses a growing market need for objective-centric risk management, where risks are not assessed in isolation but evaluated based on their impact on strategic goals, operational performance, and execution. Customers can adopt and combine both solutions flexibly, depending on their maturity level, regulatory environment and business priorities.
Commenting on the partnership**, Besfort Kuqi, Founder & CEO of Swiss GRC,** stated: “Organizations today must understand how risks affect their objectives and performance. This partnership with Profit.co allows us to combine our GRC offering with strong performance management capabilities, enabling customers to manage both performance and risk
From the Profit.co side, the partnership reflects a shared vision of aligning strategy execution with governance and risk awareness. **Priya Selvaraj, Director of Operations at Profit.co,** added: “This partnership responds directly to customer demand for integrated and flexible solutions. By combining Profit.co’s performance management capabilities with Swiss GRC’s GRC expertise, organizations gain better visibility and control across strategy, execution, and risk.”
Together, Swiss GRC and Profit.co empower organizations to translate strategy into execution while proactively managing risk, supporting stronger governance, improved performance, and sustainable business outcomes.
**About Profit.co**
Profit.co is a US-based performance management platform that helps organizations execute strategy through OKRs, Balanced Scorecards, KPIs, project portfolio management, and employee performance management. Trusted by organizations worldwide, Profit.co enables leadership teams to align goals, track progress, and drive measurable results.
Profit.co is headquartered in Plano, Texas (USA) and operates internationally, with offices in Singapore, India (Pune and Chennai), and Dubai (United Arab Emirates).
For more information, visit: [www.profit.co](http://www.profit.co)
**About Swiss GRC**
Swiss GRC is a global provider of Governance, Risk, and Compliance (GRC) software solutions. Its flagship product, the GRC Toolbox, delivers an integrated platform for managing governance, risk, compliance, and resilience. Swiss GRC supports organizations worldwide in building trust, transparency, and resilience for sustainable success.
Swiss GRC is headquartered in Switzerland and operates internationally, serving customers across Europe, the Middle East, Africa, Asia and the Americas.
For more information, visit: [www.swissgrc.com](https://www.swissgrc.com)
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Presilience and the Reinvention of Risk Leadership](https://swissgrc.com/fr/news/presilience-and-the-reinvention-of-risk-leadership/)
**Published:** février 15, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** Dr. Fayadh Alenezi, Associate Professor at Jouf University in Saudi Arabia, Certified Presilience Practitioner, and contributor to the third edition of the GRC Compass, examines a critical question facing modern organizations: how risk leadership must evolve beyond traditional frameworks to strengthen decision-making and adaptive capacity in complex environments.
**Content:**
**As systemic complexity reshapes the global risk landscape, traditional governance models are reaching their limits. In the third edition of the GRC Compass, Dr. Fayadh Alenezi introduces Presilience as a forward-looking leadership capability designed to strengthen decision-making, adaptability, and organizational performance under uncertainty.**
Risk leadership is entering a period of structural transformation, not as a matter of incremental improvement, but of foundational repositioning. Geopolitical volatility, technological acceleration, regulatory expansion, and deeply interconnected operating models are redefining how uncertainty manifests inside organizations. Risks no longer materialize as isolated exposures that can be assessed and contained within functional silos. Instead, they evolve as systemic dynamics, propagating across supply chains, digital infrastructures, regulatory regimes, and stakeholder ecosystems.
For boards, Chief Risk Officers, CISOs, and compliance leaders, this shift introduces a strategic inflection point. If complexity is now the operating baseline rather than the exception, then the central question is no longer how risks are documented, but how effectively they inform decisions. It is precisely this reframing that anchors the third edition of the GRC Compass, Swiss GRC’s quarterly thought leadership publication dedicated to examining how governance, risk, and compliance must evolve in response to structural change.
###### **From Managing Risk to Enabling Decisions**
In his contribution, Dr. Fayadh Alenezi, Associate Professor at Jouf University in Saudi Arabia and Certified Presilience Practitioner, examines why many established risk practices struggle to deliver impact despite increasing methodological sophistication.
Historically, risk management frameworks were engineered for environments characterized by relative stability. Their primary mandate was protection: identifying exposures, enforcing controls, and ensuring compliance within predictable planning horizons. That paradigm is losing operational relevance.
Risk management is shifting from a monitoring function to a decision-enablement discipline embedded within leadership processes.

###### **Repositioning Risk Intelligence**
This evolution places renewed focus on the concept of risk intelligence but in a form that extends beyond analytical sophistication.
While quantitative modeling, predictive analytics, and scenario simulations remain indispensable, they do not determine outcomes in isolation. Decisions are made within human systems shaped by perception, experience, incentives, and cognitive bias.
Dr. Alenezi emphasizes that risk rarely fails in methodology; it fails in interpretation. Insight that is technically sound but cognitively inaccessible, politically sensitive, or misaligned with leadership perception will not influence action.
This introduces a critical translational gap between risk analysis and risk action.
Bridging that gap requires risk leaders to operate not only as analysts, but as interpreters of uncertainty, capable of framing risk in ways that resonate with decision-makers navigating pressure, ambiguity, and competing priorities.
###### **The Shift from Resilience to Presilience**
It is at this intersection of human judgment and systemic complexity that the concept of Presilience emerges.
Where resilience traditionally focuses on recovery capacity after disruption, presilience shifts the temporal lens forward. Its emphasis lies in building adaptive readiness before stress materializes, strengthening how leaders think, decide, and collaborate when uncertainty unfolds.
Rather than centering exclusively on crisis response, presilience integrates behavioral science, decision theory, and systems thinking to enhance performance in volatility.
Importantly, this does not displace existing governance paradigms. Instead, it expands them.
Compliance establishes boundaries and accountability. Resilience ensures continuity and recovery. Presilience builds anticipatory capability, enabling organizations to engage uncertainty proactively rather than defensively.
Together, they form a cumulative maturity model for modern risk leadership.
###### **Leadership Implications in Complex Systems**
This reframing carries structural implications for GRC leaders and executive stakeholders alike.
If the purpose of risk management is evolving toward decision enablement, then traditional success metrics require recalibration. Control coverage and documentation rigor remain necessary, but they are insufficient proxies for effectiveness.
Greater emphasis must be placed on whether risk practices tangibly enhance organizational performance. This includes their ability to:
- Clarify strategic trade-offs
- Surface weak or emerging signals early
- Sustain performance under pressure
- Strengthen alignment across leadership teams
Such outcomes are influenced not only by governance structures, but by human conditions — psychological safety, cognitive capacity, trust, and openness to dissent.
In complex environments, these factors are not peripheral. They determine whether risk insight travels, is challenged, and ultimately shapes decisions.
Governance effectiveness, in this sense, becomes inseparable from human performance.
###### **The Role of Thought Leadership in Advancing the Discipline**
By convening interdisciplinary perspectives, the GRC Compass serves as more than a publication. It functions as a platform for advancing the maturity of the global GRC discourse.
Swiss GRC brings together academic research, practitioner experience, and executive insight to examine how governance frameworks must adapt to emerging systemic realities.
The third edition continues this mission by challenging organizations to move beyond tool-centric risk models and toward leadership-centric risk capabilities grounded in decision intelligence and adaptive readiness.
The third edition of the GRC Compass is now available for download:
**[Rethinking Risk for a Complex World: The Evolution of Risk Intelligence Toward Presilience](https://www.swissgrc.com/Downloads/TheGRCCompass/Edition3.pdf)**
---
### [Swiss Cyber Security Days: Swiss GRC Exhibiting at the Event](https://swissgrc.com/fr/news/swiss-cyber-security-days-swiss-grc-exhibiting-at-the-event/)
**Published:** février 16, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** The Swiss Cyber Security Days 2026 will kick off tomorrow in Bern. The event is one of Switzerland's most important platforms for exchange on cyber security, digital resilience, and enterprise-wide risk management, bringing together representatives from business, the public sector, research, and technology. Swiss GRC will be exhibiting and presenting its platform for governance, risk, and compliance at its booth in Hall 2.2, Booth K08.
**Content:**
*Under the motto “Digital Sovereignty – The New Frontier,” the Swiss Cyber Security Days 2026 will bring together national and international leaders to find answers to one of the most pressing questions of our time.*
**The Swiss Cyber Security Days 2026 will kick off tomorrow in Bern. The event is regarded as one of Switzerland’s leading platforms for dialogue on cyber security, digital resilience, and enterprise risk governance, bringing together representatives from industry, the public sector, academia, and technology.**
This year’s edition is held under the guiding theme “Digital Sovereignty – The New Frontier.” Against a backdrop of geopolitical tensions, growing technological dependencies, and escalating cyber threats, the concept of digital autonomy and the ability of states, organizations, and societies to act independently in the digital domain has moved to the forefront. The event aims to foster dialogue around new solution approaches and to explore pathways toward shaping digital futures with greater self-determination.
From a programmatic perspective, the agenda addresses current developments at the intersection of technology, geopolitics, business, and society. Key areas of focus include the resilience of critical infrastructure, secure digital value chains, governance considerations surrounding artificial intelligence, and strategic approaches to strengthening digital sovereignty at both national and international levels.
Within this context, [Swiss GRC AG](https://www.swissgrc.com), headquartered in Lucerne, Switzerland, is represented as an exhibitor. At its booth in Hall 2.2, Stand K08, the Swiss software provider is presenting its Governance, Risk & Compliance platform, which unifies applications spanning information security, risk management, data protection, business continuity, compliance, internal controls, and third-party risk management within an integrated solution. The portfolio is further complemented by the contract management software [Contraqto](https://www.contraqto.com), which enables AI-driven automation across the entire contract lifecycle.
Over recent years, Swiss GRC has established itself as a market-shaping provider within the GRC landscape and is widely regarded as one of the leading software vendors in this segment. At the same time, the company continues to expand its international footprint, gaining visibility and market traction beyond Switzerland.
Its software solutions are deployed across security- and risk-critical industries including financial services, insurance, automotive, and the public sector. International analyst firms and specialist media regularly feature Swiss GRC in market analyses and industry assessments. Most recently, the company was recognized as the [only vendor headquartered in the DACH region](https://www.computerworld.ch/themen/business-und-it-strategie/swiss-grc-im-int-marktueberblick-zu-software-governance-risk-compliance) included in Forrester’s current “Governance, Risk, and Compliance Platforms Landscape Report.”
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Monte Carlo Simulation, AI and DORA in the latest release](https://swissgrc.com/fr/news/monte-carlo-simulation-ai-and-dora-in-the-latest-release/)
**Published:** mars 24, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** With the latest release, Swiss GRC continues to evolve its GRC software to address key demands in modern risk management. The update brings together advanced quantitative risk analysis, AI-driven capabilities, and enhanced support for regulatory frameworks such as DORA. In the area of quantitative risk analysis, the GRC Toolbox provides advanced capabilities for modelling and assessing risk, including Monte Carlo simulation.
**Content:**
*Monte Carlo simulation in practice: quantitative risk analysis using scenarios and probability distributions to support data-driven decision-making directly within the GRC system.*
**With the latest release, Swiss GRC continues to evolve its GRC software to address key demands in modern risk management. The update brings together advanced quantitative risk analysis, AI-driven capabilities, and enhanced support for regulatory frameworks such as DORA.**
In the area of quantitative risk analysis, the GRC Toolbox provides advanced capabilities for modelling and assessing risk, including [Monte Carlo simulation](https://swissgrc.com/en/risk-management-software/). This enables organizations to move beyond qualitative assessments and quantify risks based on scenarios and probability distributions, improving the understanding of potential losses and tail risks.
The release also strengthens collaboration with third parties. With enhanced external user management, organizations can onboard vendors and external stakeholders in a structured and secure way, supporting more effective [Third-party Risk Management (TPRM)](https://swissgrc.com/en/tprm-software/).
Another focus is the continued evolution of AI in GRC. The enhanced AI Assistant supports research, content creation, and analytical tasks, while built-in governance mechanisms ensure controlled and compliant use of AI across the organization.
In addition, web search integration extends the platform with real-time external data. This enables AI-driven insights to incorporate up-to-date information, improving the context and relevance of risk assessments and decision-making.
From a regulatory perspective, the release further supports [DORA compliance](https://swissgrc.com/en/digital-operational-resilience-act-dora/). The integrated DORA Information Register allows organizations to structure, manage, and export regulatory data efficiently, supporting compliance with the Digital Operational Resilience Act and increasing audit readiness.
Overall, the latest release reflects the ongoing shift toward integrated, data-driven GRC platforms that combine risk management, AI, and regulatory compliance within a single environment.
[**Schedule a discovery call with our team to learn more.**](https://swissgrc.com/en/digital-operational-resilience-act-dora/)
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC appoints Rajeev Dutt as Managing Director MEA & APAC](https://swissgrc.com/fr/news/swiss-grc-appoints-rajeev-dutt-as-managing-director-mea-apac/)
**Published:** avril 15, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** Rajeev Dutt previously served as General Manager for the region and now takes on broader responsibility for the further development of Swiss GRC’s business across MEA and APAC. He brings more than 25 years of experience in Governance, Risk and Compliance and Business Continuity Management. Prior to joining Swiss GRC, he held senior roles at InfiniteBlue, SAI360 and MetricStream.
**Content:**
*Rajeev Dutt is a highly accomplished leader and brings more than 25 years of experience in Governance, Risk and Compliance and Business Continuity Management.*
**Dubai, April 15, 2026 – Swiss GRC has appointed Rajeev Dutt as Managing Director MEA & APAC. With this step, the company is strengthening its leadership structure across the Middle East, Africa and Asia-Pacific regions.**
Rajeev Dutt previously served as General Manager for the region and now takes on broader responsibility for the further development of Swiss GRC’s business across [MEA and APAC](https://swissgrc.com/en/news/swiss-grc-opens-dubai-office-to-support-company-growth-in-the-region/). He brings more than 25 years of experience in Governance, Risk and Compliance and Business Continuity Management. Prior to joining Swiss GRC, he held senior roles at InfiniteBlue, SAI360 and MetricStream.
The appointment reflects the continued development of Swiss GRC’s international business. Since establishing its presence in the region two years ago, the company has built a growing customer base that includes major organisations such as G42 Group, Qatar National Bank, Rotana Hotels, Crown Prince Court of Abu Dhabi, Dubai Chambers and [The BENEFIT Company Bahrain](https://swisstrade.com/news/detail/news/swiss-grc-staerkt-finanzinfrastruktur-in-bahrain/).
Swiss GRC is also strengthening its regional organisation. **Babu Manickan** has been promoted to Head Presales MEA & APAC, recognising his strong contribution to the region and his expertise in customer engagement, solution advisory and presales leadership. **Shankar Omandhu**, Head Consulting International, brings extensive GRC experience and a strong track record in leading implementation and advisory engagements. Together, they further strengthen Swiss GRC’s leadership and delivery capabilities across MEA and APAC.
“Rajeev has played an important role in building our presence across MEA and APAC,” said Besfort Kuqi, Founder and CEO of Swiss GRC. “He understands the regulatory and business realities of the region very well and has a strong ability to translate customer needs into practical outcomes. His appointment reflects both his contribution to date and our commitment to further developing these markets.”
Rajeev Dutt said: “Organisations across the region are facing increasing expectations in governance, resilience and risk management. I am pleased to take on this expanded role and to continue working closely with our customers, partners and team as we further develop our business across MEA and APAC.”
With this step, Swiss GRC continues to invest in regional leadership, customer experience and delivery capabilities to support its next phase of growth across international markets.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Risk Management in an Uncertain World](https://swissgrc.com/fr/news/risk-management-in-an-uncertain-world/)
**Published:** avril 29, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** Geopolitical fault lines, technological disruption and a tightening regulatory landscape are reshaping the global risk profile from the ground up. At the ninth SWISS GRC DAY on 20 May 2026 in Zurich, the community will discuss what this means for governance, risk and compliance — in the year that host Swiss GRC AG marks its tenth anniversary.
**Content:**
*For the ninth time, SWISS GRC DAY 2026 will serve as a meeting place for professionals and executives from the business, legal, and technology sectors. The conference will focus on current and future developments in governance, risk, and compliance—topics that are more critical than ever in light of rapid technological, regulatory, and geopolitical changes.*
**Lucerne, April 29, 2026 – Geopolitical fault lines, technological disruption and a tightening regulatory landscape are reshaping the global risk profile from the ground up. At the ninth SWISS GRC DAY on 20 May 2026 in Zurich, the community will discuss what this means for governance, risk and compliance — in the year that host Swiss GRC AG marks its tenth anniversary.**
The world has grown harder to read. Supply chains react more sharply to political shocks; technological shifts — above all the deployment of artificial intelligence — are opening new dependencies and attack surfaces; and a thickening regulatory landscape, from the EU’s Digital Operational Resilience Act (DORA) to its Network and Information Security Directive (NIS2), is raising the bar for companies year after year. Conventional, often retrospective risk models are reaching their limits precisely where risks now emerge — in networked, cascading patterns with high impact depth.
This is where [**SWISS GRC DAY 2026**](https://swissgrc.com/swissgrcday) comes in. Under the motto « Risk Management in an Uncertain World, » the conference’s ninth edition convenes speakers from business, academia and practice on 20 May 2026 at the Radisson Blu Zurich Airport.
### Six perspectives on a shifting risk landscape
Opening the program is **Prof. Dr. Werner Gleißner**, board member of FutureValue Group AG and professor of risk management at TU Dresden, with the keynote « How Risky Is the World? » — locating the global trend lines in context and drawing out their implications for practice.
**Florian Worm**, Head of Enterprise Risk Management at HARTMANN GRUPPE, then makes the case for rigorous quantification as the foundation for better decisions — an argument bound to spark debate in a field where risk assessments still often rest on qualitative judgment.
**Alexandra Burns**, Partner and Head of Risk & Regulatory Consulting at PwC, takes on the new generation of systemic risk types under the pointed heading « Black Swans, Gray Rhinos and Green Dragons. »
**Prof.Dr. Stefan Hunziker**, Head of the Competence Center Risk & Compliance Management at Lucerne University of Applied Sciences and Arts, and **Dr. Alexander Hilsbos**, Head of Risk Management at the Insel Gruppe, face off in the « Science vs. Practice » debate, putting the often-invoked bridge between research and application to a genuine test.
**Michael Niedermann**, Head of Consulting at Swiss GRC, closes with the cultural dimension and the question of whether the human factor is risk management’s weakest link or its greatest lever.
### A moment of reflection, also on our own journey
The 2026 edition also marks a significant anniversary. Founded ten years ago by **Besfort Kuqi** and **Reto Zbinden**, Swiss GRC AG has established an international presence and now serves more than 250 clients across multiple industries. At the same time, SWISS GRC DAY has evolved into a key fixture for the community, attracting around 300 participants each year from leading and innovative companies across the DACH region.
Participation is free of charge, with limited capacity. The full programme, speakers, and registration details are available at **[www.swissgrc.com/swissgrcday](http://www.swissgrc.com/swissgrcday)**.
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC introduces new AI-native BPM software](https://swissgrc.com/fr/news/swiss-grc-introduces-new-ai-native-bpm-software/)
**Published:** juin 11, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** The Swiss GRC Process Center is a new AI-native process management software solution. It combines process management with governance, risk, and compliance (GRC) as well as operational resilience, providing an integrated view of processes, risks, controls, responsibilities, IT systems, data, and their interdependencies.
**Content:**
*The Swiss GRC Process Center visualizes the relationships between processes, risks, controls, documents, and responsibilities, and helps companies analyze operational impacts and critical dependencies.*
**Lucerne, June 11, 2026 – Swiss GRC AG expands its portfolio with the Swiss GRC Process Center, a new AI-native process management software. This solution merges process management with Governance, Risk & Compliance (GRC) and Operational Resilience, providing an integrated view of processes, risks, controls, responsibilities, IT systems, data, and their interdependencies.**
Many companies manage processes, risks, controls, and regulatory requirements in separate systems. The Swiss GRC Process Center takes an integrated approach, bringing this information together on a centralized platform. This way, organizations gain greater transparency regarding their process landscape and the interactions between processes, risks, controls, and supporting resources.
In addition to modeling and documenting business processes, the solution offers features for analyzing dependencies and impacts. Companies can trace which processes are interconnected, which risks affect critical operations, and which controls contribute to risk minimization. This allows for visibility of operational dependencies and enables more informed decision-making.
“Our goal was to rethink process management and closely link it with Governance, Risk, Compliance, and Operational Resilience. The result is a platform that makes relationships visible, breaks down silos, and assists companies in making more informed decisions,” says Besfort Kuqi, founder and CEO of Swiss GRC.
Key features of the Swiss GRC Process Center include a visual process designer, integrated document management in the process context, linking risks and controls with individual processes, and analyzing dependencies between processes, organizational units, IT systems, and data. The solution is supplemented with collaborative features for reviews, approvals, and teamwork among process stakeholders.
To facilitate a quick start, an import wizard assists in transferring existing process information. This allows companies to efficiently integrate and develop their existing process landscapes within the platform.
Another focal point of the solution is the support for Operational Resilience initiatives. Critical processes, dependencies, and control mechanisms can be documented, analyzed, and assessed centrally. This simplifies both the identification of potential vulnerabilities and the implementation of regulatory requirements.
Interested companies can explore the solution today through an interactive product preview at .
The official unveiling of the Swiss GRC Process Center will take place during the free webinar **“From Process Mapping to Process Management: Integrating BPM and GRC”** on **June 23, 2026, at 10:00 AM**. Participants will receive an in-depth understanding of the new solution, its features, and use cases for the first time. Participation is free and open to all interested parties.
Register for the webinar:
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
### [Swiss GRC and Volatilis Announce Strategic Partnership for Board-Ready Risk Intelligence](https://swissgrc.com/fr/news/swiss-grc-and-volatilis-announce-strategic-partnership-for-board-ready-risk-intelligence/)
**Published:** juin 16, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC and Volatilis, a specialist in quantitative risk management technology, today announced a strategic partnership with a shared mission: to make advanced quantitative risk analysis accessible and actionable at the board level, empowering decision-makers to lead with confidence.
**Content:**
*Driven by a shared mission to make risk management truly relevant at the board level, the partnership unites Switzerland’s leading GRC platform with Volatilis’s Monte Carlo simulation engine and AI-driven risk intelligence. Together, they translate complex quantitative analysis into clear, decision-ready insights for executive teams.*
**Lucerne/Munich, June 16, 2026 – Swiss GRC, the leading Swiss provider of integrated Governance, Risk & Compliance (GRC) software, and Volatilis, a specialist in quantitative risk management technology, today announced a strategic partnership with a shared mission: to make advanced quantitative risk analysis accessible and actionable at the board level, empowering decision-makers to lead with confidence.**
The collaboration combines Swiss GRC’s comprehensive GRC Toolbox, a platform covering risk management, internal controls, compliance, business continuity, and third-party risk, with Volatilis’s high-performance simulation engine, Monte Carlo analytics, copula-based correlation modeling, and AI-driven risk intelligence. The partnership is effective immediately, with the first joint release being the successful integration of Volatilis’s simulation capabilities into the risk module of Swiss GRC’s GRC Toolbox.
For too long, sophisticated quantitative risk methods have remained the domain of specialists, rarely reaching the decisions that matter most. Swiss GRC and Volatilis share a conviction that boards and executive teams deserve the same analytical rigor in their risk decisions that is standard in financial modeling and actuarial science. The partnership is built to close that gap: surfacing probabilistic risk insights in a form that is intuitive, credible, and immediately actionable for top management.
“For years, boards have had to rely on traffic lights and heat maps to make critical risk decisions. By embedding Volatilis’s simulation engine into the GRC Toolbox, we change that. Decision-makers now get the quantitative depth they need, presented in a way they can actually use and act on.” – Besfort Kuqi, Founder & CEO, Swiss GRC
“Our shared mission is board-ready risk management. Sophisticated quantitative methods should not remain locked in spreadsheets seen only by risk specialists. Together with Swiss GRC, we bring them into the boardroom, giving leadership teams the analytical foundation for better, more confident strategic decisions.” – Florian Worm, Founder & CEO, Volatilis
Swiss GRC x Volatilis - About & Contacts About Swiss GRC
Swiss GRC is the leading Swiss software company for Governance, Risk & Compliance (GRC). Headquartered in Lucerne, Switzerland, Swiss GRC serves clients across the DACH region and internationally. Its GRC Toolbox is a comprehensive platform covering risk management, compliance, internal controls, BCM, information security, audit management, and more. Swiss GRC was recognized in Forrester's GRC Platforms Landscape Q4 2025. [swissgrc.com](https://swissgrc.com)
About Volatilis
Volatilis is a Munich-based firm built on two pillars: a consulting practice for highly advanced quantitative risk modelling projects, and a technology practice comprising the Risk Intelligence Suite, a powerful platform capable of running and analyzing hundreds of thousands of correlated future scenarios within milliseconds. [volatilis.org](https://volatilis.org)
Media Contact, Swiss GRC
Yahya Mao
Swiss GRC
Hirschmattstrasse 36, 6003 Lucerne
Media Contact, Volatilis
Florian Worm
Volatilis
Munich, Germany
[ ](tel:0041412207500)
[ ](https://swissgrc.com/fr/contact/)
[ ](https://outlook.office365.com/owa/calendar/BuchungsseiteSwissGRCDiscoveryCall@swissgrc.com/bookings/s/rpj1TEhKVE6NqHsINYMApA2)
---
## Webinars
### [Information Isn't Intelligence: Connecting the Dots in Third-Party Risk](https://swissgrc.com/fr/webinar/information-isnt-intelligence-connecting-the-dots-in-third-party-risk/)
**Published:** juillet 18, 2026
**Author:** superadmin
**Excerpt:** Data tells you what happened. Connected intelligence tells you what matters. Join us for the exclusive introduction of the new Swiss GRC Third-Party Intelligence Center (TPIC).
**Content:**
Organizations have access to more third-party data than ever before, from financial indicators and cyber ratings to sanctions lists, adverse media and ESG information. Yet more data does not automatically lead to better decisions.
Effective third-party risk management requires connected intelligence: the ability to understand which signals matter, how organizations and risks are related, where hidden dependencies exist and how external developments affect your own business.
In this webinar, we will introduce the new [SwissGRC® Third-Party Intelligence Center](http://third-party-intelligence-center "SwissGRC® Third-Party Intelligence Center"). Discover how TPIC transforms scattered external information into actionable intelligence, reveals emerging exposure and brings relevant insights directly into the SwissGRC® Platform. You will learn how organizations can move beyond isolated scores and periodic assessments towards continuous, intelligence-driven third-party risk management. A live demonstration will show how company relationships, dependencies, external risk signals and internal GRC processes are brought together to support faster and more confident decisions.
---
### [Modern approaches to risk quantification: How stochastics and simulation make the future tangible](https://swissgrc.com/fr/webinar/modern-approaches-to-risk-quantification-how-stochastics-and-simulation-make-the-future-tangible/)
**Published:** mai 18, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** How can risks be made tangible and well-informed decisions be made in the face of uncertainty? Find out more in our webinar on risk quantification.
**Content:**
How can organizations make risks more tangible and enable sound decision-making under uncertainty? Modern approaches to risk quantification go far beyond traditional heat maps and subjective assessments. By leveraging stochastic methods, simulations, and quantitative models, organizations can assess risks more transparently, simulate scenarios, and strengthen data-driven strategic decision-making.
In this webinar, **Florian Worm**, Founder & Managing Director of [Volatilis](https://www.volatilis.org/) GmbH, **Prof. Dr. Stefan Hunziker**, Professor of Risk Management and Head Competence Center Risk & Compliance Management at Lucerne University of Applied Sciences and Arts, as well as **Nikolai Tsenov**, Head Solutions & Innovation at [Swiss GRC](https://swissgrc.com/), will explore modern approaches to risk quantification and demonstrate how quantitative methods are already being successfully applied in corporate management and decision-making processes.
The session will combine academic perspectives with practical business applications, ranging from the fundamentals of stochastic modeling to the use of quantitative methods in the boardroom. Participants will also gain insights into how modern risk quantification and simulation approaches can be integrated within the GRC Toolbox to support informed and data-driven decisions. Key topics include:
- Myths and misconceptions surrounding risk quantification
- Risk quantification today: context, opportunities, and challenges
- Bridging science and practice in modern risk models
- How stochastic methods and mathematical models support informed decision-making
- Quantitative methods in the boardroom and corporate steering
- The value of simulations for transparency, resilience, and decision-making capabilities
- Practical examples and insights into implementation within the GRC Toolbox
**Who should attend?**
This webinar is designed for professionals and decision-makers in Risk Management, Enterprise Risk Management (ERM), Governance, Compliance, Internal Audit, Finance, as well as executives and board-level stakeholders seeking to strengthen data-driven decision-making and modernize their approach to risk management.
Discover how organizations can make uncertainty measurable and use risk as a strategic management factor.
---
### [Harmonizing Governance and Risk across NEQSOL Holding with Swiss GRC](https://swissgrc.com/fr/webinar/harmonizing-governance-and-risk-across-neqsol-holding-with-swiss-grc/)
**Published:** novembre 26, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** During this webinar, Samir Karimov, Head of Risk Management and Sustainability at NEQSOL Holding, will offer an inside look at how the Group built a modern GRC system with Swiss GRC.
**Content:**
Managing governance, risk and compliance across a diversified international group is a demanding task — especially when different countries, regulatory expectations, and organizational structures must work together under one framework. [NEQSOL Holding](https://www.neqsolholding.com/) faced exactly this challenge while operating in more than 10 countries and across a variety of industries, from energy and telecommunications to high-tech and construction.
To address these complexities, NEQSOL Holding chose to implement a unified digital platform using the GRC Toolbox. The solution enables subsidiaries to [manage risk](https://swissgrc.com/fr/risk-management-software/ "Risk Management Software"), ICS, compliance, and HSE processes autonomously while providing group leadership with transparency, comparability and a single source of truth. The result is a GRC ecosystem that supports both strategic oversight and operational ownership — a balance that many international organizations struggle to achieve.
During this webinar, **Samir Karimov, Head of Risk Management and Sustainability at NEQSOL Holding**, will offer an inside look at how the Group built a modern GRC system that works across borders, business models and maturity levels.
If you want to learn what it takes to build a scalable and future-proof GRC framework in practice — not just in theory — this session will be highly relevant. **Reserve your spot** to gain exclusive insights from a journey where governance, risk, compliance and sustainability were brought together into one effective framework.
---
### [Information Security with a System: How Helvetia Made It Work](https://swissgrc.com/fr/webinar/information-security-with-a-system-how-helvetia-made-it-work/)
**Published:** septembre 29, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** In this webinar, Bruno Freschi, Group CISO at Helvetia, will share how his team turned the ISMS into a system that works across borders and business lines. Expect valuable insights and best practices.
**Content:**
## Implementing and operating an ISMS at scale is not a theoretical exercise. It’s a challenge that tests organization, integration, and technology. Few companies have pushed it as far as **Helvetia**, one of Switzerland’s largest insurers.
Helvetia’s **decentralized ISMS spans multiple business units and multiple locations**. To achieve this, Helvetia partnered closely with **Swiss GRC** to design and roll out the ISMS **step by step**. Together, they built one of the most mature ISMS implementations in the market—capable of meeting high regulatory expectations, including the requirements of the [EU Digital Operational Resilience Act (DORA)](http://swissgrc.com/fr/dora).
In diesem Webinar berichtet Bruno Freschi, Group CISO bei Helvetia, wie sein Team das ISMS zu einem System gemacht hat, das über Grenzen und Geschäftsbereiche hinweg funktioniert. Freuen Sie sich auf Einblicke und Best Practices zu folgenden Themen:
- Build and govern an ISMS within an international group
- Connect the ISMS across the organization because security is never an island
- Leverage automation and advanced capabilities, such as:
- Integrations (e.g. ServiceNow for ITSM, LeanIX as CMDB, SAP for third parties)
- Workflow automation (e.g. security in projects, security risk management, asset management, supplier security checks)
- Reporting to ensure transparency, consistency, and management-ready insights at scale
Helvetia employs around 14,400 people worldwide and operates in Switzerland, Germany, Austria, Italy, Spain and France, as well as selected international markets such as Liechtenstein and Singapore. With its three business segments—non-life insurance, life insurance, and asset management—Helvetia is one of the largest and most internationally active insurers in Switzerland.
This session is for professionals who want to see what **ISMS maturity looks like in practice** when a leading insurer and a leading GRC provider join forces to create a system that truly works.
Reserve your spot and gain exclusive insights from a journey where strategy, expertise, and technology came together for lasting impact.
---
### [From Risk Management to Risk Intelligence: Evolving Your TPRM Approach](https://swissgrc.com/fr/webinar/from-risk-management-to-risk-intelligence-evolving-your-tprm-approach/)
**Published:** juillet 31, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Join us with Michael Rasmussen for a webinar to learn how leading organizations are evolving their Third-Party Risk Management (TPRM) strategies - backed by expert knowledge and award-winning technology.
**Content:**
## In a world of growing interdependencies, managing third-party risk requires more than checklists and compliance. It calls for **real-time intelligence, automation, and strategic insight**.
Join us for a high-impact webinar to explore how leading organizations are evolving their **Third-Party Risk Management (TPRM)** strategies supported by expert insights and award-recognized technology.
We’re honored to welcome **Michael Rasmussen**, globally renowned GRC analyst, as our **guest speaker**. Michael will open the session with a thought-provoking look at today’s TPRM landscape highlighting emerging risks, overlooked blind spots, and how businesses can stay ahead.
**Nikolai Tsenov**, our Head Strategy & Business Development, will then showcase how Swiss GRC’s [TPRM software](https://swissgrc.com/fr/tprm-software), recently named a **2025 Best of Technology Awards finalist** by *WirtschaftsWoche*, enables organizations to:
- Efficiently **onboard and classify third parties**
- Assess **inherent risk and service criticality**
- Apply smart **tiering, due diligence, and exit strategies**
- Integrate with **external intelligence** (e.g. cyber scores, ESG data, creditworthiness, company profiles)
This session will be moderated by **Yahya Mohamed Mao**, our Head Marketing & Communications. It’s ideal for professionals in **risk, compliance, procurement, and IT** who want to move beyond traditional risk management and harness the power of **risk intelligence**.
**Reserve your spot now** and learn how to turn risk data into strategic action with expert insights and award-recognized technology.
---
### [Artificial intelligence in Swiss law: understanding requirements and implementing them in practice with the AI GRC module](https://swissgrc.com/fr/webinar/artificial-intelligence-in-swiss-law-understanding-requirements-and-implementing-them-in-practice-with-the-ai-grc-module/)
**Published:** mai 23, 2025
**Author:** superadmin
**Excerpt:** Take part in our webinar with Reto Zbinden, Dimitri Korostylev and Nikolai Tsenov: Understanding AI in Swiss law and implementing it with AI-GRC modules.
**Content:**
## Content
In this webinar with [Swiss Infosec AG](https://www.infosec.ch) , you will receive a practical overview of the current regulatory requirements for the use of AI applications in Swiss SMEs. The focus is on AI in Swiss law – in **particular data protection, copyright, the Unfair Competition Act, transparency obligations and risk management**. It’s not just about technology, but about the legally compliant use of AI in accordance with Swiss law.
Using our **[AI GRC-Moduls](https://swissgrc.com/ai-grc/)**, we show how companies can systematically record, evaluate and control their AI systems – and thus create the basis for compliance, transparency and responsible innovation. Ideal for compliance, data protection and IT managers who want to establish future-proof and legally compliant AI processes.
## Questions and further steps
At the end of the webinar, you will have the opportunity to ask your individual questions and discuss specific use cases with our experts.
---
### [Responsible Use of AI: Findings from FINMA AM 08/2024 and Practical Solutions](https://swissgrc.com/fr/webinar/responsible-use-of-ai-findings-from-finma-am-08-2024-and-practical-solutions/)
**Published:** janvier 31, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Take part in our webinar with David Rosenthal, one of Switzerland's leading experts in data and technology law. We will shed light on the findings of FINMA AM 08/2024 and show practical solutions.
**Content:**
## Content
In the new FINMA Guidance 08/2024 on governance and risk management in the use of artificial intelligence, FINMA draws the attention of supervised institutions to the need for appropriate identification, assessment, management and monitoring of the risks resulting from the use of AI and the associated challenges.
On this occasion, we cordially invite you to our webinar on the topic of ‘AI use obligated: Findings from FINMA AM 08/2024 and practical solutions’ to join us.
Together with David Rosenthal, one of the leading Swiss experts in data and technology law, we will highlight the weaknesses and challenges identified by FINMA on 18 February 2025 from 10:00 a.m. and present practical solutions using our GRC toolbox, including with regard to classification, governance, oversight, performance management, transparency and compliance of AI use cases.
---
### [Enhancing Vendor Security: A Deep Dive into Automation and Continuous Monitoring](https://swissgrc.com/fr/webinar/enhancing-vendor-security-a-deep-dive-into-automation-and-continuous-monitoring/)
**Published:** novembre 11, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Organizations must now contend with a vast and ever-evolving attack surface, making it imperative to maintain a strong security posture across their entire ecosystem. Join Swiss GRC and BitSight for a webinar on transforming your vendor cyber risk management.
**Content:**
## Content
As digital interdependencies grow, so does the complexity of managing vendor risk. Organizations must now contend with a vast and ever-evolving attack surface, making it imperative to maintain a strong security posture across their entire ecosystem.
**The Solution: Continuous Monitoring and Automation**
Organised by Swiss GRC and [Bitsight](https://www.bitsight.com/), this webinar will delve into the power of continuous monitoring and automation to streamline your vendor risk management process. Our industry experts will share insights on:
- **Identifying and Assessing Critical Vendors:** Learn how to prioritize vendors based on risk and impact.
- **Leveraging Automation for Efficiency:** Discover how to automate data collection and analysis to save time and resources.
- **Implementing Continuous Monitoring:** Understand the benefits of real-time monitoring to detect and respond to threats promptly.
- **Enhancing Vendor Relationships:** Learn how to collaborate with vendors to improve their security practices.
**What You’ll Gain:**
- Practical strategies to reduce vendor risk
- Best practices for implementing a robust vendor risk management program
- Actionable insights from industry experts
- The opportunity to network with other security professionals
**This webinar took place on Wednesday, January 22, 2025 10:00 AM (CET). If you were unable to attend, you can request the recording by completing the form on the right.**
---
### [GRC in the Age of AI: 2024 Insights and AI Capabilities of the GRC Toolbox](https://swissgrc.com/fr/webinar/grc-in-the-age-of-ai-2024-insights-and-ai-capabilities-of-the-grc-toolbox/)
**Published:** juin 10, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Discover how AI is transforming Governance, Risk, and Compliance in 2024. Join our webinar to explore AI capabilities of the GRC Toolbox, learn about the latest trends, and gain strategies to enhance your organization's resilience and efficiency. Don't miss out!
**Content:**
## Content
As we navigate through 2024, the integration of Artificial Intelligence (AI) into [Governance, Risk, and Compliance (GRC)](https://swissgrc.com/fr/solutions) frameworks becomes pivotal. Consequently, organizations strive to maintain robust compliance standards, manage risks effectively, and ensure corporate governance. This webinar provides participants with recent insights. Learn how AI transforms GRC practices. You will also learn about the latest AI functions of our GRC Toolbox. **This webinar has been held in English**.
## Subjects
- **Overview of GRC Trends 2024 by Rajeev Dutt, General Manager MEA & APAC of Swiss GRC:** Gain insights into the latest trends shaping the GRC landscape in 2024. Rajeev Dutt will provide an in-depth analysis of emerging GRC practices, focusing on how AI is transforming governance, risk management, and compliance.
- **Demo of the GRC Toolbox by Nikolai Tsenov, Head of Product & Business Development of Swiss GRC:** Experience a live demonstration of the GRC Toolbox, featuring Advanced Analytics and AI-powered use cases: AI Assistant, EU AI Act, Sanction and Media Screening, ESG and Business Intelligence Scores, Cybersecurity Scores and Speech Analytics.
---
### [Case Study PostFinance AG: Integrated Risk, Compliance and Security Management](https://swissgrc.com/fr/webinar/case-study-postfinance-ag-integrated-risk-compliance-and-security-management/)
**Published:** février 8, 2023
**Author:** shayeste
**Excerpt:** From experts directly from practice. RM and ICS were followed by GRC:
- Unified control of various GRC processes
- Insight into the GRC software solution (live demo)
- Exchange of experiences and tips from the speakers
**Content:**
## Content
Integrated risk, compliance and security management: procedure and advantages of integrating different GRC disciplines with the help of software support.
Mirko Hegi, Deputy Head of Risk Control Services at PostFinance AG shares his knowledge and experience around the digitalization and optimization of GRC disciplines. We will explore on how PostFinance, with the help of the Swiss GRC software solution, has replaced various individual solutions and step by step has created a unified control of various GRC activities. In addition to the practical report with a hands-on exchange of experiences and tips from the speakers, you will also be able to watch the GRC solution live in action.
## Subjects
- Strategic and operational risk management
- Internal Control System (ICS)
- Business Impact Analysis
- Information Security Management
- Data protection management
- Contract management
- Other regulatory topics
---
### [SWISS GRC DAY 2021](https://swissgrc.com/fr/webinar/swiss-grc-day-2021/)
**Published:** février 8, 2023
**Author:** shayeste
**Excerpt:** You are warmly invited to the ONLINE SWISS GRC DAY 2021! At the SWISS GRC DAY, the GRC community from all over Switzerland and nearby countries will meet. News, challenges and trends in the areas of governance, risk management and compliance (GRC) will be discussed at first hand.
**Content:**
## Content
In extraordinary times, it is all the more important not to lose sight of crucial developments. Take this opportunity to get first-hand, overarching information on trends, challenges and solutions in the GRC sector and keep an overview of the whole.
## Presentations
- The Risk Intact Process. The process that does not exist (Alexander Hilsbos)
- BCM – Implementation of a systemically important bank (Sandra Greminger)
- Cyber Risk & Resilence – Quo vadis? (Axel Sitt)
- The EU Whistleblower Directive and its significance for Swiss companies (Moritz Homann)
- Risk and Compliance Management based on the Three Lines of Defence Model (Bea Katona / Anuschka Küng)
- News from the world of enterprise risk management (Prof. Dr. Stefan Hunziker)
---
### [The new data protection law and its implementation](https://swissgrc.com/fr/webinar/the-new-data-protection-law-and-its-implementation/)
**Published:** février 8, 2023
**Author:** shayeste
**Excerpt:** Experts explain and show how a software solution can help to efficiently implement legal requirements.
**Content:**
## Content
In September, the draft of the total revision of the Data Protection Act was approved. The new data protection law will be stricter and based on the EU General Data Protection Regulation (GDPR). But what will change for companies? And how can a software solution help?
- Swiss data protection law compared to the EU GDPR
- Most important changes for companies
- GRC Toolbox and data protection
---
## Success Stories
### [Modernizing Risk Management at IB Langenthal AG](https://swissgrc.com/fr/success_story/modernizing-risk-management-at-ib-langenthal-ag/)
**Published:** mai 29, 2026
**Author:** superadmin
**Excerpt:** IB Langenthal AG is a regional energy and infrastructure provider headquartered in Langenthal, Switzerland. The company reliably supplies the region with electricity, gas, heating, telecommunications, water, and a range of additional services, making a significant contribution to the quality of life and economic development of the area.
In addition to ensuring a secure and dependable supply of essential services, IB Langenthal AG is committed to sustainable solutions and responsible, forward-looking corporate governance.
**Content:**
#### IB Langenthal AG relies on the GRC Toolbox to centrally manage risks, streamline reporting processes, and establish a reliable foundation for strategic decision-making.
## Initial situation and objectives
[IB Langenthal AG](https://ib-langenthal.ch/ "IB Langenthal AG") faced the challenge of adapting its [risk management](https://swissgrc.com/fr/risk-management-software/ "Risk Management Software") processes to growing organizational requirements. The previous Excel-based approach was increasingly proving insufficient, particularly in terms of transparency, traceability, and efficient reporting. At the same time, both the complexity of risks and the expectations of the Executive Management and Board of Directors regarding transparency and reporting continued to increase.
As a result, there was a need for a solution that could centrally manage risks while enabling flexible and meaningful analyses. With the implementation of the [GRC Toolbox](https://swissgrc.com/fr/solutions/ "Solutions"), a modern, database-driven platform was introduced to support the structured recording and consistent assessment of risks. All relevant information is now centrally available and can be evaluated efficiently.
The objective was to further develop risk management in a future-oriented manner, reduce manual processes, and provide a reliable basis for decision-making for both Executive Management and the Board of Directors.
## Implementation and collaboration
To further enhance its [risk management](https://swissgrc.com/fr/risk-management-software/ "Risk Management Software") capabilities, IB Langenthal AG implemented the Risk Management module of the GRC Toolbox. The implementation was carried out in a practical manner and tailored to the company’s existing requirements.
The collaboration with Swiss GRC was consistently cooperative, professional, and efficient. Additional requirements, particularly in the area of reporting, were openly addressed and jointly implemented. Thanks to the close coordination between both teams, the solution was seamlessly integrated into existing processes.
## Challenges and lessons learned
01 ChallengeReplacing a legacy Excel solution with limited analysis capabilities
SolutionIntroduction of a central, database-driven platform for structured risk management
02 ChallengeGrowing demands for transparency and reporting from the Board of Directors
SolutionDevelopment of flexible, customizable reporting functions in close coordination with the specialist departments
03 ChallengeAdditional, project-specific requirements during implementation
SolutionOpen intake of requirements and iterative further development together with Swiss GRC
## Key outcomes and benefits
The decision to choose Swiss GRC was based on strong references, a high level of professionalism, and a reliable partnership. In practice, the solution stands out through its structured data management, efficient reporting capabilities, and reliable support for regulatory requirements.
- **Centralized Risk Management Platform:** Consistent capture and availability of all relevant risk data
- **Transparency and Traceability:** Clear structures that support informed decision-making and audit-ready documentation
- **Efficient Reporting:** Tailored reports with minimal effort, fully aligned with regulatory requirements
- **Optimized Processes:** Replacement of manual Excel-based activities with automated workflows
- **High Flexibility:** Continuous adaptation and enhancement to meet evolving requirements and standards
---
### [BENEFIT’s Journey to Combined Assurance with Swiss GRC](https://swissgrc.com/fr/success_story/benefits-journey-to-combined-assurance-with-swiss-grc/)
**Published:** avril 8, 2026
**Author:** superadmin
**Excerpt:** The BENEFIT Company is the Kingdom of Bahrain’s leading provider of electronic financial transactions and fintech services, operating at the core of the national financial infrastructure. Its mandate includes enabling secure, interoperable, and innovative transaction services that support the financial ecosystem of Bahrain.
**Content:**
#### The BENEFIT Company has significantly strengthened its governance, risk, and compliance (GRC) capabilities through the implementation of Swiss GRC’s integrated platform. What began as a strategic exploration evolved into a transformation towards true Combined Assurance, enhancing collaboration, automation, and audit excellence across the organization.
## Background and strategic starting point
In Q4 2023, [BENEFIT](https://benefit.bh/ "BENEFIT") launched a strategic initiative driven by the Cyber Risk Committee: to explore Governance, Risk, and Compliance (GRC) solutions and implement a platform capable of automating processes and improving collaboration across assurance functions.
The initiative was closely aligned with Internal Governance Committee discussions, bringing together stakeholders from Compliance, Internal Audit, Business Continuity, Risk Management, Information Security, and Legal. The objective was clear: move away from fragmented and manual processes towards a more integrated and transparent governance framework.
To inform the decision-making process, BENEFIT assessed GRC providers within Bahrain, leveraging insights from organizations that had already implemented such solutions locally.
## Challenges Along the Way
The evaluation process revealed two key challenges:
**Cost vs. Organization Size**
Many GRC solutions were designed for large enterprises with extensive assurance teams, resulting in cost structures that were not aligned with BENEFIT’s organizational size.
**Limited Customization**
Available solutions lacked the flexibility to adapt to the specific operational and regulatory context in Bahrain, making it difficult to tailor them to BENEFIT’s needs.
These challenges highlighted the need for a solution that could balance sophistication with flexibility and scalability.
## A turning point
In January 2024, BENEFIT attended a two-day GRC event in Dubai, where multiple providers presented their solutions. During this event, the team met Rajeev Dutt from Swiss GRC.
What stood out was a simple but decisive question:
*«What do you need? What are your expectations?»*
This shifted the conversation from product capabilities to organizational requirements.
The immediate question from BENEFIT was:
*«Can Swiss GRC be customized to our needs, processes, and budget?»*
The answer was a confident **«Yes.»** From that moment, the foundation for the partnership was established.
## Selection and implementation
Following a thorough evaluation and internal alignment process, BENEFIT recommended Swiss GRC to its Board Committees. After approval, the implementation and licensing agreement was signed, and the rollout began. A key differentiator was Swiss GRC’s ability to provide deep customization without impacting other customers. This enabled BENEFIT to design workflows tailored precisely to its internal processes while maintaining a consistent governance structure.
## Implementation Approach and Phased Rollout
The implementation was structured in phases to ensure a controlled and sustainable rollout:
**Phase 1 – Internal Audit**
[Internal Audit](https://swissgrc.com/fr/internal-audit-software/ "Internal Audit Software") was the first function to go live, with fully automated workflows aligned to the Global Internal Audit Standards 2024.
**Phase 2 – Compliance**
Compliance requirements were finalized and prepared for deployment, ensuring regulatory processes would be integrated into the broader governance framework.
**Phase 3 – Expansion Across Functions**
The platform was further extended to include:
- Policy Management
- Risk Management
- Business Continuity
- Legal
- Information Security
One of the platform’s standout capabilities, which will be further leveraged in the future, is its integration potential, providing flexibility for continued expansion and system connectivity.
## Achievements and Global Recognition
As part of the implementation, BENEFIT’s Internal Audit function aligned its methodology and digital workflows with the Global Internal Audit Standards (GIAS) 2024, issued by the Institute of Internal Auditors (IIA), the globally recognized authority for the internal audit profession.
An independent external assessment confirmed full conformance, leading to the Internal Audit team receiving the Full Compliance Award from the IIA during the 2025 Audit, Anti-Fraud, and Information Technology Conference in Abu Dhabi.
The award was accepted on 20 November 2025 by Mansoor AlAlwan, Chief Audit Executive, on behalf of The BENEFIT Company. This achievement, acknowledged by representatives of the IIA, ISACA, and ACFE, underscores BENEFIT’s leadership in governance, audit quality, and professional practice. It also reflects the strength of BENEFIT’s operational readiness and the maturity of its internal control environment. Swiss GRC’s platform played an essential role in enabling the digital execution of these standards, providing the structural and functional capabilities required to meet internationally recognized benchmarks.
## Key outcomes and benefits
Through the implementation of Swiss GRC’s technology platform, The BENEFIT Company has achieved measurable improvements across its assurance functions, strengthening both operational effectiveness and organizational governance maturity.
**Customization and Flexibility** Swiss GRC adapted seamlessly to BENEFIT’s size, processes, and budget, enabling a tailored implementation.
**Enhanced Collaboration Across Functions** The platform strengthened coordination between assurance functions, supporting a true Combined Assurance approach.
**Global Recognition and Standards Alignment** Full compliance with international audit standards was independently validated and recognized on a global stage.
---
### [System-Enabled, Cross-Functional Risk Management at Visana with Swiss GRC](https://swissgrc.com/fr/success_story/system-supported-and-cross-functional-risk-management-at-visana-with-swiss-grc/)
**Published:** février 2, 2026
**Author:** superadmin
**Excerpt:** Visana is one of the leading Swiss health and accident insurance providers. The company offers health, accident, supplementary, and property insurance for both private and corporate customers. Overall, Visana serves around 900,000 private customers and approximately 17,000 corporate clients. Its headquarters are located in Bern, with around 1,400 employees working in approximately 50 agencies across Switzerland. The total premium volume exceeds CHF 4 billion.
**Content:**
#### Discover how Visana implemented the Swiss GRC Toolbox to establish a system-supported, transparent, and cross-functional risk management framework.
## Initial situation and objectives
[Visana](https://www.visana.ch/privatpersonen/lebenssituationen/ereignisse/neu-in-der-schweiz/welcome-to-switzerland) was faced with the challenge of harmonizing its GRC landscape and mapping it within a central system solution. A key objective was to strengthen the interaction between existing governance and control systems and to consolidate the previously heterogeneous storage structures into a unified environment.
With the implementation of the Swiss GRC Toolbox, a central platform was established on which all [risk-relevant information](https://swissgrc.com/fr/tprm-software/ "Software Solution for Third Party Risk Management (TPRM)") is systematically captured, managed, and documented. Cross-functional collaboration improved significantly thanks to standardized folder structures, clear user guidance, and transparent processes.
Visana pursued the goal of further developing its GRC system. The focus was on replacing parallel data repositories and introducing largely automated processes for risk assessment. The implementation of an annual cut-off was also important in order to enable transparent and system-supported comparisons.
## Implementation and collaboration
Following an evaluation, Visana decided to choose Swiss GRC. The decisive factors were the user-friendliness and clarity of the [GRC Toolbox](https://swissgrc.com/fr/solutions/ "Solutions"), the high level of flexibility in integrating existing processes, and the future-proof architecture of the solution.
In collaboration with the Swiss GRC consulting team, the new GRC modules were gradually implemented and successfully put into operation.
## Challenges and lessons learned
**Challenges****Solution approach**Different GRC requirementsModular implementation and iterative expansionComplexity of regulatory requirementsUse of configured standards and customizable templates
## Key outcomes and benefits
**Holistic GRC on one platform:** All core GRC processes are integrated into a single solution and documented in a traceable and auditable manner.
**Traceability and audit readiness:** Clear structures and system-supported processes enable easier audits and reviews.
**Scalability:** The modular design allows flexible further development according to evolving needs.
**Increased efficiency:** Standardization and digitalization of previously separate processes.
---
### [Integrated Risk and Business Continuity Management at Zurich University Hospital](https://swissgrc.com/fr/success_story/integrated-risk-and-business-continuity-management-at-zurich-university-hospital/)
**Published:** janvier 13, 2026
**Author:** Yahya Mohamed Mao
**Excerpt:** Zurich University Hospital (USZ) is one of Switzerland’s leading medical centers, offering a comprehensive range of highly specialized diagnostics, treatments, and research. With more than 10,000 employees, USZ fulfills a central role in patient care, medical education, and scientific advancement. The combination of clinical excellence, research expertise, and innovative care models makes USZ a key institution within the Swiss healthcare system.
**Content:**
#### Discover how Zurich University Hospital (USZ), in collaboration with Swiss GRC, established a central platform for information security, risk management, business continuity, and audit, laying the foundation for a robust security culture and sustainable governance in healthcare.
## Initial situation and objectives
[Zurich University Hospital (USZ)](https://www.usz.ch) is one of Switzerland’s leading healthcare institutions and faces complex daily requirements related to security, quality, and resilience. Through the Association of Zurich Hospitals, USZ became aware of Swiss GRC at an early stage. The trigger for the project was a strategic decision to establish an integrated and standardized risk and business continuity management approach that would optimize and consolidate existing processes.
This need was driven by both internal objectives and external requirements. Internally, the focus was on strengthening the hospital’s risk and security culture, increasing transparency, and creating a consistent data basis across all departments. Externally, rising regulatory expectations and the growing complexity of the healthcare sector acted as catalysts for expanding and scaling the existing GRC framework.
The project objectives were clearly defined:
- Establishment of a standardized, integrated GRC system
- Increased transparency and traceability of all risk and security processes
- Replacement of decentralized documentation with a central digital platform
- Efficiency gains through standardized workflows and clearly defined central responsibilities
## Implementation and collaboration
The implementation of the GRC Toolbox was carried out in close coordination between the USZ project team and the consultants from Swiss GRC. From the outset, the collaboration was characterized by open communication, short decision-making paths, and a strong focus on execution. Requirements were jointly specified, processes were systematically mapped, and both functional and technical questions were resolved efficiently.
Challenges that arose during implementation were addressed and resolved promptly thanks to the constructive partnership. Particularly valuable for USZ was the fast response time of Swiss GRC, which significantly accelerated the project and enabled the continuous evolution of the solution.
The modular architecture of the GRC Toolbox allowed for a phased rollout of key functional areas. Today, USZ already uses the **[ISMS](https://swissgrc.com/fr/information-security-management-isms-software/ "Information Security Management / ISMS-Software")**, **Risk Management**, **BCM**, and **Audit** modules. The **Data Protection** and **Internal Control System (ICS)** modules are nearing final implementation. In addition, the expansion to include a **[Third Party Risk Management (TPRM)](https://swissgrc.com/fr/tprm-software/ "Software Solution for Third Party Risk Management (TPRM)")** module is planned for the coming year, enabling structured and transparent management of external dependencies.
## Challenges and lessons learned
**Challenges**Solution approachHeterogeneous, partly manual and Excel-based risk and security processesIntroduction of a central digital platform with standardized and traceable workflowsNeed for greater transparency and a consistent data foundationEstablishment of clearly defined structures, roles, and assessment methodologies within the toolboxStrengthening the security and risk culture in hospital operationsSystematic mapping of processes within ISMS, Risk Management, and BCM to promote a unified approachInterdisciplinary collaboration across multiple departmentsClose coordination, an agile implementation approach, and continuous support from Swiss GRC
## Key outcomes and benefits
The implementation of the GRC Toolbox enabled USZ to structurally strengthen and modernize core elements of its risk and security management. Previously decentralized and partially manual processes were replaced by a unified digital platform that now provides a consistent data foundation across all relevant areas. This has resulted in significantly improved transparency, efficiency, and traceability in day-to-day operations.
A key benefit is that all data can now be centrally captured, analyzed, and evaluated. The harmonization of processes also facilitates coordination between departments and enables structured, audit-ready documentation. As a result, USZ now operates a GRC framework that not only supports compliance with internal standards but also provides a strong foundation for meeting regulatory requirements. The clearly defined digital standards within the toolbox create clarity for all users and foster a shared understanding of risk and security processes.
## Decision to choose Swiss GRC
The decision in favor of Swiss GRC was driven by several factors. Particularly decisive were the **positive references** USZ obtained from other organizations, as well as the additional trust created by the option to procure the solution via the **[Association of Zurich Hospitals](https://swissgrc.com/fr/news/vzk-and-swiss-grc-join-forces-to-strengthen-grc-in-zurich-hospitals/ "Partnership Swiss GRC VZK")**. Swiss GRC also impressed with a modular solution that can be flexibly adapted to the needs of a complex hospital environment, combined with strong domain expertise in governance, risk, and compliance.
The implementation demonstrated that the GRC Toolbox is not merely a technical tool, but a strategic foundation for building a resilient risk and security culture. The close collaboration and continuous enhancement of the solution further confirm the value of the chosen partnership.
---
### [Harmonizing Governance and Risk across NEQSOL Holding](https://swissgrc.com/fr/success_story/harmonizing-governance-and-risk-across-neqsol-holding-with-swiss-grc/)
**Published:** octobre 30, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** NEQSOL Holding is an international group of companies active in telecommunications, energy, construction materials, and technology. The group’s portfolio includes Azerconnect, Bakcell, Vodafone Ukraine, Nobel Energy, Norm, and Nobel Upstream.
**Content:**
#### Through close collaboration with Swiss GRC, NEQSOL Holding has transformed its approach to governance, risk, and compliance by implementing a comprehensive GRC platform that unites diverse business entities under a single digital framework, enhancing transparency, efficiency, and accountability across the Group.
## Background and objectives
NEQSOL Holding, an international group with headquarters in Amsterdam, Baku, and Kyiv, operating in 11 countries and comprising subsidiaries such as Bakcell, Azerconnect Group, Vodafone Ukraine, Nobel Energy, Nobel Upstream, and Norm, set out on a journey to further digitalize its governance, risk, and compliance practices. Operating across diverse markets, NEQSOL Holding explored the options to adopt a unique approach to cover a group-wide risk management system that could respect the unique requirements of each subsidiary while maintaining a unified oversight structure at the holding level.
**Key drivers behind the initiative:**
- Upgrade the risk management practices across its group companies.
- Meet internal compliance and regulatory requirements.
- Digitize health, safety, and environment (HSE) processes for efficiency and greater transparency and accountability.
## Implementation and collaboration
The implementation of the GRC Toolbox was the result of a close and structured collaboration between NEQSOL Holding and Swiss GRC. From the outset, both teams worked hand in hand through a series of focused workshops to define requirements, model workflows, and tailor the platform to the diverse realities of each subsidiary while preserving consistency across the holding.
Built on a modular architecture, the solution empowers subsidiaries to manage their risks, controls, and compliance activities autonomously. At the same time, it provides NEQSOL Holding with a unified, real-time view of group-wide performance—turning complexity into transparency.
On NEQSOL’s side, **Samir Karimov**, Head of Risk Management, guided the initiative, ensuring alignment between strategic goals and practical execution. From Swiss GRC, **Erlete Baliqi (Solution & AI Engineer)** led the technical implementation and served as the primary contact throughout the project, later joined by **Edona Shala (GRC Consultant)**.
The result is a fully integrated GRC ecosystem covering **[Risk Management](https://swissgrc.com/risikomanagement-software/ "Risk Management"), [Internal Control System (ICS)](https://swissgrc.com/iks-software/), Compliance, Corporate Governance, Strategic Initiatives, Contracts, and Health, Safety & Environment (HSE)**, supporting consistent governance and risk oversight across the entire Group.
## Challenges and lessons learned
ChallengeSolution ApproachDifferent requirements across subsidiariesCreation of a configurable solution enabling each entity to adapt the framework locally while maintaining overall consistency.Complexity of HSE processesDigitalization of the full HSE process chain—from permits and approvals to incident reporting, inspections, and employee health registers.Ensuring group-wide adoptionContinuous engagement through workshops, iterative testing, and user training to foster ownership and drive user acceptance.Data consistency and reporting across entitiesImplementation of standardized data structures, reporting templates, and automated dashboards. Balancing speed and quality during rollout Phased implementation approach, ensuring stable rollouts with continuous feedback cycles and quality assurance at each stage.These challenges were overcome thanks to the strong collaboration and mutual understanding between NEQSOL Holding and Swiss GRC teams. This close cooperation ensured that requirements were clearly understood, solutions were quickly adapted, and both sides worked as one team throughout the project.
## Key outcomes and benefits
NEQSOL Holding chose Swiss GRC for its ability to deliver flexible, dynamic solutions that could adapt to a group-wide environment with very different local requirements.
The key benefits include:
- Risk management across four companies is now harmonized in one tool, with clear responsibilities and efficient review cycles.
- Compliance and ICS frameworks are fully digitized, reducing manual effort.
- HSE processes are simplified and transparent, empowering employees and managers with real-time insights and faster approvals.
By implementing a unified platform, NEQSOL Holding has not only improved daily operations but also ensured alignment with both regulatory requirements and internal governance standards. The solution has significantly enhanced transparency, governance, and efficiency across all relevant areas.
---
### [Integrated risk, compliance and security management with the GRC Toolbox](https://swissgrc.com/fr/success_story/postfinance/)
**Published:** décembre 28, 2023
**Author:** Shayeste Afzaly
**Excerpt:** PostFinance is one of the largest financial institutions in Switzerland and offers a wide range of banking services.
**Content:**
#### Find out how PostFinance uses our solutions successfully.
With the GRC Toolbox from Swiss GRC, PostFinance has implemented a [central solution](https://swissgrc.com/fr/solutions/) that makes it possible to fulfill external and internal requirements in the areas of risk management, internal control system (ICS), business continuity management (BCM), information security management (ISMS), data protection and contract management in a transparent, pragmatic and sustainable manner.
A key advantage of this solution is its high level of acceptance among users. The system offers user-friendly access to relevant information, automatically reminds users when tasks are due and ensures an appropriate escalation procedure. The implementation of workflows has made it possible to establish uniform and comprehensible GRC processes for all those responsible.
Another success factor is the consistent decentralized approach, which has firmly anchored the solution in the various areas of the company. The company originally began using three or four GRC Toolbox apps, but ten are now in use. This underlines the user-friendliness and success of Swiss GRC’s GRC approach.
## Takeaways
- PostFinance was looking for a modern GRC solution and found the best option in the GRC Toolbox from Swiss GRC.
- The GRC Toolbox enabled PostFinance to efficiently meet the requirements in various business areas, with a particular focus on risk management and compliance.
- The user-friendliness of the GRC Toolbox led to a high level of acceptance among users, who benefited from automatic reminders and easy access to relevant information.
- Standardized and understandable GRC processes were successfully implemented.
- The integrated approach has led to the solution being used successfully in various areas of the company.
---
### [Paul Scherrer Institute (PSI) strengthens Risk and Control Management with Swiss GRC](https://swissgrc.com/fr/success_story/paul-scherrer-institute-psi-strengthens-risk-and-control-management-with-swiss-grc/)
**Published:** octobre 17, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** With around 2,300 employees and an annual budget of CHF 460 million, the Paul Scherrer Institute (PSI) is Switzerland’s largest research institute for natural and engineering sciences. It hosts the country’s major large-scale research facilities and, as part of the ETH Domain, forms a key pillar of the Swiss research landscape. PSI conducts cutting-edge research in future technologies, energy and climate, health innovation, and the fundamental principles of nature.
**Content:**
#### Discover how the Paul Scherrer Institute (PSI) has digitalized, structured, and future-proofed its risk and internal control processes through the use of Swiss GRC’s GRC Toolbox — seamlessly integrated with existing systems and designed to enable consolidated reporting.
## Initial situation
As a national research center of international standing, the [Paul Scherrer Institute (PSI)](https://www.psi.ch/de) is part of the ETH Domain under the supervision of the Swiss Confederation. In this role, the Institute bears responsibility not only for scientific excellence but also for ensuring safe, compliant, and transparent governance.
Before the project began, [risk management](https://swissgrc.com/fr/risk-management-software/ "Risk Management Software") and [internal control](https://swissgrc.com/fr/internal-control-software-ics/ "Internal Control Software / ICS") activities were largely manual — decentralized spreadsheets and multiple data silos characterized the landscape. The desire for a structured and auditable solution grew steadily within the compliance function. Additionally, the opportunity to leverage synergies with other institutions within the ETH Domain — some of which were already using Swiss GRC solutions — played a role in PSI’s decision to evaluate Swiss GRC.
## Objectives
PSI set out to establish a digitalized and structured representation of its internal risk management, compliance, and control processes with the following goals:
- Clearly define responsibilities,
- Enable centralized evaluation and analysis,
- Facilitate joint reporting structures with partner institutions within the ETH Domain.
## Implementation and collaboration
At the outset, PSI considered joining an existing GRC Toolbox instance already in use by another ETH Domain institution. However, a joint analysis soon revealed that this approach would involve too many limitations and too little flexibility. In close coordination, it was therefore decided to establish a dedicated instance for PSI, tailored to the specific needs of the Institute.
Today, PSI actively uses the modules for **Risk Management (RM), Internal Control System (ICS), Compliance**, and **IT Security Management**. Three of the four modules include targeted customer-specific extensions beyond the standard version. A key element was the technical integration with **SAP Signavio**, particularly within the ICS module, to leverage synergies between existing process management and the internal control system — thereby avoiding duplicate documentation.
While the implementation of this interface proved more complex than initially anticipated, it was successfully realized through phased deployment and direct, solution-oriented coordination among all stakeholders — professionally guided by **Michael Niedermann**, Lead Consulting Europe at Swiss GRC.
## Challenges and lessons learned
**Challenge****Solution Approach**Desire to use an existing instance from another ETH Domain institutionAnalysis revealed limitations → decision to implement a dedicated PSI instanceComplexity of SAP Signavio integrationClose technical coordination and phased implementationNeed for targeted module extensionsFlexible customization at module level## Key results and added value
With the GRC Toolbox from Swiss GRC, PSI today benefits from:
- A unified platform for risk management, ICS, and compliance,
- Standardized processes with clearly defined responsibilities,
- Seamless technical integration with existing systems, particularly SAP Signavio,
- A solid foundation for internal reporting and future comparability within the ETH Domain.
The solution has significantly enhanced transparency, governance, and efficiency across all relevant areas.
## Conclusion
By implementing the GRC Toolbox from Swiss GRC, PSI has laid the foundation for a professional and scalable governance system. The decisive factors for this choice included Swiss GRC’s proven expertise in the public sector and academic environment, the modular architecture allowing for phased implementation, and the company’s strong consulting and implementation capabilities.
The solution supports PSI not only in maintaining internal standards but also in sustainably strengthening institutional resilience — within an organization that combines scientific excellence with a strong commitment to transparent and reliable governance.
---
### [Information security with a system: Helvetia’s journey to an ISMS at scale](https://swissgrc.com/fr/success_story/information-security-with-a-system-helvetias-journey-to-an-isms-at-scale/)
**Published:** octobre 2, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Helvetia is a leading Swiss insurance group headquartered in St. Gallen. With around 14,400 employees, the company operates in multiple European markets as well as select international locations. Across its three business segments – non-life, life, and asset management – Helvetia ranks among the largest and most internationally active insurers in Switzerland.
**Content:**
#### Discover how Helvetia, in close partnership with Swiss GRC, established a group-wide Information Security Management System (ISMS) that not only ensures regulatory compliance, but also delivers transparency, efficiency, and sustainable governance across the organization.
## Background and objectives
With approximately 14,400 employees worldwide, [Helvetia](https://www.helvetia.com/) is one of Switzerland’s largest and most internationally active insurance groups. Headquartered in St. Gallen, the company operates in Switzerland, Germany, Austria, Italy, Spain, and France, as well as in select international markets such as Liechtenstein and Singapore. Helvetia is active across three business segments – **non-life, life, and asset management** – making it one of the most broadly diversified players in the Swiss insurance market.
Few organizations have advanced as far as Helvetia in the area of information security. By implementing a decentralized [ISMS](https://swissgrc.com/fr/information-security-management-isms-software/) that spans multiple business lines and international locations, Helvetia has set a benchmark for the industry. To realize this ambitious objective, Helvetia partnered with Swiss GRC to co-design and implement one of the most mature ISMS implementations in the market – a system that combines **centralized governance with localized execution**.
The objectives were clear:
- Ensure **group-wide consistency** while allowing for local adaptability
- Compliance with **FINMA requirements** as well as **[DORA](https://swissgrc.com/fr/dora)** and **EU-GDPR**
- Align with **leading standards** such as ISO, NIST, and ISF
- Establish a **clear governance framework** with defined responsibilities across group and local levels
- Enhance **efficiency and transparency** through seamless integration and process automation
## Implementation and collaboration
In addition to the core ISMS processes, Helvetia also integrated data protection and physical security requirements into the solution. The alignment of **information security** and **data protection** represents a recurring challenge for many organizations, as responsibilities, control frameworks, and regulatory requirements are often managed in silos. By embedding these domains into a unified system, Helvetia was able to streamline complexity, eliminate redundancies, and establish clear lines of accountability.
At the core of the solution is an **asset-centric data model**, capturing applications, IT services, platforms, and business processes. All changes, risks, and exceptions are linked directly to these assets, providing a flexible and scalable structure.
A hallmark of the program was its **deep integration with existing systems**, including:
- LeanIX and ServiceNow for architecture and configuration data
- Jira and Tempus for project and change management with embedded security approvals
- SAP Ariba for supplier management and annual security assessments
- Splunk for vulnerability and exception processes
The ISMS is operated in a **dedicated Azure cloud instance** managed by Swiss GRC. All data resides in Europe and is encrypted with Helvetia’s own keys – a decisive factor for compliance with Swiss data protection laws and the safeguarding of sensitive information.
## Project challenges and solutions
**Challenge**Solution approachComplex group structure with international subsidiariesEstablishment of a governance framework with a Group Security Officer, Chief Security Officer, and local ISOsDiverse regulatory environmentsAlignment with DORA, GDPR, and international standards (ISO, NIST, ISF), adapted locallyHeterogeneous system landscapeDevelopment of an asset-centric data model and integration of tools (LeanIX, ServiceNow, Jira, Ariba, Splunk)Time-critical implementationInterdisciplinary collaboration, pragmatic workshops, and close partnership with Swiss GRCBalancing central governance with local responsibilityCombination of group-wide standardization and local execution through national ISOs## Key outcomes and benefits
By leveraging the GRC Toolbox, Helvetia has established a **group-wide ISMS** that today serves as a central management instrument – far exceeding the boundaries of pure compliance.
The key benefits include:
- **Compliance by Design**: Regulatory requirements and standards systematically integrated
- **Operational Efficiency**: Automated workflows and system interfaces reduce manual effort
- **Transparency**: Dashboards and reports provide clear insights for management and business units
- **Future-Readiness**: Continuous development with automated controls and integration of cloud security data
The ISMS has become not only a compliance mechanism but a **strategic enabler of security, resilience, and sustainable corporate governance**.
---
### [Swiss Post turns Excel chaos into streamlined GRC operations with Swiss GRC](https://swissgrc.com/fr/success_story/swiss-post-achieves-grc-clarity-with-swiss-grc/)
**Published:** août 14, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss Post is one of Switzerland's most important companies and fulfills a public service mandate in the areas of logistics, communication, and finance. As a conglomerate with over 45,000 employees, it combines economic performance with social responsibility and stands for a secure, modern, and reliable infrastructure serving the population and the economy.
**Content:**
#### Discover how Swiss Post modernized its GRC processes, moving from manual Excel spreadsheets to an intuitive, digital system with the help of Swiss GRC.
## Initial situation
When Swiss Post’s previous [Enterprise Risk Management (ERM)](https://swissgrc.com/fr/risk-management-software/ "Risk Management Software") solution was discontinued in 2020, the company temporarily managed risks without dedicated tool support, relying instead on Excel spreadsheets and PowerPoint reports. This quickly proved inefficient and error-prone. A modern, robust, and user-friendly GRC solution became essential.
## Objectives
As a systemically important company with a public mandate, [Swiss Post](https://www.post.ch/en) is subject to strict requirements in the area of [Governance, Risk, and Compliance (GRC)](https://swissgrc.com/fr/solutions/ "Solutions"). In addition to legal regulations such as the Swiss Code of Obligations and the Postal Organization Act, the company’s management is overseen by the Federal Department of the Environment, Transport, Energy and Communications (DETEC), the Postal Regulatory Commission (PostCom), and the Swiss Federal Audit Office (SFAO). The system to be implemented had to fully meet these requirements while being sufficiently flexible to accommodate future regulatory or operational changes.
The goal was to find an intuitive, user-friendly, and easily adaptable platform that could reliably meet all existing needs from the applied risk management and internal control system (ICS) methodology. During the development process, care was taken to avoid unnecessary complexity and to design a solution that could be seamlessly integrated into the existing corporate structure. Furthermore, the solution needed to be scalable to meet future requirements.
## Approach and collaboration
Swiss Post began by defining and prioritizing its requirements, then conducting a structured evaluation across multiple providers. Swiss GRC, already known for its work with PostFinance, stood out with a concept that combined strong functionality, flexibility, user-friendliness, and an attractive price-performance ratio.
Swiss Post awarded the contract to Swiss GRC, initially implementing the ERM and [ICS modules](https://swissgrc.com/fr/internal-control-software-ics/ "Internal Control Software / ICS"). Implementation followed a hybrid approach, combining classic project structures with agile, practice-oriented working phases. On the Swiss GRC side, Gentian Ajeti (Head Consulting) and his team coordinated closely with Swiss Post’s corporate risk management function. Thanks to the platform’s intuitive usability, Swiss Post could actively participate and operate independently throughout the rollout.
The success of the first two modules sparked strong interest across the organization, leading to the phased introduction of additional modules, including:
- Information Security
- Supplier Security Management (Third-Party Risk Management)
- Compliance
- Data Protection
- Physical Security
- Audit Management
## Project challenges
****Challenge********Solution Approach****Complex corporate structure with various business units, group companies, and around 45,000 employeesStep-by-step implementation, close coordination and involvement of departments, targeted prioritizationHeterogeneous requirements and high maturity of the topicsJoint business analysis, agile approach, modular implementation, individual configurationNeed for broad coverage of assurance functionsPlatform-based solution approach with high scalability and flexibility## Key results and impact
With the introduction of the [GRC Toolbox](https://swissgrc.com/fr/solutions/ "Solutions"), Swiss Post was able to establish a central GRC platform that provides significant added value to the various assurance functions. The modular architecture enables a precise mapping of individual, subject-specific requirements and seamless integration of the solution into the complex corporate structure. Processes are documented transparently and traceably, and responsibilities are clearly assigned. In this way, the GRC toolbox makes a significant contribution to enabling Swiss Post’s assurance functions to perform their tasks efficiently, effectively, and transparently.
In the long-standing collaboration, Swiss GRC is perceived not merely as a software provider, but as a reliable and committed partner. What particularly distinguishes the cooperation with Swiss GRC is not only the technical support, but also the active enablement of Swiss Post to work independently with the GRC toolbox and even further develop it themselves. Thanks to its intuitive usability, minor adjustments and enhancements can be made in-house, without long development cycles or external dependencies.
---
### [ewl successfully streamlines GRC processes with Swiss GRC](https://swissgrc.com/fr/success_story/ewl-creates-clear-structures-for-grc-processes-with-swiss-grc/)
**Published:** août 6, 2025
**Author:** Yahya Mohamed Mao
**Excerpt:** As Lucerne’s energy and water service provider, ewl supplies the region with electricity, water, gas, heat, and telecommunications—reliably and sustainably. With around 400 employees, ewl ensures a secure energy future and is actively committed to renewable energy and innovative energy solutions.
**Content:**
#### Discover how ewl energie wasser luzern restructured and digitalized its risk management, internal control system (ICS), data protection, and IT security—and the tangible benefits the GRC Toolbox delivers in day-to-day operations and regulatory compliance.
## Initial situation
Until recently, [ewl Energie Wasser Luzern](https://www.ewl-luzern.ch/) relied on Microsoft Excel and Atlassian Jira for key areas of corporate governance such as risk management, internal control system (ICS), IT security management, and data protection. The limited automation capabilities—especially in Excel—resulted in high manual effort, increased risk of errors, and a lack of integration between departments.
Given the company’s diverse business areas and the constantly evolving market and regulatory landscape, integrated corporate risk management had become increasingly complex. This demanded continuous risk monitoring, effective implementation of protective measures, and strict adherence to data protection and security requirements.
In light of rising cyber threats, ewl placed particular emphasis on continuously enhancing the protection of sensitive data and identifying and implementing new security measures at an early stage.
## Objectives
The goal was to implement the GRC Toolbox as a central, [integrated solution for risk management](https://swissgrc.com/fr/risk-management-software/ "Risk Management Software"), [ICS](https://swissgrc.com/fr/internal-control-software-ics/ "Internal Control Software / ICS"), [data protection](https://swissgrc.com/fr/data-protection-management-software/ "Data Protection Management Software"), and [IT security](https://swissgrc.com/fr/information-security-management-isms-software/ "Information Security Management / ISMS-Software"). Standardized, software-supported processes were expected to streamline the management of measures and controls. At the same time, Excel-based solutions were to be replaced, an information security management system (ISMS) in line with the Swiss ICT minimum standard established, and a business continuity management (BCM) system—including an IT emergency plan—introduced. Further objectives included significantly improving the efficiency of audits and reviews, reducing manual workloads, minimizing sources of error, and enabling transparent reporting on GRC activities—always with the aim of ensuring compliance with applicable standards and regulations.
## Approach and collaboration
The decision in favor of the GRC Toolbox was driven by its user-friendliness, clear structure, and intuitive interface. A decisive factor was the ability to independently adapt and configure reports, input forms, and action plans, while managing multiple GRC areas centrally in one platform.
The implemented modules include **Risk Management (RM), Internal Control System (ICS), Business Continuity Management (BCM), Information Security Management System (ISMS), and Data Protection**. Together, they form an integrated system for identifying, assessing, and managing risks, ensuring effective controls, and meeting regulatory requirements in both information security and data protection.
In collaboration with Swiss GRC’s consulting team—particularly Senior GRC Consultant **Daniele Fiasco**—ewl experienced a high level of expertise, reliability, and mutual trust. This strong foundation played a decisive role in the project’s success.
## Project challenges
Despite an ambitious schedule, the project was completed successfully and on time. Cooperation between the ewl and Swiss GRC teams was seamless and solution-focused throughout.
Close coordination and the implementation partner’s in-depth expertise made it possible to address specific requirements—such as customized report templates—flexibly and efficiently. Even for complex issues, practical solutions were found quickly, without any friction or delays.
## Key results and impact
With the introduction of the GRC Toolbox, ewl fundamentally transformed its company-wide approach to governance, risk, and compliance. For the first time, previously separate areas such as ICS, risk management, data protection, information security, and business continuity management were consolidated into a single, centralized solution.
The results: clearly structured processes, standardized workflows, and significantly reduced operational effort. What was once characterized by manual work and siloed applications is now fully digitalized, transparent, and easy to manage.
The new solution enables systematic implementation of regulatory and internal standards, early identification of risks, and targeted responses to developments—especially in security-critical areas such as protecting sensitive data.
A key success factor was partnering with a regional provider. As a Lucerne-based company, Swiss GRC not only delivered a powerful technology solution but also impressed with its local presence, strong consulting expertise, and deep understanding of ewl’s challenges. This combination of local roots and professional excellence greatly contributed to the successful implementation and strengthened trust in the solution.
---
### [Swiss GRC technology for modern risk and control management at Mobiliar](https://swissgrc.com/fr/success_story/mobiliar/)
**Published:** août 19, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Mobiliar occupies a leading position in the Swiss market and is one of the largest property insurers in Switzerland.
**Content:**
#### Find out how the introduction of the GRC Toolbox ensured Mobiliar’s ability to adapt to regulatory changes.
## Initial situation
[Mobiliar](http://www.mobiliar.ch/) occupies a leading position in the Swiss market and, with a premium volume of over CHF 4.5 billion and more than 2.3 million insured persons, is one of the largest non-life insurers in Switzerland. It is known for its deep roots and strong local connections with its 80 general agencies in Switzerland and Liechtenstein. The digital transformation and changing regulatory requirements also pose new challenges for Mobiliar.
## Challenge: Adapting to management and regulatory requirements
Mobiliar had been using a GRC tool to manage its governance, risk and compliance activities for over a decade. The new requirements of management and the supervisory authorities could no longer be fully covered by the existing solution. These included, in particular, the need to be able to efficiently carry out risk and control assessments centrally and decentrally. In addition, increased support for control monitoring was required in order to ensure more efficient and improved risk management. Another point was the need for a user-friendly, flexible and reliable reporting system that would increase the transparency and traceability of the risk and control situation. These extensive requirements made it clear that a modern and future-oriented solution was necessary in order to effectively manage the existing and future challenges. For this reason, the options for introducing a new GRC tool were examined in detail and Swiss GRC was chosen.
## Swiss GRC as the key to advanced ICS and risk management
Swiss GRC, known for its high-quality GRC tools, offered what Mobiliar was looking for to effectively address its [internal control system (ICS)](https://swissgrc.com/fr/internal-control-software-ics/) and [risk management](https://swissgrc.com/fr/risk-management-software/) challenges. Swiss GRC’s solution stood out in particular for the following:
- Support for a risk & control assessment methodology that enables efficient identification, self-assessment and monitoring of material risks and key controls.
- A user-friendly interface and flexible reporting that simplifies the handling and analysis of risk data and thus contributes to improved decision-making.
- Audit- and regulatory-compliant functionalities that ensure that the company always meets the latest (regulatory) legal requirements.
- Cloud-based operation that ensures high scalability and adaptability to changing business needs.
- Stable performance that guarantees efficient and smooth use of the system.
With the GRC Toolbox, Mobiliar can make its risk and control assessments more efficient and tailor them to current requirements. In addition, the introduction has led to improved control monitoring. Another positive effect is the greater involvement and motivation of employees, which is facilitated by the tool’s user-friendly interfaces. The tool also increases transparency in reporting, allowing decision-makers to access a consistent and uniform database. Last but not least, the GRC Toolbox supports the company’s ability to adapt to future regulatory changes, which promotes sustainable risk management.
## Takeaways
- **Improved processes:** Swiss GRC’s solution enables more efficient risk and control assessments as well as improved control monitoring.
- **User-friendliness:** The implementation of a user-friendly interface promotes employee involvement and satisfaction.
- **Future-proofing:** The tool provides a solid foundation for adapting to future regulatory changes and challenges.
- **Increased transparency and compliance:** The GRC Toolbox not only improves transparency in reporting, but also strengthens compliance and risk management overall.
---
### [Baloise optimizes ISMS and IT risk management with Swiss GRC](https://swissgrc.com/fr/success_story/baloise-optimizes-isms-and-it-risk-management-with-swiss-grc/)
**Published:** octobre 7, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Baloise is a leading Swiss all-lines insurer offering comprehensive insurance solutions and services for private individuals and companies.
**Content:**
#### Find out how the Baloise Group was able to successfully harmonize its security standards by introducing the ISMS solution from Swiss GRC throughout the Group – across countries and across the board.
## Initial situation
The [Baloise Group](https://www.baloise.com/), headquartered in Basel, is one of the leading insurance and pension providers in Europe. With around 8,000 employees in several countries (Switzerland, Germany, Belgium, Luxembourg and Liechtenstein), a uniform yet flexible solution was required to meet the increasing regulatory requirements, such as DORA, across all countries and to harmonize internal processes at the same time.
## Objectives: Standardization and automation of ISMS processes
The main challenge was to find an [ISMS solution](https://swissgrc.com/fr/information-security-management-isms-software/ "Information Security Management / ISMS-Software") that would meet the diverse requirements of the individual countries as well as Baloise’s internal standards and processes. Flexible adaptation to local requirements was necessary without jeopardizing the overarching standardization of information security processes. In addition, the various needs and priorities of the stakeholders in the different national companies had to be taken into account.
The ISMS implementation focused on the following processes:
- **Asset management**: determining protection requirements, defining and reviewing security requirements (target/actual comparison)
- **Exception management**
- **IT risk management**
- **Policy framework**
The focus was not only on digitizing these processes, but above all on automating them and making them dynamic. This made it easier for users to work more efficiently, while at the same time significantly increasing acceptance of the solution within the company.
## Evaluation process and decision-making
The evaluation process was carried out carefully and comprehensively. Swiss GRC prevailed against strong competitors by not only relying on its extensive references and proven methods, but also by demonstrating clear added value and synergy effects between the various functions of the insurance group. The convincing overall offer, which included both technical capabilities and comprehensive expertise, led to the final decision in favor of Swiss GRC. Swiss GRC’s solution stood out in particular:
- **Adaptability and seamless integration:** Swiss GRC’s ISMS solution is extremely flexible and can adapt to the different requirements of each country and the Baloise Group’s internal processes, while at the same time integrating seamlessly with existing systems.
- **Modular approach:** The modular structure meant that the Baloise Group could rely on a solution that was tailored to its requirements and could easily be expanded in the future.
- **Transparent pricing:** Swiss GRC impressed with its simple pricing, which enabled clear calculations and budgeting, thus ensuring planning security.
- **Proven experience:** Swiss GRC could look back on many years of experience and successful projects in the insurance industry, which gave the Baloise Group additional confidence in the reliability and effectiveness of the ISMS solution.
## Key Results and Takeaways
- **Efficient harmonization:** Swiss GRC enabled efficient standardization and harmonization of ISMS processes across all national companies.
- **Compliance with regulatory requirements:** The solution fulfills the specific legal requirements in each country without affecting Baloise’s internal processes.
- **Modularity for future expansions:** The modularity of the GRC Toolbox allows future expansions to be easily integrated. Based on the positive experience of the ISMS implementation, it was therefore also quickly decided to use the data protection module in the GRC Toolbox in order to be able to exploit further synergy effects across departmental boundaries.
- **Trustworthy partner:** Swiss GRC has proven to be a long-term and trustworthy partner that consistently supports and promotes Baloise’s information security goals.
---
### [Canton-wide and transparent internal control system (ICS) in the Canton of Uri](https://swissgrc.com/fr/success_story/canton-wide-and-transparent-internal-control-system-ics-in-the-canton-of-uri/)
**Published:** septembre 26, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** As one of the oldest cantons in Switzerland, the canton of Uri has a well-organized administrative structure. With several directorates and specialized departments, it is responsible for a wide range of public tasks and services.
**Content:**
#### Find out how Swiss GRC supported the Canton of Uri in establishing a canton-wide and transparent Internal Control System (ICS) and also integrating important insurance and claims management activities.
## Initial situation
The [Canton of Uri](https://www.ur.ch/), a historically important canton in Switzerland, faces specific challenges as a public sector. Public administrations are increasingly required to ensure transparency, accountability and efficiency in their processes in order to meet the increasing expectations of citizens, authorities and supervisory bodies. In the area of risk management and internal control in particular, the Finance Directorate of the Canton of Uri saw the need to modernize its working methods and introduce a future-proof, flexible system that meets the complex requirements of the public sector.
## Challenge: Meeting the high demands of the public sector
As a public institution, the Canton of Uri has particularly high demands on a governance, risk and compliance (GRC) tool. The system had to meet the extensive requirements for transparency and accountability, while at the same time being efficient and easy to use for employees. Added to this were the complex legal regulations and the need for a solution that serves both the [internal control systems (ICS)](https://swissgrc.com/fr/internal-control-software-ics/ "Internal Control Software / ICS") and risk management. Another key criterion was the ability to integrate the tool seamlessly into existing public administration structures.
## Swiss GRC as an ideal solution for the public sector
After a comprehensive analysis, the Canton of Uri chose the GRC Toolbox from Swiss GRC. This solution met the requirements of the Canton of Uri and offered an optimal balance between user-friendliness, flexibility and legal compliance. Particularly convincing was the ability of the GRC Toolbox to meet the specific requirements of the public sector, including:
- **High transparency:** The GRC Toolbox enables clear traceability of all risk management and control processes, which is crucial for the public sector.
- **Efficient adaptation to legal requirements:** The GRC Toolbox ensures that the Canton of Uri always meets the latest regulatory requirements, which is essential for a public institution.
- **Seamless integration:** The GRC Toolbox can be easily integrated into the existing structures of the cantonal administration and thus supports smooth operations.
- **Flexibility and scalability:** The GRC Toolbox impresses with its flexibility to adapt to the changing needs of the public sector and to scale the processes as required. This has enabled more and more use cases to be integrated over time.
Since the introduction of the GRC Toolbox, the Canton of Uri has made significant progress in risk management and internal control. The GRC Toolbox has significantly improved decision-making processes through increased transparency, allowing the administration to provide detailed reports on risks and controls. By automating risk and control assessments, manual workflows have been significantly reduced, resulting in more efficient use of resources. The GRC Toolbox also supports compliance with legal requirements and offers the flexibility to respond quickly to future changes in the regulatory environment. The software’s user-friendly interface has also increased employee engagement in dealing with risks and controls, which has further improved compliance.
## Takeaways
- **Suitable solution for the public sector:** The GRC Toolbox from Swiss GRC is prepared for the complex requirements of the public sector and offers a comprehensive solution for risk management and internal control.
- **Transparency and accountability:** The solution increases transparency and strengthens accountability to taxpayers, which is crucial for public institutions.
- **Future-proof and scalable:** Thanks to the flexibility and scalability of the solution, the canton of Uri is well equipped to respond to future challenges in the public sector. For example, insurance and claims management have also been integrated.
- **Smooth integration:** Seamless integration into existing administrative structures ensures efficient and uninterrupted operation.
---
### [Opportunity and risk management of the City of Zurich with the GRC Toolbox](https://swissgrc.com/fr/success_story/opportunity-and-risk-management-of-the-city-of-zurich-with-the-grc-toolbox/)
**Published:** février 12, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** As the largest city in Switzerland, Zurich's city administration has a comprehensive structure. With 70 service divisions and nine departments, it is responsible for a wide range of municipal tasks.
**Content:**
#### Find out how the City of Zurich successfully masters the balancing act of dealing with opportunities and risk with ou solutions.
## Initial situation
With its extensive structure of 70 service divisions, nine departments, 30,000 employees and a budget of over CHF 10 billion, the [City of Zurich](https://www.stadt-zuerich.ch/portal/en/index.html) is exposed to a wide range of risks. In 2007, the City Council decided to introduce a new risk and insurance regulation instead of the previous insurance solution, which provides for risks to be increasingly borne by the city itself rather than insured. In view of these dimensions, effective risk and control mechanisms are of crucial importance. However, Zurich is taking an innovative approach by actively addressing not only risks but also opportunities.
## Challenge and solution approach
The City of Zurich was faced with the challenge of implementing effective risk and control management mechanisms to cope with the complex requirements of a city administration of this size. To meet this need, the city was looking for a comprehensive approach that could efficiently integrate opportunity and [risk management (RM)](https://swissgrc.com/fr/risk-management-software/) and the [internal control system (ICS)](https://swissgrc.com/fr/internal-control-software-ics/). To meet this need, it opted for Swiss GRC and its GRC Toolbox, which makes it possible to combine both RM and ICS in a single tool. By integrating these two key functions, all relevant processes and data can be seamlessly merged and managed.
## Continuous risk reporting up to the city council
The GRC Toolbox offers a variety of functions specifically tailored to the needs of organizations that have complex risk and control requirements. With a user-friendly interface and powerful analysis tools, the GRC Toolbox enables the City of Zurich to precisely identify, assess and prioritize risks. In addition, the software provides a clear and transparent process for risk reporting up to the City Council. This ensures comprehensive and timely communication about risks and enables decision-makers to make informed decisions.
## A solid basis for comprehensive risk control
For the City of Zurich, the introduction of Swiss GRC technology has strengthened its risk management capabilities and created a robust foundation for comprehensive risk management. The precise identification, assessment and management of risks has not only helped to mitigate potential threats, but has also improved the ability to identify and exploit opportunities. Transparent reporting has improved decision-making in the city administration and increased stakeholder confidence in the integrity and transparency of administrative processes. The City of Zurich can now respond proactively to new risks and opportunities and further strengthen its position as one of Switzerland’s leading cities.
## Takeaways
- Swiss GRC and its GRC Toolbox enable the City of Zurich to efficiently integrate opportunity and risk management and the internal control system in one tool.
- The GRC Toolbox offers user-friendly functions for precise risk reporting, which leads to well-founded decisions at city council level.
- The implementation of Swiss GRC technology strengthens the City of Zurich’s risk management capabilities and creates a solid basis for comprehensive risk management.
- Transparent risk reporting improves decision-making and strengthens stakeholder confidence in the administration.
- Swiss GRC technology provides a flexible basis for adapting to changing risks and opportunities and strengthening the City of Zurich’s position as a leading Swiss city.
---
### [Swiss GRC strengthens Thurgauer Kantonalbank’s Risk Management and Operational Resilience](https://swissgrc.com/fr/success_story/swiss-grc-strengthens-thurgauer-kantonalbanks-risk-management-and-operational-resilience/)
**Published:** septembre 19, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Thurgauer Kantonalbank is the leading universal bank in the canton of Thurgau. As a regionally anchored cantonal bank, it makes a significant contribution to economic development and financial stability in the canton. Thurgauer Kantonalbank is one of the twenty largest banks in Switzerland. TKB is a public-law bank with a state guarantee.
**Content:**
#### Find out how Thurgauer Kantonalbank implemented the GRC Toolbox to strengthen its risk management, compliance and operational resilience.
## Initial situation
[Thurgauer Kantonalbank (TKB)](https://www.tkb.ch/private) is an essential part of the financial system in the canton of Thurgau and plays a central role in the regional economy. As a cantonal bank, TKB bears a special responsibility, both to its customers and to the canton, which guarantees its stability. In this role, the bank must meet the highest standards in terms of risk management and compliance in order to maintain financial security and operational resilience. In view of the increasing regulatory requirements and the complexity of modern banking, it has become increasingly difficult to make the previous manual processes efficient while ensuring the necessary transparency and accountability.
## Challenge: Meeting the increasing requirements of regulators and operational resilience
TKB faces the challenge of meeting the complex requirements of regulators while maintaining strong risk management and a resilient operational structure. To manage the growing complexity, particularly in relation to transparency, accountability and operational resilience requirements, a solution had to be found that integrates all aspects of [risk management](https://swissgrc.com/fr/risk-management-software/) and compliance, strengthening operational resilience while improving efficiency.
## Swiss GRC impresses with deep integration and simplicity
After a comprehensive review of the GRC solutions available, Thurgauer Kantonalbank opted for the GRC Toolbox from Swiss GRC. The solution impressed with its comprehensive integration and simplicity, as well as its ability to meet the bank’s specific requirements. The key benefits included:
- **Integration of multiple modules:** The GRC Toolbox enabled TKB to manage risk management, outsourcing management, contract management, information security, business continuity management, internal controls and compliance in a single system, resulting in a significant improvement in process overview and control.
- **Strengthening operational resilience:** The platform helped the bank to improve its operational resilience by identifying risks early and implementing robust control mechanisms.
- **Efficiency and automation:** By automating risk and control assessments, the bank was able to significantly reduce the manual workload, use resources more efficiently and, above all, meet the many regulatory documentation requirements.
- **Transparent reporting:** The GRC toolbox enabled detailed and transparent reporting, which facilitated both internal decision-making and compliance with regulatory requirements.
Since the comprehensive implementation of the entire GRC toolbox, Thurgauer Kantonalbank has made significant progress in several areas. The full implementation of this solution, which covers various modules of risk management, [internal controls](https://swissgrc.com/fr/internal-control-software-ics/) and compliance, was a significant project for the bank.
Thanks to improved transparency and accountability, the bank can now provide comprehensive reports on its risks and control mechanisms, which has made it much easier to meet its accountability obligations to supervisory authorities and stakeholders. The automation of risk and control processes has led to a reduction in manual activities, particularly in monitoring, which has improved the efficiency of resource use and optimized workflows.
TKB’s operational resilience has also been strengthened, as the bank has a transparent and rapid overview of risks, BCM, information security and the associated controls per business process and/or function of the bank and can react quickly to operational risks. This is particularly important for a bank with regional responsibility. In addition, the GRC Toolbox enables TKB to reliably fulfill all regulatory requirements and to react flexibly to changes in the regulatory environment. The successful implementation of the entire solution underlines the long-standing cooperation between Thurgauer Kantonalbank and Swiss GRC and demonstrates the importance of a comprehensive and integrated solution for an institution of this size.
## Takeaways
- **Integrated solution:** Thurgauer Kantonalbank benefits from the comprehensively integrated GRC toolbox, which combines governance, risk management and compliance in one system.
- **Efficiency and resilience:** Automated processes have increased efficiency and at the same time strengthened the bank’s operational resilience.
- **Transparency and compliance:** The GRC Toolbox ensures increased transparency in reporting and strengthens the bank’s regulatory compliance.
---
## Jobs
### [Unsolicited application](https://swissgrc.com/fr/job/unsolicited-application/)
**Published:** octobre 10, 2023
**Author:** superadmin
**Excerpt:** At Swiss GRC, we are always on the lookout for talented individuals.
If you cannot find a suitable job listing on our website but believe your qualifications could be an asset, please feel free to apply to us proactively.
**Content:**
At Swiss GRC, we are always on the lookout for talented individuals.
If you cannot find a suitable job listing on our website but believe your qualifications could be an asset, please feel free to reach out to us with your unsolicitied application. We offer an engaging and dynamic work environment with exciting insights into topics related to [governance, risk, and compliance](https://www.handelszeitung.ch/insurance/governance-risk-und-compliance-werden-noch-immer-reaktiv-betrieben-540959).
We look forward to receiving your comprehensive application with a cover letter via email at [hr@swissgrc.com](mailto:office@swissgrc.com).
### Why Swiss GRC?
Swiss GRC AG is the leading software company in Switzerland for the development and implementation of GRC solutions. Our GRC Toolbox is the result of over 30 years of experience and our performance promise to help our customers achieve more transparency and control in the area of governance, risk and compliance with a comprehensive approach. True to our credo « where Governance, Risk & Compliance meet for success », we enable them to digitalise their GRC processes end-to-end so that they have an integrated, easy-to-use and flexible software solution.
---
## Events
### [#RISK GCC 2023, 2 - 3 October 2023](https://swissgrc.com/fr/event/risk-gcc-2023-2-3-october-2023/)
**Published:** octobre 2, 2023
**Author:** Yahya Mohamed Mao
**Excerpt:** A first of its kind for the region, the #RISK GCC conference will bring together data protection and security compliance professionals from around the region to share knowledge, enhance learning and promote innovation. Swiss GRC is delighted to sponsor this event, produced by GRC World Forums in partnership with Dubai International Financial Centre (DIFC) and the Ministry for AI.
---
### [#RISK London 2023, 18 - 19 October 2023](https://swissgrc.com/fr/event/risk-london-2023-18-19-october-2023/)
**Published:** octobre 18, 2023
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC will be exhibiting at #RISK London 2023, Europe’s leading expo on governance, risk, compliance, ESG and workplace culture, on 18 and 19 October 2023 at ExCel London. Speak to us about how our solutions empower organizations to masterfully navigate governance, risk, and compliance (GRC).
---
### [World CyberCon 2023 India](https://swissgrc.com/fr/event/world-cybercon-2023-india/)
**Published:** décembre 1, 2023
**Author:** Yahya Mohamed Mao
**Excerpt:** World CyberCon 2023 India serves as a unique occasion for world leaders and government officials to converge, share their perspectives, and impart expert knowledge in the realm of cybersecurity. Swiss GRC is delighted to announce its Silver Sponsorship.
---
### [G[P]RC Summit Riyadh, 24-25 January 2024](https://swissgrc.com/fr/event/gprc-summit-riyadh-24-25-january-2024/)
**Published:** janvier 24, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC is sponsoring the G[P]RC Summit 2024, covering an important event in the MEA/APAC region taking place in Riyadh, KSA. This is in line with the strategic growth of Swiss GRC. Visit our booth and talk to our experts, including General Manager MEA/APAC Rajeev Dutt and Head of Product & Business Development Nikolai Tsenov.
---
### [G[P]RC Summit Dubai, 29 - 30 January 2024](https://swissgrc.com/fr/event/gprc-summit-dubai-29-30-january-2024/)
**Published:** janvier 29, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC is sponsoring the G[P]RC Summit 2024, covering an important event in the MEA/APAC region taking place in Dubai, UAE. This is in line with Swiss GRC's strategic growth. Visit our booth and talk to our experts, including General Manager MEA/APAC Rajeev Dutt and Head of Product & Business Development Nikolai Tsenov.
---
### [Future IT Summit 2024](https://swissgrc.com/fr/event/future-it-summit-2024/)
**Published:** février 19, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The Future IT Summit is an event dedicated to exploring the transformative power of AI and its profound impact on our world and economy. Swiss GRC is participating in the 10th Future IT Summit in Dubai and is part of the dialogue that will shape the direction of AI's impact in the coming decade.
---
### [Risk-!n conference 6th edition, 30 – 31 May](https://swissgrc.com/fr/event/risk-n-conference-6th-edition-30-31-may/)
**Published:** mai 29, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The Risk-!n conference 6th edition will take place on 30 - 31 May in Hamburg Zurich. Risk-!n is the first independent European event aimed at risk professionals. Swiss GRC presents itself as Silver Sponsor while Rajeev Dutt, General Manager MEA & APAC will speak about resilience and BCM.
---
### [IT-GRC Congress 2024](https://swissgrc.com/fr/event/it-grc-congress-2024-hamburg/)
**Published:** mai 31, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The IT GRC Congress 2024 will take place on 3 and 4 June in Hamburg. The focus will be on current developments in the areas of information security, IT auditing, IT governance and compliance as well as risk management. Swiss GRC Germany GmbH will be exhibiting at the event.
---
### [The World CIO 200 Summit 2024](https://swissgrc.com/fr/event/the-world-cio-200-summit-2024-dubai/)
**Published:** mai 31, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The World CIO 200 Summit 2024 will take place in Dubai and Swiss GRC is one of the sponsors with Rajeev Dutt, General Manager MEA & APAC representing us. Through a series of workshops, knowledge sharing sessions, inspiring life experiences, keynote speeches, panel discussions and networking events, the Summit will explore the latest trends and innovations in IT leadership.
---
### [2024 Corporate Risk Minds](https://swissgrc.com/fr/event/2024-corporate-risk-minds/)
**Published:** mai 31, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC will play a central role as an event partner at Corporate Risk Minds 2024. The conference, which will take place on 26 and 27 June 2024 at the Maritim ProArte Hotel in Berlin, will focus this year on the crucial topic of how organisations must adapt their risk management in the face of current transformations and crises in order to remain competitive. Nikolai Tsenov, Head Product & Business Development of Swiss GRC is among the speakers and will give a presentation on NextGen GRC.
---
### [46.MEET SWISS INFOSEC!](https://swissgrc.com/fr/event/46-meet-swiss-infosec/)
**Published:** février 14, 2025
**Author:** Gent Krasniqi
**Excerpt:** MEET SWISS INFOSEC! is the leading and largest event of its kind. In the 46th edition of the popular event series, experts will present current experience and practical reports. Swiss GRC will be there as a silver sponsor on 23 September 2024. Visit us at our stand.
---
### [Integrity Europe Conference – Governance. Risk. Compliance. 7 – 8 November 2024](https://swissgrc.com/fr/event/integrity-europe-conference-governance-risk-compliance-7-8-november-2024/)
**Published:** juin 5, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** For the first time, Swiss GRC is sponsoring the Integrity Europe Conference, which was launched by the Institute of Financial Services Zug IFZ of the Lucerne School of Business. The focus is on current topics in the areas of compliance, risk management, corporate integrity, anti-corruption and responsible leadership.
---
### [MENA ICT Forum, 20. – 21. November 2024](https://swissgrc.com/fr/event/mena-ict-forum-20-21-november-2024/)
**Published:** février 14, 2025
**Author:** Gent Krasniqi
**Excerpt:** Under the patronage of King Abdullah II Bin Al Hussein, the 10th edition of the most important biennial event for the ICT industry in the Middle East and North Africa (MENA ICT Forum 2024) will take place on 20 and 21 November 2024 at the King Hussein Bin Talal Convention Center on the Dead Sea in Jordan. Swiss GRC will be a premium exhibitor together with its partner Tjdeed.
---
### [47.MEET SWISS INFOSEC!](https://swissgrc.com/fr/event/47-meet-swiss-infosec/)
**Published:** février 14, 2025
**Author:** Gent Krasniqi
**Excerpt:** MEET SWISS INFOSEC! is the leading and largest event of its kind. In the 47th edition of the popular series of events, experts will present current experience and practical reports. Swiss GRC will be there as a silver sponsor on 20 January 2025. Visit us at our stand.
---
### [G[P]RC Summit 2025 Riyadh, 19 - 20 May. January 2025](https://swissgrc.com/fr/event/gprc-summit-2025-riyadh-19-20-may-january-2025/)
**Published:** février 14, 2025
**Author:** Gent Krasniqi
**Excerpt:** Swiss GRC is underlining its ever-growing influence in the global GRC space by returning as a platinum sponsor to the prestigious G[P]RC Summit 2025. The event, which will take place in Riyadh from 19-20 January 2025 and Dubai from 22-23 January 2025, will once again bring together top GRC experts and decision-makers from around the world to discuss the latest trends and innovations in the field.
---
### [G[P]RC Summit 2025 Dubai, 22-23 January 2025](https://swissgrc.com/fr/event/gprc-summit-2025-dubai-22-23-january-2025/)
**Published:** février 14, 2025
**Author:** Gent Krasniqi
**Excerpt:** Swiss GRC is underlining its ever-growing influence in the global GRC space by returning as a platinum sponsor to the prestigious G[P]RC Summit 2025. The event, which will take place in Riyadh from 19-20 January 2025 and Dubai from 22-23 January 2025, will once again bring together top GRC experts and decision-makers from around the world to discuss the latest trends and innovations in the field.
---
### [GRC Day India 2025, 11 February 2025](https://swissgrc.com/fr/event/grc-day-india-2025-11-february-2025/)
**Published:** février 14, 2025
**Author:** Gent Krasniqi
**Excerpt:** The first GRC DAY INDIA, to be held on 11 February 2025 at The Leela, Mumbai, promises to be a premier platform for professionals and executives to explore the latest developments in Governance, Risk and Compliance (GRC). Look forward to hearing from global experts, including a session with a prominent representative from the Bombay Stock Exchange (BSE).
---
### [Maha Privacy Conference, 7 March 2025](https://swissgrc.com/fr/event/maha-privacy-conference-7-march-2025/)
**Published:** février 14, 2025
**Author:** Gent Krasniqi
**Excerpt:** Organised by DPO Club, Maha Privacy 2025 brings together experts to explore the issues of privacy, data protection and cyber security in India's digital landscape. With the Digital Personal Data Protection Act, 2023 coming into effect, the conference promotes collaboration, awareness and strengthens the rights of individuals with respect to their data. Swiss GRC is a key partner of the event.
---
### [imh Banking Congress KURS 2025 - IT in Banks, 25 - 26 March 2025](https://swissgrc.com/fr/event/imh-banking-congress-kurs-2025-it-in-banks-25-26-march-2025/)
**Published:** février 14, 2025
**Author:** Gent Krasniqi
**Excerpt:** Austria's No. 1 banking congress celebrates its anniversary: 20 years of KURS! At the 20th edition of Austria's largest banking congress, the key players in the banking sector will have their say. The event will focus on the latest developments and the biggest challenges in the banking sector. Swiss GRC is a sponsor of the congress focussing on ‘IT in banks.
---
### [Austrian GRC Day 2025, 6 May 2025](https://swissgrc.com/fr/event/austrian-grc-day-2025-6-may-2025/)
**Published:** février 17, 2025
**Author:** Gent Krasniqi
**Excerpt:** The motto of the Austrian GRC Day 2025 is ‘GRC Reloaded: Risk Intelligence as the Key to Value Creation’ and shows how governance, risk and compliance enable strategic value creation beyond pure compliance. Experts will discuss ESG, AI-supported risk analyses and geopolitical risks. Swiss GRC is a Gold Sponsor and is presenting an exciting customer use case together with ÖBB.
---
### [Risk-!n Conference 7th Edition, 11 - 13 May 2025](https://swissgrc.com/fr/event/risk-n-conference-7th-edition-11-13-may-2025/)
**Published:** février 17, 2025
**Author:** Gent Krasniqi
**Excerpt:** Risk-!n 2025 is the leading event for risk management, resilience, insurance, compliance and security. From 11 to 13 May 2025 in Zurich, the conference will bring together over 300 experts to discuss current challenges and innovations. One highlight is the premiere appearance of Michael Rasmussen, one of the leading GRC experts. Swiss GRC is a Silver Sponsor.
---
### [SWISS GRC DAY 2025, 14 May 2025](https://swissgrc.com/fr/event/iss-grc-day-2025-14-may-2025/)
**Published:** février 17, 2025
**Author:** Gent Krasniqi
**Excerpt:** The SWISS GRC DAY is the central meeting point for experts and interested parties from all over Switzerland and neighbouring countries. Organised by Swiss GRC AG, the annual conference offers a unique platform for exchanging views on the latest news, challenges and trends in the areas of governance, risk and compliance (GRC). Participants can look forward to an exciting programme with top-class speakers.
---
### [IT GRC Congress 2025, 26 - 27 May 2025](https://swissgrc.com/fr/event/it-grc-congress-2025-26-27-may-2025/)
**Published:** février 17, 2025
**Author:** Gent Krasniqi
**Excerpt:** The IT GRC Congress 2025 will take place on 26 and 27 May in Cologne and is dedicated to the latest developments in IT governance, information security, IT auditing, regulation, compliance and risk management. In addition, the ISACA specialist groups will present relevant future topics. Swiss GRC is a sponsor of the congress and will be actively on site to discuss current challenges and solutions in the field of IT GRC with fellow experts.
---
### [GCC GRC DAY 2024](https://swissgrc.com/fr/event/gcc-grc-day-2024/)
**Published:** mai 22, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** The GCC GRC DAY, taking place on 22 May 2024 at the Conrad Dubai, is specifically designed for GRC experts from across the GCC region. Organised by Swiss GRC in collaboration with GEC Media Groupe, this conference aims to promote collaboration, knowledge sharing and innovation.
---
### [45th MEET SWISS INFOSEC!](https://swissgrc.com/fr/event/45th-meet-swiss-infosec/)
**Published:** mai 31, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** MEET SWISS INFOSEC! is the leading and largest event of its kind. In the 45th edition of the popular event series, experts will present current experience and practical reports. Swiss GRC will be there as a silver sponsor on 24 June 2024. Visit us at our stand.
---
### [20th German IT Security Congress of the BSI](https://swissgrc.com/fr/event/20th-german-it-security-congress-of-the-bsi/)
**Published:** avril 25, 2024
**Author:** Yahya Mohamed Mao
**Excerpt:** Swiss GRC Germany GmbH will be exhibiting for the first time at the 20th German IT Security Congress. This important event, organised by the Federal Office for Information Security (BSI), will take place digitally from 7 to 8 May 2024 and is free of charge for all participants.
---
## Client Regions
### [Switzerland](https://swissgrc.com/fr/wlshowcase_region/switzerland/)
---
### [Europe](https://swissgrc.com/fr/wlshowcase_region/europe/)
---
### [Middle East & Africa](https://swissgrc.com/fr/wlshowcase_region/middle-east/)
---
### [Asia-Pacific](https://swissgrc.com/fr/wlshowcase_region/asia-pacific/)
---
### [Americas](https://swissgrc.com/fr/wlshowcase_region/americas/)
---